Chinese APT Group Hits Air-Gapped Systems in Europe with Malware

0
[ad_1]

IN SUMMARY

  1. Cybersecurity researchers at Kaspersky Labs identified the malware.
  2. The malware used by APT31 targets European industrial control systems.
  3. The Chinese APT31 group is also known as Zirconium and Judgment Panda).

In its latest research report published on July 31, 2023, Kaspersky ICS CERT shared exclusive details of a new threat trend gaining momentum and targeting air-gapped ICS systems.

Researchers at Kaspersky noted that attackers are using second-stage malware after first-stage implants to remotely access crucial industrial control systems (ICS) systems and extract data from them in this campaign. Later, the malware allows third-stage tools to invade the device and transmit data.

The attack should not come as a surprise due to recent reports exposing the activities of Chinese Group Storm-0558. These reports revealed the group’s successful hacking of email accounts belonging to European government officials.

Additionally, there was another report indicating the Chinese APT group’s targeting of European embassies using the SmugX malware. Moreover, just last month, it was reported that Chinese espionage malware was used to target European healthcare systems, utilizing malicious USB drives as a vector of attack. These alarming incidents highlight the need for heightened cybersecurity measures and vigilance in countering such threats.

Reportedly, Kaspersky ICS CERT researchers were investigating a string of cyberattacks targeted against critical infrastructure in Eastern Europe when they discovered second-stage malware capable of evading data security measures typically protecting air-gapped systems.

Researchers believe that through using this novel malware, threat actors are trying to establish a permanent presence on the ICS systems to keep exfiltrating sensitive data stored on these systems.

Further investigation revealed signs indicating the involvement of Chinese state-backed APT31 (aka Zirconium and Judgment Panda), even though the perpetrators had used advanced TTPs to obfuscate their actions.

For instance, they used encrypted payloads, DLL hijacking, injected payloads in legit processes, and embedded malware in authorized apps’ memory to evade detection. These steps highlight the “sophistication of their tactics,” explained Kaspersky ICS CERT’s senior security researcher Krill Kruglov.

For your information, second-stage malware is far more complex and harder to detect than single-stage as it involves two steps to perform its malicious tasks. It is typically disguised as a legit program and can bypass advanced antivirus solutions. 

During their research, the Kaspersky threat intelligence team also identified over fifteen distinct implants, along with several variants, which they divided into three categories. Two of these implants loaded the second-stage malware, one of which is a modular malware that can profile and contaminate removable drives with a worm. It can steal data from air-gapped/isolated ICS networks.

This malware contains three modules, each performing different tasks. For instance, it uses separate tools for profiling/handling removable drives, capturing screenshots, and planting second-stage malware on all connected devices. The second implant can steal data from local computers and transmit it to Dropbox through third-stage tools.

The attack starts with invading the ICS network, for which APT31 uses already known remote access and data collection tools. Once infiltrated, the attackers deploy an advanced modular malware to contaminate the storage devices, and afterwards, data exfiltration commences.

The third and final stage of the attack chain entails exfiltrating data using a range of tools and uploading it on a C2 server. This operation has been planned meticulously, considering that the threat actor uses multiple attack tactics to ensure persistence without getting detected.

APT31's New Malware Evades Detection, Infects Air-Gapped ICS System

This is a developing story, as Kruglov states that this is an ongoing research. Hackread will update its readers as soon as there is any update. Meanwhile, industrial organizations are urged to upgrade their cybersecurity defences, keep enterprise OT network components updated, limit the use of privileged accounts, and exercise caution to prevent the threat.

“As the investigation continues, remain resolute in its dedication to safeguarding against targeted cyber-attacks and collaborating with the cybersecurity community to disseminate actionable intelligence.”

Krill Kruglov
  1. Stealing data from air-gapped PC by turning RAM into WiFi Card
  2. New malware tool can steal files from airgapped PCs using USBs
  3. China-Linked Spyware in Google Play Store Apps, 2m Downloads
  4. Hackers Can Now Steal Data from Air-Gapped PCs via SATA Cables
  5. Malware can extract data from air-gapped PC through power supply
  6. ETHERLED & GAIROSCOPE attacks – Data stealing from air-gapped PC

[ad_2]
Source link
The ASUS Zenfone 10 comes with this groundbreaking camera feature

0
[ad_1]

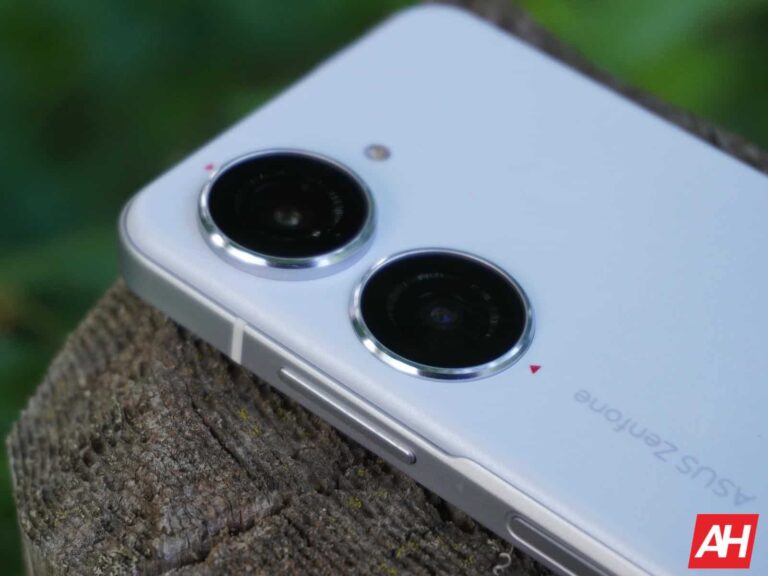
The Zenfone 10 is the latest device from ASUS and it comes with a pretty groundbreaking feature called adaptive EIS, or adaptive electronic image stabilization. ASUS partnered up with IMNIT (Image Intelligence) to power the adaptive EIS with IMINT’s Vidhance Smart Stabilization software.

It was designed with the intention of ensuring your video recordings come out super smooth. IMINT says you won’t need any sort of user input to get the desired results. And it claims you can also forego using any types of physical stabilization products like gimbals. Even if the scenes being captured include plenty of movement and shaky action. The software allows users “to record videos that previously required a separate sports action cam utilizing the Adaptive EIS feature,” says IMINT CEO Andreas Lifvendahl.

The feature was made possible in part by IMINT’s new Vidhance Smart Stabilization software. But also with the help of Qualcomm’s Snapdragon 8 Gen 2 mobile platform. ASUS is also using the new 6-axis Hybrid Gimbal Stabilizer 2.0 in this device. And all of these things together work to achieve the goal of smooth video and images at high quality.

Adaptive EIS on the Zenfone 10 auto-adjusts in real-time

Moments worth capturing happen quickly and that means you may have to adapt quickly. Luckily, if you’re using the Zenfone 10 to capture photos and video you have some help. The adaptive EIS feature on the Zenfone 10 can automatically adjust settings in real-time. The user doesn’t have to input these changes either according to IMINT. The Vidhance Smart Stabilization software does that for you.

Additionally, IMINT says the software provides “Intelligent Motion Recognition” with live motion data from the phone’s gyroscope. It helps in other ways too. For example, the camera can always capture with the largest field of view. Thanks to the VSS software’s ‘Dynamic Crop’ feature. With this, videos aren’t cropped nearly as much as they would be with other phones that have EIS. So you get more of what you’re capturing in the image as a result. Overall, you’re getting super smooth, stable video when recording with the Zenfone 10.


[ad_2]
Source link

Samsung on track to launch its XR headset soon

0
[ad_1]

Samsung is on track with the development of its upcoming XR (extended reality) headset. TM Roh, the company’s head of mobile business, recently teased that an announcement isn’t too far off now. He didn’t give a more precise launch timeframe, though.

During Samsung’s Galaxy S23 launch event in February, the company announced a collaboration with Google and Qualcomm to build the next XR experience. There hasn’t been much follow-up to it since then. The ongoing project made a brief appearance at Google’s I/O 2023 conference in May, and that’s it. Meanwhile, rumors surfaced that the device may debut in February 2024.

However, the launch of Apple’s Vision Pro in June (scheduled to arrive in early 2024) reportedly affected Samsung’s plans. The Korean firm has gone back to the drawing board and is making significant changes to the design and specs of its XR headset. These changes may delay the launch by around six months, pushing it to the second half of next year.

Unsurprisingly, Samsung avoided talking about its XR efforts during its Galaxy Unpacked event last week. However, Roh opened up on it in a press conference after the event. “We are not looking to be happy about launching a single product or creating an ecosystem for one company. Like smartphones, what we are doing is opening an XR ecosystem,” Roh said. “We are expecting an announcement in the not-too-far-off future.”

Samsung and Apple expect the XR headset market to fly soon

The Samsung executive opined that the XR industry will grow “in the vein of smartphones” in the coming years, ZDNet reports. Apple sees a similar future where XR headsets will be as ubiquitous as smartphones and computers. However, the Korean firm may take a different path to that future than Apple. It may start small with XR experiences that rely on smartphones rather than independent content.

“For the short term, perhaps many features or experiences [in] mixed reality would be in connection with [the] smartphone,” Roh told CNET’s Lisa Eadicicco, hinting at Samsung’s current approach. The Korean firm has a long experience in VR and AR technologies, and so do Google and Qualcomm. However, getting multiple teams from multiple companies to work on a project together is easier said than done.

Apple has been reportedly working on the Vision Pro for more than seven years now. Samsung, Google, and Qualcomm’s joint venture is likely just a few years old. We might have to wait a while before the trio has something ready for public demonstration. Roh’s words may have suggested an imminent launch, but he said the same in February as well. Stick around to find out more about Samsung’s upcoming XR headset.


[ad_2]
Source link

Fancy a chit-chat with Abraham Lincoln? AI chatbots coming to Meta

0
[ad_1]

Having absolutely no friends whatsoever will no longer be an excuse for not engaging in online chats. Spare your excuses and embrace modernity, because Meta is working on artificial intelligence (AI) chatbots to entertain you.

A Reuters article retells a Financial Times report about Meta’s latest plans on how to keep users involved on their platforms and not switch to rivals like TikTok or Twitter (sorry, sorry – X). We’ve already reported on Zuckerberg’s search for ‘retention hooks’ to mitigate the Threads exodus; maybe these new AI chatbots are part of that plan.

Meta has apparently been very busy and kept a secret in these last few months because the report claims this new feature is to be launched as soon as September. Allegedly, Meta’s developers are coding relentlessly different prototypes for chatbots. The goal is for Meta users to have sort of humanlike chit-chats with machines without realizing they’re interacting with a very sophisticated collection of zeros and ones.

Choose your chat companion


As the report tells, there would supposedly be several personalities to choose from. One of the AI chatbot variants would be coded in such a way that it could answer like… Abraham Lincoln. Other cited Meta AI chatbot would be in the style of a ‘surfer’ – ask him about places to travel and he’ll answer.

What could go wrong?


There are two key questions surrounding these AI chatbots. First, how to be sure that tech giants are making something unbiased and neutral? Second, on a completely technical level, how are they ensuring that they’re implementing the authentic style of a given historical figure?

The possibilities are endless, just like the possibilities for screwing up royally. These AI chatbots could potentially gather so much personal information about the users it interacts with, it’s hilarious.


[ad_2]
Source link

New Android Malware Via WhatsApp Steal Call logs

0
[ad_1]

According to reports, a new Android malware is circulating under the guise of a fake chat application that is being distributed through WhatsApp.

This malware is discovered to belong to the APT Bahamut and has some footprints of tactics used by the DoNot APT.

This malicious Android application is initially termed “Coverlm” which is installed under the name “SafeChat” on Android devices.

This application’s user interface seems to be deceiving and would convince any Android user that it is a legitimate chat application. 

However, once installed, the malware exploits unsuspected Android libraries for extracting and transmitting the data to a C&C (Command and Control) server.

This android malware seems to be targeting individuals in the South Asian region.

Android Malware Via WhatsApp

As previously stated, the app appears as a chat app and requests permission upon opening.

It asks for the “ignore battery optimization” permission which lets the application run on the backend and communicate with the C&C smoothly.

Ignore Battery Optimisation (Source: CYFIRMA)

Upon providing the permission, the signup page appears. Proceeding further, the application asks for another permission under the question, “This permission is required to function properly,” which, when “allowed,” takes the victim to the Accessibility settings.

Unknown permission asked by the application (Source: CYFIRMA)

This permission pops up again and again until the permission is enabled. Once the user allows this permission, the application takes the user to the dashboard, which looks like a legitimate chat application.

Android Malware Behaviour

Reviewing the code in the Android Manifest file of this application showed that the threat actor declared many permissions to perform malicious behaviors with this application.

Some of the dangerous permissions include,

PermissionsDescriptions
ACESS_FINE_LOCATIONAllows the threat actor to fetch precise locations and track the live movement of mobile phones.
READ_CONTACTSThis permission allows TA to read and fetch contacts.
READ_EXTERNAL_STORAGEThis permission allows the threat actor to access the file storage of the mobile.
READ_SMSThis allows the threat actor to read all the SMSs of the device.
READ_CALL_LOGThis permission allows the threat actor to read call logs.
READ_CONTACTSThis permission allows the threat actor to read all the saved contacts in the device.

Furthermore, the application used port 2053 for communicating with the C&C server.

Modules of the application represented the use of the Ktor framework developed with Kotlin which was used for communicating with command and control servers.

Previously, DoNot APT deployed the retrofit library for communication. 

The application is capable of collecting information like IMEI, device ID, SIM details, and location. 

One Nation State Interest

Analyzing further, this attack by APT Bahamut and their previous attack indicated that they have been part of one nation-state government’s interest.

In addition, it is suspected that these threat actors are based out of India as most of their targets pose an external threat to India.

Nevertheless, the facts are yet to be confirmed about their whereabouts. A complete report about the malware’s operation was published by Cyfirma which shows the source code, operation, and other detailed information about this malware and the APT group.

Indicators of Compromise

IndicatorTypeRemarks
8A35D0B20B6F057FE42E606A124CB84D78FA95900A16B056269F1CC613853989Hash: SHA256Safe_Chat.apk
https://laborer-posted[.]nl:2053Domain and portCommand and control

Keep yourself informed about the latest Cyber Security News by following us on GoogleNews, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

YouTube Multiview is finally available, but not for mobile or web devices

0
[ad_1]

For the past few months, the YouTube Multiview feature has been undergoing tons of testing. Finally, this feature is making its way to some users of the video streaming platform. Of course, this new feature will come in handy for these users, as it’d enable them to watch content in an entirely new way.

It’s a bit easy to tell the use of this new YouTube Multiview feature that is currently rolling out. As its name states, it aims to help users watch more than one content at the same time and on the same screen. Those hoping to watch the upcoming NFL season games on their YouTube TV device will be able to benefit from this new feature.

However, this new feature has a limitation that will affect how users access channels. Another limitation is the fact that not all YouTube users will be able to access this feature now that it is available. For those who won’t feel the impact of these limitations, accessing the multiview feature will be very easy.

Limitations affecting the new YouTube Multiview feature that is now official

Lots of YouTube fans were thrilled when the company took to its Twitter page to announce the arrival of this new feature. However, a closer look at the announcement means that the joy for some fans will be short-lived. In the post, YouTube explained that the launch of this feature was “for WNBA League Pass subscribers on YouTube TV” and Primetime Channels.

This statement highlights two limitations that’d impact certain users of the streaming platform. The first is that only subscribers to the WNBA League Pass channel will be able to use this feature. Additionally, the YouTube Multiview feature will only work for live game streaming.

Another limitation this announcement points out is that this feature will only be available for YouTube TV users. So if you want to stream WNBA live games at the same time, you can’t do so with your mobile smartphone or via the YouTube web platform. You can only access this feature via the YouTube TV platform on a smartTV or a streaming device.

To access it via the TV app, you can look under the “recommended multiview” or “watch next” tabs. Here you’d find a curation of up to four games that you can watch at the same time on the same screen. YouTube is also planning to make this feature available on more channels, hence giving users the ability to pick what they want to multiview.


[ad_2]
Source link

iPhones with old Twitter branding offered for astronomical prices

0
[ad_1]

Believe it or not, iPhones with old Twitter branding are selling for astronomical prices. Prices reach as much as $25,000, for whatever reason.

As many of you know, the Twitter rebrand started not long ago. Elon Musk decided to ditch the Twitter name, and go with ‘X’ instead. The logo has been replaced along with the name, along with a number of other details within the app. The process is still ongoing, though.

iPhones with older Twitter branding are on sale for astronomical prices

Having said that, many people don’t like this change, and would prefer for Twitter branding to stay. That prompted some iPhone owners to try and make money in the process. Some of them are selling iPhones with the old Twitter app and branding for astronomical prices.

Those are simply apps that have not been updated with the X name or logo. There’s an eBay listing that has the iPhone 11 Pro Max with the old Twitter app, and it’s selling for $25,000. That doesn’t mean it’ll actually be sold, but… it’s there.

There are other sellers too, though they’re a bit more realistic. They’re demanding between $800 and $15,000 for used iPhones with the Twitter app installed on them.

Some of them are selling such devices via Twitter aka X too

Heck, people are even trying to sell their iPhones with the Twitter app via Twitter (aka X) itself, notes Phone Arena. Like Andrew Clare, for example, which was used as an example (shown below). He’s selling his iPhone 14 Pro with the Twitter app for $4,200.

If you think this is all ridiculous, well, it may be, to the vast majority of people, but some are willing to pay the price. As a reminder, a first-gen iPhone was sold for over $190,000 last month.

Some people are willing to give it a shot, and if they managed to do it, great. If not, well… nobody was hurt in the process.


[ad_2]
Source link

Human or AI? Instagram might label AI-generated content

0
[ad_1]

Recently, Meta, in collaboration with Microsoft, introduced the new Llama 2 – a next-generation large language AI model. This new technology enables companies to customize AI for their specific needs, like creating chatbots and image generators. It seems that consumer-facing generative AI tools based on this model are already on the horizon.According to reverse engineer Alessandro Paluzzi (via Engadget), it looks like Meta is developing several new generative AI features for Instagram. These features include labels that will help users to identify images “generated by Meta AI.”

If you wonder what reverse engineers do, they are sort of detectives for technology. They take apart things like software or devices to figure out how they work, even if they were not the ones who originally made them. It’s like solving a puzzle to understand the hidden secrets behind the technology.

The screenshot shared by Paluzzi shows an in-app message explaining that posts created using Meta’s generative AI tools may soon be labeled within Instagram. This suggests that the company could be interested in helping users identify AI-generated content.

There have been concerns about the safety and impact of free consumer-facing AI tools on our online presence. Some worry that they could aid the spread of misinformation or mislead people. To address these concerns, some AI companies, including Meta, have pledged to adopt AI safety measures, like using watermarks for AI-generated content. The introduction of labels for AI-generated content on Instagram might just be part of these measures.

Microsoft, Google, and OpenAI stand at the forefront of the artificial intelligence sector in the US. Last month, following a call to action from the White House, they made commitments to incorporate safeguards into their AI technology. Additionally, these industry leaders have joined hands to establish the Frontier Model Forum, an association focused on advancing AI, of which Meta is also a part. The forum’s primary goal is to ensure the secure and ethical advancement of frontier AI models.

As AI continues to advance at a rapid pace, social media platforms should pay more attention to AI-generated content and clearly label it, even if the content is generated from third-party apps or software. Instagram already has many AI-generated human-like models posing as influencers, which can lead to confusion and misperception of reality.

[ad_2]
Source link

Iranian Hackers Posed as Israelis in Targeted LinkedIn Phishing Attack

0
[ad_1]

IN SUMMARY

  1. The phishing attack targeted Israeli researchers and civil servants.
  2. The scammers engaged in conversations to send malware files.
  3. The campaign has been thwarted by the Israeli security agency, Shin Bet.

The ongoing cyber war between Iran and Israel has once again made headlines, as the Israeli internal intelligence agency, Shin Bet, successfully foiled a sophisticated spear-phishing attack targeted at Israeli users, particularly researchers and civil servants from various organizations.

The attack, carried out apparently by state-backed hackers from Iran, utilized fake LinkedIn profiles and sophisticated social engineering techniques to gain unauthorized access to Israeli citizens’ computers and steal sensitive information.

Citing i24news, Shin Bet revealed that the modus operandi of the Iranian hackers involved creating fake profiles, impersonating real Israeli citizens, and initiating conversations on LinkedIn before continuing the communication via email. This approach allowed the hackers to establish trust and credibility, making it easier to convince the targets to open attachments or click on links.

During the conversation, the malicious actors would send seemingly harmless attachments, such as invitations to conferences or files related to the targets’ professional interests, such as studies or articles.

Unbeknownst to the recipients, these attachments contained malware that, once opened, infected their computers. This malware granted the Iranian hackers full access privileges, enabling them to remotely take over the infected devices and access all stored information.

Iran Phishing Campaign Targeting Israeli Users Thwarted by Shin Bet
Chat screenshot (Credit: i24NEWS English)

The Iranian cyber attackers were cunning in their preparation, gathering information for their fake LinkedIn profiles from various social media networks. By doing so, they could create connections based on shared interests and past interactions, making the phishing campaign more convincing and difficult to detect.

This incident is not the first time that Israeli citizens have faced targeted phishing attacks. In the past, hackers have employed various tactics, including spear-phishing email campaigns containing malware disguised as explicit content. These sophisticated attacks aim to exploit human curiosity and emotions, enticing unsuspecting users into opening dangerous files.

As cyber warfare continues to escalate, nations and organizations must remain vigilant against such threats. Experts in the cybersecurity field advise users to exercise caution when engaging with unknown contacts, even on professional platforms like LinkedIn. It is crucial to verify the authenticity of profiles and refrain from opening attachments or clicking on links from suspicious sources.

Additionally, organizations and individuals are encouraged to keep their systems and software up-to-date, use reliable antivirus software, and regularly back up critical data to mitigate the impact of potential cyberattacks.

The battle between Iran and Israel in cyberspace is a reminder that the digital landscape is becoming an increasingly contested and complex arena. Governments and institutions worldwide must join forces to counter and defend against these state-sponsored cyber threats, as the consequences of such attacks can have far-reaching implications on national security and individual privacy.

  1. Hamas hacked smartphones of over 100 IDF soldiers
  2. US Charges 3 Iranian Hackers Over Ransomware Attacks
  3. Iranians Drop RatMilad Android Spyware Mimicking a VPN App
  4. Hamas hackers posed as women to con IDF into downloading malware
  5. Hackers Posed as Women to Con Israeli Officials into Installing Malware

[ad_2]
Source link

Organizations with 51-200 Employees Targeted by Ransomware

0
[ad_1]

High-profile ransomware attacks on corporations like Kaseya, Colonial Pipeline, and MOVEit may lead to the misconception that only large organizations are targeted.

However, the fact is that underestimating the risk due to focusing on large organizations may increase your vulnerability to ransomware attacks.

Cybersecurity researchers at Trellix recently asserted that organizations with 51-200 employees, which are small or medium-sized organizations, are frequently targeted by ransomware attacks.

The Method and Source of Ransomware

Trellix Advanced Research Center gathered data on 9,000 global ransomware victims, showing any organization can be targeted.

Trellix researchers used statistics to enhance victim profiles with organization details, revealing unique insights. Moreover, they also speculated that the unlisted victims likely exist.

While the details of the companies or organizations that are used to evaluate these data are mainly:-

  • Company sector
  • Company location
  • Company revenue size
  • Company size

Data from 97 ransomware groups over 2 years show Lockbit as the top extorter on leak pages, except for Clop’s recent rise.

Victims per ransomware group (Source – Trellix)

Data shows the highest number of victims from 51-200 employee companies (20.57%), then less than 50 employees (16.91%), and decreases for larger companies.

Distribution of global ransomware victims (Source – Trellix)

Here below, we have mentioned the decreasing percentages for larger companies:-

  • 501-1,000 at 7.12%
  • 1,000-5,000 at 9.92%
  • 5,000-10,000 at 2.38%
  • 10,000+ at 4.46%

Apart from this, there is an “unknown” category that accounts for 27.87% of victims, totaling 8,943 ransomware cases.

While in the U.S. ransomware attacks, 33.57% of victims are companies with 51-200 employees.

Small businesses (less than 50 employees) rank second at 24.48%, larger organizations have lower percentages.

Data on 8,943 cases reveals the “unknown” category is the largest at 32.36%. The companies with a revenue range of $10M-$50M were most affected at 21.93%, followed by $1M-$10M and $1B-$10B at 14.04% and 9.71%.

Company size by revenue globally (Source – Trellix)

Data overview of U.S. ransomware victims by revenue size:- 

  • $10M-$50M most impacted (37.63%)
  • $1M-$10M close second (19.49%)
  • Smaller (6.27%) and larger (2.46%) companies were also affected

Sector Impacted

Here below, we have mentioned all the sectors that are impacted:-

  • Technology
  • Health Care
  • Oil & Gas
  • Industrials
  • Financials
  • Consumer Services
  • Consumer Goods
  • Basic Materials
  • Telecommunications
  • Government
  • Utilities

Data on 8,943 ransomware cases shows industrial (24.61%) and consumer services (14.28%) sectors are most impacted, but, besides this, the “Unknown” category stands at 27.28%.

Publicly exposed ransomware victims (Source – Trellix)

A clear heatmap of 8,493 victims shows the U.S. was targeted most, followed by the UK, Germany, Canada, and Italy. Other countries were not excused; lower percentages hint at targeting accuracy or underreporting.

Keep informed about the latest Cyber Security News by following us on GoogleNews, Linkedin, Twitter, and Facebook.


[ad_2]
Source link