Adobe Patched Critical ColdFusion Zero-Day Flaw Under Attack

0
[ad_1]

Adobe released an emergency security patch for ColdFusion, addressing a critical zero-day vulnerability. The tech giant warned users of active exploitation of the flaw, urging users to update their systems as soon as possible.

Active Exploitation Detected For Adobe ColdFusion Zero-Day

Adobe’s recent security bulletin highlights addressing a critical-severity zero-day flaw affecting Adobe ColdFusion.

ColdFusion is Adobe’s proprietary software development platform facilitating rapid web application development. The platform includes an integrated IDE and full scripting language. It helps develop diversified applications from data-driven sites to remote services such as WebSockets, REST services, SOAP web services, etc.

According to Adobe’s advisory, the service has addressed three vulnerabilities in the tool. One of these, CVE-2023-38205, is a critical-severity flaw with a CVSS score of 7.5. Adobe confirmed this vulnerability as a zero-day, detecting its active exploitation in “limited attacks.”

The firm has not shared details about this vulnerability besides listing it as a security feature bypass due to improper access control. However, researchers from Rapid7 reported the matter in detail when they noticed active exploitation attempts chaining the previously patched vulnerabilities CVE-2023-29298 (discovered by Rapid7) and CVE-2023-38203 (discovered by ProjectDiscovery). The researchers observed that the patch for CVE-2023-29298 didn’t completely fix the issue, leaving space for adversaries to exploit the flaw.

Following this discovery, Rapid7 swiftly reported the matter to Adobe, which then included the patch for CVE-2023-29298 with CVE-2023-38205.

The other two vulnerabilities fixed with the latest ColdFusion release include a critical code execution vulnerability due to the deserialization of untrusted data, CVE-2023-38204 (CVSS 9.8), and a moderate severity security feature bypass, CVE-2023-38206 (CVSS 5.3).

Adobe listed the following software versions as vulnerable to the flaws.

  • ColdFusion 2023 (Update 2 and earlier)
  • ColdFusion 2021 (Update 8 and earlier)
  • ColdFusion 2018 (Update 18 and earlier)

Whereas the firm patched the issues with ColdFusion 2023 (Update 3), ColdFusion 2021 (Update 9), and ColdFusion 2018 (Update 19). Users must update their systems to these versions to receive the patches accordingly.

Let us know your thoughts in the comments.


[ad_2]
Source link
Netflix rolls multiple features into My Netflix tab on mobile

0
[ad_1]

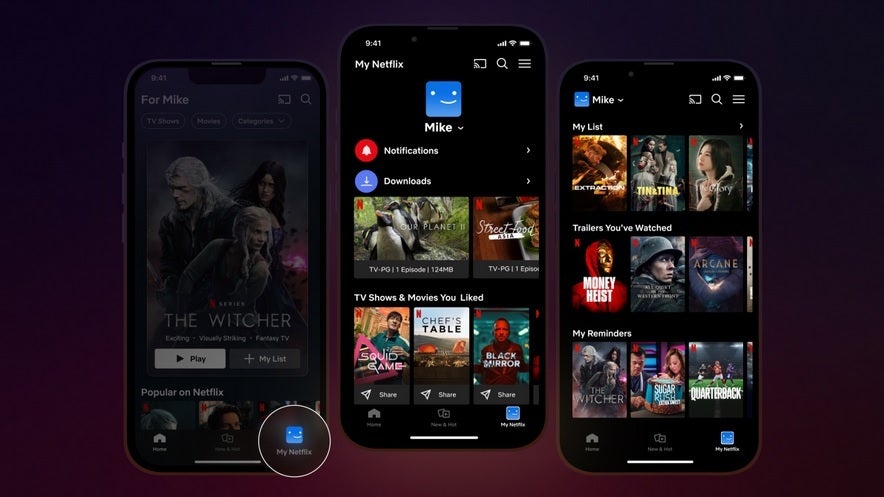
Netflix is hoping you’ll forget about the password sharing crackdowns with the launch of its new feature called the My Netflix tab. It’s a “one-stop shop tailored to you with easy shortcuts to help you choose what you want to watch,” the company says in a blog post.

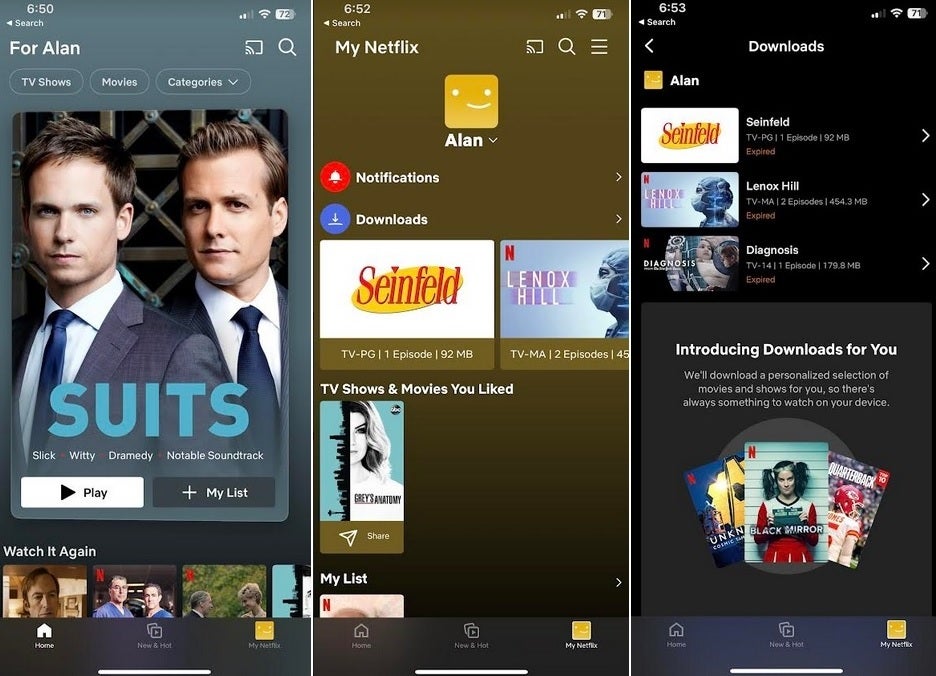
Basically, the My Netflix tab is taking the place of downloads in the mobile app. Downloads will now be rolled into the new tab along with a handful of other features the service offers. Tapping on the new tab, you can find not only your downloads, but a host of content you’ve interacted with. Including shows and movies you’ve liked, things you’ve added to your list, and reminders.

It even contains a carousel of trailers you’ve watched on the platform. That last one could actually be quite useful. Had you watched any trailers for content you think you might be interested in. But forgot to add to your list.

The My Netflix tab rolls out to iOS users today, and Android soon

My Netflix Tab Feature (2)

Netflix is rolling out this new feature beginning today, but only for iOS users. The company says iOS users can find the My Netflix tab in the app from today. But Android users won’t have access to it until August.

The company doesn’t mention a specific time for the Android arrival of the feature. So if you’re looking forward to it, it might be best to just assume it’ll show up at the end of the month. That way if it shows up earlier you can be excited that it’s available sooner than you were expecting.

Netflix says the more you tell it what you like, the more you’ll see on this new tab. So think of it kind of like recommendations. Where the recommendations for content pop up the more you watch stuff on Netflix as it tries to learn what content to serve you. For now this seems to be an iOS and Android only feature. Which means you shouldn’t expect it to show up on the website, or the apps for other platforms like consoles or smart TVs.


[ad_2]
Source link

The coming Spotify Premium price hike will hit the US next week

0
[ad_1]

Recent reports from the Wall Street Journal point out that US users will see a Spotify Premium price hike. Currently, premium subscribers pay a monthly fee of $9.99, but that is set to see a change in this price in the coming days. The increment to premium subscription pricing is one that the company’s CEO has been hinting at over the past few months.

Spotify sees this price increment as being okay since it’d help boost profit for the company. However, users of the streaming platform’s services might not see things from Spotify’s point of view. Once this price increment hits, there might be some compliance on the part of users in the US.

For now, the reports point out that this price hike will affect US users sometime next week. But Spotify isn’t the first streaming service to hike its prices in recent times. Also, this isn’t the first time that Spotify will be increasing the prices of its subscription prices across various plans.

The US will soon see a Spotify Premium price hike, here is what you need to know

Back in 2021, Spotify increased the prices of plans in certain markets by up to $2. From then till now, users of Spotify in these markets have been able to adapt to that price change. Now, two years after the last price increment, Spotify is a few days away from increasing the price for their plans again.

This time around, the coming price increase is said to be up to $1 on certain plans. At the moment, Spotify’s Basic plan costs $9.99, but the coming increase might cost $10.99. This is a slight increase, but a good amount of users will complain about this increase.

So, if users will get irritated by the price increase, why would Spotify still affect it by next week? At the moment, Spotify hasn’t made any comment about the coming price increase. However, over the past few months the streaming platform has been informing users of this coming change, so prepare themselves.

Other streaming platforms like Apple Music, Amazon Music, Tidal, and even YouTube Music have kicked up their prices. These are the biggest competitors in the music streaming industry and they have all made some adjustments to their subscription prices. For some reason, Spotify is the last on this list to increase prices for its plans.

By next week, users in the US will get to know the new price they’d pay for monthly subscriptions. This change might go into effect with subscriptions for the coming month. Users will get to know the new price they’d pay to continue streaming without ads by next week.


[ad_2]
Source link

Netflix adds new feature to iOS, Android to help you quickly find content to watch

0
[ad_1]

Netflix announced today that it is adding a new feature to its popular mobile phone app. Called My Netflix, this is a one-stop shop for both iOS and Android users that features shortcuts to help you find something to stream on the platform. The new My Netflix Hub will show you the content you recently downloaded, the movies and television shows you gave a thumbs up to, shows and movies you’ve saved to My List, trailers that you’ve viewed, what content you’re in the middle of watching, content you’ve recently viewed and more.

With the My Netflix Hub, you can check it out wherever you are to get ideas of what to watch next including shows and movies that you’re in the middle of watching, or content that you’ve downloaded to view at any time. Even with the capabilities of the My Netflix Hub, you can always visit your Home tab or other parts of the app to see the entire Netflix library.

The My Netflix Hub learns more about you the more you use it. So if you save more medical dramas or give a thumbs up to every episode of Grey’s Anatomy, you’re apt to find more medical dramas in the My Netflix Hub. The Hub is rolling out today to iOS users and will be available on Android devices early next month. Check to see if the My Netflix Hub has arrived by opening the app and looking for the tab on the bottom right corner of the display.

If the My Netflix Hub hasn’t been added to your iOS Netflix app, you can try to manually update the app by opening the App Store and tapping on the profile picture in the upper right corner. You’ll see a list of apps that are in a queue to be updated. Scroll down until you see “Netflix” (that is, if it appears on the list) and tap on “Update.” Wait for the app to be updated before you open the Netflix app to check whether the My Netflix Hub has arrived on your iPhone. I can tell you that the update has hit the Netflix app on my iPhone 11 Pro Max running iOS 16.6.

And one last thing. If you don’t have the Netflix app on your device, you can tap on this link to install it on your iOS device or tap on this link to install it on your Android device.

[ad_2]
Source link

Cl0p Ransomware Gang Leaks MOVEit Data on Clearweb Sites

0
[ad_1]

At the time of writing, the clearweb domain of the Cl0p Ransomware Gang was offline; however, the gang’s entry to the clearweb reveals upcoming cybersecurity threats intended for their victims.

The Cl0p ransomware gang is among the cybercrime syndicates that have exploited the MOVEit vulnerability more extensively than any other. To exacerbate the situation, the ransomware gang is now leaking the data it stole through the MOVEit vulnerability on its clearweb domain.

According to security researcher Dominic Alvieri, the Cl0p ransomware gang is leaking the data they stole from the MOVEit Transfer platform in May on the publicly accessible website. The gang exploited a zero-day vulnerability in the secure file transfer platform, leading to a data breach that drastically impacted hundreds of businesses and government institutions worldwide. 

Cl0p has dumped the data as large downloadable files instead of opting for specific searchable items and didn’t host the site on the Tor network, as has been the case in many previous data leaks.

Cl0p Ransomware Gang Leaks MOVEit Data on Clearweb Sites
Screenshot from Cl0p’s dark web domain (Image credit: Hackread.com)

What is the difference between Clearweb and Dark Web

The Clearweb, also known as the Surface Web or Visible Web, refers to the part of the internet that is easily accessible and indexed by search engines like Google. It includes websites and web pages that can be accessed through standard web browsers without requiring any special configurations.

On the other hand, the Dark Web is a portion of the internet that is intentionally hidden and not indexed by traditional search engines. Accessing the Dark Web requires specialized software, such as the Tor browser, which provides anonymity and encryption.

This anonymity allows users to access hidden websites that use “.onion” domains. The Dark Web is often associated with illicit activities, illegal marketplaces, and anonymous forums where users can communicate without revealing their identities.

It is worth noting that Cl0p has recently developed this tactic to blackmail their victims where the gang creates Clearnet websites hosted on the surface web to leak stolen data. They first tried this tactic to leak data stolen from the PWC business consulting firm, which was uploaded in four spanned ZIP archives. Later Cl0p used the same tactic for leaking data from TD Ameritrade, Aon, Kirkland, and Ernest & Young.

Screenshot from Cl0p’s clearweb domain (Image credit: Hackread.com)

Perhaps, the Cl0p ransomware gang believes it to be a more effective method for extorting victims (even though such websites get quickly removed). Leaking data on Tor-hosted darknet platforms has lost the charm given their restricted reach.

Although Tor offers anonymity, not all users can access the sites without a specialized browser, whereas, on the surface web, anyone having the website link can download the stolen data.

Another reason is that search engines don’t index darknet content, so, download speed is usually pretty slow, whereas, on Clearweb, the site gets indexed, and downloading is quicker. Nonetheless, this tactic is more detrimental for the victims as they become vulnerable to harassment and online scams from all fronts.

Cl0p is among the most notorious hacking gangs currently having successfully targeted high-profile firms and extracted millions of dollars in ransom. Per Coveware’s latest report, the gang has raked in $75-$100 million from their latest MOVEit attacks. Coveware CEO Bill Siegel noted that only a handful of Cl0p’s victims generally give in to their demands.

Therefore, the hackers are using different extortion strategies. Siegel also noted that MOVEit attacks have proven far more successful than GoAnywhere data theft, where the hackers could breach 130 victims and didn’t receive their desired ransom as well.

As expected, all Clearweb extortion sites created by the Cl0p ransomware gang have been taken offline, proving the short-lived nature of this method. Security researchers highlighted that Cl0p’s latest site lacks the sophistication seen in the approach used by the rival ALPHV ransomware gang, aka BlackCat, which introduced this method to pressurize their victims more profoundly.

  1. Big Head Ransomware Found in Fake Windows Updates
  2. LockBit Ransomware Expands Attack Spectrum to Mac Devices
  3. Genesis Market’s Clearnet domain seized; Dark Web site still online

[ad_2]
Source link

Police stop removal of Twitter HQ Sign halfway through

0
[ad_1]

Twitter is having an interesting day, first with the official changeover to the branding as X and now with San Francisco Police having stopped the removal of the Twitter HQ sign halfway through the process. If you’ve spent any amount of time on the site today then you’ve probably already seen the new logo. Elon Musk confirmed over the weekend that Twitter would be re-branded. The new name is now X and today set those changes in stone. At first it was just the disappearance of the iconic bird logo. Which, by the way, was apparently named Larry.

Larry is gone now. In its place, a generic letter “X” that isn’t even an original logo, but basically just the letter X in unicode. That however, isn’t even the most hilarious part of today’s Musk antics. Because after all these changes, surely the next step would be to change out the company sign on your building. Musk tried to do just that and got all the way to the letter “e” before San Francisco police arrived and shut down the operation. Why is anyone’s guess. But some online seem to think that it might have to do with permits. Or in this case, lack thereof.

Police may have stopped the Twitter HQ sign removal for lack of permits

This hasn’t been confirmed, but the suspicion is that Musk may not have acquired permits for the equipment being used to take down the sign. Presumably, you’d need a permit for that equipment to be on the street. And if Musk didn’t acquire them, it seems reasonable to assume that there was potential for authorities to show up an put a stop to things. Which seems to have happened.

The end result is that now the majority of the sign is gone. But you can still see the letter e and r on one side. The entire “Twitter” branding is still there facing the other direction.

There’s no word yet on whether or not the sign removal will resume. Or when. But it seems likely that if Musk is serious about keeping these changes (he’s rolled back quite a few before), then at some point he’ll want the rest of the sign taken down. Either way, it’s sort of comical if you think about the whole situation.


[ad_2]
Source link

Twitter will become history today, ‘X’ set to take over

0
[ad_1]

Twitter will basically become history soon, as Elon Musk plans to rebrand it to ‘X’. Elon Musk, the owner of Twitter, confirmed as much recently. Even the X.com redirects to Twitter.com now.

Twitter is becoming history, ‘X’ is expected to take over today

This rebrand will see the Twitter logo get replaced by an “interim X logo”. Musk shared a lot of tweets regarding the rebrand, but he didn’t really say all that much in the process.

We do know that the change is expected at some point today, actually, so we won’t have to wait for long. He even said the following: “we’re cutting the Twitter logo from the building with blowtorches”.

Musk allegedly also sent an email to Twitter employees, informing them of the change. He also mentioned that it’s the last email they’ll receive from a Twitter address.

We know what the logo will look like

Elon Musk said that the company is going for a “minimalist art deco” approach when it comes to the ‘X’ logo. It will likely refine the logo later on, though. Twitter’s CEO, Linda Yaccarino, went ahead and actually shared the logo the company will be using, it’s shown below.

Twitter new logo X

If you go over to Elon Musk’s Twitter profile, you’ll notice that he changed his profile picture to the ‘X’ logo. It’s not exactly a secret that Elon Musk wants to push Twitter to be the “everything app”.

He bought the X.com domain from PayPal back in 2017, and he’s now putting it in use, it seems. We won’t have to wait for long to see this change, as already mentioned, it’s taking place later today.

We’re not sure if only the logo and the domain name will change, or will we see more changes take place in the process. It’s anyone’s guess at this point, but one thing is for sure, the ‘Twitter’ name and logo are becoming a thing of the past today.


[ad_2]
Source link

Google is Blocking Employee Internet Access

0
[ad_1]

Google is to start a pilot program to have employees work without internet access as a way to decrease the risk of cyberattacks.

According to internal documents, Google is implementing a program to minimize the likelihood of cyberattacks. The company notes that its employees are often targeted by such attacks.

Google Pilot Program:

The pilot program can refer to different things depending on the context. It can be a small-scale experiment to test a large-scale project, a peer-support initiative for mental health, a virtual program with strategies, tactics, and tools, and a program that creates initiatives for low-income inner-city students.

Initially, the organization selected more than 2500 employees, but they opened it to volunteers to use the pilot program; CNBC reported.

The company planned to enable only internal web-based tools and their owned websites like Gmail and Google Drive. Internet access is allowed only who need compulsory Internet access to work.

As per an internal description, the program aims to decrease the occurrence of cyber-attacks as Googlers are often targeted by such attacks.

Providing internet access to all employees can lead to attackers gaining access to user data and infrastructure code, which may result in a major incident for the company.

Turning off internet access secure from attackers, they cannot easily run arbitrary code remotely or grab data.

Google is training for a companywide rollout of various artificial intelligence tools, trying to boost its security.

Microsoft reported that Chinese intelligence hacked into company email accounts belonging to two dozen government agencies, including the State Department, in the U.S. and Western Europe in a “significant” breach.

“Ensuring the safety of our products and users is one of our top priorities,” a Google spokesperson said.


[ad_2]
Source link

YouTube just lifted another feature from TikTok

0
[ad_1]

In the social media war, companies “borrowing” features from other companies is not unheard of. We’ve seen features tossed around between TikTok, YouTube, Instagram, and Snapchat, and it’s not stopping anytime soon. YouTube is testing the feature to turn comments into actual Shorts, according to Android Central.

If this sounds familiar, this is a feature that TikTok brought a while back. If someone comments on your “Tok”, you’re able to select that comment and craft a separate video off of that. This could come in handy if someone posts a comment that sticks out to you.

YouTube will let you create Shorts out of comments

There’s no sugar-coating this; YouTube definitely copied TikTok’s homework on this one. It seems like it will function exactly the same way as TikTok’s feature. If someone comments on your Short, you’ll be able to select that comment and create a full Short from that comment. That short will show up on your profile as well as the main Shorts feed.

It seems that other people can create Shorts based comments, and not just the original video creator. So, if you’re watching someone else’s video, you might be able to create a short based on a comment on that video.

That seems neat, but there’s one thing to note. If someone makes a Short based on a comment on your video, YouTube will not notify you. Also, if someone makes a Short on a comment you posted, you won’t be notified. We’re not sure if that’s going to change, as this is still in the early stages.

You most likely won’t see this feature at the moment. YouTube is testing this feature on a limited selection of users. So, chances are that you either won’t see this feature for a while or you won’t see it at all. If you want to see if you’re part of the test, make sure that your YouTube app is up to date.


[ad_2]
Source link