Motorola Defy Satellite Link is now available for purchase in the US

0
[ad_1]

With satellite connectivity being a big deal, the Motorola Defy Satellite Link is here to save the day. Motorola put this device in the spotlight a few months ago after its launch, and it is now available for purchase. The idea behind the development of this device is that it can help users access the internet even in areas with little or no internet coverage.

To access the internet, users would only need the Motorola Defy Satellite Link, which would find a nearby satellite to connect with. Once this connection between the Defy device and the satellite is secure, the user would be able to access certain services on their smartphone. This piece of technology is great for those whose jobs entail that they move into areas with low network coverage.

Well, anybody can own this device as it can come in handy in the event of a network outage. Some devices already have satellite connectivity features built in just for rainy days. If your device doesn’t have this feature, and you see it as being important, then you can opt to get the Motorola Defy Satellite Link.

Details, pricing, and where to buy the Motorola Defy Satellite Link

A few months ago, details on the Motorola Defy rugged device to launch in collaboration with Bullitt Group hit the internet. This device, although not yet available, would come with built-in satellite connectivity features. But while fans anticipate the launch of this rugged smartphone with satellite connectivity, Motorola is offering satellite connectivity for less.

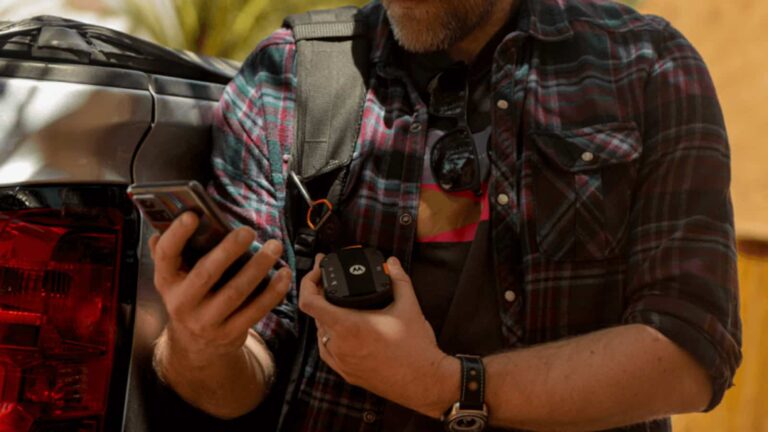
The Motorola Defy Satellite Link is a compact device that can give your device access to satellite connectivity. Staying true to the Motorola Defy brand, this is a rugged device that comes with Ingress Protection (IP68). It is drop and water-resistant, it also features MIL SPEC 810H certification and is resistant to thermal shock.

In certain parts of Europe, this device has been available for usage over the past few months. However, the company is finally extending availability and support to the US now. Other regions such as South America, Africa, and Australia will get support for satellite connectivity with this device in the coming months.

So if you are living in the US and need a device that can help you to access the internet via satellites, you can get one. The Motorola Defy Satellite Link is priced at $149. This device will connect to your smartphone via Bluetooth and offer satellite internet connectivity.

With satellite internet, users can send and receive text messages as well as send out SOS alerts. But to access these features, users would need to pay for either the Essential, Everyday, Premium, or Freedom plans. All except the Freedom plan are monthly subscriptions, the more a user pays, the more features they get access to.

Some specifications of this device include a 600mAh battery that can last 4 days on a single charge. It uses a USB-C charger to power up the battery once there is a need to. For processing power, it makes use of the MediaTek MT6825 NTN chipset. Lastly, it has a Lanyard, so it can be attached to the user without getting lost.


[ad_2]
Source link
Mockingjay Process Injection Technique Permits EDR Bypass

0
[ad_1]

The newly devised Mockingjay process injection technique can evade most existing security mechanisms, allowing EDR bypass. It’s a trivial process to carry out, requires minimal steps, and delivers maximum results merely by exploiting legit DLLs.

Researcher Devised Mockingjay Process Injection Technique

According to a recent post from Security Joes, Mockingjay is an advanced process injection strategy that successfully bypasses most detection measures.

Process injection is a known attack strategy where an adversary may inject codes directly into a trusted running process. Some process injection types include Dynamic-link Library Injection and Process Doppelgänging. The aim is to escape detection while gaining access to the process memory and network resources and gain elevate privileges.

While it’s a viable technique, process injection involves some specific actions, such as interacting with Windows APIs, that most existing EDR (Endpoint Detection and Response) systems effectively monitor. That’s where Mockingjay becomes important as it allows evading such EDRs. That’s because Mockingjay doesn’t rely on Windows APIs; but instead uses legitimate DLLs RWX (read, write, execute) sections.

Describing Mockingjay, the post reads,

Our unique approach, which involves leveraging a vulnerable DLL and copying code to the appropriate section, allowed us to inject code without memory allocation, permission setting, or even starting a thread in the targeted process.

Briefly, the researchers demonstrated their attack strategy via the vulnerable DLL msys-2.0.dll inside Visual Studio 2022 Community. The team searched for this DLL and found it possessed the default RWX section they could exploit. They then loaded this DLL into the memory space of their custom apps to load and execute the injected code.

The attack happened entirely without Windows API use, demonstrating the efficiency of bypassing EDRs. Moreover, it didn’t require memory allocation, permission settings, or creating threads for code execution.

The researchers have shared the details about Mockingjay in their post, whereas the following video demonstrates the technique.

Suggested Remediation

Since Mockingjay indicates the inefficiency of existing endpoint protection measures, the researchers advise the organizations to implement dynamic analysis for analyzing runtime behaviors, identify anomalous activities, employ signature-based detection for known threats, deploy reputation-based filtering to flag suspicious activities, and ensure robust memory protection.

Let us know your thoughts in the comments.


[ad_2]
Source link

Google Pixel 8 Pro Protoype leaks

0
[ad_1]

Here’s our first look at a prototype of the upcoming Google Pixel 8 Pro. And it comes with very few surprises, actually.

The biggest change we can see here is that Google is going with a two-tone backside again. With the top, above the camera bar, looking darker than the bottom part. Of course, that could also just be due to the lighting in the room where this picture was taken.

The other big change we’re seeing here is the camera bar. It looks like there’s now one cut out for the triple-camera setup. Instead of an oval for the ultrawide and wide sensors, and another cutout for the telephoto lens. It also doesn’t look like it’s quite as curved as the Pixel 7 Pro.

On the front, there’s not a whole lot that this shows us. However, it does show that this is a flat display, instead of a curved one, so that’s good to see.

Pixel 8 Pro Prototype

Pixel 8 Pro codename has been rumored to be “husky”

Many of you might be wondering why we think this is the Pixel 8 Pro? Well, we have seen leaks and rumors that the codename for the Pixel 8 Pro is going to be “Husky”, and that’s what’re seeing on this model. It’s also quite obvious that this is a Pixel device here.

There’s a few other things that these images of “husky” show us, including the fact that it has 12GB of Samsung’s LPDDR5 RAM and 128GB of storage from SKHynix. That’s the same RAM and Storage as the Pixel 7 Pro, so it doesn’t look like there’s any upgrades in that department.

Google is set to announce the Pixel 8 series later this year, typically around the beginning of October. So we still have a couple of months before this device is made official. And that means plenty more leaks coming.


[ad_2]
Source link

Mastodon’s Android App Gets a New Look with Material You

0
[ad_1]

Over the weekend, Elon Musk tried yet again to kill Twitter, and sent a lot of people over to Mastodon. And that was shortly after Mastodon had rolled out a new update which brought about a Material You redesign. And we must say, it looks amazing.

Mastodon is a federated social media network, and was actually growing quite significantly in the days following Musk’s takeover of Twitter back in October. It’s since slowed down a bit, but it does have nearly 13 million users right now. So it’s not small like Bluesky, which has just a few hundred thousand people on-board right now. And actually had to halt sign ups over the weekend due to Twitter’s rate limiting. Which is insane, since it’s still invite only.

Material You for everyone

Now with Material You on Mastodon, it’s the best looking social media app on Android. It just looks so great in Material You. Since it’s going to take accents from your wallpaper, just like the rest of the Google apps and Settings already does. So you can really customize how Mastodon looks on your Android device.

You can switch between light and dark mode, and also have it follow the system-wide setting. Making it easier to switch between light and dark mode on your Android device.

The only bad thing here is that, there’s no enhancements for larger screens like the Pixel Fold and Pixel Tablet. As I noted on Twitter over the weekend, Mastodon does work better on the Pixel Fold’s main display, since it does use up the whole display, but it’s kind of not usable. And that’s because it’s just stretched out on a 6:5 aspect ratio display.

Hopefully some changes to the large display format will come soon for Mastodon. But as for now, they aren’t here. Instead, we get treated with Material You.


[ad_2]
Source link

Siemens Automation Device Flaw Let Attackers Execute Code

0
[ad_1]
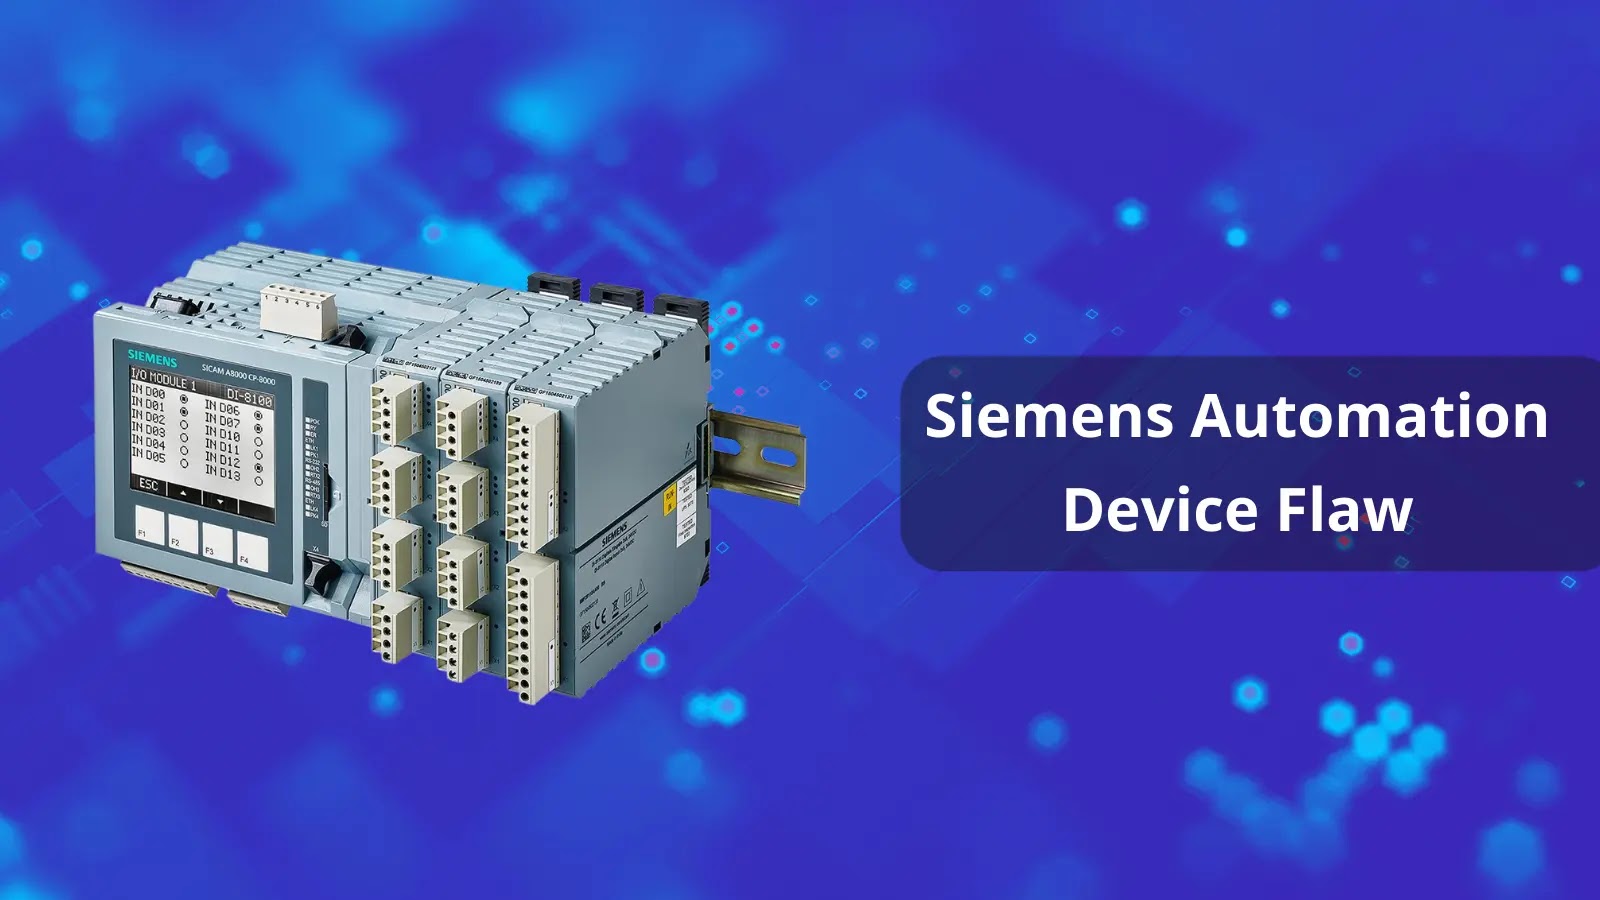
Siemens Automation Device Flaw

It has been discovered that the Siemens A8000 CP-8050 and CP-8031 PLCs contain a vulnerability that can be exploited for Remote Code Execution (RCE) without the need for authentication.

The Siemens SICAM A8000 is a versatile device that can be used for power distribution, transmission, and microgrids. It can also function as a communication gateway for a variety of networks and protocols.

Vulnerability Details

According to SEC Consult, which discovered the vulnerability, the Siemens A8000 CP-8050 and CP-8031 PLCs are affected.

The CPCI85 firmware of SICAM A8000 CP-8031 and CP-8050 is affected by multiple vulnerabilities, such as authenticated remote command injection, exposure of serial UART interface, and hard-coded credentials (for UART login).

CVE-2023-28489 – RCE

An attacker could exploit the flaw by sending a crafted HTTP request to the Siemens Toolbox II port 80/443; arbitrary commands can be executed without authentication.

This attack may lead to the full compromise of the device, and operation will get affected.

CVE-2023-33919 – Authenticated Command Injection

The flaw is due to a lack of input sanitation; any user with access to the SICAM WEB can execute arbitrary commands as a “root” user.

CVE-2023-33920 – Hard-coded Root Password

The “root” password hash remains the same for all the devices, so if the password is known, it could be used to log in via UART and SSH.

CVE-2023-33921 – Console Login via UART

To access the UART interface, physical access to the PCB is required. Once connected, the boot information will be displayed, followed by a login prompt.

Updates

An update to firmware CPCI85 V05 has been released by Siemens; the updates can be found here and here.

Workaround

The possible workaround is to block access to the A8000 CP-8050/CP8031 module or disable the Toolbox II communication on port 80/443 and limit physical access.

A complete report from SEC Consult can be found here.

“AI-based email security measures Protect your business From Email Threats!” – Request a Free Demo.


[ad_2]
Source link

HBO shows are finally coming to Netflix

0
[ad_1]

Netflix has been the temporary home of content from many companies. However, there’s one company that’s yet to place its shows on the streaming service, and that’s HBO. However, thanks to a report from Deadline (via Engadget), HBO is finally making some of its content available on Netflix in the US.

The home of most of HBO’s shows and movies can be found on MAX. The company originally showed all of its content on HBO MAX, but the company merged its content with Discovery+. The merged streaming service is MAX, and it gives you access to content from both of the streaming services. However, HBO had to shed a bunch of its HBO MAX content in the process.

If you’re interested in getting a subscription, the plan starts off at $9.99/month ($99.99/year) for the ad-supported tier. Going ad-free will cost you $15.99/month ($149.99/year),  and the top-tier plan costs $19.99/month ($199.99/year).

These HBO shows are coming to Netflix in the US

There’s a handful of shows crossing the pond to Netflix, but there’s only one show currently streaming. This is a gradual rollout, so the other shows will show up on Netflix in due time.

The show that’s on Netflix now is Insecure. This show was created by Issa Rae, and it’s highly acclaimed. This comedy-drama “looks at the friendship of two modern-day black women, as well as all of their uncomfortable experiences and racy tribulations.”, as per the description on HBO.com. All five seasons are currently on Netflix, so you can start binging now.

If you manage to burn your way through that show, don’t worry. There are other shows making their way over to Netflix. Band of Brothers, Six Feet Under, Ballers, and The Pacific are also making their way over to Netflix. These shows will arrive as time goes on. Also, remember, this refers to the US market. If you’re outside of the US, you’ll be able to watch True Blood.


[ad_2]
Source link

Netflix on Google TV and Android TV now supports frame rate matching

0
[ad_1]

Frame rate matching originally became available on Android TV sometime last year. Google TV devices also got this feature at about the same time its counterpart (Android TV) got it as well. However, up until this point, Netflix has not supported frame rate matching on their streaming platform.

Finally, users of Android and Google TV can now benefit from frame rate matching while streaming. In a recent YouTube video from FlatpanelsHD, this feature can be seen in action on the Netflix app. What this feature does is very simple but essential to ensure a great viewing experience for streamers.

Users of Netflix on Google TV and Android TV might have not had a reason to complain about their streaming experience. But with the Netflix app now supporting the frame rate matching feature, they’ll be a clear improvement to streaming. But what are the benefits of this feature, or what does it bring to the table for Netflix streamers?

Benefits of the frame rate matching feature now available for Netflix on Google TV and Android TV

The frame rate matching feature helps the TV match the content’s frame rate. This helps the TV sync with whatever the user is watching, hence improving the viewing experience. So as the contents frame rate keeps changing, that of the TV will sync with it and change accordingly.

Users can benefit from this feature while streaming movies on Netflix, but it doesn’t stop there. Even when users are just scrolling through the Netflix app, the frame rate matching feature is also active. This makes each animation, screen change, and scroll appear smoother.

From the FlatpanelsHD video on YouTube, it is clear how this feature now available on the Netflix app works. The YouTuber tracked the frame rate of their TV by pulling up the VRR information from the settings page. While navigating across the Netflix interface, it was clear that the frame rate stayed the same.

Also, while streaming movies, the frame rate at which the movie is displayed stays in sync with the TV. Users can now wave goodbye to any choppy viewing experience while they use Netflix on Google TV and Android TV. However, it is good to note that supporting this feature will not bring a mind-blowing change to the Netflix app.

Before Netflix supported it, the viewing experience for most users was pretty good. To get support for this feature on your Google TV or Android TV, you’d need to update the Netflix app. Possibly, other streaming services available on Google TV and Android TV would also support this feature.


[ad_2]
Source link

Proton Pass Password Manager Is More Of An Identity Manager

0
[ad_1]

After beta testing Proton Pass for some time, Proton has launched its password manager for all users. Describing its prominent features, the service explains how Proton Pass can even serve as a decent identity manager, offering password as well as email alias protection.

Proton Pass Password Manager Also Protects Users’ Identity

Earlier this year, Proton – the firm behind the popular freemium VPN ProtonVPN – announced launching its own password manager ‘Proton Pass.’ Initially, the tool remained confined to beta testing with an invite-only mode. But now, the firm has announced opening it up for Proton users.

As elaborated in a recent blog post, Proton users can now find Proton Pass available as a browser extension for all major browsers across desktops, Android, and iOS devices.

Proton Pass typically markets itself as a password manager, facilitating users to create strong passwords and safely store their credentials and other sensitive data. However, it has one unique feature that surpasses almost all existing password managers – identity protection.

Specifically, Proton Pass offers users to shield their email addresses when signing up on any website. It allows them to use a “hide-my-email” alias that masks the actual email address. Signing up with this alias saves users’ actual email addresses from possible data breaches a website may face. If such an incident happens, the breach would only expose the Proton Pass-created email alias, leaving the actual email address unaffected.

With this feature, Proton aims to save users from potential identity theft risks that may arise due to email address exposures.

Moreover, Proton Pass encrypts all fields, such as usernames and URLs, instead of other password managers that merely encrypt passwords. Such detailed encryption saves users’ information from intruders if they get access

The tool is currently free to all Proton users with premium subscriptions (Proton Unlimited, Business, Visionary, or Family plan). Whereas other Proton users can purchase a Proton Pass subscription for as low as $1/month until the end of July and $3.99/month afterward.

Let us know your thoughts in the comments.


[ad_2]
Source link

New Meduza Malware Targets Wallets, Passwords and Browsers on Windows

0
[ad_1]

Meduza authors are pushing the malware as a subscription-based service, offering plans for 1-month, 3-month, and lifetime access.

Crimeware-as-a-Service (CaaS) operations have become the latest fad in the world of cybercrime, and the Meduza Malware is the newest weapon added to its ever-increasing arsenal.

Uptycs Threat researchers report that Meduza Stealer is under active development and boasts comprehensive data-stealing capabilities, along with advanced detection evasion techniques.

How Was Meduza Stealer Discovered?

Uptycs researchers discovered the Meduza malware while monitoring Telegram channels and Dark Web forums. Initial examination revealed that the stealer was developed by someone with the username Meduza. According to the malware admin, Meduza does not perform ransomware operations and only functions as an information stealer.

Meduza Targets- Windows Systems and Browsers

The malware is designed to target Windows-based systems and organizations. Currently, it targets ten countries and pilfers a wide range of system and browser data, from login credentials to browsing history, bookmarks, etc.

It also targets data stored by 2FA, crypto wallets, and password managers. All types of extensions are vulnerable to Meduza. Check out the list of countries it can and cannot target:

  • Russia
  • Kazakhstan
  • Belarus
  • Georgia
  • Turkmenistan
  • Uzbekistan
  • Armenia
  • Kyrgyzstan
  • Moldova
  • Tajikistan

What Makes Meduza Unusual?

Researchers noted that it has a “crafty” operational design since, unlike other common malware, Meduza’s binary doesn’t use obfuscation techniques, making it virtually undetectable. The malware administrator has employed highly sophisticated marketing tactics to generate hype and trust for Meduza malware.

“In a calculated move to gain trust and confidence, they have initiated static and dynamic scans of the Meduza stealer file using some of the industry’s most reputable antivirus software. Screenshots were then shared, demonstrating that this potent malware could evade detection by these top-tier antivirus solutions,” researchers wrote in the report published on June 30th, 2023.

This malware is being fiercely marketed across different cybercrime forums and Telegram channels. Most antivirus software cannot detect its binary dynamically and statically, making the situation much more problematic for security researchers. The pricing model for Meduza is the real game-changer.

The admin offers numerous subscription packages, such as 1-month, 3-month, and lifetime access plans, at competitive prices ($199 per month, $399 for a 3-month subscription, and $1,199 for a lifetime license).

New Meduza Malware Targets Wallets, Passwords and Browsers on Windows
The Meduza malware is being advertised on the infamous Russian cybercrime and hacker forum XSS.IS (Left) – Meduza author boasting about the malware’s AV-evading capabilities. (Images: Hackread.com)

Moreover, the stolen data is available on a user-friendly web panel. Subscribers can create customized binaries and access, download, and delete sensitive data, including IP addresses, geographical data, stored cookies, wallets, passwords, and OS build names directly from the panel.

Meduza Data Stealing Capabilities

After infecting the machine, the malware scans for geolocation data against a predefined list of excluded countries and aborts operations if a match is found. Meduza malware connects to its operator’s C2 server if it doesn’t match. It starts stealing data only after the connection is established. It steals data from various Windows APIs, including GetUserName, GetComputerName, GetCurrentHWProfile, and EnumDisplayDevices.

It also collects system build CPU computer details, execute path, geolocation, OS, RAM, hardware IDs, GPU, TimeZone, screenshot resolution, username, etc. It also collects browser info, miner’s registry info, password manager info, and installed games details, probably to gain extensive financial and personal data.

Meduza comes with a predefined browser list and checks the User Data folder to get browser-related data such as cookies, history, web data, login data for accounts, and local state. It also steals Telegram Desktop app data from these Windows Registry paths:

HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\{53F49750-6209-4FBF-9CA8-7A333C87D1ED}_is1

HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\{C4A4AE8F-B9F7-4CC7-8A6C-BF7EEE87ACA5}_is1

What’s worse, Meduza malware is also capable of collecting data from 19 password managers, stealing clients, Discord, 95 web browsers, and 76 cryptocurrency wallet extensions.

To stay protected, you must keep the OS, browsers, and installed applications updated so that vulnerabilities are time patched and use stronger passwords.

  1. Legion SMS Hijacking Malware Sold on Telegram
  2. 100k Hacked ChatGPT Accounts Sold on Dark Web
  3. Hackers Leak i2VPN Admin Credentials on Telegram
  4. Hackers Advertising New Info-Stealer Malware on Dark Web

[ad_2]
Source link

Nothing OS 1.5.5 will expand your available RAM and more

0
[ad_1]

Nothing is still developing an identity for Nothing OS, and we’re expecting some notable changes coming with Nothing OS 2.0. However, it doesn’t mean that the company isn’t still working on the current version. According to a report from Gizmochina, Nothing is releasing Nothing OS 1.5.5. This version is going to bring some useful improvements that Nothing fans will enjoy.

We’re all waiting for the Nothing Phone (2). This phone is going to get its official announcement on July 11th. That’s not far away, so Nothing fans will be able to sink their teeth into this phone before too long. We expect it to have a similar design to the first-generation device. However, the most notable change will be the different Glyph interface.

Nothing OS 1.5.5 brings some welcomed improvements

Nothing OS is set to get a welcomed update that will bring some nice features for those sporting the Nothing Phone (1). Not only that, but the update will also bring your run-of-the-mill stability fixes.

Starting off with the features, this update will improve the accuracy of the face unlock feature. The changelog mentions that the update will improve its performance in darker environments. That’s a welcomed change, as it gets frustrating having to switch to different unlock methods when one fails.

This next change will help improve the battery life. It will reduce the Bluetooth power consumption when the device is in standby mode at night. There’s no use in having the Bluetooth function using battery power when you’re not using the functionality.

Perhaps the most notable change is the RAM expansion. The changelog states that you can increase the number of apps open in the background by 10%. While that number will vary depending on how much RAM each app uses, it’s still a welcomed change.

This most likely expands the RAM by using some of your storage as RAM. This is a common practice with phones nowadays, especially less expensive devices. With this, a phone can launch with a decent 8GB of  RAM and expand it to 12GB or even 16GB using some of the storage.

Bug fixes

As for the minor changes, the update fixes a handful. The update fixes the issue where adaptive brightness randomly turns off. Other than that, the update fixes the issue preventing the camera from taking pictures and the various problems related to face unlock.


[ad_2]
Source link