AT&T has a ChatGPT-based AI tool to help employees

0
[ad_1]

AI technology is a growing entity, and it’s rooting its way into more industries. AT&T, a major US phone carrier, just announced that it developed a new AI tool to help out its employees. According to a blog post from the company (via Insider), it’s called Ask AT&T, and it’s meant to help out its employees in several ways.

This AT&T AI tool was developed with Microsoft

It should be no shock that big companies are jumping on the AI train. The thinking behind this is to increase productivity. This seems to be the thought behind Ask AT&T. This is a generative AI Tool that the employees can use to help augment their work.

AT&T collaborated with Microsoft in order to develop this tool. As you may know, Microsoft has been a huge investor in OpenAI, and it’s pushing the technology into more of its services. So, working with Microsoft seems to be a good call.

As for what the chatbot will do, there won’t really be a customer-facing change. Basically, don’t expect to speak to an AI chatbot when you’re trying to get customer service. Instead, it’s more of a way to help people who are on the inside.

AT&T mentioned developers as an example. The rise in generative AI spells trouble for developers because it gives anyone the ability to generate code based on text prompts. AT&T mentioned this, but it said that its tool will help and assist its internal developers with their coding.

Another example has to do with customer documentation. One thing about AI is that it’s really good at processing and presenting information for you to absorb. This is one thing that Google wants to do in the medical field.

Well, the tool could be used to translate customer documentation. This may mean that it will allow people to pull up specific information about customers without needing to look up their entire documents.

There are plenty of applications for this chatbot, so it might be a major step forward for the company. Let’s just hope that this doesn’t lead to any massive layoffs from the company. This is one of the main things that people worry about in this new AI-driven era.


[ad_2]
Source link

Zoom is coming to Google TV, but there’s a big catch

0
[ad_1]

One of the biggest video chat apps, Zoom, is finally coming to Google TV. This should make a lot of people who own TVs powered by Android TV, but there’s a major caveat that comes with that statement. The big catch is that the Zoom for TV app will only be available on Sony Bravia TVs, at least initially.The Japanese giant announced this week that its Bravia TVs, compatible with Bravia Cam, will be the first to support the Zoom for TV app on Google Play Store. The new app will allow Bravia TV users to communicate through a much bigger screen with the Bravia Cam.

Besides video communication and screen sharing, Zoom for TV app will also allow users to take advantage of various collaboration tools. To start zooming, Bravia TV users must first attach the Bravia Cam to the TV, install the Zoom app, and then simply launch the app with the TV’s remote.

Thanks to the Bravia Cam, users will benefit from advanced features like Ambient Optimization Pro, which recognizes your position in the room and how far you are from the TV in order to adjust sound and picture settings accordingly. Additionally, more advanced features like Gesture Control, Proximity Alert, and Auto Power Saving Mode are available for Bravia TV owners while using Zoom (and not only).

According to Sony, the Zoom for TV app will be available by early summer on select Bravia TVs compatible with Bravia Cam. If you own one of these TV and a Bravia Cam, then you should probably get the app in just a few weeks at most.


[ad_2]
Source link

Kali Linux Tutorial – Pentesting Toolkit for mitm, Spoofing, DOS, Sniffing

0
[ad_1]

Xerosploit is a penetration testing toolbox whose objective is to perform man-in-the-middle attacks.

It brings different modules that permit to acknowledge of proficient assault and furthermore permit to do DOS attacks and port filtering.

We can use this tool to perform DOS, and MITM attacks, also the tool has driftnet modules that capture images and also it will be used in performing Injection attacks.

It was Committed by LionSec1, it is a powerful and simple-to-use tool.

  • nmap
  • hping3
  • build-essential
  • ruby-dev
  • libpcap-dev
  • libgmp3-dev
  • tabulate
  • terminaltables
  • Port scanning
  • Network mapping
  • Dos attack
  • Html code injection
  • Javascript code injection
  • Download interception and replacement
  • Sniffing
  • DNS spoofing
  • Background audio reproduction
  • Images replacement
  • Drifnet
  • Webpage defacement and more.

Kali Linux Tutorial – Xerosploit

To clone Xerosploit git clone https://github.com/LionSec/xerosploit and to run installation sudo python install.py

Need to select your operating system and launch type Xerosploit.

Just need to type help to view all the commands.

First, we need to scan the network to map all the devices. Xero  scan

Then select the target IP address and type help.

You can select any Module to attack, let’s start with port scanner pscan.

Next, we go on try launching a Dos attack, for examining packets we have configured Wireshark in the recipient system.

Type back to go to the main menu and then dos >> run to perform the attack.

Now let’s try sniffing the images that your friend sees on his computer.

Once the attack is launched we can sniff down all the images that he is viewing on his computer on our screen.

We can do much more with this tool simply by using the move you can shake the browser contents and with Yplay you can make audio play in the background.


[ad_2]
Source link

Ransomware attackers email bemused students as leverage for a payout

0
[ad_1]

We take a look at one group’s creative tactics to ensure a payout from a compromised university.

The University of Manchester has fallen victim to a ransomware gang, who are currently applying an interesting twist to their attack. Blackmail and pressure are two ways to extract funds from potential victims. We see this in sextortion cases, as well as in social engineering. Here, the fraudsters are directly mailing affected students in an effort to exert more pressure on the University of Manchester to pay up.

The incident, first discovered on June 6th, involved the likely theft of data by an unauthorised party. Bleeping Computer says it was informed by sources that the attack was ransomware.

The University has not confirmed if ransomware was used specifically, or if the attackers were only interested in stealing data. At time of writing, its cyber incident update page still makes no mention of it:

During the week commencing 6 June, we found out that the University is the victim of a cyber incident. It has been confirmed that some of our systems have been accessed by an unauthorised party and data has likely been copied.

Our in-house experts and external support are working around-the-clock to resolve this incident, and to understand what data has been accessed.

While there are several sets of detailed instruction and information available to students in need of guidance, the threat of data leakage has been hanging over the incident since day one. Sadly, we seem to be at that point now and the University is not playing ball with the attacker’s demands.

As a result, emails like the below are being sent to students:

We have stolen 7TB of data, including confidential personal information from students and staff, research data, medical data, police reports, drug test results, databases, HR documents, finance documents, and more. The administration is fully aware of the situation had had been in discussion with us for over a week. They, however, value money about the privacy and security of their students and employees. They do not care about you or that ALL of your personal  information and research work will soon be sold/or made public!

The mail then goes on to list several professors, as well as stating that this is the last warning people from the University will receive.

The aim here is to cause a mass panic of angry students demanding that the University pays up. It’s certainly a bold strategy. It’s also very likely to fail. However, ransom success is probably not the aim of the game here. This feels much more like a scorched earth approach.

You won’t pay up? Fine. We’ll cause some chaos on your campus instead.

I have to say, I don’t think this approach will work either despite the (understandably) aggrieved tweets from some students.

As Bleeping Computer notes, no group has claimed responsibility for this attack yet. If the threats are genuine, you should expect to see the data dump uploaded to a site with a countdown timer at some point. Then we’ll know for sure who is behind it.

How to avoid ransomware

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; disable or harden remote access like RDP and VPNs; use endpoint security software that can detect exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like Malwarebytes EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.

Malwarebytes EDR and MDR removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW

[ad_2]
Source link

This is how much the Nothing Phone (2) could cost in Europe

0
[ad_1]

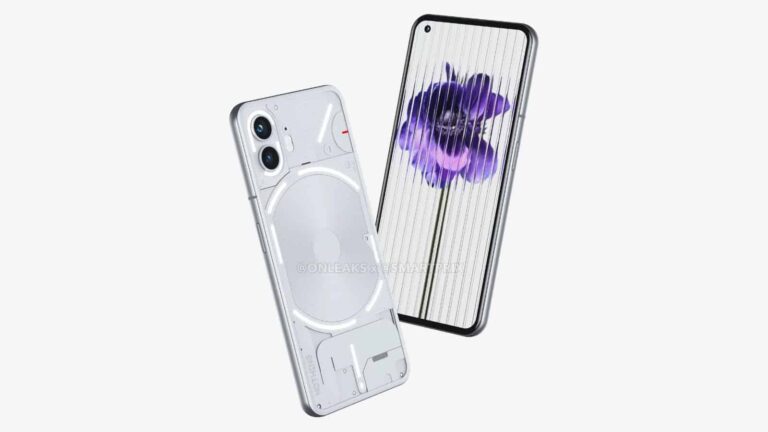
The Nothing Phone (2) is going to be one of the most exciting phones of the year. It will be the second generation of devices from OnePlus co-founder Carl Pei. While we don’t know how much the Nothing Phone (2) will cost, we may know how much it will cost in Europe.

There are several factors as to why we don’t know what to expect for the price. For starters, prices for tech, in general, are going up. So, there’s a chance that we may see a price increase because of that.

Another main reason is that nothing has decided to use a more powerful processor. Last year, the company used a mid-range processor to power this phone. However, this year, nothing is going to use the Snapdragon 8+ Gen 1 processor. This could possibly jack the price of the phone up a bit.

This is how much the Nothing Phone (2) might cost in Europe

Since we are talking about a leak, you will want to take this information a grain of salt. This information could change, or it could possibly be completely false. According to Phone Arena, the European prices were just leaked. If these prices are true, then we will see a notable price increase between the Nothing Phone (1 )and the Nothing Phone (2).

For starters, we are expecting two different variants of the phone. One may have 512GB of storage the other one will have 256GB of storage. We’re not sure if there will be any other differences between the two variants.

The cheaper model is expected to come in at €729 (around $796). That’s a hefty price jump from the first iteration. This definitely puts this in the flagship price range. It’s not quite scraping $1,000, but it puts it in close competition with the likes of the base model Galaxy s23.

The more expensive version is expected to cost €849 (about $930). These are very large numbers for the Nothing Phone series. We were used to seeing a more mid-range phone with a radical design. However, since these phones are using some serious power, they’re definitely going to cost some serious coin. Also, 512GB is a lot of storage.

At this point, we’re still waiting on more information on this phone, so any of the information could change. Just keep your fingers crossed. We expect the NothinPhone (2) to launch on July 11th.


[ad_2]
Source link

Apple seeds iOS 17 and iPad OS 17 Beta 2

0
[ad_1]

After launching iOS and iPad OS 16.5.1 earlier today, we thought the updates were over for the day. Nope. Apple just released the second beta for iOS 17 and iPad OS 17. Which is honestly the update that most people were looking for.

The update is fairly large, coming in at around 1.46GB in size. But that’s expected with a beta update. As there’s a lot of things changing here, and potentially new features being added.

Additionally, this new beta has a new update screen too. Now, at the bottom of the screen, you’ll see a blue “Update Now” button, as well as an “Update Tonight” button below it. So you can choose to have it update tonight while it’s charging, or to do it right away.

What’s new in iOS 17

Despite iOS 17 being rumored as a pretty small update, and one that is focusing mostly on bug fixes, there are quite a few quality of life improvements here. That includes new call screens for when you call people. This also includes a pretty large revamp for the iMessage app. Which now gives you an app drawer for all of your iMessage apps. Among a few other things.

Now with Beta 2, Apple is not releasing any major changelog here. Which is not a surprise, since this is a beta.

However, many are hoping that Apple has improved battery life and fixed a few bugs like the keyboard. Battery life has been pretty horrendous on iOS 17 Beta 1, where many of us are charging twice a day now. And the keyboard is probably the worse bug on iOS 17 right now. Basically, it will disappear when you need it, or stick around when you don’t. It also becomes transparent (sort of) over spotlight search results. Making it pretty tough to read.

Obviously, this is a beta, so things are going to change. But hopefully this second beta is a bit better. The Public Beta will be launching next month.


[ad_2]
Source link

Samsung brings its AI image editor app to more premium Galaxy phones

0
[ad_1]

Initially launched on the Galaxy S22 series last year, and the Galaxy S23 series in 2023, the Galaxy Enhance-X app is now available for a bunch of additional Galaxy premium smartphones, Samsung announced. Along with the announcement, Samsung confirmed its powerful AI image editor app is now out of beta.Officially launched on June 20, the Galaxy Enhance-X app is available for a range of premium Galaxy smartphones, including the Galaxy S23 series, S22 series, S21 series, Note20 series, Z Fold4, Z Flip4, Z Flip3, Z Fold2, Z Flip 5G and Z Flip LTE devices powered by One UI 5.1 or above.

In addition to these premium smartphones, Samsung announced that support for Galaxy Enhance-X on Galaxy A series, Galaxy M series and Galaxy tablets will be available at a later date. However, the company didn’t say if all the features that owners of Galaxy premium users benefit from will also be available to those who own non-premium phones.

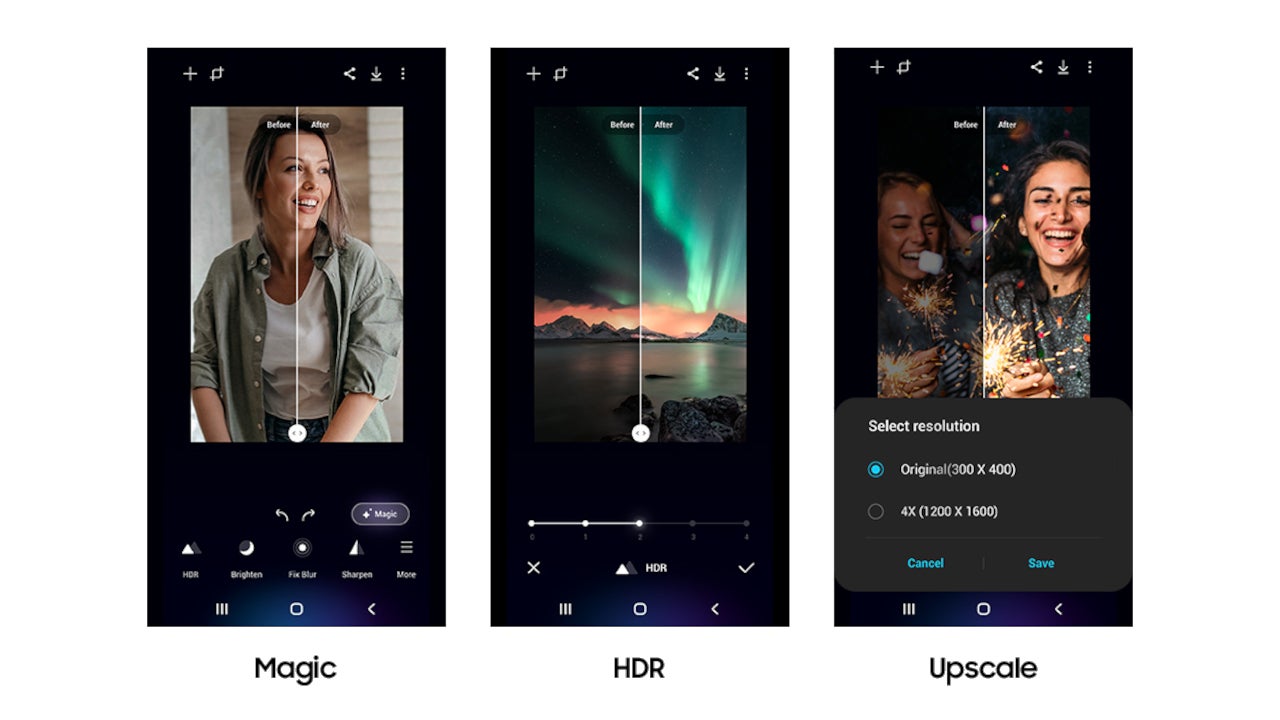
If you haven’t used Samsung’s Galaxy Enhance-X app, it’s worth noting that this app promises to automatically refine any visual noise, blur and low details, thus improving the image quality. What makes the app extremely easy to use is that all this is done with a single tap.

That’s not to say that the AI image editor app doesn’t have a wide range of tools that allows users to customize their images. If you want, you can use different levels of HDR intensity, take advantage of the Upscale tool to boost the resolution of images under 1MP by up to four times, as well as remove shadows from certain areas in a picture.

The Galaxy Enhance-X editing functions include a bunch of other features such as Brighten, Fix Blur, Sharpen, Remove Reflection and Fix Lens Distortion. The app is available for download for free via the Galaxy Store.


[ad_2]
Source link

DDoS Attack Hits European Investment Bank

0
[ad_1]

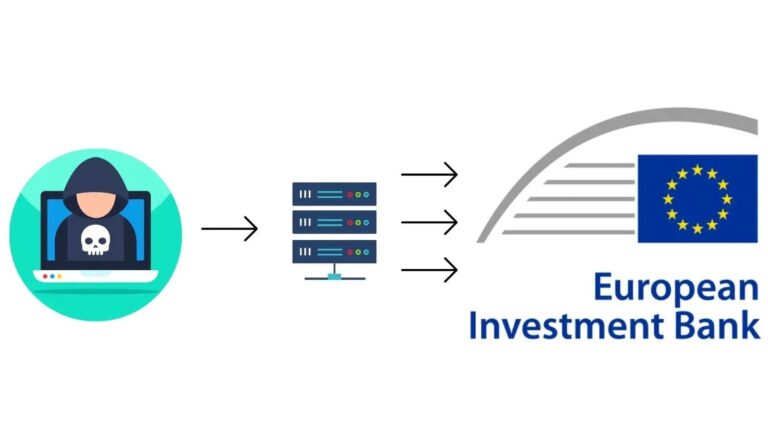
Recent reports indicate that a cyber attack hit the European Investment Bank (EIB) – DDoS Attack claimed to be from Russian threat actors.

Cybercrime activities have seen a large rise after the Russia-Ukraine LoCs heated up in 2022.

Several threat groups have targeted several countries and organizations in support of Ukraine and Russia.

These threat actors have previously threatened to target the Western financial system supporting Ukraine.

DDoS Attack on the EIB – Speculation

As per the current attack report, there has been a Distributed Denial of Service attack against the EIB, which was speculated to have been done by the Killnet gang.

EIB is owned by the European member states and is said to hold around €500 billion in funds.

The EIB spokesperson said, “While we have seen groups claiming responsibility for the incident, we will not speculate at this stage.” So as this was said, Anonymous Sudan, another Hacktivist group, has also posted on their Telegram channel, which reads, “ Anonymous Sudan | KILLNET Start a Devastating Campaign against the European Bank Sector.”

Killnet was the threat group responsible for taking down the NATO and US Air Force Strategic command earlier in February. 

Their Modus Operandi revolves around conducting a DDoS flood on the targeted servers flooding them with traffic that results in becoming unavailable for usage.

This threat group is in link with the Russian threat actors and has support from the country’s authorities.

However, Critical Infrastructure was unaffected as the organizations kept their critical operational systems off the grid. 

Cybercrime groups have been taking advantage of the situation in Ukraine and conducting various activities under the “Support for Ukraine” hood.

The countries must look into their critical infrastructure and protect it at all costs by bringing criminals to justice.

Looking For an All-in-One Multi-OS Patch Management Platform – Try Patch Manager Plus


[ad_2]
Source link

FTC lawsuit claims Amazon duped people into signing up for Prime

0
[ad_1]

Amazon is facing a lawsuit from the FTC over alleged deceptive practices with its Prime membership service. According to the lawsuit, Amazon had tricked customers into signing up for Amazon Prime memberships, then made it hard to cancel those memberships.

Amazon “sabotaged” their attempts to cancel, the lawsuit states. Noting that the process was intentionally designed to steer customers away from cancelling. The signup process is at the heart of the matter. The FTC alleges that customers were unknowingly signing up for a recurring Prime subscription. As Amazon made it a challenge to buy things without Prime, while failing to inform them that the buy button they were clicking to complete the transaction was also an agreement to the membership.

Amazon Prime has a monthly cost of $14.99 a month, although you can sign up for an annual subscription that carries a price tag of $139 instead. This saves you about $40 a year. For those prices, customers often get free two-day shipping on many different products. In addition to freebies from services like Prime Gaming, and thousands of movies and shows to stream through Prime Video.

The FTC has been investigating Amazon over Prime since 2021

While the FTC has just now filed the lawsuit against Amazon, the regulatory agency has been investigating the company over the alleged deceptive practices since 2021. The lawsuit states.

It also alleges that Amazon has done everything possible to prevent changes that would make the cancellation process simpler for customers. In some cases Amazon slowed changes that would aid consumers in cancelling their Prime membership if the company wasn’t able to stave them off, the lawsuit says.

This week’s Amazon Prime lawsuit from the FTC is merely one of a handful of the company’s legal worries. An earlier report states that the US senate is planning to investigate the company over its warehouse safety practices. It’s also facing a lawsuit over jointly inflating iPhone prices alongside Apple.


[ad_2]
Source link

US Senate to investigate Amazon over warehouse safety practices

0
[ad_1]

It’s no secret that Amazon’s warehouse safety standards and employee working conditions have been a matter of concern for some time now. However, Amazon has now found itself in hot water, as the US Senate Health, Education, Labor and Pensions (HELP) Committee is investigating the company’s alleged warehouse safety practices.

The letter sent by Senate HELP Committee Chairman Bernie Sanders accuses Amazon of prioritizing profits above all else, resulting in unsafe working environments for warehouse staff and inadequate access to medical care. Additionally, the letter highlights Amazon’s knowledge of these working conditions and intentional disregard for them, reflecting a corporate culture that treats employees as expendable.

Furthermore, the letter references data from the Strategic Organizing Center (SOC), a coalition of North American labor unions, which characterizes Amazon’s safety record as exceptionally hazardous. This is because, in the past year alone, warehouse workers experienced nearly 39,000 injuries, with 95% of them being severe enough to require time off work or modified duties. Moreover, Amazon’s warehouses reported a serious injury rate of 6.6 injuries per 100 workers, more than double the rate reported in non-Amazon warehouses.

Amazon’s response

In response to Sanders’ letter, Steve Kelly, an Amazon spokesperson, stated, “Our critics can manipulate data to fit their narrative, but the truth is that we’ve made progress, as evident from our numbers. Since 2019, we have reduced our rate of recordable injuries across our global network by over 23%, and our Lost Time Incident Rate has decreased by 53%. These facts are easily verifiable by examining the data we report to OSHA.”

Despite the company’s response, Sanders has demanded that CEO Jassy provide more information on Amazon’s rates of injury and employee turnover, as well as data regarding the company’s on-site medical clinic called AMCARE, dating back to 2019. Additionally, he also seeks clarification on whether Amazon has conducted any internal or third-party investigations into the potential relationship between the pace of work in its warehouses and the prevalence or cost of injuries. Lastly, Amazon has until July 5 to respond to Sanders’ warehouse safety inquiries.


[ad_2]
Source link