OnePlus is not interested in making laptops

0
[ad_1]

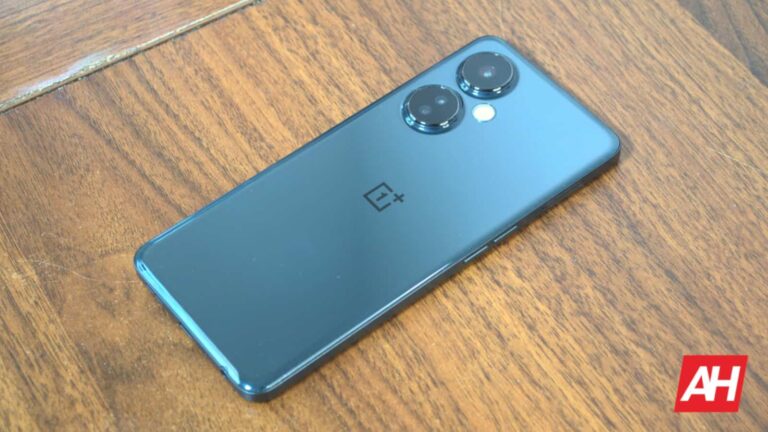
OnePlus is not interested in making laptops, at least not at the moment. Trusted Reviews had a chance to talk to Kinder Liu, the President and COO of OnePlus. During that interview, he shared some thoughts on tablets and laptops.

Don’t expect a budget tablet to arrive from the company, at least not anytime soon

Kinder Liu was asked whether the company plans to make more affordable tablets, following the launch of the OnePlus Pad. After all, the company is making ‘Nord’ phones, which are budget devices.

OnePlus doesn’t seem to be interested in such devices, though. Liu said: “focus remains on the higher end of the price segment, but if feedback suggests that a lower-spec and more affordable [sic], we are open to exploring it”.

Liu explained that the company only launched one tablet thus far. It has to be careful at this point, but he did leave the future wide open, of course.

OnePlus is currently not interested in making laptops

When asked about laptops, Liu explained that the company is not interested in making them at the moment. He said: “Our vision for technology puts smartphones and tablets as the primary devices for people to work and play, meaning that PCs and laptops are not something we’re exploring currently”.

He also added the following: “Technology is constantly evolving and that’s never going to change. What is relevant and ‘essential’ to consumers today may not be in 5, 10 or 20 years from now”.

Things are changing, that is true, especially when it comes to technology. So, who knows what could happen down the line. At the moment, though, there are no laptops in the pipeline, so don’t expect one to come from OnePlus.

OnePlus has at least one major device to launch this year, its first foldable

OnePlus does have at least one more exciting device in the pipeline this year. We’re talking about the company’s very first foldable smartphone, the OnePlus Fold aka OnePlus V Fold. That device is coming in Q3 this year, we still don’t know the date, though.


[ad_2]
Source link
Unreleased Music Stolen and Sold on Dark Web: Hacker Fined

0
[ad_1]

The dark web hacker previously pleaded guilty to multiple charges, including copyright offences, computer misuse, possession of criminal property, and converting criminal property.

In a significant development for intellectual property crime, a court has granted a confiscation order against a hacker who was previously jailed for stealing unreleased music owned by Ed Sheeran and Lil Uzi Vert and selling it on the dark web in exchange for cryptocurrency.

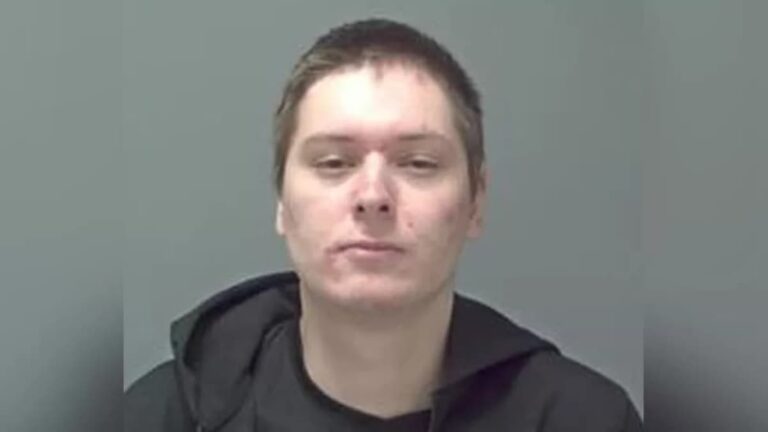
Adrian Kwiatkowski, a 23-year-old resident of Ipswich, was given three months to pay £101,503 by the Ipswich Crown Court on May 26, 2023. The order was secured by the Police Intellectual Property Crime Unit (PIPCU) at the City of London Police. The confiscated amount consists of £51,975 held in a bank account owned by Kwiatkowski and 2.64 BTC (Bitcoin), which is worth £49,528.

The assets were seized by PIPCU officers when they arrested Kwiatkowski in 2019. Failure to comply with the payment within the stipulated three months will result in an additional 18 months of imprisonment for Kwiatkowski.

Kwiatkowski had previously pleaded guilty to multiple charges, including copyright offences, computer misuse, possession of criminal property, and converting criminal property. He spent 18 months in prison after being sentenced at Ipswich Crown Court in October 2022. His actions had caused significant financial harm to several musicians and their production companies, while also depriving them of the ability to release their own work.

  1. 7 Online Activities That Can Get You Arrested
  2. Man arrested for uploading Deadpool on Facebook
  3. Online piracy hackers network Sparks Group bused
  4.  Europe’s largest illegal IPTV op dismantled by police
  5. Websites and Piracy Apps Seized in Operation 404.4

The investigation into Kwiatkowski’s activities was initiated by the Manhattan District Attorney’s Office in 2019. Management companies of several musicians had reported that an individual known as “Spirdark” had gained unauthorized access to cloud-based accounts and was selling the content saved in them.

According to the press release from the City of London Police, the investigation linked the email address used to set up Spirdark’s cryptocurrency account to Kwiatkowski, and the IP address used to hack one of the accounts was traced back to his home address. As a result, the investigation was referred to PIPCU.

Working in collaboration with the International Federation of the Phonographic Industry (IFPI), PIPCU officers discovered that Kwiatkowski had made £131,000 from selling the stolen music.

Unreleased Music Stolen and Sold on Dark Web: Hacker Fined
Adrian Kwiatkowski (City of London Police)

Upon his arrest in September 2019, PIPCU seized seven devices, including a hard drive containing 1,263 unreleased songs by 89 artists. During his police interview, Kwiatkowski confessed to hacking the musicians’ accounts and selling their songs online under the alias Spirdark.

Detective Constable Daryl Fryatt from PIPCU emphasized the complexity of Kwiatkowski’s scheme and the significant financial and creative harm caused to artists and their production companies.

Fryatt stated, “Our work doesn’t just stop at conviction, and this result means that Kwiatkowski will not be able to benefit any further from the money he earned through criminal activity.”

Melissa Morgia, the Director of Global Content Protection and Enforcement at the International Federation of the Phonographic Industry (IFPI), welcomed the recent developments in the case.

She acknowledged that such criminal activities jeopardize the work of artists and the efforts of the teams supporting the creation and release of music. Morgia expressed gratitude to both the Manhattan District Attorney’s Office and the City of London Police for their cooperation and support in the matter.


[ad_2]
Source link

Galaxy S23 series to get a “June super update” next week

0
[ad_1]

Samsung is supposed to roll out a major update to the Galaxy S23 series in June. While the update was expected to arrive early in the month, it didn’t. There was no telling when it would. The company reportedly needed more time to polish a few things. It appears the wait won’t be much longer now. We are hearing that the new Samsung flagships will get the promised update next week.

The new timeline doesn’t come directly from the company but from noted tipster Ice Universe. They have been frequently sharing information about the upcoming update for the Galaxy S23 series, even giving us an early look at one of the new camera features that this update will bring. The tipster recently took to Twitter to announce that the devices will get this month’s “super update” next week. They didn’t provide a precise release date, though.

Meanwhile, the tipster added that the update will arrive “one after another”. It’s unclear if that means multiple updates for the Galaxy S23 series over the next few weeks. The latest flagships are in line for plenty of goodies, including new features, functional improvements, and bug fixes.

We won’t be surprised if Samsung pushes multiple updates to the phones in the coming weeks. That said, since the source isn’t a native English speaker (originating from China), something could have been lost in translation.

The new Galaxy S23 update will bring plenty of goodies

The same source recently claimed that the June update improves the “overall fluency” of the Galaxy S23 phones. The UI should feel smoother post this update. An internal tester also told them that the “battery life is still great”.

The new Samsung flagships offer excellent battery life thanks to a Galaxy-exclusive Snapdragon 8 Gen 2 processor at the helm. While new updates sometimes cause massive battery drain, that seemingly won’t be the case with this Galaxy S23 update. Perhaps Samsung is taking time to get everything right before pushing it to users.

As for the new features that Samsung has lined up for the Galaxy S23 series, it’s adding a 2x zoom option for portrait shots. The company is also improving Zoom videos and low-light videos.

The devices should also get a fix for the HDR issue that causes a halo effect on photos. It remains to be seen if Samsung bundles everything in the same update next week or if it will push multiple updates. We will let you know when the rollout begins.


[ad_2]
Source link

Google launches new AI visual try-on experience for online shopping

0
[ad_1]

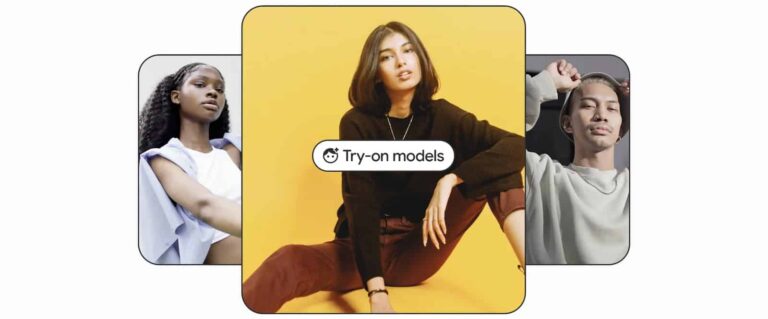
2023 has truly been the year where artificial intelligence makes its way into our daily lives. Companies like Google and Microsoft really push to expand its boundaries. Now, in line with these efforts, Google is introducing a new AI visual try-on experience. This would accurately visualize apparel on various body types and help users find the perfect item, thus solving one of the biggest problems for online shoppers.

Launched as an update to Google Shopping, the visual try-on experience uses Google’s internal diffusion models to enable shoppers to try on garments and see how they would appear on a diverse range of real-life models. Additionally, the model also encompasses a broad spectrum of skin tones, ethnicities, hair types, and body shapes from XXS to 4XL, therefore ensuring that users can always find the representation that closely aligns with their physique.

How did Google train the new model?

When it comes to training, Google states they used pairs of images featuring individuals wearing garments in distinct poses. For example, an image of someone wearing a shirt while standing sideways would be paired with another image of them standing forward, and so on. Additionally, the company also used random pairs of images of garments and people to make the model more robust and helpful.

Although the virtual try-on experience will initially focus on women’s tops from renowned brands like H&M, Anthropologie, Everlane, and Loft, Google has already announced plans to expand the feature to include men’s tops and other types of apparel shortly.

Reasoning behind the new feature

Google says their motivation to launch the visual try-out experience stemmed from a survey that highlighted the fact that over 42% of online shoppers didn’t feel represented by the images of models, and over 59% were disappointed with their online purchases due to differences in appearance.

“When you try on clothes in a store, you can immediately tell if they’re right for you. You should feel just as confident shopping for clothes online,” said Lilian Rincon, the senior director of consumer shopping products at Google.

In addition to the new visual try-on feature, Google is also debuting new filters that leverage the power of machine learning algorithms to enable users to refine their searches based on specific criteria, such as color, style, and patterns. Ultimately helping them to discover new products and make purchases.


[ad_2]
Source link

Hackers Set Up Fake GitHub Repos to Deliver Malware

0
[ad_1]

Recently, the cybersecurity researchers at VulnCheck identified a growing trend of hackers masquerading as cybersecurity researchers on social platforms like Twitter and GitHub. 

While hackers are doing so to spread fake proof-of-concept exploits for the vulnerabilities that are Zero-day in nature and capable of infecting both most used operating systems:-

Alleged experts affiliated with a fraudulent cybersecurity company, ‘ High Sierra Cyber Security,’ are actively spreading these malicious exploits.

Hackers’ primary focus is on cybersecurity researchers and companies actively participating or involved in vulnerability research.

The repositories appear legitimate, with the individuals responsible for them masquerading as actual security experts from renowned security companies like ‘Rapid7.’ 

Not only that, but they also utilize the pictures of these security professionals to further their deception, based on the report from VulnCheck.

To give their research and code repositories on platforms like GitHub a sense of legitimacy, the same personas also manage Twitter accounts.

Additionally, they exploit social media to lure unsuspecting victims into their traps.

Since May 2023, this malicious campaign has been ongoing and actively promoting zero-day vulnerabilities for the renowned and most used apps, which include:-

  • Chrome
  • Discord
  • Signal
  • WhatsApp
  • Microsoft Exchange

Across all instances, the malicious repositories contain a Python script named ‘poc.py,’ here this script serves as a means of downloading malware on the following systems:-

The script connects with a distinct website to retrieve a ZIP file, subsequently downloading it onto the targeted computer. 

The choice of the appropriate file is contingent upon the operating system currently in place. As here, both Linux and Windows  users get the same file but with different names that we have mentioned below:-

  • Linux users: ‘cveslinux.zip’
  • Windows users: ‘cveswindows.zip’

Here below we have mentioned the storage directories or locations of the malware:-

  • Windows: %Temp%
  • Linux: /home/<username>/.local/share

The Windows binary inside the ZIP file (‘cves_windows.exe’) raises concerns among more than 60% of antivirus engines on VirusTotal, indicating its potential risk.

Unlike its Windows counterpart, the Linux binary (‘cves_linux’) shows a greater level of stealthiness, managing to evade detection from most of the scanners, as three antivirus scanners managed to detect it.

The exact nature of the installed malware remains uncertain, but both executables install a TOR client. Besides this, the Windows edition is recognized as a trojan with the ability to steal passwords.

Malicious Repositories, Fake GitHub & Twitter Accounts

Here below, we have mentioned the malicious repositories that should be avoided:-

  • https://github.com/AKuzmanHSCS/Microsoft-Exchange-RCE
  • https://github.com/MHadzicHSCS/Chrome-0-day
  • https://github.com/GSandersonHSCS/discord-0-day-fix
  • https://github.com/BAdithyaHSCS/Exchange-0-Day
  • https://github.com/RShahHSCS/Discord-0-Day-Exploit
  • https://github.com/DLandonHSCS/Discord-RCE
  • https://github.com/SSankkarHSCS/Chromium-0-Day

Here below, we have mentioned all the fake Twitter accounts that should be avoided:-

  • https://twitter.com/AKuzmanHSCS
  • https://twitter.com/DLandonHSCS
  • https://twitter.com/GSandersonHSCS
  • https://twitter.com/MHadzicHSCS

Here below, we have mentioned all the fake GitHub accounts that should be avoided:-

  • https://github.com/AKuzmanHSCS
  • https://github.com/RShahHSCS
  • https://github.com/BAdithyaHSCS
  • https://github.com/DLandonHSCS
  • https://github.com/MHadzicHSCS
  • https://github.com/GSandersonHSCS
  • https://github.com/SSankkarHSCS

Looking For an All-in-One Multi-OS Patch Management Platform – Try Patch Manager Plus


[ad_2]
Source link

Pick up the OnePlus Nord N30 for $299 today!

0
[ad_1]

We’re following rumors about the upcoming OnePlus Nord 3, but the next best thing to this phone is the Nord N30. This phone was made official not too long ago, and now you can pick one up. The OnePlus Nord N30 just launched, according to DroidLife.

No longer the flagship killer company, OnePlus now has a thriving series of budget and mid-range phones that it offers to people at a low price. We followed rumors about this phone over the past couple of months, and we just got an idea of what it offers not too long ago.

The OnePlus Nord N30 just launched for $299

The Nord N30 sits in the middle ground between the Nord 3 and the Nord N300. By the way, Android Headlines has a review of the Nord N300, and you can read it here.

The Nord N30 is sporting a 6.72-inch LCD display with a 2400 x 1080 resolution. It runs at a smooth 120Hz refresh rate. Moving onto the internals, it uses the mid-range Snapdragon 695 5G SoC. That’s backed up by 8GB of RAM and 128GB of internal storage. That’s pretty standard for a mid-ranger.

This phone has a large 5,000mAh battery. That’s the same capacity that we find in most phones from the company. Fortunately, this phone does come with a charger in the box. It’s a 50W SUPERVOOC charger.

The Nord N30 has a triple-camera setup. This includes a large 108MP main camera. Just know that the phone will bin the images down to a lower resolution by default. The main camera is accompanied by a 2MP macro camera and a 2MP depth sensor. Up front, this phone has a 16MP selfie camera.

Even though the OnePlus Nord N30 has launched, you can still capitalize on the deal that was live during the pre-order stage. You’ll get a pair of $60 OnePlus Nord Buds for free. This is a great accessory to get your smartphone experience off on the right foot.


[ad_2]
Source link

Senators want to deny the Section 230 shield to AI companies

0
[ad_1]

Just as the European Union (EU) gears up to regulate artificial intelligence, a couple of US senators have come up with new bipartisan legislation that holds companies accountable for any illegal or harmful content generated by their AI tools. Introduced by Senators Josh Hawley (R-Missouri) and Richard Blumenthal (D-Connecticut), the No Section 230 Immunity for AI Act does what its name suggests. The proposed Senate bill denies Section 230 safeguards to AI creators.

Section 230 is the shield that protects social media platforms from being held accountable for the content that users post or create on their platforms. It gives companies like Facebook, Twitter, and YouTube immunity against misinformation or harmful content shared by their users. There have been several attempts to reform the legislation over the years. Hawley himself has been part of the group pushing for this reform in the past. However, all of those attempts stalled very quickly and Section 230 remained intact.

But, the burgeoning AI growth in recent months has now led to another push for reform. Generative AI tools such as ChatGPT, Google Bard, Dall-E, Google MusicLM, and others can generate various forms of content based on prompts provided by users. These tools can create everything from lengthy text and images to music and videos simply using short text prompts. The newly-introduced bill aims to hold the creators of these tools accountable for illegal content generated by users, like deepfake images or audio.

This Senate bill would strip Section 230 immunity from AI companies

“AI-generated deepfakes – lifelike false images and videos of real individuals – are exploding in popularity. Ordinary people can now suffer life-destroying consequences for saying things they never said or doing things they never would.

Companies complicit in this process should be held accountable in court,” senators Hawley and Blumenthal said (via). They want to strip Section 230 immunity from these companies and empower US citizens to sue them in court should someone use AI tools to ruin their reputation. Along with the person who misused the tool, of course.

This comes shortly after ChatGPT creator OpenAI’s CEO Sam Altman called for the government to act on AI. There are already talks over a pause on AI experimentation to give lawmakers time to come up with regulations.

Some industry experts see unregulated AI as dangerous as nuclear war. European lawmakers recently passed an AI Act and are aiming to turn it into law by the year. It remains to be seen if Hawley and Blumenthal succeed in realizing this proposed legislation. An equivalent House bill needs to pass a vote before it can turn into law.


[ad_2]
Source link

Microsoft Patch Tuesday June Arrived With 77 Vulnerability Fixes

0
[ad_1]

This week marked the arrival of monthly scheduled Microsoft Patch Tuesday updates for June 2023. The update bundle addresses some critical, and a large number of important severity vulnerabilities. Thus, users must ensure updating their systems at the earliest (if not updated automatically) to receive all bug fixes in time.

Microsoft June 2023 Patch Tuesday Overview

The June Patch Tuesday update bundle addressed six different critical severity vulnerabilities across different Microsoft components.

The most severe (CVE-2023-29363, CVE-2023-32014, and CVE-2023-32015) affected the Windows Pragmatic General Multicast (PGM). Each of these vulnerabilities received a CVSS score of 9.8.

Exploiting these flaws could allow a remote adversary to execute malicious codes by sending specially crafted files over the network. However, the exploitability required the Windows message queuing service to be enabled and running on the PGM server environment.

Another severe vulnerability, CVE-2023-29357 (CVSS 9.8), affected the Microsoft SharePoint Server. Exploiting the flaw could allow an attacker to gain admin privileges without prior authentication.

Besides, the other two critical-severity vulnerabilities patched with this update bundle include CVE-2023-24897 (CVSS 9.8) – a remote code execution flaw affecting the .NET, .NET Framework, and Visual Studio, and CVE-2023-32013 (CVSS 6.5) – a DoS vulnerability in the Windows Hyper-V.

Alongside these six critical vulnerabilities, Microsoft patched 68 other vulnerabilities with June Patch Tuesday. These include 9 denial of service vulnerabilities, 16 privilege escalation flaws, 5 information disclosure issues, 9 vulnerabilities leading to spoofing, 4 security feature bypass, and 22 remote code execution vulnerabilities across different components.

One noteworthy important severity vulnerability includes CVE-2023-24896 affecting Microsoft Dynamics 365 (on-premises). Microsoft reported it as a cross-site scripting flaw that allowed an authenticated attacker to steal login credentials and other sensitive information via maliciously crafted popups linked to web pages or emails.

Alongside these issues, this update bundle includes a low-severity bug fix for CVE-2023-29345 – a security feature bypass in Microsoft Edge.

While these vulnerabilities would automatically reach the eligible devices, users should still check for any updates manually for timely bug fixes. Also, it’s wise to enable automatic updates on all systems.

Let us know your thoughts in the comments.


[ad_2]
Source link

Finding tablet apps on the Play Store is now much easier

0
[ad_1]

The Google Play Store is mostly populated by smartphone apps, but it’s also the home to apps you can play on your tablet and Chromebook. The thing is, it can be hard to find apps that will run perfectly on your tablet. However, that’s going to change. Google just made it easier to find tablet apps on the Play Store.

Google has been working on making Android a much better place for tablets, so this new feature comes as no surprise. It’s been optimizing its apps to work better with tablets. This is in the hopes that other companies will follow suit and make their apps more compatible with Android tablets.

It’s now easier to find tablet apps on the Google Play Store

As stated before, if you see apps on the Google Play Store, they’re most likely optimized for your phone. That’s great, but with this new Android tablet revolution happening, people are more likely to be looking for tablet apps. Thus, help finding apps for tablets is appreciated.

According to 9To5Google (via Android Police) the Play Store now has a new tab dedicated to locating tablet apps. When you open up the Play Store, it will automatically open to the For You tab. You will see that up top. In order to find the tablet apps, tap on the Other Devices tab.

While in that tab, you will see chips for the different types of devices you can find apps for. You will see one for Watch, TV, and Car. There are two new chips: Chromebook and tablet. When you tap on one of these chips, you will see a feed of apps designed specifically for these devices.

When you tap on the chip, you will see the apps organized and categorized to make finding apps easier. Some of the categories include educational apps, stylus-friendly apps, creativity apps, streaming apps, etc. This is a great addition for anyone who has a tablet and wants to use it to its full potential


[ad_2]
Source link

Music publishers file a lawsuit against Twitter over copyright infringement

0
[ad_1]

It comes as no surprise ever since Elon Musk took over Twitter, the social media giant has been under a slew of controversies and lawsuits. Now, in a recent development, the National Music Publishers’ Association (NMPA), on behalf of 17 prominent music publishers, has filed a lawsuit against Twitter for hosting an abundance of unauthorized copies of musical compositions, thus violating the exclusive rights of publishers.

The lawsuit, filed in a federal court in Tennessee, is seeking over $250 million in damages, alleging that the platform infringed thousands of copyrighted works from major publishers like Universal Music Publishing Group, Sony Music Publishing, BMG Rights Management, The Royalty Network, Anthem Entertainment, and Concord.

Additionally, the lawsuit highlights that nearly all other major social media platforms, including Instagram and TikTok, have successfully established licensing deals with music publishers. And although Twitter is not as music-centric as TikTok, the plaintiffs take issue with users incorporating copyrighted music into Twitter videos.

However, it’s important to note the platform engaged in negotiations with music publishers to secure a licensing agreement prior to Musk’s acquisition, but discussions failed due to the platform’s reluctance to bear associated costs.

Highlighting Musk’s tweets

To make matters worse for Twitter, the lawsuit utilizes Elon Musk’s own tweets against him, referencing his public criticisms of copyright law and the Digital Millennium Copyright Act (DMCA). Furthermore, Musk’s recent decision to allow Blue subscribers to upload videos up to 3 hours long also indirectly contributes to the allegations of copyright infringement.

“Twitter stands alone as the largest social media platform that has completely refused to license the millions of songs on its service. Twitter knows full well that music is leaked, launched, and streamed by billions of people every day on its platform. No longer can it hide behind the DMCA and refuse to pay songwriters and music publishers,” said David Israelite, president of the National Music Publishers’ Association trade group.


[ad_2]
Source link