More Galaxy A series devices get Samsung’s May 2023 update

0
[ad_1]

Samsung‘s May 2023 update has reached a couple more Galaxy devices. The company is rolling out the latest security patch to the Galaxy A42 5G and Galaxy A20s. These two Galaxy A series models follow dozens of other devices, including Galaxy S series flagships, Galaxy Z series foldables, and more in receiving the May SMR (Security Maintenance Release).

The latest update for the Galaxy A42 5G is currently available in Europe. Samsung is widely rolling out the May SMR to the 2020 mid-range smartphone in the region. The new firmware build number for the device is A426BXXU5DWE1 (via). While the build number suggests more than just a security patch, Samsung’s official changelog doesn’t mention anything else. Maybe there are some system optimizations hidden here, but don’t expect any new features.

The Galaxy A42 5G may or may not receive the May SMR in other regions. That’s because the device is only eligible for biannual security updates (two updates in a year), so Samsung may skip this release in some markets. It could push one of the future security releases to the phone in other markets, such as the US. The handset will receive security patches at least until the end of 2024. November 2024, to be precise.

Interestingly, the Galaxy A42 5G is still running Android 12 in Europe and most parts of Asia where it was sold. It has already picked up Android 13 in most other regions, including the US, Samsung’s home country South Korea, and Hongkong. The handset debuted with Android 10 and isn’t eligible for Android 14. We will let you know if and when Android 13 rolls out to Galaxy A42 5G users in the remaining markets.

The Galaxy A20s is also getting Samsung’s May update

The Galaxy A20s is another Samsung phone that is now receiving the latest security patch. The Korean firm has begun the rollout in select Asian countries, namely India, Sri Lanka, Bangladesh, and Nepal. The device is picking up the firmware build number A207FXXS5CWE1 with this update. This device is also only eligible for biannual security updates, so there’s no guarantee that users in other regions will get the May SMR.

This update doesn’t bring anything notable to the Galaxy A42 5G and Galaxy A20s but fixes some series security issues. Samsung revealed earlier this month that the May SMR patches at least six critical flaws across the Galaxy lineup. It also patches more than 50 high-severity flaws and a few less severe ones. In total, this month’s security patch contains more than 70 fixes, around 20 of which are Galaxy-specific.


[ad_2]
Source link
Meta begins another round of mass layoffs, third in three months

0
[ad_1]

Meta has reportedly begun another round of mass layoffs. This is the third and final round of a massive job cut announced in mid-March. Facebook‘s parent company has laid off around 10,000 employees across these three rounds. It previously cut more than 11,000 jobs in November last year, taking the total layoffs to over 21,000.

According to Reuters, the latest round of mass layoffs at Meta mostly affect non-engineering roles. The report states that employees across marketing, site security, enterprise engineering, program management, content strategy, and corporate communications have lost their jobs this week. In a separate report, the publication said that this job cut affected around 490 jobs at the company’s international headquarters in Dublin, Ireland. That’s almost 20% of its Irish workforce.

Meta hasn’t officially announced these layoffs. But the company said in March that it will let go of more than 10,000 employees over the next few months and freeze hiring for around 5,000 open positions globally. Following some job cuts in March, it fired around 4,000 employees in April. A few thousand more are now being let go. As said earlier, this comes after an even bigger layoff in November last year when Meta laid off more than 11,000 employees.

The latest mass layoffs reduce Meta’s global workforce by 25% in six months

A total of 21,000 job cuts by Meta means that the company has reduced its global workforce by about 25% over the past six months or so. CEO Mark Zuckerberg said in November that the goal is to “become a leaner and more efficient company” amid a challenging economic situation. The social network behemoth is also shrinking its real estate footprint, “transitioning to desk sharing for people who already spend most of their time outside the office”.

It hasn’t scaled back investments in the metaverse and AR/VR technologies, though. Zuckerberg has said that Meta will prioritize growth for certain products over others in these challenging situations.

Of course, Meta isn’t the only tech biggie feeling the heat of this global economic downturn. Pretty much every other firm has announced massive job cuts over the past few months to reduce their operational costs. Amazon fired around 27,000 employees across two rounds of mass layoffs in January and March of this year.

Google parent Alphabet has cut 12,000 jobs while Microsoft has let go of around 10,000 employees. Disney (7,000), Dell (6,650), Twitter (more than 6,000), IBM (3,900), and PayPal (2,000) are a few other firms that have cut multi-thousand jobs in recent months. Samsung, Apple, and others have also announced small-scale layoffs.


[ad_2]
Source link

Samsung ASLR Bypass Flaw Is Actively Exploited – Warns CISA

0
[ad_1]

US CISA recently issued an alert, warning Samsung users about an ASLR bypass flaw being under attack. The attackers are reportedly exploiting this vulnerability to deploy spyware on target devices. Since Samsung has patched the flaw, users only need to ensure updating their devices with the latest system updates to receive the fix.

Samsung ASLR Bypass Vulnerability Under Active Attack

The tech giant Samsung patched a severe kernel vulnerability affecting its smartphones and related devices.

Identified as CVE-2023-21492, Samsung has described the flaw as a kernel pointers exposure in log file without sharing many details in its advisory.

Yet, while confirming a patch release with May 2023 updates, Samsung mentioned the issue as an ASLR bypass flaw that allowed local privileged attackers to access sensitive data. The tech giant also admitted having detected active exploitation of the flaw.

Nonetheless, it still marked the vulnerability as a moderate severity issue that affected the devices with Android versions 11, 12, and 13.

The US CISA has warned users of this vulnerability while listing it in its Known Exploited Vulnerabilities Catalog.

Although, neither Samsung nor CISA elaborated on the vulnerability, probably, given its exploitation in the wild. However, numerous entities have already detected and disclosed the abuse of this vulnerability in recent spyware campaigns.

For instance, Google’s Threat Analysis Group reported in March 2023 about numerous vulnerabilities actively exploited by the threat actors to deploy mercenary ransomware. From the several zero-days and n-days, Google TAG researchers also found the ASLR bypass under attack during these campaigns. The report also stated about informing the matter to Samsung officials.

Likewise, Amnesty International also published a detailed post about mercenary spyware campaigns actively targeting Android and iOS devices. Those campaigns also involved the exploitation of ASLR bypass for Samsung devices.

Given the patch has already been released, users need not worry about possible exploitation. But for that, they must promptly update their devices with the latest releases.

Let us know your thoughts in the comments.


[ad_2]
Source link

Google Play Games for PC beta is now available in 56 countries

0
[ad_1]

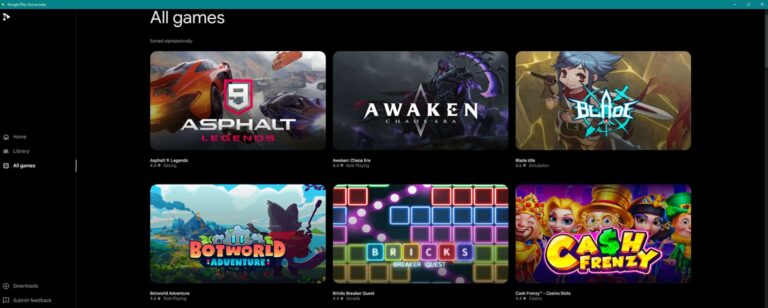
The Google Play Games for PC beta is rolling out to users in Europe this week. Expanding Google’s feature to Microsoft’s operating system for harmonious gaming fun in more places than ever.

Prior to the expansion, this feature was only available for users in 14 countries. None of those countries are in Europe. Access included the US, Canada, Mexico, and Brazil for North and South America. It also included multiple countries in Southeast Asia such as Indonesia, Malaysia, the Philippines, Singapore, Taiwan, and Thailand. The remaining countries included Hong Kong, South Korea, Japan, and Australia.

Now, the beta is available in a total of 56 countries when you factor in all the new countries who now have access.

Google Play Games for PC beta expands to Europe and New Zealand

The Play Games for PC beta is a great way for users to access their favorite Android games on their Windows PC. But it’s less exciting if you’re region isn’t included in where the feature can be enjoyed.

Now users in New Zealand as well as numerous countries in Europe can download the Google Play Games for PC beta and try things out for themselves. In addition to New Zealand, users in the UK, Austria, Belgium, France, Germany, Poland, Sweden, Norway and many others in Europe can now download the app as well. The full list of countries can be found here.

To access the beta you’ll still need to meet some minimum requirements. For starters you need to be on Windows 10 (v2004) or Windows 11. You’ll also need to have an SSD with at least 10GB of storage and at least 8GB of RAM. Google also suggests at least an Intel UHD Graphics 630 GPU or similar. Though it shouldn’t be too hard to meet that requirement these days. If you live in a supported region and want to check out the beta for yourself, you can grab it from the button below.

Google Play Games for PC beta


[ad_2]
Source link

Verizon is laying off 6,000 employees amidst restructuring efforts

0
[ad_1]

It’s no secret that in this post-pandemic economy, many companies have resorted to job cuts as a way to save operational costs and stay afloat. Now, just days after revamping its wireless data plans, Verizon is reportedly laying off over 6,000 of its customer service employees as part of its efforts to restructure and streamline its operations.

The company announced this decision in a meeting with all of its employees, and while Verizon has promised to provide further details on May 25th, affected employees will reportedly have two options: accepting a severance package based on their years of service, which offers two weeks of pay per year of tenure, or exploring potential new positions within Verizon that focus on customer experience, loyalty, and technology. However, it’s important to note that the second option does not guarantee a job, and employees will need to wait until June 23rd to learn about their future at Verizon.

Moving the customer service team overseas

After the layoffs, Verizon reportedly plans to outsource its customer service and after-sales assistance operations to foreign companies. The rationale behind this decision is that by outsourcing to countries where labor costs are significantly lower, Verizon can achieve greater cost-effectiveness and operational savings. And this is the reason why the company reduced domestic hiring for customer service positions.

This decision of laying off employees comes shortly after Verizon fell short of Wall Street expectations in its Q1 ’23 earnings, reporting a loss of 127,000 postpaid net new phone subscribers. Additionally, the company’s recent decision to replace premium services like Apple Music and the Disney Bundle with a $10 monthly charge for every service chosen may also impact customer satisfaction as subscribers adjust to paying for previously included services. However, in an effort to expand the reach of 5G technology and attract new users, Verizon has plans to introduce the C-band spectrum in more areas over the next few months.


[ad_2]
Source link

In time for WWDC, the Apple Developer app is updated to allow iPhone users to follow the action

0
[ad_1]
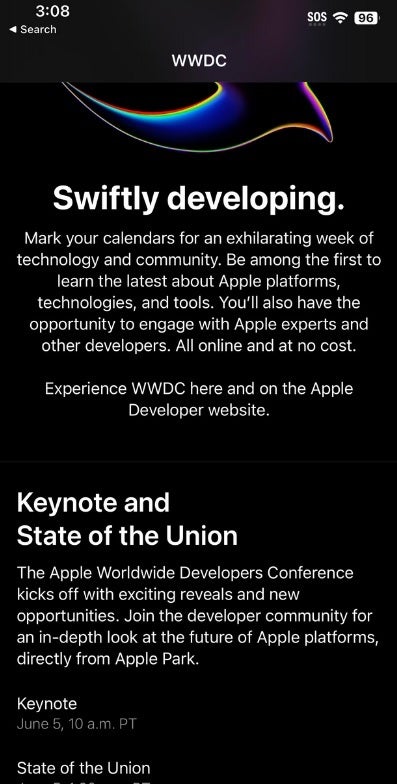
The Apple Developer app is available from the App Store (tap on this link) and Apple calls it “your source for developer stories, news, and educational information — and the best place to experience WWDC.” With the latter in mind, and with the knowledge that WWDC 2023 is just 11 days away (the event kicks off on June 5th), Apple has updated the app to make it easier for those with an iPhone to follow the event from home, work, or play.
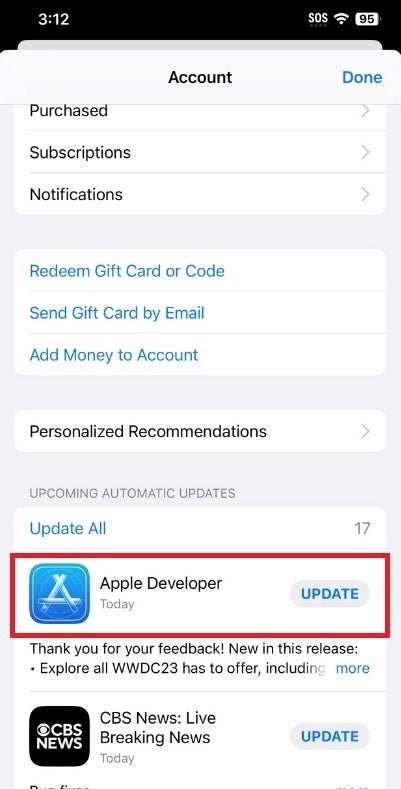
With the update, the Developer app will now support videos, sessions (via videos and transcripts), labs, forums, activities, and more. When you open the Apple Developer app, tap on the WWDC tab at the bottom of the display. In the release notes for the update Apple writes, “Explore all WWDC23 has to offer, including session videos, activities in Slack, 1-on-1 labs, and more.” It also says that it has fixed bugs and added other enhancements that it didn’t name.

To make sure that you have the latest version of the Apple Developer app, open the App Store and tap the profile picture or your initials in the upper right corner. Near the bottom of the display will be a list of apps that are ready to be updated; look for the Apple Developer app and tap on the “Update” pill. Or you can just tap the “Update All” link in blue.

Besides the Keynote, which will start streaming on Monday, June 5th, at 10 am PDT (1 pm EDT), the State of the Union will stream starting at 1:30 pm PDT. As for “Sessions,” new videos and transcripts will be posted daily from June 6th through June 9th.

The Keynote should include a preview of iOS 17 and of course, everyone is eager to see the introduction of Apple’s expensive mixed reality AR/VR headset. The device, rumored to come with a $3,000 price tag, takes an already available product to a brand-new level. In a way, you might compare it to Macworld on January 9th, 2007 when Steve Jobs introduced the iPhone. In other words, you might not want to miss the WWDC Keynote on June 5th.

[ad_2]
Source link

GuLoader Uses Google Drive to Download Payloads

0
[ad_1]
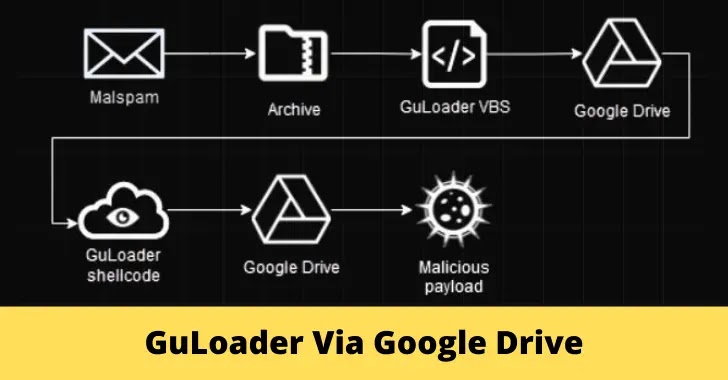
GuLoader via Google Drive

Antivirus products continuously advance to combat evolving threats, prompting malware developers to create new bypassing techniques like “packing” and “crypting,” GuLoader is a notable service employed by cybercriminals to avoid detection by antivirus software.

The cybersecurity researchers at Check Point affirmed that GuLoader employs a range of evasion techniques and stands out for its encrypted payload being uploaded to a remote server, enabling attackers to utilize a securely protected shellcode-based loader that downloads, decrypts, and executes the payload in memory without storing decrypted data on the hard drive.

Besides Google’s diligent attempts to impede the encrypted malicious payloads of GuLoader, most instances still witness GuLoader successfully retrieving payloads from Google Drive.

Malware Delivered using Google Drive

Conclusive evidence uncovered by researchers indicates that GuLoader is presently being employed as a distribution mechanism for the subsequent malware strains:-

  • Formbook
  • XLoader
  • Remcos
  • 404Keylogger
  • Lokibot
  • AgentTesla
  • NanoCore
  • NetWire

Earlier iterations of GuLoader were VB6 applications that utilized encrypted shellcode to handle essential tasks like loading the encrypted payload, decrypting it, and executing it from memory, while the current prevalent versions rely on:-

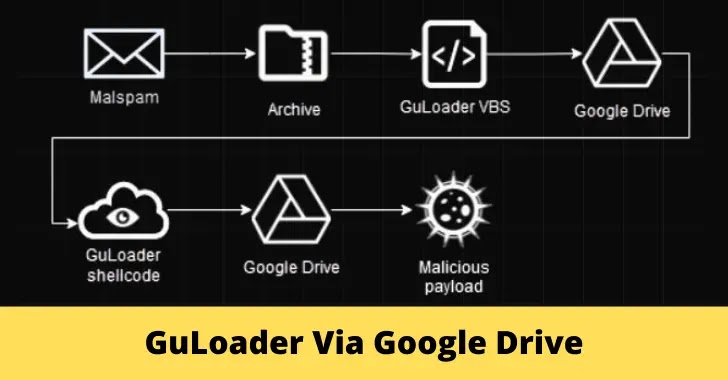
GuLoaded attack chain

Techniques Followed by GuLoader

Both the NSIS and VBS variants of GuLoader utilize the same version of shellcode, which incorporates numerous anti-analysis techniques similar to previous versions.

Here below, we have mentioned the techniques used:-

  • Sandbox evasion techniques
  • Anti-debugging techniques

While previous versions of GuLoader could be bypassed using a debugger during dynamic analysis, security analysts face significant challenges in the new version due to a technique that hampers both debugging and static analysis.

Since late 2022, GuLoader’s shellcode has incorporated a novel anti-analysis method involving generating numerous exceptions that disrupt the code’s regular execution flow, with control subsequently transferred to a dynamically calculated address through a vector exception handler.

The storage method for the payload decryption key mirrors that of the encrypted strings, yet the key remains unencrypted distinctively. Typically, the key length falls within the range of 800 to 900 bytes.

To evade automated analysis, GuLoader employs a deceptive tactic by using a different size, not the one stored with the key, which poses a challenge for decryption as only the initial 843 bytes of the payload can be decrypted accurately, leaving the remaining data fragmented.

From previous versions of GuLoader, the payload decryption algorithm remains unchanged, with the initial 64 bytes of the downloaded data skipped.

GuLoader obtains the final key by assuming that the first 2 bytes of the decrypted payload are “MZ” and calculates a 2-byte XOR key (rand_key), which is used to XOR the payload decryption key.

By employing encryption, omitting headers, and separating payloads from the loader, threat actors render their malicious payloads undetectable by antiviruses, enabling them to utilize Google Drive as a storage medium and circumvent its antivirus safeguards, with some download links to these payloads persisting for extended durations.

Shut Down Phishing Attacks with Device Posture Security – Download Free E-Book


[ad_2]
Source link

Wasserstein unveils a stand for the Pixel Tablet stand (you read that right)

0
[ad_1]

The Pixel Tablet is set to start shipping before too long, and we’re all excited to see how it will perform. While Google has its first-party accessories for the device, Wasserstein just unveiled a third-party add-on for the tablet, according to Cision. This one is an interesting one.

If you want to know more about the Pixel Tablet, then you can read here. We explain what you need to know about this tablet. Also, if you’re looking to put in your pre-order, you can click here. It’s a quick guide to make the process that much easier.

Wasserstein unveils the stand for the Pixel Tablet charging stand

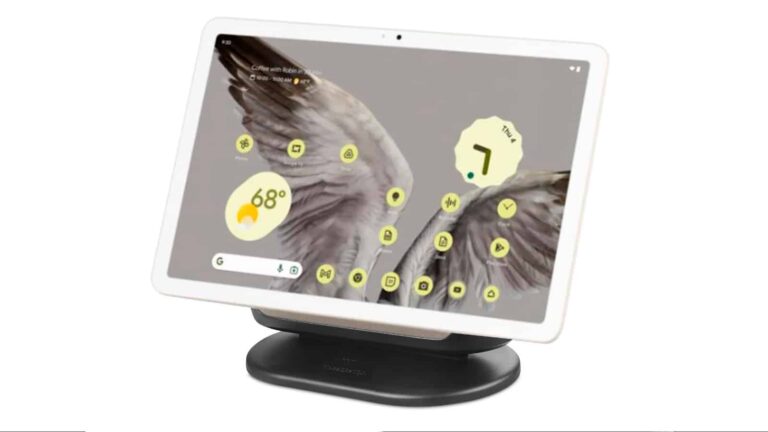
The main selling feature of the Pixel Tablet stand is the charging stand. You can attach your tablet to it so that it can enter docked mode. This will turn it into a smart display. Also, the stand will charge the tablet and act as a speaker.

The only issue is that you’re stuck with only one angle. It’s a comfortable angle, but it’s not for everybody. This is where Wasserstein comes in with its Pixel Tablet Speaker Stand. This is an add-on that will let you adjust the angle of your tablet.

Wasserstein Pixel Tablet Stand 2

It’s an external stand that you’ll place your Pixel Tablet and dock inside of. The Wasserstein stand will tilt up and down so that you can choose your preferred angle. It’s perfectly crafted to fit the charging dock, so you won’t need to worry about it falling out.

When your tablet is in the stand, just know that it will be rather tall. If you’re planning on getting this stand, then you’ll want to keep that in mind.

Not only can you tilt it, but you can also rotate it. This makes it much easier to move and adjust your Pixel Tablet. If you’re thinking about picking one up, it’s currently on sale for $24.99 ($15 off). Normally, this stand goes for $39.99. You can order it below.

Wasserstein Pixel Charger Stand


[ad_2]
Source link

Wild-looking PS VR2 game ‘Synapse’ gets official release date

0
[ad_1]

Back in February we got our first look at an upcoming PS VR2 title called Synapse, and now it has an official release date for those who are looking forward to playing.

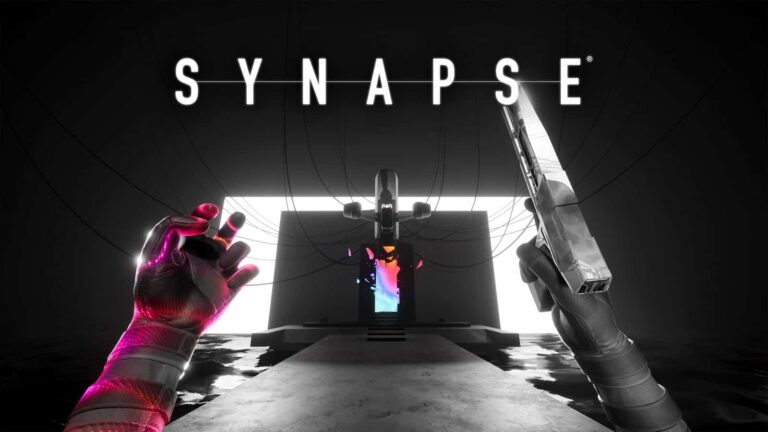
What’s even better is that the release date is probably closer than you think. If you aren’t familiar with Synapse, it’s a first-person shooter for PS VR2 that mixes gunplay with telekinetic powers for the main character to result in some really interesting and exciting-looking combat.

Naturally you’ll be able to grow your powers to make your attacks stronger. And you can expect a varied arsenal of weapons to dispatch enemies too. If you need a quick refresher on what the game looks like, you can check out the announcement trailer in the announcement post.

As for the release, you’ll be able to get your first taste of what the game has to offer on July 4.

nDreams reveals more than just the Synapse release date for PS VR2

Synapse for PS VR2 2

As part of the release date reveal during yesterday’s PlayStation Showcase, nDreams gave players a look at some new footage of the game. This includes introducing players to the main characters that they’ll be interacting with throughout the majority of their play time.

There’s also a brand-new trailer to check out if the announcement trailer didn’t have enough action for you. Although it does have plenty, the latest trailer is packed with even more carnage and crazy moments. Even crazier though is that a core part of the game is the player entering what seems like the main antagonist’s subconscious to find and retrieve intel on some dangerous new neurosynaptic technology.

Synapse is surely going to be a wild ride for PS VR2 owners when it arrives in just over a month. If you didn’t catch the showcase, you can watch the entire thing here, and you can view the new Synapse trailer below. You can also keep an eye on the availability to buy the game on the PlayStation Store. Right now it seems you can only wishlist it. But now that the release date was revealed, it shouldn’t be long before the game is purchasable.


[ad_2]
Source link

Google Introduces Mobile VRP For Its Android Apps

0
[ad_1]

Shortly after announcing major upgrades to the Android devices bug reward program, Google had now announced launching Mobile VRP for its Android apps. The new rewards program will specifically cover vulnerabilities affecting the security of Google’s Android applications and their users.

Google Mobile VRP For Apps Will Reward Up To $30K

The tech giant Google has launched a dedicated Mobile Vulnerability Rewards Program (VRP) for its Android apps. The program welcomes bug hunters and researchers to scan and analyze Google-developed and Google-maintained Android applications, and detect vulnerabilities.

As elaborated on the program rules’ page, Google Mobile VRP applies to its “Tier-1” mobile applications which include the following.

  • Google Play Services (com.google.android.gms)
  • AGSA (com.google.android.googlequicksearchbox)
  • Google Chrome (com.android.chrome)
  • Google Cloud (com.google.android.apps.cloudconsole)
  • Gmail (com.google.android.gm)
  • Chrome Remote Desktop (com.google.chromeremotedesktop)

Moreover, the program will also cover apps developed by the following developers.

  • Google LLC
  • Developed with Google
  • Research at Google
  • Red Hot Labs
  • Google Samples
  • Fitbit LLC
  • Nest Labs Inc.
  • Waymo LLC
  • Waze

Qualifying Vulnerabilities Under Mobile VRP

Regarding the type of vulnerabilities covered in this bug reward program, Google lists the following as qualifying vulnerabilities.

  • Arbitrary code execution (ACE)
  • Sensitive data exposure. Here, ‘sensitive’ data includes details leading to unauthorized access to users’ accounts (such as login credentials), users’ contact lists, photos, SMS logs, and other user-generated content, and any PII, PHI, or financial information. However, in this category, Google doesn’t classify location data, non-sensitive internal files, or any data exposure not directly caused by Google’s apps.
  • Intent redirections
  • Path traversal
  • Orphaned permissions
  • Vulnerabilities triggered due to unsafe use of pending intents

Again, security issues like hard-coded keys, trivially exploitable low-severity bugs, StrandHogg variants, and attacks due to device rooting do not qualify for Mobile VRP.

Regarding the rewards, Google shared a detailed breakdown of bounties for various Application Tiers (including Tier 2 and Tier 3). The highest rewards ($30,000) are reserved for remote arbitrary code execution flaws (requiring no user interaction) in Tier 1 apps. Whereas such ACEs in Tier 2 and Tier 3 apps will reward the researchers with $25,000 and $20,000, respectively.

More details about Mobile VRP are available on the Rules page, which interested researchers can visit to learn and leverage this new money-making opportunity.

This move arrived shortly after Google announced some major upgrades to its VRP for Android system and devices. With these updates, Google aimed at achieving better remediation of reported security issues.

Let us know your thoughts in the comments.


[ad_2]
Source link