Google brings app streaming to ChromeOS

0
[ad_1]

Companies are still working on better connecting your phone with your computer. Google just announced a new way to do this in a short blog post. According to the post, Google just introduced an app streaming feature for ChromeOS.

This feature is still in the beta testing stage, so it won’t be available to the general populace. You will need to be a ChromeOS beta tester in order to use it. Also, since it is in beta, you should expect some general bugginess and instability, as Google is still working on it.

Google is testing an app streaming feature for ChromeOS

The feature itself is pretty straightforward, but in order to use it, you have to have Phone Hub enabled. Also, your phone will need to be running Android 13 or later. The blog post points to Pixel phones no older than the Pixel 4a. Also, it points to the Xiaomi 12T, 12T Pro, 13, and 13 Pro. The compatibility will expand as the test progresses.

When you have this feature enabled, you’ll be able to interact with certain smartphone apps and functions right from your ChromeOS device. You won’t be able to completely control your device from your Chromebook. So, you won’t be running full apps, changing settings, or other things.

We’re not sure about the full extent of this feature just yet. It’s still in testing, and more functionality should arrive as time goes on. The blog post refers to you being able to check your rideshare status, update your shopping list, and reply to conversations.

Having limited functionality might work in this feature’s favor. This seems more like a feature to give you access to just a few of your most used smartphone features. If you’re working, then this will help you avoid having to stop and unlock your phone just to access your messages.

This could just be a way to avoid distractions. If you are on the beta version of ChromeOS, you can enable this feature now. Check out this help article if you need assistance enabling it.


[ad_2]
Source link

Google is integrating generative AI suggestions to Google Search

0
[ad_1]

Ever since Microsoft integrated ChatGPT into its Edge browser as the Bing AI chatbot, search engine giants like Google have been on their toes to develop a rival. At the Google annual I/O developer conference, Cathy Edwards, VP of engineering at Google, announced that the company would be integrating AI into its search engine, revolutionizing how users search for information online.

According to Google, the new AI Search will provide users with a summary of the pros and cons of any given topic, along with an AI-powered snapshot of key information to consider and links to further study on the topic. And if users tap on one of the suggested next steps, the new Search will take them to a new conversational mode where they can ask Google more about the topic they’re exploring, similar to the Bing AI chatbot.

For example, if a couple is looking for a vacation spot in Europe, the search engine will gather all the available information and provide a recommendation based on the advantages and disadvantages of each spot.

However, the new AI Search, which is not yet available to the public, will be accessible with a waitlist under a new experimental program called Search Labs. Users in the U.S. can join the waitlist today by tapping the Labs icon in the latest version of the Google app or Chrome desktop.

New AI Shopping Experience

Google will also offer a new AI shopping experience built on Google’s Shopping Graph, which will help users quickly connect with useful information online and make informed decisions when shopping for products. For example, if a user is searching for a new bicycle, the AI would give them a snapshot of noteworthy factors to consider and recommend bicycles based on their budget and preferences.

However, it is also worth noting that, like Microsoft’s Bing AI chatbot, the new AI Search will show ads in dedicated ad slots throughout the page. But, Google has ensured that these ads will be distinguishable from the organic search results.

Google search ai tools


[ad_2]
Source link

Sysco confirms data breach

0
[ad_1]

Food distribution company Sysco has confirmed that customer, business and employee data was stolen in a cyber attack it suffered earlier this year. 
The cyber attack is thought to have taken place on January 14, 2023 and was detected by Sysco on March 5.

According to BleepingComputer, Sysco said in an internal memo sent on May 3 that data from companies and suppliers located in the US and Canada as well as data from US employees may have been accessed during the cyber attack. The employee data accessed is believed to include name, social security number, account numbers and other personal information provided to Sysco for payroll purposes.

In data breach notices sent to those affected by the breach, Sysco said that the threat actor responsible for the cyber attack gained unauthorized access to its systems and “claimed to have acquired certain data”.

Sysco also disclosed the breach in a quarterly report filed with the US Securities and Exchange Commission on May 2, in which the company said the malicious actor “extracted certain company data, including data relating to operation of the business, customers, employees and personal data”.

An investigation into the breach is ongoing, with Sysco saying it has “begun the process of preparing to comply with its obligations with respect to the extracted data”. The food distribution company has also employed a cyber security firm to investigate the breach.

According to Sysco, its operations were not affected by the cyber attack and its networks are now secure as safeguarding measures to prevent further breaches. 


[ad_2]
Source link

New Discord username policy raises user privacy fears

0
[ad_1]

We take a look at the reaction to Discord’s proposed changes to how usernames work, and why many users aren’t happy with the upcoming alterations.

Discord, the Voice over IP (VoIP) and instant message communications tool, is changing how usernames function in a major way soon. Many users are not keen on this change at all.

What is going on over there, and why are so many people concerned about the upcoming alterations?

When Discord launched back in 2017, the developers didn’t want you to try and sign up only to be told “Username taken”. They wanted you to jump straight into the chatroom-based action. When people started wanting to talk to their friends located in other servers (essentially, another chat room) Discord introduced a friend system and a number system called “discriminators”.

This is just another way of saying “We put a four digit number at the end of your username”. If you wanted to be Steve, into the chat you’d go as Steve#3857. If another Steve signed up, they’d be Steve#3858. And so on. A drawback of this system is that if 9,999 Steves already exist, then we’re all out of Steves because this is the maximum number you can have of one particular username.

It remained like this for about 8 years, and now we’re at the point where everything is changing. Very soon, Discord will ask you to amend your username to something more specific. All of our Steves will fight to the death in order to become the one true Steve, shorn of numbers forever. If you miss out on landing the Steve handle, sorry: you’re probably going to be St3ve from now on.

This isn’t so bad, you may think. However, a lot of privacy related issues are bubbling up to the surface. Users of Discord quite enjoy the level of anonymity afforded by the numbers system. It’s a bit like having a giant online user directory, but one where the user is in full control of how that information leads back to them in the majority of situations.

With the numbers system in place, it’s as good as impossible for someone to track you down specifically inside of Discord. Where would you start? The answer, of course, is likely “From Steve#0001 all the way up to #9999″. Nobody is going to do this, and so users are afforded some degree of privacy as a result.

This is not to say using Discord keeps you 100% anonymous. Even so, someone usually has to tie a profile to something external and identifiable to run into trouble.

The new system means people have to make a choice. Secure a username that unambiguously ties to your online presence for as long as you use the service, or run the risk of impersonators grabbing your desired identifier.

Worse still, the way this is going to happen is that name availability will be done on a first come, first served basis with people who’ve been on the platform longer getting first choice. Lots of early adopters of the platform will no doubt have amassed many alternate accounts down the years. This not only gives them a distinct advantage in the “name yourself first” stakes, it also provides an opportunity for trolling or security threats. It would theoretically be straightforward to use an army of dormant accounts to “squat” usernames of famous people or business entities. From there, those accounts could be used for phishing or other scams. This isn’t a far-flung theory; you can read folks already raising this issue and thinking about the potential ramifications of Discord’s intended plan.

There are some additional wrinkles added to the new scheme. Users will be able to have a “non-unique display name” which is how your name will appear to other users. Users of social media will already be familiar with this approach. For example, your Twitter URL (here the equivalent of a Discord username) may be twitter(dot)com/Steve, but your display name might say Steven LotsOfNumbers.

The default for this display name when the changes kick in will be whatever your original Discord username happened to be. So, for a while, #Steve0001 will live on.

The sheer generic aspect of user accounts also helped relieve anxiety over phishing and compromise to some degree. Lost your account to a scammer? Assuming you haven’t spent a small fortune on premium features tied to your account, no big deal. Spin up a new one and #Steve0002 rides again.

Now that usernames will be very specific and tied to individuals, it’s not hard to imagine scammers increasing returns on stolen accounts. Streamers and other visible people in gaming circles lose their accounts all the time. What happens when Steven the Streamer, with three million YouTube subscribers, loses his account due to phishing?

Blackmail and potentially juicy returns for fraudsters, that’s what.

Discord has long been a home for entirely (and semi) anonymous folks to hang out in a stress free environment. It’s long since stopped being a hang out spot for gamers only. TV shows, films, products, and more may have a dedicated Discord space. I, myself, have used it for tech support from PC hardware suppliers.

In fact, it’s now so popular that it’s slowly tipping into the realm of unpopular where some user collectives are concerned. Old school forums, filled with search engine indexed solutions to obscure problems are being replaced by Discord, which cannot be indexed. Increasingly, more things are ending up in Discord which should be available elsewhere too. Video game mods, patch updates notes, and more are all drifting toward Discord. This is because it’s simple and easy to set up, and you don’t have to worry about maintaining a website or forum while chasing after security updates.

This tendency toward making information which would be better served existing outside of a chat room has been frustrating folks for a while now. Adding a username controversy on top of this may put some users off for good.

Tips for keeping your Discord account safe and private

If you’re a Discord user, here are some of the ways you can keep your account safe from scammers and other slices of fraud:

  • Beware Nitro offers. Nitro is a paid service which adds more features to Discord. “Free Nitro” messages in Discord channels from Bots, other users, and non Discord websites should be treated with caution. Check the official page for genuine offers.
  • Non-Discord theft: Scammers will target gamers with phishing links targeting gaming platforms such as Steam. As before, check official sites for word of special offers.
  • Don’t join the spam chain conga line: Bots are common in Discord channels, often there to help with admin tasks. Rogue bots will send direct messages and ask you to spam on its behalf, or invite you to a channel so it can send spam there. Don’t fall for it! 
  • Compromised server peril: If the admin is hijacked, any message sent in public or privately could be risky. Server admins should enable two-factor authentication on their accounts to minimise the risk.
  • Privacy settings: Current name policy changes aside, Discord offers several useful features including direct message filtering, explicit image filters, automatic spam filters, and granular control over who can add you as a friend.

Malwarebytes EDR and MDR remove all remnants of ransomware and prevent you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW

[ad_2]
Source link

Sony unveils Xperia 10 V with 6.1″ display, audio jack & more

0
[ad_1]

Sony announced two new smartphones during its press event today. We’ve already talked about the flagship Xperia 1 V, and are here to check out the Sony Xperia 10 V. This is Sony’s new mid-ranger, actually.

The Sony Xperia 10 V is a compelling mid-range phone in a compact body

If you don’t need the absolute best Sony has to offer, and want a more compact phone at the same time, well… this may be the device for you. The Xperia 10 V does resemble the Xperia 1 V from the design standpoint, to a degree, but its internals and size are different.

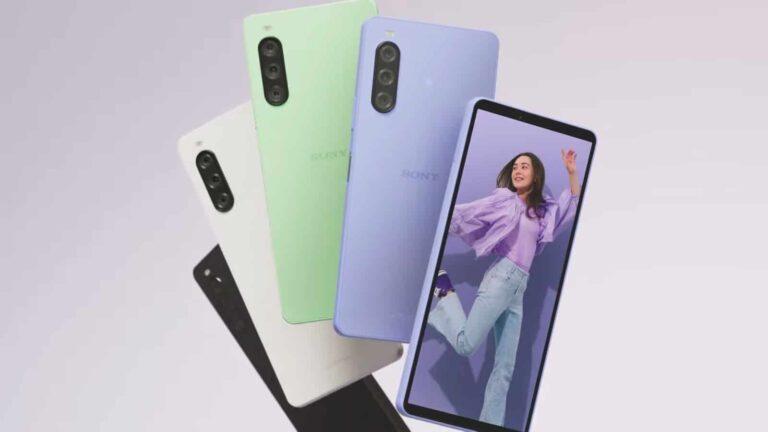
This phone has flattish sides, a flat display, and three cameras on the back. Those three cameras are vertically aligned, and inside a single camera island. Sony’s logo is included on the back, but it’s quite understated.

The device does not include a display camera hole, as Sony opted for thicker top and bottom bezels instead. A power/lock button on the device doubles as a fingerprint scanner, and this handset even included an audio jack. Sony also placed an audio jack on the Xperia 1 V.

A 6.1-inch display is included here, while 30W charging is also supported

Sony opted to include a 6.1-inch fullHD+ (2520 x 1080) OLED display on this device. We’re looking at a 21:9 aspect ratio here, while the Gorilla Glass Victus protects it. The Snapdragon 690 fuels the phone, and is paired with 8GB of LPDDR4X RAM and 128GB of UFS 2.1 flash storage. You can also expand that storage thanks to a microSD card (up to 1TB).

A 5,000mAh battery is also included here, and it supports 30W wired (USB PD) charging. Wireless charging is not supported. Android 13 comes pre-installed, while there are two nano SIM card slots here. Do note that you can opt to use the second SIM card slot for a SIM card, or a microSD card.

It has three cameras on the back, and the phone is water & dust resistant

A 48-megapixel main camera (f/1.8 aperture, 80-degree FoV, Hybrid OIS/EIS) is backed by an 8-megapixel ultrawide camera (120-degree FoV, f/2.2 aperture). An 8-megapixel telephoto camera (f/2.4 aperture, 10x hybrid zoom) also sits on the back. A single 8-megapixel camera (f/2.0 aperture, 1.12um pixel size, 78-degree FoV) is included on the front.

The Xperia 10 V is IP65/68 rated for water and dust resistance. Bluetooth 5.1 is supported here, while the device also offers 5G connectivity. Stereo recording is supported too, and stereo speakers included.

The phone measures 155 x 68 x 8.3mm, while it weighs 158 grams. The Xperia 10 V comes in Black, Lavender, Sage Green, and White color options. It’s priced at €449 / £399, and it will become available in Europe, the UK, and a few other countries from mid-June.


[ad_2]
Source link

Apple is launching Final Cut Pro and Logic Pro on iPad

0
[ad_1]

It’s no secret that over the past few years, Apple has marketed its iPad Pro devices as a tool that can replace laptops for professionals and creators alike. However, the lack of professional apps, including Apple’s video editing suite, i.e. Final Cut Pro, has refrained many creators from switching to an iPad-only workflow. Now, in an effort to address this issue, Apple is finally bringing Final Cut Pro and Logic Pro to the iPad, which will be available to download from the App Store at a monthly subscription of $4.99 or an annual subscription of $49.

Enhancements to the Final Cut Pro and Logic Pro for iPad

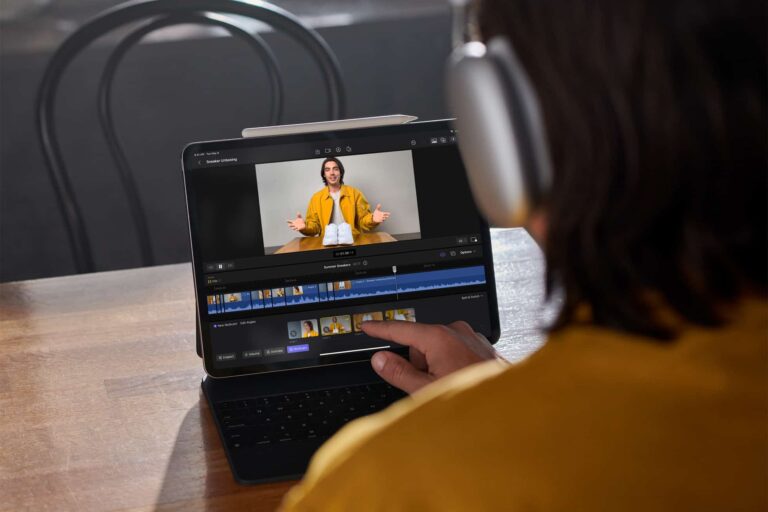
Apple says its new touch-first interface for the apps and intuitive tools allows creators to unleash their creativity in even more places than before. One of the most exciting features is the new jog wheel, which allows users to navigate the Magnetic Timeline, move clips, and make fast frame-accurate edits with just a tap of a finger. Additionally, the new Line Drawing tool enables users to draw and write directly on top of video content using their Apple Pencil. Similarly, the Apple Pencil hover feature lets users skim through preview footage without ever touching the screen.

Meanwhile, Logic Pro for iPad comes with several enhancements as well, such as Multi-Touch Gestures. These gestures let music creators play software instruments and interact with controls naturally, as well as help them navigate complex projects with pinch-to-zoom and swipe-to-scroll gestures.

Additionally, the Logic Pro app for iPad comes with a new sound browser that uses dynamic filtering to help users discover different types of sounds. The app also debuts a new Beat Breaker plug-in that allows users to manipulate the timing and pitch of their sounds with ease by simply swiping and pinching. Moreover, users will also be able to move Logic Pro projects between the app on Mac and iPad.

One month free trial

Apple’s decision to bring Final Cut Pro and Logic Pro to the iPad will enable content creators to switch to an iPad-only ecosystem and take full advantage of their Magic Keyboard or Smart Keyboard Folio to enter keyboard commands. Moreover, Apple is also offering a one-month free trial for users to explore the apps’ features and see if they work for them.

“We’re excited to introduce Final Cut Pro and Logic Pro for iPad, allowing creators to unleash their creativity in new ways and in even more places. With a powerful set of intuitive tools designed for the portability, performance, and touch-first interface of iPad, Final Cut Pro and Logic Pro deliver the ultimate mobile studio,” said Bob Borchers, Apple’s vice president of Worldwide Product Marketing.


[ad_2]
Source link

New Linux NetFilter Kernel Flaw Let Attackers Gain Root Privileges

0
[ad_1]
Linux NetFilter Kernel Flaw

A recently found Linux NetFilter kernel vulnerability, identified as CVE-2023-32233, enables unprivileged local users to gain root-level privileges and full control over the affected system. However, the severity of the flaw has not yet been assessed.

The security issue with Netfilter nf_tables results from accepting invalid configuration updates, leading to subsystem state corruption through certain invalid batch requests.

New Linux NetFilter Kernel Flaw

Netfilter, an essential part of the Linux kernel, can be manipulated to create a use-after-free vulnerability, allowing unauthorized access and manipulation of kernel memory.

Security researchers developed and shared a proof-of-concept exploit to demonstrate the exploitation of CVE-2023-32233, a vulnerability affecting multiple Linux kernel versions, including the current stable release, v6.3.1, but requiring local access a Linux device for exploitation.

Engineer Pablo Neira Ayuso submitted a Linux kernel source code commit that introduces two functions to handle the lifecycle of anonymous sets in the Netfilter nf_tables subsystem, effectively preventing memory corruption and the potential privilege escalation to the root level by addressing the use-after-free issue.

Researchers Patryk Sondej and Piotr Krysiuk found a security flaw in Linux that enables unprivileged local users to gain root access, sharing their exploit privately with the Linux kernel team along with detailed techniques and source code to aid in developing a fix.

The analysts announced their intention to release the exploit and its detailed techniques, in accordance with the Linux-distros list policy, on May 15th, 2023, within the required 7-day timeframe.

Obtaining root-level access on Linux servers is a valuable tool for hackers, but CVE-2023-32233 requires attackers to first gain local access to the system before exploiting it, which is a mitigating factor.

While apart from this, in the mainline kernel git repository, the fix for the problem is available.


[ad_2]
Source link

Update now! May 2023 Patch Tuesday tackles 3 zero-day vulnerabilities

0
[ad_1]

Microsoft’s Patch Tuesday round up for May 2023 includes patches for three zero-day vulnerabilities and one critical remote code execution vulnerability

It’s that time of the month again: We’re looking at May’s Patch Tuesday roundup. Microsoft has released its monthly update, and while the total number of patched vulnerabilities is relatively low at 38, among them are three zero-day vulnerabilities.

Microsoft classifies a vulnerability as a zero-day if it is publicly disclosed or actively exploited with no official fix available. Of the three included in this month’s update cycle, two have been found to be actively exploited and the third has been publicly disclosed.

The Common Vulnerabilities and Exposures (CVE) database lists publicly disclosed computer security flaws. The three zero-days are listed as:

  • CVE-2023-29336: a Win32k Elevation of Privilege (EoP) vulnerability. Exploitation of this vulnerability in the Win32k Kernel driver could provide an attacker with SYSTEM privileges. The Cybersecurity & Infrastructure Security Agency (CISA) has added this vulnerability to its Known Exploited Vulnerabilities Catalog, based on evidence of active exploitation.
  • CVE-2023-24932: a Secure Boot security feature bypass vulnerability. To exploit the vulnerability, an attacker needs either physical access or administrative rights to a target device to install an affected boot policy. The vulnerability has been used to install the BlackLotus UEFI bootkit, a type of malicious infection which targets the Master Boot Record located on the physical motherboard of the computer.  Attaching malicious software in this manner can allow for a malicious program to be executed prior to the loading of the operating system. The primary benefit to a bootkit infection is that it cannot be detected by standard operating systems processes because all of the components reside outside of the Windows file system. UEFI and Secure Boot have been very effective in reducing the number of bootkits, but this vulnerability allows an attacker to bypass those restrictions.
  • CVE-2023-29325: a Windows OLE Remote Code Execution (RCE) vulnerability. This vulnerability is present in Microsoft Outlook and Explorer and can be exploited by attackers in order to remotely install malware. Microsoft says this vulnerability can be exploited merely by viewing a specially-crafted email in the Outlook Preview Pane. This type of RCE vulnerability is bound to become very popular among malware peddlers, and knowing that it has been publicly disclosed means that it is available for them to use. Microsoft advises users that can’t install the patch immediately to read email messages in plain text format.

Another vulnerability to keep an eye on is an RCE vulnerability with a CVSS score of 9.8 out of 10. Listed as CVE-2023-24941 this is a Windows Network File System (NFS) RCE vulnerability which can be exploited over the network by making an unauthenticated, specially crafted request. This vulnerability is not exploitable in NFSV2.0 or NFSV3.0. Prior to updating your version of Windows that protects against this vulnerability, you can mitigate an attack by disabling NFSV4.1. This could adversely affect your ecosystem and should only be used as a temporary mitigation. More information about how to do this and when not to can be found in the Microsoft advisory about this vulnerability under Mitigation.

Other vendors

Other vendors have synchronized their periodic updates with Microsoft. Here are few major ones that you may find in your environment.

Apple released an update addressing two actively exploited zero-day flaws.

Cisco released security updates.

Google has released Android updates.

Mozilla releases security advisories for Firefox 113 and Firefox ESR 102.11.

SAP released patch day updates.

VMWare fixed four vulnerabilities in virtualization software.


Malwarebytes EDR and MDR remove all remnants of ransomware and prevent you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW

[ad_2]
Source link

Twitter improves messaging, readies voice and video call support

0
[ad_1]

Messaging on Twitter is getting a lot better. The company has announced improved DM replies and more emoji reactions. It is also gearing up to add voice and video call support along with encrypted messaging.

According to a recent tweet from Twitter Support, you can now reply to any message in a conversation. Similar to messaging apps like WhatsApp and Telegram, you can select a message and send a reply specific to it. Twitter currently doesn’t have this ability. You cannot mark your response as a reply to any specific message you receive in DMs. This change makes “conversations smoother and more intuitive,” the company says.

On that note, Twitter DMs now support a lot more emoji reactions as well. “We’ve also added a new Emoji Picker to DMs, allowing you to react to messages with a wider range of emojis than ever before,” Twitter Support said. In a separate tweet, Elon Musk added that you can use any emoji reaction. Currently, you can choose from seven emojis to react to a message, including haha, wow, cry, love, fire, thumbs up, and thumbs down.

Since these features are new to Twitter, they may not always work perfectly. Moreover, availability appears limited to mobile apps. But the company assures that it is already working on improving the new features. It will soon improve the rendering for replies to media messages. Additionally, the social network giant is also preparing to bring these features to the web version of Twitter.

Twitter will add voice and video call support

While Twitter Support didn’t share anything else, the aforementioned tweet from Elon Musk contained more information. Firstly, he announced that Twitter will finally start encrypting messages. “Release of encrypted DMs V1.0 should happen tomorrow. This will grow in sophistication rapidly. The acid test is that I could not see your DMs even if there was a gun to my head,” he said on Tuesday evening.

Additionally, Musk revealed Twitter’s plans to add voice and video call support. The Twitter CEO says you will be able to call anyone on the platform using your handle. You don’t need to share your phone number or know the other person’s phone number. This ability is “coming soon” but we don’t have a timeline. But the wait shouldn’t be much longer. Elon Musk has always wanted to encrypt Twitter DMS and support voice and video calls. He has talked about these features several times in the past. His latest announcement suggests the wait is almost over. Stick around and find out.


[ad_2]
Source link

MediaTek Dimensity 9200+ official with massive CPU and GPU boost

0
[ad_1]

MediaTek has launched the Dimensity 9200+, its latest flagship chipset for smartphones. It’s an upgraded version of the Dimensity 9200 launched in November last year. The new chip brings a much faster CPU and GPU while keeping most other things unchanged. The first batch of devices powered by the new MediaTek processor will arrive later this month.

MediaTek launches Dimensity 9200+ with much faster CPU and GPU

The Dimensity 9200+ is a 4nm processor with an octa-core CPU setup. It features one ARM Cortex-X3 prime core clocked at 3.35GHz, three Cortex-A715 medium cores clocked at 3.0GHz, and four Cortex-A510 efficiency cores operating at a maximum frequency of 2.0GHz. In comparison, the Dimensity 9200 has its CPU cores clocked at 3.05GHz, 2.85GHz, and 1.80GHz, respectively.

This is a massive CPU frequency boost for a mid-year refresh from MediaTek. In the past, it mostly equipped the “Plus” version with a faster prime CPU core and GPU while keeping most other things unchanged. Speaking of the GPU, the Taiwanese firm didn’t reveal the precise frequency of the ARM Immortalis-G715 MC11 GPU on the Dimensity 9200+. However, it said the new chip brings a 17 percent performance boost. The GPU is clocked at 981MHz on the Dimensity 9200.

According to MediaTek, these CPU and GPU upgrades on the Dimensity 9200+ don’t come at a cost of power efficiency. “Power consumption remains the same versus the Dimensity 9200,” it assured. The new chip doesn’t bring any other notable upgrade, though. Both chipsets are manufactured by TSMC using its second-gen 4nm process node. They share the ISP (Image Signal Processor), cellular modem, connectivity options, AI Processing Unit, display specs, connectivity, and more.

For a quick recap, the Dimensity 9200 supports up to 320MP cameras with 8K video recording at 30fps (frames per second). It can handle Full HD+ displays with up to 240Hz refresh rate and WQHD displays with up to 144Hz refresh rate. The chip offers both sub-6GHz and mmWave 5G connectivity with multi-mode and carrier aggregation. The Dimensity 9200 also supports the latest RAM and storage standards (LPDDR5X RAM and UFS 4 storage). Last but not least, it boasts Wi-Fi 7 and Bluetooth 5.3. All of this carries over unchanged to the Dimensity 9200+.

The new MediaTek chip will ship inside phones later this month

MediaTek hasn’t named any devices that would be using the Dimensity 9200+. However, it confirmed that the new chipset will ship inside phones as early as this month. There are rumors that Vivo is readying new models in the Vivo X90 series with this chip. The Vivo X90 Pro is currently the only Dimensity 9200-powered phone available globally. You can read our review of the phone for its everyday performance.


[ad_2]
Source link