Activision Players Attacked by Password Stealing Malware

0
[ad_1]

Activision, the powerhouse behind popular titles such as Call of Duty, is currently embroiled in an investigation into a hacking campaign aimed at its players.

The primary objective of cybercriminals is to siphon off player credentials, focusing on gaming accounts and cryptocurrency wallets.

Sources close to the situation, who have requested anonymity due to the matter’s sensitivity, have revealed that the hackers are infiltrating victims’ computers with malware. The malicious software then proceeds to extract passwords for various accounts.

The extent of the damage and the precise method of the malware’s distribution remains in mystery.

Speculation suggests that the issue may be confined to users who have installed third-party tools on their systems.

Document
Run Free ThreatScan on Your Mailbox

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Try Trustifi Free Threat Scan with Sophisticated AI-Powered Email Protection .

Activision Blizzard’s internal team is reportedly hard at work, attempting to eradicate the malware and restore security to any player accounts that have been compromised.

Despite the urgency of the situation, Activision spokesperson Delaney Simmons has emphasized that the company’s servers are secure and have not been breached.

Instead, the spotlight is on unauthorized third-party software as the likely culprit behind the malware infections.

The Discovery and Response

The malware campaign’s initial discovery is credited to an individual known as Zebleer, who is involved in the development and sale of cheating software for Call of Duty.

Zebleer stumbled upon the issue when a customer reported the theft of their account for the cheat software.

This prompted an investigation that led to unearthing a database filled with stolen credentials.

Zebleer has since taken proactive measures, alerting Activision Blizzard and other cheat providers whose users might be at risk.

TechCrunch has independently verified a sample of the stolen logins, confirming the authenticity of at least a portion of the data.

However, the freshness of the data remains uncertain.

The Impact on Players

At this juncture, there is no evidence that the average Activision game player is in danger.

The threat specifically targets individuals who utilize third-party applications, including cheats.

Nevertheless, Activision’s Simmons has advised all users who feel their accounts may have been compromised to change their passwords and enable two-factor authentication as a precautionary measure.

As the investigation continues, the gaming community is on high alert.

The incident is a stark reminder of the risks of downloading and using unauthorized software.

It also underscores the importance of cybersecurity measures such as two-factor authentication in safeguarding digital identities.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link
Camera-boosting Galaxy S24 update has reached the US

0
[ad_1]

About a week ago, Samsung started rolling out a camera-boosting update to the Galaxy S24 series, but not the US users. Well, the update is finally starting to roll out in the US as well.

Users in the US are now receiving the camera-boosting Galaxy S24 series update

This update not only delivers a number of camera improvements, but a new security patch too. The US users are now receiving an Android security patch for April 2024. The update is rolling out to factory-unlocked Galaxy S24, Galaxy S24+, and Galaxy S24 Ultra phones.

This particular update is coming with the firmware version S92xU1UEU1AXCB. It’s actually quite a chunky update, so you may want to use WiFi for this one. That’s up to you.

So, what exactly has changed in terms of the cameras? Well, the changelog is the same as the one we talked about a week ago. It’s identical, which was expected, as this is essentially the same update for a different market.

It will improve white balance accuracy & exposure on the devices

This update improves white balance accuracy and exposure on the Galaxy S24 series phones. On top of that, it improves low-light image quality on all three smartphones. You should be able to see some notable improvements.

If you’re taking plenty of high-range zoom shots, well, the text clarity should be better post-update. Samsung has also added support for videos with 480×480 resolution in the Instant Slow Mo feature.

The last addition to the changelog has to do with the ExpertRAW camera app. Samsung improved color accuracy in that app, though do note that this change will come as a separate update to the ExpertRAW camera. It should arrive once you install this April update.

Your smartphone will let you know when it’s time to update. You can, though, check for yourself too, of course. Simply open Settings, and navigate to the Software update section. There you’ll want to hit the Download and install option.


[ad_2]
Source link

Microsoft 365 & Gmail accounts in danger from new phishing kit

0
[ad_1]

In today’s technological age, most people believe that using two-factor authentication is their last line of defense. While this assumption is not wrong, there are ways hackers can bypass 2FA and steal personal data. Those who want to get around the 2FA security system allegedly use a new Adversary-in-The-Middle (AiTM) phishing kit called Tycoon 2FA, which is a threat to both Microsoft 365 and Gmail.

The kit is linked with the Tycoon 2FA Phishing-as-a-Service (PhaaS) platform. Using the kit, hackers are trying to target Microsoft 365 and Gmail accounts. With this kit and techniques like using Apple’s customer care number to trick unsuspecting victims, the threat of phishing attacks is higher than ever.

What is the new Gmail threat, the Tycoon 2FA phishing kit?

First discovered by the Sekoia Threat Detection & Research team, Tycoon 2FA is a Phishing-as-a-Service platform originally advertised through private Telegram channels. It works using an Adversary-in-The-Middle phishing kit, where a reverse proxy server hosts the phishing page. Legitimate services then relay the credentials.

There are a few steps that victims follow that make the Tycoon 2FA attack a success for the hackers. The attack usually begins when a victim receives an email with a malicious QR code or website that directs the victim to the phishing site. When interacted with, the QR code or link has victims visit Cloudflare security check that many websites utilize to prevent unwanted traffic and filter out the bots. Thanks to how common these challenges or checks are, most people don’t think much of it.

Once the victims complete the security challenge, they are redirected to a fake Microsoft page that harvests their credentials. At this stage, the kit mimics the 2FA prompts, such as SMS OTP, call verifications and authenticator app push notifications. By getting their hands on the 2FA inputs, hackers can generate valid session cookies and bypass Multifactor Authentication (MFA) protections.

Once the hackers authenticate using the relayed credentials, the victims are redirected to a legitimate-looking error page. The page conceals the success of the phishing attack. However, since the attackers can freely access the victim’s accounts, they can do anything with them.

How to protect yourself against Tycoon 2FA?

These phishing scams use sophisticated methods to trick their prey into assuming they input their credentials into legitimate websites. However, you can protect yourself using some of these steps. Firstly, avoid trusting links and QR codes sent to you via unsolicited emails or messages, and visit official sites manually to verify.

You can also use a 2FA method that uses hardware security keys or biometrics, as hackers can not bypass those using phishing attacks. Lastly, read up on all the new phishing techniques that hackers are using so you can better prepare yourself. After all, techniques hackers use to acquire user credentials are ever-evolving, and staying on your toes is crucial.


[ad_2]
Source link

AT&T admits a 2021 data breach affecting 73 million customers

0
[ad_1]

AT&T has finally admitted a data breach affecting 73 million current and former customers. The breach happened several years ago, but the company repeatedly denied it saying that the leaked data didn’t originate from its systems. It acknowledged the breach about two weeks after a threat actor publicly dumped the stolen data on the dark web. The carrier has sent email notifications to affected customers.

AT&T confirms a data breach impacting 73 million customers

In August 2021, a well-known threat actor claimed to have breached AT&T’s security systems and stolen the personal information of over 70 million users. Samples leaked on the dark web contained a wide range of information about AT&T customers, including names, addresses, phone numbers, email IDs, social security numbers, and dates of birth. The hacker offered to sell the entire database for $1 million.

Despite potential privacy and security risks to its customers, AT&T denied suffering a breach. While there hasn’t been any follow-up for over two years, another threat actor shared the database for free on a hacking forum last month. Multiple sources independently verified that the database contains information about AT&T customers, people with online AT&T accounts, or people previously associated with AT&T.

Two weeks later, the carrier giant officially acknowledged that the breach impacted its customers. In a statement to TechCrunch, AT&T said the leak affects 7.6 million current users and 65.4 million former users. Emails sent to affected users state that the breach also compromised account passcodes, which are typically four-digit numbers. The company has reset compromised passcodes from its end.

AT&T still hasn’t identified the source of the leak, though. It does not know “whether the data in those fields originated from AT&T or one of its vendors.” The company says it “does not have evidence of unauthorized access to its systems resulting in exfiltration of the data set.” Nevertheless, if you are a current or former AT&T user, you should remain vigilant and actively monitor your account activities and credit reports.

AT&T offers complimentary identity theft and credit monitoring services

According to AT&T, the leaked data set is from 2019 or earlier and does not contain personal financial information or call history. Moreover, the information varied by customer and account. For users who had their sensitive personal information compromised in this leak, the company is offering complimentary identity theft and credit monitoring services. AT&T has put up a support page with more information about the breach and steps to secure your account.

ATT data breach confirmation email


[ad_2]
Source link

WhatsApp’s locked chats set to sync across all your linked devices

0
[ad_1]
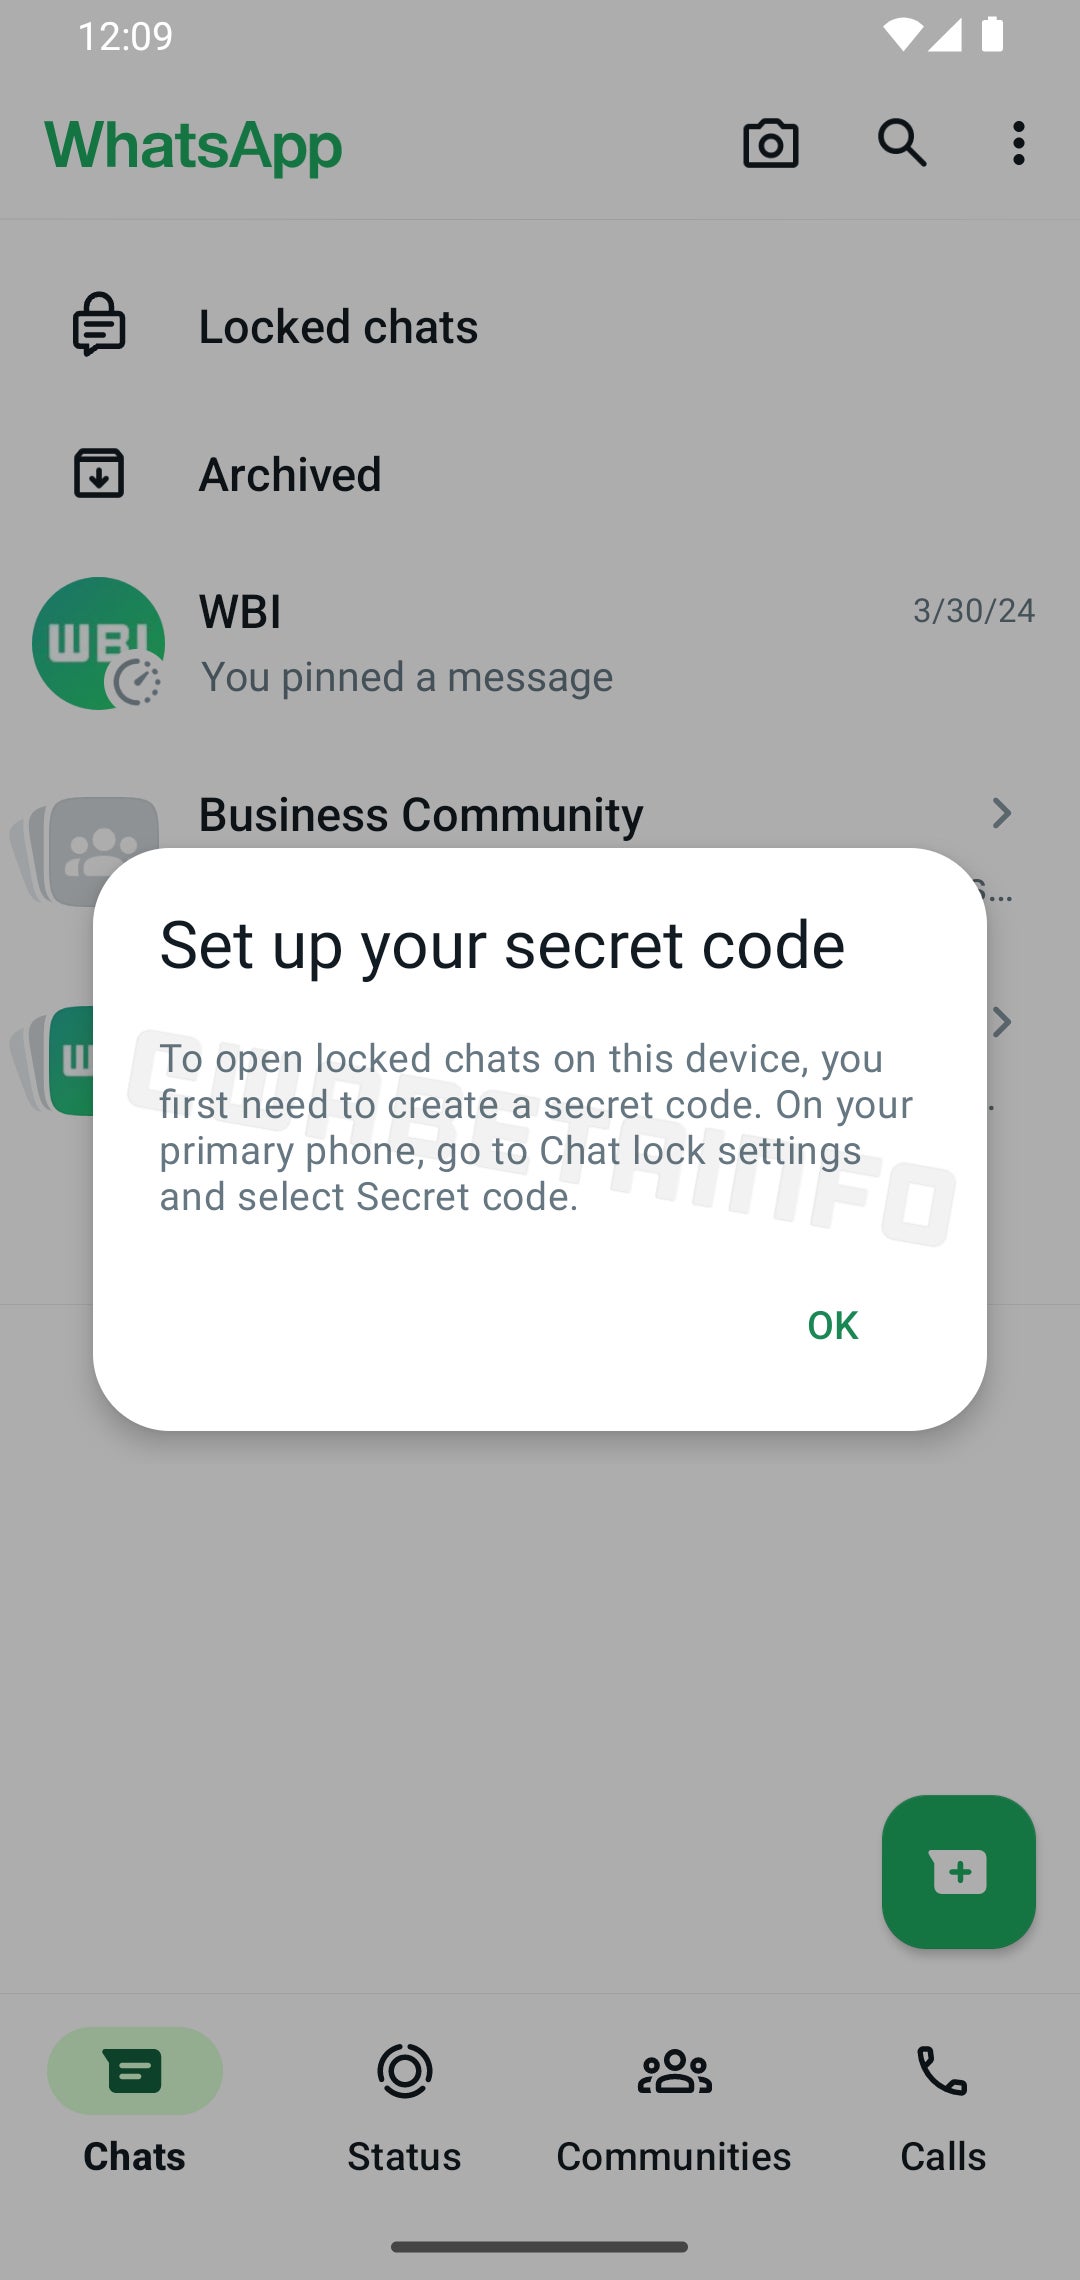
Towards the end of last year, WhatsApp dropped a neat little update that beefed up its privacy and security game: a secret code to lock down chats. This nifty tweak aimed to give users an added layer of privacy by hiding locked chats from plain sight and requiring a personal code for access. But for now, it is only available on primary devices. However, that might change soon.According to the go-to source for WhatsApp updates, WABetaInfo, the latest WhatsApp beta for Android 2.24.8.4 update on the Google Play Store reveals something interesting: WhatsApp is cooking up a locked chats feature for linked devices.

If you check out the attached screenshot, you will see that WhatsApp explores the idea of locked chats support for linked devices in a future app update. To unlock these chats on a linked device, users will need to set up a secret code.

This code can be set up on the primary phone under chat lock settings by choosing the secret code option. Once set up, locked chats vanish from the chats list and can only be accessed via this privacy feature on linked devices.

Introducing this feature for linked devices is a win for both privacy and user convenience. It ensures that locked chats stay synced across all devices, letting users easily access their protected conversations from anywhere without worrying about prying eyes.

Currently, locked chats are stuck on the primary device, potentially exposing conversations on linked devices – a privacy no-no. The locked chats feature for linked devices is in the works and will roll out in a future update.

In other WhatsApp news, the messaging app also started rolling out a new bottom navigation bar for smoother use and is testing a fresh look for its calling screen, making it easier to hang up. Keep an eye out for updates!


[ad_2]
Source link

Imperva Web Application Firewall Flaw Let Attackers By WAF Rules

0
[ad_1]

Imperva SecureSphere WAF, a security tool for on-premise web applications, has a vulnerability in some versions that allows attackers to bypass filters when inspecting POST data. 

By sneaking malicious content past the WAF, attackers could potentially exploit security flaws in the protected web applications that the WAF would normally block, which compromises the security of the web applications shielded by the WAF. 

A critical vulnerability (CVE-2023-50969) exists in Imperva SecureSphere WAF versions that lack the update referenced in the  “Fixed Version(s)” section, allowing attackers to bypass WAF rules designed to inspect POST data, potentially enabling the exploitation of vulnerabilities in protected applications that the WAF would normally block. 

The attacker doesn’t need to authenticate and can exploit the vulnerability remotely, while it is rated critical due to the high severity of bypassing security controls. 

Document
Run Free ThreatScan on Your Mailbox

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Try Trustifi Free Threat Scan with Sophisticated AI-Powered Email Protection .

Technical Details Of The Vulnerability:

The code snippet demonstrates a PHP webshell vulnerability named clam.php, which creates a form that allows users to submit arbitrary commands through a text input field. 

Code snippet

When the form is submitted, the `system` function is used to execute the submitted command on the server, posing a security risk because it allows attackers to remotely execute arbitrary code on the server, potentially compromising the system.

The lack of proper input validation and sanitization in the code allows for the injection of malicious code through user input, which an attacker could use to upload malicious files, steal sensitive data, or deface the website.

A security vulnerability exists where a system command can be executed through a POST request with a specific parameter, where standard WAF rules typically block such attempts (e.g., reading password files). 

Attempts blocked by a standard WAF rule

By manipulating the Content-Encoding header, one can get around the rules by tricking the WAF into misinterpreting the data and allowing the malicious command to run. 

Result after modifying request

A specific WAF rule vulnerability allows attackers to bypass security by sending a malformed HTTP request with a double Content-Encoding header (“No Kill No Beep Beep” and “deflate”) followed by a throwaway parameter before the actual malicious data. 

According to the Hoya Haxa, a vulnerability was reported to Imperva on November 10th, 2023, and an update to address this vulnerability was released through Imperva’s ADC rules on February 26th, 2024, whereas  details regarding the vulnerability and the remediation process were publicly disclosed in a blog post on March 27th, 2024.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link
Google Home ‘vision’ & more highlighted during Reddit AMA

0
[ad_1]

Multiple managers of Google Home held a Reddit AMA (Ask Me Anything). Most were inundated with active users and home automation tinkerers.

The team developing and managing Amazon Alexa’s main rival in home automation assured they have a “vision and roadmap”. However, several Redditors who pounced on the opportunity to discuss Google Home’s future had more queries than answers.

Google Home on the web and “additional controls” on their way

Google Home is one of the most aggressively priced home automation and AI virtual assistants. The uniquely shaped Alexa competitor also rivals third-party and open-source solutions.

The Google Home team that participated in the Reddit AMA included quite a few product and engineering managers. Instead of a multimedia question-answer session, the Reddit CEO held recently to justify his handsome compensation, the Google Home team had a text-only session.

We’re the team behind the latest updates to Nest devices and Google Home for web – ask us anything!
byu/kelanfromgoogle ingooglehome

Using the platform, several Redditors posted multiple lengthy posts. One particular post asked when Google would release additional Google Home controls on the web, add devices, and replace Google Assistant with Gemini.

Google Home team is actively working to, “bring additional device control to Google Home for web,” revealed Jacqueline, a Google Home and Nest Product Manager. Needless to add, this does not truly address the question, and the team hasn’t offered any timeline.

As is the norm, support for new devices and additional controls for the existing home automation and IoT devices should first appear in a Public Preview. As expected, the team remained tight-lipped about letting Google’s Gemini AI engine take over from Google Assistant.

Offline or local interactions coming soon to Google Home

For a multi-billion-dollar company, Google Home doesn’t appear to have an expansive and quickly-growing support for smart devices. Additionally, the product often struggles to understand human voices, several comments on the Reddit AMA indicated.

Presumably, that’s why Google Home doesn’t get as much promotion as a Pixel smartphone. The open-source Home Assistant platform, in comparison, has a lot of traction.

The entire Google Home platform seems to trailing its main rival Amazon Alexa and its products and services. During the Reddit AMA, the platform’s managers couldn’t commit to a large number of features, bugs, troubleshooting requests, and additions Redditors eagerly requested.

The team, however, did indirectly admit that Google Home’s instructions and interactions faced reliability and latency issues. To improve the speed or reduce the time taken between a user speaking out instructions and Google Home addressing them, Google is focused on routing more instructions locally.

Team member Daniel revealed that once Google feels it has a “significant” amount of your traffic operating locally, it will shift to focus on bringing “powerful” offline capabilities through the app. At present, Google Home users need an active internet connection for most of the instructions. This could change soon with a definitive offline mode for Google Home.


[ad_2]
Source link

Backdoor in upstream xz/liblzma Let Attackers Hack SSH Servers

0
[ad_1]

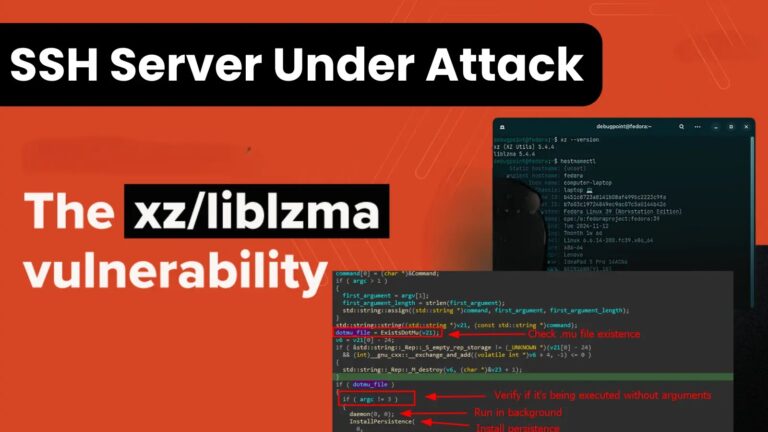
A startling revelation has identified a dangerous security vulnerability in the xz compression utility, specifically within its liblzma library. This vulnerability has been found to compromise SSH server security.

Xz Utils is a tool found almost everywhere in Linux. It helps to shrink data without losing any information on almost all systems similar to Linux.

It’s important for making data smaller or returning it to its original size during various tasks. Xz Utils can also work with the old .lzma format, which makes it even more useful.

The issue, traced back to a backdoor in the upstream xz repository, was first noticed due to unusual system behavior on Debian sid installations, including excessive CPU usage during SSH logins and errors reported by the memory error detector, Valgrind.

Discovery of the Backdoor

The investigation, led by security expert Andres Freund, uncovered that the backdoor was not limited to Debian’s package but was, in fact, present in the upstream xz tarballs for versions 5.6.0 and 5.6.1.

This malicious code was ingeniously hidden within the distributed tarballs and not in the source code available on the repository, making it particularly insidious.

The backdoor operates by injecting an obfuscated script into the build process, which then modifies the Makefile to execute a payload hidden within seemingly innocuous test files.

Once executed, this payload can modify the behavior of the SSH server, significantly slowing down SSH logins and potentially allowing unauthorized access.

Document
Run Free ThreatScan on Your Mailbox

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Try Trustifi Free Threat Scan with Sophisticated AI-Powered Email Protection .

Scope and Impact

The vulnerability explicitly targets x86-64 Linux systems built with GCC and the GNU linker and appears to be designed to evade detection by only activating under certain conditions, such as during the build process of Debian or RPM packages.

This targeted approach suggests a sophisticated understanding of Linux distribution build systems and a clear intent to infiltrate these systems undetected.

Notably, the backdoor does not directly affect the OpenSSH package but exploits a dependency chain where subsystem, patched into openSSH by several Linux distributions, relies on the compromised liblzma.

This indirect attack vector highlights the complex interdependencies in modern software ecosystems and the potential for widespread impact from a single vulnerability.

According to the Red Hat report, this backdoor is only in the latest branch of xz (version 5.6 and 5.6.1). People still running versions 5.4 and older should be fine.

“Current investigation indicates that the packages are only present in Fedora 40 and Fedora Rawhide within the Red Hat community ecosystem, No versions of Red Hat Enterprise Linux (RHEL) are affected”.

Response and Mitigation

The discovery of this vulnerability has prompted immediate action from the security community.

Red Hat has assigned the issue CVE-2024-3094, and efforts are underway to patch affected systems and prevent further exploitation. A detection script has also been developed to help system administrators identify potentially vulnerable installations.

Given the severity of the vulnerability and the potential for unauthorized access to affected systems, users and administrators of potentially impacted systems are urged to upgrade their installations as soon as possible.

The discovery of this backdoor serves as a stark reminder of the ongoing threats to software security and the need for vigilance in monitoring and securing critical infrastructure.

The discovery of a backdoor in the widely used xz compression utility underscores software security’s persistent challenges.

As attackers develop sophisticated infiltration methods, the security community must remain vigilant in identifying and mitigating vulnerabilities.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link
Google Play ‘Super Weekly Prize’ gives away 200 Pixel phones

0
[ad_1]

Google Play is organizing an enticing new giveaway, the “Super Weekly Prize,” exclusively for Gold, Platinum, and Diamond tier members of the Play Points program. The prize raffle is one of the many perks you get if you haven’t redeemed your Play points in a while and you have reached the Gold tier or above.

Google is offering you a chance to score a Pixel 8 phone with Google Play Points

According to 9to5Google’s recent post, members of Play Points from Gold, Platinum, and Diamond levels are now receiving invites to participate in the “Super Weekly Prize.” Under this promotion, the prizes for Platinum users include Pixel 8 Pro Mint (100 pcs), Pixel 8 Mint (100 pcs), and 1000 Google Play points each for 10,400 people.

There haven’t been any claims regarding Pixel 8 or 8 Pro distribution yet, which means a random selection process is in effect. All participants only have one chance of winning, and the winner selections are random.

The Super Weekly Prize is one of the reasons why Google Play Points members should rejoice since it doesn’t require any Play Points redemption. In addition, during the year 2022, Google introduced an exclusive giveaway with T-shirts for its Play Point Platinum members.

Google’s reward-based scheme has grown to over two hundred million members across all thirty-five marketplaces, making it one of the most extensive loyalty programs globally. Its enhanced incentives include the Super Weekly Prize Giveaway Campaign, rewarding its consistent followers with amazing opportunities where they can win valuable prizes.

Only Gold, Platinum, and Diamond tier members fit the criteria to participate in the giveaway

Participants must understand that prizes change depending on their level of membership and other qualifications may apply. Prizes depend on stock availability and eligibility requirements with the new ones getting shipped every Friday at 12:00 AM, midnight.

Super Weekly Prize adds some extra flavor to the Google Play Points program by offering members a chance to win Pixel 8 and 8 Pro handsets or point-based rewards, which make the overall membership experience slightly more thrilling.


[ad_2]
Source link