Hisense 50-inch U6 Series 4K TV Discounted to $499 for a Limited Time

0

[ad_1]

Amazon sells the Hisense 50-inch U6 Series Google TV for just $299. That’s going to save you over $200 off of the regular price. Which is low enough for an all-time low price on this model.

But other sizes are also on sale. The 58-inch is now $349 (reg. $599), the 65-inch is now $449 (reg. $749) and the 75-inch is now $629 (reg. $1,149). Great prices on all of these models to be honest.

The Hisense U6 Google TV is a great option for anyone looking for a high-quality 4K TV with a great smart TV platform. The TV features a number of impressive specs, including a 50-inch 4K Ultra HD display with HDR10+ support, a powerful quad-core processor, and 2GB of RAM. This combination of features provides smooth and crisp images with excellent color reproduction.

In addition to its impressive picture quality, the Hisense U6 Google TV also has a number of other features that make it a great choice for anyone looking for a smart TV. The TV runs on the Android TV operating system, which gives you access to a wide variety of streaming apps, including Netflix, Hulu, Disney+, and Amazon Prime Video. The TV also has a built-in Chromecast, so you can easily cast content from your phone or tablet to the TV.

Another great thing about the Hisense U6 Google TV is its price. The TV is currently on sale for just $499, which is a great value for all the features it offers. If you are looking for a great 4K TV with a great smart TV platform, then the Hisense U6 Google TV is a great option.

Here are some of the reasons why you should buy the Hisense U6 Google TV:

Excellent picture quality: The Hisense U6 Google TV features a 50-inch 4K Ultra HD display with HDR10+ support. This means that you can enjoy movies and TV shows with stunning clarity and detail.

Powerful processor: The Hisense U6 Google TV is powered by a quad-core processor and 2GB of RAM. This ensures that the TV can handle even the most demanding tasks, such as streaming 4K content or gaming.

Android TV operating system: The Hisense U6 Google TV runs on the Android TV operating system. This gives you access to a wide variety of streaming apps, including Netflix, Hulu, Disney+, and Amazon Prime Video.

Built-in Chromecast: The Hisense U6 Google TV has a built-in Chromecast. This means that you can easily cast content from your phone or tablet to the TV.

If you are looking for a great 4K TV with a great smart TV platform, then the Hisense U6 Google TV is a great option. The TV is currently on sale for just $299, so act fast before this deal expires.

Hisense U6 Google TV – Amazon

[ad_2]

Source link

Trezor Data Breach Exposes Email and Names of 66,000 Users

0

[ad_1]

Trezor, the hardware wallet manufacturer, has disclosed a data breach involving unauthorized access to a third-party support portal used by the company.

In a worrying development for cryptocurrency enthusiasts, hardware wallet manufacturer Trezor disclosed a data breach on January 20, 2024, that potentially exposed the contact information of nearly 66,000 users.

While the company assures that no user funds were compromised, the incident highlights the importance of cybersecurity even for hardware wallets, which are often touted as the most secure way to store digital assets.

What Happened?

The breach involved unauthorized access to a third-party support portal used by Trezor. The incident occurred on January 17, 2024, and potentially affected users who interacted with the support team since December 2021. The exposed information included email addresses and usernames, however, Trezor confirmed that the attacker did not access the phone numbers or postal addresses of victims.

We are making every effort to work with the third-party service provider to comprehensively investigate the incident. However, our internal audit of the incident suggests potential access to contact details, limited to email and name/nickname.

Trezor

Why is This Concerning?

Even though user funds and addresses remain safe, the exposed contact information puts users at risk of phishing attacks. Hackers could use this information to send targeted emails impersonating Trezor and attempt to steal users’ login credentials or private keys. These keys are essential for accessing and managing cryptocurrency holdings, and if compromised, could lead to significant financial losses.

Trezor Data Breach Exposes Email and Names of 66,000 Users
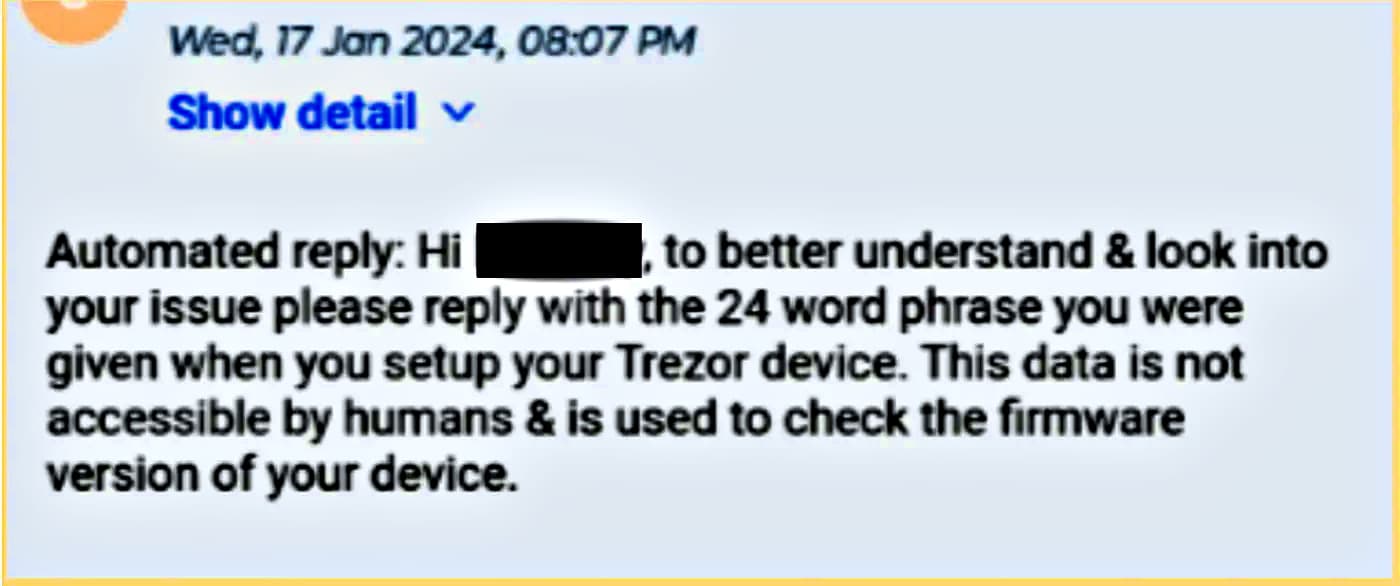
Here is an image capturing the email sent to users by the malicious actor during the security breach. (Screenshot via Trezor’s blog post)

What Trezor is Doing

Trezor has taken several steps in response to the breach:

  • Notified all 66,000 potentially affected users via email.
  • Emphasized that user funds were not compromised.
  • Investigated the incident and took steps to prevent future breaches.
  • Advised users to be wary of phishing attempts and to take steps to protect their online accounts.

What Users Can Do

If you are a Trezor user and received an email about the breach, here are some steps you can take to protect yourself:

  1. Be cautious of any emails claiming to be from Trezor. 
  2. Do not click on any links or open any attachments in suspicious emails.
  3. Change your Trezor PIN and password immediately.
  4. Enable two-factor authentication for your Trezor account.
  5. Regularly update your software and operating system.
  6. Report any suspicious activity to Trezor support.

Impact of the Breach

The Trezor data breach is a reminder that no system is foolproof, even for hardware wallets. While user funds were not compromised in this incident, it serves as a wake-up call for the cryptocurrency community to be vigilant about cybersecurity. Users should be aware of the risks associated with phishing attacks and take steps to protect themselves.

  1. 6 of the Best Crypto Bug Bounty Programs
  2. Outdated Wallets Threatening Billions in Crypto Assets
  3. Crypto Scammers Exploit Gaza Crisis in Donation Scam
  4. We Need Smarter Smart Contracts To Prevent DeFi Hacks
  5. Scammers Use Fake Ledger App on Microsoft Store to Steal $800K
  6. Inferno Drainer Phishing Nets Scammers $80M from Crypto Wallets
  7. “Get Paid to Like Videos”? This YouTube Scam Leads to Empty Wallets


[ad_2]

Source link

Google Messages is finally adding image captioning thanks to RCS

0

[ad_1]

Google flipped the switch to RCS messaging a while back, and messaging on Android has gotten so much better. One of the most popular messaging applications for Android is Google Messages. Not to be confused with Google Chat, Google Messages is the platform that people use for typical phone number-based communication. Well, Google Messages is bringing image captioning, another great benefit of having RCS technology.

RCS messaging brings a ton of benefits over the oldest SMS messaging. People using Google Messages have already seen some benefits of this including better security, larger file sharing, message reactions, and more. Later this year, Apple is going to finally enable RCS messaging for iPhones. However, Apple’s implementation will still be a fair bit behind Google’s.

Google Messages is finally bringing image captioning.

We’re all used to sharing images with our messages, and we sometimes want to add just a little bit more context to them. Maybe you want to send an image of a cat comfortably sleeping inside of a juice pitcher with a caption reading “my weekend plans”.  Well, certain platforms like Facebook Messenger and WhatsApp allow you to add a caption directly onto an image posted. It means that the text and image will occupy one message bubble. This is actually a relatively new feature for WhatsApp.

However, in the case of Google Messages, this was not a possibility. When you would send an image with text, they will be sent as separate messages. However, according to a new report from @AssembleDebug on X, Google Messages is working on bringing image captioning. In the image shared by AssembeDebug, we see screenshots with the text added.

Google messages image captioninig

This is a great feature to have, and it will make sending messages between people in Google Messages what’s more convenient. At this point, we don’t know when Google is going to roll this feature out to everyone. It seems complete enough to be rolled out soon. However, there’s no telling if Google is going to roll this out arbitrarily or as part of a new feature drop. If it’s part of a feature drop, then it will be a few months away. Hopefully, that’s not the case


[ad_2]

Source link

Unlocked Galaxy S21 finally gets Android 14 in the US

0

[ad_1]

At long last, Samsung has released its Android 14-based One UI 6.0 update for the unlocked variants of the Galaxy S21 series in the US. The big Android update is rolling out widely to users on all major carrier networks. The remaining few will also join the party soon.

Android 14 is now available for unlocked Galaxy S21 in the US

Samsung started pushing Android 14 and One UI 6.0 to the Galaxy S21, Galaxy S21+, and Galaxy S21 Ultra in November last year. Following an international release, the update arrived in the US in early December. However, the company initially only updated the carrier-locked units of the 2021 flagship trio.

It was expected to roll out One UI 6.0 to unlocked units in a week or two but the company kept users waiting for over six weeks. The wait has finally ended. The update is rolling out to the unlocked Galaxy S21 trio with the firmware build number G99xU1OYM9FWL3. It is available nationwide on most networks.

Since this is a major Android OS upgrade, the update that you are getting over the air (OTA) is massive. It has a download size of over 2GB. The update brings UI revamps, new camera features and editing tools, improved stock apps, smoother system animations, and many functional improvements to your Galaxy phone.

Additionally, Samsung is pushing the December 2023 security patch with more than 60 vulnerability fixes. So, your phone is getting security enhancements too. The Korean firm has already released the January 2024 patch, which is also available to the carrier-locked Galaxy S21 in the US. It contains 80 security fixes. Unlocked units should get it in the coming weeks.

If you are using a Galaxy S21, Galaxy S21+, or Galaxy S21 Ultra in the US and haven’t yet received One UI 6.0 or a new security update, you can check for it from the Settings app. Go to the Software update section and tap on Download and install. If there is no update available for you, wait a few days and check again.

The aging Samsung flagships will get One UI 6.1 soon

Android 14 is the penultimate major Android OS upgrade for the Galaxy S21 series. The lineup will get Android 15 and that’s it. While the next version of Android is still several months away, another major feature update is on the way for the devices. Samsung is readying One UI 6.1 with new AI features. The update is expected to roll out in the coming months.

[ad_2]

Source link

Massive data breach includes 26 billion records and 12TB of data

0

[ad_1]

Data breaches are happening with alarming frequency lately, which means it’s increasingly likely your data is out in the wild somewhere. If there’s one place that user data is likely to exist, it’s in a massive data breach pool that was recently discovered by CyberNews and SecurityDiscovery.com. This data pool looks to be a compilation of many major breaches and includes over 26 billion data breach records. That amounts to over 12TB of data, and it includes more than just passwords.

The exact nature of the records is unknown, but there are a few possibilities. The most likely records to be found in this data breach are usernames and passwords. However, it’s possible that other types of information, like credit card information or addresses are included as well. The good news is, the researchers do not suspect that new data is included in the pool. Rather, it’s a major sourcing of pre-existing data breaches. According to the researchers, this suggests that the owner has a “vested interest in storing large amounts of data.”

What’s included in the data breach’s 26 billion records

The research into this data breach was led by Bob Dyachenko, a cybersecurity expert and the owner of SecurityDiscovery.com. Although the team says that no new data leaks are known to be included, that doesn’t mean end users shouldn’t be concerned. “The dataset is extremely dangerous as threat actors could leverage the aggregated data for a wide range of attacks,” the researchers told CyberNews. “Including identity theft, sophisticated phishing schemes, targeted cyberattacks, and unauthorized access to personal and sensitive accounts.”

The data breach’s 26 billion records also include information that users probably won’t want getting out. The company or brand with the most leaked records in the data pool was Tencent, a Chinese tech giant, who had 1.5 billion records leaked. Tencent, among other things, operates the Tencent QQ messaging app. Other sites with millions of leaked records include LinkedIn, Deezer, Adobe, and Canva. Some adult sites were also included in the data pool such as 220 million records from AdultFriendFinder.

Besides companies and brands, some data is also stolen from governments, such as the U.S., Brazil, Germany, Philippines, Turkey, and more. But the real concern is that malicious actors could use the stolen data for more widespread identity theft. For example, if you use the same password for LinkedIn as your banking app, you might be in trouble. A potentially-compromised social media site could spiral into a financial disaster quickly.

How to check if your data is in the breach

There’s no clear cut way to know if your data has been breached with absolute certainty. However, there are a few things you can do. There’s a search bar at the bottom of CyberNews’ article that lets you search through every site that was compromised. If you use a site that has been breached, you should change your password just to be safe. You can also visit haveibeenpwned.com and enter your email to see if it has appeared in a data breach. Otherwise, a good rule of thumb is to use strong passwords, different passwords, and change them if you think they’ve been compromised.

[ad_2]

Source link

Bind For Cleaning Blood And Bullet Marks In Counter-Strike 2

0

[ad_1]

One of the most needed functions in the CS console has always been a command that allows you to instantly remove all traces of blood and bullet marks on the walls. This bind is useful not only for aesthetic reasons — traces of blood have been proven to slightly reduce FPS in Counter-Strike 2.

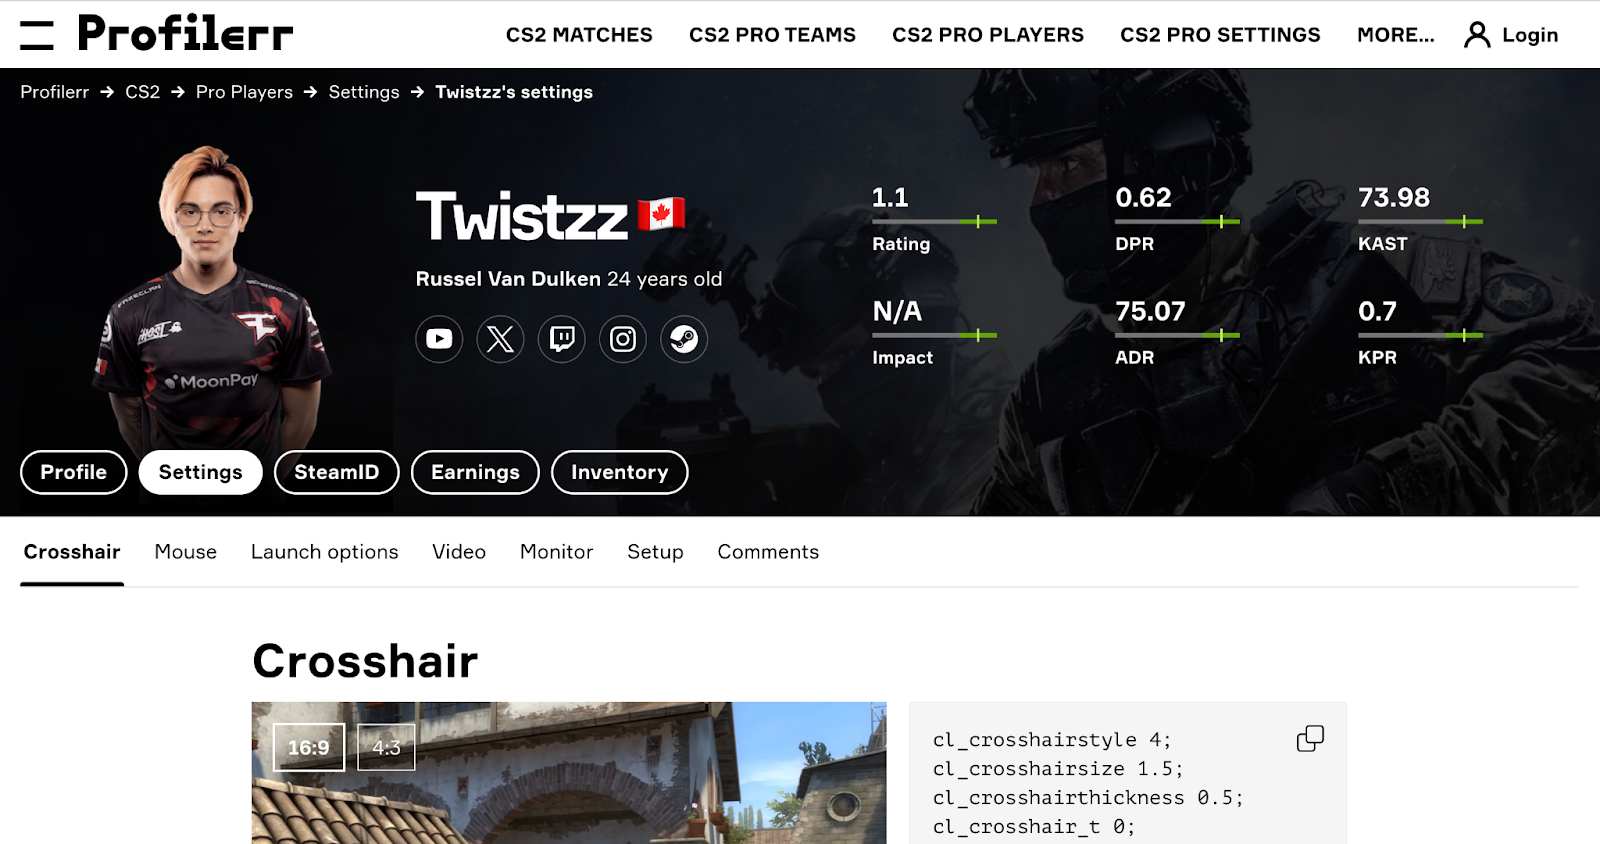
If you want an effective game that will allow you to achieve success on par with the best pro players, this article from eZstah is for you. You can also further explore grim, KSCERATO from FURIA Esports, or twistzz CS2 settings on the Profilerr platform.

Binds In CS2: What Is It?

Many people know that CS2 has a fairly impressive set of commands. The classic version of their use involves activating the console and entering a certain set of characters manually.

It’s long and inconvenient. Another option is that some commands can be attached or changed in the game settings. But not everything is there. Plus, it’s not always convenient.

However, binds solve this problem! It is enough to configure everything once, and then everything will work by pressing a certain button!

The fact is that binds in KS2 are a special system that allows you to bind one or another command existing in the game to a specific button.

It turns out the following:

  • The gamer sets up the bind once – it should be linked via the console to a specific command to a specific button.
  • During the game or during pauses between battles, a person presses a button to execute a command.
  • The result is a quick response to commands. Control is carried out with maximum comfort and speed for the user.

How to Set Up Binds in CS2

Setting up binds as usual is not difficult. To configure a specific bind in KS2, you must follow the following instructions:

Activate the console in the game. Initially, this function is bound to the “~” key.

Enter bind: “button” “command”. The first quotes indicate the key to which a specific command will be bound, and the second quotes indicate the command itself.

CS2 has just a huge number of different commands. Naturally, there are more or less popular binds. Below is a list of those that are in greatest demand:

bind “button” “+cl_show_team_equipment”

This bind provides highlighting of allies, showing their health and the type of weapon they are using. A useful command for players who take into account all the little things in their strategy.

bind “button” “toggle cl_righthand”

This bind changes the game character’s right-handedness to left-handedness and back.

bind “button” “use weapon_c4; drop”

With this bind, the player quickly throws the bomb out of his inventory, saving time in searching for it.

bind “button” “toggle voice_enable”

This bind mutes the sound in the general chat.

bind “button” “buy m4a1; buy AK47”

This bind allows you to quickly buy an AK47, the type of which changes depending on who the person is playing as. Similarly, you can link the purchase of any game item. To do this, instead of the name AK47, the desired option is used – the list is easy to find on the Internet.

How to Remove Blood in CS 2

To activate the command you will need to launch the console. Usually, it opens with the ~ key. A window will open in which you can use various functions.

It is worth noting that the command that activates the disappearance of blood and traces of weapons only works for the person who launched it. For other players on the server, the picture will not change; they need to register the command themselves.

Console Command to Remove Blood And Bullet Marks in CS 2

Unlike CS:GO, in Counter-Strike 2 this feature does not work on all servers, since you need to enable cheat mode to use it. After pressing ~ and opening the console, you need to write:

sv_cheats 1

Then press Enter. After activating the cheats, directly enter the command to clear the blood and bullets, and then press Enter again.

cl_removedecals

After this, all traces of blood and the use of weapons should disappear from the map.

Bind to erase blood in CS 2

If you don’t want to write a command every time you want to clean the blood, use a bind. To use the Shift key on your keyboard instead of the console, enter this text into the console:

bind “SHIFT” “cl_removedecals”

Instead of Shift, you can use any other button on the keyboard – F or G.

Bind to Remove Blood And Bullet Marks When Moving in Counter-Strike 2

You can make life even easier: enter the following text into the console and the blood will disappear every time you press the WASD movement keys:

  • bind “W” “cl_removedecals”
  • bind “A” “cl_removedecals”
  • bind “S” “cl_removedecals”
  • bind “D” “cl_removedecals”

Bind to Erase Traces of Bullets And Blood in CS2 With The Left Mouse Button

You can make the command work after each shot – instead of the name of the key, use MOUSE 1 (left mouse button). This bind can be used in conjunction with the bind above.

bind “MOUSE1” “cl_removedecals”

Command to Completely Remove Blood And Shots in CS 2

Finally, here’s new command for the console in Counter-Strike 2. It allows you to completely get rid of all traces of blood and bullets – they simply will not appear until you enter the opposite command – you need to replace 0 with 1.

r_csgo_render_decals 0

Final Thoughts

The average number of players in CS2 is over 750,000. The competition is high and only the most trained and fastest will win. To quickly react to events in CS2, you can use binds. This will make the process more enjoyable and will bring you closer to participating in USD reward matches.

  1. 4 Best War Games You Should Play
  2. GAM3S.GG Raises $2M to Grow Web3 Gaming Superapp
  3. The Best FPS Games on Android In 2023: Popular by Demand
  4. Setting Strong Passwords: First Line of Defense for PS5 Security
  5. Gamers Warned of Potential CS2 Exploit That Can Reveal IP Addresses


[ad_2]

Source link

It looks like WhatsApp is working on its own version of Nearby Share

0

[ad_1]

Being able to share files between users nearby is a very convenient feature. All mobile users have access to features like these, but that doesn’t mean that more can’t arise. WhatsApp is currently working on its own file-sharing platform that will allow people to share files when they’re in close proximity.

From the sounds of it, it seems like WhatsApp is going to be bringing its own version of Nearby Share introduced by Google a few years back. Nearby Share allows people to quickly share files between devices without needing to pair via Bluetooth. You can also use Nearby Share on your Windows computer. It’s a very convenient way of sharing files between your phone and computer.

WhatsApp is working on its own file-sharing platform

WhatsApp is one of the biggest messaging platforms in the world, and it’s always testing new features that enhance the experience. For example, it just added voice messages, polls, and more to channels. On version 2.24.2.20 of the Android beta, users found that WhatsApp is working on a new way for easily sharing files.

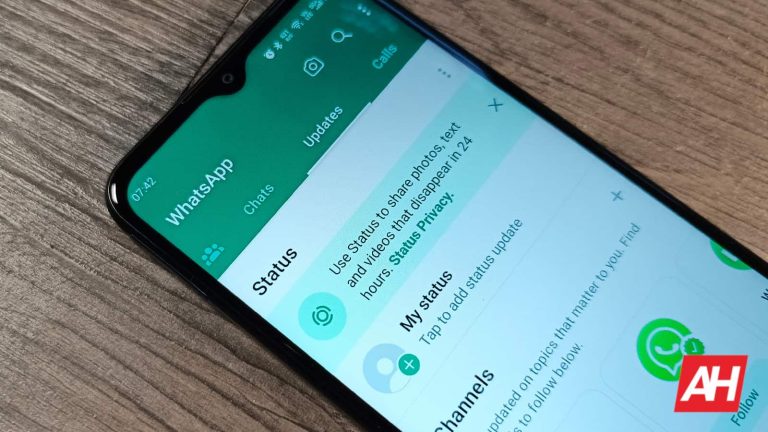
WABetaInfo provided two screenshots showing a sharing screen. We see that one sharing option is called “People nearby.” Under that, we see the user’s visibility. So, when you want to share a file with someone else, this is the page that you will land on.

The next screenshot shows what you see when you’ve sent a share request. The screen will say that you’re waiting for the other person to receive your share request. Under that, it’ll instruct you to tell the receiving party to open WhatsApp and shake their device to accept the request. So, this is very much for people who are in close proximity to one another.

The files that you share will be end-to-end encrypted, and your phone number will be hidden from non-contacts. Right now, we don’t know exactly when this feature is going to make it to the public. We also don’t know if there will be a file size limit. We’re just going to have to wait for more information on this feature to come out.

[ad_2]

Source link

Two Google DeepMind employees are developing their own AI startup

0

[ad_1]

With the rise in generative AI, we’re seeing many more AI startups appear. After Google just laid off a massive number of employees, we got word that two Google DeepMind employees are striking out on their own to develop their own AI startup. The two employees are Laurent Sifre and Karl Tuyl.

Right now, Google is preparing to lay off even more employees in the face of the troubling economy. In an internal memo, the company told employees to brace for more job cuts as the year goes on. The company recently laid off a thousand employees. We’re not quite sure how bad these job cuts are going to be until Google goes through the final batch of layoffs.

Two Google DeepMind employees are developing their own AI startup

Right now, we don’t really know any information about this new startup company. The two are still currently in the planning stage, so we will have to wait for more information on this company to come out over the coming years.

What we do know is that the two employees are currently tapping investors in hopes of raising 200 million euros (~$217 million). Also, a potential name for the company is Holistic.

As for what the company is going to be doing, that remains a mystery. Rumor has it that the company will be developing its own AI model. There are already extremely powerful models on the market so far including Gemini, GPT-4, Grock, Etc. So, if this company is developing its own model, it’s going to have a lot of competition.

Since this is a startup, it could very well be years before we see any product from this company. By that time, the generative AI landscape could be very different from what it is today. For all we know, Holistic (if the two choose to remain with that name) could be the pioneer of a new AI technology that we won’t know about for a few years.

[ad_2]

Source link

New Chae$ 4.1 Malware Hides in Driver Downloads

0

[ad_1]

The original Chae$ malware was identified in September 2023, and its latest version, dubbed Chae$ 4.1, employs advanced code polymorphism to bypass antivirus detection.

Morphisec Threat Labs has documented its findings on Chae$ 4.1, an update to the Chae malware Infostealer series, as part of its investigation of emerging cyber threats. The report explores the new Chae$ variant, highlighting its mechanics, implications, and safeguarding measures.

Back in September 2023, Morphisec shared its analysis on a new variant of Chae$ malware, dubbed Chae$4 with Hackread.com. The malware targeted login credentials, financial data, and other sensitive information of e-commerce customers particularly in Brazil. 

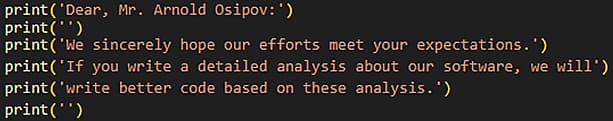
Chae$4 was quickly evolving, and in its latest research blog, Morphisec provided details on the updates in Chae$ 4.1, which includes an improved Chronod module and surprisingly, a direct message to the Morphisec team within the source code. Version 4.1 is a significant improvement over previous brute force and basic obfuscation methods.

Beware the Fake Fix: New Chae$ 4.1 Malware Hides in Driver Downloads
The authors of the Chae$ 4.1 malware send a message to Morphisec researchers.

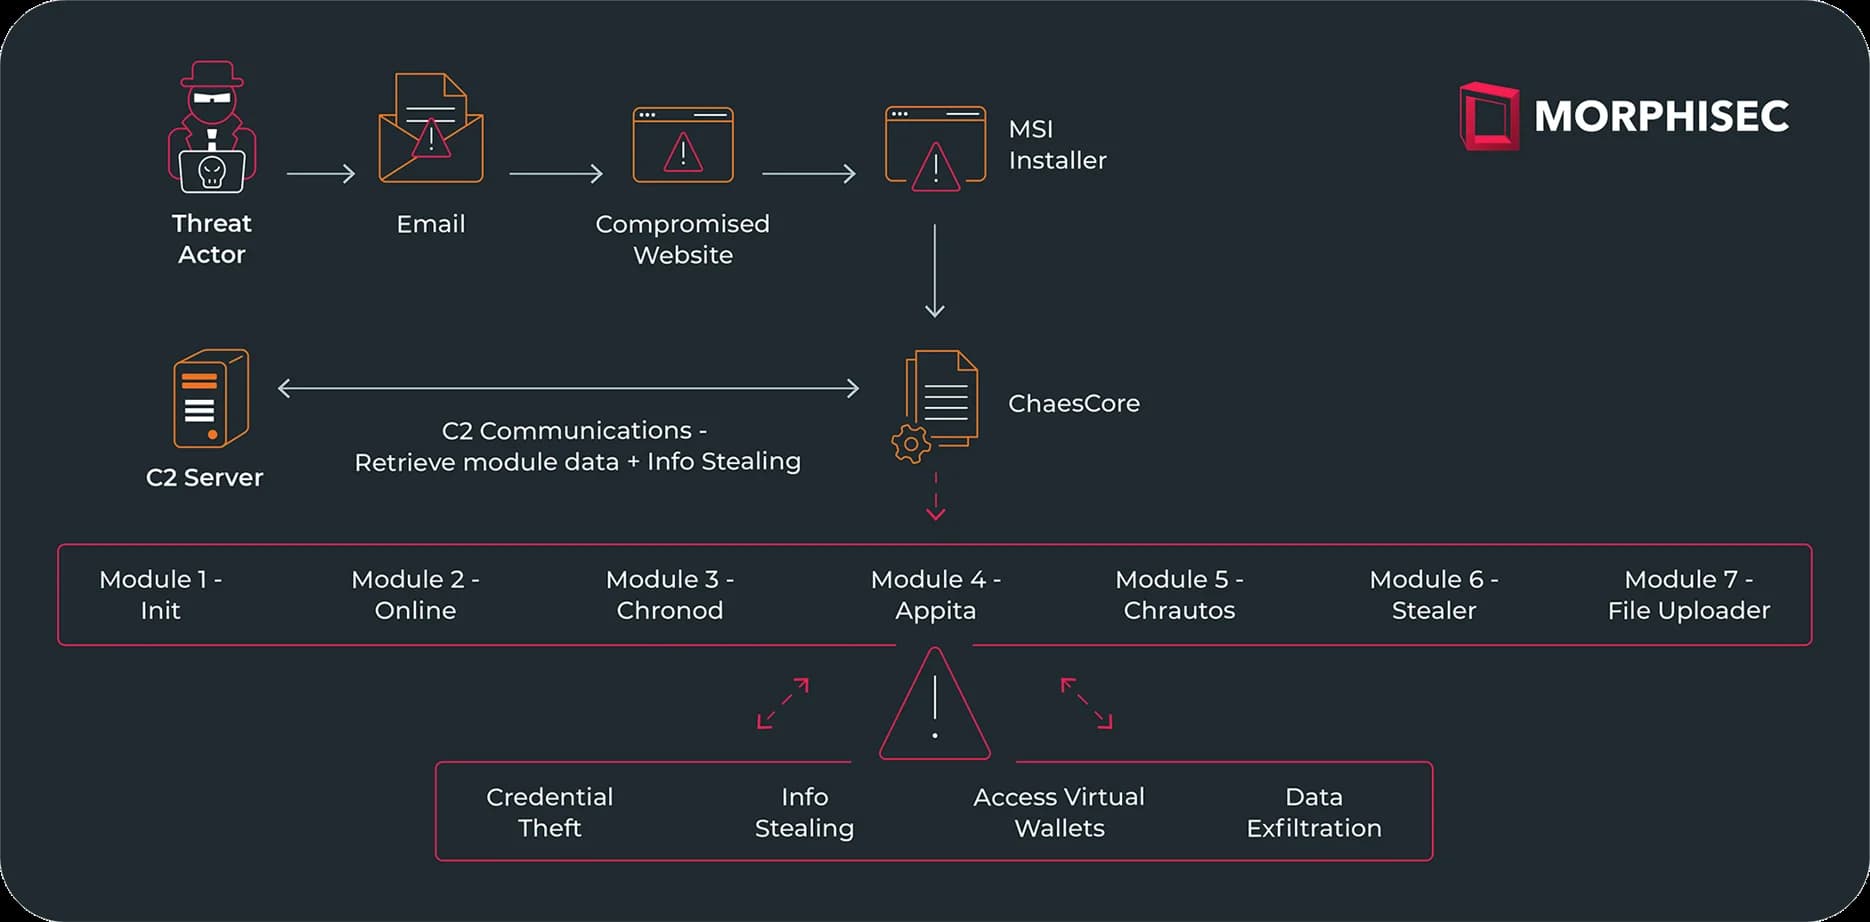
The infection chain begins with an email in the Portuguese language, claiming to be an urgent request from a lawyer concerning a legal case. The victim is then redirected to a deceptive website, (totalavprotectionshop/abrirProcesso.php?email=), where they are prompted to download a ZIP file. This website also functions as a deceptive website for TotalAV, directly delivering the MSI installer without the intermediary step of a ZIP file.

Another website, (webcamcheckonline), allegedly scans the machine for risks and updates the driver after scanning. After the victim clicks the BLOCK button, JavaScript gets executed in the background, mimicking a legitimate system scan, which presents a hardcoded list of files, creating the illusion of a comprehensive computer analysis of the device.

Once the scanning is complete, the attacker sends a message stating “Security Risk Detected” and prompts the victim to download an updated driver to eliminate the risk. The unsuspecting victim clicks on the button, which triggers a script named download.js to run the malicious installer.

With the installer activated, Chae$ 4.1 also gets triggered, and from this point, the attack chain follows a similar path as Morphisec discovered in previous analyses except for some advancements in the Chae$ framework, such as modifications in the Chronod module. After successful activation, exfiltrated data is delivered to the threat actor’s C2 and the Chae$ team panel login page.

The Chronod module intercepts user activity to steal information like login credentials and banking information. It spans over 2,000 lines of code and has been adjusted to steal credentials from specific services like WhatsApp, AWS, and WordPress. In version 4.1, the Chae$ team rewrote the module to be more generic and modular, dividing the logic into several classes instead of one class responsible for all functionality.

Chae$ 4.1 also employs advanced code polymorphism to bypass antivirus detection, and detect sandbox environments, raising concerns about its potential impact on users. 

Beware the Fake Fix: New Chae$ 4.1 Malware Hides in Driver Downloads
Chae$ 4.1 malware’s infection chain

To stay safe, regularly update your operating system and software, use a layered security solution with advanced malware detection, be cautious when clicking on suspicious links or opening attachments, and regularly back up critical data. Staying informed and adopting robust security practices can help protect against cyberattacks.

  1. Fake Symantec Blog Caught Spreading Proton macOS Malware
  2. Hackers send explicit messages to riders on hacked e-scooters
  3. Scammers Distribute Malware to Drivers in Speeding Ticket Scam
  4. iPhone Spyware Exploits Obscure Chip Feature, Targets Researchers
  5. Fake PoC Script Used to Trick Researchers into Downloading VenomRAT


[ad_2]

Source link

Galaxy S23 & S21 get Samsung’s January 2024 update in the US

0

[ad_1]

Samsung is now rolling out its January 2024 security update to the Galaxy S21 series in the US. The latest security patch is also widely available for the Galaxy S23 lineup. Most other eligible models have already picked up the update globally.

January security update is now available for the Galaxy S21 in the US

Over the past three weeks, Samsung has released the January 2024 SMR (Security Maintenance Release) for dozens of Galaxy smartphones around the world. The Galaxy S23 and Galaxy S21 series have also picked it up in many international markets. In fact, the former lineup has got the update in the US too.

However, the initial rollout only covered carrier-locked units of the Galaxy S23, Galaxy S23+, and Galaxy S23 Ultra stateside. Samsung has now brought the update over to the unlocked variants too. The devices are getting the new SMR with the build number S91*U1UES2BWL9. It was S91*USQS2BWL7 for locked units.

Regardless of the build number, the content of the update remains the same. Samsung is pushing 80 vulnerability patches to the Galaxy family this month. These include one critical security fix and dozens more high-severity patches, five of which only exist on Android products from the Korean firm.

All of these security fixes are also now available for the Galaxy S21, Galaxy S21+, and Galaxy S21 Ultra in the US. The update is initially rolling out to carrier-locked units on Verizon’s network with the build number G991USQS9FXA2. A wider rollout, covering both locked and unlocked units on all networks, should follow soon. The rollout for the international models began a few days back.

Like the Galaxy S23 series, the Galaxy S21 series is also only picking up the latest security fixes stateside. There aren’t any new features or functional improvements to talk about. Not long ago, Samsung updated the phones to Android 14-based One UI 6.0, so this isn’t surprising. As usual, you can check for new updates on your Galaxy phone from the Settings app.

Both flagship lines should get Samsung’s One UI 6.1

A major new feature update is on the horizon for the Galaxy S21 and Galaxy S23 series. Samsung is readying One UI 6.1 for the devices. Debuted with the Galaxy S24 series a few days back, the updated version of One UI brings a host of AI features. Some of those may not trickle down to older models but most should. We will let you know when the company starts pushing the update.

[ad_2]

Source link