23andMe blames its users for the massive data breach

0
[ad_1]

In a lawsuit stemming from a data breach, DNA service provider 23andMe has drawn sharp criticism for its response letter, in which it attempts to pin the blame on the affected customers.

In October 2023, 23andMe, the popular DNA testing company based in Mountain View, California, experienced a data breach. During this incident, hackers exposed the personal information of more than 7 million customers.

Additionally, another hacker attempted to sell genetic records of 23andMe users for $100,000 for a bundle of 100,000 profiles. The information taken by the hackers in the data breach included the following details:

  • Names
  • Genders
  • Birth years
  • Ancestry reports
  • Some DNA data
  • Self-reported locations
  • Predicted relationships
  • Most recent login dates
  • Relationship labels (e.g., “mother,” “cousin”)
  • Health-related information based on genetic profiles
  • Percentage of DNA shared with DNA Relatives matches

As a consequence of the data breach, 23andMe is facing a lawsuit. In a letter filed in the Circuit Court of Cook County, the company attributed the data breach to customers themselves, contending that the breach occurred because users reused their login credentials.

Specifically, the company claims, users employed the same usernames and passwords on 23andMe as on other websites that had experienced previous security breaches. According to 23andMe, this practice and users’ failure to update their passwords after these incidents were unrelated to any security lapses on 23andMe’s part.

The letter also claims that threat actors could not have caused “pecuniary harm” as it lacked Personal Identifiable Information (PII) data, such as social security number, driver’s license number, or any payment or financial information.

“… unauthorized actors managed to access certain user accounts in instances where users recycled their own login credentials—that is, users used the same usernames and passwords used on 23andMe.com as on other websites that had been subject to prior security breaches, and users negligently recycled and failed to update their passwords following these past security incidents, which are unrelated to 23andMe.” “Additionally, the information that the unauthorized actor potentially obtained about plaintiffs could not have been set to cause pecuniary harm (it did not include their social security number, driver’s license number, or any payment or financial information).”

23andMe

It is worth noting that initially, 23andMe claimed only 14,000 accounts were directly compromised, stating the hackers used “credential stuffing“, meaning stolen login credentials from other websites were used to access 23andMe accounts. This led some to criticize the company for suggesting user negligence played a role in the breach.

However, further investigation revealed the attackers accessed information from a much larger number of profiles: 5.5 million DNA Relatives profiles and 1.4 million Family Tree profiles connected to the compromised accounts. While 23andMe still maintains the initial breach involved 14,000 accounts, this broader access to information fueled criticism that the company downplayed the severity of the incident.
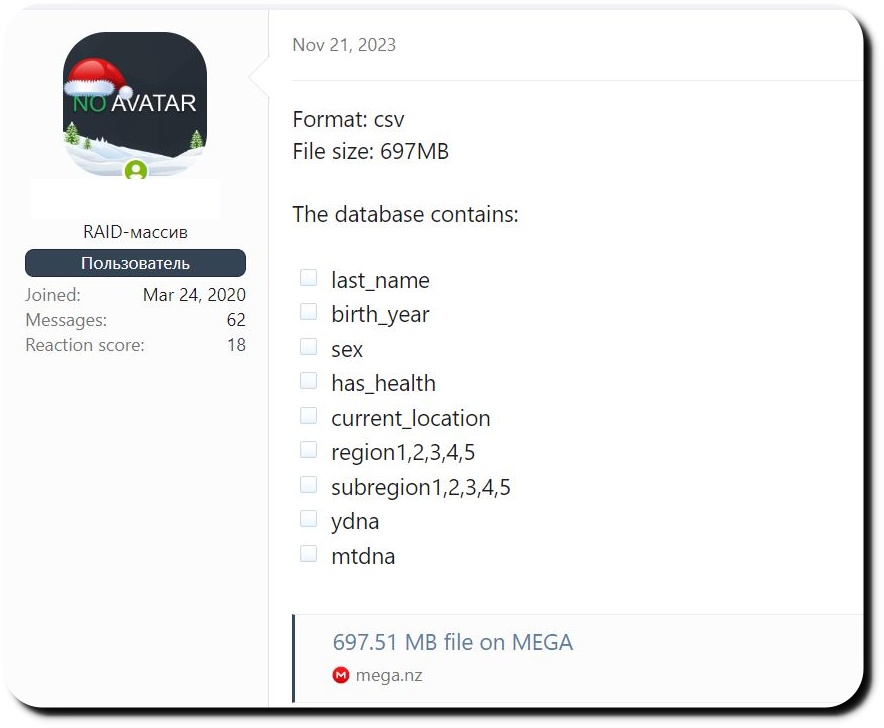
23andMe blames its users for the massive data breach
23andme leaked on a popular Russian hacker and cybercrime forum (Screenshot: Hackread.com)

It’s important to note that relying solely on passwords is considered a security vulnerability. This is why many experts advocate for two-factor authentication (2FA) as an additional layer of security. Interestingly, 23andMe introduced mandatory 2FA for all users after the breach, suggesting they acknowledged the password-only system wasn’t sufficient.

For insights into 23andMe’s claims, we reached out to Nick Rago, Field CTO at Salt Security, adds:, who emphasised that, “In this age of sophisticated social engineering attacks, any claim that a data breach can not cause “pecuniary harm” because it did not consist of social security numbers, driver’s license number, or credit card data has to be done tongue in cheek.”

Nick countered 23andMe’s version of things explaining hackers do not require PII data to harm unsuspecting users, especially with the emergence of deepfake and AI technologies. Nick also warned that revealing genealogy or relationship details can aid attackers in constructing targeted social engineering attacks on both small and large scales.

“Exposing any genealogy or relationship information would be quite useful to an attacker when building a targeted social engineering attack, whether it be targeted at scamming a consumer, stealing an identity, or as a phase of a more sophisticated attack campaign, such as getting privileged system access in a corporate infrastructure,” said Nick.

Erfan Shadabi, Cybersecurity Expert at comforte AG, told Hackread.com, “Attributing the entirety of blame to users is a flawed argument that oversimplifies the complex landscape of cybersecurity. While it is true that users must follow best practices for account safety, companies also must protect the sensitive information that has been entrusted to them. It is admirable that 23andMe has taken the recent step of requiring two-factor authentication (2FA) to strengthen defences against credential-stuffing attacks.”

  1. DNA testing website MyHeritage hacked; 92M user accounts stolen
  2. Researchers Encode Physical DNA with Malware to Infect Computers
  3. Software firm leaks 25GB worth of subscription, Ancestry.com user data

[ad_2]
Source link

Official Galaxy Xcover 7 renders show all of its sides

0
[ad_1]

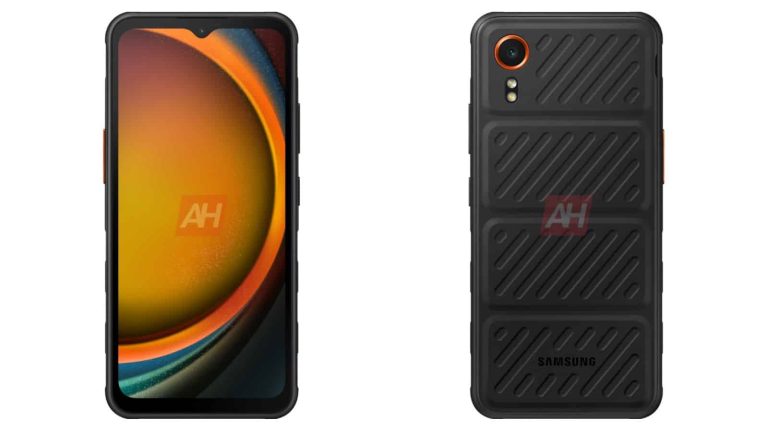
In early November, we exclusively revealed the design of the Galaxy Xcover 7, Samsung’s upcoming rugged smartphone. We now have another set of exclusive official renders of the device to share with you courtesy of our trusted, confidential source. The new renders show the handset from more angles and include the official wallpaper for the phone.

Samsung Galaxy Xcover 7 new official renders

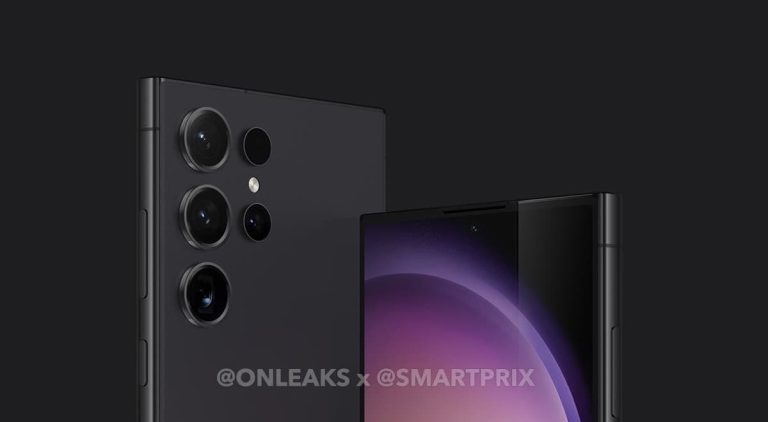
The latest Galaxy Xcover 7 renders reveal that Samsung will ship the device with a default wallpaper inspired by the Galaxy S23’s wallpaper. With the screen lit, we can now see its front design more clearly. Since we are talking about a rugged phone, there are thick bezels around the display with a U-shaped notch at the top. There’s a raised bumper along the edges to protect the screen during falls. The display itself should have a protective layer on top.

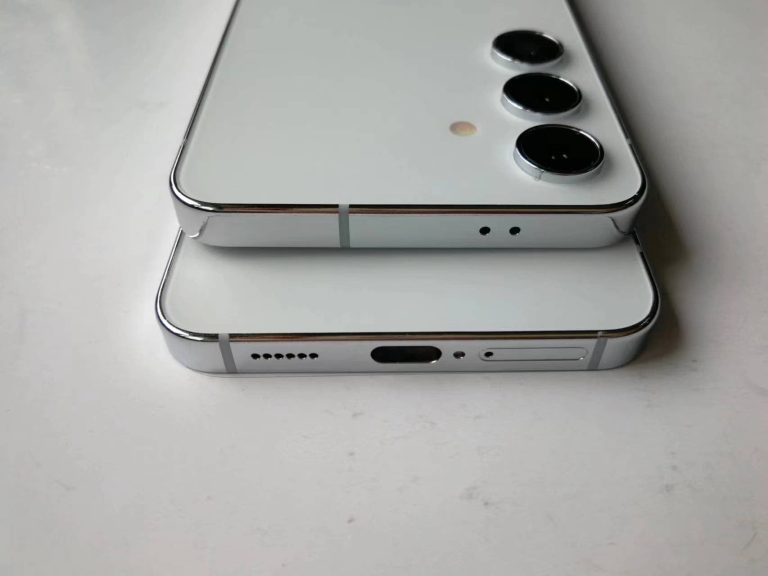
The back panel of the phone is user removable, and so should be the battery. Samsung has created grooved patterns on the cover for a stronger grip. The Galaxy Xcover 7 has a single camera on the back with a copper-colored ring around the lens. A dual LED flash unit sits below the camera. The edges of the phone also have a rugged design. The customizable action key on the left side has a similar copper-colored accent.

Those familiar with Samsung’s Xcover lineup already know that this key can be customized to execute any function. You can assign it to open an app or launch some other feature. On the other side of the phone are the power and volume buttons. The top edge has a 3.5mm headphone jack and a microphone hole. There’s another microphone hole at the bottom, sitting alongside a USB Type-C port and a speaker.

We can also see two golden pins at the bottom of the Galaxy Xcover 7. This means the device will support charging over Pogo pins in addition to USB-C. It appears to lack a fingerprint scanner, though. We don’t expect Samsung to include an under-display solution while there is no physical scanner to be found in the renders we have today. The power button seemingly doesn’t incorporate one. We don’t have a confirmation, though.

Samsung will launch the new rugged phone soon

The Galaxy Xcover 7 may not remain under wraps for much longer. Leaks have already revealed most of its key specs. The device features a 6.6-inch display with an FHD+ resolution. We expect an LCD panel with a 120Hz refresh rate and a Corning Gorilla Glass Victus+ protective layer. Under the hood, we might get MediaTek’s 5G-enabled Dimensity 6100+ chipset paired with 6GB RAM and 128GB storage.

The device is fueled by a 3,950mAh battery with 25W fast wired charging. It boasts NFC, Wi-Fi 5, and Bluetooth 5.3 and will run Android 14 out of the box. The handset should come with MIL-STD-810H-grade ruggedness, IP68 dust and water resistance, and drop-to-concrete resistance. It’s rumored to cost €379 or around $400. Samsung may launch the Galaxy Xcover 7 alongside the Galaxy Tab Active 5 over the next few months.


[ad_2]
Source link

Google Files’ ‘Important’ tab will be removed after February 15, 2024

0
[ad_1]

Google will retire the ‘Important’ tab feature in its Files by Google app available on both Android and iOS soon. Introduced last year and exclusively available for devices in India, the ‘Important’ tab scans users’ phones to identify crucial documents such as passports, IDs, and other essential files.

This ‘Important’ tab feature inside Files by Google aligned well with the Indian government’s DigiLocker service. However, Google will remove this feature from the app in the next update scheduled for February 15, 2024. Users should make copies of their important files before the tab’s discontinuation.

Users of the ‘Important’ tab in Google Files can leverage the share option in the Files app

As noted by an APK Insight post from 9to5Google, a notice inside the app informs about the removal of the ‘Important’ tab, emphasizing that the feature will no longer be available after February 15, 2024. It further states, “Your saved documents in the ‘Important’ tab will be permanently deleted from Files after this date. To save a copy of your documents, use the Share option to do so before 15 February 2024.”

Users who have utilized the ‘Important’ tab feature should take note that they will no longer have access to all files stored under this category inside the Files app after the specified date. To safeguard their crucial documents, users can create copies before the impending removal. Google suggests utilizing the ‘Share’ option within the app to create copies of the stored documents inside the ‘Important’ tab.

In an effort to prevent users from losing their important documents, Google will also send out notifications to users, informing them about the impending shutdown of the ‘Important’ tab inside Files by Google. The notification may look something like “Files is removing the Important tab. Your saved documents in the Important tab will be deleted after 15 February 2024”


[ad_2]
Source link

Google Bard could get an upgrade (and a price tag)

0
[ad_1]

2023 was the year of AI for Google, and it saw the introduction of Google Bard. We’ve known for a while that Bard was going to be powered up by Gemini, and now we have more information on that. According to a leak on X (formally Twitter), Google is working on a chatbot called Bard Advanced, and it looks like it will not be free to use.

We have everything you need to know about Google Gemini, so it can answer any questions you may have. Also, if you’re confused about how Google Bard and Gemini are different, you can read up on that. It’s important to know how these products differ, as Google unveiled both of them in the same year.

Google is working on Bard Advanced, and it likely will not be free

Bard has been up for some time, and Google has powered up many of its services using it. However, in December, we were introduced to Bard powered by Gemini. This version of the chatbot uses the Gemini Pro LLM (large language model). This version is currently available and free to use.

However, the most advanced version of Gemini is called Gemini Ultra, and this model has the ability to generate images and audio along with text. It’s absolutely gigantic, and it’s in competition with OpenAI’s GPT-4 model. Gemini Ultra is currently not available at the moment, but Google did tease a January release.

Well, it appears that Google is going to power up Bard using Gemini Ultra, and it could be named Bard Advanced. So, Bard Advanced might be able to generate images and music. However, that remains to be seen.

Based on the code in Google Bard, as discovered by Bedros Pamboukian on X, Bard Advanced will cost money to use. Within the code, we see the text ” try Bart Advanced for 3 months, on us”. This means that you’ll have to pay for the service after a 3-month trial.

Also in the code, we see a non-functioning Google One link. This points to the fact that you may be required to have a Google One subscription to use Bard Advanced. This is similar to how you’re required to have an X Premium+ subscription to use Grok.

Right now, we don’t know the price for Bard Advanced so we’ll have to wait for more information to know for sure.


[ad_2]
Source link

WhatsApp could let you show your verification badge on your channels

0
[ad_1]

Right now, Meta is working on bringing WhatsApp to Meta Verified. The company has been testing several changes in the app that point to this. According to a new report, WhatsApp will eventually let you add your verification badge to your new channels.

If you don’t know what Meta Verified is, here’s a quick rundown. Meta owns Facebook, Instagram, and WhatsApp. All three of these platforms have their own set of features and perks. However, if you want to unlock additional perks, you can get a Meta Verified subscription. This adds additional perks to these platforms like a verified badge confirming your authenticity, a boost in the algorithm, and more. You can read everything you need to know about Meta verified to get more information.

WhatsApp could let you add your verified badge to your new channels

It shouldn’t come as a surprise that WhatsApp wasn’t initially offered with Meta-verified, as it has a premium business subscription tier. However, back in September, Meta announced that it was working on bringing WhatsApp over. The company is currently testing this capability. When WhatsApp does eventually land on Meta Verified, it will only be for business accounts. So, personal accounts will not be verified.

While WhatsApp is not currently part of the verified crew, the company will eventually let you show your verification status in your channels. You can’t imagine, this only applies to channels created by business accounts.

As spotted in the latest beta version of WhatsApp for Android, WhatsApp will let you show your verification badge on your channels. Since this is a leak from a beta version of the app, you may want to take this news with a grain of salt. There’s no telling if WhatsApp will introduce this feature.

Being able to show your verification status for your channels is a great feature because, if you are following a business accounts Channel, you will want to trust that the business is legitimate. Well, a verification badge is a way of showing legitimacy. Verified accounts are much more trusted than unverified accounts.

Whatsapp chennel badge

At this point, we don’t know when Meta will roll this feature out, but we imagine that it will launch when WhatsApp officially lands on Meta Verified. So, we will just have to wait and see


[ad_2]
Source link

23andMe blames “negligent” breach victims, says it’s their own fault

0
[ad_1]

In a surprising move, in a letter to legal representatives of victims of the recent 23andMe data breach, the company has laid the blame at the feet of victims themselves.

23andMe even goes as far as to claim that this wasn’t a data breach at 23andMe at all. The reasoning:

“… unauthorized actors managed to access certain user accounts in instances where users recycled their own login credentials—that is, users used the same usernames and passwords used on 23andMe.com as on other websites that had been subject to prior security breaches, and users negligently recycled and failed to update their passwords following these past security incidents, which are unrelated to 23andMe.”

In other words, it was their own fault since they re-used their passwords for services that were breached in the past. Accessing accounts on a website by using lists of usernames and passwords exposed on another is known as “credential stuffing”, and it’s both common and effective. It works because users often use the same password for multiple websites.

What 23andMe seems to have forgotten is that only 14,000 accounts were breached by credential stuffing. Afterwards, the attackers used those accounts to access a much larger trove of data via 23andMe’s feature called DNA Relatives which matches users with their genetic relatives.

So, in what was only made possible by 23andMe, customers who didn’t re-use their passwords and even had 2FA enabled still saw their data stolen. This resulted in the data of as many as seven million 23andMe customers being offered for sale on criminal forums.

We spoke about the breach in our most recent Lock and Code podcast episode. You can listen to that wherever you get your podcasts, or below:

This is the second time the company has attempted to downplay the incident. In its first communication about the incident, 23andMe claimed the stolen data did not include genomic sequencing data.  Later, the company acknowledged that for a subset of these accounts, the stolen data might indeed contain health-related information based upon the user’s genetics.

The data in a file found by BleepingComputer contained information including 23andMe users’ account IDs, full names, sex, date of birth, DNA profiles, location, and region details.

As a result, at least four class action complaints were submitted in California seeking relief for the damage done by 23andMe’s failure to protect customer data. The lawsuits focus on different failures on 23andMe’s side to guard the safety of sensitive data, communicate appropriately about the incident, and monitor its network for abnormal activity.

In its defense, 23andMe reasons that customers re-used their passwords, gave permission to share data with other users on 23andMe’s platform, and that the medical information was non-substantive.

I put the emphasis on “other users” in order to point out a flaw in 23andMe’s reasoning—agreeing to share with other users is hardly the same as agreeing to share with a data thief. Without knowing the exact details of what happened, we feel that monitoring would indeed have raised alerts about abnormal activity and allowed them to stop the breach earlier. As it seems now, 23andMe only became aware of a problem when someone offered the data up for sale.

Whatever the judges may decide in the end, it’s looking like 23andMe has shown a lot of disregard for its customers’ privacy and the level of sensitivity of the data.

Data breach

There are some actions you can take if you are, or suspect you may have been, the victim of a data breach.

  • Check the vendor’s advice. Every breach is different, so check with the vendor to find out what’s happened, and follow any specific advice they offer.
  • Change your password. You can make a stolen password useless to thieves by changing it. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose one for you.
  • Enable two-factor authentication (2FA). If you can, use a FIDO2-compliant hardware key, laptop or phone as your second factor. Some forms of two-factor authentication (2FA) can be phished just as easily as a password. 2FA that relies on a FIDO2 device can’t be phished.
  • Watch out for fake vendors. The thieves may contact you posing as the vendor. Check the vendor website to see if they are contacting victims, and verify any contacts using a different communication channel.
  • Take your time. Phishing attacks often impersonate people or brands you know, and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.
  • Set up identity monitoring.Identity monitoring alerts you if your personal information is found being traded illegally online, and helps you recover after.

We don’t just report on threats – we help safeguard your entire digital identity

Cybersecurity risks should never spread beyond a headline. Protect your—and your family’s—personal information by using Malwarebytes Identity Theft Protection.


[ad_2]
Source link

New Galaxy S24 benchmark scores hint at optimized performance

0
[ad_1]

Days ahead of their official unveiling, Samsung’s Galaxy S24+ and Galaxy S24 Ultra have surfaced in new benchmark entries on Geekbench. While the listings don’t reveal any new information, the benchmark scores can be a talking point. The scores of both devices have improved over the past couple of months or so, particularly in the multi-core CPU tests. It appears Samsung has optimized the software ahead of the market debut.

Galaxy S24 benchmark scores surge ahead of launch

We have long known that Samsung will ship the Galaxy S24 phones with two different chipsets. The Ultra model will arrive with an overclocked version of Qualcomm’s Snapdragon 8 Gen 3 processor globally. The other two models will also get the Snapdragon chip in the US, Canada, China, and a few other markets. However, they will be powered by Samsung’s in-house Exynos 2400 processor in the rest of the world.

Well, there are rumors of the Plus mode getting the Snapdragon in more markets than the vanilla Galaxy S24. But the gist is that they won’t exclusively feature the Qualcomm chip. Geekbench listings have already confirmed Samsung’s dual-chip strategy for these phones. While benchmarks never tell the full story, some early entries suggested a sub-par performance for the Exynos-powered Galaxy S24+ and Snapdragon-powered Galaxy S24 Ultra.

In one previous instance, the Plus model scored 2,067 in the single-core CPU test and 6,520 in the multi-core test. The Ultra scored 2,234 and 6,807, respectively. These scores aren’t the best in the segment. Thankfully, the devices are capable of delivering a better performance than that. In recent Geekbench runs, the Galaxy S24+ scored 2,193 and 6,895 while the Galaxy S24 Ultra scored 2,297 and 7,104, respectively.

As you can see, the scores have increased substantially, particularly the multi-core scores. If anything, this suggests Samsung’s continuous work on optimizing the software ahead of the launch. The Snapdragon chip still outperforms the Exynos but we are comparing two different phones. The Ultra is bigger and must have a more robust cooling system than the Plus. It’d be better to compare the Exynos and Snapdragon versions of the Galaxy S24+.

The new Samsung flagships are just around the corner

These benchmark entries for the upcoming Samsung flagships come just ahead of their official unveiling. The Korean behemoth has scheduled the launch event for January 17. All three models will debut on the same day and will be available for pre-order shortly, at least in most major markets. Samsung hasn’t announced pre-order benefits but we expect a free memory upgrade and some discount coupons.


[ad_2]
Source link

Free Decryptor Released for Black Basta Ransomware

0
[ad_1]

A vulnerability in the encryption algorithm used by the Black Basta ransomware has led researchers to develop a free decryptor tool.

Active since April 2022, the Black Basta ransomware group employs a double extortion strategy, encrypting the vital servers and sensitive data of their victims and threatening to reveal the sensitive information on their public leak site.

Since the beginning of 2022, the criminal group has received at least $107 million in Bitcoin ransom payments. Over 329 victims have been affected by the ransomware gang, according to the experts.

A free decryptor has been offered by independent security research and consulting company SRLabs to assist victims of the Black Basta ransomware in getting their files back.

How Can the Files Be Recovered?

Researchers claim that if the plaintext of 64 encrypted bytes is known, data may be recovered. The size of a file determines whether it may be recovered entirely or partially. Files with less than 5000 bytes in size cannot be restored. 

Complete recovery is achievable for files ranging in size from 5000 bytes to 1GB. The first 5000 bytes of files larger than 1GB will be lost; however, the remaining bytes can be restored.

“The recovery hinges on knowing the plaintext of 64 encrypted bytes of the file. In other words, knowing 64 bytes is not sufficient in itself since the known plaintext bytes need to be in a location of the file that is subject to encryption based on the malware’s logic of determining which parts of the file to encrypt”, the researchers said.

It is possible to know 64 bytes of plaintext in the correct location for several file types, particularly virtual machine disk images.

Researchers developed various tools to aid in analyzing encrypted files and determining whether decryption is feasible.

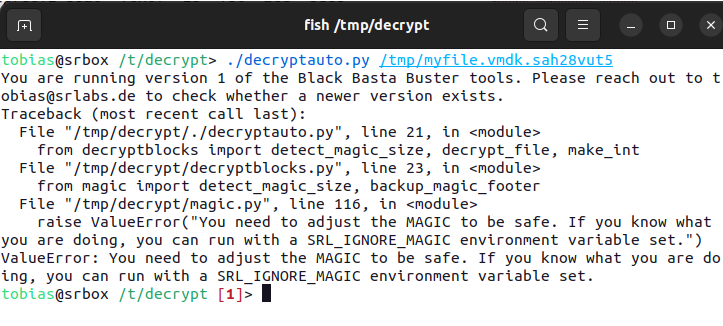
The decrypt auto tool may recover files containing encrypted zero bytes. Manual review may be required depending on how often and to what extent the malware has encrypted the file.

Decrypting file with the decryptauto.py tool

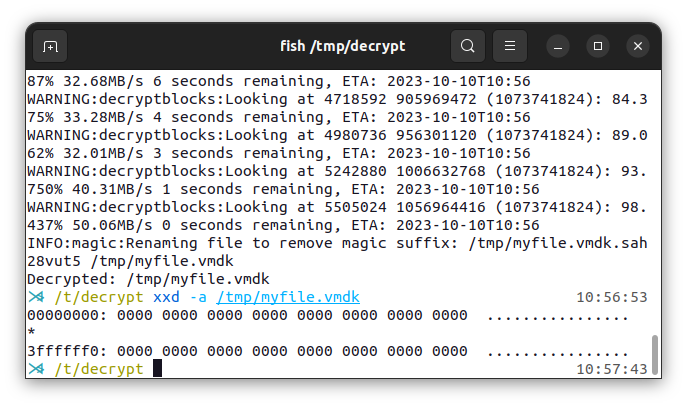
Researchers say a magic byte sequence that is not included in the encrypted file is left by the malware at the end. The file only has zero bytes after the tool has finished running. Thus, the file has been successfully decrypted.

The file successfully decrypted

Depending on the file size, the first 5000 bytes are used correctly by the keystream. Stated otherwise, those bytes—aside from the initial 64—will be lost.

Researchers say, “Virtualized disk images, however, have a high chance of being recovered because the actual partitions and their file systems tend to start later.

So the ransomware destroyed the MBR or GPT partition table, but tools such as “testdisk” can often recover or re-generate those.”


[ad_2]
Source link

Facebook introduces another way to track you – Link History

0
[ad_1]

In what seems like yet another attempt to adapt its platform to prepare for new regulations, Facebook has started rolling out a new feature called Link History.

Link History allows users to view and re-visit links they have visited with their Facebook browsing activity.

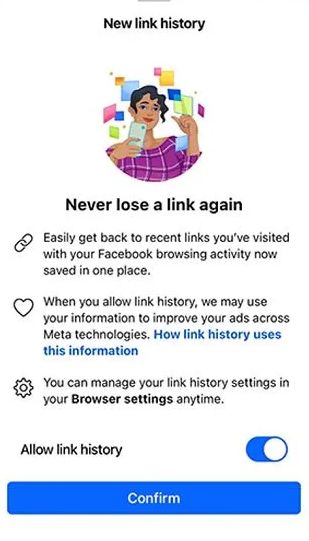
Link History prompt

Obviously Facebook will tell us that the new feature is for its users’ benefit, but we can see several ways in which this benefits Meta even more. The only positive for me is that it could be a handy option for finding that thing that you saw on Facebook that one time, but you can’t quite remember the details. This gets defeated partially by the fact that users that have Link History enabled report they were unable to see the Link History page at all when looking at Facebook on their laptop.

However, as Facebook tracking goes at least this is an option that you have some control over. On most, if not all, popular websites you’ll find Meta’s and other’s tracking pixels. With an ongoing battle against cookies and other trackers, this may be a new way for Facebook to track its user’s behavior.

With Link History, Facebook now has another separate place where it stores details about the websites you visit along with the settings to control that data. Settings that are, deliberately or not, hard to find and easy to misinterpret.

The company itself says:

“When you allow link history, we may use your information to improve your ads across Meta technologies.”

Translated, this means that they will use the information to provide you with targeted ads.

Recently Meta got sued over coercing users to pay to stop tracking. Organizations concerned about our privacy say that by doing this, Meta has changed the user’s choices from “yes or no” to “pay or okay.”

Research in 2022 showed that in-app browsers inject JavaScript code into third party websites that cause potential security and privacy risks to the user. This resulted in a class-action complaint against Meta in San Francisco’s federal court, alleging the company built a secret workaround to Apple’s safeguards that protect iPhone users from tracking.

So this may be another attempt to follow users around on the web. Unlike on your desktop, clicking a link in Facebook, or Instagram, will open a special browser built into the app, rather than the default browser of the device.

For now, a limited number of Android and iPhone users will see this option appear in the Facebook Mobile Browser. But the company says it will roll out the option globally over time.

Link history is turned on by default so you will have to opt-out if you don’t want it.

  1. Tap any link inside the Facebook app to open Facebook’s Mobile Browser.
  2. Tap the three dots (more actions) in the bottom right, then tap Go to Settings.
  3. To turn link history on, tap the slider to on (blue) next to Allow link history, then tap Allow to confirm.
  4. To turn link history off, tap the slider to off (grey) next to Allow link history, then tap Don’t allow to confirm. 

Note: When you turn link history off, this will immediately clear your link history, and you will no longer be able to see any links you’ve visited. Facebook promises to delete the link history it’s created for you within 90 days.


We don’t just report on privacy—we offer you the option to use it.

Privacy risks should never spread beyond a headline. Keep your online privacy yours by using Malwarebytes Privacy VPN.


[ad_2]
Source link

Galaxy S24 Ultra captures better 10x zoom photos, 8K videos at 5x

0
[ad_1]

After confirming the Galaxy S24 launch for January 17, Samsung has gotten down to the business of hyping up the new flagships. It is teasing new AI capabilities of the phones, including AI-powered cameras. The company touts unprecedented clarity in zoom shots thanks to artificial intelligence, particularly on the Ultra model. A fresh leak has shed more light on what Samsung has up its sleeves. The new zoom camera can record 8K videos.

Galaxy S24 Ultra can capture 8K videos at 5x zoom

Samsung has made a major change to the camera hardware of its Ultra flagship this year. In place of a 10MP 10x zoom camera, the Galaxy S24 Ultra has a 50MP 5x lens. Thanks to the new high-resolution sensor, the zoom camera can now record 8K videos at 5x magnification, X tipster Ahmed Qwaider revealed. The Galaxy S23 Ultra can only record 4K videos with its zoom camera.

While the 200MP main camera of the 2023 model can capture 8K videos, you lose quality when zooming in unless you settle for 4K resolution. So, this change seems to have brought improvements to the overall camera experience of Samsung’s top-of-the-line flagship. If you are worried about shorter optical zoom capabilities (5x instead of 10), Samsung is using AI to match 10x optical zoom quality with in-sensor crop from the 5x lens.

This is something we have heard from another reputed leakster, Ice Universe. In fact, they say the Galaxy S24 Ultra captures better 10x zoom shots than the Galaxy S23 Ultra. “Many people are pessimistic about the quality of 10x photos taken by S24 Ultra… I was pessimistic [too]… until I saw the comparison of samples,” the tipster said. The new flagship “definitely” takes better pictures at 10x zoom, they added.

The same X post from Ahmed Qwaider adds that Samsung’s Single Take function will work even at 10x zoom. Single Take captures multiple photos and short videos of a scene at once. You can check the results and keep the best shots. Additionally, the Galaxy S24 Ultra‘s 5x zoom camera will be available in Portrait Mode. So, if you want to capture a close-up portrait, the new Samsung flagship can do it for you.

Older Samsung flagships might get some new AI features

Camera enhancements aren’t the only applications of Samsung’s Galaxy AI built into the Galaxy S24 lineup. The company has also readied AI-powered photo and video editing tools, AI call translation in real-time, AI wallpapers, AI lockscreen effects, and more. Some of these features will be available offline, while others work online and require an internet connection. You may also have to sign in with a Samsung or Google account.

Samsung has baked these AI features into One UI 6.1, the new version of its custom software that will debut with the Galaxy S24 series. It will push the latest version to older flagships via a software update. It remains to be seen if the new AI features make it into those phones. The company may start rolling out the updates once the new flagships arrive on the market. Rumors suggest Samsung will open general sales of the Galaxy S24 lineup on January 30.


[ad_2]
Source link