OnePlus 12R twin is now official with powerful specs, great price

0
[ad_1]

The OnePlus 12R twin has just been announced in China. The device in question is, of course, the OnePlus Ace 3. The OnePlus 12R will be the same as the OnePlus Ace 3, but ship with software for global markets. That’s the only expected difference, in addition to perhaps different RAM + storage combinations. That being said, let’s see what the OnePlus Ace 3 has to offer.

The OnePlus Ace 3 is is now official, the OnePlus 12R twin

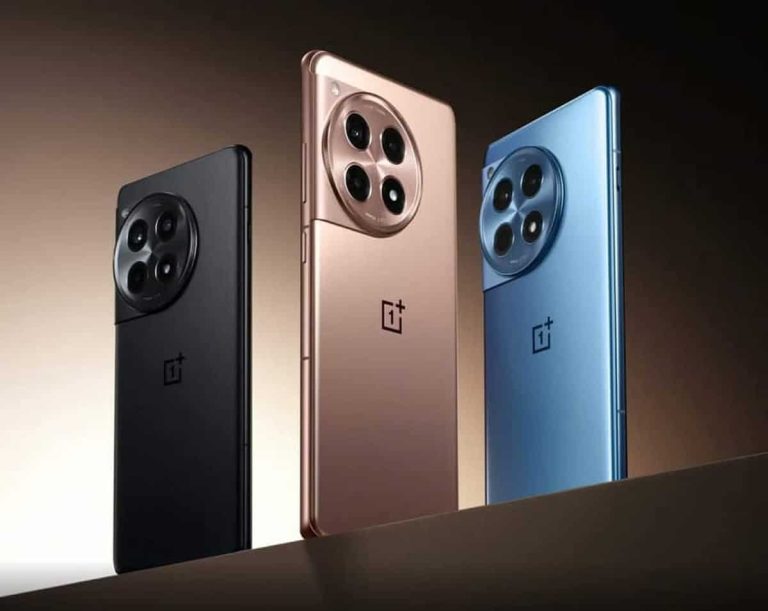
The rumors and leaks were more or less accurate. The OnePlus Ace 3 looks very similar to the OnePlus 12. You can notice the difference if you focus on the camera island on the back, but it’s not instantly obvious.

The phone features a curved display, with thin bezels, and a centered display camera hole. There are three cameras included on the back, inside a circular camera island, which is connected to the frame via a piece of metal.

A 6.78-inch 2780 x 1264 LTPO AMOLED panel sits on the front here. That panel goes from 1-120Hz as needed, and the peak brightness is set at 4,500 nits. This panel also offers a 2,160Hz high-frequency PWM dimming, and a 360Hz touch sampling rate. A 2,160Hz instant touch sampling rate is also in effect. The Gorilla Glass Victus 2 protects this panel.

The Snapdragon 8 Gen 2 fuels this smartphone, while 100W charging is supported too

OnePlus’ new smartphone is fueled by the Snapdragon 8 Gen 2, Qualcomm’s flagship SoC for last year. The phone was announced in 12GB and 16GB LPDDR5X RAM variants. 256GB, 512GB, and 1TB UFS 4.0 storage options are available.

OnePlus Ace 3 official image 1112

Android 14 comes pre-installed on the OnePlus Ace 3, along with ColorOS 14. A 5,500mAh battery is also included here, while the phone supports 100W wired charging. SuperVOOC charging is in effect here, and the charger is included in the package.

The OnePlus Ace 3 also includes stereo speakers and supports Dolby Atmos. It has an infrared sensor at the top, and an in-display fingerprint scanner as well. Bluetooth 5.3 is supported here, as is Wi-Fi 7. There are also two SIM card slots included (2x nano SIM).

There are three cameras on the back, with the emphasis on the main one

A 50-megapixel main camera (Sony’s IMX890 sensor, f/1.8 aperture, OIS) is backed by an 8-megapixel ultrawide camera (Sony’s IMX355 sensor, f/2.2 aperture), and a 2-megapixel macro camera (Howe OV02B sensor, f/2.4 aperture). A 16-megapixel selfie camera (Samsung’s S5K3P9 sensor, f/2.4 aperture) is also included.

The phone also includes a Tiangong cooling system with 9,140mm² VC vapor chamber. That should help the phone to stay cool at all times, even during gaming.

The OnePlus Ace 3 measures 163.3 x 75.3 x 8.8mm, and it weighs 207 grams. The device comes in Cool Blue, Gold, and Iron Gray color variants. The pricing starts at CNY2,599 ($365), and goes up to CNY3,499 ($492) in China. OnePlus will start selling this handset in China on January 8. The OnePlus 12R will launch on January 23 for global markets.


[ad_2]
Source link

Active Directory Infiltration Methods Employed by Cybercriminals

0
[ad_1]

Active Directory infiltration methods exploit vulnerabilities or weaknesses in Microsoft’s Active Directory to gain unauthorized access.

Active Directory is a central component in many organizations, making it a valuable target for attackers seeking access to:-

  • Sensitive information
  • User accounts
  • Network resources

While successful infiltration allows threat actors to:-

  • Establish persistence
  • Exfiltrate data
  • Disrupt operations

Cybersecurity researchers at ASEC recently discovered that threat actors are actively exploiting Microsoft’s Active Directory infiltration methods.

Document
Free Webinar

Compounding the problem are zero-day vulnerabilities like the MOVEit SQLi, Zimbra XSS, and 300+ such vulnerabilities that get discovered each month. Delays in fixing these vulnerabilities lead to compliance issues, these delay can be minimized with a unique feature on AppTrana that helps you to get “Zero vulnerability report” within 72 hours.

Active Directory Infiltration Methods

Active Directory (AD) in Windows manages user and resource data in a network. Domain Controllers control domains in AD, and compromising one means the entire domain is at risk. 

In short, the domain Admins have ultimate control, and this ability makes them prime targets for threat actors aiming to exploit the entire domain. 

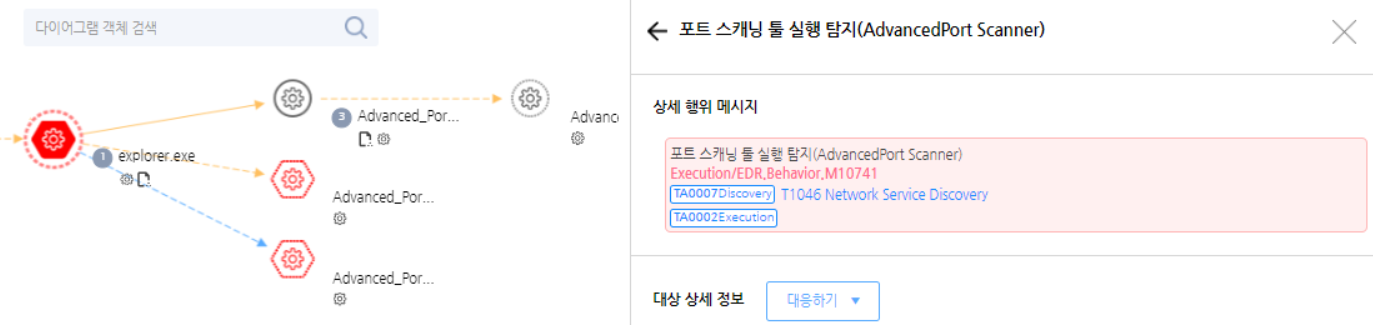
To achieve this, threat actors seeking vulnerabilities first analyze the domain structure using tools like:-

Port scanning extracts network info, including running services and port numbers from a target domain. Threat actors use it to uncover network structure, subnet, and host details. 

Cobalt Strike’s default port scanning aids reconnaissance. The tool checks security vulnerabilities in company networks. It encompasses features like:-

  • Internal reconnaissance
  • Privilege escalation
  • Lateral movement
  • Command and control
Log detecting a port scanning tool (Source - ASEC)
Log detecting a port scanning tool (Source – ASEC)

Default in Windows the net commands manage network resources that is useful for user and network data lookup, especially in Active Directory.

Threat actors seize control and then deploy net commands for basic network info collection. While the main net commands were used in attacks on Active Directory environments.

Here below, we have mentioned all the commands:-

  • net time
  • net user
  • net group /domain
  • net group /domain “Domain Admins”
  • net group /domain “Enterprise Admins”
  • net group /domain “Domain Computers”
  • net group /domain “Domain Controllers”
  • net localgroup Administrators

PowerView in PowerSploit gathers and displays Windows domain info that helps threat actors in:-

  • Understanding the network structure 
  • Targeting for privilege escalation 

AdFind is also similar to PowerView, which is a command line tool for Active Directory info that offers a stealthier approach. 

Ryuk ransomware employed AdFind to covertly collect domain data, surpassing typical anti-malware detection.

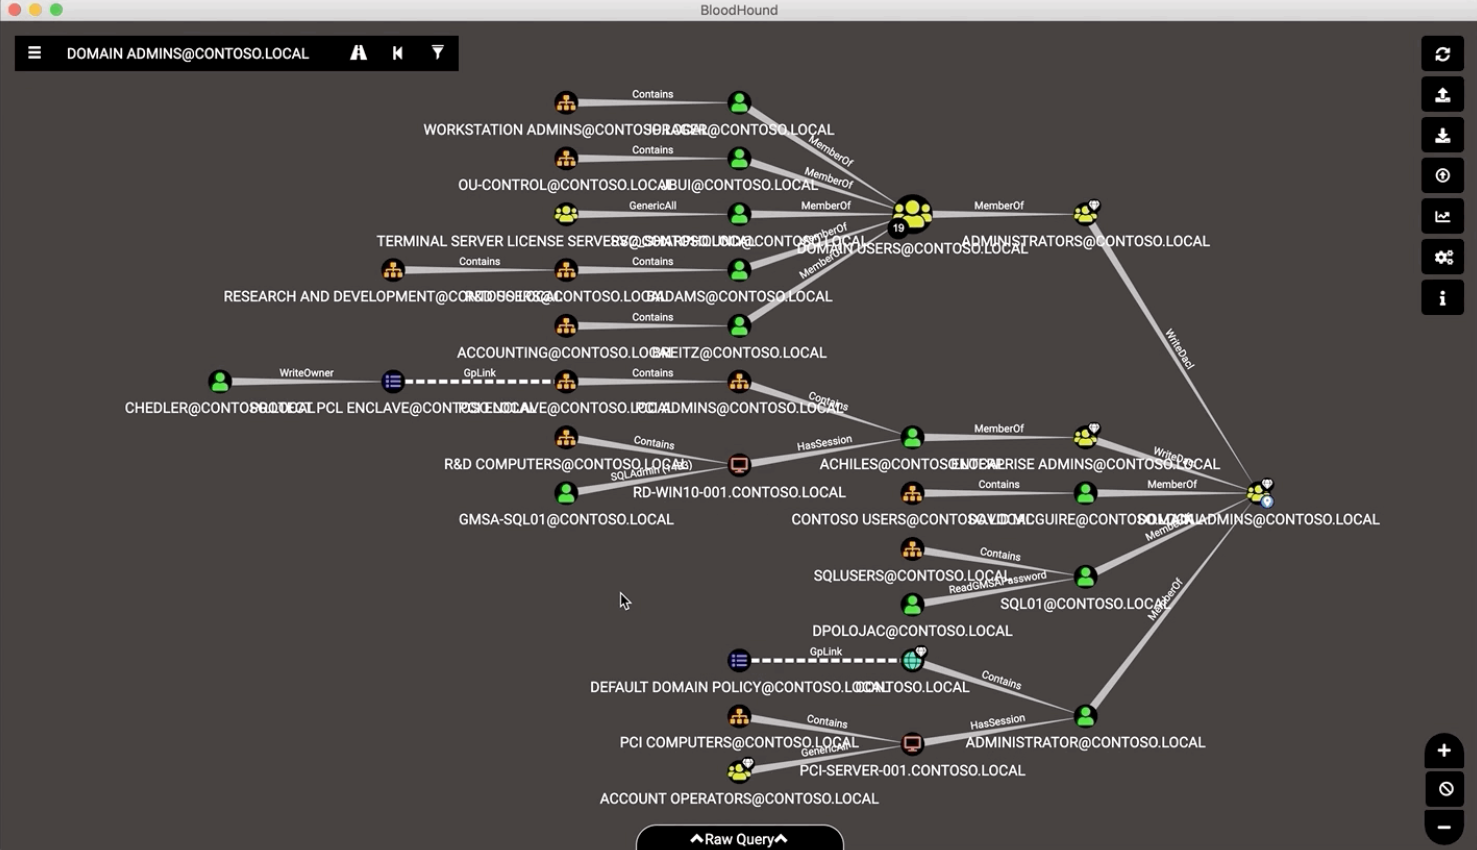
Besides this, the BloodHound maps attack paths for privilege escalation in Active Directory, utilizing SharpHound for info collection through executable or PowerShell script formats. 

Result of parsing the collected information through BloodHound
Result of parsing the collected information through BloodHound (Source – ASEC)

Infiltrators in Active Directory environments deploy tools like PowerView and AdFind for:-

  • Reconnaissance
  • Targeting domain admin privileges

While the BloodHound optimizes lateral movement paths, traditional security software may miss these threats.


[ad_2]
Source link

HONOR Magic6 Pro appeares in real-life images

0
[ad_1]

The HONOR Magic6 Pro launch is right around the corner. That phone has been surfacing for quite some time now, and it will launch alongside the vanilla Magic6. As we’re waiting for the January 10 launch event, the HONOR Magic6 Pro just surfaced in real-life images. These images come from Digital Chat Station, a well-known tipster. Do note that it’s not the first time we’re seeing a live image of the device, as one appeared last month.

The HONOR Magic6 Pro has surfaced in two real-life images, revealing new details

If you check out the images below this paragraph, you’ll see the phone in two of them. One is showing the device from the front, and the other from the back. The first thing that I noticed is that the sides of the phone seem to be flat.

That was not the case with the HONOR Magic5 Pro, so it’s interesting. The HONOR Magic6 Pro will retain a curved display, though, while its pill-shaped camera hole will move to the central position. That camera island will also be thinner, and wider, it seems.

As you can see in the first image, the bezels on this phone are very thin all around. The frame will be flat around the phone, but it will have slightly curved edges, so that it’s more comfortable to hold.

The second image shows us the phone’s backside

The second image in the gallery gives us a look at the phone’s backside. Truth be said, this image is not of the best quality, which is a shame. Still, we do get to see the phone’s back side, which surfaced several times thus far.

This is the green model of the phone, and it’s made out of metal and glass. You can clearly see the triple camera setup on the back. It looks similar to what the HONOR Magic5 Pro offered, but it’s tweaked a bit.

You’ll notice that the top camera seems to be larger than the rest. That is allegedly a 200-megapixel periscope telephoto camera that HONOR decided to utilize here. The other two cameras are the main shooter and the ultrawide camera.

The Snapdragon 8 Gen 3 is expected to fuel the HONOR Magic6 Pro, while the device will have top-of-the-line specs through and through.


[ad_2]
Source link

Official OPPO Find X7 Ultra camera samples are here

0
[ad_1]

The OPPO Find X7 series will launch on January 8 in China. As we’re waiting for that launch to happen, OPPO just shared some new info. The company shared the OPPO Find X7 Ultra camera samples on Weibo.

OPPO just shared the OPPO Find X7 Ultra camera samples

In that post, OPPO mentioned that the phone will provide a more realistic blur effect, better capturing of shadows, and improved photos of people’s faces, amongst other things.

If you check out the images in the gallery below, you’ll see the camera samples OPPO shared. Do note that these images have been compressed, though. To access them in their full size, click here. Do note these images have been captured with a 3x telephoto camera, not the main sensor.

These images do look great, that’s hard to deny. The blur effect is on point, and they do look like they’ve been shot with a professional camera, more or less. These images have been captured by a professional photographer, though, almost certainly, so… do take that into account.

The OPPO Find X6 Pro is still one of the best camera smartphones on the market. It’s a shame it did not launch globally. We do hope that the OPPO Find X7 Ultra will reach markets outside of China.

OPPO seems to be replacing the ‘Pro’ moniker with the ‘Ultra’ one

Having said that, it seems like the ‘Ultra’ will replace the ‘Pro’ this time around. Only the OPPO Find X7 and OPPO Find X7 Ultra are tipped to arrive. The OPPO Find X7 Pro is nowhere to be found.

That being said, the OPPO Find X7 Ultra will, of course, be a more powerful device. It will also include a better camera setup. OPPO is once again expected to utilize all 50-megapixel cameras on the back.

Unlike the OPPO Find X6 Pro, the OPPO Find X7 Ultra will have four cameras on the back. The phone will include a 50-megapixel main camera, Sony’s new LYT-900 sensor. Two periscope telephoto cameras (both 50MP) are also expected, and they will provide up to 6x optical zoom. The last camera on the back will be a 50-megapixel ultrawide unit.


[ad_2]
Source link

WhatsApp whips out the blue paint for business channels and verified badges

0
[ad_1]
Blue or green? Wait, this isn’t the Android vs iPhone RCS battle, it’s WhatsApp that we’re talking about.

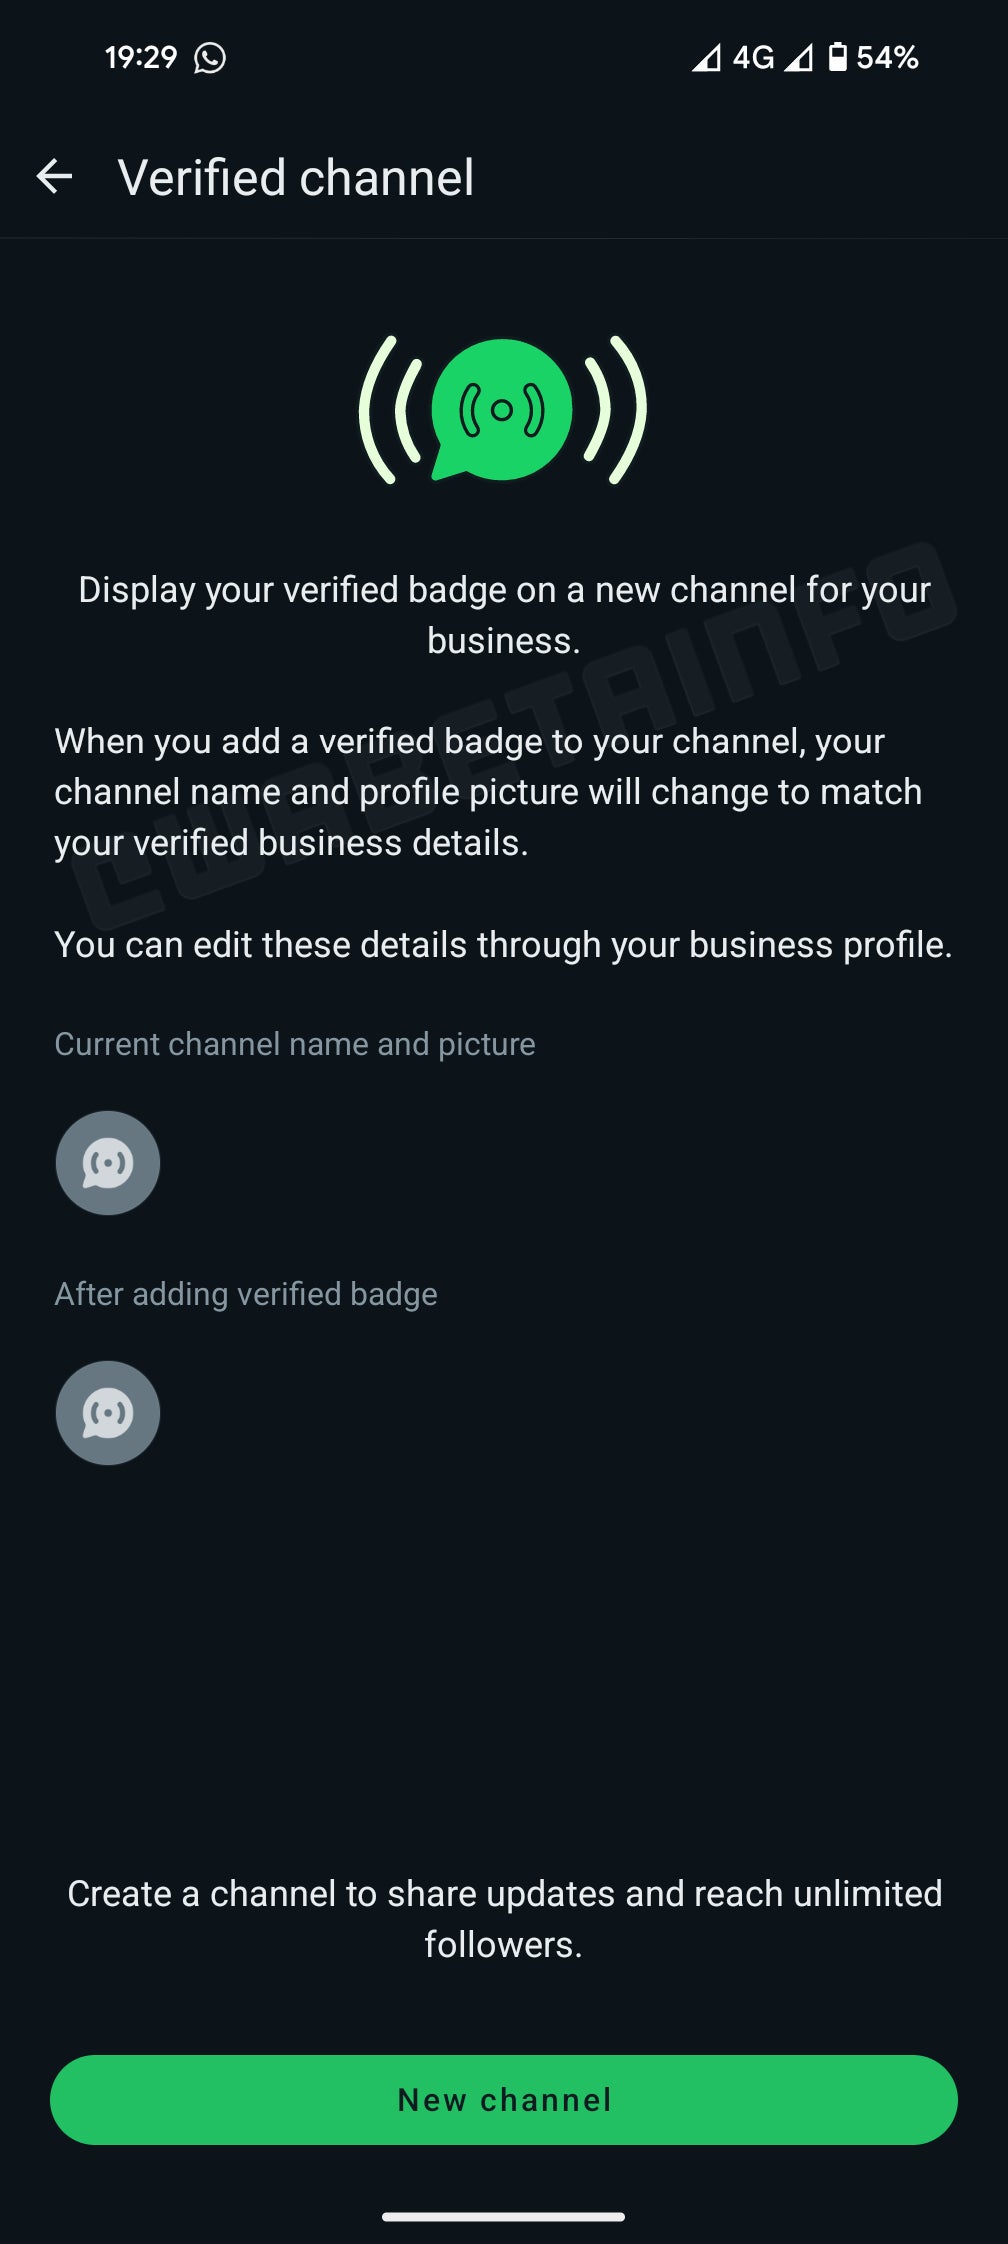
Soon, the world’s most popular messaging app will replace the green verification badge with a blue checkmark for verified channels and businesses, thus standardizing and aesthetically harmonizing the verification badge color across all Meta apps, as the verification checkmark is blue on both Instagram and Facebook.

Those who are part of WhatsApp’s beta testing program can update their versions to 2.24.1.18 (for Android) and check it out for themselves since the update is only limited to beta users at the moment (via MySmartPrice).

As usual, there’s a detailed report on the latest beta version updates over at WABetaInfo plus a screenshot. Here it is:

As the new screen shows, when business users add verified badges to their channels, their channel name and profile picture will be updated to match the verified business details. These details will be eligible for further editing through their business profile.

There’s something else to be done beforehand, though – to get a verified business badge on their channel, WhatsApp business users will have to be subscribed to Meta Verified.

“This is not so surprising as we already announced that Mark Zuckerberg recently revealed that the ability for businesses on WhatsApp to subscribe to Meta Verified will be available in the future, which would give them a verification badge for their profile and other advantages. It’s important to note that the Meta Verified subscription will be optional and exclusively accessible to businesses”, the WABetaInfo report states.

Additionally, the company has stated that to get Meta Verified, the channel information should be coherent with the corresponding business details to prevent misuse of the verification system and impersonation.


[ad_2]
Source link

Wireshark 4.2.1 Released – What’s New!

0
[ad_1]

Wireshark is a popular open-source network protocol analyzer that allows users to inspect and capture data on a network in real time. 

It enables detailed examination of network traffic for the following purposes:-

  • Troubleshooting
  • Analysis
  • Security purposes
  • Development
  • Education

Several key factors make Wireshark one of the leading network packet analyzers available on the internet, and here below, we have mentioned all the key factors:-

  • Open Source
  • Cross-Platform Compatibility
  • Rich Protocol Support
  • User-Friendly Interface
  • Active Community and Updates
  • Extensive Filtering capabilities
  • Search capabilities
  • Customizable Output
  • Powerful Display Filters
  • Support for Third-Party Extensions
  • Comprehensive Documentation
Document
Free Webinar

Compounding the problem are zero-day vulnerabilities like the MOVEit SQLi, Zimbra XSS, and 300+ such vulnerabilities that get discovered each month. Delays in fixing these vulnerabilities lead to compliance issues, these delay can be minimized with a unique feature on AppTrana that helps you to get “Zero vulnerability report” within 72 hours.

However, besides this, Wireshark Foundation recently launched a new version of Wireshark, which is Wireshark 4.2.1, that brings multiple bug and vulnerability fixes.

What’s New?

Vulnerability Fixes

Here below, we have mentioned all the vulnerability fixes:-

Bug Fixes

Here below we have mentioned all the bug fixes:-

  • Capture filters not saved to a recently used list. Issue 12918.
  • CFM dissector does not handle Sender ID TLV correctly when Chassis ID Length is zero. Issue 13720.
  • OSS-Fuzz 64290: wireshark:fuzzshark_ip: Global-buffer-overflow in dissect_zcl_read_attr_struct. Issue 19490.
  • Overriding capture options set by preference by command line arguments (like -S) doesn’t work. Issue 14549.
  • Segfault when enabling monitor mode on wireless card that falsely claims to support it. Issue 16693.
  • The documented format of the temporary file name is out of date in the Wireshark User’s Guide. Issue 18464.
  • Selection highlight is lost when the interface list is sorted. Issue 19133.
  • HTTP3 malformed packets. Issue 19475.
  • Capture filter compilation fails with an obscure error message. Issue 19480.
  • XML: Parsing encoding attribute failed when standalone attribute exists. Issue 19485.
  • Display filter expressions where the protocol name starts with a digit and contains a hyphen are rejected. Issue 19489.
  • diameter.3GPP-* display filters not working after upgrade to version 4.2.0. Issue 19493.
  • GigE-vision: Control Protocol shows \”unknown\” as a value for the ASCII character set. Issue 19494.
  • The HTTP/3 Request Header URI is not correct. Issue 19497.
  • QUIC/TLS not extracting \”h3\” from ALPN in a capture. Issue 19503.
  • Documentation on system requirements should be updated. Issue 19512.
  • 4.2.0: init.lua in subdirectories not loaded anymore. Issue 19516.
  • Malformed SIP/SDP messages: components are not decoded properly. Issue 19518.
  • heuristic_protos do not reset on profile swap. Issue 19520.
  • Wireshark 4.2 crashes on Apply As Column. Issue 19521.
  • NFLOG timestamp is incorrect. Issue 19525.
  • Qt6 Crash (Double Free) When Attempting to Save TCP Stream Graph. Issue 19529.
  • Fixed parsing display filter expressions containing literal OID values, e.g. snmp.name == 1.3.6.1.2.1.1.3.0.

Installation Packages

Here below we have mentioned the complete list of third-party packages that can be found on the official download page of Wireshark:-

  • Windows x64 Installer
  • Windows Arm64 Installer
  • Windows x64 PortableApps®
  • macOS Arm Disk Image
  • macOS Intel Disk Image
  • Source Code

[ad_2]
Source link

Picking the right headphones for precision transcription work

0
[ad_1]

In the intricate world of transcription, precision isn’t just a preference; it’s a necessity. Every syllable, pause, and nuance matters, making the choice of tools a critical decision for both seasoned transcribers and those stepping into the realm of transcription for the first time. Among these tools, the importance of headphones cannot be overstated. They are the bridge between spoken words and written text, making the selection of the right pair a vital aspect of ensuring accuracy and efficiency in transcription work. In this comprehensive guide, we will explore the key factors to consider when choosing headphones for precision transcription work and how the right pair can elevate your productivity and accuracy to new heights.

Understanding the Transcriber’s Needs

Transcription is a nuanced craft that demands a unique set of skills, focus, and an acute ability to decipher spoken words, even in challenging audio environments. The first step in selecting the right headphones is to understand the distinctive needs of transcribers, who often find themselves working with a variety of audio sources, from interviews and dictations to recordings of meetings. Here are some key considerations:

1. Noise Isolation vs. Noise Cancellation:

– Noise Isolation: Headphones with noise isolation capabilities are designed to physically block out ambient sounds. This can be particularly useful if you work in a noisy environment or need to transcribe recordings with background noise. Look for headphones with over-ear or in-ear designs that provide a snug fit to minimize external sounds.

– Noise Cancellation: While noise isolation deals with physical barriers, noise cancellation relies on advanced technology to actively eliminate external sounds. This can be beneficial if you’re working in a busy office or other loud environments. However, keep in mind that noise cancellation might affect audio quality and could be less effective against certain types of noise.

2. Comfort for Extended Sessions:

– Transcription work often involves long hours of listening and typing. Opt for headphones that prioritize comfort. Look for adjustable headbands, cushioned ear cups, and a lightweight design to prevent discomfort during extended sessions.

3. Wired vs. Wireless:

– Wired: Traditional wired headphones are known for delivering consistent audio quality without concerns about battery life. However, the cable can sometimes be restrictive, and there’s always the risk of tangling.

– Wireless: Wireless headphones offer more freedom of movement, which can be convenient during transcription work. Ensure that the wireless headphones you choose have a reliable connection and sufficient battery life for your needs.

The Best Headphones for Transcription

Now that we’ve explored the general considerations for transcription headphones, let’s delve into specific recommendations from Gotranscript, a leading transcription service. Gotranscript recognizes the importance of accurate transcription and recommends headphones that align with the needs of professional transcribers.

1. Sennheiser HD 280 PRO:

– Noise Isolation: These over-ear headphones provide excellent noise isolation, allowing transcribers to focus on the audio without interference from external sounds.

– Comfort: The Sennheiser HD 280 PRO is designed for comfort during prolonged use, featuring padded ear cups and an adjustable headband.

– Durability: Built with durability in mind, these headphones can withstand the rigors of daily use, making them a reliable choice for transcription professionals.

2. Audio-Technica ATH-M50x:

– Sound Quality: Renowned for their exceptional sound quality, the ATH-M50x headphones deliver clear and detailed audio, ensuring accurate transcription.

– Portability: The swiveling ear cups and foldable design make these headphones easy to transport, ideal for transcribers who are on the move.

– Detachable Cable: The ATH-M50x comes with a detachable cable, providing flexibility and convenience for users.

3. Sony WH-1000XM4:

– Noise Cancellation: For transcribers working in noisy environments, the WH-1000XM4’s advanced noise-canceling technology can be a game-changer.

– Wireless Convenience: With wireless connectivity and a long battery life, these headphones offer the freedom to move without being tethered to a device.

– Touch Controls: The touch-sensitive controls on the ear cups provide a seamless and intuitive user experience.

Making Your Decision: Additional Factors to Consider

When delving into the crucial decision-making process of selecting the perfect headphones for precision transcription work, there are additional factors that demand careful consideration. Let’s explore these aspects in detail to ensure that your choice aligns seamlessly with the demands of your transcription endeavors.

1. Frequency Response: A Symphony of Nuances

– Transcription is an art that requires the faithful reproduction of audio frequencies. To truly capture the subtleties of speech, transcribers should seek headphones with a wide frequency response. This parameter ensures that the headphones can faithfully reproduce both the low and high frequencies inherent in spoken language. The result? A richer, more nuanced listening experience that allows transcribers to discern every inflection, tone, and cadence with unparalleled clarity.

2. Open-Back vs. Closed-Back Design

– Open-Back Design: Picture a pair of headphones as a window into the auditory world. Open-back headphones, with their unique design, allow some sound to escape. This intentional ventilation creates a more natural and spacious sound, akin to the experience of listening to speakers in a room. However, it’s crucial to note that while this design enhances the acoustic experience, it may not be the best choice in environments filled with ambient noise. If your transcription space is serene and controlled, open-back headphones could offer an immersive listening experience.

– Closed-Back Design: On the other side of the acoustic spectrum, closed-back headphones present a different proposition. These headphones, with their sealed ear cups, offer superior noise isolation. This design is particularly beneficial for transcribers working in shared offices or environments with external disturbances. The closed-back design ensures that you can focus on the task at hand without external sounds interfering with your concentration.

Compatibility: Ensuring Seamless Integration

– Transcription work often involves a combination of devices, from computers to transcription foot pedals. To avoid any hiccups in your workflow, it’s paramount to ensure that the headphones you choose are compatible with the devices you’ll be using. This includes checking for compatibility with various computer systems and verifying connectivity with transcription foot pedals if they are part of your transcription toolkit.

Conclusion

In the world of precision transcription, the right headphones are indispensable. Gotranscript, recognizing the pivotal role of headphones in transcription work, recommends models that strike a balance between comfort, audio quality, and features tailored for the needs of professional transcribers.

As you embark on your journey to find the perfect transcription headphones, consider the specific demands of your work environment. Whether you prioritize noise isolation, comfort for long hours, or the convenience of wireless connectivity, there’s a pair of headphones that aligns with your needs.
[ad_2]
Source link

Cyber attack targets Ukraine phone operator

0
[ad_1]

Ukraine’s biggest mobile network operator has suffered a cyber attack connected to its ongoing conflict with Russia. Kyivstar, which has more than half of Ukraine’s population as mobile subscribers, said earlier this week that it had been targeted by a “powerful hacker attack” that knocked internet access and mobile communications and damaged IT infrastructure. It also disrupted air raid alert systems in parts of Kyiv.

The company’s CEO Oleksandr Komarov said the attack was a result of the war with Russia, reported Reuters. “War is also happening in cyber space. Unfortunately, we have been hit as a result of this war,” he told national television. “(The attack) significantly damaged (our) infrastructure, limited access, we could not counter it at the virtual level, so we shut down Kyivstar physically to limit the enemy’s access.”

Russian hacktivist group Killnet claimed responsibility for the attack via a statement on the Telegram messaging app, but did not provide evidence to support its claims.

Personal data of subscribers not compromised

In a Facebook post, Kyivstar said it was investigating the issue with law enforcement agencies and was “working to eliminate the consequences and restore communications” as soon as possible. The incident has been reported to Ukrainian state services, it added.

“The most important thing is that, as of now, the personal data of subscribers has not been compromised. Our team will definitely compensate those subscribers who had no connection or could not use our services,” the firm said. “Yes, our enemies are cunning. But we are ready to face any challenges, overcome them and continue working for Ukrainians.”

In a post on X (formerly Twitter), internet monitoring company NetBlocks wrote: “The cyber attack on Ukraine’s Kyivstar telecoms operator has impacted all regions of the country with high impact to the capital, metrics show, with knock-on impacts reported to air raid alert network and banking sector as work continues to restore connectivity.”

Cyber attacks are often geopolitical

“Cyber attacks are geopolitical, there is no doubt about it. When thinking about the theatre of war, communications are always a critical target,” commented Bobby Cornwell, threat detection expert at cyber security company SonicWall. “If an attacker can confuse different parties, it will eventually stir up chaos. Cutting off the cellular phones which are used in the battlefield due to lack of other types of communications, can cause troops to be misinformed/misguided, or vulnerable.”

There’s an overlooked aspect that often escapes many people’s thoughts – access to the telecom infrastructure, he said. “While hacking can dismantle communication networks, what if the hacker’s aim isn’t to disrupt but to camouflage their true goal? Imagine a scenario where a threat actor infiltrates a telecom company’s computer systems with a trojan horse, gaining access to phone telemetry.” Threat actors could exploit compromised phones to pinpoint their location and launch targeted attacks, he added. “This is not far-fetched, it’s an unfortunate reality of an ever-evolving cyber threat landscape.”

Russia’s winter cyber offensive

Russia is upping its cyber offensive, shifting its tactics to target western critical national infrastructure (CNI) and increasing its use of hacktivism, according to new research from cyber security firm Cyjax. The Cyber Winter of Discontent report analyzes the conflict in Ukraine and predicts how Russia may conduct cyber military activity over the coming winter.

It found that Russia is facing a crisis of resources and manpower and, with Ukraine receiving a steady supply of defensive weapons and technology from the West, Russia may struggle to effectively deploy malware against its CNI at scale. As such, analysts believe that Russia may turn its attention to more cost-effective tactics outside of the region in an effort to disrupt supply chains and deter the West from supplying its ally.

Cyjax has observed several hacktivist groups increasing in activity including UserSec, SiergedSec, NoName057, Anonymous Sudan, AnonymousRussia and Killnet. The firm has also detected many pro-Kremlin hacktivist collectives switching their targeting away from Ukraine to attacks on organizations based in Israel and those countries supporting it.

“The West’s support to Ukraine’s cyber defenses has stagnated Russian attacks, putting Russia in a difficult position as it struggles to find resources for a cyber and kinetic attack,” said Roman Faithfull, cyber intelligence Lead at Cyjax. “Thus far, Russia’s cyber warfare against Ukraine CNI hasn’t paid off which is why it makes sense that it would turn its attention to western CNI to induce war fatigue and disrupt supply chains.”

This week, the UK’s Joint Committee on the National Security Strategy warned of the catastrophic ransomware risk faced by UK CNI, with the lack of planning for such an incident meaning that the entire country is essentially being held “hostage to fortune.” Earlier this month, an international cyber security advisory from multiple governments accused the Russian FSB of carrying out a spear-phishing campaign against the UK, US and allies.


[ad_2]
Source link

Malware found in more than 190 Android apps

0
[ad_1]

SpinOk malware has been found in multiple Android apps that have been downloaded more than 30 million times.

The malware-riddled apps were found on the Google Play store, following an investigation by cyber security company CloudSEK. Following their investigation, the research team found that 193 apps on the Google Play store were infected with malware, 43 of which were active within the last week.

SpinOk malware was first discovered by cyber security software company Dr Web in May 2023. Distributed as an advertisement software development kit (SDK), the Trojan malware actually acts as spyware. Dr Web found in May that the malware was present in apps that had been downloaded more than 421 million times.

SpinOk malware is particularly malicious as it poses as a legitimate SDK for minigames with daily rewards. This entices both developers to download and use the kit on their apps and victims to download and run the malware frequently.

Once on a device, SpinOk malware is able to steal private data including images, files and videos on the device and send it to a private server. It can also hijack payments to cryptocurrency wallets and steal payment card details and login credentials. This can have a devastating impact on victims, as hackers may have access to personal or private images, documents and may steal their identities or money.

SpinOk malware was able to infect so many apps as it was distributed via a SDK-based supply chain attack. Software developers likely downloaded the SDK without knowing about the Trojan malicious software held within it.

The Google Play store has said it is taking “appropriate action on apps that violate [its] policies”. 


[ad_2]
Source link