Russian Hackers Exploiting JetBrains Vulnerability to Hack Servers

0
[ad_1]

The Federal Bureau of Investigation (FBI), the National Security Agency (NSA), and other co-authoring agencies have issued a warning that Russian Foreign Intelligence Service (SVR) cyber actors are widely exploiting CVE-2023-42793, aiming their attacks at servers that host JetBrains TeamCity software since September 2023.

Cyber actors affiliated with the Foreign Intelligence Service (SVR) are also referred to as Advanced Persistent Threat 29 (APT 29), Dukes, CozyBear, and NOBELIUM/Midnight Blizzard.

According to the reports, the victims include businesses that offer software for marketing, sales, medical devices, billing, employee monitoring, financial management, hosting, tool manufacturers, small and large IT companies, and an energy trade association.

Cyber Actors Exploiting JetBrains Vulnerability

The SVR continues attacking computer companies with this newly attributed operation that targets networks that host TeamCity servers. 

The authoring agencies determine that by taking advantage of CVE2023-42793, a software development program, the SVR might gain access to victims, especially by giving the threat actors the ability to compromise the networks of several software developers.

The flaw identified as CVE2023-42793 impacts the version before 2023.05.4; it was possible to bypass authentication in JetBrains TeamCity, which might result in RCE on TeamCity Server.

Software developers manage and automate software development, compilation, testing, and release using TeamCity servers, according to the CSA. 

Malicious actors may be able to undertake malicious supply chain operations, get source code, sign certificates, disrupt software deployment and compilation procedures, and much more if they have access to a TeamCity server.

The CSA also stated threat actors carry out malicious operations like moving laterally, backdoor deployment, privilege escalation, and other actions to guarantee long-term, continuous access to the compromised network environments.

In mid-September 2023, JetBrains released a fix for this CVE, which restricted the SVR’s ability to operate to exploit unpatched TeamCity servers accessible over the Internet.

Although the authorizing agencies evaluate that the SVR is still likely in the preparation phase of its operations and has not yet utilized its access to software developers to access customer networks, the SVR’s access to these networks gives it a chance to enable difficult-to-detect command and control (C2) infrastructure.

 “Russian cyber actors continue taking advantage of known vulnerabilities for intelligence collection,” said Rob Joyce, Director of NSA’s Cybersecurity Directorate. 

“It is critical to ensure systems are patched quickly, and to implement the mitigations and use the IOCs listed in this report to hunt for adversary persistent access.”

Recommendation

Based on the malicious actions of the SVR cyber actors, the agencies advise enterprises to enhance their cyber security posture by implementing the mitigations in the alert. The mitigations are as follows:

  • Implementing a patch from JetBrains TeamCity
  • Monitor the network
  • Setting up host-based and endpoint protection solutions
  • Utilizing multi-factor authentication
  • Auditing log files

[ad_2]
Source link
HONOR partners up with Porsche Design; first product coming next month

0
[ad_1]

HONOR and Porsche Design have announced their global partnership. Porsche Design, as many of you know, is a luxury lifestyle brand, and it’s well-known for its partnership with Huawei over the years.

Huawei and Porsche Design have announced a number of joint products over the years. Those were usually special editions of existing devices, and that’s what we’re expecting from these two companies as well.

HONOR & Porsche Design announce their global partnership

HONOR said that “both brands are united by the vision of creating innovative products that combine exceptional and functional design with cutting-edge technology”. The company also said that the partnership will focus on “creating premium devices that embody the essence of both HONOR and Porsche Design”.

The very first product that will be a part of this partnership is coming next month, in January 2024. Do note that it will launch in China, that’s something HONOR wanted to be clear on. Now, that doesn’t mean it won’t launch globally too, but it’s coming to China first.

It’s also worth noting that Porsche Design has been in the smartphone industry for 15 years. It co-released a number of products over that period of time. It will be interesting to see what will this new partnership deliver.

HONOR had a very successful year

HONOR had a very successful year in 2023. The company managed to grow quite a bit, and improve its position in a number of markets. Some interesting products also got announced, like the HONOR Magic V2.

That device is coming to global markets, by the way, in Q1 next year. We’re not sure of the exact timeline yet, but do take note of that. It’s still the lightest tablet-style foldable in the market.

It will be interesting to see where will Porsche Design fit in. We’re expecting a variant of the HONOR Magic6 series to be co-developed with Porsche Design, as the timing fits, but we’ll see.


[ad_2]
Source link

CISA Asks on Google Workspace Secure Configuration Baselines

0
[ad_1]

In a groundbreaking stride towards fortifying cloud security, the Cybersecurity and Infrastructure Security Agency (CISA) unveils the Secure Cloud Business Applications (SCuBA) Google Workspace (GWS) Secure Configuration Baselines. 

This architectural marvel establishes a robust groundwork, elevating data security across nine core GWS services, encompassing Gmail, Drive, Meet, and Calendar.

Delve into the essence of SCuBA GWS baselines. Carefully crafted blueprints delineate each service’s minimum viable security configurations. 

These serve as the bedrock upon which organizations sculpt their bespoke security postures. 

Addressing pivotal facets like access controls, data encryption, and logging, these predefined settings fortify the frontline against the ever-evolving landscape of cyber threats.

Baselines, while formidable, require vigilant oversight. 

Enter ScubaGoggles – an ingenious assessment tool from CISA. 

This watchful guardian scans GWS environments in real-time, gauging adherence to baselines. 

By spotlighting security gaps, ScubaGoggles empowers organizations to fortify their defenses proactively. 

It is a beacon, ensuring security configurations harmonize seamlessly with the established baselines.

CISA’s Open Invitation

CISA acknowledges that security is an ongoing odyssey, not a static destination. 

An open invitation echoes through the corridors of federal agencies and organizations, urging active participation in sculpting the final form of SCuBA GWS baselines. 

Embrace the opportunity to adopt draft baselines, tailoring them to specific needs. 

Share experiences and insights during the public comment period until January 12, 2024, sculpting baselines that are lucid, pragmatic, and impactful.

SCuBA GWS Initiative

A leap forward in cloud security, the SCuBA GWS initiative reshapes the narrative. 

Armed with baseline configurations and the vigilant gaze of ScubaGoggles, CISA propels organizations into a realm of control over their cloud security posture. 

This collaborative journey, fueled by open feedback, forges a pathway towards a more secure and resilient cloud ecosystem.

The draft SCuBA GWS baselines and ScubaGoggles beckon exploration. 

Actively contribute to this transformative initiative, charting a course towards a more secure future for your organization and the cloud at large. 

Key Takeaways:

  • CISA pioneers draft SCuBA GWS baselines and ScubaGoggles for nine core GWS services.
  • Baselines epitomize minimum viable security configurations, enhancing cloud security.
  • ScubaGoggles, a vigilant assessment tool, provides real-time visibility into compliance.
  • Public feedback is welcomed until January 12, 2024, shaping the final baselines.
  • SCuBA GWS initiative fosters collaboration, strengthening the cloud security posture.

[ad_2]
Source link

Last weekend Google spread the date that Eminem died even though he’s still alive and well

0
[ad_1]

When you think about all of the news and information that travels online each day, the amount is staggering. Occasionally you get someone who wishes to create some sort of reaction by posting fake news on Wikipedia for a laugh. Most of the time, the fake news never makes it past the Wikipedia stage as it is caught by a reader and brought to the attention of the people at Wikipedia who are in charge of correcting these types of things.

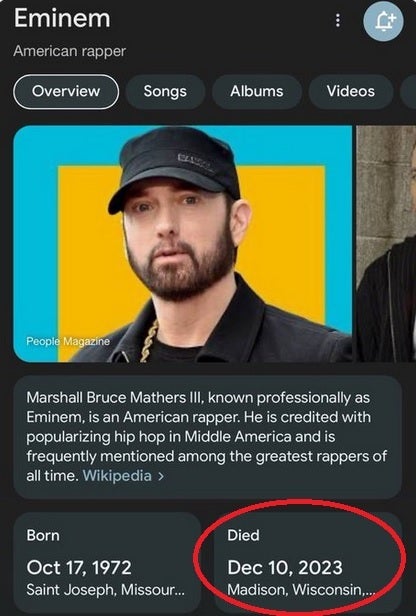
But what happens when a totally made-up piece of news seeps from Wikipedia into a part of the internet with a larger audience? We found out the other day when Google’s Knowledge Graph reported on the demise of a famous recording artist who had not actually passed away. The Knowledge Graph is a box filled with information that appears on the top or off to the right side of Google’s search results.
Last weekend, Google’s Knowledge Graph reported that rapper Eminem had died at the age of 51 in Madison, Wisconsin on December 10th. Per Newsweek, the hoax began when a post on Eminem’s Wikipedia page mentioned that the rapper had died. This information, which was totally fabricated by someone with a macabre sense of humor, changed Google’s search results for Eminem (whose real name is Marshall Bruce Mathers III) as the December 10th date of his passing was listed in the Knowledge Graph.

Anyone who happened to look up Eminem using Google Search on December 10th might have seen the Knowledge Graph showing that Eminem had died. And to help spread the news, over a 24-hour period the rapper’s fans wrote things like “Can’t believe he’s gone.” And the posts from fans of the Real Slim Shady included the hashtag #RIPEminem. 

That hashtag actually appeared back in 2020 when another hoax spread online that Eminem was dead after a user on what was then called Twitter posted a tweet that said, “I killed Eminem.” In that case, the account was suspended but not before the rumor of Eminem’s death had circulated throughout the internet.

Google commented on last week’s incident by noting that the Knowledge Graph uses a variety of sources including Wikipedia. Google says that it has systems in place that are supposed to detect if any of the Knowledge Graph’s sources have been tampered with. However, Google says that this system is not perfect. In the event that the system fails, as it did with the fake death of Eminem, Google expects to be informed by users so that it can manually fix the Knowledge Graph.


[ad_2]
Source link

U.S. facing cyberattacks from foreign nations, China the latest

0
[ad_1]

The United States has faced numerous cyberattacks from foreign bodies recently, and the country’s latest threat comes from China. Hackers with ties to the People’s Liberation Army have successfully broken into roughly two dozen U.S. systems over the past year, the Washington Post reported. The Post spoke to unnamed U.S. and industry security officials to get that figure, which lines up with public data from official reports. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) is the government body that handles cyberinfrastructure, and has cited China as an associate of the culprits of numerous cyberattacks in the U.S.

The U.S. claims that China is the sponsoring nation behind the cyberattacks on U.S. infrastructure, particularly targeting transportation. Other utilities, like water and power stations, are top targets as well. China could be using these cyberattacks as “practice” for a war. This comes as tensions between the U.S. and China are coming to a head, with the former looking to gain manufacturing independence. If there was ever a full-scale conflict between the two powerful countries, cyberattacks could slow response or cause homeland chaos.

“It is very clear that Chinese attempts to compromise critical infrastructure are in part to pre-position themselves to be able to disrupt or destroy that critical infrastructure in the event of a conflict, to either prevent the United States from being able to project power into Asia or to cause societal chaos inside the United States — to affect our decision-making around a crisis,” Brandon Wales, the executive director of CISA, told the Post. “That is a significant change from Chinese cyber activity from seven to 10 years ago that was focused primarily on political and economic espionage.”

The groups behind U.S. cyberattacks may be associated with China

China isn’t the only country launching cyberattacks on the U.S. Iran has also tried to breach U.S. infrastructure, according to government officials. And the idea that potential cyberattacks could be used as part of a larger conflict is more than just suspicion. In Russia’s ongoing invasion of Ukraine, Russia is attacking the country with ground assaults, air strikes, and cyberattacks.

The U.S. government has identified a group known as Volt Typhoon as a source of the cyberattacks. Additionally, it describes the group as a “People’s Republic of China (PRC) state-sponsored cyber actor.” The group uses an attack method known as “living off the land.” Through this process, attacks from the Volt Typhoon can blend in with normal usage and go undetected.

Cyberattacks could intensify as China and the U.S. continue moving toward hostilities. We’ve already seen plenty of cyberattacks against companies in the private sector, too.


[ad_2]
Source link

ASUS ROG Phone 8 launch date confirmed alongside renders

0
[ad_1]

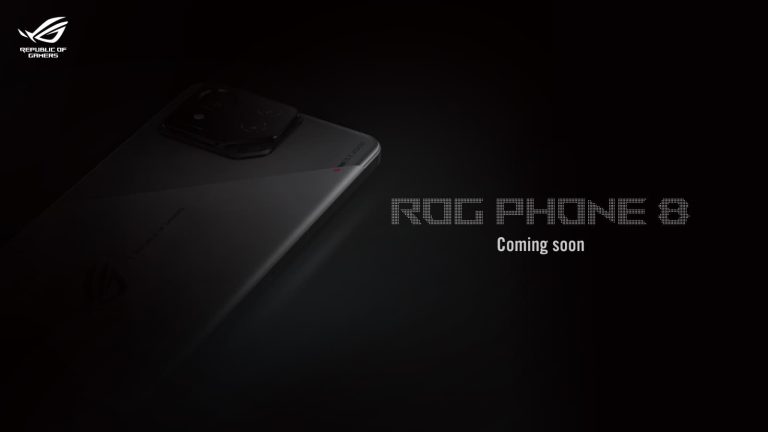
The ASUS ROG Phone 8 launch date has been confirmed by ASUS ahead of CES next month, which is expected to feature the new phones. The ASUS ROG line of phones has been a favorite among many for years now. These phones are the go-to for anyone recommending the best gaming phone on the market. While previous ROG phones have tinkered with unique features, it seems the Phone 8 will focus on cameras this time around.

When will ROG Phone 8 launch?

The ROG Phone 8 will be launching in China on the 16th of January. ROG’s Weibo account mentioned the product launch conference will take place on that date. This comes after the phone had already been teased prior by ASUS, drumming up speculation amongst consumers. The ROG phones have been featuring wildly untraditional designs for the last few iterations, but the ROG Phone 8 seems to have dialed it back slightly.

ASUS shifting gears

ASUS seems to have taken a page out of the books of industry giants like Samsung, Apple, and Oppo. While Galaxy and iPhone flagships battled it out in the camera department, ROG phones experimented with radical new features. For example, the ROG Phone 7 had an airflow port to help with thermals when using the AeroActive Cooler 7 attachment. When you put the attachment on it opens the port and allows for more air to keep temps low and performance optimal.

The AeroActive Cooler 7 also had a built-in subwoofer for more bass-heavy audio. On the rear side of the phone, there was a second screen, mostly used for eye-catching visuals. ASUS ROG Phone 8 has other priorities in mind, however.

New renders and a focus on cameras

ASUS has been talking about how it has been hard at work improving the cameras for the Phone 8 lineup. They’re quite confident too, and are holding a blind test where people have a chance of winning one of the new phones. ASUS has recently revealed some new renders of the ROG Phone 8 as well.

The phone seems to have a pentagon-like camera cutout on the back. ASUS has also slimmed down the bezels, making for the sleekest-looking screen ever seen on a ROG phone. However, much like the focus on cameras, an industry standard has been adopted as well. The renders show that the new screen has a punch-hole camera, ending ASUS’s streak of being one of the few manufacturers who still produced whole screens.

Naturally, the phone shines in other aspects. It is undoubtedly going to be one of the most powerful phones to launch in 2024, and definitely one to keep an eye on. It isn’t every day you get a phone with 24GB of RAM.


[ad_2]
Source link

U.S. will take “strongest possible” action against Huawei

0
[ad_1]

Following the surprise breakthrough in chip manufacturing from China in Huawei phones, the U.S. has vowed to take the “strongest possible” action. Previously, the U.S. had levied strict sanctions against companies in the U.S. and its allies. This prevented these companies from selling advanced tech to China. That meant Huawei had to work with the Chinese company Semiconductor Manufacturing International Corporation to get chips for new products. However, the sanctions took time to take effect in foreign countries, so China was able to secure advanced equipment under the wire.

The new chip fabrication equipment, called deep ultra-violet technology, has helped Huawei and SMIC break the 7nm barrier. While it isn’t on par with the latest chips from Samsung or TSMC, it’s still a breakthrough for China. The new 7nm chips power the latest Huawei Mate 60 Pro. This was released in August. It served as an alternative flagship in China. Though the technology industry sees China’s advancements as a surprising development, the U.S. isn’t as happy about it. Some government leaders are calling for action against what they view as a violation of U.S. sanctions.

“Every time we see something that’s concerning, we investigate it vigorously,” said Gina Raimondo, the U.S. secretary of commerce, in an interview with Bloomberg. Although Raimondo refused to comment on whether an official investigation has been opened, she did call the developments “deeply concerning.” The U.S. Bureau of Industry and Security, which is an arm of the Commerce Department, has the authority to investigate further. However, Raimondo has asked for more resources to aid in that effort.

“The investigations take time,” Raimondo added. “You know, we need them to stick. We need to gather information. So at this point, all I will say is that was concerning and we will take whatever action is the strongest possible in order to protect America.”

Did Huawei violate U.S. sanctions against China with new chips?

The Mate 60 Pro has a 7nm Kirin 9000s 5G chip inside, which is the source of the questions raised by the U.S. However, it’s unclear whether China actually broke any rules in developing the chip. The sanctions try to limit what chips, and which equipment needed to make chips, can be sold to China. However, ASML Holding is a leader in chip manufacturing equipment, and Bloomberg reported that it provided the equipment required to make 7nm chips.

The problem is, that ASML is based in the Netherlands. After the U.S. drew up these sanctions, it took months for the Netherlands to adopt them. This could have given China enough time to source equipment before sanctions were enacted.

“The US has time and again abused export-control measures, and this is not in the interests of global and industrial supply chains,” said Mao Ning, a spokeswoman for the Chinese Foreign Ministry.


[ad_2]
Source link

The EU, Apple’s two-letter headache, has the tech giant reaching for the aspirin again

0
[ad_1]
Apple has a two-letter headache. Those two letters are EU. Thanks to the Common Charger law passed by the EU, Apple replaced its proprietary Lightning port for charging and data transfers with a USB-C port starting with the iPhone 15 series this year. The EU’s Digital Markets Act (DMA) also applied a little pressure on Apple resulting in the decision to allow the iPhone to support Rich Communication Services (RCS) sometime next year.

Regulators in the EU have pressured Apple into replacing Lightning with USB-C and adding RCS support

By supporting RCS, iPhone users will be able to get features like read receipts, typing indicators, high-quality photos and videos, and end-to-end encryption when messaging with an Android user. 

Apple has never allowed iPhone users to sideload apps because it means that users will be able to install apps that Apple cannot check for malware like it can with the apps in the App Store. But thanks to the DMA, Apple could be forced to allow sideloading next year, but it might only approve sideloading on iPhone units available in the EU’s 27 member states. Sideloading is still expected to be blocked by Apple in the U.S. and most other countries outside of those who are members of the EU.

And now there’s more. According to Bloomberg, EU regulators are close to deciding whether to punish Apple for preventing apps that offer music streaming subscriptions from redirecting subscribers to alternative websites where payments can be made. Apple is trying to prevent this from happening because it bypasses Apple’s own in-app payment platform. The tech giant takes 15% to 30% of in-app revenue that it processes using its payment platform and this so-called Apple Tax has been at the center of much controversy.
Besides forcing Apple to allow music streamers to collect payments using alternative methods, Apple could be fined 10% of its fiscal 2023 revenue of $383.3 billion, or $38.3 billion. Even for a huge company worth over $3 trillion like Apple, that is a huge chunk of change. The company could also be forced to change its business model in the EU. The EU is expected to decide at the beginning of next year. 

Some changes forced on Apple by the EU, such as sideloading, will be allowed in the 27 member states only

The Digital Markets Act will take effect next March and will prevent companies from promoting their own services in the EU ahead of the competition. The tech giants will also be prevented from combining personal data collected from their various services. The DMA also states that data received from third-party merchants can not be used by the big tech firms to compete against these merchants.

When it comes to changing the Lightning ports to USB-C and supporting RCS, Apple decided that it would be too costly and time-consuming to make these changes only for iPhone units sold in the EU. But with sideloading, the stakes are too high for Apple to support third-party app stores worldwide. The potential for iPhone users to accidentally install a malicious app from an app storefront other than the App Store is just too great for Apple to allow sideloading in markets other than the EU where it is being pressured to allow it.

While Apple says that it needs to prevent sideloading to keep users iPhones safe, app developers have complained that Apple takes this position to force developers into paying the Apple Tax. As for iPhone users, most say that they paid for the device and if they want to risk installing malware that steals their personal data, that should be their decision.

[ad_2]
Source link

The EU rolls its first-ever comprehensive AI regulation bill

0
[ad_1]

As AI is expanding its role in our everyday lives, governments around the world are in a rush to enact their own set of regulations. The goal is to mitigate AI risks for citizens and pave the way for trustworthy AI development. The US first introduced the AI Bill of Rights as a set of principles for safe AI deployment. It was then followed by the EU with the AI Act.

While AI regulations in the United States are still changing hands between lawmakers, the EU’s Parliament and Council negotiators reached a vital agreement to regulate AI on the continent.

According to The Washington Post (via Engadget), a 72-hour debate between negotiators resulted in a historic agreement. The agreement is said to be the most comprehensive of its kind. The deal was reached while nations like France, Germany, and Italy were worried that enacting new laws might prevent EU members from developing cutting-edge AI technologies.

The EU takes a big leap forward in regulating AI in the continent

The new legislation basically proposes a set of guidelines for organizations that want to rely on AI for their work. For example, proposed regulations prohibit entities from using AI to design biometric categorization systems. Such systems could be used to target civilians based on their philosophical beliefs, political, religious, etc.

Additionally, using AI to create facial recognition databases and exploit people’s vulnerabilities is banned. According to the EU’s new legislation, designing AI systems to manipulate human behavior, designing social scoring systems, and launching emotion recognition in the workplace are other examples of banned AI applications.

The legislators have considered some exemptions for law enforcement agencies to use biometric identification systems (RBI). The RBI would be used in cases such as looking for abduction, trafficking, and sexual exploitation victims. Other uses are finding criminals and preventing a terrorist attack. Most details about the new legislation are still undercover. However, the MEPs also mandated high-risk and general AI systems to a set of rules for protecting civilians’ rights.


[ad_2]
Source link

You can now set your Instagram status as a selfie video and reply to notes with more than just text

0
[ad_1]
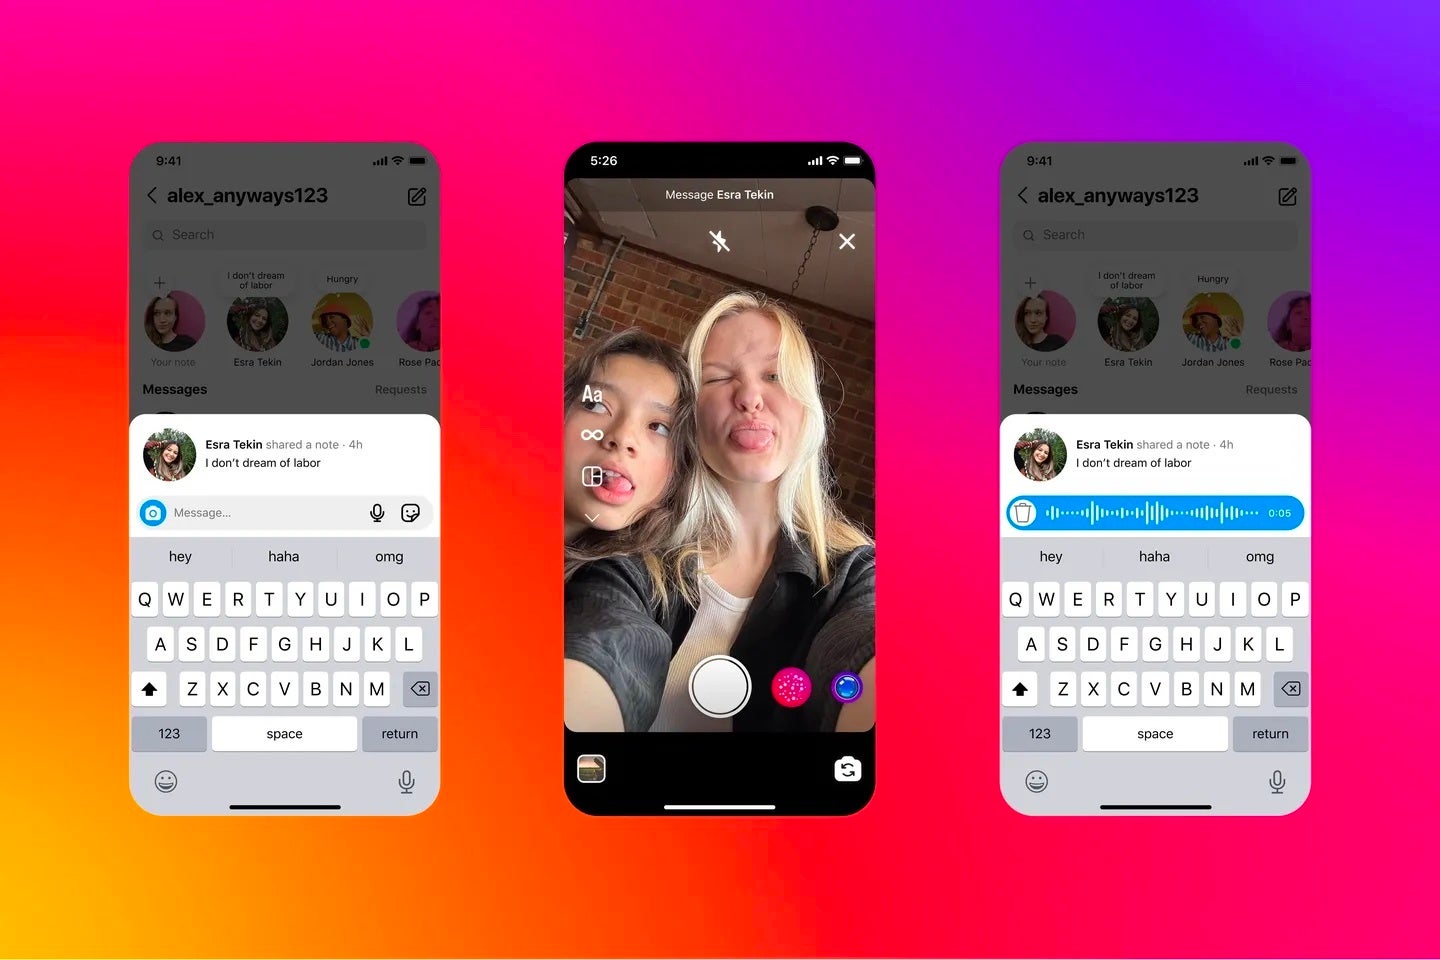
Instagram’s Notes, once a quiet corner for ephemeral text updates, is undergoing a metamorphosis. The platform announced today that it is expanding its capabilities by mixing in multimedia, such as video notes, emoji-infused replies, and an exciting new way to express yourself beyond the limitations of text.Gone are the days of static text updates. Video notes take center stage, allowing users to capture and share fleeting moments in just two seconds. Whether it’s a quick burst of laughter, a heartfelt message to a loved one, or a glimpse into your daily life, video notes will offer you a way to showcase it. However, these short looping updates will be reserved for your inner circle as only mutual followers and your designated “Close Friends” can view them.
Creating a video note will be as easy as navigating to your inbox, tapping on your profile picture, and letting your creativity flow. Each take is capped at two seconds, and the ever-present “trash can” button stands ready for creative retakes. Once your note is ready, you can add an extra touch a with a text bubble, post it, and wait for it to disappear in 24 hours.

This new feature was teased by Instagram boss, Adam Mosseri, when it began its testing stages. At the time, Mosseri shared a video on how a video note could be created, as seen below.

But the evolution doesn’t stop there. Instagram Notes now will allow users to reply with GIFs, photos, videos, audio recordings, and stickers. Responding is as simple as tapping on a note and composing your reply. 

These replies will arrive as direct messages, fostering a more personal and engaging conversation. With this update, Instagram embraces the power of the ephemeral messages, encouraging users to ditch generic comments and express themselves through video, audio, and emojis. 


[ad_2]
Source link