2FA _ Your Secret Weapon for Digital Defense

0
[ad_1]

As we rely on the Internet for communication, business transactions, and various aspects of our daily lives, the need for robust digital security measures becomes increasingly evident. 

Two-factor authentication (2FA) is one such measure that has emerged as a secret weapon for digital defense, significantly enhancing the security of our online accounts. 

Now, we will explore the world of 2FA, its significance, and how it works to protect our digital assets.

What is 2FA? 

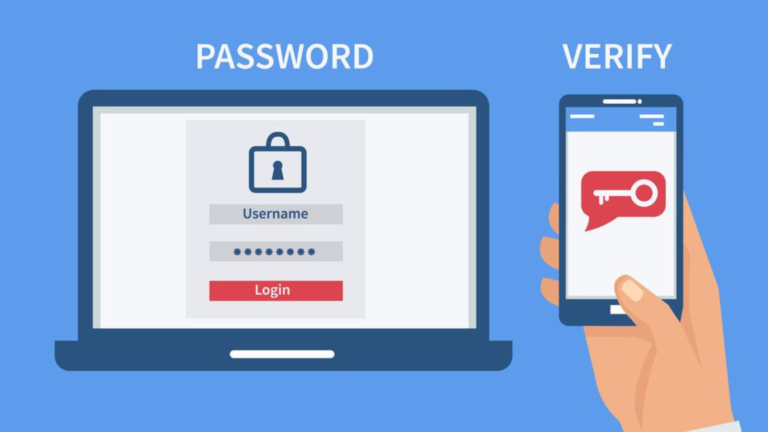
Two-factor authentication, or 2FA authentication service, is a process of security that needs users to provide 2FA before granting access to an online account or system. 

These factors are categorized as “something you know” and “something you have.” By combining two distinct types of authentication, 2FA adds an extra layer of security, making it significantly more challenging for unauthorized individuals to gain access to your accounts.

2FA typically involves using two out of three possible authentication factors: something you know, something you have, and something you are. 

How 2FA Enhances Digital Security

Adding a Second Layer of Protection 

The primary purpose of 2FA is to add a layer of security to your online accounts. It ensures that even if an attacker manages to obtain your password, they would still need the second factor (something you have or something you are) to gain access. This makes unauthorized access significantly more challenging.

Protecting Against Password Theft and Phishing 

2FA is highly effective in protecting against password theft, a common goal of cybercriminals. Even if a malicious actor tricks you into revealing your password through a phishing attack, they won’t be able to access your account without the second factor.

The Role of Time-based One-time Passwords (TOTP) 

One typical implementation of 2FA involves time-based one-time passwords (TOTP). TOTP generates temporary codes that are valid for a short period, typically 30 seconds. 

This time-limited code ensures that even if it’s intercepted, it becomes useless after a short time, adding an extra layer of security.

Types of 2FA

SMS-based 2FA 

SMS-based 2FA sends a one-time code to your mobile phone via text message. While widely used, it is not considered the most secure method, as SMS can be intercepted or redirected by attackers.

Mobile App-based 2FA 

Many online services offer mobile apps that generate one-time codes for two-factor authentication provider. These apps are more secure than SMS-based methods and are user-friendly.

Hardware Token-based 2FA 

Hardware tokens are physical devices that generate one-time codes. They are highly secure, as the token is separate from your computer or mobile device. However, they can be costly and less convenient.

Biometric-based 2FA 

Biometric authentication relies on unique physical characteristics, such as fingerprints or facial recognition. While highly secure, it may not be available on all devices or services.

Setting Up 2FA

Enabling 2FA for your accounts is a straightforward process, typically requiring you to visit the security settings of the service and follow the provided instructions. 

Most services will guide you through the setup, making it a user-friendly experience.

Choosing the Right 2FA Method 

When enabling 2FA, consider the available methods and choose the one that suits your needs and preferences. Mobile app-based 2FA is a popular choice due to its convenience and security.

The Importance of Backup Codes 

Many 2FA systems provide backup codes that you should keep securely. These codes can be used if you lose access to your primary 2FA method, ensuring you can still access your accounts.

Benefits of 2FA

Improved Security 

The primary benefit of 2FA is improved security. It significantly reduces the risk of unauthorized access and data breaches by requiring two distinct forms of authentication.

Reduced Risk of Unauthorized Access 

With 2FA in place, even if your password is compromised, your accounts remain secure. It provides an additional layer of defense against hackers and cybercriminals.

Protection Against Identity Theft 

2FA helps protect your identity and personal information, reducing the risk of identity theft and the potential consequences of unauthorized account access.

Compliance with Regulations 

In some industries and regions, compliance with data security regulations is mandatory. 2FA can assist in meeting these requirements and avoid legal complications.

Tips for a Secure 2FA Experience

Regularly Update and Secure your Devices 

Keep your mobile devices and computers up to date with the latest security patches and updates to minimize vulnerabilities.

Safeguard your Backup Codes 

Store your backup codes securely, ensuring you can access your accounts if you lose your primary authentication method.

Use a Password Manager 

Consider using a password manager to generate and store complex passwords for your accounts, making it even more challenging for attackers to gain access.

Conclusion

By combining “something you know” with “something you have” or “something you are,” 2FA creates an effective barrier against unauthorized access. 

As we navigate the ever-changing landscape of cyber threats, embracing 2FA as our secret weapon for digital defense is not just a wise choice; it’s an imperative one. 

So, take the extra step, enable 2FA for your accounts, and fortify your digital security today. Your online presence and personal information will be all the safer for it.


[ad_2]
Source link

How To Make Drupal Migration Successful: 6 Useful Tips

0
[ad_1]

As of 2023, there are over 1.7 million websites using Drupal, underscoring the significance of acquiring Drupal tips and tricks. The migration process can be crucial and challenging for newcomers.

Drupal is one of the most popular solutions for creating and personalizing websites. Today, this system is used by various businesses from different industries, from small start-ups to world-famous large enterprises. Thus, more than 1 million websites around the world are powered by Drupal.

At the same time, technology does not stand still. This means that if a business is interested in its stable development and sustainability, it is imperative to keep up with the times. Drupal, as technology, is constantly improving, providing developers with more tools to implement ideas and companies the opportunity to expand the quality of their service and customer satisfaction using a website.

This is how we come to Drupal migration. The main reason why Drupal migration is an important step is that you can ensure the longest life expectancy of your site, as well as make it more functional with this approach.

In addition, security is among the top priorities for online businesses. Therefore, ignoring system updates means that your website may not receive critical security updates.

Although migrating to newer versions of Drupal often occurs without problems or particular difficulties, it is still a process worth paying attention to and planning. Migrating to another version of Drupal is not only about launching an update but also the APIs, modules, and other core elements that your website includes.

In other words, ensuring that your website does not lose its functionality due to migration and continues to work correctly is essential. Let’s take a look at tips that may help you plan your migration to a new version of Drupal.

Tips For Drupal Migration 

Businesses are encouraged to consider upgrading to the latest version of Drupal for several reasons, the main ones being additional features, improved security, and higher website performance.

Sometimes migration can be challenging, but if you plan the process well, migrating to a new version of Drupal can be done efficiently and with no problems in most cases.

Here are some tips on how to make migration to the latest version of the system convenient and smooth:

Plan Your Migration 

The first and most important step is planning. It is essential to have a clear migration strategy before starting the process.

To do this, you need to conduct a thorough analysis to determine the scope of migration and understand how best to complete it. Factors to consider when drawing up a plan include:

  • workload assessment
  • setting migration deadlines
  • defining migration stages
  • website functionality assessment
  • possible impact of migration on the website

It is critical to clearly understand the specifics of how your website functions and to have a migration implementation plan. The more detailed and thoughtful your plan is, the better, as this will avoid unforeseen problems and delays in the process, thereby ensuring a successful and smooth transition of the website to the new version of Drupal.

Make A Backup

Before making any changes, you should always make a backup first. This is a necessary step that should not be ignored because something may always go wrong in the process, so it is essential that you have an “extra life” and can get back to where you started. Therefore, make sure you have copies of all website files and data before the migration process.

In addition, keep a backup copy of the website and its elements in a safe place, which you can also easily access if necessary. Only after you have made a backup can you make changes and experiment with the features of Drupal and your website.

Assess The Existing Modules

Conceptually, Drupal is a system that relies heavily on modules and themes. Due to this approach, Drupal expands the functionality of the system and provides new features.

However, this feature of the system may lead to the fact that some of the modules or themes you use on your website may be incompatible with the new version of Drupal. This is why it is essential to assess existing modules and themes before starting the migration process. This will give you time to replace some models or find other alternatives.

Drupal Core Update

This is the essential step in the migration process. For the migration to be successful and smooth, it is critical to update the system core first.

Therefore, before starting the process, use a tool like the Drupal Upgrade Status module. Its job is to identify issues and dependencies that may affect or hinder the migration of your website to a new version of Drupal.

Thus, update the core first and only then proceed with the system’s changes.

Test The Website

After updating your website, be sure to fully test the website for errors and evaluate its performance.

Factors to consider first include:

  • Website features and elements
  • Content and its display on the website
  • Website forms, modules, and themes
  • Third-party integrations and APIs
  • User accounts and data

To test a website, you can use the Drupal Functional Testing module. This tool automates the testing process and can quickly find and report errors.

Train The Team 

Migrating to a new version of Drupal means that some of the features and modules may work differently. Therefore, be sure to train your team and explain to them the new features and capabilities of the system that they can use from this moment.

This step should not be ignored, as understanding how the new version of Drupal works will allow your team to use the system effectively and avoid mistakes.

Learn more about migration processes and Drupal views data export at ElevatedThird.

  1. 5 WordPress Security Solutions with Free SSL Certificates
  2. Critical Vulnerability in Drupal CMS Used for Cryptomining
  3. How to perform a website security check- Here are 6 tools
  4. How can I protect myself from hackers if I want to start a blog?
  5. Leading, effective, and powerful tools for identifying site visitors

[ad_2]
Source link

This iPhone 16 Pro Max concept changes two key design elements

0
[ad_1]

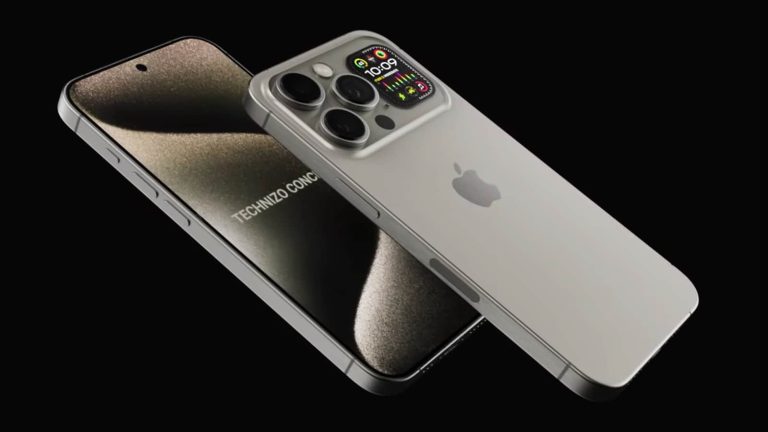
A new iPhone 16 Pro Max concept is out, and it’s presented in a video format. This video has been published by the Technizo Concept YouTube channel, and it does present an interesting-looking device.

This iPhone 16 Pro Max concept makes unrealistic design choices, but it’s fun

Now, in the title, I did note that two key design elements are changed here (in comparison to the iPhone 15 Pro Max). I was referring to the cutout on the display, and the area next to the cameras on the back.

This concept includes a regular display camera hole, instead of a large pill-shaped cutout. We likely won’t see that until the iPhone 17 Pro series, but there’s a slim chance a punch hole may be included on the iPhone 16 Pro series.

The second change won’t be happening at all, almost certainly, but it’s rather interesting. You’ll see a second screen on the back of this concept phone, next to its triple camera setup.

The second display is not happening, but it’s nice to see

That display is very small, but it can be very useful at the same time. Knowing Apple, there’s no way the company will go for something like this, at least not anytime soon. Still, it would be useful for notifications, music control, alarms, checking out the time, and so on.

Another difference compared to the iPhone 15 Pro Max is the general area around the cameras. The cameras and this second display are part of a singular camera island, which takes up a large chunk of the phone’s back.

The camera layout on the back remained the same, basically, as did other parts of the phone’s design. The sides are still flat, with slight curves on the edges, the back and front are mostly flat, and so on.

The iPhone 16 series launch is almost a year away, and this is definitely not what the iPhone 16 Pro Max will look like. Still, it’s nice to see such designs that tickle our imagination from time to time.


[ad_2]
Source link

Ddostf DDoS Malware Attacking MySQL Servers in Windows

0
[ad_1]

Researchers found that vulnerable MySQL servers are being deployed with the Ddostf DDoS bot, which is capable of launching Distributed Denial of Service (DDoS) attacks.

Ddostf, which was first identified around 2016, is well-known for supporting both Windows and Linux platforms and is believed to have been built in China.

As such, attacks targeting MySQL servers operating in Windows environments are continuously being discovered, according to the AhnLab Security Emergency Response Center.

Previous analysis indicates that Gh0st RAT and AsyncRAT malware variants account for most malware strains targeting susceptible MySQL servers.

Ddostf DDoS Bot Malware Attacking MySQL Servers

Ddostf has an ELF format that can be used in Linux environments and a PE format that can be used in Windows environments.  

Ddostf DDoS bot being installed via MySQL service

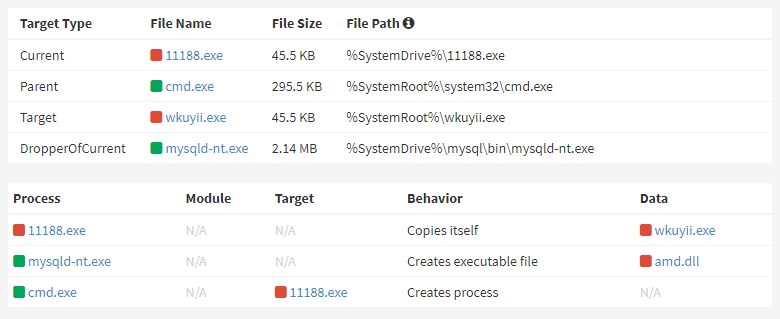
The inclusion of the “ddos.tf” string in Ddostf’s binary is a distinguishing feature. Before registering as a service, Ddostf copies itself in the %SystemRoot% directory under a random name when it is executed.

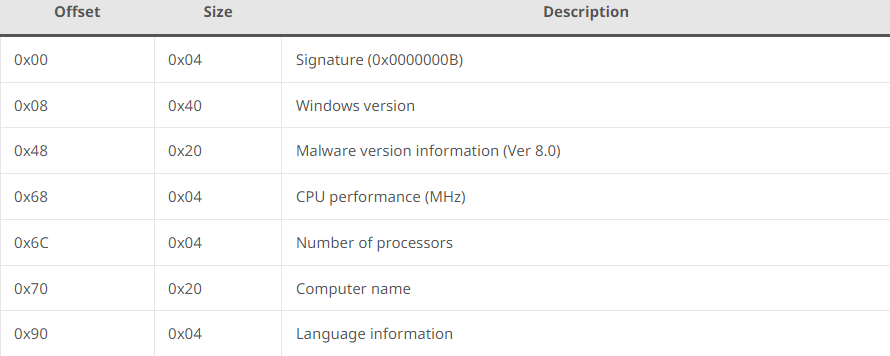
When it first connects, it gathers the most basic data from the compromised device and transmits it to the C&C server, reads the report.

Document
Protect Your Storage With SafeGuard

StorageGuard scans, detects, and fixes security misconfigurations and vulnerabilities across hundreds of storage and backup devices.

The C&C server responds with data in addition to commands when it receives information from the compromised system. It contains the download URL, for instance, in the case of specific DDoS attack methods or download commands.

System information sent to the C&C server

SYN Flood, UDP Flood, and HTTP GET/POST Flood attacks are just a few of the techniques used in internal DDoS attacks.

Further, Ddostf is unique in that it can establish a connection to a newly obtained address from the C&C server and run commands there for a certain amount of time.

This suggests that the threat actor Ddostf can infect a large number of systems and subsequently sell DDoS attacks as a service.

Dictionary and Brute Force AttacksServers

Generally, threat actors will use scans to find possible targets for their attacks. Scanners look for systems that use the 3306/TCP port, which is used by MySQL servers, among the systems that are publicly accessible.

Threat actors can then target the system using dictionary or brute-force attacks.

If the system manages user credentials improperly, threat actors may be able to get administrator account credentials.

Additionally, if the system is running an unpatched version with vulnerabilities, threat actors may be able to make use of these vulnerabilities.

Recommendation

  • Administrators should set strong passwords for their accounts and reset them regularly.
  • Applying the most recent fixes will also help to avoid vulnerability attacks.
  • Use security programs such as firewalls for externally accessible database servers.

Patch Manager Plus, the one-stop solution for automated updates of over 850 third-party applications: Try Free Trial.


[ad_2]
Source link

TikTok now lets you save songs directly to music streaming apps

0
[ad_1]

TikTok has announced an impressive new feature. Called “Add to music app,” the feature does precisely what its name suggests. It lets you save songs you discover on TikTok to your playlist on the music streaming app of your choice. Amazon Music, Spotify, and Apple Music appear to be the three streaming services supported at launch.

TikTok integrates music apps to let you save newly discovered songs

TikTok may have made its name as a video-based social network but it also serves as a great music discovery app. People make videos using trending songs and music tracks on the app, with new songs added regularly. Thanks to its massive global popularity, you may bump into a song you haven’t heard before and like it, or have listened to it sometime back but never added it to your playlist.

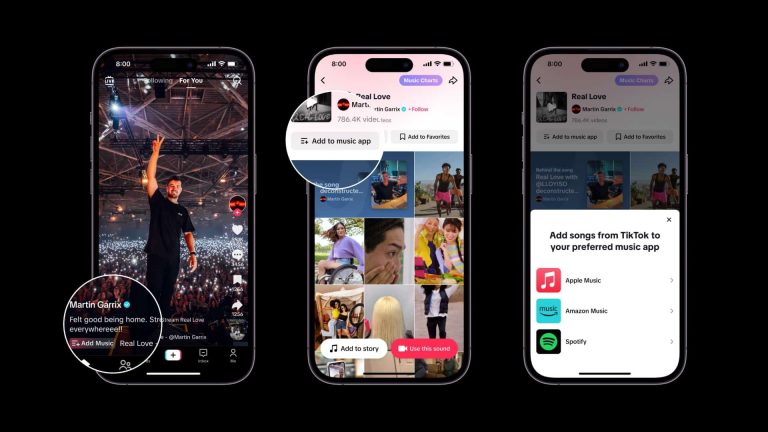
The videos do feature the track’s title and artist, so you can easily search for it on your music app. However, that means leaving TikTok and going back to open a new app. The company is simplifying this process by integrating streaming services into TikTok. When watching a video in the For You feed, you will now find a new “Add music” button next to the track name at the bottom.

Tapping this button will let you pick the music app you want to save the song to (a list of installed apps is shown). Select the app and add the song to your playlist. Once you have saved your first song, TikTok will pick the default app and playlist for all future saves (you can change the default app anytime). You will also find an “Add to Music App” on the Sound Detail page. It sits alongside “Add to favorites” above the video grid.

According to TikTok, Spotify will save songs in the Liked Songs playlist. On Amazon Music, you can save it to a playlist of your choice or the app will automatically create a TikTok Songs playlist. Only Amazon Prime members and Amazon Music Unlimited customers can use this feature. TikTok’s announcement doesn’t mention Apple Music but the accompanying image shows it alongside the other two streaming services.

This feature is rolling out in two countries

TikTok’s new music discovery tool is currently rolling out to users in the US and the UK. The company promises to bring the feature to more markets but doesn’t commit to a timeline for that. It’s also unclear if it plans to add support for more music streaming apps anytime soon. Always keep the TikTok app updated so you don’t miss out on the latest features.

TikTok add music spotify Amazon


[ad_2]
Source link

A guide to Bitcoin-adjacent digital assets

0
[ad_1]

The cryptocurrency landscape has undergone a remarkable transformation since the inception of Bitcoin in 2009. What started as an experiment in digital currency has now become a global phenomenon, with Bitcoin (BTC) leading the charge. Bitcoin’s meteoric rise has not only changed the way we perceive money but has also paved the way for a multitude of other digital assets. In this article, we will explore the world of Bitcoin-adjacent digital assets, providing you with a comprehensive guide to understand their significance, use cases, and investment potential. Take control of your financial future with Bitcoin trading and leverage the tools and knowledge available at SyntroCoin to make informed trading decisions and achieve success.

Bitcoin’s Origins and Significance

Genesis of Bitcoin

Bitcoin was introduced to the world by an individual or group of individuals using the pseudonym Satoshi Nakamoto. It aimed to create a decentralized digital currency that operates independently of traditional financial institutions. The release of the Bitcoin whitepaper in 2008 marked the beginning of this revolutionary journey.

Bitcoin as a Digital Store of Value

One of the primary reasons behind Bitcoin’s popularity is its role as a store of value. Often referred to as “digital gold,” Bitcoin is seen by many as a hedge against inflation and economic instability.

Role in the Decentralization Movement

Bitcoin also played a pivotal role in popularizing the concept of decentralization. Its blockchain technology, which relies on a distributed ledger, inspired the creation of various other blockchain projects aiming to decentralize everything from finance to governance.

Understanding Bitcoin-Adjacent Digital Assets

Definition and Classification

– Altcoins: Bitcoin’s Siblings
Altcoins are digital currencies that emerged after Bitcoin. They are sometimes viewed as alternative cryptocurrencies, and they come in various forms, each with its unique features and use cases.
– Tokens and Their Diverse Functions
Tokens are digital assets built on existing blockchain platforms like Ethereum. They serve various purposes beyond being a medium of exchange, including representing ownership, enabling access to services, and more.

The Appeal of Bitcoin-Adjacent Assets

Bitcoin-adjacent assets offer investors and users a chance to diversify their crypto portfolios and access a wider range of functionalities beyond what Bitcoin offers.

Market Dynamics and Correlations

Understanding the dynamics of the cryptocurrency market is crucial. Bitcoin often acts as a barometer for the entire market, with the prices of other digital assets often correlating with Bitcoin’s price movements.

Exploring Altcoins: Beyond Bitcoin’s Shadow

Ethereum (ETH)

Ethereum, often dubbed as Bitcoin’s closest competitor, introduced the concept of smart contracts and decentralized applications (DApps). It has undergone a major upgrade, Ethereum 2.0, which is transitioning to a more energy-efficient proof-of-stake (PoS) consensus mechanism.

Ripple (XRP)

Ripple stands out for its focus on cross-border payments. It aims to revolutionize international money transfers by enabling faster and more cost-effective transactions. However, it has faced legal challenges and regulatory scrutiny.

Litecoin (LTC)

Litecoin, often referred to as “silver” to Bitcoin’s “gold,” shares many similarities with Bitcoin but offers faster transaction confirmations. It has also seen technological advancements and development updates.

Tokenization and Its Role in the Crypto Space

What Are Tokens?

Tokens represent assets or utility within a blockchain ecosystem. They can be fungible (interchangeable) or non-fungible (unique), depending on their use case.

Token Standards: ERC-20, ERC-721, and Beyond

Ethereum introduced token standards like ERC-20 and ERC-721, which have become the basis for creating tokens with standardized functionality and features.

Real-World Applications of Tokenization

– Non-Fungible Tokens (NFTs)
NFTs have taken the world by storm, enabling ownership and provenance of digital and physical assets, including art, music, and collectibles.
– Security Tokens (STOs)
Security tokens represent ownership in real-world assets, such as real estate or company equity. They offer a regulated and compliant way to invest in traditionally illiquid assets.

Risks and Challenges in Tokenization

Tokenization brings its own set of challenges, including regulatory compliance, security concerns, and issues related to the representation of real-world assets in a digital form.

Investment Strategies for Bitcoin-Adjacent Assets

Portfolio Diversification

Diversifying your cryptocurrency portfolio by including Bitcoin-adjacent assets can help spread risk and potentially enhance returns.

Risk Management and Due Diligence

Thorough research and due diligence are crucial when considering investments in Bitcoin-adjacent assets. Understanding the technology, team, and market conditions is essential.

Long-term vs. Short-term Holding

Investors can choose between holding Bitcoin-adjacent assets for the long term, hoping for price appreciation, or engaging in short-term trading for profit-taking.

Tax Considerations

Tax regulations regarding cryptocurrencies vary by country. It’s important to understand tax implications when buying, selling, or holding Bitcoin-adjacent assets.

Risks and Considerations

Volatility and Market Fluctuations

The cryptocurrency market is notorious for its price volatility, which can lead to significant gains or losses in a short period.

Security and Custody Challenges

Safeguarding your digital assets is crucial. Security measures such as hardware wallets and secure exchanges are essential.

Regulatory Environment and Legal Compliance

Cryptocurrency regulations are evolving. Staying informed about the legal landscape in your jurisdiction is essential to avoid potential legal issues.

Scams and Frauds: Staying Safe in the Crypto Wild West

The crypto space is not immune to scams and fraudulent schemes. Being cautious and skeptical of too-good-to-be-true opportunities is vital.

Conclusion

In conclusion, Bitcoin-adjacent digital assets offer a world of opportunities beyond Bitcoin itself. Ethereum, Ripple, Litecoin, and a multitude of tokens have expanded the cryptocurrency ecosystem, each with its unique features and use cases. Tokenization is changing how we represent ownership, and the investment strategies and risks associated with these assets require careful consideration. As the cryptocurrency landscape continues to evolve, understanding Bitcoin-adjacent digital assets becomes increasingly important for both investors and enthusiasts. The future of this space is full of possibilities, and staying informed is the key to navigating this exciting journey.


[ad_2]
Source link

WhatsApp introduces voice chats for large groups on iOS and Android

0
[ad_1]
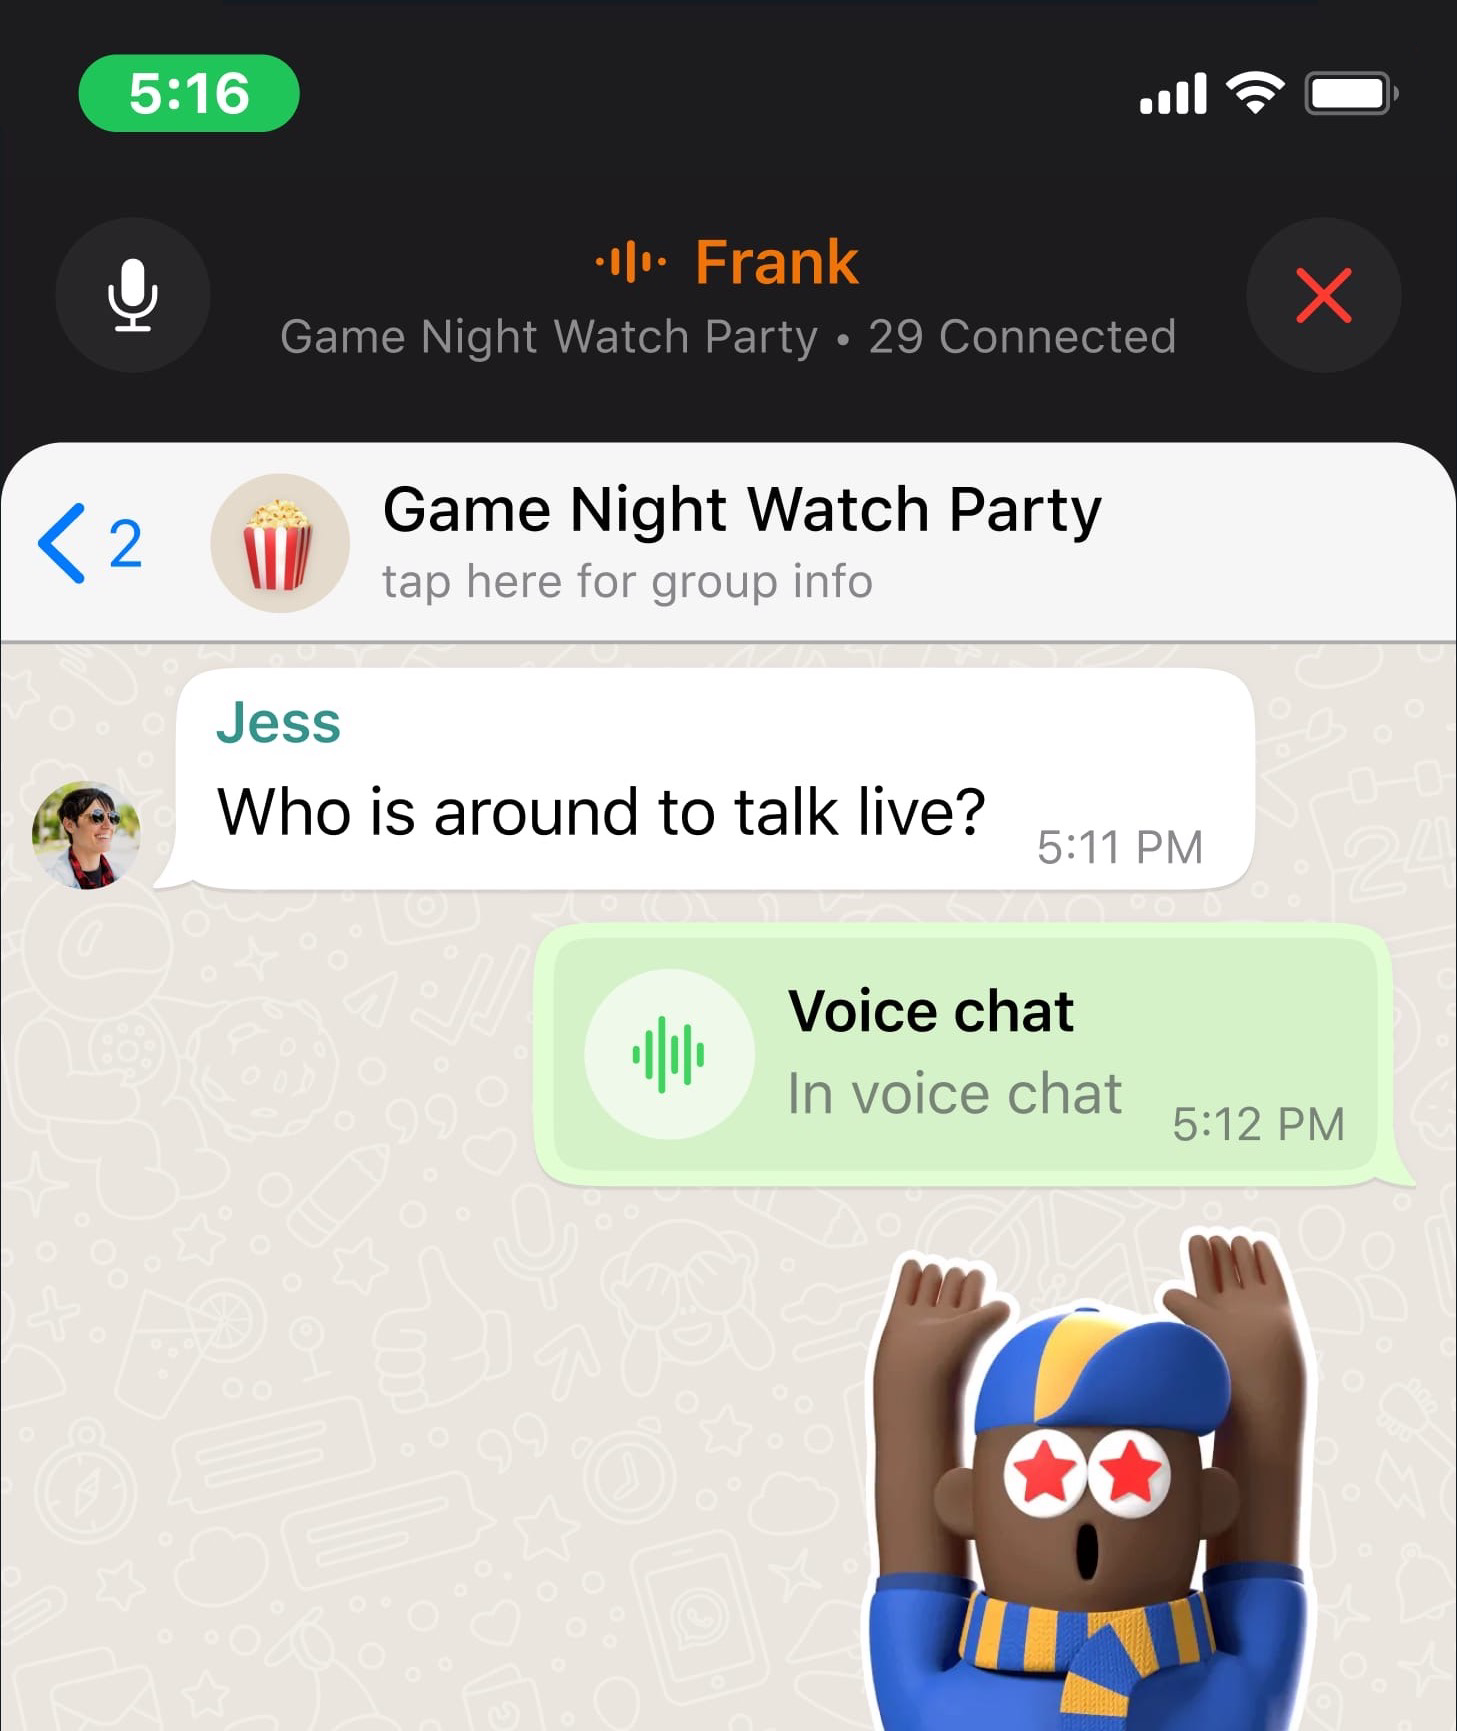
WhatsApp is introducing a new feature aimed at enhancing audio calls within group chats, allowing users to initiate an audio room that other members can seamlessly join.

WABetaInfo reports that the Meta-owned app is widely rolling out the update, which simplifies group communication by enabling the initiation of group calls silently without causing disruptions to others. Users can access this feature after updating to the latest versions of WhatsApp for both iOS and Android. Currently, it’s specifically deployed for larger groups.

This new functionality makes it more convenient for users to engage in group chats, providing an alternative method to start voice calls by sending silent push notifications, thus avoiding disturbances to other members of the group.
Voice chats bring a fresh experience to WhatsApp calling, streamlining connections for later discussions. Users can join voice chats within their groups at any time and start speaking without triggering notifications for everyone in the group chat. If a voice chat remains inactive for 60 minutes, it will automatically end. However, users can initiate a new voice chat whenever they wish.

The key advantage of voice chats lies in the ability to make calls without ringing each member’s phone individually. Upon initiation, every group member receives a silent push notification. Members not participating in the ongoing voice chat can view the active participants in the call from the chat header and the Calls tab, with the flexibility to join or leave the call at any time.

It’s worth noting that voice chats benefit from end-to-end encryption, ensuring that only the involved members can access the call’s content.

WhatsApp is one of the apps that gets new updates and features regularly. Recently, a new feature to initiate group calls with up to 31 participants was rolled out. A long-awaited feature was also introduced: multiple accounts on a single device.


[ad_2]
Source link

Confluence Vulnerabilities Exploited By Effluence Backdoor

0
[ad_1]

Researchers have found a new malware exploiting Atlassian Confluence vulnerabilities. Identified as Effluence, the new malware is a backdoor that chains a known vulnerability with a newly reported security flaw affecting Atlassian Confluence servers. Once deployed, patching the vulnerabilities won’t remedy the malware attack, demanding utmost security vigilance from the users.

Effluence Backdoor Exploits Atlassian Confluence Vulnerabilities

According to a recent post from Aon’s Stroz Friedberg Incident Response Services, a new malware is actively exploiting two separate Atlassian Confluence vulnerabilities, chaining them to target vulnerable servers.

As explained, the researchers found the new malware exploiting the recently discovered vulnerability CVE-2023-22518 to gain access to vulnerable systems. They detected this malware when analyzing a known vulnerable Atlassian Confluence Data Center server for a client’s network.

The recently discovered vulnerability is a critical severity flaw that allows creating rogue admin accounts, leading to a loss of confidentiality, integrity, and availability.

Once deployed, the malware, identified as “Effluence” serves as a backdoor that spreads laterally on the target network and steals data from Confluence.

However, to achieve this goal, the malware exploits a previously known vulnerability, CVE-2023-22515.

As the researchers observed, the malware reaches the target system and embeds a novel web shell that hijacks the underlying Apache Tomcat webserver, which positions itself between the Tomcat and Confluence. Thus, it becomes available on every web page, including unauthenticated pages, while remaining under the radar as it doesn’t affect the web pages.

Nonetheless, as it allows requests to pass through, it triggers malicious functionalities when encountering a specific request.

Explaining the web shell, the post reads,

The web shell is split into two parts, a loader and payload. The loader acts as a normal Confluence plugin but utilizes a modified legitimate Java collections class, similar to IdentityHashMap, to hide its malicious payload. The loader is triggered via an overloaded equals() method, which decrypts the payload into a byte array containing a Java class, then loads that class via reflection—hence the raw Java class is never written to the filesystem. Once the payload is loaded, it runs a function which hides the plugin among Confluence “System Apps”, whereas a user loaded plugin would normally be among “User-Installed Apps”.

Next, it creates rogue admin accounts, removes users, executes arbitrary commands, reads/writes/deletes files, uploads unauthorized plugins, uninstalls plugins, extracts information, purges app logs, and meddles with user passwords to allow unauthorized access to user accounts.

The researchers have shared a detailed technical analysis of this malware in their post.

As explained, the Effluence backdoor threatens all vulnerable Atlassian Confluence servers, and once infected, patching the vulnerabilities won’t remedy the attack. Therefore, users must stay vigilant about the yet unpatched and uninfected Confluence servers to patch immediately. Whereas the other users must take adequate remedying measures to detect and remove the backdoor from their network.

Let us know your thoughts in the comments.


[ad_2]
Source link

ASUS ROG Phone 8 charging speed revealed… it’s unsurprising

0
[ad_1]

The ASUS ROG Phone 8 charging speed has just been revealed. The phone appeared over at the 3C authority in China, where its charging speed was confirmed. The ASUS ROG Phone 8 will offer 65W wired charging.

The ASUS ROG Phone 8 charging speed gets revealed way early

This is completely unsurprising, as its predecessors offered the same charging. Both the ASUS ROG Phone 7 and ROG Phone 7 Ultimate supported 65W wired charging. Those two phones also offered 10W reverse wired charging, which will likely be the case with this device too.

ASUS seems to be uninterested when it comes to adding wireless charging to its gaming smartphone lineup. Now, wireless charging is not usually confirmed by the 3C authority, so there’s still a chance, but… don’t get your hopes up.

The charging speed is the only thing the 3C authority confirmed here. The phone appeared under the ‘ASUS-AI2141_A’ model number. The phone will support charging at the following modes: 15W (5V/3A), 27W (9V/3A), 45W (15V/3A) and 65W (20V/3.25A).

The entire ROG Phone 8 series will utilize the Snapdragon 8 Gen 3 SoC

We don’t have much information about the ROG Phone 8 just yet. What we do know is that it will be fueled by the Snapdragon 8 Gen 3, and that goes for the entire smartphone series.

We’re once again expecting to see more than one device, as we’ll likely get two smartphones in the series. You can expect a ton of gaming features once again, and top-of-the-line specifications too.

ASUS will likely utilize LPDDR5X or LPDDR5T RAM, and UFS 4.0 flash storage. Advanced cooling will be a part of the package, as will the shoulder trigger on the right-hand side of the device.

Now, the ASUS ROG Phone 8 is not expected to drop anytime soon. The ROG Phone 7 series arrived in April 2023, while the ROG Phone 6 series launched in July 2022. So, chances are we’ll have to wait until Q2 next year, at the very earliest.

ASUS ROG Phone 8 charging 3C authority


[ad_2]
Source link