ShellTorch Flaw Exposes Thousands of AI Servers to RCE Attacks

0
[ad_1]

ShellTorch Serve is an open-source model-serving library developed by PyTorch that simplifies the deployment of machine learning models for inference in production environments. 

It provides a scalable and efficient way to serve PyTorch models, making integrating them into applications and services easier.

The Oligo Security team found critical vulnerabilities, including CVE-2023-43654, enabling full chain RCE (Remote Code Execution). 

Thousands of exposed instances, even in major organizations, risk the following things:-

  • Unauthorized access
  • Malicious AI model insertion
  • Complete server takeover

AI models are now essential for critical tasks, from safety to security, but they also demand trust with sensitive data, impacting global conflicts and crucial decisions.

Document
FREE Demo

Implementing AI-Powered Email security solutions “Trustifi” can secure your business from today’s most dangerous email threats, such as Email Tracking, Blocking, Modifying, Phishing, Account Take Over, Business Email Compromise, Malware & Ransomware

PyTorch

PyTorch, a leading ML framework, stands at the intersection of AI and open-source libraries. In late 2022, attackers exploited dependency confusion to compromise PyTorch, introducing malicious code.

TorchServe, an influential PyTorch model-serving framework backed by Meta and Amazon, boasts widespread adoption in research and industry, including giants like-

It’s central to various projects and available as a managed service on major cloud platforms.

Experts found tens of thousands of exposed IP addresses, including Fortune 500 companies, vulnerable to Oligo’s discovered flaws in TorchServe versions before 0.8.2, enabling:- 

  • Remote code execution
  • Server takeover
  • Data theft

Exploiting ShellTorch CVE-2023-43654 allows an attacker to gain server control through API misconfigurations, SSRF vulnerabilities, and unsafe deserialization, potentially compromising AI models and sensitive data.

Vulnerabilities

There are three vulnerabilities, and we have mentioned them:-

  • Unauthenticated Management Interface API Misconfiguration
  • Remote Server-Side Request Forgery that Leads to RCE – CVE-2023-43654 (NVD, CVSS: 9.8)
  • Java Deserialization RCE – CVE-2022-1471 (GHSA, CVSS: 9.9)

Security Risks in AI

2023, “The Year of AI,” sees rapid innovation and fierce competition. Open-source tools drive AI growth but introduce significant security risks, challenging the balance between innovation and vulnerability in a hypergrowing AI industry.

Oligo’s discovered vulnerabilities illustrate real-world risks in the recent OWASP Top 10 for LLM Applications, including:-

  • Supply Chain Vulnerabilities
  • Model Theft
  • Model injection

ShellTorch vulnerabilities highlight the risk even in widely trusted projects maintained by top companies. Managed services by trusted providers may still have vulnerabilities. 

Even default self-managed containers by Amazon and Google were vulnerable to ShellTorch, although both companies have issued updates and advisories.

Mitigations

Here below, we have mentioned all the mo=itigations offered by the security experts:-

  • Update TorchServe to 0.8.2 or higher, but note that this update only adds a warning, not a fix, for the SSRF vulnerability.
  • To limit potential impacts, configure the management console correctly to prevent remote access using default settings.
  • Ensure your server fetches models exclusively from domains that are trusted.

Protect yourself from vulnerabilities using Patch Manager Plus to quickly patch over 850 third-party applications. Take advantage of the free trial to ensure 100% security.


[ad_2]
Source link
Pixel 8 internals exposed in a detailed teardown video

0
[ad_1]

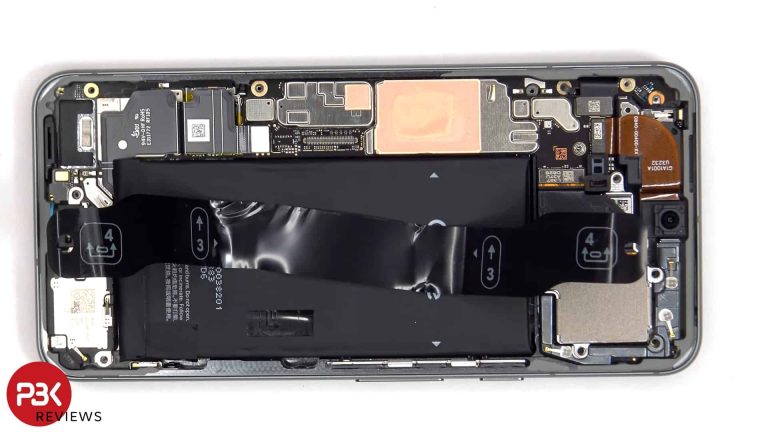
Google‘s latest Android smartphones are now official and available for pre-orders. If you have placed your order for the Pixel 8 or Pixel 8 Pro, you might be eagerly waiting to get your hands on it. Meanwhile, there’s already a teardown video of the base model on YouTube, showing the phone inside out.

You can pre-order the phones below:

Pre-order the Pixel 8 (Best Buy)

Pre-order the Pixel 8 Pro (Best Buy)

Pixel 8 teardown gives us an inside look at Google’s hardware engineering

YouTube channel PBKReviews, which is known for tearing apart brand-new smartphones and reassembling them, has just published one such teardown video for the Pixel 8. The video kind of acts as a guide for DIY (do it yourself) enthusiasts. The YouTuber gives detailed instructions on how to get inside the new Google phone without damaging it.

At first, you should remove the physical SIM tray, which sits on the left side of the phone when the screen is facing up. You can then proceed to remove the screen. Apply some heat to loosen the adhesive under the display and use a pry tool to carefully cut through the adhesive. A suction cup can be used to lift the screen as you push the pry tool under it.

Once you have completely cut the adhesive, carefully lift the display from right to left. This is because the screen has a cable under it on the left side. You have to remove a metal covering before you can disconnect the cable from the main board. The screen then comes off along with the under-display fingerprint scanner. Put it aside and you have a clear look at the Pixel 8‘s internals.

This isn’t the easiest phone to repair

Google has kept everything in place with 14 screws, a few of which are hidden under the graphite film. Removing the screws frees up the massive aluminum plate that runs top to bottom. It comes off with the vibration motor attached and makes room for battery removal. Simply disconnect the battery cable and use the provided pull tab to peel the battery off. You have to be careful to not pull the tab itself out, as the YouTuber did in this case.

If the pull tab doesn’t work its magic, you’ll have to use isopropyl alcohol to dissolve the adhesive and use a pry tool to remove the battery. The rest of the setup is mostly connected via Lego-style connectors, though you have to remove two more screws before the main board can be lifted off. Like before, Google has soldered the USB-C charging port to the main board on the Pixel 8 as well. This affected the phone’s repairability score, with PBKReviews rating it 7 out of 10. You can watch the full video below.


[ad_2]
Source link

AT&T looking to get out of the TV Business

0
[ad_1]

Back in 2015, AT&T acquired DIRECTV. In what looked like an attempt to go all-in with pay TV, including buying Time Warner in 2016. But it looks like AT&T has had a change of heart. Selling off Time Warner entirely, and now looking to do the same with DIRECTV.

Currently, DIRECTV controls all of AT&T’s remaining TV services, this includes U-verse TV as well as DIRECTV Stream. AT&T already sold off a portion of it to TPG Capital in 2021, while AT&T still owns a controlling 70% of DIRECTV.

But Bloomberg is reporting that AT&T is looking at options to sell all of its remaining shares of DIRECTV, or to sell part of the company to other investors.

Cable TV is a losing business now

Cable TV used to be a cash cow. Everyone had cable and was paying over $100 per month for a cable package with hundreds of channels that most did not watch. Now, most have cut the cord, and many more are doing so each day. In fact, in the first quarter of 2023, cable TV companies lost 1,135,143 subscribers. And in the second quarter that went up to 1,513,532. It’s a shrinking business, because everyone is relying on streaming services, or streaming Live TV services like DIRECTV Stream or YouTube TV.

AT&T knows this and could be why they are looking to ditch pay TV, and stick to wireless. And now that there are talks about it selling off the rest of DIRECTV, we could see the DISH and DIRECTV merger rumors coming back to life. These rumors have been around for many years. But DISH may not be that interested, given that it is now focusing on its 5G network – partly due to the deadlines set by the FCC.

Imagine going to court to spend $85.4 billion on acquiring a company that you then spun off just a few years later. And spending $49 billion for DIRECTV. AT&T did get a tiny bit of that DIRECTV acquisition cost back with the spin off to TPG Capital, but they only paid $1.8 billion for a third of the company. It’s clear that pay TV is declining, and AT&T is likely looking to get some of their money back before it’s all gone.


[ad_2]
Source link

Linux Vulnerability Attacks Root Privileges

0
[ad_1]

A buffer overflow issue has been disclosed in the GNU C Library’s dynamic loader ld.so, which might allow local attackers to acquire root privileges on vulnerable Linux systems. 

The Linux vulnerability is identified as “Looney Tunables” and tagged as CVE-2023-4911. The flaw was discovered in glibc version 2.34, which was released in April 2021.

Document
FREE Demo

Implementing AI-Powered Email security solutions “Trustifi” can secure your business from today’s most dangerous email threats, such as Email Tracking, Blocking, Modifying, Phishing, Account Take Over, Business Email Compromise, Malware & Ransomware

Local Privilege Escalation in the glibc’s ld.so

The GNU C Library, commonly called glibc, is the C library in the GNU system and most Linux-based kernels. 

It defines the system calls and other fundamental features that a normal program requires, such as open, malloc, printf, exit, and so on. The dynamic loader of the GNU C Library is a critical component of glibc that is responsible for program preparation and execution.

The GLIBC_TUNABLES environment variable was included in glibc to allow users to change the behavior of the library during runtime, avoiding the need to recompile either the application or the library.

Users can change different performance and behavior parameters by setting GLIBC_TUNABLES, which are then implemented when the application starts.

The Qualys researchers discovered that they could control the ld.so loader’s library search path and compel it to load a malicious shared library under the control by overwriting a specific function pointer in memory.

The ld.so loader is in charge of locating and loading shared library dependencies for executables during runtime. The vulnerability lies especially in ld.so’s handling of the GLIBC_TUNABLES environment variable, which configures glibc tuning parameters. 

Attackers can cause a buffer overflow and corrupt memory by providing a corrupted GLIBC_TUNABLES value.

Impact of Looney Tunables

Numerous Linux distributions are in danger because the dynamic loader’s handling of the GLIBC_TUNABLES environment setting has a buffer overflow vulnerability. 

For developers and system administrators, this environment variable is a crucial tool for tuning and optimizing glibc-linked applications. Its abuse or misuse has a significant impact on system security, dependability, and performance.

On default installations of Debian 12 and 13, Ubuntu 22 and 23, and Fedora 37 and 38, the vulnerability is activated while processing the GLIBC_TUNABLES environment variable.

Researchers say while some popular distributions, such as Alpine Linux, are unaffected since they utilize the musl libc rather than the glibc, many of them are possibly weak and may soon be exploited.

Patch Now!

System administrators must take immediate action given the vulnerability’s capacity to grant complete root access to well-known operating systems including Fedora, Ubuntu, and Debian.

Users of Alpine Linux may now sigh in relief, but others should prioritize patching to maintain the security and integrity of their systems.

Protect yourself from vulnerabilities using Patch Manager Plus to quickly patch over 850 third-party applications. Take advantage of the free trial to ensure 100% security.


[ad_2]
Source link
You can get Amazon’s 50″ Omni 4K TV for only $149; Here’s how

0
[ad_1]

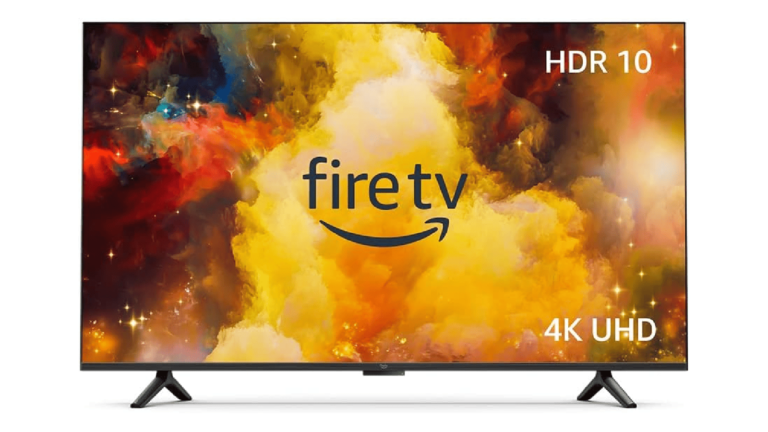
As you probably are aware, Amazon is doing its second Prime Day next week – Prime Big Deals Days – from October 10 to the 11. And with that, comes some pretty big deals, and some that are going to be invite only. That includes this Amazon 50-inch Omni Fire TV. This is a 4K TV that is on sale for just $149 – that’s down from $376.

This is an invite-only deal, so you’ll need to be a Prime member first. If you’re not, you can sign up for a 30-day free trial here. Secondly, you need to request an invite. You’ll be placed in a queue and sent an invite when one becomes available. This is to help negate products selling out super quick, and Amazon’s website crashing, as has happened in the past.

This TV from Amazon is actually a really good one, I have it in the 65-inch model, and absolutely love it. It’s a 4K TV HDR support. Which includes HDR 10, HLG and Dolby Digital Plus. There’s no Dolby Atmos on this model, that is saved for the Omni QLED models which cost a bit more. And kind of explains why the original price on this one was already under $400.

Amazon is also touting a 6-month subscription to MGM+ with your purchase here, which is a really nice one. You’ll get access to thousands of Hollywood movies and original series.

You can sign up to get an invite for the Amazon 50-inch Omni Fire TV by clicking the link below.

Amazon 50-inch Omni Fire TV – Amazon


[ad_2]
Source link

Google Assistant is now getting Bard functionalities

0
[ad_1]

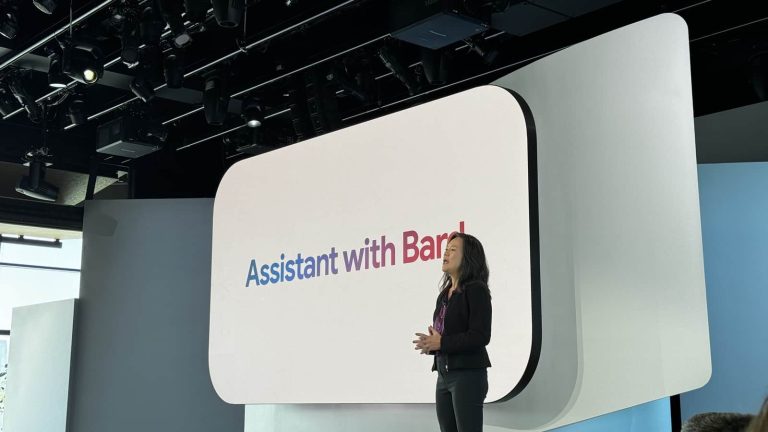
When Google first launched its Assistant back in 2016, it took the world by storm due to its capabilities. But, like many other voice assistants, Google Assistant has seen limited development over the years. However, all this is about to change as Google has announced it is integrating Bard functionalities in Assistant.

According to Sissie Hsiao, Google’s Vice President of Assistant/Bard, the Assistant with Bard will retain its existing capabilities and gain access to users’ personal Google apps such as Gmail, Docs, Drive, Maps, and YouTube. This enhancement not only allows users to ask tailored questions like “summarize my important emails from this week” but also enables the Assistant to function like an AI chatbot, as users can now use it to plan trips, create shopping lists, or even generate social media captions.

Moreover, users who want more functionality can also install “Bard Extensions,” which would allow the Assistant to track flights and make hotel bookings. However, it is important to note that users have the option to enable these personalized responses.

New multimodal capabilities

During the event, Google highlighted new multimodal capabilities, enabling users to interact with the Assistant through voice commands, typed queries, or even the camera via Google Lens. In a demonstration, Hsiao showcased a scenario where a group planning a hike with a small dog encountered a trail fork. And when the user captured an image of the trail and asked, “What path do you recommend for a group and my small dog?” the Assistant recommended the North Trail.

“Google Assistant, over the past seven years, has been helping hundreds of millions of people get things done through natural and conversational methods. And now, with generative AI coming, there are new opportunities to deliver an even more intelligent, more personalized, more intuitive digital assistant. And we think it should extend beyond voice,” said Google.

Availability

While Google plans to initially launch this functionality on Pixel 8 and 8 Pro before a broader rollout across Android and iOS, other Pixel phones and select Samsung phones will also gain the ability to activate a conversational overlay, which allows users to engage with Bard based on what’s visible on their screen by long-pressing the power or home button.


[ad_2]
Source link

Gmail app on Wear OS makes its debut along the Pixel Watch 2

0
[ad_1]

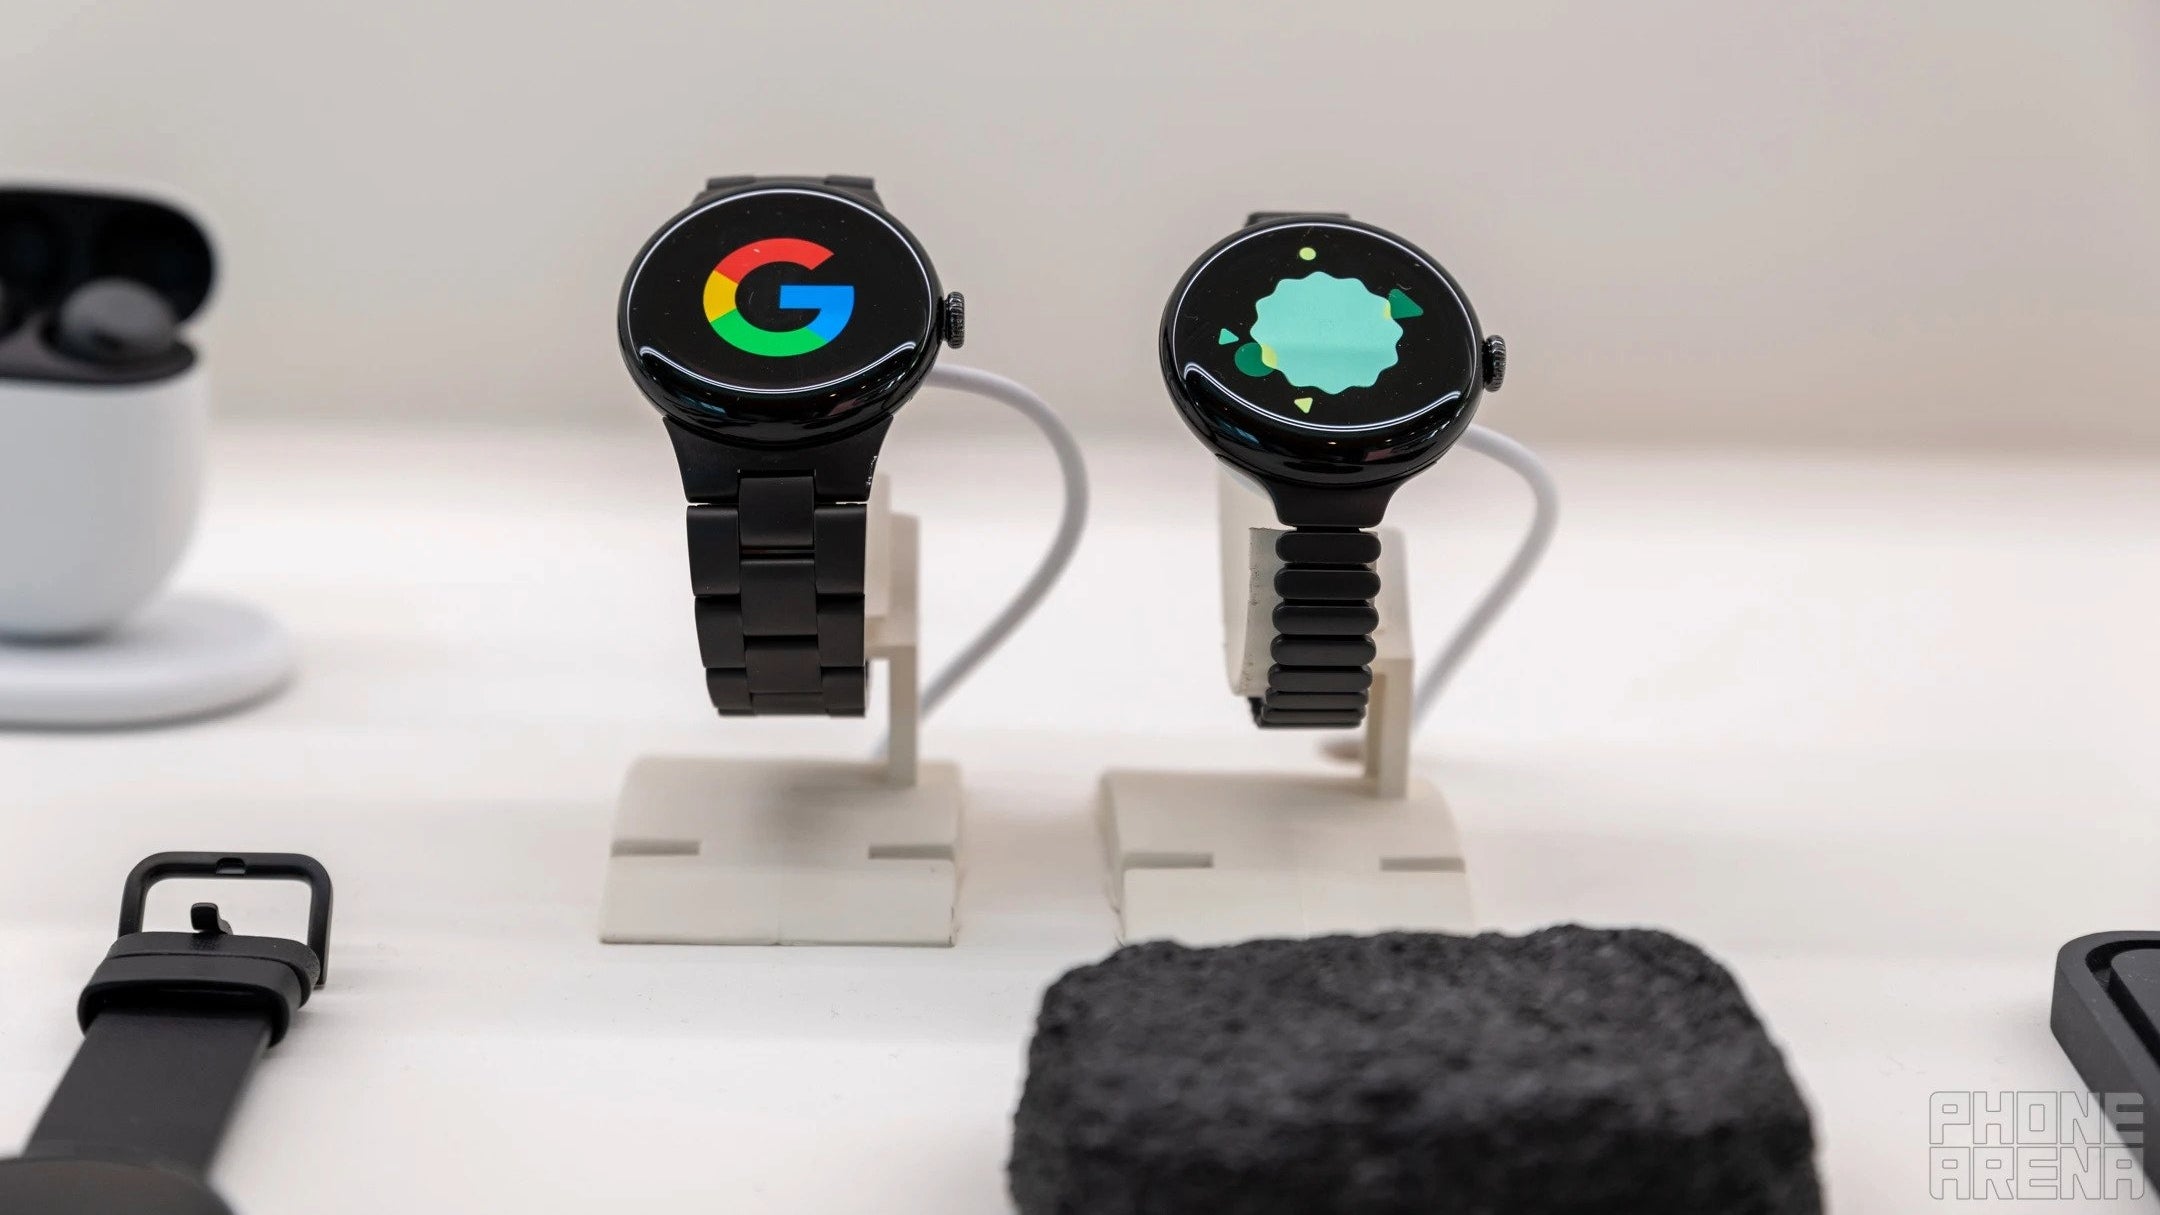
The Made by Google event has wrapped up, and the Pixel 8, Pixel 8 Pro, and Pixel Watch 2 are now officially out in the wild (available for pre-order). With new devices on the scene, you can bet some software updates and features are tagging along. This time is no exception. Google unveiled its spanking new AI-powered Assistant with Bard, and Android 14 is already making its way to devices. But that is not the whole story; Wear OS users are in for a treat, too.

Google is rolling out a Gmail app for Wear OS that will allow smartwatch users to view their inbox and open messages. The app was first spotted on Google Play Store by 9to5Google. It supports the ability to view your inbox as well as supporting multiple Gmail accounts at once. The app can open full emails, which you will be able to scroll through. You can also manually refresh your inbox if needed.

The app also includes a watch face complication that displays new emails. It doesn’t showcase all your unread emails, only the ones that have shown up recently.

In the past, Wear OS watches could receive Gmail push notifications, but users were limited to archiving, replying, or deleting in response. For a while, there have been whispers about Gmail making its way to Wear OS smartwatches, and it’s a relief to finally see the app debut with the new Pixel Watch 2. Other smartwatches running Wear OS 3 or 4 will also be able to grab this app.

Ready to give it a spin? Whether you’re rocking a Pixel Watch or a, for example, Samsung Galaxy Watch 5 or Galaxy Watch 6, you can already download the app from the Google Play Store. Just a note: there is still no Gmail app for Apple Watch, and it is still unclear if there ever will be.


[ad_2]
Source link

Wireshark 4.0.10 Released: What’s New!

0
[ad_1]

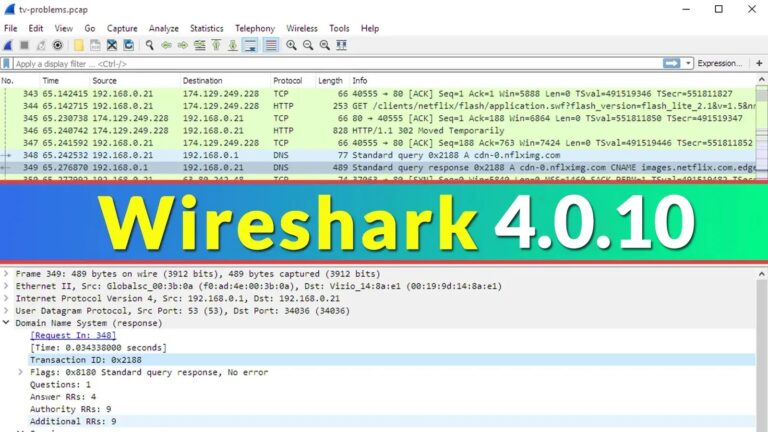
Wireshark that is formerly known as Ethereal is a widely used, free, and open-source network protocol analyzer, which allows users to capture and inspect data packets on a computer network.

This network analyzer tool is primarily used for the following purposes:-

  • Network Troubleshooting
  • Security Analysis
  • Software protocol development
  • Network Monitoring
  • Communications protocol development
  • Education

The widespread use of Wireshark reflects its effectiveness for network analysis. Wireshark 4.0.10 is the latest version that brings new updates and features for enhanced packet examination, making it a top choice for users and organizations across several sectors.

Document
FREE Demo

Implementing AI-Powered Email security solutions “Trustifi” can secure your business from today’s most dangerous email threats, such as Email Tracking, Blocking, Modifying, Phishing, Account Take Over, Business Email Compromise, Malware & Ransomware

What’s New?

This latest version, Wireshark 4.0.10 doesn’t bring any new features but comes with a fix, and here below we have mentioned that fix:-

  • Error loading g729.so plugin with Wireshark 4.0.9 and 3.6.17 on macOS. Issue 19374.

Wireshark and TShark search various locations for config files, plugins, SNMP MIBS, and RADIUS dictionaries, which vary by platform. To find default locations, use Help › About Wireshark › Folders or tshark -G folders.

This new version of Wireshark 4.0.10 doesn’t bring any new protocol support, updated protocol support, new and updated capture file support, or new file format decoding support.

As for Windows, make sure to use the most recent 3.6 version as there are no official 32-bit Windows packages for Wireshark 4.0+. 

Run “Uninstall ChmodBPF,” then “Install ChmodBPF” while using the macOS 13 upgrade to reset the ChmodBPF Launch Daemon.

Where to download?

The latest version of Wireshark (Wireshark 4.0.10) is available on the official portal of Wireshark Foundation, and you can download the latest version of Wireshark from the official download page, which you can access here.

Protect yourself from vulnerabilities using Patch Manager Plus to quickly patch over 850 third-party applications. Take advantage of the free trial to ensure 100% security.


[ad_2]
Source link
NPM Typosquatting Attack Deploys r77 Rootkit via Legitimate Package

0
[ad_1]

EXECUTIVE SUMMARY

  • ReversingLabs researchers have discovered a new typosquatting campaign exploiting the NPM platform.
  • Researchers observed a malicious NPM package called node-hide-console-windows delivering the r77 rootkit to innocent users.
  • Typosquatting is a deceptive method where cybercriminals create domain names and social media accounts using the same spelling as the original organization’s name.
  • 10 versions of the malicious NPM package were discovered. 
  • In this cybersquatting attack, scammers have exploited the legitimate package node-hide-console-window to deceive users.

ReversingLabs’ cybersecurity researchers have uncovered a malicious NPM package (node-hide-console-windows) created using typosquatting to resemble a legitimate NPM package called node-hide-console-window.

As evident, the attackers have added an ‘s’ in the title of the malicious package to separate it from the original one. The concerning part is that this malicious package has been downloaded over 700 times. This campaign started at the end of August 2023.

ReversingLabs revealed that when a user installs this malicious package, a Discord bot is downloaded that plants the open-source r77 rootkit. This rootkit hides itself within the OS to remain undetected and lets the attacker obtain complete control of the victim’s device.

Researchers examined the executable fetched by a file titled index.js, which turned out to be DiscordRAT 2.0. All ten versions of the malicious NPM package downloaded the same DiscordRAT2.0 executable. However, the last two versions contained an additional malicious payload disguised as a visual code update and fetched by index.js.

For your information, DiscordRAT 2.0 is a Discord Remote Administration Tool promoted for training purposes but is an open-source malware. Threat actors must register the bot with the Discord developer portal and add it to the Discord server or guild before deploying it. The guild ID is added to the DiscordRAT 2.0 executable and delivered to the victims through phishing email attachments or packages available on public repositories.

Further probing revealed that the Discord guild for the malware was launched on August 15, just 10 days before the malicious NPM package’s first version was published. The executable creates a channel in the connected Discord server for each victim and sends the initial payload to the infected host.

From there, the bot receives additional commands from the attacker and can perform a range of tasks like disabling Windows Defender, blocking the victim’s mouse and keyboard, bluescreening the device, and killing processes. There’s a long list of commands it facilitates but most important is the ‘!rootkit’ command recently added to DiscordRAT 2.0 to launch the r77 rootkit on the infected device.

This open-source, fileless ring 3 toolkit features extensive documentation and can disguise files/processes. This rootkit hides itself within the OS to remain undetected and lets the attacker obtain complete control of the victim’s device.

It is worth noting that this is the first time researchers have identified a malicious NPM package that facilitates functionality. This indicates a need to secure open-source projects as cybercriminals are preferring to exploit them to distribute malware.

Attackers used other tactics to ensure developers added the malicious package to their applications, such as creating an NPM page similar to the legitimate package’s page. Moreover, just like the original package, the malicious one also featured 10 published versions.

In their blog post, researchers have noted an uptick in campaigns exploiting the NPM package register platform. In August 2023, ReversingLabs researchers discovered multiple malicious NPM packages linked to a campaign targeting cryptocurrency providers. 

Another NPM-related campaign was discovered in July 2023, targeting developers and end-users with malicious code that stole sensitive user data via fake Microsoft.com login forms and implanted credential-stealing scripts in apps that unintentionally incorporated NPM packages.

For your information, the original package (node-hide-console-window) is used to toggle the console window visibility of an application.

In order to protect yourself against typosquatting attacks, it is essential to check the addresses while typing or searching for addresses/packages online so that you visit the original site/repository.

In addition, closely inspect the package’s name and description before installing. Install a reliable security solution to detect/block malicious packages timely. If you suspect your device is infected with the r77 rootkit, quickly run a system scam using a reliable antivirus and change the passwords for all accounts, especially banking passwords.

  1. Luna Grabber Malware Hits Roblox Devs Through npm Packages
  2. 6 official Python repositories plagued with cryptomining malware
  3. CISA warns of trojanized versions of JavaScript library’s NPM package
  4. VMCONNECT: Malicious PyPI Package Mimicking Common Python Tools
  5. Crypto Discord Communities Targeted by Malicious Bookmarks & JavaScript

[ad_2]
Source link

Google Pixel 8 wallpapers are available to download

0
[ad_1]

Google announced its new Android flagships yesterday, the Pixel 8 and Pixel 8 Pro, and their wallpapers are now available to download. These wallpapers have been shared by Android Authority.

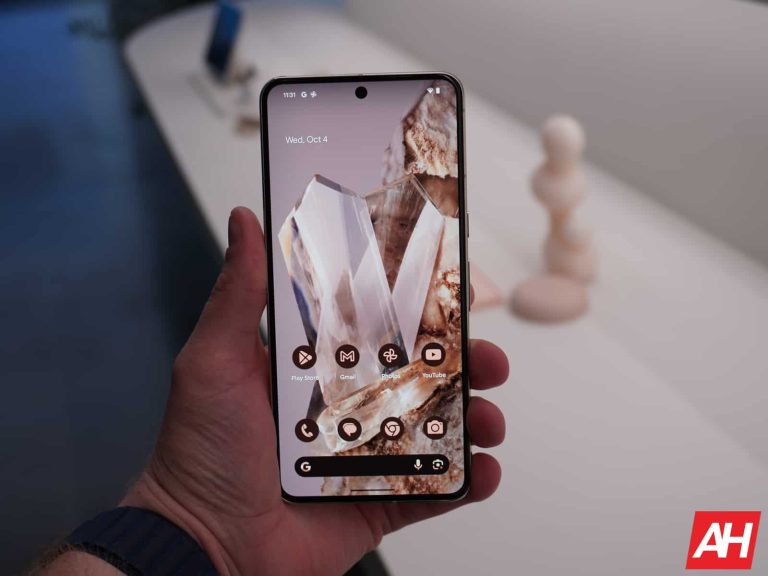
The Google Pixel 8 and Pixel 8 Pro wallpapers are now available to download

These wallpapers are actually specifically made to color-match the Pixel 8 and Pixel 8 Pro models. Google announced Bay, Hazel, Obsidian, Porcelain, and Rose color variants of its new flagships. Well, some of these colors are exclusive to one device, like Bay for the Pixel 8 Pro, for example.

In any case, the point is that these colors are kind of made for the colors of the phones. Andrew Zuckerman created them, and the theme he used is ‘Minerals’. You can check out all the wallpapers in the gallery below, and you’ll immediately realize why the theme is ‘Minerals’.

Now, do note that the images shown in the gallery are compressed, just to show you what you’re getting. If you’d like to grab them in their full size, you’ll need to tap the link below the article.

Once you download them, setting the wallpaper is easy, just do it like you’d do it with any other image. You can either long-press on an empty spot on your home screen, do it via the Settings, or directly from the gallery. It’s up to you.

The Pixel 8 series phones do look quite similar to their predecessors

Now, the Pixel 8 and Pixel 8 Pro do resemble their predecessors quite a bit, but there are some changes. They’re both quite curvy, and the Pixel 8 Pro now has a flat display too. The Pixel 8 is smaller than its predecessor, and also lighter.

Google improved the SoC here, both phones are fueled by the Tensor G3. The cameras have also been improved, though the Pixel 8 Pro comes with most improvements in that regard. It even has some exclusive software features.

Android 14 comes pre-installed on both phones, while it has also started to roll out to a bunch of other Pixel phones.

Download Google Pixel 8 series wallpapers


[ad_2]
Source link