New BEC 3.0 Campaign Exploiting Dropbox for Phishing

0
[ad_1]

According to Checkpoint’s research, a new attack campaign is leveraging Dropbox to send emails that redirect unsuspecting users to credential-harvesting pages.

Business Email Compromise (BEC) campaigns have continuously evolved since researchers first detected it. From gift card scams to emails from compromised accounts, threat actors have tried a wide range of tactics, and now we have BEC 3.0, in which legitimate services are spoofed to lure innocent users.

This new technique is gaining popularity among threat actors, which is a concerning issue because detecting foul play is difficult as the email is sent from a legitimate platform.

The same technique has been used in the new BEC 3.0 campaign discovered by Checkpoint Harmoney email researchers. In this attack, threat actors are exploiting Dropbox. This is an active campaign, with 5,440 attacks detected in the first two weeks of September.

According to Checkpoint’s report, attackers create fake login pages on Dropbox and use them to send emails to unsuspecting users and eventually steal their credentials by redirecting them to a malicious URL. The catch in this attack is the email, which is the standard mail sent by Dropbox notifying the recipient to view a document.

The phishing email (Checkpoint Harmoney)

The user is then requested to visit a legitimate Dropbox page. This page is similar to the OneDrive page, but the URL is hosted on Dropbox. The document is available on this page. When users click Get Document, they will be redirected to another page. This page is maliciously designed to steal users’ login credentials.

BEC 3.0 attacks are easier because scammers can exploit legitimate services and deceive users.

“These attacks are increasing, and hackers are using all your favourite productivity sites—Google, Dropbox, QuickBooks, PayPal, and more. It’s one of the cleverer innovations we’ve seen, and given the scale of this attack thus far, it’s one of the most popular and effective,” read Checkpoint’s blog post.

Checkpoint informed Dropbox about this campaign on 18th September. To stay safe, end-users must remain vigilant and check the sender before opening a document or responding to the instructions in the email. In this attack, the fact that a Dropbox document is hosted on a One Drive look-alike page is enough to raise suspicion.

Moreover, researchers urge users to adopt AI-powered technology that can identify phishing indicators and thwart complex attacks. Lastly, a robust URL protection and comprehensive security solution is essential to protect browsers and documents.

  1. Dropbox, Linkedin hacker sentenced to 7 years in prison
  2. Chinese Group ‘Admin338’ Use DropBox To Deliver Their Payload
  3. MoleRats using Facebook, Dropbox, Google Docs to spread malware

[ad_2]
Source link

iPhone is scared about the future in Google’s new Pixel ad

0
[ad_1]

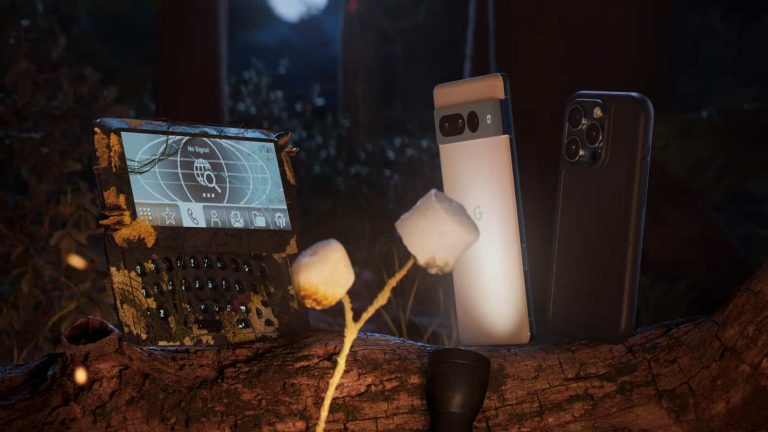
Google has once again decided to poke some fun at Apple. It rolled out another one of its #BestFriendsForever ads, even though the hashtag now is #BestPhonesForever, for some reason. This time around, the iPhone talks to the Pixel, and admits it’s scared about the future.

The iPhone is scared about the future in Google’s latest Pixel ad

This ad takes place in the forest, in a spooky setting. It starts with the Pixel 7 Pro telling a scary story to an unnamed iPhone. For legal reasons, the phone has a case on, and a model is not mentioned, but it looks like one of the ‘Pro’ iPhones. Google also clarifies that ‘iPhone’ is Apple’s trademark.

In any case, the scary story is about a physical QWERTY keyboard, and the Pixel got cut off by an iPhone during it. The phone admits it’s worried about the future. Then mentions that a Pixel event is coming, and that the attention may be shifted to it.

Google decides to throw shade at Apple via this ad, as it gets iPhone to mention the Action Button, “Dynamic-er Island”, and a USB-C port as its only “innovations” (referring to the iPhone 15 Pro series). The Pixel 7 Pro is trying to comfort the iPhone, of course, as was the case a number of times thus far in these ads.

A phone with a QWERTY keyboard makes an appearance too

Towards the end of the ad, a phone with a QWERTY keyboard jumps out, and scares both devices. They all become friends at the end, though. It’s another fun and entertaining ad from Google, and yet again some fingers were pointed.

As many of you know, Google’s Pixel event is coming. It will take place on October 4, or in other words, on Wednesday next week. The Pixel 8, Pixel 8 Pro, and the Pixel Watch 2 will be announced during the show.

The company’s upcoming devices have been leaking intensively over the last couple of weeks. So there’s really not much to hide at this point. Still, Google could have some aces left in its sleeve.


[ad_2]
Source link

DOJ files lawsuit against eBay over environmental violations

0
[ad_1]

In a recent development, the Department of Justice (DOJ) has reportedly filed a lawsuit against eBay for allegedly selling environmentally harmful products and violating the Clean Air Act and other environmental regulations.

The lawsuit, filed on behalf of the U.S. Environmental Protection Agency in a federal court in Brooklyn, NY, alleges that eBay has sold over 343,000 aftermarket “defeat devices,” which are designed to circumvent vehicle emission controls, thus allowing manipulation of emissions tests and giving a fake appearance of compliance with EPA standards. As a result, eBay could face penalties of $5,580 for each violation of the Clean Air Act.

In addition to these allegations, there are concerns about other violations. Such as eBay violating the Federal Insecticide, Fungicide, and Rodenticide Act (FIFRA) and the Toxic Substances Control Act (TSCA). This is because the lawsuit claims that eBay sold over 23,000 unregistered and toxic pesticides. Along with products making fake claims about protecting against the SARS-CoV-2 virus. To make matters worse, eBay also allegedly sold 5,614 harmful paint and coating removal products. These allegedly contained methylene chloride, a chemical known to cause brain and liver cancer.

“The complaint filed today demonstrates that EPA will hold online retailers responsible for the unlawful sale of products on their websites that can harm consumers and the environment,” said David M. Uhlmann of the EPA’s office.

eBay’s response to the DOJ lawsuit

eBay, in response to the DOJ lawsuit, has denied all allegations and stated that it plans to “vigorously defend itself.” Moreover, the company emphasized its commitment to maintaining a secure marketplace for its buyers and sellers. Claiming it would allocate significant resources and provide proper training to its teams to prevent the listing of banned items.

“Indeed, eBay is blocking and removing more than 99.9% of the listings for the products cited by the DOJ, including millions of listings each year. And eBay has partnered closely with law enforcement, including the DOJ, for over two decades on identifying emerging risks and assisting with prevention and enforcement,” said eBay.


[ad_2]
Source link

Samsung Galaxy S24 Ultra leak shows its flat display

0
[ad_1]

Earlier today, we got our first look at the Samsung Galaxy S24 courtesy of CAD-based renders shared by reliable leakster OnLeaks. The same source has now given us an exclusive look at the Galaxy S24 Ultra. The leakster has teamed up with SmartPrix to share multiple renders and a 360-degree video of the next-gen Samsung flagship.

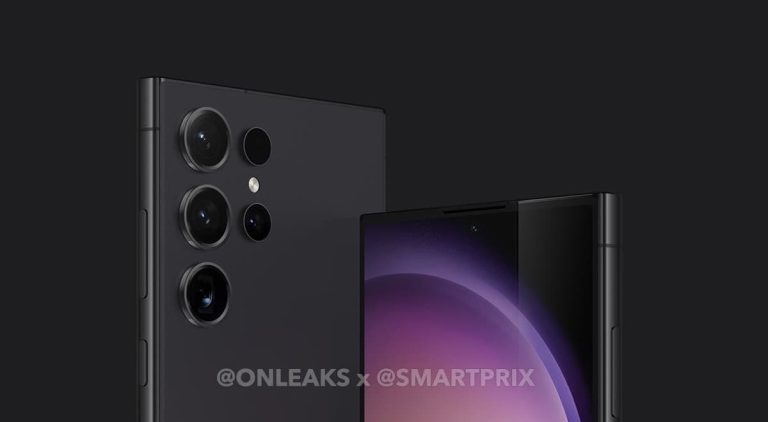
Leaked Galaxy S24 Ultra renders confirm a flat display

You might have come across rumors that Samsung will switch to a flat display on the Galaxy S24 Ultra, ditching the tradition of curved displays on its most expensive S-Series phone. The newly leaked renders confirm this redesign. The screen is still a 6.8-inch panel, but it no longer has curves on the edges. This change means you’ll notice bezels on the two sides, while Samsung seems to have shrunk top and bottom bezels for a symmetrical front design.

With no curve display, the Korean firm has made the Galaxy S24 Ultra slightly wider to keep a 6.8-inch screen (78.1mm vs. 79mm). The new phone is also slightly shorter (163.4mm vs. 162.3mm) and thinner (8.9mm vs. 8.6mm). The rest of the design doesn’t change much, though. We are still getting a boxy design with flat edges and sharper corners than the regular Galaxy S24, which is getting flatter edges too.

The power and volume buttons sit on the right side, with Samsung making room here for the UWB (Ultra-Wideband) antenna as well. Similar to the base model, the Galaxy S24 Ultra also has two holes at the top. The bottom edge houses the USB Type-C port, speaker, microphone, SIM tray, and the S Pen slot. The left side is blank with no holes, ports, or buttons. All we can see is an antenna line, which is found on other sides as well.

The rear camera array is unchanged

Coming to the cameras, Samsung appears to be making its so-called “signature Galaxy design” permanent. As you can see, there’s no camera bump with sensors protruding out of the back panel. We have three cameras stacked vertically in one column, with the laser autofocus sensor, LED flash, and a fourth camera sitting next to them. Rumors are that Samsung is replacing the 10x zoom camera with a 5x unit next year.

The Galaxy S24 series is rumored to arrive a couple of weeks earlier than the Galaxy S23. If these rumors turn out to be accurate, we should see the phones go official in mid-January next year. In the interim, you can expect plenty more leaks about the phones, including more renders and detailed specifications. We will keep you posted accordingly.


[ad_2]
Source link

The Meta Quest 3 won’t support some Quest 2 accessories

0
[ad_1]

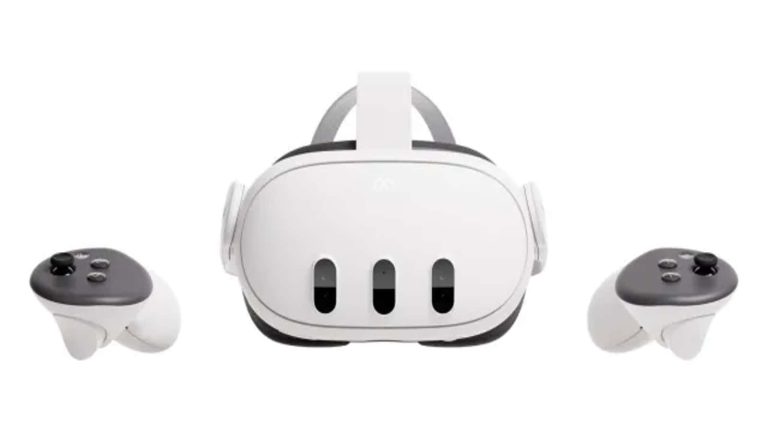
Meta Quest 2 owners may have to say goodbye to some of their accessories if they plan to upgrade to the Quest 3. According to a new report from Android Central, most accessories for the Quest 2 won’t be supported by the Quest 3.

That’s not entirely surprising since there were more than a few changes to update the design of the headset. Like new thicker arms on the side to fit the larger speakers. Because of this physical change the Quest 2 straps are the incorrect size. Though Android Central notes that this could be rectified by modding the straps in some way. That being said some manufacturers may end up releasing kits that allow the older straps to fit.

In addition to the older headset straps, some of your other favorite accessories might just be obsolete.

The Quest 3 may not support Quest 2 face covers

Another accessory that may not be compatible are the face covers. This goes for any potential aftermarket options that you may have purchased. Such as the one that Razer released back at the end of March. This hasn’t necessarily been confirmed yet, but it seems quite possible due to the changes to the lenses and the new face gasket. So if you had an aftermarket face cover, you might have to get a new one for the Quest 3 VR headset.

Other accessories that may not work include the straps for the controllers and specific charging docks. As the Quest 3 moves the USB-C charging port to the inside of the arm. And this new placement may make older docks incompatible. This last part might not be so bad given Meta’s new official wireless charging dock. Though if you wanted to save money, it might not be in the cards. Still, it’s always safe to assume that with certain tech products, an upgrade to the main product may lead to required upgrades for accessories. And that seems to be the case here.


[ad_2]
Source link

Update Chrome now! Google patches another actively exploited vulnerability

0
[ad_1]

Google has updated its Chrome Stable Channel to fix, among other things, an actively exploited vulnerability

Google has updated the Stable Channel for Chrome to 117.0.5938.132 for Windows, Mac and Linux. This update includes ten security fixes. According to Google there is an active exploit for one of the patched vulnerabilities, which means cybercriminals are aware of the vulnerability and are using it.

The easiest way to update Chrome is to allow it to update automatically, which basically uses the same method as outlined below but does not require your attention. But you can end up lagging behind if you never close the browser or if something goes wrong—such as an extension stopping you from updating the browser.

So, it doesn’t hurt to check now and then. And now would be a good time, given the severity of the vulnerabilities in this batch. My preferred method is to have Chrome open the page chrome://settings/help which you can also find by clicking Settings > About Chrome.

If there is an update available, Chrome will notify you and start downloading it. Then all you have to do is relaunch the browser in order for the update to complete.

screenshot of up-to-date Chrome

After the update, the version should be 117.0.5938.132 for Windows, or later.

Google never gives out a lot of information about vulnerabilities, for obvious reasons. Access to bug details and links may be kept restricted until a majority of users are updated with a fix. However, from the update page we can learn a few things.

The Common Vulnerabilities and Exposures (CVE) database lists publicly disclosed computer security flaws. The zero-day patched in this update is listed as CVE-2023-5217, which is described as a heap buffer overflow in vp8 encoding in libvpx.

A buffer overflow is a type of software vulnerability that exists when an area of memory within a software application reaches its address boundary and writes into an adjacent memory region. In software exploit code, two common areas that are targeted for overflows are the stack and the heap.

The heap is an area of memory made available for use by the program. The program can request blocks of memory for its use within the heap. In order to allocate a block of some size, the program makes an explicit request by calling the heap allocation operation.

The open source video codec library libvpx serves as the reference software implementation for the VP8 and VP9 video coding formats. Reportedly, the  weakness lies in the VP8 encoding part of the library. The exploitation occurs when a program uses one method to allocate or initialize a resource, but an incompatible method then accesses that resource, potentially providing unsecured access to the browser’s memory.

As we have seen, such attacks can be leveraged in an attack chain to fully compromise a vulnerable device. And given the huge Chrome userbase, this makes the browser an attractive target. Libvpx, as part of the WebM Project, is used in many other applications, so there could be more updates coming your way.


We don’t just report on vulnerabilities—we identify them, and prioritize action.

Cybersecurity risks should never spread beyond a headline. Keep vulnerabilities in tow by using Malwarebytes Vulnerability and Patch Management.


[ad_2]
Source link

Leaks have surfaced of the new Pixel Buds Pro colors

0
[ad_1]

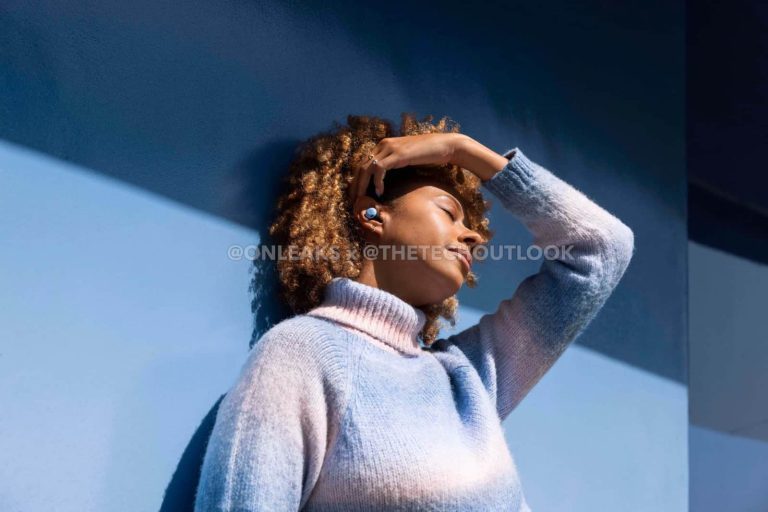
New colors of the Pixel Buds Pro have leaked just days ahead of Google’s Fall event on October 4 where they were suspected to be revealed. The leaks come from The Tech Outlook and show off several closeup images of the products. And for good measure it appears there’s two marketing images included so you can see what they look like when people have them in.

Outside of the new colors, there’s nothing new to see here. These are the same Pixel Buds Pro that are already available. Just in different shades than before. However, they might be right up your alley if you didn’t like any of the previous color options. Which currently includes Charcoal, Fog, Lemongrass, and Coral.

In addition to showing off the new colors, the leak also mentions what are allegedly the official color names.

The new Pixel Buds Pro colors are said to be “Bay Blue” and “Porcelain”

Previous leaks had suggested that Google’s upcoming devices would have a Sky Blue color option. But it seems that won’t be the case. Instead, the color will be called Bay Blue. The white color of the upcoming products is going to be called Porcelain according to the leak. Though that’s no surprise given Google already uses that name for some of its other products.

There’s no other new information about these upcoming earbuds other than the color names. But pricing and availability are expected to be the same as the already available options. Pending stock doesn’t quickly deplete after their launch. In which case they could end up hard to find. Google is expected to reveal the new Pixel 8 and Pixel 8 Pro in addition to the Pixel Watch 2 alongside these new earbud colors.

All of which should be available not long after the official reveal as Google usually launches its flagship products the same month it announces them.


[ad_2]
Source link

Tim Cook confirms Apple is working on generative AI

0
[ad_1]

Apple CEO Tim Cook has finally confirmed that his company is jumping into the AI bandwagon by focusing on generative AI, Phonearena (via Apple Insider) reports.

The AI space is currently divided between Microsoft and Google. In the early days of the ChatGPT launch, Microsoft seized the opportunity to invest in the parent company, OpenAI, and get access to the tech behind the chatbot. Google also launched the Bard chatbot in response. This game could have a new player soon.

Speaking to UK media, Tim Cook confirmed Apple is working on generative AI and hiring related staff in the UK. “We’re hiring in that area, yes, and so I do expect [recruitment] to increase,” Cook said.

Apple might launch a rival for ChatGPT, Tim Cook confirms

The chief Apple executive stated that the company uses AI in all its products, including Fall Detection on the Apple Watch, Crash Detection, atrial fibrillation detection, ECG, and predictive typing on the iPhone. Additionally, Cook said Apple is evaluating the possibility of launching a ChatGPT-like service.

Apple’s interest in launching an AI chatbot, like ChatGPT, could impact the whole industry and add fuel to the fire of competition with Google and Microsoft. A dedicated Apple-designed AI chatbot on iPhones, iPads, and Macbooks would excite customers and enhance the user experience. Of course, Apple’s ChatGPT-like service might not come anytime soon.

Apple’s approach toward AI is interesting. Instead of bragging about AI and how it can affect users’ lives, Apple simply tries to improve its devices and user’s experience with AI. In WWDC 2023, the company unveiled AI additions to its products, like the iPhone’s ability to identify a user’s pet or a Digital Persona feature. In another example, AirPods Pro can automatically turn off noise canceling when a user starts to talk with another person.

Ultimately, Tim Cook asserted Apple’s commitment to the UK’s “vibrant” tech economy. The UK currently hosts Apple’s third largest employee population, and it’s a leading developer community for Europe, according to Cook.

Competition is AI space is getting tighter everyday, and once in a while, a new company steps in to launch an AI-driven service. Beside AI services, the AI hardware is also getting the eyes of investors. Apple’s former designer Jony Ive is reportedly in talks with OpenAI’s Sam Altman to develop an AI gadget.


[ad_2]
Source link

Dependabot impersonators cause trouble on GitHub

0
[ad_1]

We take a look at a clever attack imitating GitHub’s Dependabot in order to publish rogue project updates.

GitHub is experiencing issues of the “breached account and malicious code” variety. ITPro reports that unnamed individuals have been compromising accounts and using them to install malware capable of password theft. It’s a fairly elaborate scam which even includes imitation of GitHub’s popular Dependabot feature.

To make this scam work, attackers first obtained access tokens belonging to their targets. Once the attackers have control over the stolen accounts, they would change the alias for said accounts to “Dependabot[bot]” and begin making potentially dangerous code commits.

If you’re unfamiliar with the language of GitHub, don’t worry. GitHub is the place where developers can manage their project code. Bug tracking, software feature requests, task management, and wikis for each and every project are available to users.

When a developer is writing their code, they can eventually publish from their local workstation to GitHub’s staging directory. At this point, a “Commit” is made. The Commit is another way of saying “a snapshot”, a version of your project as it exists at a specific moment in time.

In this case, the attackers deploy malicious code into the projects they hijack. They then steal secrets from the compromised project and send it back to base. Additionally, existing JavaScript files already present in the project are tampered with to add malware. Said malware will attempt to steal passwords from form submissions and send them to the command and control server run by the attackers. Stolen tokens gave access to many private repositories so both public and private projects were impacted.

In terms of how the attackers initially got in, some accounts were found to have been taken over by stolen personal access tokens. As Bleeping Computer notes, these tokens allowed developers to access GitHub without having to make use of two-factor authentication (2FA) steps. 

With the tokens stored locally on the developer’s machine, it’s possible that someone hijacking the system could easily grab the tokens required to breach individual GitHub accounts. Whether this was achieved by malware, social engineering or phishing, nobody has the answers at time of writing.

The sneaky part of this escapade is the imitation of the previously mentioned Dependabot. This helpful addition to GitHub assists developers in keeping on top of their project and all associated dependencies tied to it. Dependabot automates dependency updating tasks which helps to keep security issues at bay.

What’s happening up above is that the attackers are disguising their bogus updates under the visage of Dependabot. If you’re on GitHub for any length of time, seeing Dependabot popping up in relation to an update is commonplace. As a result, seeing the imitation Dependabot on a page is going to fool quite a few people who will assume all is well.

While the imitation helper isn’t perfect and doesn’t replicate the real thing exactly, those behind this will still reap some rewards. If you’re wanting to be on the lookout for fake Dependabot posts, the most overt signifier of fake activity is the profile avatar. Dependabot has a square profile image and a “bot” tag. Regular accounts have a circular avatar and are also unable to properly replicate the bot tag signifier.

Fake commit attacks have been seen before using a variety of techniques, but imitating the bot helper is new. It’s also somewhat ironic to see a GitHub function dedicated to keeping things secure being imitated in a way which severely impacts the safety of platform users. It may be that GitHub makes the Dependabot even more distinctive than it already is to help ward off future similar attacks.

Stay safe out there!


We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.


[ad_2]
Source link

Apple iPhone 15 Pro Max display gets strong DXOMark ranking

0
[ad_1]

Test scores for the iPhone 15 Pro Max display are now available as the device secures the top 5 spots on the DXOMark ranking. Over the years, DXOMark has become reputable in its test rankings and set the testing bars for various smartphones in different categories. The results from the reviews and scientific testing of DXOMark for the iPhone 15 Pro Max display are now here.

As you might expect, the display test results for the 15 Pro Max prove its flagship identity. Once again, this Pro-series device cements Apple’s name across various DXOMark testing categories. Some major testing categories that users look out for on these tests are display, camera, and audio.

This article will focus on the display testing and score of the new iPhone 15 Pro Max. Over the years, Apple has done a good job with the displays on their devices, especially the Pro models. You might be wondering how this new entry performed under DXOMark’s display testing, here are the details you need.

The iPhone 15 Pro Max ranks 4th on DXOMark display testing, falling behind other premium devices

Making the top 5 list of DXOMark’s top-performing device displays is the iPhone 15 Pro Max. This new flagship device scores 149 on the test and this is impressive but leaves a lot to the imagination. The fourth place is shared by a total of four devices, three of which are from Apple and one from their sworn rivals, Samsung.

Apple iPhone 15 Pro Max, 14 Pro Max, and 14 Pro are the three devices from the Cupertino-based company in fourth place. From Samsung’s side is the company’s new clamshell folding device, the Galaxy Flip 5. All four devices have a score of 149. Ahead of them is the Honor Magic 5 Pro and Google Pixel Fold in second place with a score of 151.

Topping the list is the Samsung Galaxy Z Fold 5 with a score of 152, three points ahead of Apple’s new flagship. However, in comparison with its predecessor, the new device from Apple comes with little or no display improvements. Out of all six major display tests, the new top-of-the-line Apple flagship device saw improvements in only two areas.

In two display test areas, the new flagship let it hands down in comparison with its predecessor. The areas of display improvements are Artifacts and Motion, where the decline is in Video and Color. However, display test areas such as Readability and Touch stay the same.

Could the display performance of the iPhone 15 Pro Max have been any better? That question will be left to Apple because the display is very good in comparison with other flagship devices. Over the years, the Cupertino-based tech company has done well in terms of the displays on their flagship device, but some improvements will make things better.


[ad_2]
Source link