5 reasons why you should buy the Garmin Venu 3

0
[ad_1]

Last week Garmin launched its latest sports watch that you can buy, the Venu 3. It retails for $449.99 and supports both Android and iOS. Being this is the third-generation of the watch in Garmin’s Venu series, it’s Garmin’s most refined model yet. With tons of improvements and new features. Making it a well-rounded sports watch for those who already live or want to live a more active lifestyle.

Now you might be asking, “why should I buy the Garmin Venu 3?” And that’s a valid question. I mean, there are plenty of smartwatches and sports watches out there. What makes Garmin’s latest a better option or what makes it worth my hard-earned money. At the end of the day, only you can decide if the watch is right for you, but we can tell you why you should at the very least consider the Garmin Venu 3 as your next watch.

With that said, let’s go over some reasons that we think are excellent representations of why this is a watch you definitely want.

Garmin Venu 3 – Best Buy

You should buy the Garmin Venu 3 because it has better battery life than most smartwatches

The biggest reason you should buy the Garmin Venu 3 is battery life. Most smartwatches, including the Apple Watch, and just about every single Wear OS watch, all have at best, passable battery life. Some, like the Galaxy Watch 5 Pro do last longer and are good for a Wear OS watch. But not necessarily good compared to all smartwatches and sports watches.

With the watches that come from Garmin, it’s rare you won’t find one that lasts for several days in smartwatch mode. The Venu 3 is no different here. It can last for up to 14 days on a single charge. Two whole weeks. In smartwatch mode with access to all or most of the best features the watch has to offer. Like connected apps, smartphone notifications, activity and sleep tracking and much, much more.

You can pull this thing off the charger and not have to worry about the battery for quite a few days. That is unless you’re using things like GPS for extended periods of time. Then you’ll want to at the very least check the battery by the end of the day. But when you aren’t using those features with more heavy battery drain, and that’s likely to be the case most of the time, don’t expect the battery to die until much later. No one needs one more thing to worry about having to charge every or every other night. The Venu 3 gives you peace of mind in that regard.

The wheelchair mode makes this a more inclusive smartwatch

Garmin Venu 3 Wheelchair Mode

This is a really neat feature that you won’t see everywhere. If honestly, anywhere else at all. For those who happen to be in a wheelchair but are still quite active, the Venu 3 offers a wheelchair mode. Maybe you weren’t aware this was a thing and if not, we’re happy to bring it to your attention.

The wheelchair mode works to track pushes instead of steps. It also supports tracking handcycle movements and gives wheelchair users an animated representation of wheelchair-specific workouts. If you’re in a wheelchair and want a sports watch that is more tailored to you, the Garmin Venu 3 is that watch.

Safety and tracking features if you need help

Hopefully the safety and tracking features are ones you’ll never have to use. But it is nice that they’re there just in case. Because it’s better to be prepared. As they say, it’s better to have and not need, then to need and not have.

With the safety and tracking features on Garmin’s Venu 3 watch, should you need help in a particularly dangerous situation, the watch can alert your emergency contacts. Now you do have to set this feature up. That means adding emergency contacts to the watch through the companion app. The watch also needs to be paired to a smartphone so in the event of needing to alert an emergency contact, it can.

Once set up, emergency contacts will be alerted through message or voice call during certain events, such as incident detection, and be given your location. Your phone does need to have network coverage for this to work. But it could be a lifesaving feature and that’s even more peace of mind.

The nap tracking is a next-level feature

Garmin Venu 3 Nap Tracking

It’s simple. And yet, one of the best features we’ve seen on a watch in a while. Naps are not to be taken for granted. Because a good nap can be just what you need to recharge your body and your mind. With the Garmin Venu 3, you can set up the watch to automatically track naps. The watch can use this feature to log your nap length and that information gets used for even more insightful features. For instance, the watch will tell you how the length of your naps is impacting things like the Body Battery feature. Or how it impacts your energy monitoring.

Since you probably aren’t planning your naps out, the automatic nap tracking ends up being pretty useful. And it’s a great companion feature to the sleep tracking which provides even more insights to how your rests are impacting everything from your workouts to your daily routine.

Coaching by Garmin to help you prepare for your next big race

Another good reason to buy the Garmin Venu 3 is the Garmin Coach. Some people thrive off having a coach to help them through training. And the Garmin Coach can certainly be that if needed.

With this feature, you get assisted coaching in preparing you for your next big 5K, 10K, or half marathon. You can set goals for yourself and then train with one of three Garmin Coaches and get a new dynamic training plan that changes based on the performance of your last training sessions. So the training plans move with you.

There’s also the animated workouts to help you ensure you’re doing everything the way you’re supposed to and motivate you get through your toughest workouts. The animated workouts support cardio training, Pilates, HIIT and yoga, and even strength training.

Garmin Venu 3 – Best Buy


[ad_2]
Source link

Microsoft Teams will let you revist old meeting, but at a cost

0
[ad_1]

If you use Microsoft Office for work, then you most definitely use Microsoft Teams to conduct your meetings. Meetings are often full to the brim with useful information, and retrieving that information can be a pain. Well, Microsoft Teams will let you revisit and record your old meetings. However, this does come at a cost.

Speaking of Microsoft Teams, Microsoft has unbundled Teams from Office in Europe, which is unfortunate. Before you get your pitchforks out, this wasn’t entirely Microsoft’s decision.

Not too long ago, Slack CEO Eric Yuan asked the EU to look into Microsoft about it bundling Teams with Office as a possible antitrust violation. This prompted the company to unbundle the services in Europe. Yuan has since asked the United States FTC to investigate as well.

You can revisit your old Teams meetings but at a cost

If you need to recall something from a meeting that you didn’t write down or go over what was said, Microsoft now gives you the ability to do so. According to Techradar, Microsoft released an API that will allow you to pull transcripts from past meetings.

This will cost the user .24¢ per minute. So, if you pull a full hour, then it will cost you about 14¢. That’s not much if you’re just going back through a few meetings, but if your meetings go long, or if you need to sift through a ton of meetings, then the costs will add up.

What if you want to pull actual recordings? Well, you can do this as well. This will cost a bit more money at 3¢ per minute. So, pulling a full hour would cost you $1.80. Again, in the grand scheme of things, that’s not a lot. However, the costs could rack up if you need to pull a bunch of recordings.

If you use Microsoft Teams in the US, keep an eye out for any new changes coming down the road. If the FTC looks into Microsoft as per Slack’s request, then Teams might be unbundled from Office.


[ad_2]
Source link

Hackers Steal Over $5,700 from ATMs Using Raspberry Pi

0
[ad_1]

The Raspberry Pi is a budget-friendly Linux computer system board that features GPIO pins for physical computing and IoT exploration. However, besides this, threat actors also abuse this board for several illicit purposes as well.

Recent arrests in Lubbock involve three men accused of using electronic devices to steal money from regional ATMs, as revealed in court documents from EverythingLubbock.

At a hotel in the 6600 block of I-27 on August 3, the following three accused were arrested:-

  • Abel Valdes, 38
  • Yordanesz Sanchez, 41
  • Carlos Jordano Herrera-Ruiz, 33

Hackers Robbed ATMs Using Raspberry Pi 

However, it’s been unveiled that the authorities in Lubbock were already alerted to a group stealing substantial amounts of US currency from ATMs in West Texas, as reported by the Texas Financial Crime Taskforce.

In this event, to access the cash drawer, the trio employed a “Raspberry Pi” device to disable ATM security.

Before the arrest from a 50th Street ATM, the accused had stolen more than $5700 by using Raspberry Pi devices.

Moreover, it’s been detailed in the court documents that authorities found two Raspberry Pi devices in the suspects’ hotel room.

The specific Pi model used by the hackers during this event and their exact use in bypassing security remain unspecified and unconfirmed.

Criminal Offenses

The accused were charged with the following criminal offenses:-

  • Unlawful Interception
  • Use or Disclosure of Wire
  • Oral or Electronic Communications
  • Engaging in criminal activity
  • Forgery

Besides this, at the moment, the accused trio is in federal detention at the Lubbock County Detention Center.

Keep informed about the latest Cyber Security News by following us on Google News, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

Samsung releases September security update, reveals details

0
[ad_1]

Samsung has revealed the details of the September 2023 security update for Galaxy devices. The latest security patch contains fixes for more than 60 vulnerabilities of varying severity. The Korean firm has already related the update for the Galaxy A14 5G, with other eligible models to follow soon.

According to Samsung, the September SMR (Security Maintenance Release) for Galaxy devices contains 23 Android OS patches. These patches are part of Google’s latest Android Security Bulletin (ASB). Four of these are critical vulnerabilities that could allow bad actors to remotely gain access to an affected phone. The rest were labeled high-severity vulnerabilities by Google.

As usual, the latest ASB also contains some patches that don’t apply to Samsung devices. On the other hand, the Korean firm fixed 35 Galaxy-specific security issues this month. Called Samsung Vulnerabilities and Exposures (SVEs), these flaws don’t exist on Android products from other brands. Samsung hasn’t detailed them all out of security reasons, but we have information about a few SVEs patched with the September SMR.

One of them was a high-severity issue caused by improper access control in Dual Messenger. It allowed local attackers to launch activity with system privilege. Another high-severity issue in Settings Suggestions caused by improper input validation allowed attackers to launch arbitrary activity. Samsung also patched issues with KnoxAI, One UI Home, Samsung Keyboard, LockSettings, and many other system apps and services.

The September SMR for Galaxy devices also contains four Samsung Semiconductor patches. One of those was a moderate severity issue caused by improper authorization of 5G NAS (network-attached storage) messages. These issues affected various Exynos chipsets and modems, including processors found inside smartphones, wearable devices, and automotive products.

The Galaxy A14 5G is getting Samsung’s September security update

All of the aforementioned security patches are already rolling out to the Galaxy A14 5G. The new budget smartphone is currently picking up the September SMR in Malaysia, SamMobile reports. The updated firmware build number for the phone is A146PXXU4BWH4. It’s unclear if Samsung is pushing anything more to the device or if it’s just the latest security update.

Nonetheless, the September security patch should soon reach more Galaxy devices. While flagship models usually get priority, there’s no hard and fast rule. If you’re holding a Samsung device, watch out for an update in the coming days. That’s unless you have a Galaxy Note 10. The Korean firm has ended software support for the 2019 Note series. They will no longer get new updates.


[ad_2]
Source link

Android users might switch to iPhone 15 for this feature

0
[ad_1]

The iPhone 15 series is actually shaping up to be a pretty big upgrade for the iPhone this year. We were not originally expecting it to be much of a redesign, nor bring in new features. But it’s doing both. And the biggest new feature it is bringing in is, USB-C.

That lead SellCell to conduct a survey and see if that might make some Android users witch to the iPhone. And well, it looks like a good number of them would. Now this is a small sample size, as SellCell surveyed only 1,000 iPhone and 1,000 Android users in the US. Existing iPhone users, 63% said that Apple moving to USB-C would influence their decision to upgrade to the iPhone 15. Surprisingly, only 37% said they would upgrade because of USB-C as it would allow them to use one cable to charge everything.

44% of Android users said they would be tempted to switch

In this same survey, about 44% of existing Android owners surveyed said that they would be tempted to buy an iPhone 15 if Apple adopts a USB-C port. Of that 44%, about 35% said that their motivation stemmed from the fact that the iPhone would now work with their existing non-Apple chargers.

Now as to how many would buy an iPhone 15? Well, 66% of the group said they would not be buying one. While about 34% said they would potentially upgrade to the iPhone 15.

While these groups are pretty small, they are also not all that surprising. Most Android users aren’t looking to switch to the iPhone, because then they’d have to leave the Android ecosystem – whether that be Google, Samsung or another company. And start over in another ecosystem. Not to mention they’d have to re-buy all of their apps. But the number of iPhone users willing to upgrade because of USB-C is a bit surprising. As this means they need new cables and potentially new charging bricks too.


[ad_2]
Source link

Hackers Use Flipper Device to Attack Nearby iPhone

0
[ad_1]

Flipper Zero Devices have been discovered with the capability to perform Denial of Service attacks on iPhones.

Threat actors can probably spam the iPhones with so many pop-ups prompting about nearby AirTag, Apple TV, AirPods, and other Apple devices.

Moreover, Flipper Zero Devices can also perform wireless attacks that target car keyfobs, RFID cards, iPhones, and many more.

Security Researcher Anthony, who discovered this attack, termed this as “a Bluetooth advertising assault”.

Flipper Zero Attack Nearby iPhones

Flipper Zero firmware can be used for conducting a broadcast called “Bluetooth Advertising,” which is a type of transmission in the Bluetooth Low Energy protocol used by Apple for enabling iDevice users to connect to Apple Watch and other Apple devices and send pictures using the Bluetooth file sharing system AirDrop.

TechCrunch was able to replicate the vulnerabilities in both the iPhone 8 and the recently released iPhone 14 Pro models, which could potentially be exploited by attackers.

This was done by changing the Flipper Zero firmware with a custom compiled code. After this, a simple switching “ON” of Bluetooth from Flipper Zero begins the broadcasting of pop-up signals to nearby iPhones.

“The exploits worked on iPhones both when Bluetooth was enabled or switched off in the Control Center, but could not reproduce the exploit when Bluetooth was fully switched off from the Settings,”.

Furthermore, the researcher (Anthony) also said that he was able to create an attack that can broadcast signals over longer distances, even miles, and create pop-ups with millions of devices spamming at a high range.

However, he is not providing more details about the attack as it could lead to a vast attack surface for threat actors who intend to spam victims.

A complete exploit and research was published by Anthony, providing more information about the Denial of Service (DoS) attack.

He also added that Apple could mitigate this issue by verifying the integrity of the Bluetooth Devices connecting to the iPhones. They can also reduce the distance at which iDevices can connect to other devices using Bluetooth.

Keep informed about the latest Cyber Security News by following us on Google News, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

New Agent Tesla Variant Uses Excel Exploit to Infect Windows PC

0
[ad_1]

The new Agent Tesla variant exploits CVE-2017-11882/CVE-2018-0802 vulnerability to execute the malware. 

Key Findings

  • A new variant of the Agent Tesla malware family is being used in a phishing campaign.
  • The malware can steal credentials, keylogging data, and active screenshots from the victim’s device.
  • The malware is spread through a malicious MS Excel attachment in phishing emails.
  • The malware exploits an old security vulnerability (CVE-2017-11882/CVE-2018-0802) to infect Windows devices.
  • The malware ensures persistence even when the device is restarted or the malware process is killed.

New Agent Tesla Variant Detected in Malicious Phishing Campaign

FortiGuard Labs threat researchers have detected a new variant of the notorious Agent Tesla malware family used in a phishing campaign. Report author Xiaopeng Zhang revealed that the malware can steal “credentials, keylogging data, and active screenshots” from the victim’s device. Stolen data is transferred to the malware operator through email or SMTP protocol. The malware mainly infects Windows devices.

For your information, Agent Tesla malware is also offered as a Malware-as-a-Service tool. The malware variants use a data stealer and .NET-based RAT (remote access trojan) for initial access.

How Phishers Trap Users?

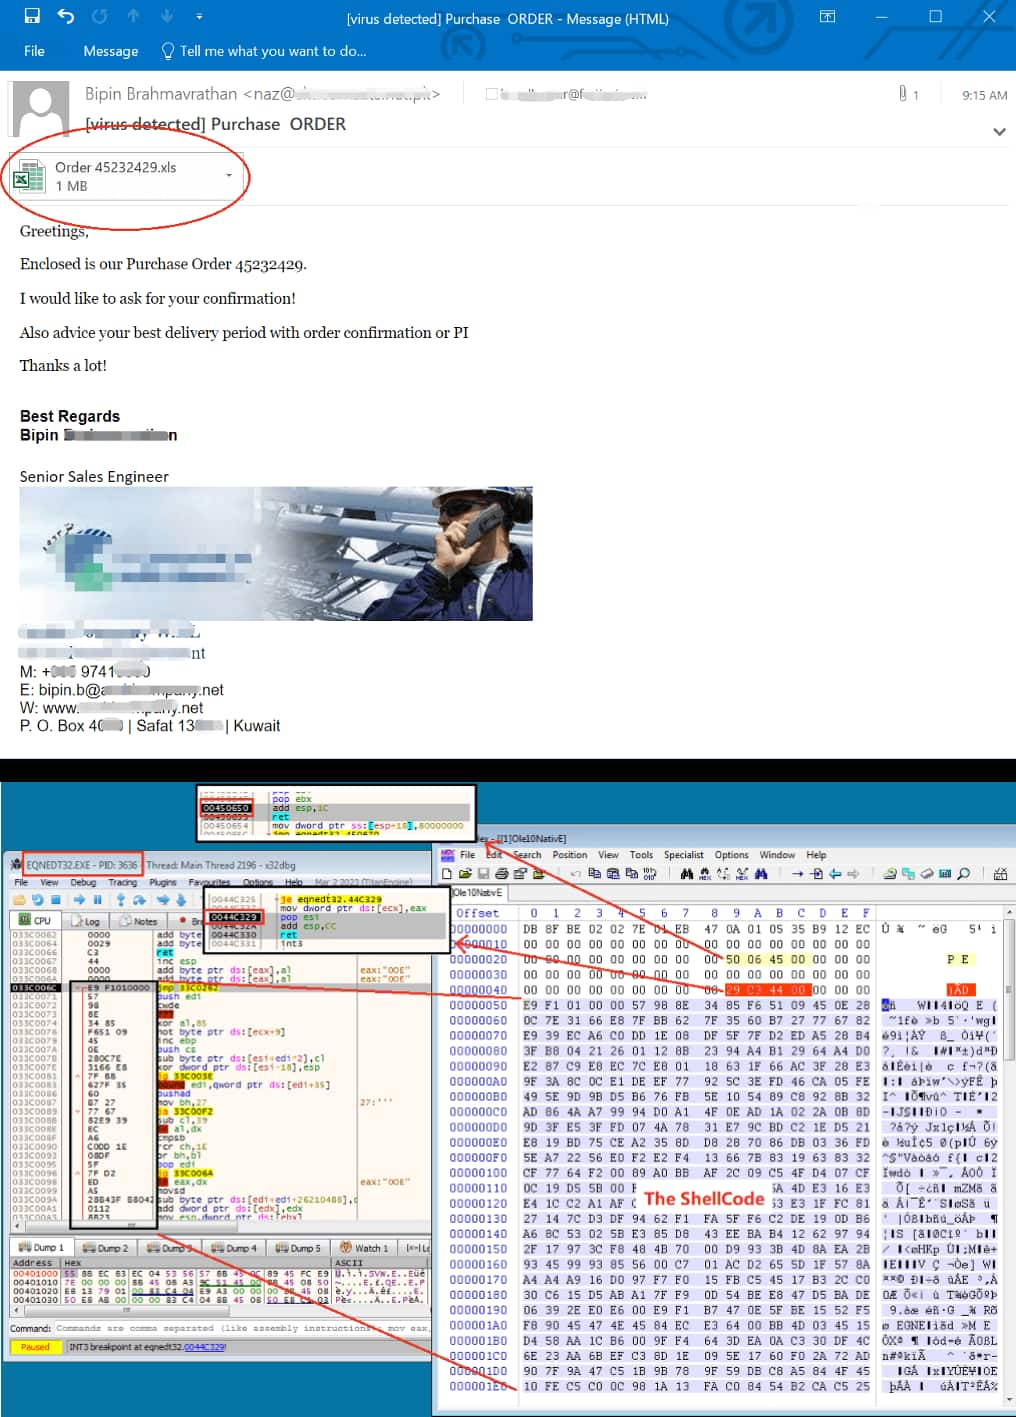
This is a phishing campaign, so initial access is gained through a phishing email designed to trick users into downloading the malware. The email is a Purchase Order notification that asks the recipient to confirm their order from an industrial equipment supplier.

The email contains a malicious MS Excel attachment titled Order 45232429.xls. This document is in OLE format and contains crafted equation data that exploits an old security RCE vulnerability tracked as CVE-2017-11882/CVE-2018-0802 instead of using a VBS macro.

This vulnerability causes memory corruption in the EQNEDT32.EXE process and allows arbitrary code execution through ProcessHollowing method, in which a hacker replaces the executable file’s code with malicious code.

A shellcode download/execute the Agent Tesla file (dasHost.exe) from this link “hxxp://2395.128.195/3355/chromium.exe” onto the targeted device. It is a .NET program protected by IntelliLock and .NET Reactor. Relevant modules are encrypted/encoded in the Resource section to prevent its core module from detection and analysis.

It is worth noting that Microsoft released fixes for this vulnerability in November 2017 and January 2018. However, it is still being exploited by threat actors indicating the presence of unpatched devices. Per FortiGuard research, they observe around 1300 vulnerable devices daily and mitigate 3,000 attacks at the IPS level per day.

New Agent Tesla Malware Uses Excel Exploit to Infect Windows Devices
The phishing email and the ShellCode identified by the researchers (Screenshots: FortiGuard Labs)

Analysis of Agent Tesla Activities

According to FortiGuard Labs’ report, published on 5 Sep 2023, Agent Tesla variant steals stored credentials from web browsers, email clients, FTP clients, etc. There is a long list of targeted software and email clients available here.

The malware sets a keyboard hook through the API SetWindowsHookEx() to monitor low-level keyboard inputs and calls the callback hook procedure “this.EiqpViCm9()” whenever the victim types something on the device. The malware steals the program title, time, and input contents at regular intervals. A Timer calls a method to check the log.tmp file every 20 seconds and sends the info to the attacker via STMP. Moreover, the malware uses another Timer with a 20-minute interval to check for device activities and determine when to capture screenshots.

How does Agent Tesla maintain persistence?

Agent Tesla malware ensures persistence even when the device is restarted, or the malware process is killed, using two methods. It either executes a command for creating a task in the TaskScheuler system in the payload module or adds an auto-run item in the system registry. These methods allow duplication of dasHost.exe to launch automatically when the system restarts.

Protection against such campaigns

Be suspicious of any email that asks for your personal or financial information: Phishing emails often try to trick you into giving up your passwords, credit card numbers, or other sensitive information. Never click on links or open attachments in emails from senders you don’t know or trust.

Keep your software up to date: Software updates often include security patches that can help protect you from malware. Make sure to install security updates as soon as they are available.

Use a strong antivirus and anti-malware program: Antivirus and anti-malware programs can help detect and remove malware from your computer. Keep your antivirus and anti-malware programs up to date and scan your computer regularly.

Be careful what you click on: Phishing emails often contain links that lead to malicious websites. If you click on a link in an email, make sure to check the URL carefully before visiting the website.

Use a spam filter: A spam filter can help reduce the number of phishing emails that you receive.

Educate yourself about phishing: The more you know about phishing, the better you will be able to spot it. Read up on phishing scams and how to protect yourself.

  1. Hackers leak logins of vulnerable Fortinet SSL VPNs
  2. Hackers Using Stolen Ivacy VPN Certificate To Sign Malware
  3. Smoke Loader Drops Location Tracker Whiffy Recon Malware
  4. Luna Grabber Malware Hits Roblox Devs Using npm Packages
  5. Chae$4 Malware Steals Login, Financial Data from Businesses
  6. Adobe ColdFusion Vulnerabilities Exploited to Deploy Malware

[ad_2]
Source link

Phones will soon have more RAM than your computer

0
[ad_1]

Remember the days when the most advanced smartphones came out with 3GB of RAM? Well, the numbers have only gone up from there to the point where phones are gaining on mid-range computers. According to a rumor from Digital Art Station, a phone company is testing a phone with 32GB of RAM.

Since this is a rumor, you’ll want to take this with a grain of salt. Digital Art Station has been a trusted leaker in the past. However, we’ll need to wait for official information from the companies to be sure.

Phones with 32GB of RAM could be in testing

At this point, at least for Android phones, flagship phones typically have either 12GB or 16GB of RAM like the ASUS ROG Phone 7. 8GB, which was flagship grade just a few years ago, is decidedly mid-range while 4GB is now reserved for budget devices.

While 16GB seems to be the ceiling (many decently powerful computers have this much RAM), the OnePlus Ace Pro 2 has a gob-stopping 24GB of RAM. That’s insane, but this is OnePlus, the company that brought the first phone with 8GB of RAM back before Android could even utilize that much RAM.

Now, it seems that sometime down the road, we might see phones with 32GB of RAM. That seems a bit excessive because that’s double what top-tier phones are using now. That should be enough to store any app that a person would use on a daily basis.

While that’s the case, we don’t know if Android will be able to fully utilize all of that RAM when/if that phone comes out.

Right now, we don’t know what company is testing 32GB of RAM on its phone. If that phone comes closer to launching, then we expect it to be the main selling point. In any case, we don’t expect this phone to actually hit the market any time soon. As stated before, we just now got our first phone with 24GB of RAM. We might not see a phone with more RAM for a few years.


[ad_2]
Source link

Sonos Move 2 goes official with better battery life, Stereo Audio

0
[ad_1]

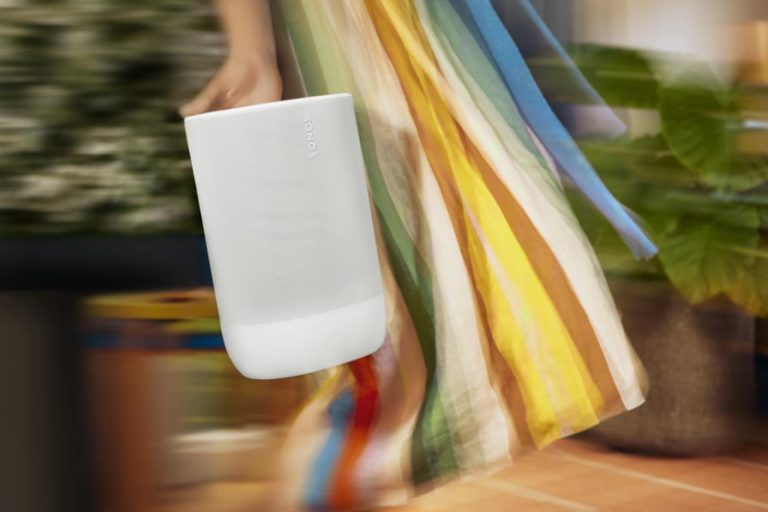
Sonos, today, announced the Move 2. Its second-generation portable speaker that everyone seems to love. The biggest new feature on this one is the improved battery life. Sonos claims that the Move 2 can last a full 24 hours on a charge. That’s more than double what the original Move was able to do.

On top of that, Sonos is also adding a USB-C port to the Move 2. That means that you can charge your speaker with the same cable as your phone, laptop and basically everything else. You can also directly connect things like your phone to the Sonos Move 2.

The other big feature for the Sonos Move 2 is the stereo output. So now you can get stereo audio out of the Sonos Move 2. That’s a big change, since the original version could only output audio in mono. The company also mentions that the Move 2 has a “completely overhauled acoustic architecture” and that includes dual tweeters and a precision-tuned woofer. So it should sound way better than the original.

There is support for AirPlay 2, Bluetooth, Amazon Alexa and Sonos Voice Control. You’ll notice that Google is missing, and that likely has to do with their lawsuit.

When can you buy the Sonos Move 2

Pre-orders for the Sonos Move 2 open up today. It’ll cost $449, and start shipping on September 20. And it’ll be available in three colors. There’s the usual black and white colorways, but Sonos has also added an Olive color this time around. Since the Sonos Move is something that Sonos things you’ll be taking around and out of the house, having some more fun colors are a good move.

That is a $50 price increase over the original Sonos Move. However, given the pretty big upgrades here, that $50 increase isn’t that bad. It is one of the more expensive portable speakers on the market, but given the incredible sound here, and battery life, it is definitely a better option than a lot of other options on the market.


[ad_2]
Source link

Russian APT28 Hackers Attacking Critical Power Infrastructure

0
[ad_1]

The АРТ28 hacking group, suspected to have ties to Russian special services, has made an audacious attempt to breach the critical power infrastructure of Ukraine. 

This latest cyberattack has raised alarms within the cybersecurity community and heightened concerns over the security of vital infrastructure.

Deceptive Tactics Exposed

The modus operandi of the АРТ28 group involved the use of bulk emails from a forged sender’s address. These emails contained a link to a seemingly innocuous ZIP archive.

However, upon opening this deceptive attachment, the attackers would have gained unauthorized access to the targeted organization’s systems and sensitive data.

Security experts have underscored the sophistication of this attack, emphasizing that the hackers leveraged legitimate services, including Mockbin, and exploited standard software functions to conceal their activities.

CERT-UA has provided an in-depth analysis of the attack chain, revealing the intricate details of the cyber assault.

They have also shared their findings on how the attack was ultimately thwarted. For those seeking comprehensive insights into this cyber threat, the detailed analysis is available on the CERT-UA website at [cert.gov.ua/article/5702579](https://cert.gov.ua/article/5702579).

The Computer Emergency Response Team of Ukraine (CERT-UA), operating under the State Service of Special Communications and Information Protection (SSSCIP), swiftly detected and analyzed a targeted cyberattack orchestrated by the notorious АРТ28 group.

The attackers intended to compromise a Ukrainian critical power infrastructure facility, potentially causing widespread disruption.

АРТ28’s Troubling History

The АРТ28 hacking group, which is known by various aliases such as Pawn Storm, Fancy Bear, and BlueDelta, has consistently targeted Ukraine in previous cyber operations:

  • In July 2023, CERT-UA uncovered an АРТ28 cyberattack aimed at stealing Ukrainians’ email account credentials.
  • In June, through collaboration with Recorded Future, CERT-UA exposed a spying campaign directed against Ukrainian organizations.
  • In April, cybercriminals associated with АРТ28 attempted to infiltrate Ukrainian governmental agencies through fake ‘OS updates.’

This pattern of relentless cyber aggression against Ukraine underscores the ongoing security challenges in the region and the need for constant vigilance against cyber threats.

Keep informed about the latest Cyber Security News by following us on Google News, Linkedin, Twitter, and Facebook.


[ad_2]
Source link