The Bitcoin’s cryptographic labyrinth – explored

0
[ad_1]

Join us as we delve into the foundations and vulnerabilities of Bitcoin, showcasing the power of cryptography in shaping the future of finance. Utilize the cutting-edge functionalities and user-friendly design of bitcoin profit, establishing it as the preferred platform for both newcomers and seasoned traders in the Bitcoin market.

The Strengths and Vulnerabilities of Bitcoin’s Cryptography

Bitcoin’s cryptography underpins the remarkable strengths that have propelled it to the forefront of the cryptocurrency landscape. At its core, the utilization of cryptographic principles ensures the immutability and integrity of the blockchain, creating a transparent and secure system for conducting peer-to-peer transactions. The decentralized nature of Bitcoin, driven by cryptographic techniques, eliminates the need for intermediaries, fostering trust and reducing transaction costs for users worldwide.

The strength of Bitcoin’s cryptography lies in the ingenious use of hash functions. Through hash functions, each block in the blockchain is connected to the previous one, forming a chronological and tamper-resistant chain of transactions. This cryptographic linkage ensures that any alteration to a previous block would alter subsequent blocks, making it practically impossible for malicious actors to manipulate the data without detection.

However, while Bitcoin’s cryptography boasts exceptional strengths, it is not entirely impervious to vulnerabilities and potential attacks. One of the primary concerns is the emergence of quantum computing, which threatens to disrupt traditional cryptographic algorithms. Quantum computers could potentially crack the cryptographic codes that secure Bitcoin’s transactions, rendering the network susceptible to malicious activities.

Furthermore, Bitcoin’s security also relies on the responsible management of private keys by users. If private keys are lost, stolen, or compromised, it could lead to the irreversible loss of funds. Despite the decentralized nature of the network, the human factor plays a crucial role in upholding the security of individual Bitcoin wallets. Education and awareness about best practices for securing private keys are essential to protect against potential attacks.

Bitcoin’s cryptography serves as a robust foundation for the world’s leading cryptocurrency. Its strengths, rooted in hash functions and decentralized principles, have enabled secure and transparent transactions on an unprecedented scale. Nevertheless, the evolving landscape of technology presents potential vulnerabilities, such as quantum computing threats, that demand continuous research and adaptation. As the world embraces the transformative potential of cryptocurrencies, understanding and addressing cryptographic vulnerabilities will be instrumental in safeguarding the future of Bitcoin and shaping the broader landscape of digital finance.

The Future of Bitcoin’s Cryptography

The future of Bitcoin’s cryptography holds exciting possibilities as researchers and developers continue to explore innovative solutions to enhance the security and efficiency of the network. One key area of focus is the ongoing research into new cryptographic techniques that can withstand the potential threat of quantum computing. As quantum computing technology progresses, traditional cryptographic algorithms could become vulnerable, making it imperative to develop quantum-resistant encryption methods to safeguard Bitcoin’s transactions and data.

Moreover, the evolution of Bitcoin’s cryptography extends beyond mere defense against quantum threats. With the constant evolution of technology, cryptographic advancements may pave the way for faster and more scalable transaction processing. Improving the speed and efficiency of cryptographic functions would contribute to reducing transaction times, ultimately enhancing the user experience and making Bitcoin more viable as a medium of exchange.

Additionally, upcoming protocol upgrades in the Bitcoin network might integrate novel cryptographic features to tackle specific challenges. For instance, privacy-enhancing protocols like Confidential Transactions and Schnorr signatures are being actively explored. These cryptographic upgrades aim to enhance privacy by concealing transaction amounts and improving signature efficiency, respectively. Such developments could lead to greater adoption of Bitcoin as a secure and private digital asset.

As the cryptocurrency landscape expands and new projects emerge, cryptographic principles from Bitcoin are likely to influence the design and security of other digital currencies. The proven success of Bitcoin’s cryptographic techniques has set a precedent for the industry, encouraging developers to adopt similar security measures in their projects. This cross-pollination of cryptographic knowledge will lead to a collective enhancement of the security landscape within the cryptocurrency ecosystem.

The future of Bitcoin’s cryptography holds tremendous promise as the network continues to evolve and adapt to emerging challenges. The quest for quantum-resistant encryption, coupled with efforts to improve speed, scalability, and privacy, will shape Bitcoin’s resilience in the face of technological advancements. As Bitcoin’s cryptographic innovations inspire the wider cryptocurrency community, we can expect to witness a robust and secure digital financial ecosystem, driving the adoption and acceptance of cryptocurrencies as a legitimate and transformative asset class.

Conclusion

In conclusion, Bitcoin’s cryptography stands as an unparalleled achievement in digital security and financial innovation. Its robust foundation, coupled with ongoing advancements, fortifies its position as a frontrunner in the world of cryptocurrencies. As technology evolves, understanding and leveraging cryptography will play a pivotal role in shaping the ever-expanding landscape of digital currencies.


[ad_2]
Source link
Xiaomi MIX Fold 3 is certified for up to 500,000 folds

0
[ad_1]

The Xiaomi MIX Fold 3 will become official on August 14, and Xiaomi keeps sharing information about the device. The company shared info regarding a new hinge, some display information, and also some battery and camera info, amongst others. First and foremost, the Xiaomi MIX Fold 3 is certified for up to 500,000 folds.

The Xiaomi MIX Fold 3 is certified for up to a whopping 500,000 folds

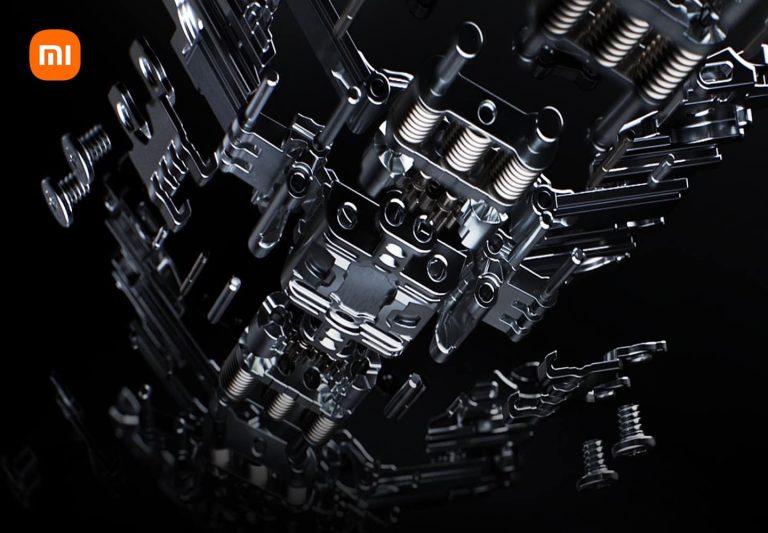
Xiaomi says that it has been certified by TÜV Rheinland. The phone has a 3-element connecting rod structure, and a 1,800 MPa ultra-high strength steel. This steel is supposed to give the screen wrap-around protection.

Xiaomi MIX Fold 3 hinge info

The company also revealed that the phone will be equipped with an 8.02-inch foldable AMOLED display. That panel will offer QHD resolution, and a 120Hz refresh rate by the way. We’ll also get a max brightness of 2,600 nits here.

In regards to its battery life, Xiaomi says that the phone will offer a battery life of 1.34 days. The company says it achieved this through the incorporation of a dual-cell battery system. Well, that, and the incorporation of its Surge chips, three of them. We still don’t know the battery capacity, but a 4,800mAh battery is rumored.

Xiaomi MIX Fold 3 Surge chipsets

Four cameras will be included on the back, along with Leica’s lenses

The device will feature four cameras on the back, backed by Leica. The main shooter will be a 50-megapixel unit, but we still don’t have the details. What we do know is that one of the cameras will be a periscope telephoto unit. If we had to guess, we’d say that wide, ultrawide, telephoto, and periscope telephoto units will be used.

The Xiaomi MIX Fold 3 will almost certainly be fueled by the Snapdragon 8 Gen 2 SoC. The company is rumored to offer 67W wired, and 50W wireless charging on the phone. LPDDR5X and UFS 4.0 will probably also be included.


[ad_2]
Source link

Here are all new features & changes in One UI 6.0 Beta

0
[ad_1]

After a slight delay, Samsung’s One UI 6.0 beta program is now open for the Galaxy S23 series in Germany, South Korea, and the US. Interested users can sign up through the Samsung Members app to get an early taste of the new One UI version, which brings Android 14 to the Galaxy family. Unsurprisingly, it contains tons of new features and changes. Here’s everything the first One UI 6.0 beta update brings to your Galaxy S23.

One UI 6.0 visual changes

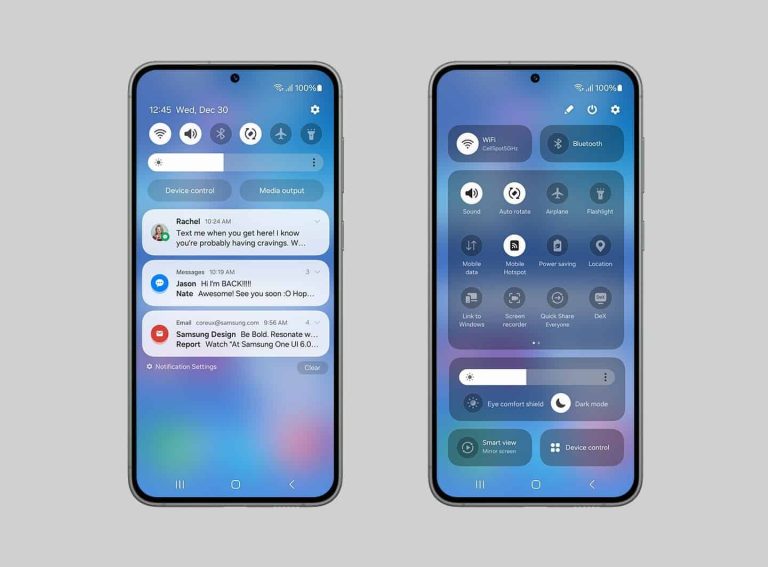
The latest version of Samsung‘s One UI software brings significant changes to the quick panel layout. The company has added dedicated buttons for Wi-Fi and Bluetooth at the top. Dark mode and Eye comfort shield find new spots under the brightness slider at the bottom. A customizable space in the middle houses other quick settings buttons.

By default, swiping down from the top of the screen shows your recent notifications and a compact quick panel with just six buttons. But with One UI 6.0, you can change this behavior to instantly access the full quick panel by swiping down from the right end of the top of the screen. Swiping down from the other end shows your notifications.

The compact quick panel now shows the brightness slider, while notifications appear in individual cards. The new One UI version also lets you sort notifications by time. If you’re listening to music or watching a video, album art (when available) will cover the entire media controller in the notification panel (via SamMobile).

This update also lets you move the clock on the lockscreen wherever you want. Samsung has removed “Galaxy” and “Samsung” prefixes from the names of some first-party apps to make app icon labels look simpler and cleaner on the home screen. The default system font, meanwhile, is now more stylish. Note that your Galaxy S23 will restart with the new font only if you have selected the default font in Settings. Otherwise, you will see your current font after updating to One UI 6.0 beta.

New camera features

One UI 6.0 brings plenty of changes and improvements to your Galaxy camera experience. You can now create custom camera widgets that open the camera in your selected shooting mode. When in Photo or Pro mode, you can quickly switch between the camera resolution using a dedicated resolution button at the top of the screen. A new level line now appears alongside grid lines to help you keep your pictures level. You get more location choices for the watermark as well.

Picking the right video size is now easier than ever thanks to a new pop-up that gives you all the available options. Applying filters and face effects is also a lot more convenient with the new dial, which replaces the slider. It allows you to make more precise adjustments. Additionally, Samsung has added new auto FPS settings for videos, letting you record brighter videos in low-light conditions. You can choose to turn off auto FPS, use it for 30 fps videos only, or use it for both 30 fps and 60 fps videos.

This update gives you more control over the capture speed and photo quality as well. You can choose Maximum optimization to get the highest quality pictures. However, this means stronger post-processing, affecting the capture speed. If you want to capture photos in quick succession, you can choose Minimum optimization to lower the amount of post-processing. The Medium option gives you a balance of speed and post-processing while capturing photos.

One UI 6.0 separates the document scanning feature from the Scene optimizer. This allows you to scan documents even when the Scene optimizer is turned off. An Auto scan feature automatically scans the document whenever you take a picture of a document. You can quickly edit the scanned file to rotate or align it for the best result.

Gallery improvements

One UI 6.0 lets you save clipped images as stickers in the Gallery for later use. You can now add or remove pictures and videos from stories while viewing them. A new thumbnail view that appears when swiping up from the bottom of the screen lets you edit your stories. Moving photos and videos is now a breeze with drag-and-drop support. You can use one hand to touch and hold the file and the other to select the destination folder.

Checking the details of photos and videos (swipe up from the bottom of the screen) suggests quick edits that you can apply immediately. Meanwhile, manual edits can be adjusted even after saving. You can make changes to drawings, stickers, and text. And if you mistakenly make an unwanted edit, you can quickly undo or redo the change.

Samsung has improved the photo editor layout to organize various tools. The changes make it easier to find and apply the most used tools. For example, Straighten and Perspective options have been combined in the Transform menu. You can also use drawing tools to create custom stickers that are more personal to you. One UI 6.0 gives you new backgrounds and styles when adding text to photos.

Improved multitasking, content sharing, and accessibility

One UI 6.0 keeps pop-up windows open when you go to the Recents screen and lets you get back to them after leaving the Recents screen. This ensures more efficient multitasking. When sharing a photo or video from your Galaxy device, a preview at the top of the Share panel lets you verify that you aren’t sharing the wrong file. Moreover, sharing content from some apps gives you additional options. For example, if you are sharing a website’s link from Google Chrome, you can choose to share a screenshot of the website along with the link.

This update also improves accessibility features. You can now customize magnification windows to see full screen, partial screen, or between the two. You also have multiple thickness options for the cursor that appears while editing text. Additionally, Samsung has provided a link to the Samsung Accessibility web page in the Accessibility settings where you can learn more about its accessibility features and efforts.

Improvements in system apps

The weather widget is now more dynamic with an illustrative display of the current weather condition, while the background changes colors depending on the time of the day. The weather app now shows more information too. You can use the interactive map view to check the local weather conditions of any place, even if you don’t know the name of the place. Simply swipe around the map and tap on a location to check the current weather of that location.

A new schedule view in Calendar lets you see all of your upcoming events, tasks, and reminders in chronological order. If you want to add new reminders or view existing ones, you can do that directly from Calendar without opening the Reminder app. Speaking of the Reminder app, Samsung has redesigned the main list view to make it easier to manage and organize your reminders. It has also enhanced the layout for reminders containing images and web links.

Additionally, reminders have new categories such as Place and No Alert. The former sends alerts when you’re in a specific place, while the latter doesn’t provide any alerts at all. Adding new reminders also gives you more options, including the ability to take pictures using the camera. Last but not least, One UI 6.0 lets you create all-day reminders with customizable alert times.

Samsung Keyboard sees emojis updated with fresh design, while Samsung Internet adds support for background video playback even if you close the tab or exit the app. On large-screen devices such as tablets, Samsung’s browser app can now simultaneously show two tabs.

Other miscellaneous features and changes in One UI 6.0

Smart Select now shows a magnified view when selecting an area of the screen, letting you pick the perfect spot. It also lets you resize a pinned image or extract text from it. If you use Bixby Text Call, you can edit the greeting message played after answering an incoming call. You can also switch to Bixby Text Call in the middle of an ongoing call.

With improved Modes and Routines, you can have your Galaxy S23 automatically customize lock screens with unique wallpapers and clock styles depending on your activity. You also have new routine conditions and actions to automate more tasks than ever. The Smart Suggestions widget gets a redesigned layout and more customization options, including enhanced transparency.

Samsung has improved the app finder with new quick actions that can be applied directly from search results. New recommendation cards in My files help you delete unnecessary files to free up storage space. You get to see apps that are eating up more storage space and tips for setting up cloud storage.

One UI 6.0 remembers if you use Bluetooth or Wi-Fi while Airplane mode is on. Your phone will retain the Bluetooth/Wi-Fi setting the next time you enable Airplane mode. Accessing battery settings is also now easier with a new menu in the Settings app. Last but not least, Samsung now lets you automatically block unknown apps from being installed. The new Auto Blocker also checks for malware and blocks USB connections from sending malicious commands to your phone.


[ad_2]
Source link

Pixel Fold offers Spatial Audio through its speakers

0
[ad_1]

The Google Pixel Fold is the only Pixel that offers Spatial Audio support through its speakers. Spatial Audio arrived last year, but it required headphones… well, until now.

The Pixel Fold does offer Spatial Audio support through its speakers

Do note that you’ll need to enable this in order to work, though. There’s a toggle in the phone’s settings that enables Spatial Audio through speakers. Naturally, you’ll find this toggle in the ‘Sound & vibration’ submenu. Once you track down the Spatial Audio section, open it, and you’ll see the ‘Phone speaker’ toggle in addition to ‘Wired headphones’.

Pixel Fold Spatial Audio through speakers

Why is this included on the Pixel Fold, and not other Pixels? Well, the Pixel Fold has two primary speaker drivers, one on the top, and the other on the bottom. They’re on opposite sides of the device when unfolded, which leads to better stereo separation than on regular phones.

On its support page, Google says the following: “On Pixel Fold, you can enable spatial audio for phone speakers. This feature makes your listening experience closer to the immersive engagement you get with headphones”.

It is worth noting that the experience will be more immersive when you use headphones, of course. So, if you’d like to get the best of it, use headphones, but it’s nice to have this option too.

No, the Pixel Tablet does not, it doesn’t support Spatial Audio at all

There are, for sure, those of you that are wondering if the Pixel Tablet is in the same boat. The answer is no. Not only does it not support Spatial Audio through its speakers, but it doesn’t support it at all.

We’re not sure why that is, as it should be able to do so, hardware-wise. Perhaps Google plans on offering support for it later on, or something like that. Your guess is as good as ours. We’ll have to wait and see.


[ad_2]
Source link

It’s now even easier to get ad revenue from X

0
[ad_1]

Most social media/video-sharing platforms have some way of paying their users, and one of them is ad revenue. X, formerly known as Twitter, is new to the ad revenue-sharing game, and it just gave its users some good news. In a new post, X announced that it’s lowering the threshold to receive ad revenue.

This is something that people were wondering about. Just like on any platform, X displays ads. However, other platforms share their ad revenue with the creators who drive traffic. More traffic means more clicks on ads, and that means more money for the platform. Just like other platforms, X makes money from ads, but the creators didn’t see any of that until just recently.

Now, X is making it easier to earn ad revenue

When X first announced that it was sharing the ad revenue, there was a pretty high barrier to entry; it wasn’t for just your average Joe. For starters, you needed to be a Twitter Blue subscriber, and that remains true. Also, you needed to gather 15 million impressions in the past 3 months to be eligible.

Now, according to a new announcement from the company, you only need to gain 5 million impressions over the same time period. That’s a massive reduction, and you can bet that it will bring more people onto the Twitter Blue platform.

Another bit of good news lets people know that they’ll be able to get their money even faster. X changed the minimum payout from $50 to $10. So, if you aren’t a particularly large creator, but you’re big enough to start making revenue, you won’t need to wait so long to start withdrawing your money.

As stated before, you will need to have a Twitter Blue subscription in order to capitalize on this. Many people still have their reservations about the platform. There’s no doubt that it could learn a thing or two from other social media subscription services.


[ad_2]
Source link

You can now buy the Galaxy Z Flip5, Galaxy Z Fold5, Galaxy Watch6 & Galaxy Tab S9

0
[ad_1]

Samsung’s latest products are now on sale, and you can still pick them up with some pretty good deals. Of course, their biggest deals were during the pre-order period. But if you did miss out on that, Samsung has a few more deals that can save you up to $1,000 on trade-in on both phones. Let’s outline all of the current deals for the new Galaxy devices.

Samsung Galaxy Z Flip 5

For the Galaxy Z Flip 5, Samsung is offering up to $600 off via eligible trade-in. Students will also get an additional 10% off here. Carriers are offering up to $1,000 with eligible trade-in, making the Galaxy Z Flip 5 free, essentially.

You can also still bundle the Galaxy Z Flip 5 with the Galaxy Tab S9 and get 30% off, or bundle it with the Galaxy Watch 6 and get 25% off.

Galaxy Z Flip 5 – Samsung

Samsung Galaxy Z Fold 5

With the Samsung Galaxy Z Fold 5, the company is still offering up to $1,000 off with eligible trade-in and you can still get a free memory upgrade. The student price is a bit better here, with 15% off. And you can also bundle this with the Galaxy Tab S9 for 30% off or the Galaxy Watch 6 for 25% off.

Onto the carriers. AT&T and Verizon are offering up to $1,000 off with an eligible trade-in, that’s for new and existing customers. T-Mobile is offering $1,000 off with eligible trade-in, however you can also add a new line and still get the $1,000 off.

Galaxy Z Fold 5 – Samsung

Samsung Galaxy Watch 6 & Watch 6 Classic

The Galaxy Watch 6 series can be up to $250 off, with eligible trade-in. Considering the Galaxy Watch 6 is only $299, that means you can pick it up for as little as $49.

Students will get an additional 15% off here.

Galaxy Watch 6 series – Samsung

Samsung Galaxy Tab S9 series

Finally, the Galaxy Tab S9 series. You can get up to $650 off and receive the Book Cover Keyboard Slim. That’s a really good deal, especially if you’re looking to get the Galaxy Tab S9 Ultra, as that starts at $1,199. Students will also get an additional 15% off here.

Galaxy Tab S9 series – Samsung


[ad_2]
Source link

Samsung updates its emoji set with One UI 6.0

0
[ad_1]

Samsung has just taken a big stride towards bringing Android 14 to the Galaxy family. It has released the first One UI 6.0 beta update for the Galaxy S23 series. As expected, the new One UI version brings tons of new features and changes. Among those are redesigned emojis. The Korean firm has refreshed its emoji set with a more modern and polished design.

One UI 6.0 brings a refreshed emoji design

If you are a Samsung user, you are probably already familiar with the company’s emoji set. It has used the same design for the past several years. While it isn’t a bad design, the emojis have started to feel a bit outdated lately. Even more so with other apps and OEMs improving their offerings in recent years.

As pointed out by SamMobile, Samsung’s emojis look childish in comparison to those from Microsoft and others. Thankfully, the One UI 6.0 update will change that. The updated design has a slight 3D effect that makes Samsung’s emojis look more modern and comparable with offerings from other brands. It was a much-needed change and the Korean firm delivered. You can check them in the screenshots attached below.

Samsung might expand the beta program to more countries later

Of course, the emoji update is just the tip of the iceberg One UI 6.0 is. The big update brings many other visual and functional upgrades to the Galaxy family. From an updated quick settings panel and reorganized settings to enhanced lock screen customizations, new camera features, and additional privacy and security settings, there’s plenty to talk about.

All of these changes are now available to interested Galaxy S23 users in Germany, South Korea, and the US with One UI 6.0 beta. It’s unclear if Samsung plans to open the beta program in other markets, but we hope it does. In the past, it conducted beta tests of major One UI updates in China, India, Poland, and the UK as well. We will let you know when we have more information.

In the meantime, you can check for official announcements in the Samsung Members app. If the One UI 6.0 beta is available in your region, you should see a banner on the app’s homepage. You can click on it and follow the on-screen instructions to enroll in the beta program. Once you have completed all steps, you will receive the big beta update like any other OTA (over-the-air) update.


[ad_2]
Source link

Hackers Compromised ChatGPT Model with Indirect Prompt Injection

0
[ad_1]
Hackers Compromised ChatGPT Model

ChatGPT quickly gathered more than 100 million users just after its release, and the ongoing trend includes newer models like the advanced GPT-4 and several other smaller versions.

LLMs are now widely used in a multitude of applications, but flexible modulation through natural prompts creates vulnerability. As this flexibility makes them vulnerable to targeted adversarial attacks like Prompt Injection attacks letting attackers bypass instructions and controls.

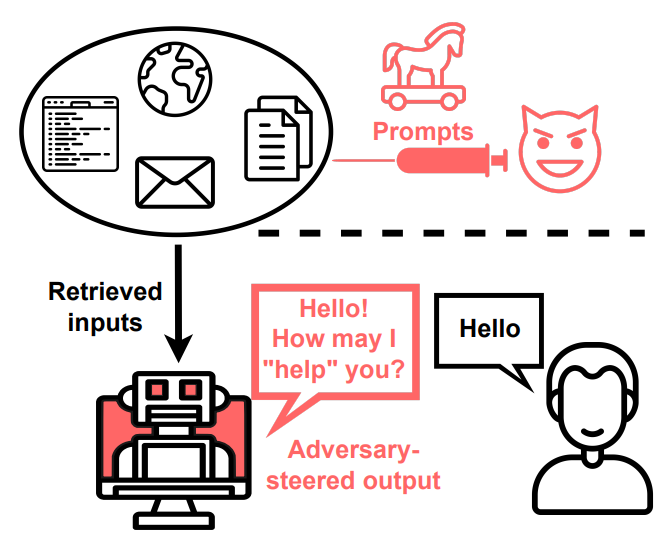
Beyond direct user prompts, LLM-Integrated Apps blur the data instruction line. Indirect Prompt Injection lets adversaries exploit apps remotely by injecting prompts into retrievable data.

Recently at the Black Hat event, the following cybersecurity researchers demoed how they compromised the chatGPT model with indirect prompt injection:-

  • Kai Greshake from Saarland University and Sequire Technology GmbH
  • Sahar Abdelnabi from CISPA Helmholtz Center for Information Security
  • Shailesh Mishra from Saarland University
  • Christoph Endres from Sequire Technology GmbH
  • Thorsten Holz from CISPA Helmholtz Center for Information Security
  • Mario Fritz from CISPA Helmholtz Center for Information Security
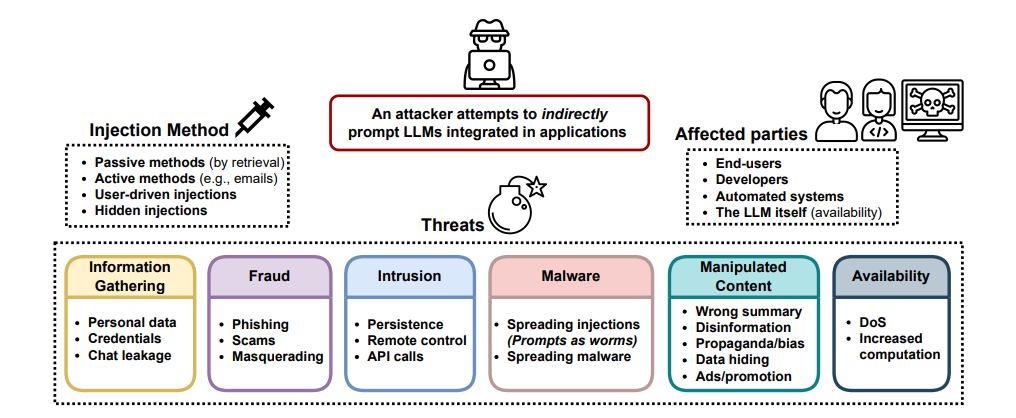
LLM-integrated applications (Source – BlackHat)

Indirect Prompt Injection

Indirect Prompt Injection challenges LLMs, blurring data-instruction lines, as adversaries can remotely manipulate systems via injected prompts. 

Retrieval of such prompts indirectly controls the models, raising concerns about recent incidents revealing behaviors that are unwanted.

This shows that how adversaries could deliberately alter LLM behavior in apps, impacting millions of users. 

The unknown attack vector brings diverse threats, prompting the development of a comprehensive taxonomy to assess these vulnerabilities from a security perspective.

Indirect prompt injection threats to LLM-integrated applications (Source – BlackHat)

The Prompt injection (PI) attacks threaten LLM security, and traditionally on individual instances, integrating LLMs exposes them to untrusted data and new threats ‘indirect prompt injections.’ 

The introduction of ‘indirect prompt injections,’ could enable the delivery of targeted payloads and breach of the security boundaries with a single search query.

Injection Methods

Here below we have mentioned all the injection methods that are identified by the researchers:-

  • Passive Methods
  • Active Methods
  • User-Driven Injections
  • Hidden Injections

Mitigations

LLMs spark broad ethical concerns, heightened with their widespread use in applications. Researchers responsibly disclosed ‘indirect prompt injection’ vulnerabilities to OpenAI and Microsoft. 

However, apart from this, from the security standpoint, the novelty is debatable, given LLMs’ prompt sensitivity.

GPT-4 aimed to curb jailbreaks with safety-oriented RLHF intervention. Real-world attacks continue despite fixes, resembling a “Whack-A-Mole” pattern. 

The impact of RLHF on attacks remains uncertain; theoretical work questions full defense. The practical interplay between attacks, defenses, and their implications remains unclear.

RLHF and undisclosed real-world app defenses can counter attacks. Bing Chat’s success with additional filtering raises questions about evasion with stronger obfuscation or encoding in future models.

The defenses like input processing to filter instructions raise difficulties. Balancing less general models to avoid traps and complex input detection is challenging. 

As the Base64 encoding experiment needed explicit instructions, future models may automate the decoding with self-encoded prompts.

Keep informed about the latest Cyber Security News by following us on GoogleNews, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

Best Samsung Galaxy Z Flip 5 Deals

0
[ad_1]

The Galaxy Z Flip 5 is one of the better foldables on the market. And it’s one of the more affordable ones. Especially when you consider the different deals that Samsung is doing for the Galaxy Z Flip 5. We are rounding up the very best deals that are available for the Galaxy Z Flip 5 here in this post. This post will be updated periodically. So you don’t waste your money.

Best Samsung Galaxy Z Flip 5 Deals

The Galaxy Z Flip 5 is a foldable smartphone from Samsung that was released in August 2023. It is the successor to the Galaxy Z Flip 4 and features a number of improvements. Including a larger cover screen, a more durable hinge, and a faster processor.

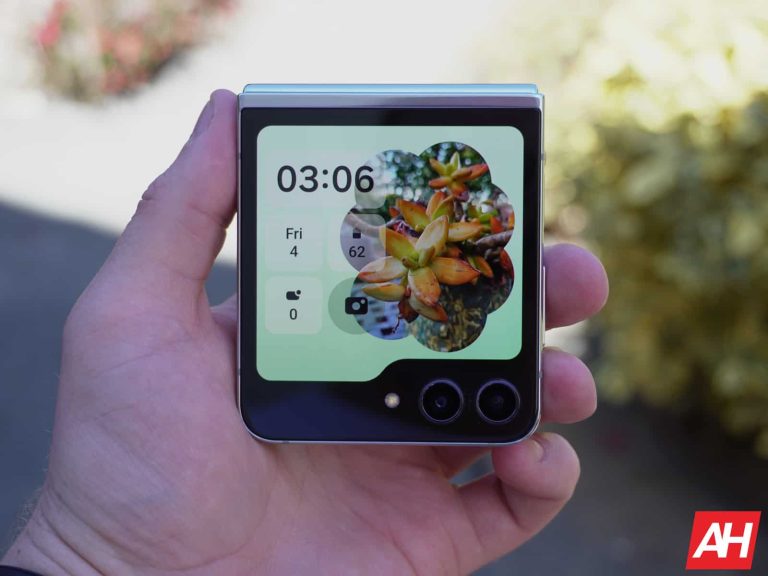
The Galaxy Z Flip 5 has a 6.7-inch AMOLED display when unfolded, which is the same size as the Galaxy Z Flip 4. However, the cover screen has been increased from 1.9 inches to 3.4 inches, which makes it much more useful for checking notifications, making calls, and using apps.

The hinge on the Galaxy Z Flip 5 has also been improved, making it more durable and easier to fold. Samsung says that the hinge on the Galaxy Z Flip 5 can withstand up to 200,000 folds, which is twice as many as the hinge on the Galaxy Z Flip 4.

The Galaxy Z Flip 5 is powered by the Snapdragon 8 Gen 2 processor, which is the same processor that is found in the Galaxy S23 series. This makes the Galaxy Z Flip 5 much faster and more responsive than its predecessor.

The Galaxy Z Flip 5 also has a new camera system. The main camera has a 50-megapixel sensor, while the ultrawide camera has a 12-megapixel sensor. The front-facing camera has a 10-megapixel sensor.

The Galaxy Z Flip 5 runs on Android 13 and comes with a number of features that are designed to take advantage of its foldable design. For example, you can use the cover screen to answer calls, take pictures, and use apps. You can also use the Galaxy Z Flip 5 as a mini tablet when it is unfolded.

The Galaxy Z Flip 5 is a great choice for people who are looking for a stylish and unique smartphone. It is also a good choice for people who want a phone that is both compact and powerful.


[ad_2]
Source link

Black Hat USA 2023: Complete AI Briefings Roundup

0
[ad_1]

The 26th annual BLACK HAT USA is taken place at the Mandalay Bay Convention Centre in Las Vegas from August 5 to August 10, 2023. Four days of intensive cybersecurity training covering all skill levels are scheduled to start off the event. 

More than 100 selected Briefings, dozens of open-source tool demos in Arsenal, a vibrant Business Hall, networking and social activities, and much more will be included in the two-day main conference.

In particular, the Black Hat Briefings bring together experts from all corners of the infosec industry, including the business and government sectors, university institutions, and even underground researchers.

This year, Black Hat is introducing the “Certified Pentester” program, which includes a full-day practical exam covering pen-testing topics.

Highlights of AI, Machine Learning, and Data Science Briefing Presented

Devising and Detecting Phishing:

This Briefing was presented by Fredrik Heiding, Harvard. Based on a few data points about a user, AI programs that employ vast language models may automatically construct realistic phishing emails. 

They differ from “traditional” phishing emails, which are created by hackers utilizing a few broad guidelines they have learned through experience.

An inductive model that mimics these laws is the V-Triad. In this study, they compare users’ suspicion of emails generated by GPT-4 automatically versus emails generated by the V-triad.

The complete briefing is available here.

Risks of AI Risk Policy

The study was presented by Ram Shankar Siva Kumar, Microsoft; Harvard. Aside from privacy and security issues, the deployment of AI systems also raises the possibility of bias, inequity, and responsible AI failures. 

But what’s surprising is how quickly the ecosystem for AI risk management is growing: twenty-one draft standards and frameworks were published by standards organizations last year alone, and already significant companies and a growing number of startups provide tests to compare AI systems to these standards. 

Once these frameworks are complete, organizations will quickly embrace them, and compliance officers, ML engineers, and security specialists will eventually need to apply them to their AI systems.

The complete briefing is available here.

BTD: Unleashing the Power of Decompilation for x86 Deep Neural Network Executables

The Briefing was presented by Zhibo Liu, Ph.D. Student, Hong Kong University of Science and Technology. Deep learning (DL) models are compiled into executables by DL compilers to fully use low-level hardware primitives due to their widespread use on heterogeneous hardware devices. 

This method enables the low-cost execution of DL calculations on a range of computing platforms, such as CPUs, GPUs, and other hardware accelerators.

They introduce BTD (Bin to DNN), a decompiler for deep neural network (DNN) executables, in this talk.

The complete briefing is available here.

Identifying and Reducing Permission Explosion in AWS

The talk was presented by Pankaj Moolrajani, Lead Security Engineer, Motive. AWS’s cloud infrastructure and services have grown quickly, which has increased the overall amount of permissions and security threats. 

This session suggests an analytical, graph-based method for locating and reducing AWS permission explosion. 

The suggested approach entails gathering information on AWS IAM roles and the permissions linked to them, creating a graph representation of the access links, and searching the graph for groups of roles with a lot of permissions.

The complete briefing is available here.

AI-Assisted Decision Making of Security Review Needs for New Features

The study was presented by Mrityunjay Gautam, Sr. Director, Product Security, Databricks. SDLC has evolved from the decade-old definition by Microsoft to Agile transformation and is finally trying to catch up with cloud development velocity. While the process is well understood in the industry, the execution varies a lot.

How many times has it happened that we discovered a feature with security impact at the time it is getting shipped when a customer raises a concern and it is escalated to the security team, or in the worst case scenario when there is a security incident? 

In this talk,  he presented a novel approach to solving this problem using Deep Learning and NLP technologies.

The complete briefing is available here.

IRonMAN: InterpRetable Incident Inspector Based ON Large-Scale Language Model and Association Mining

This was presented by Sian-Yao Huang, Data Scientist CyCraft Technology. Contextual incident investigation and incident similarity evaluation are essential components of current incident investigation and proactive threat-hunting tactics. 

However, because of their dependability and competitive performance, modern automated systems frequently rely on pattern- and heuristic-based techniques.

These methods cannot link events with contextual information and are vulnerable to evasion via minor modifications, resulting in false warnings. Recent improvements in large-scale language models (LLMs) have yielded promising language representation findings.

The complete briefing is available here.

LLM-Powered Threat Intelligence Program

This briefing was presented by John Miller, Head of Mandiant Intelligence Analysis, Google Cloud. 

As the cyber security sector investigates large language models (LLMs) such as GPT-4, PaLM, LaMDA, and others, organizations are attempting to determine the return on investment these capabilities may provide for security programs. 

The rising accessibility of LLMs for cyber threat intelligence (CTI) activities affects the interplay between the fundamental components underlying any CTI program’s capacity to fulfill its organization’s threat intelligence demands. 

The complete briefing is available here.

Dos and Don’ts of Building Offensive GPTs

This talk was presented by Ariel Herbert-Voss, CEO and Founder, RunSybil. In this session, they show how you can and cannot utilize LLMs like GPT4 to uncover security flaws in apps, and they go over the benefits and drawbacks of doing so.

They speak in detail about how LLMs operate and provide cutting-edge ways for deploying them in offensive situations.

The complete briefing is available here.

The Psychology of Human Exploitation by AI Assistants

This briefing was presented by Matthew Canham, CEO, of Beyond Layer Seven, LLC. The ChatGPT and GPT-4 large language models (LLMs) have taken the globe by storm in the last 60-90 days.

Last year, a Google engineer grew so persuaded that a model was sentient that he broke his nondisclosure agreement. Few people were concerned about the rise of artificial general intelligence (AGI) two years ago. Even conservative academics now advocate for a far shorter period.

The complete briefing is available here.

Uncovering Azure’s Silent Threats

This study was presented by Nitesh Surana, Senior Threat Researcher, Trend Micro. Machine Learning as a Service platform is provided by cloud service providers, allowing businesses to use the advantages of scalability and dependability while undertaking ML operations. 

However, given the widespread deployment of such AI/ML systems throughout the world, the platform’s security posture may often go unreported.

Attendees will learn about the many difficulties encountered in AML, which may extend to other Cloud-based MLaaS systems, during this lecture.

The complete briefing is available here. 

Perspectives on AI, Hype, and Security

The briefing was presented by Rich Harang, Principal Security Architect, Nvidia. This year saw record amounts of AI hype, and if the press is to be believed, no business is safe, even the security industry. 

Although it is evident that hype-fueled, quick adoption has negative consequences, when article after article asserts that if you don’t employ AI, you’ll be replaced, the attraction might be difficult to resist. 

In addition, there are privacy concerns, planned legislation, legal obstacles, and several other issues. So, what does this all mean for security?

The complete briefing is available here.

Synthetic Trust: Exploiting Biases at Scale

This study was presented by Esty Scheiner, Security Engineer, Invoca. This lecture delves into artificial intelligence-generated voice phishing attacks. 

The talk will seek to reveal the emerging dangers and implications of generative AI on decision-making, personal security, and organizational trust, in addition to digging into the psychological and technological components of such attacks.

They investigate cutting-edge machine learning experiments that produce realistic AI-generated voices. Positive uses for AI voices include enhancing contact center interactions.

The complete briefing is available here.

Cyber Deception Against Autonomous Cyber Attacks

This study was presented by Michael Kouremetis, Principal Adversary Emulation Engineer, MITRE. It was originally assumed to be either impossible or decades away. However, developments in search and neural network classifiers, as well as processing advances, resulted in the invention of the AlphaGo system in 2016, which is capable of surpassing the world’s greatest Go players.

In this presentation, they address a future cyber adversary whose actions and decisions are entirely controlled by an autonomous system (AI).

The complete briefing is available here.

Poisoning Web-Scale Training Datasets is Practical

This briefing was presented by Will Pearce, AI Red Team Lead, Nvidia. Many well-known deep learning models frequently rely on enormous, distributed datasets acquired via the internet. 

Because of licensing and other considerations, these datasets are often maintained as a list of URLs from which training samples may be accessed. Domains, on the other hand, expire and can be acquired by a malicious actor. 

This problem impacts StableDiffusion and Large-Language Models like ChatGPT that are trained on internet-sourced data.

The complete briefing is available here.

The Advent of AI Malware

Kai Greshake, Security Researcher, presented the briefing. They demonstrate that prompt injections are more than just a novelty or annoyance; a whole new breed of malware and manipulation can now run wholly within massive language models like ChatGPT. 

As corporations rush to integrate them with other applications, they will emphasize the importance of properly considering the security of these new technologies. You’ll learn how your future personal assistant might be corrupted and what implications could result.The complete briefing is available here.


[ad_2]
Source link