Google’s “browse privately” is nothing more than a word play, lawyers say

0
[ad_1]

Google will have to appear in court after a judge denied their request for summary judgment in a lawsuit filed by users alleging the company illegally invaded the privacy of millions of people.

Lawsuits against big tech over privacy issues are not much of a surprise these days, unfortunate as that may be. What makes this case stand out is that Google allegedly misled Chrome users by implying that they could browse privately by using the Incognito mode.

The judge in the suit said that Google appears to confuse users by portraying Incognito mode as a distinct offering without clearly articulated privacy terms for the service.

But despite the implied promise of privacy, Google’s cookies, analytics, and tools in apps allegedly continued to track internet browsing activity even after users activated Incognito mode.

Incognito is an option which is often used in troubleshooting browser issues, since it disables extensions and caching. Two factors that are often at play when websites do not get displayed properly.

This mode is also useful in that it essentially starts up a fresh identity for you to browse the web with, then wipes it all as soon as you close the window. This is nice if you are using a computer that isn’t your own and you want to limit your footprint.

The option to start an incognito window can be found under the hamburger icon (3 vertical dots).

open new options in Chrome

At the time of writing Chrome displays this information when you start an Incognito window.

Incognito Splash Screen

Incognito Splash Sereen

Note: the “Block third-party cookies” section was not present years ago.

Google’s motion hinges on the idea that plaintiffs consented to Google collecting their data while they were browsing in private mode. The court ruled otherwise, because Google never explicitly told users that it does so.

Whenever a user visits a website that is running Google Analytics, Ad Manager, or some similar Google service, Google’ software directs the user’s browser to send a separate communication to Google. This happens even when users are touring the web in private browsing mode, unbeknownst to website developers or the users themselves.

The lawsuit was filed in 2020, and the plaintiffs are seeking a $5,000 in damages per user, which could end up amassing $5 billion.

Let the record show that all major web browsers include a private browsing mode that does not store browsing history, cookies, or temporary files across browsing sessions. Unfortunately, users have misconceptions about what this mode does—misconceptions that are encouraged by the wording these very same browsers use when describing their own features.

A 2018 study based on user surveys among 460 participants showed that participants use private mode to hide browsing activity, prevent the saving of log-in information, and avoid cookies. A very common and big misconception, that 56.3% of participants believed, was that even though a user was logged into a Google account, their search queries would not be saved while in private mode.

One of the conclusions of the study was that of the thirteen browser disclosures about private mode that were tested, only the current and old versions of Chrome’s desktop disclosure led to significantly more correct answers. Meaning that other browsers were doing an even worse job. The term “private” is heavily overloaded and the name “private mode” implies unintended meanings. The disclosures fail at the task of correcting misconceptions users derive from the name “private mode.”

It’s important to realize that a browser can be fingerprinted even in private mode and that many online tracking systems use techniques that are much more advanced than the use of cookies.


Malwarebytes EDR and MDR removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

OnePlus will make it easier to use your phone in the rain

0
[ad_1]

Many smartphones today come out with IP water resistance, so you won’t have to worry about the phone getting caught in the rain. However, if you’re trying to use your phone in a downpour, it’s still pretty tedious. Well, OnePlus has a new technology called Rain Water Touch, and it will let you use your phone in the rain.

The issue here isn’t with water ingress; the issue is that when you’re using your phone while the screen is wet, the phone can get confused and think that you’re touching it. Because of that, you’ll see random inputs on the screen where you’re not touching it. This can even prevent the phone from picking up your input altogether.

With Rain Water Touch, OnePlus plans to fix this

OnePlus posted a video on Chinese microblogging site Weibo, (via Android Police) and it showcases the upcoming OnePlus Ace 2 Pro standing next to an iPhone. Then, we see water jets being blasted at both phones. This is to simulate a harsh downpour of rain.

While both of the phones are being doused, the testers were able to use the OnePlus phone with no issue at all. The iPhone, on the other hand, suffered the same issues that capacitive touch screens have been going through.

OnePlus achieved this through the use of a proprietary chip. Alongside the main SoC, this chip, along with some algorithms, makes sure that the phone doesn’t register random touch inputs when the screen is wet.

This isn’t only an advertisement for the chip, we also get a glimpse of the upcoming OnePlus Ace 2 Pro. This phone, among other things, is the handset that’s going to bring a whopping 24GB of RAM. That’s the kind of spec you’d expect to see in a computer; and a pretty good one at that.

OnePlus is set to announce this new phone in the next couple of days, so you’ll want to stay tuned for more information on it.


[ad_2]
Source link

YouTube makes sweeping changes to tackle spam on Shorts videos

0
[ad_1]

YouTube is making drastic changes to combat a a growing tide of spam comments on the Shorts video category.

YouTube is rolling out unclickable links. 

Video portals like YouTube have had to deal with spam comments and bogus links for many years. With new additions to a platform come new places for scammers to go about their business. YouTube is now cracking down on links posted to the comments section of Shorts.

Shorts has been around for a few years now, but you may not have noticed the video format up until this point. They’re most commonly found on the frontpage of YouTube, in the form of horizontally framed Tik-Tok style clips. Clicking into a Shorts video will give you an endless, scrolling feed of seemingly random content. Some videos have hashtags you can click into, but for the most part it can feel like a chaotic, non-curated experience.

As with regular YouTube videos, users of the site can leave comments and replies to videos on Shorts, but that’s introduced a new problem. So, YouTube introduced sweeping changes that will affect people who are trying to build out a Shorts platform. From the release detailing the changes:

Since introducing Shorts two years ago, the volume and speed of content published on YouTube has increased in fun and exciting ways. At the same time, this speed and level of engagement has made it easier for spammers and scammers to share links in Shorts comments and Shorts descriptions that harm the community – for example, clickable links that drive users to malware, phishing, or scam-related content.

Essentially: if you build it (and by “it”, I mean “a rapid-fire barrage of non-stop content”) they will come (and by “they”, I mean “a cavalcade of spam the likes of which the moderation team simply cannot police”).

The list of link-related casualties is as follows:

Starting on August 31st, 2023, links in Shorts comments, Shorts descriptions, and links in the vertical live feed will no longer be clickable – this change will roll out gradually. We don’t have any plans to make any other links unclickable. Because abuse tactics evolve quickly, we have to take preventative measures to make it harder for scammers and spammers to mislead or scam users via links.

YouTube also goes on to say that “clickable social media icons from all desktop channel banners will no longer show, as they can be a source of misleading links.” As The Verge notes, these links are used to direct content viewers to their accounts on other websites. Considering the Shorts platform is fairly limited in functionality to others of a similar nature, removing anything along these lines could cause issues for Shorts makers.

There are plans to replace these links with something, though there’s no word yet as to what form this may take. 

In 2022, one of YouTube’s transparency reports showed that a big problem was in the realm of misinformation—122,000 videos (not channels) were removed for violating misinformation policies from an overall total of four million removals in Q2 2022. And 89 of these were removed due to being classed as “Spam, misleading, and scams.” The biggest reason for videos being removed was child safety, clocking 1,383,028 removals (31 percent of the overall tally).

With this in mind, it makes sense that YouTube would be keen to bring the banhammer down on a sudden rise in scams affecting the Shorts platform. The quick-cut video content is geared toward younger users; indeed, it’s popular with the 16 – 24 age group. The last thing YouTube or Google needs is a potential child safety issue spreading wildly out of control with rogue links and dubious comments lurking in potentially blink-and-you’ll-miss-it comments sections.

Ultimately, this could be a burden for Shorts creators, but it is a proactive move and anything which impacts the terrifying volume of spam on one of the biggest video platforms in the world can only be a good thing.


We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.


[ad_2]
Source link

Instagram will let you add music to your photo slideshows

0
[ad_1]

We’re all used to adding images to Instagram, but sometimes, we want our images to have a little bit more flair. Music is a good way to do this, and the company is launching a new feature that users will like. Instagram will let you add music to your photo slideshows, according to Engadget.

Let’s not mince words here; This idea is not new. TikTok, the thorn ever stuck in Mark Zuckerberg’s side, came up with this idea last year. However, top social media/video-sharing platforms take from each other to remain competitive.

Instagram will let you add music to your photo slideshows

As stated before, photos could stand to have a little more flair. If you post a picture of you at a ta concert, it’d help to hear music from the act that was performing. If you post pictures from your latest skiing trip, why now have “Let It Go” playing in the background?

This feature was launched in collaboration with Olivia Rodrigo and her new pop single “Bad Idea, Right?”. When you add your photo slideshow, you’ll be able to pick from a list of licensed music that you want to accompany the photos. The company launched this feature on the back of the music for feed photos, so that’s another way that you can add music to your posts.

Along with this feature, Instagram now allows up to four people to make collabs. That’s up from only two people. So, if you and three of your friends really want to collaborate on Reel, you can.

Next up, Instagram added a change to the Add Yours sticker. People are able to add their own prompts and content to a Reel. Well, after this new update, the creators will be able to actually highlight the post that stuck out to them the most. It’s a great way for creators to interact with their followers.

Lastly, Instagram is partnering with Spotify to bring its music library to more people. It will expand to more countries and showcase today’s most popular music.


[ad_2]
Source link

Old exploit kits still kicking around in 2023

0
[ad_1]

Internet Explorer may be a thing of the past, but there are still users and threat actors trying to deliver drive-by downloads.

The year is 2023 and there still are some people using Internet Explorer on planet Earth. More shocking perhaps, is the fact there are still threat actors maintaining exploit kit infrastructure and dropping new malware.

In this quick blog post, we review two well-known toolkits from the past, namely RIG EK and PurpleFox EK with the latest traffic captures we were able to collect.

RIG EK

The RIG exploit kit continues to be used by a single threat actor that leverages adult traffic schemes. In this latest instance, it dropped the Lumma Stealer.

RIG EK

PurpleFox EK

PurpleFox is more than just an exploit kit, it is a complete framework with rootkit capabilities. The exploit kit is one of the delivery mechanisms for the PurpleFox malware.

PurpleFox EK

Thank you to researchers at First Watch Security for providing information on this attack chain.

Protection

Even after all these years, Malwarebytes continues to protect agains these exploit kits targeting vulnerabilities in Internet Explorer, the browser no longer supported by Microsoft.

MBAE

Indicators of Compromise

RIG EK

adsgoandway[.]xyz
45.138.27[.]52

Lumma Stealer payloadd

07e06e8277980a60e595da9cd9e03a4ecd2e8f8bdbd3cf5c930ab878ac5b0836

Lumma Stealer C2

solopodvip-my[.]xyz

PurpleFox EK

oernatel[.]shop
uabeoee.otvidluioad[.]online
via0[.]com

Payload

f627070c4cbb03556896601870cf575b1c8f47b062fdfef5c3516ff5a07db40c

[ad_2]
Source link

Pixel 8 Pro Audio Magic Eraser shown in promo video leak

0
[ad_1]

The Pixel 8 Pro has shown up in a promo video leak. The leaked video clip isn’t long but it’s long enough to showcase two things. One of the color options of the phone and an upcoming feature that Google seems to be releasing alongside it called Audio Magic Eraser.

Worth keeping in mind is that the video comes from a brand-new X account, likely created for the sole purpose of sharing this clip and nothing else. Make of that what you will. The promo video leak of the Pixel 8 Pro also clearly has some sort of edited filter over it. Perhaps to obscure things for whatever reason. With all of that out of the way, the video does have some interesting things to take out of it.

First, the Pixel 8 Pro can be seen in a new light blue color as noted by 9To5Google. It’s fairly close to the blue color of the Pixel 7a. So Google looks to be continuing its color scheme here. That’s not too surprising as Google is already doing this with other hardware products that it offers.

The Pixel 8 Pro promo video leak shows Audio Magic Eraser in action

If you were curious about how this feature might work, it’s probably how you’re imagining it. With the regular magic eraser feature for photos, you can use it to remove people or things from a shot. Audio Magic Eraser looks to do the same exact thing but for sound. In the promo video, it shows the user of the Pixel 8 Pro viewing a recording of someone skateboarding across a concrete bridge. They then hit the Audio Magic Eraser button, which scans audio in the recorded clip to identify it. After which, the user drags a bar all the way to the left to remove the sound of the skateboard wheels traveling across the concrete.

Obviously, it’s not clear if the feature will work as well as it’s portrayed in the video. But it’s an impressive feature nonetheless if the video is even remotely accurate. And it should make editing clips a little simpler for times when surrounding noises might be drowning out what you want.


[ad_2]
Source link

Google tests a new look for search results in the Google app

0
[ad_1]
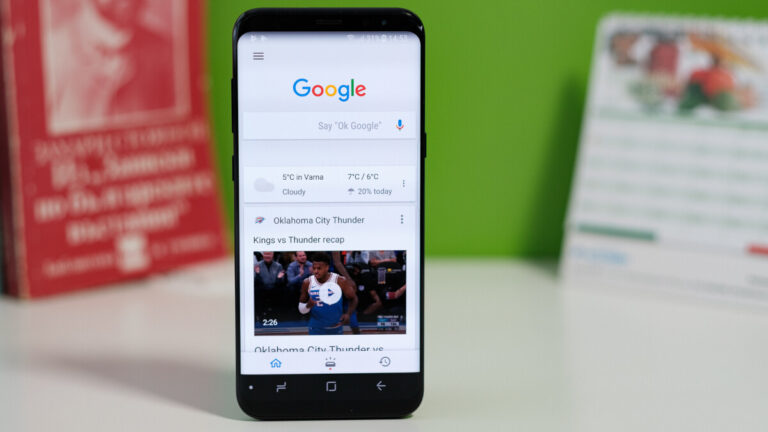
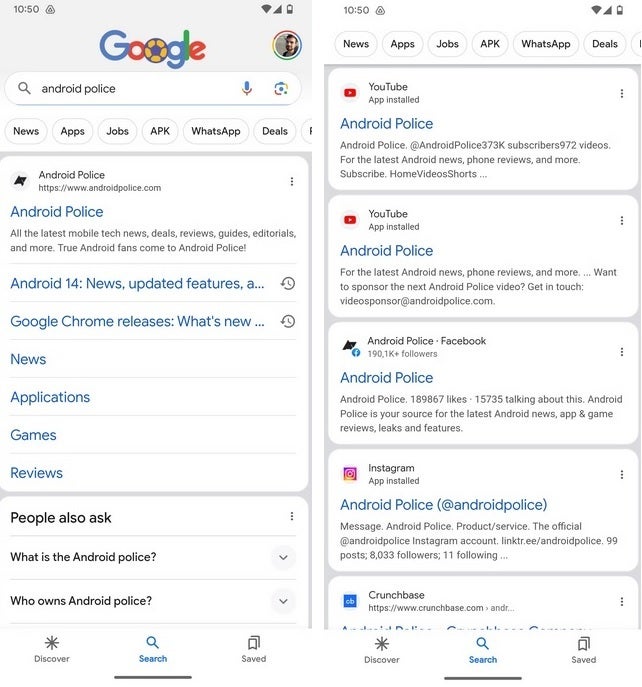
Google has been testing a new card-style UI for search results on its iconic Google app. The new UI generates a card for each search result that includes rounded corners to help you clearly see where one card ends and the next one begins. The goal is to make the app look less dated although this new look is the subject of one of Google’s typical A/B tests and it isn’t clear whether this look will be canceled or disseminated to one and all in due time.
Android Police discovered that the new card-style search results UI for the Google app was spotted by some users in version 14.31.19.29 of the Android version of the app. But since this is an A/B test, some of those with that version of the Google app on their Android phone may not have the updated look yet. For example, my Pixel 6 Pro is running Android 14 Beta 5 and the version of the Google app that we mentioned earlier in this paragraph. But the new UI has yet to appear on the phone.
Just because Google is testing the card-style UI for search results doesn’t mean that it will elect to keep it after completing its testing. For example, in January of this year, the bottom bar of the Google app received a brief Material You makeover in a test that highlighted the tab that you selected from the choices on the bottom bar of the app: Discover, Search, or Collections. The tab you tapped on would be highlighted by a “blue pill”  and while it was a nice touch, Google did decide to end the testing without adding the feature permanently.
Google might decide to keep the card-style UI for search results because it gives the results a more organized look. Still, as you can see from the previous paragraph, Google has no problem shutting down a test if it feels like it should.

[ad_2]
Source link

Several hospitals still counting the cost of widespread ransomware attack

0
[ad_1]

A widespread ransomware attack affecting 16 hospitals last week has led to ongoing cleanup efforts.

The 16 hospitals struck down by ransomware last week are still dealing with the fallout from the attack. The healthcare facilities located in Connecticut, Pennsylvania, Rhode island, and California had the ransomware attack confirmed by the FBI. Issues started to emerge last Thursday with patients diverted to other locations and some operations put on hold.

The AP reported that staff were forced to resort to pen and paper and manually running records to different departments. When dealing with potentially critical health issues, every second counts, and this is especially the case where so much critical healthcare equipment is reliant on networks and interconnected digital systems.

A recent Facebook update from Waterbury Hospital, CT reads as follows:

Our computer systems continue to be down throughout the network. We are following downtime procedures including the use of paper records. The outage has affected some of our outpatient services, mostly diagnostic imaging and blood draw and some patient appointments. We have contacted and will continue to contact any affected patients. 

The post also states that a diagnostic radiology department is affected.

At the time of the attack, no ransomware group had claimed responsibility for the network breach. Now, according to The Record, several sources told Recorded Future News that the ransomware group behind this widespread attack is Rhysida. It’s standard practice that law enforcement will not comment on a ransomware group directly while an investigation is taking place.

What’s interesting given the alleged claims from sources is that the US Department of Health and Human Services recently published a warning to hospitals last week about this specific group. The document said about Rhysida:

Rhysida is a new ransomware-as-a-service (RaaS) group that has emerged since May 2023. The group drops an eponymous ransomware via phishing attacks and Cobalt Strike to breach targets’ networks and deploy their payloads. The group threatens to publicly distribute the exfiltrated data if the ransom is not paid. Rhysida is still in early stages of development, as indicated by the lack of advanced features and the program name Rhysida-0.1.

The ransomware also leaves PDF notes on the affected folders, instructing the victims to contact the group via their portal and pay in Bitcoin. Its victims are distributed throughout several countries across Western Europe, North and South America, and Australia. They primarily attack education, government, manufacturing, and technology and managed service provider sectors; however, there has been recent attacks against the Healthcare and Public Health (HPH) sector. 

The HHS notes that the ransomware is relatively new. When it first made an appearance on our Ransomware Review in July of this year, we said the following:

Rhysida, a new ransomware gang claiming to be a “cybersecurity team,” has been in operation since May 17, 2023, making headlines for their high-profile attack against the Chilean Army. 

The gang published a whopping eighteen victims on their leak site in June, making it one of the most prolific newcomers in our month reviews to-date.

In terms of how Rhysia spreads, the primary methods of infection include phishing attacks, and dropping payloads across compromised systems once Cobalt Strike or other command and control frameworks are in place. Once the ransomware has taken hold, the group uses tried and tested double threat extortion tactics. A ransom note threatens to distribute stolen data publicly unless the ransom is paid.

The threat isn’t “just” locked computers, or patients unable to be assisted. There’s the very real possibility of said patients having their medical or other personal data thrown online for all to see.

Some ransomware groups won’t touch medical attacks for fear of reprisals. On many occasions where a medical facility or healthcare provider has been attacked, those responsible will apologise and provide free decryption tools. Others will do much the same thing alongside blaming rogue affiliates.

Certain attacks simply draw too much heat and generate waves of negative publicity for the culprits. If your entire gimmick is that you can (just about) be trusted to unlock PCs and return data if you receive a ransom, taking down hospitals will not encourage others to trust you.

All this leads to in the long term is a probable drop in ill-gotten gains, and you can bet the ransomware authors would prefer that to not be the case.

Hopefully, all of the impacted healthcare operations will be back up and running soon. We’d suggest anyone potentially affected keep in touch with their local hospital and pay attention to the updates page for more information.

How to avoid ransomware

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; disable or harden remote access like RDP and VPNs; use endpoint security software that can detect exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like Malwarebytes EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.


Malwarebytes EDR and MDR removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

Samsung pushes August update to Galaxy S22 series in the US

0
[ad_1]

A couple of days back, Samsung released the August 2023 security update for the Galaxy S22 series in Latin America. The update has now crossed boundaries to reach the US. More precisely, the company is pushing the new SMR (Security Maintenance Release) to its 2022 flagships in Puerto Rico. It should soon be available in the mainland US as well. Users in other parts of the world can also expect to receive the latest security patch in the coming days.

Samsung‘s August SMR is currently rolling out to factory-unlocked variants of the Galaxy S22, Galaxy S22+, and Galaxy S22 Ultra in Puerto Rico. The new firmware build number for the phones is S90*U1UES3CWG2. The official changelog supplied by the Korean firm reveals that the devices aren’t getting anything more than this month’s security patches. Users in Latin America also only received the August SMR and nothing else.

As said earlier, Samsung will soon expand the rollout of the August SMR for the Galaxy S22 series to other parts of the US as well as the rest of the world. The update will also be available for users with carrier-locked units. The build number may vary, but the changelog should remain the same. The company has already revealed that the latest security patch contains fixes for more than 80 vulnerabilities, including at least three critical patches.

If you’re using a Galaxy S22, Galaxy S22+, or Galaxy S22 Ultra, you can expect to receive a notification promoting you to download the August update in the coming days. You can tap on the notification and follow the on-screen instructions to install the latest security enhancements on your phone. You can also navigate to Settings > Software update > Download and install to check for new OTA (over the air) updates manually.

Samsung has begun beta testing the Android 14 update for Galaxy devices

As Samsung pushes the August SMR to more Galaxy devices, the company is also simultaneously beta-testing the Android 14 update. The first beta build of the big Android update, which brings the company’s One UI 6.0 custom software, is now available for the Galaxy S23 series in Germany, South Korea, and the US.

Interested Galaxy S23 users in these countries can enroll in the One UI 6.0 beta program from the Samsung Members app. The company is expected to open the beta program for more devices and expand the availability to other countries later this month. The stable update should arrive in November, if not earlier.


[ad_2]
Source link

Hackers Leak PII Data and Photos of Brazilian Plastic Surgery Patients

0
[ad_1]
  • Thesnake02 hacker group exposes sensitive data from Brazilian Plastic Surgery Clinic.
  • Breach occurred in July 2023, leaking 1.25 GB of private patient data, including surgery-related images and financial documents.
  • Trend of healthcare cyberattacks continues; Roberto Polizzi Plastic Surgery Clinic joins the list of victims.
  • Detailed analysis reveals trove of confidential patient info, nude images, and PII, but no passwords or credit/debit card data.
  • While primarily in Portuguese, leaked nude images pose significant risks; potential for exploitation by cybercriminals.
  • Previous cybercrime groups like REvil, The Dark Overlord, and Tsar Team targeted plastic surgery clinics, extorting ransom payments and leaking data.
  • Breach underscores urgent need for improved healthcare cybersecurity to protect patient confidentiality and data.

A group of hackers operating under the alias Thesnake02 have leaked a trove of sensitive data belonging to the Roberto Polizzi Plastic Surgery Clinic based in Belo Horizonte, Brazil.

The breach, which occurred on July 26th, 2023, has resulted in the leak of approximately 1.25 GB of highly sensitive and private data, including surgery-related images, financial documents, and personal information of patients.

The clinic, managed by Dr. Roberto Polizzi, has become the latest victim of a growing trend of cyberattacks targeting healthcare and medical institutions. The leaked data, initially made public on the latest version of Breach Forums, has been closely examined by Hackread.com.

Hackers Leak PII Data and Photos of Plastic Surgery Patients
Post of the Breach Forums (Screenshot: Hackread.com)

Detailed analysis of the compromised data reveals a vast trove of confidential patient information, including nude images related to surgical procedures, WhatsApp messages, audio notes, receipts, CVs, invoices, internal clinic documents, and contact details.

The breach also exposed a wealth of personally identifiable information (PII), such as driver’s licenses, CPF IDs (Brazil’s equivalent of social security numbers), Covid certificates, and more. Importantly, no credit card or debit card information was among the leaked data.

Hackers Leak PII Data and Photos of Plastic Surgery Patients
The leaked data has been blurred over privacy concerns. (Screenshot: Hackread.com)

While the leaked records are primarily in Portuguese, we warn that the exposure of surgery-related nude images carries substantial potential risks. Cybercriminals could exploit this sensitive content in various harmful ways, including extortion and blackmail.

In the past, several notorious cybercrime syndicates, including REvil hackers (also known as the Sodinokibi group), The Dark Overlord, and Tsar Team, were involved in cyberattacks targeting plastic surgery clinics. These groups would extort ransom payments from their victims and, when these demands went unmet, proceeded to expose sensitive data online.

In December 2020, The Hospital Group, situated in Manchester, England, fell victim to REvil’s cyber attack. The plastic surgery clinic London Bridge Plastic Surgery (LBPS) was targeted by The Dark Overlord in October 2017, while Tsar Team successfully hacked and subsequently leaked data from Grozio Chirurgija, a cosmetic surgery clinic located in Kaunas, Lithuania back in May 2017.

As for the Roberto Polizzi Plastic Surgery Clinic, given the language barrier, the immediate impact of this breach might be somewhat limited. However, the incident underscores the critical need for enhanced cybersecurity measures within the healthcare sector, where patient confidentiality and data protection are of paramount importance.

  1. Hacked Finnish psychotherapy clinic files for bankruptcy
  2. Dental clinic alerted to ransomware attack via hacker phone call
  3. Plastic surgery tech firm leaks images of 100,000s of customers
  4. Breast Cancer Charity Exposed Sensitive Images of U.S. Patients
  5. Medical software firm leaked personal data of 3.1 million patients

[ad_2]
Source link