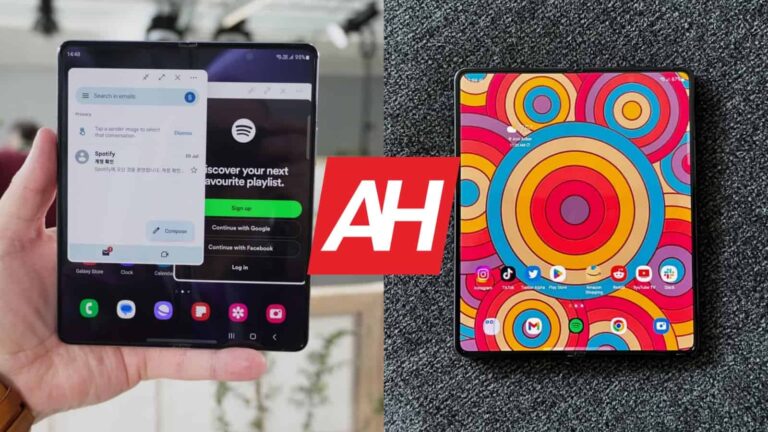
Samsung Galaxy Z Fold 5 vs Samsung Galaxy Z Fold 4

0
[ad_1]

During its recent ‘Unpacked’ event, Samsung announced two new foldable smartphones. The Galaxy Z Fold 5 is one of them, and we’re here to compare it to its predecessor. In this article, we’ll compare the Samsung Galaxy Z Fold 5 vs Samsung Galaxy Z Fold 4. You probably already heard that the two phones are quite similar design-wise, and that is true. Still, some differences are there, and they’re definitely worth noting.

We’ll first list their specifications, and will then move to compare these two foldable smartphones across a number of categories. We’ll compare their designs, displays, performance, battery life, cameras, and audio performance. This comparison will hopefully help you make a purchasing decision. So, let’s get started.

Specs

– Screen size (main): 7.6-inch Foldable Dynamic AMOLED 2X display (120Hz, HDR10+, 1,750 nits (Fold 5) / 1,200 nits (Fold 4))
– Screen size (cover): 6.2-inch Dynamic AMOLED 2X (120Hz)
– Screen resolution (main): 1812 x 2176
– Screen resolution (cover): 2316 x 904
– SoC: Snapdragon 8 Gen 2 for Galaxy / Snapdragon 8+ Gen 1
– RAM: 12GB (LPDDR5X) / 12GB (LPDDR5)
– Storage: 256GB/512GB/1TB / 256GB/512GB/1TB
– Rear cameras: 50MP (wide, f/1.8 aperture, OIS), 12MP (ultrawide, 123-degree FoV), 10MP (telephoto, 3x optical zoom)
– Front cameras: 4MP (under display, main display, f/1.8 aperture), 10MP (cover display, f/2.2 aperture)
– Battery: 4,400mAh
– Dimensions (unfolded): 154.9 x 129.9 x 6.1mm / 155.1 x 130.1 x 6.3mm
– Dimensions (folded): 154.9 x 67.1 x 13.4mm / 155.1 x 67.1 x 14.2-15.8mm
– Weight: 253 grams / 263 grams
– Connectivity: 5G, LTE, NFC, Wi-Fi, USB Type-C, Bluetooth 5.3 / 5.2
– Security: Side-facing fingerprint scanner
– OS: Android 13 with One UI / Android 12 with One UI (upgradable)
– Price: $1,799 / $1,799
– Buy: Samsung / Samsung

Samsung Galaxy Z Fold 5 vs Samsung Galaxy Z Fold 4: Design

These two smartphones look so similar, that many people would not even be able to tell the difference. There are two easy ways to differentiate between them, though. The first one is how they look when they’re folded. The Galaxy Z Fold 5 is the first device in the series that folds flat, the Galaxy Z Fold 4 does not. The Fold 5 also has an LED flash on the right side of its rear-facing cameras. The Fold 4’s LED flash is located below the camera island.

Both smartphones are made out of metal and glass, and both have the same form factor and shape. They both also come with flat sides all around. The Galaxy Z Fold 5 is a bit lighter, for about 10 grams, but that’s the difference that you likely won’t notice. Therefore they’ll both feel very similar in the hand, especially when unfolded. The Galaxy Z Fold 5 does have a more durable hinge, though, which should make the phone and its foldable display more durable.

They are basically identical in terms of height and width, that goes for both their folded and unfolded forms. The Galaxy Z Fold 5 is a bit thinner, though, but not by much. It’s still nowhere as thin as some of the competition. Both phones do come with an IPX8 rating for water resistance, and they both feel like truly quality products in the hand. They are both quite slippery, though.

Samsung Galaxy Z Fold 5 vs Samsung Galaxy Z Fold 4: Display

These two smartphones have the same displays, actually, in all but one area. That goes for both their main and cover displays. A 7.6-inch 1812 x 2176 Foldable Dynamic AMOLED 2X display sits on both phones. That panel offers a 120Hz refresh rate, and supports HDR10+ content. We’re looking at 373 ppi here, in case you were wondering.

Samsung Galaxy Z Fold 5 AH 17
Samsung Galaxy Z Fold 5

The cover display measures 6.2 inches, and it offers a resolution of 2316 x 904. That is a Dynamic AMOLED 2X panel too, but not a foldable one. It has a 120Hz refresh rate, and it’s protected by the Gorilla Glass Victus 2. The aspect ratio here is rather odd at 23.1:9, which makes the phone very narrow when folded.

The Galaxy Z Fold 5’s main display should be more durable overall, due to some improvements Samsung made, including a new hinge. Still, in terms of usability and image reproduction, they’re exactly the same. They feel the same to use. Now, I’ve mentioned that the two panels are not the same in one specific area. I was talking about the brightness. The Galaxy Z Fold 4’s main panel can go up to 1,200 nits of brightness at its peak, while the Galaxy Z Fold 5 goes up to 1,750 nits. That is a considerable difference, especially when you’re using the phone outdoors.

Samsung Galaxy Z Fold 5 vs Samsung Galaxy Z Fold 4: Performance

The Snapdragon 8 Gen 2 fuels the Galaxy Z Fold 5, while the phone also includes 12GB of LPDDR5X RAM and UFS 4.0 flash storage. On the flip side, the Galaxy Z Fold 4 is fueled by the Snapdragon 8+ Gen 1 SoC. The phone also includes 12GB of LPDDR5 RAM and UFS 3.1 flash storage. The Galaxy Z Fold 5 does have more powerful internals, but how does that reflect on actual performance?

Well, we only used the Galaxy Z Fold 5 for a couple of days thus far, but the performance has been solid. We do notice that the apps on the Fold 5 load a bit faster, but other than that, the two phones seem to be on par in terms of performance. They both fly through everyday tasks, while they’re also quite good for gaming. Both phones do get quite warm during gaming sessions, but that’s perfectly normal.

Samsung Galaxy Z Fold 5 vs Samsung Galaxy Z Fold 4: Battery

Samsung opted to stick with a 4,400mAh battery inside the Galaxy Z Fold 5. That is the same battery capacity the Fold 4 offers. The charging speed also remained unchanged, unfortunately. Both smartphones support 25W wired charging, in addition to 15W wireless charging, and 4.5W reverse wireless charging. Another thing to note is that neither of the two phones comes with a charger in the box. That 25W charging can get both phones to 50% in about 30 minutes, while it will take them about twice that much to reach a full charge.

What about the battery life? Well, it’s similar to what the Galaxy Z Fold 4 offered, at least based on our initial usage. Getting around 6-7 hours of screen on time is doable, as long as you’re not pushing the phone hard. If you’re gaming on it, you can expect noticeably worse numbers on a daily basis. Granted, this is based on our usage, but your mileage may vary considerably. Not only because you’ll use different apps, and have different signal strengths, but also because your usage will be different, and there are two screens included here. It all depends on how much time you’ll spend on the inner screen. We did use the outer screen quite a bit thus far.

Samsung Galaxy Z Fold 5 vs Samsung Galaxy Z Fold 4: Cameras

You will find identical camera hardware on these two smartphones. A 50-megapixel main camera is included, with an f/1.8 aperture, and OIS support. A 12-megapixel ultrawide camera also sits on both phones, with a 123-degree FoV. The third camera on the back is a 10-megapixel telephoto unit with 3x optical zoom support. On the main display, there is a 4-megapixel under-display camera, while a 10-megapixel selfie shooter sits on the cover display of both phones.

Samsung Galaxy Z Fold 4 Review AM AH 27
Samsung Galaxy Z Fold 4

In case you’re wondering about camera samples, well, they’re not too different. It’s not exactly a secret Samsung likes saturated images, as do most users. That’s what you’ll find on both of these. The images do seem to be a bit sharper on the Galaxy Z Fold 5, at least based on our initial impressions, but that could just be a placebo effect. We’re in the process of reviewing the Galaxy Z Fold 5, so you’ll get far more info in the near future.

Audio

When the audio is concerned, things are pretty much unchanged on the Fold 5. Both smartphones ship with a set of stereo speakers. Those speakers are tuned by AKG, and they sound more than fine. They’re loud enough, and also detailed enough. We don’t have any major complaints here.

What you will not find on either phone is a 3.5mm headphone jack. You can always use their Type-C ports for wired audio connections, though. If you prefer to go wireless, though, the Fold 5 supports Bluetooth 5.3, while the Fold 4 has Bluetooth 5.2 support.


[ad_2]
Source link
Musk announces that Twitter will be Dark Mode only but changes his mind

0
[ad_1]
Elon Musk has admitted that the value of his investment in Twitter has dropped precipitously since he bought the social media platform in October. From trying to monetize the verification checkmark to firing employees whose expertise was essential to running the platform, Musk got off to a bad start. In May, he hired a new CEO, and more recently capped the number of tweets that a Twitter user can view in one day.

Musk wants Twitter (or “X”) to be the next super app after China’s WeChat

And that was before he rebranded the platform from Twitter to “X” all because he wants the site to become a platform that does more than publish comments from users around the world. He wants Twitter to be another WeChat, the Chinese super-app that offers instant messaging, video games, mobile payments, social media, and more. Because of its multiple capabilities, the app has more than 1 billion monthly active users and is the largest standalone mobile app worldwide.

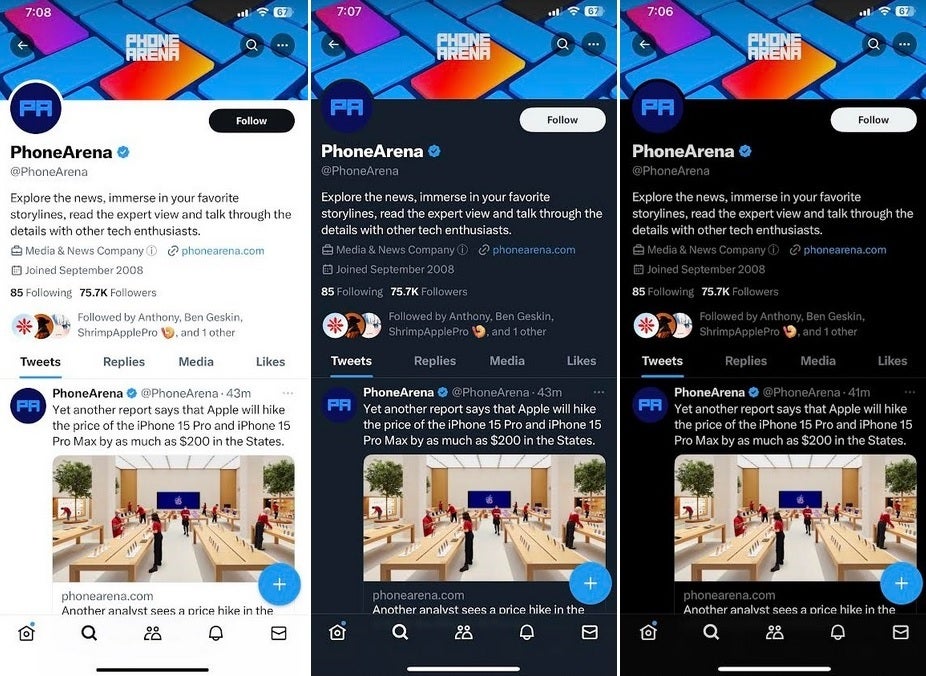
Musk has created a particular process for his changes. First, there is an initial tweet with a change so distasteful that Twitter users complain. So Musk then changes the new edict ever so slightly allowing Twitter users to think that they are getting what they want when Musk is actually making a change he wanted to make all along. That happened yesterday when Elon first announced that Twitter would eliminate Light Mode (black print on a white background) and Dim Mode leaving Dark Mode (white text on a back background) as the only option.

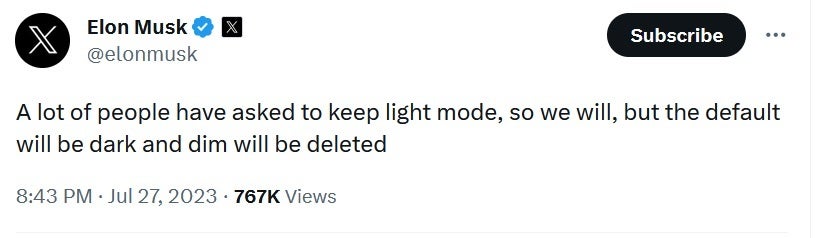
In his tweet, Musk wrote, “This platform will soon only have ‘dark mode’. It is better in every way.” The complaints soon started coming in from Twitter users not happy about the change. And sure enough, Musk soon rolled back the removal of light mode and instead announced that only the “Dim” Theme setting will be removed. This is a Dark Mode variant with a slightly lighter dark background. So Musk came to the decision that he will leave Light Mode and Dark Mode with the latter as the default setting.
If this process sounds familiar, when Musk first announced the cap on daily tweet views when this month started, he announced that new unverified members were limited to viewing 300 tweets a day, existing unverified members would be allowed to read 600 tweets daily, and verified members could see 6,000 posts a day. But after existing Twitter users tweeted their displeasure with these limits, Musk raised them to 400 Tweets daily for new unverified members, 800 tweets a day for unverified members, and 8,000 Tweets a day for those paying $8 per month for verification.

Musk made the right call by leaving Light Mode and Dark Mode

This writer believes that Musk actually made the right call by leaving light mode and dark mode. Most people feel more comfortable with Light Mode since it is easier to read in the daytime. Dark Mode is great for those who don’t want the bright white background from their phones burning the retinas of innocent bystanders while they view Twitter in a dark room or at night. 

And on OLED phones, Dark Mode can actually save battery life since creating the color black on such a display requires the appropriate pixels to be turned off. Pixels that aren’t on do not consume battery power. So a Dark Mode setting can reduce battery consumption by a small amount on phones sporting an OLED screen..

No one but Elon Musk knows how he plans on turning Twitter into “X,” the super-app. Even knowing that he wants to mold Twitter into another app like WeChat that has multiple capabilities doesn’t necessarily help us understand all of the moves he has made since buying the platform. One thing that we hope he learns is that not all Twitter users have the same tastes and preferences as he does.

Musk needs to stop shooting from the hip and tweeting out changes he wants to make to the platform without first doing some research. And now that Twitter has a CEO (Linda Yaccarino) hopefully Twitter can be run more like a business and not like a rich man’s hobby.


[ad_2]
Source link

N. Korean Lazarus Group Suspected in $37.3M CoinsPaid Crypto Heist

0
[ad_1]

IN SUMMARY

  • Crypto theft date: July 22, 2023
  • CoinsPaid strengthens systems post-attack
  • Blockchain Security firms Chainalysis and Match Systems aid the investigation

Cryptocurrency payments platform CoinsPaid has reported a massive security breach that led to the theft of $37.3 million on 22nd July. The company suspects the notorious North Korean state-backed hacker organization, Lazarus Group, to be behind the attack. CoinsPaid’s internal systems were compromised, prompting the firm to temporarily halt operations for four days.

The Lazarus Group has a long history of targeting cryptocurrency platforms. The extent of the hack caused significant damage to the company’s balance sheet and platform, leading to a temporary shutdown. However, the firm clarified that customer funds remained secure during the incident.

In response to the breach, CoinsPaid immediately engaged a team of experts to fortify their systems and minimize the impact of the attack. Despite the substantial funds stolen, the company believes that the hackers aimed for a much higher sum. As a result, the Lazarus Group ended up with a “record-low reward.”

CoinsPaid CEO, Max Krupyshev, expressed confidence that the perpetrators would face justice and emphasized the company’s commitment to fully restore operations in a new, secure environment. As of now, the platform is gradually resuming transactions, but it may take a few more days to ensure everything runs smoothly.

Collaboration with Estonian and Blockchain Security Firms

In response to the breach, CoinsPaid promptly filed a report with Estonian law enforcement to investigate the incident further. The company is working closely with local authorities to track the looted funds allegedly taken by the Lazarus Group.

Furthermore, several blockchain security firms, including Chainalysis, Match Systems, and Crystal, have joined forces to assist in the preliminary investigation during the first few days following the attack. Their expertise will aid in identifying the perpetrators and strengthening CoinsPaid’s security measures.

The Lazarus Group remains an active and notorious hacking organization with links to the North Korean Government. Beyond the attack on CoinsPaid, the group has been involved in numerous sophisticated hacking operations, targeting blockchain technology companies and cryptocurrency platforms.

Their tactics often involve spear-phishing campaigns, the use of custom malware, and exploiting native operating systems. In the past, Lazarus Group was responsible for significant heists, including the $100 million Harmony Bridge hack and the $620 million Ronin Bridge theft.

CoinsPaid’s resolve to strengthen its security measures and cooperate with law enforcement and security experts showcases the ongoing efforts to combat cyber threats in the cryptocurrency industry. 

  1. Hackers posing as LinkedIn recruiters to scam military
  2. Lazarus hackers suspected of targeting Indian space agency
  3. Phishers Exploiting Google Docs to Harvest Crypto Credentials
  4. SnatchCrypto attack hits DeFi, Blockchain Firms with backdoor
  5. LAZARUS Using TraderTraitor Malware Against Blockchain Orgs

[ad_2]
Source link

Samsung is nearing mass production of its first-gen Galaxy Ring

0
[ad_1]

Samsung‘s Galaxy Ring could enter mass production as early as next month. The Korean firm is reportedly nearing the final development stage of the tiny fitness-tracking wearable device and is expected to decide the mass production schedule in August. If things go according to the plan, Samsung may push the smart ring into production in August itself, the Korean media reports. A market release may not happen before 2024, though.

Samsung has been working on a smart ring for quite some time. The device, which can be worn on your fingers like a regular ring, will come equipped with various sensors to measure health data, including a temperature sensor, heart rate sensor, PPG (Photoplethysmography) sensor, and an ECG (Electrocardiogram) sensor. The plan is to make a comprehensive yet unintrusive mobile health and fitness tracker that offers better accuracy than wrist-worn smartwatches.

However, a smart ring is a complex device to make. Samsung has been taking its time to ensure that the first-gen Galaxy Ring is up to the mark. A couple of weeks back, the Korean publication The Elec reported that the device had entered the development stage. The same source is now reporting that the company has begun talks with its suppliers to develop the necessary parts. Once finalized, Samsung’s mobile business head TM Roh will review the parts development process next month.

The final production schedule will be determined after Roh completes the review of these development processes. Only time will tell whether the Galaxy Ring enters mass production in August. Its market release may take another year, though. Samsung will be required to obtain medical approvals for the product before selling it. This process can reportedly take 10 to 12 months. So the first-gen Galaxy Ring may not arrive until mid-2024 at the earliest.

Samsung is also exploring a Galaxy Ring for XR devices

Samsung may have yet to launch a smart ring, but the company seemingly has big plans for the industry. According to the new report, the Korean behemoth is already exploring a Galaxy Ring for XR (mixed reality) devices. It has already filed patents for related technologies.

The XR industry is expected to boom in the coming years. Apple recently launched its Vision Pro XR headset in anticipation of this impending boom. The device is scheduled to hit the market in early 2024. Samsung might be looking to grab this opportunity early with a smart ring that can work with such products. You can expect to hear more about Samsung’s Galaxy Ring efforts in the coming months.


[ad_2]
Source link

Mastodon & BeReal’s popularity has dropped significantly: report

0
[ad_1]

Mastodon, which was once seen as the most viable Twitter alternative, has fallen out of favor lately. After peaking in November 2022, when traffic to the platform exploded by nearly 600 percent, it has tumbled badly. A recent study by Uswitch.com reveals that Mastodon’s popularity has dropped about 84 percent from its peak. BeReal, Facebook, Twitter, and TikTok have also seen less interest in recent months. Instagram, Snapchat, and Telegram are among the social media platforms with growing popularity.

Mastodon drops in popularity after peaking during Twitter’s chaos

According to the new report, Mastodon amassed over four million searches in November last year. The open-source microblogging platform benefitted from Elon Musk’s chaotic takeover of Twitter in October. Musk announced several unpopular changes and also fired thousands of workers without notice. Angered by this, many Twitter users decided to quit the platform and started looking for alternatives. Mastodon emerged as the biggest name, with it gaining over 70,000 new users on the day Musk completed his Twitter takeover.

However, the chaos at Twitter gradually settled down, and it affected Mastodon’s popularity. In June 2023, it saw only 673,000 searches, an 83% drop from its peak. While it isn’t completely out of the game just yet, with searches seeing healthy growth from 450,000 in May 2023, Mastodon appears to be past its peak for once and all. The arrival of Meta’s Threads earlier this month has made things more difficult for the emerging social media platform. Threads is now seen as the real competitor for Twitter.

Since Threads is less than a month old, this study doesn’t evaluate its popularity, which has dropped a little after peaking in the first week of launch. The social media app that has seen the next worst drop in popularity after Mastodon is BeReal. Searches for this platform have declined almost 70 percent between October 2022 and June 2023. Launched in 2020, BeReal encourages users to share photos of their “real” selves rather than edited or filtered photos.

Bluesky, Discord, Facebook, Twitter, LinkedIn, TikTok, and WhatsApp are other social media platforms that have experienced a drop in searches in recent months. On the other hand, searches for Facebook Lite, Instagram, Pinterest, Snapchat, and Telegram peaked last month. Interestingly, a separate study recently showed that Americans are desperately looking to delete Instagram from their devices. So this study may not tell you the full story of a platform’s popularity. But no one can deny that Mastodon and BeReal are gradually falling out of favor.

Social media apps popularity by searches


[ad_2]
Source link

Hacker Using Google and Bing ads to Deliver Weaponized IT tools

0
[ad_1]

The latest research discovered malvertising campaigns abusing Google and Bing ads to target users seeking certain IT tools and deploying ransomware.

This campaign targets several organizations in the technology and non-profit sectors in North America. 

This campaign exhibits similar features of the infection chain that are related to the BlackCat (aka ALPHV) ransomware infection.

Sophos X ops researchers have found that a new variant of malware named Nitrogen was employed to trick users into downloading Trojanized ISO installers.

Attack Execution:

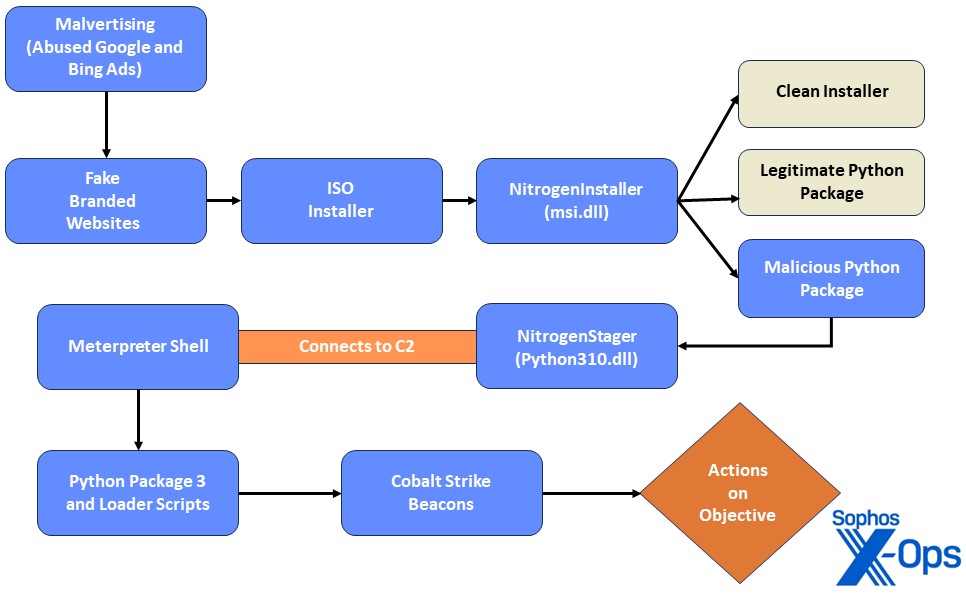
Initially, the threat actor targets users who visit advertisements on Google and Bing to obtain software tools and then redirects them to a malicious website hosted by the threat actor.

This campaign specifically targets IT professionals, as the advertised websites pose as prominent software installers such as AnyDesk, WinSCP, and Cisco AnyConnect VPN. 

For instance, when a user queries Google for WinSCP, a Google Ad referencing ‘Secure File Transfer – For Windows’ on the site softwareinteractivo[.]com

This site is a phishing page that impersonates a system administrator advice blog. 

Attack Chain

Once a user downloads a trojanized installer, ISO images are dropped on the compromised computer. 

These files are then mounted in Windows Explorer and can be transferred to a drive, where their contents are accessible.

When executed, the renamed msiexec.exe file sideloads the NitrogenInstaller file contained within the same image.

This Sideloading dynamic link libraries (DLLs)  technique is used by threat actors to disguise malicious activity as a legitimate process. 

In addition, they employ DLL proxying technique by forwarding exported functions to the legitimate msi.dll file in the system directory. 

Once executed, this NitrogenInstaller, drops a clean installer for the legitimate counterfeit application (e.g., Inno installer for WinSCP) 

In addition to that, it drops two Python packages: a legitimate Python archive and a NitrogenStager.

NitrogenInstaller attempts to gain elevated privileges by bypassing the User Access Control (UAC) with the CMSTPLUA CLSID. 

And Nitrogenstager creates a Meterpreter reverse TCP shell, enabling threat actors to execute code on the compromised system remotely.

Keep yourself informed about the latest Cyber Security News by following us on GoogleNews, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

Smartphone shipments are falling, but Pixels are rising

0
[ad_1]

The smartphone market has been in a tough spot over the past few years due to several reasons. People just aren’t as inspired to buy phones nowadays. While this is the case, Google’s Pixel phones seem to be one of the stars of smartphone shipments in Q2 2023, according to CounterPoint Research.

This isn’t a big shocker. Google was able to create a community around its phones and other devices. With the launch of the Pixel Tablet and Pixel Fold, it’s finally established its ecosystem. We’re only months away from the Pixel 8 phones, and those look to be pretty stellar devices.

Here are the smartphone shipments from Q2 2023

Here’s the quarterly smartphone market progress report, and the numbers aren’t great. The smartphone market, as a whole, saw a 24% drop. According to a previous Counterpoint report, the total number of smartphones shipped in Q1 2023 was about 280.2 million. Taking 24% from that, we get a ballpark figure of about 213 million units sold in Q2 2023.

Companies like Apple (-6%), Samsung (-37%), Motorola (-17%), and Alcatel (-69%) all saw a notable drop in their shipments compared to Q2 2022 (April 2022- June 2022). While Apple saw a 6% drop in shipments, the overall market shrunk, so its share of the smartphone market actually grew by 10%. Also, Motorola’s share managed to remain the same thanks to the shrinkage.

However, one underdog actually saw significant growth last quarter. Google’s Pixel phones saw a 48% jump in shipments. This led it to grab 3% of the market which is up from 1% during the same time last year. It’s all about timing, to be honest. The Pixel 7a launched last quarter along with the Pixel Fold. The rush of purchases on launch day is what propelled Google’s shipments.

We expect to see a similar surge in shipments when the Pixel 8 launches in the final quarter of the year. This is going to be the story for the other companies. When Apple releases the iPhone 15, we’ll see its numbers soar. Also, Samsung just announced its latest duo of foldable phones. We expect to see its numbers rise in the third quarter of the year.


[ad_2]
Source link

Intel CEO says they will incorporate AI in all platforms

0
[ad_1]

In this ongoing AI revolution, it’s no secret that many companies are trying everything at their disposal to integrate AI into their products and services. As part of these efforts, Intel has now unveiled its new ambitious plans to incorporate artificial intelligence (AI) into every product it creates.

This announcement comes just months before the upcoming Intel Meteor Lake chips, which could reportedly feature a built-in neural processor specifically designed for handling machine learning tasks. Additionally, when discussing the potential reach of AI in Intel’s products, Geslinger stated that the company would take a more comprehensive approach, with the expectation that AI will eventually become a ubiquitous feature in all Intel products, serving a wide range of use cases and customers.

“Today, you’re starting to see that people are going to the cloud and goofing around with ChatGPT writing a research paper and, you know, that’s super cool, right? And kids are, of course, simplifying their homework assignments that way, but you’re not going to do that for every client — because becoming AI enabled, it must be done on the client for that to occur, right? You can’t go to the cloud. You can’t round trip to the cloud,” said Geslinger.

Furthermore, Geslimger predicted that AI would eventually permeate all business domains, including the client-facing consumer electronics market, enterprise data centers, and even manufacturing. Additionally, he playfully mentioned that even personal devices like hearing aids will soon have AI built-in, including his own.

AI integration in Windows 12

Although Intel isn’t the one developing Windows, Geslinger also hinted that AI could play a significant role in the next iteration of Windows, opening up a new era for AI-powered computing and transforming how users interact with their devices. And as part of these efforts, Microsoft has already unveiled the co-pilot for Windows 11, allowing users to type questions and perform specific actions, such as adjusting settings to enhance focus or carrying out other tasks on the PC.


[ad_2]
Source link

Malvertising Attack Drops BlackCat Ransomware via Fake Search Results

0
[ad_1]

IN SUMMARY

  • The attack lures users into downloading malicious versions of well-known apps through Google Search results.
  • These apps include AnyDesk, AnyConnect, WinSCP, Treesize, Cisco, Slack, and more.
  • Once a system is infected, attackers install BlackCat ransomware (also known as ALPHV).

A new malvertising attack has been tracked whose prime target is businesses. According to the latest research report from Bitdefender, threat actors are luring users via advertisements to download malicious versions of popular applications, including AnyDesk, AnyConnect, WinSCP, Treesize, Cisco, Slack, etc.

Malvertising Attack Drops BlackCat Ransomware via Fake Search Results
Fake AnyDesk result on top of actual AnyDesk app on Google (Image cited by Bitdefender – It was originally identified by @mithrandir

Report authors Victor VRABIE and Alexandru MAXIMCIUC explained that in this campaign, hackers rely on DLL sideloading to inject malicious code into the fake versions to gain access to the victim’s computer.

Once invaded, they can perform a wide range of activities on the device, such as stealing credentials, exfiltrating data for extortion, establishing persistence, and installing BlackCat ransomware.

For your information, BlackCat ransomware is distributed by RaaS (ransomware-as-a-service) operators. Also called ALPHV, this ransomware is written in Rust programming language and targets Windows and Linux-based devices.

The Case of Malicious ISO Archive

In a blog post, the company wrote that cybercriminals are using a malicious ISO archive with attractive offers to lure business users. Apart from the promised software, a ZIP archive is part of the package. This file contains a Python executable (python.exe) and its dependencies, which launch the malicious code as a Meterpreter stager to let threat actors access the device and achieve their nefarious objectives.

Further probing revealed that the campaign has been active since May 2023, and organizations in North America are the prominent targets, particularly businesses in the US and Canada. So far, Bitdefender researchers have detected six organizations targeted in the US and one in Canada.

Why are Malvertising Attacks on the Rise?

Bitdefender researchers highlight that in the past few years, they have observed cybercriminals developing a preference for targeting businesses with malicious versions of commonly used business apps because it is relatively easier to exploit their popularity.

These bogus apps are distributed in ads promoted through malicious websites. First, attackers create fake websites containing malicious downloads for high-interest apps and make sure these sites appear on top of the search engine results through ads. Innocent users click on these ads and get their devices infected when downloading the fake app.

The complete list of indicators of compromise for this malvertising attack is available here (PDF).

  1. Royal Ransomware Use Google Ads to spread infection
  2. Fake Ads Manager Software Target Facebook Accounts
  3. Google Ads Malware Wipes NFT Influencer’s Crypto Wallet
  4. Fake Facebook Profiles, Google Ads Pushing Sys01 Stealer
  5. Google Ads drop FatalRAT malware from fake browser apps

[ad_2]
Source link

Hackers Attack Apache Tomcat Servers to Deploy Malware

0
[ad_1]

Apache Tomcat, a free and open-source server, supports Jakarta Servlet, Expression Language, and WebSocket technologies, providing a “pure Java” HTTP web server environment.

Apache Tomcat dominates with nearly 50% developer adoption, and it’s widely used in the following developments:-

Aqua’s cybersecurity researchers found a new campaign exploiting misconfigured Apache Tomcat servers to deliver Mirai botnet malware and cryptocurrency miners.

Technical analysis

Over two years, Aqua identified 800+ attacks on its Tomcat server honeypots, 96% linked to the Mirai botnet.

Among the attacks, 20% (152) used the “neww” web shell script, sourced from 24 IPs, and 68% came from 104.248.157[.]218.

IPs initiating the attack (Source – Aqua)

The threat actor launched a brute force attack against the scanned Tomcat servers to access the web application manager through various credential combinations.

After successful entry, threat actors deploy a WAR file with ‘cmd.jsp’ web shell, enabling remote command execution on the Tomcat server that is compromised.

The whole attack chain involves the “downloading and running” of “neww” shell script, which is then deleted using the “rm -rf” command. The script then fetches 12 binary files tailored to the attacked system’s architecture.

Attack Flow (Source – Aqua)

The WAR file holds essential files for web applications, including:-

While all these elements efficiently streamline the web app deployment on compromised Tomcat servers.

The last-stage malware is a Mirai botnet variant, utilizing infected hosts for orchestrating distributed denial-of-service (DDoS) attacks.

Threat actor infiltrates web app manager with valid credentials, uploads disguised web shell in WAR file, executes commands remotely and initiates the attack.

The findings highlight cryptocurrency mining‘s lucrative growth, with a 399% increase and 332 million cryptojacking attacks globally in H1 2023.

Recommendation

Cybersecurity analysts recommended the following recommendations to mitigate such attacks:-

  • Make sure to configure all your environments properly.
  • Make sure to frequently scan your environments for unknown threats.
  • Empower your developers, DevOps, and security teams with cloud-native tools for scanning vulnerabilities and misconfigurations.
  • Make sure to use runtime detection and response solutions.

Keep yourself informed about the latest Cyber Security News by following us on GoogleNews, Linkedin, Twitter, and Facebook.


[ad_2]
Source link