12 Norway Government Ministries were Targeted in a Cyberattack

0
[ad_1]

According to recent reports, twelve government ministries in Norway have been targeted by cyber-attacks.

The most recent attack was aimed at Norway’s public sector, and investigations are currently ongoing.

Norway has been Europe’s largest gas supplier after Russia had a drop in the supply. Norway has also become Western Europe’s largest oil exporter.

The cyber attack was identified as there was unusual traffic in Norway’s platform which was discovered on July 12.

Erik Hope, the head of the government agency and in charge of providing services to the ministries, said, “We identified a weakness in the platform of one of our suppliers and that weakness has now been shut”.

Norway Prognosticated in February

In February, the Nordic Police Security Agency (PST) was taking necessary precautions for a cyber attack in response to the war between Russia and Ukraine.

The PST said, ”Moscow would likely prioritize actions such as illegal gathering of intelligence, theft of information, cyber operations or cultivating sources, these are more probable”.

As predicted, there was a Distributed Denial-of-service (DDoS) attack against Norway’s state sector in June 2022, which was to be blamed on a “Criminal Russian pro group”.

However, the recent cyber attack did not affect the Prime Minister’s Office, including ministries like Foreign, Defense, and Justice, as they were using a different IT platform.

Norway is NATO’s northernmost member. Cyber attacks against Norway have seen massive increases between 2019 and 2021. The incidents stayed at the same level in 2022. Norway has increased military alerts ever since the war in Ukraine.

The tensions between the two nations remain in the same stage, affecting the neighboring countries and other nations.

However, cyber-attacks have seen a large increase in recent times and are predicted to increase furthermore. 

Peace must prevail between the two nations, which will contribute a lot of good towards humanity and a great benefit for the neighboring nations and the world.

Stay up-to-date with the latest Cyber Security News; follow us on GoogleNews, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

Deezer launches its new Android Automotive app

0
[ad_1]

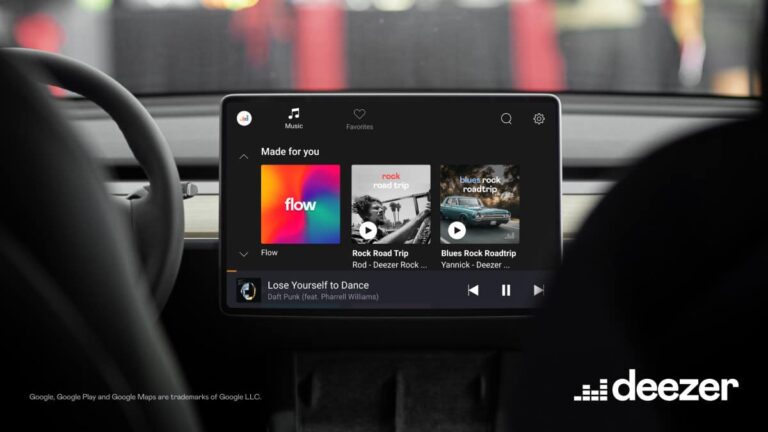
Ever since its introduction in 2017, Google has been steadily working to improve the Android Automotive experience through partnerships with various companies. Now, in line with these efforts, Deezer, the French-based music streaming service, has recently launched its new Android Automotive app on the Faurecia Aptoide app store, offering a seamless music experience without the need to connect your phone.

Although not the biggest streaming giant in the United States, Deezer has garnered a substantial following in Europe, thanks in part to its extensive music library, which includes over 120 million songs, and the “Flow” discovery search engine, which enables users to explore new music based on their preferences. And now, with this new Android Automotive integration, Deezer premium users, which cost $10.99 a month, can enjoy access to personalized playlists and AI-generated Flow recommendations in their cars without the need to interact with their smartphones.

Alternatively, the company also offers a free version that grants access to over 90 million songs, albeit with advertisements and without personalized mixes and playlists. As a result, it could become a compelling option for users who do not want to pay for the service.

“Music has the power to enhance any situation, and listening to your top songs in the car is essential to people all over the world. It’s our pleasure to introduce our new automotive app, giving drivers seamless access to their favourite music on Deezer. With this launch, we’re excited to get on the road with some of the world’s finest car manufacturers,” said Nicolas Pinoteau, VP of Product & Engineering at Deezer.

Simplicity at core

While features like the extensive library and personalized playlists are big selling points, simplicity and user-friendliness are the most important factors when designing an Android Automotive app. Taking these things into consideration, Deezer says they have designed the app to ensure that drivers can access their favourite tracks and playlists without the hassle of navigating complex menus.


[ad_2]
Source link

iPhone 16 Pro is expected use a brand new Sony camera sensor

0
[ad_1]

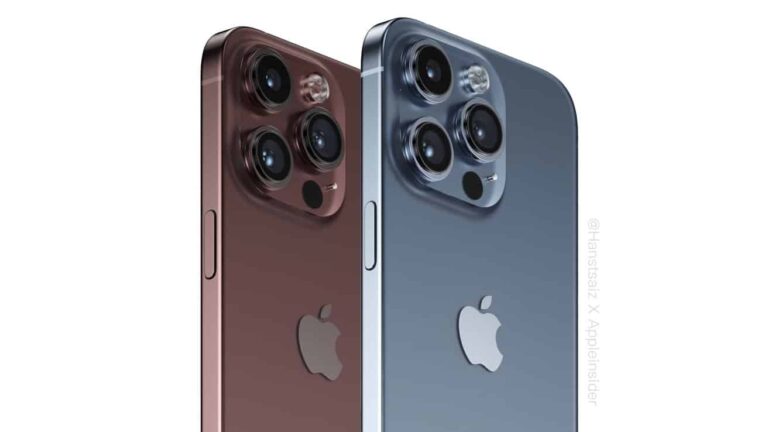
The iPhone 16 Pro is expected to use a brand new Sony camera. This information comes from Ice Universe, a well-known tipster. He claims that the phone will use a new 1/1.14” Sony main camera, and new double-layer transistor technology.

The iPhone 16 Pro is tipped to use a brand new Sony camera sensor

On the flip side, Samsung seemingly plans to stick with its ISOCELL HP2 sensor all the way to the Galaxy S26 Ultra. This means that the Galaxy S24 Ultra and Galaxy S25 Ultra will both utilize that same sensor in 2024 and 2025.

The iPhone 16 Pro, as many of you know, is coming next year. The iPhone 15 series will launch this year, either in September or October, if the rumored delay takes place. The iPhone 16 series is likely coming in September 2024.

Ice Universe says that this 1/1.14” Sony sensor can compete with the 1-inch Sony IMX989 sensor. It remains to be seen if that will be the case, but it does sound promising, that’s for sure.

Type-C is coming to iPhones

The iPhone 15 series will usher in a Type-C port for iPhones. Apple has been using Type-C on other devices, but not its iPhones. The company got pushed into making the change this year by the EU.

All iPhone 15 models will also feature a Dynamic Island on the display. The iPhone 15 Pro Max is rumored to become the very first iPhone to utilize a periscope telephoto camera. The iPhone 15 Pro seemingly won’t offer that camera, but its successor will.

The ‘Pro’ iPhone 15 models are also expected to offer the thinnest bezels in the business, at least according to rumors. The overall design won’t change much, however. Apple may use titanium for the frame of both ‘Pro’ models, however. We’ll find out everything in a couple of months.


[ad_2]
Source link

YouTube Shorts is getting a new experimental feature

0
[ad_1]

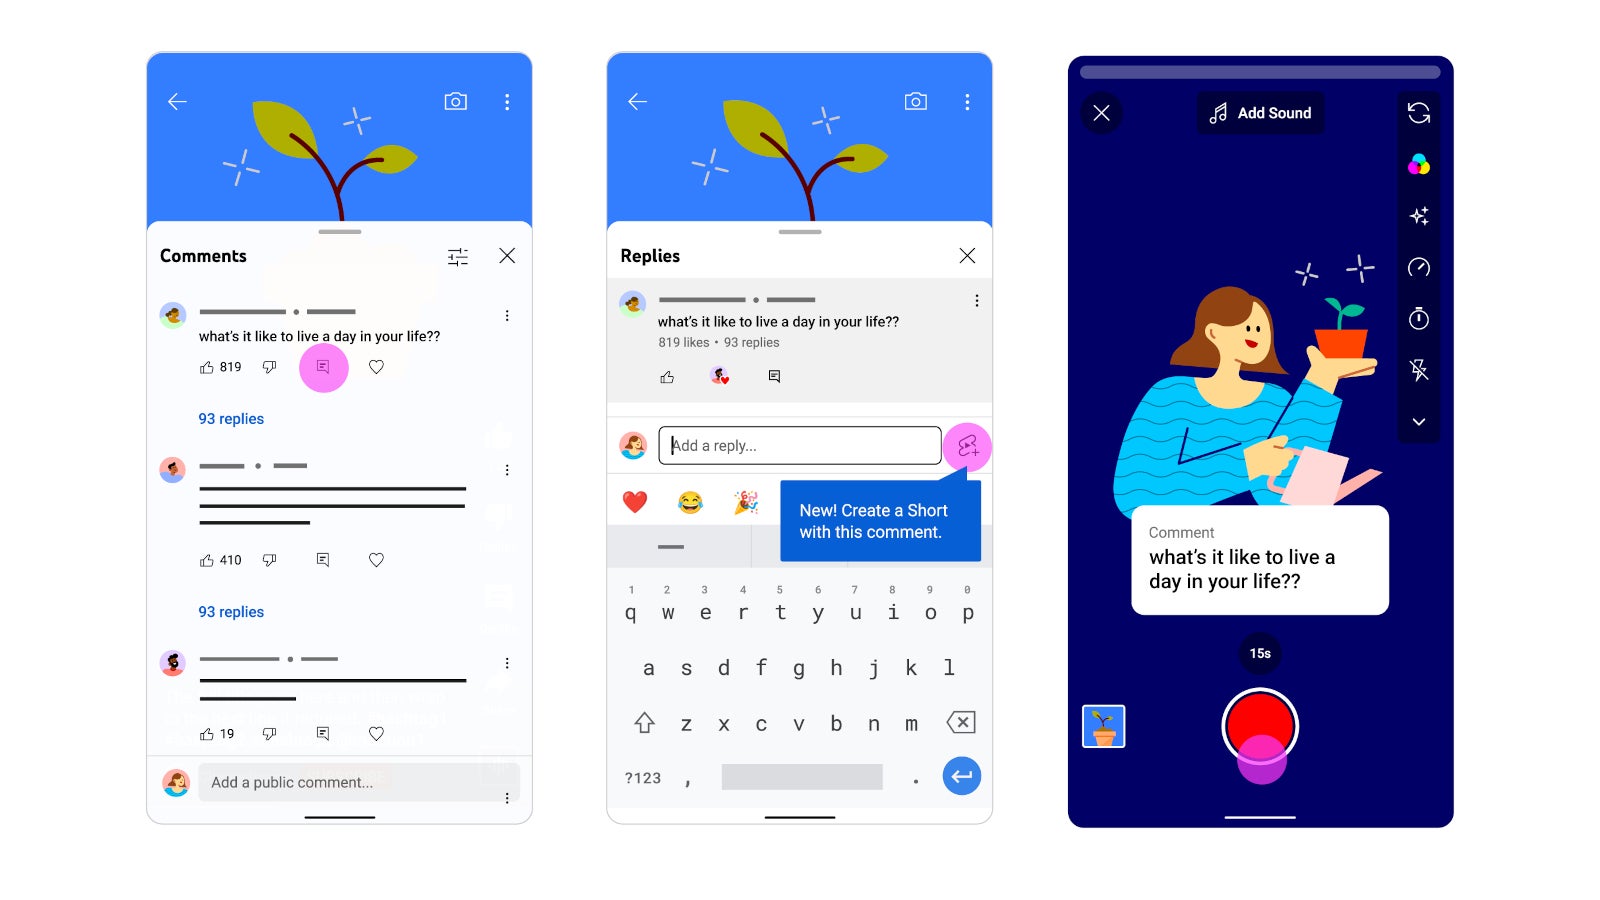
YouTube has been testing several new features since the beginning of the year, and while not all have been released to the general public, it’s interesting to see what the company’s engineers are working on. The most recent experimental feature that YouTube is testing is aimed at those who love creating Shorts, the service’s alternative to TikTok short videos.Starting today, those who have access to the new feature on mobile devices will be able to create Shorts featuring comments posted on videos they’re watching. Previously, this feature was only available for creators, who were able to reply to comments posted on their own content with a Short, so the experimental feature now offers viewers the option to create content from comments too.

YouTube says that once created, the Short should appear in the Shorts feed and on the viewer’s channel page. However, it’s important to add Shorts created by viewers don’t function the same as those posted by creators. For starters, viewer-created Shorts will not send notifications to the creator whose video comment is on, nor the comment author.

If you’re among the lucky ones to get access to the feature, here is how you can turn comments into Shorts:
  • From the watch page of a video tap Reply on a comment
  • Tap Create a Short
  • You’re good to go!

Furthermore, creators will not be able to prevent viewers from using their comments from being features in a Short, unless comments on their videos are disabled. Now, if you’re interested in getting the experimental feature and start creating Shorts from comments, we have a little bit of bad news for you.

According to YouTube, this specific feature is only available to a small percentage of viewers on Android and iOS mobile devices. On the bright side, the availability of the experimental feature isn’t limited to one or more regions, as YouTube claims it should be rolled out globally.


[ad_2]
Source link

DangerousPassword Attacks Desktops With Python Malware

0
[ad_1]

Researchers have found a new malware campaign from the DangerousPassword attack group against desktops. The threat actors have caught the malicious campaign deploying Python and Node.js malware on Linux, Windows, and Mac devices.

DangerousPassword Running Active Malware Campaigns Against Desktops

According to JPCERT/CC, the notorious DangerousPassword attack group is running active campaigns against all major desktop systems – Windows, Mac, and Linux. Specifically, the malicious campaign targets these desktops with Python and Node.js malware.

In brief, the attack flow begins by tricking the user into downloading and executing a malicious file, “builder.py,” in the Python module for handling QR codes. Upon reaching the target device, the Python malware gathers system information, transmits it to the C2, and proceeds or modifies the attack flow accordingly for the respective OS.

On Windows, the malware downloads one or more executable MSI files from an external source while communicating with C2. One of these MSI files gathers the device’s information, whereas the other MSI file downloads a DLL file (devobj.dll) and sideloads it to the rdpclip.exe (a standard Windows program) to execute the malware.

On macOS and Linux systems, after the Python malware reaches the devices, the embedded BASE64-encoded strings decode and execute as a Python file. After transmitting system details to the C2, the malware downloads the PythonHTTPBackdoor. In some cases, the researchers also noticed the attack infecting the devices with another malware, JokerSpy.

Besides the Python malware, the JPCERT/CC also observed the involvement of “route.js” and “request.js” malicious files. The Node.js malware also follows a similar attack flow to the Python counterpart, executing the attack sneakily.

The researchers have shared a detailed technical analysis of the malware campaign in their advisory.

DangerousPassword, aka “CryptoMimic” and “SnatchCrypto,” is a known malware that has been actively running malicious campaigns since 2019. Despite being known for years, the malware’s persistent success indicates its grip on executing stealthy attacks. The key to preventing such attacks is to avoid interacting with URLs, files, and attachments from unknown sources.

Let us know your thoughts in the comments.


[ad_2]
Source link

Galaxy S24 series might not get a better selfie camera

0
[ad_1]

Samsung has a major hardware launch event scheduled for this Wednesday, July 26. The company will launch new foldables, tablets, and smartwatches at the event. But behind the scenes, it’s already working on its next-gen Galaxy S flagships. The Galaxy S24 series will arrive in early 2024 with a few hardware upgrades over this year’s Galaxy S23. Unfortunately, the Korean firm may not upgrade the selfie camera.

Sources have told GalaxyClub that the Galaxy S24, Galaxy S24+, and Galaxy S24 Ultra will use the same 12MP selfie camera found on the Galaxy S23 trio. It’s not a new camera with an unchanged resolution, but the sensor itself remains unchanged. unchanged  We are talking about the Samsung S5K3LU sensor that has 1.12µm pixels and an f/2.2 aperture. It supports dual-pixel PDAF (phase detection autofocus).

That’s not to say the Galaxy S24 series won’t capture better selfies than the Galaxy S23 models, which already offer one of the best smartphone cameras out there. Samsung can still improve the picture quality with software optimizations. After all, good photos are a combination of quality hardware and powerful software processing. Just that it won’t be a substantial upgrade in selfie photos.

It’s worth noting that the 12MP selfie camera found on the Galaxy S23 series is relatively new too. Samsung used a 10MP or 40MP selfie shooter in its Galaxy S series flagships for three generations before that. It might now be looking to refine the sensor rather than opt for something new. It’s standard practice for the Korean firm to reuse the same flagship camera for a few years before upgrading it.

The Galaxy S24 might not significantly upgrade the rear cameras either

It’s not just the selfie camera that may remain unchanged on the Galaxy S24 series. Samsung will reportedly reuse the rear cameras as well. The 200MP ISOCELL HP2 sensor that debuted on the Galaxy S23 Ultra is expected to return with the Galaxy S24 Ultra next year. The 12MP ultrawide lens might also carry over unchanged, and so might the 3x zoom camera.

The 10x zoom camera, meanwhile, may get some improvements if early rumors turn out to be accurate. Since the Galaxy S24 series is still several months away, you should be cautious about the authenticity of this information. We will let you know when we know more. For the time being, stay tuned for Samsung’s Galaxy Unpacked event in a couple of days.


[ad_2]
Source link

Fable Studios showcases the SHOW-1 AI amidst the writer’s strike

0
[ad_1]

The ever-growing influence of Artificial Intelligence and generative AI has caused panic in many industries, including entertainment, where writers and actors have gone on strike. Now, amidst the strike, Fable Studios unveiled its new AI model called SHOW-1, which allegedly has the capacity to make an entire TV show and showcased its capabilities with a fake “South Park” episode.

Although the episode was just 11 minutes long and lacked the authenticity and humour of the original series, it provided a glimpse into SHOW-1’s capabilities, which utilizes a large language model (LLM) and diffusion tools to construct scripts and visuals while the user contributes by selecting characters, settings, and providing prompts for the AI to work with.

Ethical concerns

Despite demonstrating significant development in the AI field, there are ethical and creative concerns regarding its impact on the livelihoods of professionals in the entertainment industry. Additionally, with over half of Hollywood already on strike, studio executives could potentially use this technology as a cost-cutting measure, leading to widespread job losses and a decline in the quality of creative work. And this is the reason why industry professionals are calling out for strict protections against the unchecked use of AI tools by producers without artists’ express permission.

Fable’s response

When discussing the potential repercussions of introducing the SHOW-1 AI at such a sensitive time, Edward Saatchi, the CEO of Fable Studios, argued that this development could benefit the labour side of the dispute. He believes that demonstrating the capabilities of AI can prompt discussions that lead to establishing clear rules and limitations for its usage in creative processes.

“We think the timing is correct — we are right in the middle of the biggest strike in 60 years, by releasing the research (but not the ability for anyone to create episodes of protected IP), we hope [for] the Guilds in Hollywood to negotiate strong, strong, strong protections that producers cannot use AI tools without the express permission of artists,” said Edward Saatchi.

However, many people participating in the strike remain sceptical about the positive impact of this development, with some speculating it to be a clever marketing stunt. Nevertheless, Fable’s AI technology has sparked significant debate, as the company aims to achieve Artificial General Intelligence (AGI) through simulated characters living in virtual environments.


[ad_2]
Source link

Twitter sets a limit to the number of DMs an unverified user can send

0
[ad_1]

Changes have become a regular occurrence on Twitter lately. Perhaps the most significant change since Elon Musk’s acquisition of the company is the latest rebranding, where X is set to replace the blue bird. While soon the iconic bird might no longer fly around the web, sharing tweets, it is still here and brings some updates.

 
Twitter (or X, as we might soon call it) limits the number of DMs unverified accounts can send. According to the company, this change aims at reducing spam in Direct Messages. So, if you don’t have a paid account, you will have a daily limit for sending out DMs. And if you don’t want to experience this limitation, the option is for you to subscribe to Twitter Blue.


These changes, aimed at attracting more paid users seem reasonable since Twitter is still not generating profits. Elon Musk himself shared that the company is facing negative cash flow due to a significant drop in advertising revenue in addition to a heavy debt load.


The rebranding of the platform is another move by Musk to transform the company into a profitable one. We could expect X to introduce further changes to encourage unpaid subscriptions to convert into paid ones. With the bird gone, the rebranded platform can start afresh with a new vision, purpose, and features. Unlike unverified accounts, there seem to be no limitations set for Musk and his team’s imagination.


[ad_2]
Source link

Hacked Microsoft Keys Access a Wide Range of Azure Applications

0
[ad_1]

The China-linked threat actors who stole the US State Department and other Microsoft customer emails may have acquired access to apps other than Exchange Online and Outlook.com.

According to Wiz Researchers, the compromised signing key was more potent than it first appeared to be and was not restricted to just those two services.

The threat actor may have been able to forge access tokens for a variety of Azure Active Directory applications, including any that supports personal account authentication, such as SharePoint, Teams, or OneDrive, as well as customer applications that support the “login with Microsoft” feature and multi-tenant applications under specific circumstances.

It is advised to organizations look for instances of forged token usage on any potentially compromised apps.

Overview of the Hack

Microsoft issued a warning earlier this month after an advanced persistent threat group it refers to as Storm-0558 breached the systems of around 25 customers globally, including several government clients.

The hackers purportedly obtained access to private emails from U.S. Commerce Secretary Gina Raimondo and other high-profile individuals.

The Cybersecurity and Infrastructure Security Agency (CISA) collaborated with Microsoft on efforts to mitigate the damage and further examine how the hackers initially got access after government authorities informed Microsoft about the incident.

According to a statement by Microsoft earlier this month, the threat actor created access tokens for Exchange Online and Outlook.com after gaining access to an MSA consumer signing key.

The Wiz study reveals that the key gives users access to a significantly larger range of applications.

The signing keys used by identity providers are among the most potent trade secrets today. They are far more potent than TLS keys, for instance.

To have a major impact, an attacker would still need to impersonate a google.com server even if they had access to the google.com TLS key. One may instantly and directly access any email box, file service, or cloud account using identity provider keys.

To secure important keys like this one, our industry, notably cloud service providers, must commit to higher security and transparency.

The risks of compromised OpenID signing key

Which Applications Are Affected?

The analysis says the problem only affected Azure Active Directory applications that use Microsoft’s OpenID v2.0. Applications running on version 1.0 were unaffected since the token validation process did not use the compromised key.

Recommendation

  • Search for the use of forged tokens and use the Indicators of Compromise (IoCs) published by Microsoft to look for any activity that originates from the IP addresses provided by Microsoft.
  • Verify that no apps are using the cached version of the Microsoft OpenID public certificates, and clear the cache if they are.
  • Microsoft has introduced extra verifications to the official Azure SDK to prevent the use of MSA keys to authenticate organization accounts. The most recent version of the package should be updated by users.

Stay up-to-date with the latest Cyber Security News; follow us on GoogleNews, Linkedin, Twitter, and Facebook.


[ad_2]
Source link