Global CDN Service ‘jsdelivr’ Exposed Users to Phishing Attacks

0
[ad_1]

In the interconnected world of web development, open-source components play a vital role, facilitating collaboration and code sharing within the developer community. However, recent incidents have exposed vulnerabilities in the supply chain, with malicious actors leveraging open-source content delivery networks (CDNs) to serve dangerous packages even after they have been flagged and removed from package registries.

NPM Registry: A Playground for JavaScript Package Sharing

NPM (Node Package Manager) has long been the go-to package manager for the JavaScript programming language and the default choice for Node.js projects. With over a million open-source JavaScript packages available in its centralized registry, NPM enables developers to easily install, manage, and share code packages. To safeguard developers, NPM employs security measures like automated vulnerability scanning, advisories, and the ability to audit installed packages for known security flaws.

jsdelivr CDN: A Global Content Distribution Hub

jsdelivr, an open-source content delivery network, offers a fast and reliable way for developers to host and distribute files, including external libraries and resources for web projects. Operating as a global CDN with servers distributed worldwide, jsdelivr ensures that files are fetched from the server closest to the user’s location, optimizing performance and reducing latency. Its support for versioning allows developers to reference specific library versions, ensuring project stability amid updates.

Malicious Package Reactenz Exploits CDN Vulnerability

The recent discovery of the malicious package “reactenz” brought attention to a concerning flaw in the system. The package masqueraded as a legitimate alternative to the popular “react-enzyme” package, used widely in GitHub code snippets. However, upon further investigation, it was revealed that “reactenz” harbored a malicious intent.

Global CDN Service 'jsdelivr' Exposed Users to Phishing Attacks

Once integrated into a web page, “reactenz” downloaded an encoded .txt file from the jsdelivr CDN service and de-coded it as HTML. The content of the .txt file turned out to be a classic phishing HTML code, designed to trick users into resetting their Microsoft passwords and stealing their updated credentials. What’s particularly troubling is that “reactenz” was still accessible through the CDN even after being marked as malicious on NPM.

CDN Vulnerabilities and Supply Chain Attacks

This incident exposes two critical issues. First, while NPM attempts to remove malicious packages swiftly, the content served through the CDN remains accessible long after detection. Second, threat actors can leverage CDN services to serve malicious content while evading conventional security tools, which often monitor web downloads for potential malicious indicators.

Another alarming discovery was the malicious package “standforusz,” which remained accessible through the jsdelivr CDN, even a month after being marked as malicious on NPM. A similar case was found with the package “markedjs,” which was identified as malicious more than a year ago but still had accessible malicious components on the CDN.

Collaborative Security Efforts

In a blog post, Ori Abramovsky, Head Of Data Science Check Point CloudGuard said that researchers promptly reported the findings to NPM and jsdelivr, leading to the removal of the malicious packages and content from their platforms. However, this incident emphasizes the ongoing risk posed by open-source components, urging developers to be vigilant and verify the integrity of their dependencies.

Addressing the supply chain attack risks requires a collective effort from the developer community. Developers must exercise caution when using open-source packages, verify their authenticity, and adopt secure development practices. Security tools and package registries also need to strengthen measures to prevent supply chain attacks and promptly remove malicious packages.

In conclusion, the recent exploit of the jsdelivr CDN underscores the need for continued vigilance and collaboration in the open-source community. By maintaining a secure development process and staying informed about potential risks, developers can work together to protect the integrity of their projects and the safety of end-users.

  1. Content Delivery Network (CDN) FAQs
  2. Millions of websites using CDNs at risk of CPDoS attack
  3. PABX platform 3CX Desktop App suffers supply chain attack
  4. What Are Secure Supply Chain Management Solutions There?
  5. GoogleUserContent CDN Hosting Images Infected with Malware

[ad_2]
Source link

PII of Thousands of Developers Stolen

0
[ad_1]

In total, 3,943 Roblox developer accounts were compromised but what’s more concerning is that, apart from adults, children aged 13 and above are also allowed to join the Roblox Developer program.

Back in 2021, Roblox suffered a data breach, but the company reportedly hid this information for at least two years. The breach mainly impacted attendees of past conferences held between 2017-2020 for Roblox developers, who now risk harassment and online scams like identity theft.

The website Have I Been Pwned’s creator Troy Hunt brought the data exposure to public attention on 18th July. According to Hunt’s tweet, several people informed him about their private details available online. However, Hunt stated that the breach’s impact didn’t go beyond Roblox’s niche cheating communities.

Hunt explained that the breach originally occurred on 18th December 2020, and around 3,943 accounts were compromised. The exposed data included sensitive details such as names, usernames, phone numbers, email IDs, IP addresses, home addresses, date of birth, and T-shirt sizes. When he informed the company, Roblox said they had contacted all affected individuals.

“Minimally affected users just got a sorry email. For more seriously affected users, they got a year of identity protection and an apology for everyone else,” Roblox’s response to Hunt read.

Roblox Data Breach: PII of Thousands of Developers Stolen
Emails sent by Roblox

Roblox admitted that a third-party security issue led to unauthorized access to a subset of personal data belonging to its creators. The company collaborated with independent experts and launched an investigation to determine the cause and impact of this incident.

The companies maintained that it will send all impacted creators an email informing them about the steps Roblox intends to take to support them, and they will now vigilantly monitor and vet its cybersecurity systems and the affiliated third-party vendors.

It must be noted that, apart from adults, children aged 13 and above are also allowed to join the Roblox Developer program, according to this Roblox guide. However, the platform isn’t designed for minors.

This is why the data leak can have a far-reaching impact, considering that, according to the first quarter earnings report of 2023, approximately 43% of Roblox’s over 66 million daily active users were minors.

Roblox Data Breach: PII of Thousands of Developers Stolen
The leak data seen by Hackread.com shows the records indeed contain data of teen developers (Image credit: Hackread.com)

The exposure of email IDs can expose users to phishing attempts or spam campaigns. Moreover, targeted scams can be launched easily using other details.

In a comment on the Roblox breach, Samantha Humphries, Head of Security Strategy EMEA, Exabeam told Hackread.com that “The threat actors who conducted the attack were likely not going after Roblox, but the personal accounts and workplaces of those who attended the conference. Rather than attack each organisation individually, the adversary probably figured it would be easier to break through Roblox, particularly because this isn’t the company’s first data leak incident.”

Samantha warned that “For any organisation that had representatives attending the conference, it’s critical to have visibility and insights into user activities to detect anomalies, investigate, and then mitigate any abnormal behaviour.”

“To reduce the chance of unauthorised third-party access, which Roblox confirmed contributed to the release, I would encourage organisations to create a vendor risk management plan, thoroughly vet third parties, and require accountability to remain vigilant and align to best cybersecurity practices such as strong password management, Samantha advised.

Roblox is a widely used platform boasting an extensive user base and developer community. But, the platform is criticized for weak security. The company claims to protect user privacy and data, but its attempt to hide the breach for such a long time has tainted users’ trust.

Users should take precautionary measures while using these services. Always change your password periodically and enable 2FA authentication. Keep monitoring financial accounts to identify suspicious activities promptly.

  1. Hackers deface Roblox accounts with pro-Trump messages
  2. Epic Games Forums Suffer Data Breach; 800k Accounts Stolen
  3. Town of Salem data breach: Personal data of 7.6M gamers stolen
  4. Game giant Electronic Arts is the latest victim of massive data breach
  5. Fake ROBLOX and Nintendo game cracks drop ChromeLoader malware

[ad_2]
Source link

Telegram is rolling out Stories for Premium users

0
[ad_1]

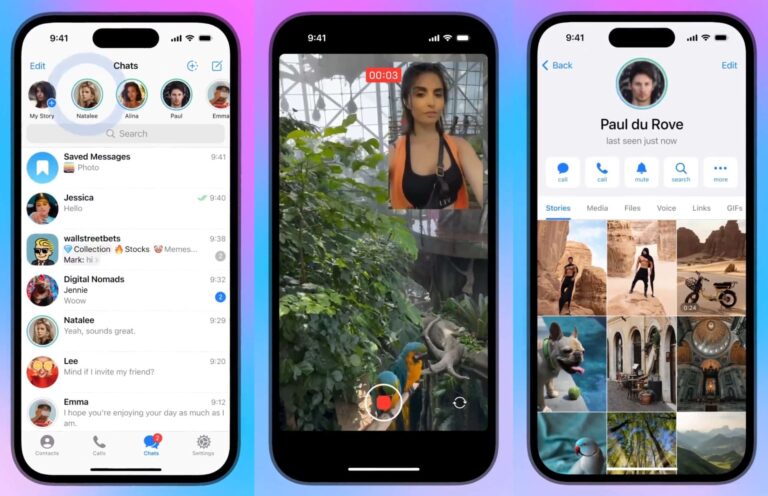
A month after the original announcement, Telegram’s Stories feature is now rolling out to users. According to the company, only Premium subscribers can “currently” post Stories. All Telegram users can see those temporary, auto-expiring photo and video statuses.

Stories appear to be available with Telegram version 9.7.0 for Android. The latest update for the app adds a + button at the top of your chat list. Tapping this button will allow you to post a Story, with Telegram allowing you to add captions and links, and tag other users as well. You get a host of photo and video-editing tools to stylize your Stories.

While you can use pre-captured photos and videos in your Stories, Telegram also lets you live-record videos with the front and back cameras simultaneously. Depending on your setting, your Story will expire in 6, 12, 24, or 48 hours. You can also make Stories permanent, though. You’ll have to manually select which Stories will permanently appear on your profile page. Telegram gives you individual privacy settings for each.

Speaking of privacy, Telegram offers a range of privacy settings for your Stories. You can choose to make a Story public or make it viewable only to your contacts, select contacts, or Close Friends. A “My Stories” section at the top of the left hamburger menu is where you will find your stories. Telegram offers two separate tabs here: Saved and Archive. The latter tab lets you pick Stories that you want to make permanent.

Only Telegram Premium users can currently post Stories

For viewers, Stories will appear in an expandable section at the top of the chat list. Once again, you get control over the Stories that you see. If you don’t want to see those updates from a certain user, you can easily block or hide them. As said earlier, all Telegram users can now see Stories posted by other users. But only those with a Premium subscription can post Stories, at least for the time being.

It’s unclear when Telegram will bring this ability to free users. Meanwhile, if you’re willing to pay the company for this feature, the $4.99 per month subscription will give you a lot more. Telegram Premium offers larger file uploads (up to 4GB), faster downloads, transcriptions, up to 20 public t.me links, premium badges, custom app icons, an ad-free experience, and a host of other perks. You can click the button below to download the latest Telegram update.

DOWNLOAD TELEGRAM


[ad_2]
Source link

ChatGPT’s new feature will make using it so much better

0
[ad_1]

OpenAI, the company behind ChatGPT, is in the middle of a pretty big investigation. However, that doesn’t mean that the company can’t push new features to its brainchild. The company just announced new custom chat instructions for ChatGPT. This will make the process of using it much quicker.

When you start a new conversation in ChatGPT, you’re starting from a blank canvas. That’s not much of an issue if you’re using the chatbot for random reasons. However, if you rely on the chatbot for a specific reason, and that reason requires several conversations, it could be a bit tedious. Every time you start a conversation, you’ll need to re-explain to ChatGPT what it’s about.

But, OpenAI developed custom chat instructions for ChatGPT

OpenAI got feedback from customers in 22 countries, and it seems that starting conversations from blank slates is a pet peeve among users. So, the company is releasing a feature that will help alleviate this issue.

The feature is called Custom Instructions. When you enable this feature, you’ll be able to tell ChatGPT a little about yourself and what kind of content you’ll generate. Then, it will remember this information for future conversations. This way, even if you start a new conversation, the AI chatbot will already know what you’re talking about.

If you’re a third-grade teacher, and you constantly use ChatGPT to help with your lesson plans, you can tell it that from the get-go. ChatGPT will remember that, so if you create a new conversation, you don’t have to tell it that you’re a third-grade teacher. You can just start generating what you want.

This is a very useful tool for avid “ChatGPT-ers”. If, at any point, you want to disable this feature, you can simply switch off the toggle. It’ll go back to giving you blank canvases to work with.

For the time being, this feature is only available for Plus subscribers. OpenAI did state that it will bring this feature to standard users eventually.


[ad_2]
Source link

OnePlus launches Genshin Impact collab OnePlus 11

0
[ad_1]

OnePlus has come up with what some might think of as a pretty unlikely collaboration, a Genshin Impact OnePlus 11 limited edition box.

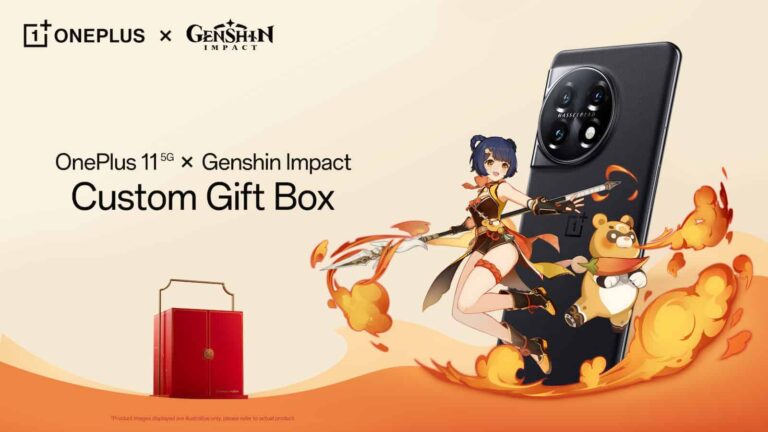
There’s two things to know about this collaboration product. One, the phone itself doesn’t have any Genshin Impact style designs or themes. It’s a standard OnePlus 11 phone and looks just like any other OnePlus 11. And two, it comes with a big collector’s box that’s meant to be put on display. The package also comes with some unique little, let’s call them gifts, based on Xiangling, who’s one of the game’s central characters and one that you can add to your party.

If you’re a Genshin Impact fan, this is actually a pretty neat product. While the phone itself doesn’t have any themed designs to it, the box and the accompanying goodies make up for that. The box itself is designed to evoke Xiangling’s passion for cooking. And if you’ve played through her story missions in the game you’ll know exactly what we’re talking about here. As for the goodies, the box comes with a handful of neat collectibles. There’s a collaboration book, Xiangling stickers, character cards, and a Stove God Gouba pin. This is all in addition to a 16GB RAM model of the OnePlus 11 in Titan Black.

There’s only 1,000 Genshin Impact OnePlus 11 boxes to be had

As is the case with most of these, there’s a limited amount of them available. That’s understandable. Given the nature of the collaboration and the likelihood that a ton of people would want them. All of that said, there’s only 1,000 of these being made which makes them fairly limited.

And if you want to get your hands on one, you can do so relatively soon. You can get them directly from OnePlus in the US and Canada for $799. US consumers will also be able to pick them up from Best Buy. The phone doesn’t go on sale until 10am PST though. Which means you still have time to get one if you’re seeing this post before then.

OnePlus 11 Genshin Gift Box


[ad_2]
Source link

The Twitter War You Don’t See

0
[ad_1]

Leakers — the growing cadre of folks who publish information and imagery about unreleased products prior to launch. They once enjoyed a relatively laissez-faire approach from the manufacturers they covered. Save for a so-called “nastygram” here and there (letter from a legal department).

However, as self-publication has become increasing frictionless thanks largely to the rise of social media. Alongside, ironically, the ubiquity of inexpensive, commoditized smartphones. Phone leakers, especially, have found themselves targeted more and more often. Primarily through the content takedown mechanism codified by 1998’s Digital Millennium Copyright Act. And while copyright holders have every right to protect their intellectual property if they so choose. Doing so is not without its risks. As some leakers have come to develop sizable followings among a given brand’s most strident fans.

Samsung’s zero-tolerance for leaks

Over the past three years, the smartphone industry’s largest manufacturer, Samsung, has adopted a zero-tolerance approach to product leaks in the lead up to its semi-annual Galaxy Unpacked launch events. Leakers big and small, experienced and fresh, can expect to be the recipient of a DMCA takedown request — enforced en masse by their publishing platform of choice — for almost any perceived infraction.

The forms are filled out directly by Samsung’s South Korean executives (despite the social networks’ mostly US origins) and target not only posts containing the material itself. But sometimes — as the DMCA allows — even ones merely linking to allegedly infringing content. This latter stipulation of the legislation is also what forces Google and its peers to remove some of their results.

Again, I’m not faulting the Samsungs of the world for trying to protect their intellectual property. What I am doing, however, is arguing that not only are the efforts wholly ineffective. Every Unpacked event over this crackdown period has seen an increasing volume of leaks. They ultimately prove to work against the companies’ best interests.

Samsung Galaxy Unpacked 2022 metaverse

Primarily, this is due to the slow but methodical change in tenor around companies like Samsung, of whom leakers almost always start out as fans, But towards whom they naturally direct their ire as post after post is taken down, sometimes with disastrous consequences. Just yesterday, up and coming leaker and prolific Samsung reporter @_SnoopyTech_ had his Twitter account disabled. Likely in response to Samsung having met whatever internal threshold of DMCA requests trigger that punitive action.

None of this happens in a vacuum. Just as gracious treatment such as pre-release review units, embargoed press material, and even junkets (sponsored travel) tend to endear writers and other content creators to their subjects. Softening the coverage and pre-empting surprise PR crises. A campaign of targeting the folks who cover your company by way of leaks, may very well have the opposite effect. That is introducing a negative bias that, while perhaps not explicit, nonetheless seeps into day-to-day coverage in a way that is readily perceived by readers, viewers, and followers. The end result may very well be a shift in the narrative about a given company and its products. And those can not only damage sales, but also become very difficult to change. Just take a look at Samsung’s mobile struggles of late for example.

Companies, then, for the sake of their bottom lines, are perhaps best served by ignoring the leaks. Rising above it all and concentrating on their core competencies and mandates. Which is making and marketing great products. If they do feel a pressing need to address leaks, the best place to start should be the low-hanging fruit where the majority of leakers get their material. In the case of Samsung, this tends to be its hundreds of creative and retail partners whose own policies and practices are not nearly as protective of third-party intellectual property as they could be. There’s a very good reason that Apple is able to keep its keynotes almost leak free vis a vis first-party imagery. While Samsung’s Unpacked can feel like a gusher of leaked content as the events draw closer.

Bottom line: what you think you need to do to protect your brand can sometimes be counterintuitive. And a strategy of realpolitik in the media realm is often the most effective. If not necessarily the most palatable at first glance.


[ad_2]
Source link

Deezer launches new automotive app for cars with Google built-in

0
[ad_1]

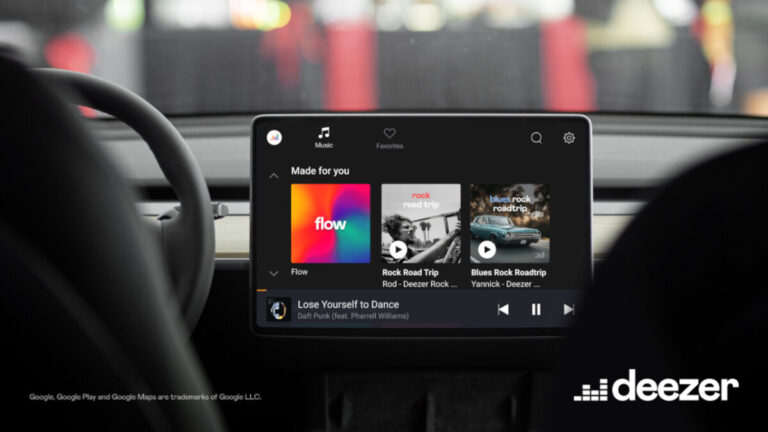
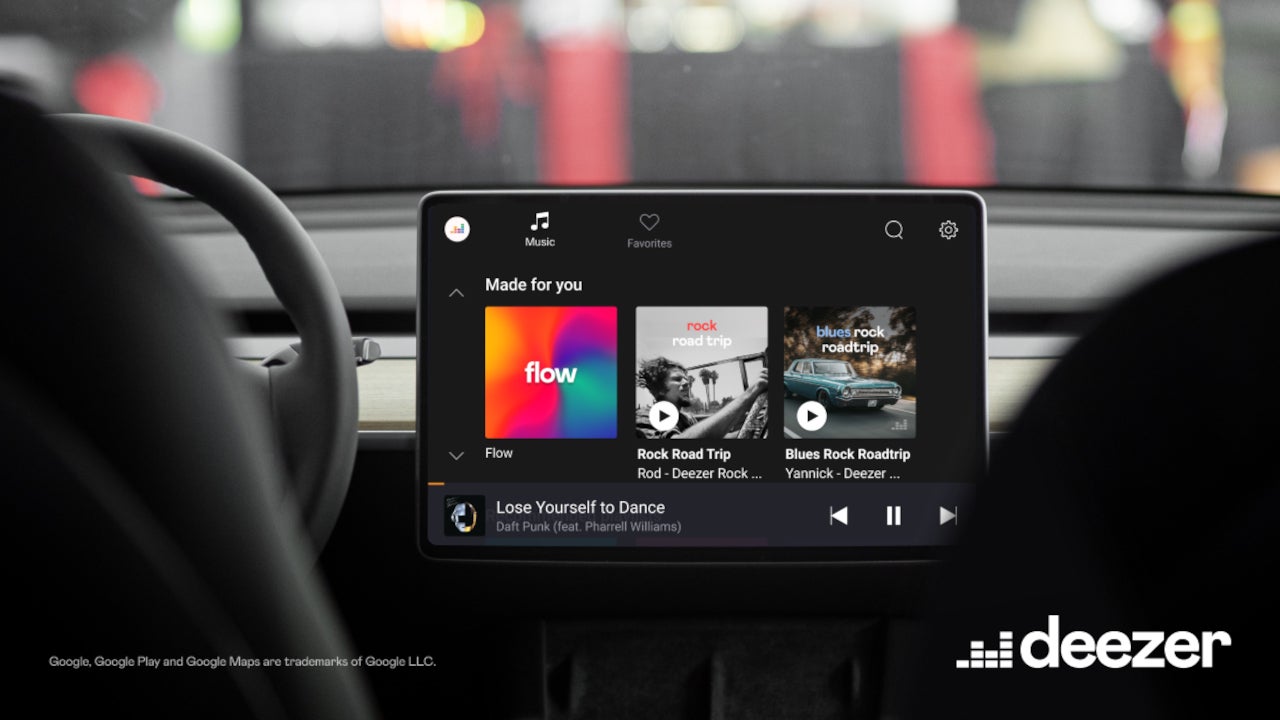
Deezer might not be among the top five most popular music streaming services in the United States, but it’s one of the few that has a dedicated automotive app available for those who drive cars with Google built-in. Earlier this week, the music streaming platform announced the launch of its new automotive app.As mentioned in the title, the app will be available in cars with Google built-in and cars with the automotive app store Faurecia Aptoide. The release of the new solution follows a growing demand for dedicated car apps with features and functionalities matching the experience of using a phone.

“Music has the power to enhance any situation, and listening to your top songs in the car is essential to people all over the world. It’s our pleasure to introduce our new automotive app, giving drivers seamless access to their favorite music on Deezer. With this launch, we’re excited to get on the road with some of the world’s finest car manufacturers,” said Nicolas Pinoteau, VP Product & Engineering, Deezer.

Deezer premium users will be able to enjoy their own playlists or a lineup of personalized AI-generated Flow of recommendations directly through the car and without using their phones. Voice control is also available for those using Deezer’s new automotive app in case they want to tune into the right playlist.

The app has been designed to provide simplicity over complicated menus, at least that’s what Deezer claims. The app offers access to an extensive catalog of more than 120 million songs, but keep in mind that you’ll need to pay $10.99 per month for Deezer Premium. A free 1-month trial is also available if you just want to try the music streaming service.

The free version of Deezer offers access to over 90 million songs, but it’s ad-supported. The free subscription plan doesn’t provide any perks in comparison with the other three (Premium, Student, Family) apart from personalized mixes and playlists.


[ad_2]
Source link

Google Outlines Common Red Team Attacks Targeting AI Systems

0
[ad_1]
Red Team Attacks Targeting AI Systems

There are rising concerns about the security risks associated with artificial intelligence (AI), which is becoming more and more popular and pervasive.

Google, a major participant in the creation of next-generation artificial intelligence (AI), has emphasized the need for caution while using AI.

In a recent blog post, Google announced its team of ethical hackers who are dedicated to ensuring the safety of AI. This marks the first time the company has publicly disclosed this information.

The company said that the Red Team was established approximately ten years ago. The team has already identified several risks to the rapidly developing field, mostly based on how adversaries could compromise the large language models (LLMs) that power generative AI systems like ChatGPT, Google Bard, and others.

Google researchers identified six specific attacks that can be built against real-world AI systems. They discovered that these common attack vectors exhibit a unique complexity.

In most cases, the attacks cause technology to produce unintended or even malicious impacts. The outcomes can range from harmless ones to more dangerous ones.

Types Of Red Team Attacks On AI Systems

  • Prompt attacks
  • Training data extraction
  • Backdooring the model
  • Adversarial examples
  • Data poisoning
  • Exfiltration
Types of Red Team Attacks on AI Systems \\ Source : Google

The first kind of frequent assaults that Google was able to identify is prompt attacks, which utilize “prompt engineering.” It relates to creating effective prompts that provide LLMs with the instructions required to carry out specific tasks.

According to the researchers, when this effect on the model is malicious, it can in turn deliberately influence the output of an LLM-based app in ways that are not intended.

Researchers also discovered an attack known as training-data extraction, which seeks to recreate exact training instances used by an LLM, such as the Internet’s content.

“Attackers are incentivized to target personalized models or models that were trained on data containing PII, to gather sensitive information,” researchers said.

Attackers can harvest passwords or other personally identifying information (PII) from the data in this way.

Backdooring the model, often known as a backdoor, is a third possible AI attack where an attacker may try to secretly modify the behavior of a model to give inaccurate outputs with a specified ‘trigger’ phrase or feature.

In this kind of attack, a threat actor can conceal code to carry out harmful actions either in the model or in its output.

Adversarial examples, a fourth attack type, are inputs that an attacker gives to a model to produce a “deterministic, but highly unexpected output”. The picture may, for instance, appear to the human eye to depict a dog while the model sees a cat.

“The impact of an attacker successfully generating adversarial examples can range from negligible to critical and depends entirely on the use case of the AI classifier,” researchers said.

If software developers are using AI to assist them in developing software, an attacker could also use a data-poisoning attack to manipulate the model’s training data to influence the model’s output in the attacker’s preferred direction.

This could endanger the security of the software supply chain. The researchers emphasized that the effects of this assault may be comparable to those of backdooring the model.

Finally, Exfiltration attacks, in which attackers can transfer the file representation of a model to steal critical intellectual property housed in it, are the last form of attack recognized by Google’s specialized AI red team.

They can utilize that data to create their models, which they can exploit to offer attackers special powers in custom-crafted assaults.

Recommendation

Traditional security measures like making sure the models and systems are securely locked down may greatly reduce danger.

The researchers advise businesses to use red teaming in their work processes to support product creation and research efforts.


[ad_2]
Source link

Samsung 65-inch S90C 4K TV Now $2,097 at Amazon

0
[ad_1]

Amazon has a great price on the Samsung 65-inch S90C OLED 4K TV right now. Where you can pick it up for $2,097. That’s going to save you $500 off of its regular price, and does bring it back down to an all-time low.

Samsung S90C OLED 4K TV – Amazon

Why you should buy the Samsung S90C OLED

The Samsung 65-inch S90C 4K TV is a top-of-the-line OLED TV that offers stunning picture quality, immersive sound, and a wide range of features. It is currently on sale for $2,097, which is a great deal for a TV of this caliber.

One of the best things about the S90C is its OLED panel. OLED panels offer perfect blacks and infinite contrast, which results in images that are simply breathtaking. The S90C also features Samsung’s Quantum HDR technology, which delivers a wider range of colors and contrast for even more realistic images.

In addition to its stunning picture quality, the S90C also offers excellent sound. It is equipped with a 4.2.2-channel speaker system that delivers rich, immersive sound. The S90C also supports Dolby Atmos, which creates a truly three-dimensional sound experience.

The S90C is also packed with features. It is a smart TV, so you can access your favorite streaming apps, such as Netflix, Amazon Prime Video, and Disney+. It also has built-in voice control, so you can control the TV with your voice.

Overall, the Samsung 65-inch S90C 4K TV is an excellent choice for anyone who wants the best possible home entertainment experience. It offers stunning picture quality, immersive sound, and a wide range of features. If you are looking for a new TV, the S90C is definitely worth considering.

Here are some additional benefits of OLED TVs:

  • Wide viewing angles: OLED TVs offer excellent viewing angles, so you can enjoy the same great picture quality no matter where you are sitting in the room.
  • Fast response time: OLED TVs have a very fast response time, which means that they can display fast-moving images without any blur or ghosting. This makes them ideal for gaming and watching sports.
  • Durability: OLED TVs are very durable and can withstand a lot of wear and tear. They are also less likely to burn in than other types of TVs.

If you are looking for a TV that offers the best possible picture quality, then an OLED TV is the way to go. The Samsung 65-inch S90C 4K TV is a great option, and it is currently on sale for a great price.

Samsung S90C OLED 4K TV – Amazon


[ad_2]
Source link

Top AI brands promise White House to develop AI responsibly

0
[ad_1]

Right now, we’re at the beginning of a new age of technology with artificial intelligence. This new age brings with it visions of hope and prophecies of doom. Thus, The US White House asked top AI brands to promise to develop AI responsibly.

Right now, all of the dangers of AI are still hypothetical. The thought of millions of writers, musicians, artists, executives, and developers being jobless because of AI automation is still just a thought. However, the government is trying to stave off that reality. The government is looking into OpenAI over how it uses and obtains data for ChatGPT. Also, Senator Casey introduced new bills to stop “Robot bosses” from happening.

Top AI brands promise to develop AI responsibly

According to The Verge, The White House will bring in Google, Meta, OpenAI, Amazon, Inflection, Anthropic, and Microsoft on Friday. During the meeting, the White House will issue a series of requests for these companies to follow. They include but aren’t limited to, developing a watermarking system, investing in cybersecurity, and discrimination research.

These address some of the issues with AI at this point. People generate all sorts of content and pass it off as though someone with actual talent made them. It’d be nice to have a watermarking system to know when something has been AI-generated.

Also, AI isn’t exactly clean from generating discriminatory content. That could lead to massive trouble on the corporate level. When it comes to cybersecurity, it’s obvious why that’s important. We don’t know how these companies are handling the data that they collect.

These are promises, not policies

While the companies agreed to meet with the White House, these are voluntary promises that the companies are making. This means that they’re not technically obligated to stick to them. There won’t be any punishment if they fail to live up to the promises.

Not to be cynical, but some of these companies struggle to obey certain guidelines even when they’re legally obligated to. It’s hard to believe that these companies will avoid breaking promises that seem to have no more weight than a pinky swear.

In any case, let’s just hope that these companies do stand by these promises. We’re just now realizing some of the dangers of AI.


[ad_2]
Source link