Last Chance to Reserve your Next Galaxy and Save $50!

0
[ad_1]

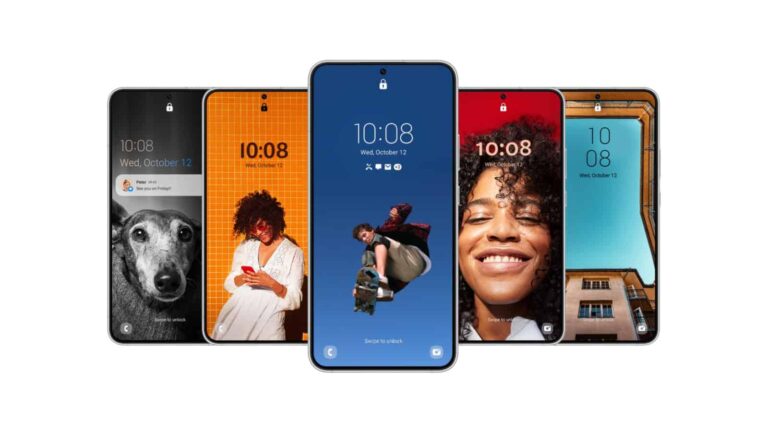
Samsung’s Galaxy Unpacked is taking place July 26, live from Seoul, South Korea. At this event, Samsung is likely to announce a number of new devices, as they typically do. And ahead of Unpacked, you can actually reserve your new Galaxy, and save $50!

All you need to do is head to this website here. You’ll be asked for your name and email (phone number is optional). And that’s it. This is a no commitment offer from Samsung. So whether you decide to buy or not to buy later on, that’s all up to you. But if you’re on the fence about getting one of the new devices from Samsung after Unpacked, it’s a good idea to take advantage of this.

You can enter your email and name on Galaxy Reserve up until 6:59AM ET on July 26. So there’s not much time left.

Galaxy Reserve – Samsung.com

What is Samsung announcing at Unpacked?

This is Samsung’s Fall Unpacked event, which is typically where they announce their new foldables, tablets and wearables. So what we’re expecting to see this time around is the Galaxy Z Fold 5, Galaxy Z Flip 5, Galaxy Watch 6 and Watch 6 Classic, as well as the Galaxy Tab S9 series. So there’s a boat load of devices coming out next week.

Now, since Samsung is holding this event in South Korea for the first time, their home, some of us are expecting something else to be announced at the event. Maybe Samsung will finally announce the Galaxy Home that they debuted way back in 2019 at this very same event? Maybe we could see some sort of VR or AR headset? Or maybe something else. We’ll have to wait until July 26 to know for certain.

Since Unpacked is taking place in Seoul this year, that means the event is starting earlier than ever. Unpacked will be starting at 7AM ET or 4AM PT for those on the West Coast. But you can also watch it here.


[ad_2]
Source link

Sen. Casey introduces new AI bills to protect workers from “robot bosses”

0
[ad_1]

Artificial Intelligence has quickly found its way into a lot of industries in recent months, and this has had the government worried about workers’ rights and protections. Now, in a recent development, Senator Bob Casey, D-Pa, has introduced two new bills aimed at safeguarding workers from workplace surveillance and AI-powered “robot bosses.”

The first bill, titled the “No Robot Bosses Act,” seeks to establish clear guidelines for employing automated systems, such as algorithms and machine learning tools, in employment-related decision-making. Additionally, the proposed legislation will also encourage employers to provide proper training to their workforce on the use of these systems and mandate transparency in their implementation. Moreover, to address concerns about AI going rogue, the bill would require companies to maintain human oversight of all AI decisions.

The second bill, known as the “Exploitative Workplace Surveillance and Technologies Task Force Act,” aims to create a separate government body responsible for examining workplace surveillance practices. Chaired by a representative from the Department of Labor, the body will include individuals from various government domains to assess the impact of workplace surveillance and automated decision systems on employee salaries, scheduling, organizing efforts, and marginalized populations in the workforce.

Reasoning behind the new bills

Senator Bob Casey stated that the primary rationale behind these bills is to limit the impact of AI and prevent the unchecked authority of “robot bosses” from making critical decisions that affect human lives and livelihoods. Additionally, Casey argues that without proper oversight, there is a risk of discriminatory practices, unfair disciplinary actions, and even unsafe working conditions. Although these scenarios may seem far-fetched today, given the rapid pace of AI development, they could become a reality in the near future.

“Systems and software, not humans, are increasingly making decisions on whom to interview for a job, where and when employees should work, and who gets promoted, disciplined, or even fired from their job,” a summary of the bill from Casey’s office explains.

Furthermore, the bill has not only garnered widespread support from fellow Democratic senators, such as Brian Schatz of Hawaii, John Fetterman of Pennsylvania, Bernie Sanders of Vermont, and Cory Booker of New Jersey but also from major labor unions, including AFL-CIO and the Communications Workers of America, as well as organizations like the National Employment Law Project.


[ad_2]
Source link

You’ve got two weeks to patch Citrix NetScaler vulnerability CVE-2023-3519

0
[ad_1]

A critical unauthenticated remote code execution vulnerability in Citrix NetScaler ADC and Citrix NetScaler Gateway is being actively exploited

The Cybersecurity and Infrastructure Security Agency (CISA) has added a critical unauthenticated remote code execution (RCE) vulnerability in Citrix NetScaler ADC and Citrix NetScaler Gateway to its Known Exploited Vulnerabilities Catalog, based on evidence of active exploitation. This means that Federal Civilian Executive Branch (FCEB) agencies need to remediate this vulnerability by August 9, 2023 to protect their networks against active threats. We urge everyone else to take it seriously too.

The recommended actions are to apply mitigations per vendor instructions or discontinue use of the product if mitigations are unavailable. Given the active exploitation, we would advise to do this as soon as possible.

The Common Vulnerabilities and Exposures (CVE) database lists publicly disclosed computer security flaws. The actively exploited CVE patched in this update is CVE-2023-3519 a Citrix NetScaler ADC and NetScaler Gateway code injection vulnerability with a CVSS score of 9.8 out of 10. The vulnerability can lead to unauthenticated RCE. It affects appliances configured as a Gateway (VPN virtual server, ICA Proxy, CVPN, RDP Proxy) or as an authentication, authorization and accounting (AAA) virtual server.

Little information has been made available about the campaign that is exploiting this vulnerability. What we do know is that the criminals use web shells—a script that can be used by an attacker to run remote commands and maintain persistent access on an already compromised system. CISA has released a cybersecurity advisory about the tactics, techniques, and procedures (TTPs) of the currently active campaign.

Reportedly, there are around 38,000 Citrix Gateway appliances exposed to the public Internet and exploits against Citrix ADC have been discussed, including the sale of a Remote Code Execution (RCE) exploit, on a cybercrime forum.

Citrix acknowledges the urgency by stating:

“Exploits of CVE-2023-3519 on unmitigated appliances have been observed. Cloud Software Group strongly urges affected customers of NetScaler ADC and NetScaler Gateway to install the relevant updated versions as soon as possible.”

The security bulletin by Citrix about this vulnerability includes two more vulnerabilities. The following supported versions of NetScaler ADC and NetScaler Gateway are affected by the vulnerabilities:

  • NetScaler ADC and NetScaler Gateway 13.1 before 13.1-49.13
  • NetScaler ADC and NetScaler Gateway 13.0 before 13.0-91.13
  • NetScaler ADC 13.1-FIPS before 13.1-37.159
  • NetScaler ADC 12.1-FIPS before 12.1-55.297
  • NetScaler ADC 12.1-NDcPP before 12.1-55.297

Citrix notes that NetScaler ADC and NetScaler Gateway version 12.1 have reached the end-of-life stage and customers should upgrade to a newer variant of the product.

Customers using Citrix-managed cloud services or Citrix-managed Adaptive Authentication do not need to take any action.

Malwarebytes blocks the IP addresses that are known indicators of compromise (IoCs) for the active campaign exploiting this vulnerability.

Malwarebytes blocks 216.41.162.172

216.41.162.172

Malwarebytes blocks 216.51.171.17

216.51.171.17

For administrators that would like to see whether their instance has been compromised and what they should do about it, I found this checklist.


We don’t just report on vulnerabilities—we identify them, and prioritize action.

Cybersecurity risks should never spread beyond a headline. Keep vulnerabilities in tow by using Malwarebytes Vulnerability and Patch Management.


[ad_2]
Source link

Samsung nears public release of the One UI 5.1.1 update

0
[ad_1]

Samsung is getting closer to the One UI 5.1.1 stable update. The company recently updated its Good Guardians app to add support for the new, unreleased One UI version. It is already running One UI 5.1.1 public beta programs for the Galaxy Z Fold 4 and Galaxy Tab S8 series.

Good Guardians, which was formerly known as Galaxy Labs, is a first-party Samsung app that gives Galaxy users access to various system management tools. It offers a battery tracker where you get detailed battery stats, tips to extend the battery life, an app performance booster, a temperature monitor, a memory utility, a media file manager, and more.

Samsung recently updated the app to version 4.5.06, but seemingly with no notable changes. The update is rolling out through the Galaxy Store, with the changelog containing just one line: support for One UI 5.1.1 (via SamMobile). This makes Good Guardians usable for Galaxy users testing the new One UI version. But more importantly, it’s an indication of a nearing public release of the update.

Good Guardians isn’t the first Samsung app that has received One UI 5.1.1 support. The company previously updated the Nice Catch app, which is a Good Lock module, as well. A few others may have gone under the radar, or without the changelog mentioning One UI 5.1.1. All in all, the Korean behemoth looks buckled up to roll out the new One UI version to compatible Galaxy devices soon.

Speaking of compatible devices, One UI 5.1.1 should be available to all recent foldables and flagship Galaxy tablets. Since the Galaxy Z Fold 4 and Galaxy Tab S8 series already have beta programs, they should be first in the pipeline. Samsung may also push it to recent Galaxy S series phones. A few features may trickle down to select Galaxy A models as well. We will let you know when we have more information.

Upcoming Samsung foldables and tablets should ship with One UI 5.1.1

Samsung is preparing to host a major launch event next week. The Galaxy Unpacked in Seoul, South Korea, on July 26 will bring several new products. The company has readied the Galaxy Z Fold 5 and Galaxy Z Flip 5 foldables, Galaxy Tab S9 series tablets, and Galaxy Watch 6 series smartwatches. If history is any indication, the new foldables and tablets should run One UI 5.1.1 out of the box. The new watches should ship with One UI 5 Watch based on Wear OS 4. Stay tuned for the big event next Wednesday.


[ad_2]
Source link

US Army is set to test the new Microsoft HoloLens 1.2 goggles next month

0
[ad_1]

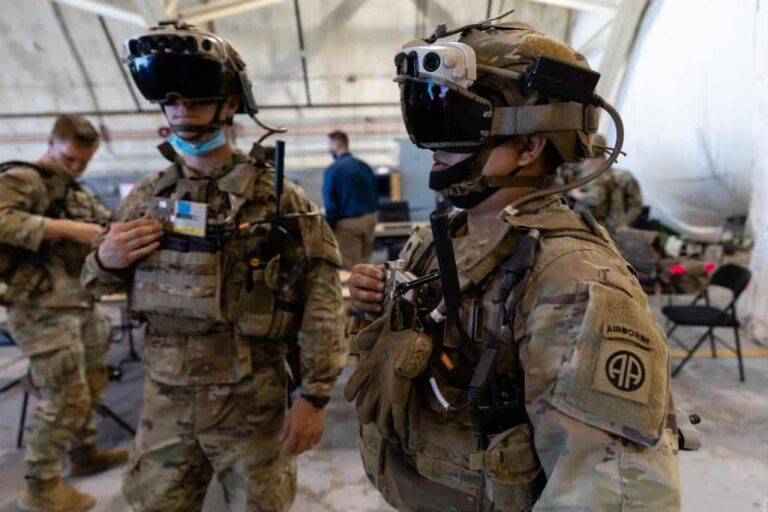
Microsoft’s first attempt at creating the HoloLens-based IVAS (Integrated Visual Augmentation System) goggles for the Army was disappointing, as many soldiers experienced nausea and other issues. Now, in a recent development, Microsoft is expected to deliver the new HoloLens IVAS 1.2 devices to the Army by the end of this month.

While the specific changes remain unclear, the headset will reportedly offer a slimmer, lighter, and more balanced design while also addressing the previous concerns with nausea. Scheduled for late August, the testing will involve two squads using 20 prototype IVAS goggles and evaluating their functionality under low-light conditions, overall reliability, and potential side effects such as nausea, headaches, and eye strain.

Why is IVAS important?

According to Master Sgt. Marc Krugh, the Microsoft HoloLens IVAS goggles are a significant development for the Army, as they enable soldiers to rehearse and train in more realistic scenarios using augmented reality, better preparing them for actual combat situations. Moreover, in battle scenarios, the goggles’ advanced night vision capabilities offer a discreet way for troops to coordinate attacks and remain vigilant for signs of injury.

Although HoloLens could become a significant asset for the military, previous versions of the goggles encountered issues that led Congress to halt further orders in January. As a result, Microsoft received $40 million to rework the hardware and address the identified problems.

Therefore, if the tests are successful, the Army might consider awarding a contract for a second field study between July and September 2024, potentially leading to an operational combat test as early as April 2025. Once the testing phase is complete, the Army plans to deploy more than 121,000 IVAS units over the next ten years.

However, failing to meet the Army’s expectations once again could result in the cancellation of the program, which would be a significant loss for Microsoft and raise doubts about the reliability of HoloLens technology.


[ad_2]
Source link

Estée Lauder targeted by Cl0p and BlackCat ransomware groups

0
[ad_1]

We take a look at reports of cosmetics firm Estée Lauder being attacked by the Cl0p and BlackCat ransomware groups.

Estée Lauder is currently at the heart of a compromise storm, revealing a major security issue via a Security Exchange Commission (SEC) filing on Tuesday.

Although no detailed explanation of what has taken place is given, there is confirmation that an attack allowed access to some systems and involved potential data exfiltration. Meanwhile, two ransomware groups are taking credit for compromises unrelated to one another. Is one of the compromises the attack mentioned in the filing? It’s worth mentioning here that Estée Lauder does not name either ransomware group. With this in mind, the relevant section from the filing reads as follows:

The Estée Lauder Companies Inc. (NYSE: EL) has identified a cybersecurity incident, which involves an unauthorized third party that has gained access to some of the Company’s systems.  After becoming aware of the incident, the Company proactively took down some of its systems and promptly began an investigation with the assistance of leading third-party cybersecurity experts. The Company is also coordinating with law enforcement.  Based on the current status of the investigation, the Company believes the unauthorized party obtained some data from its systems, and the Company is working to understand the nature and scope of that data.

The Company is implementing measures to secure its business operations and will continue taking additional steps as appropriate. During this ongoing incident, the Company is focused on remediation, including efforts to restore impacted systems and services. The incident has caused, and is expected to continue to cause, disruption to parts of the Company’s business operations.

Bleeping Computer notes that the ALPHV/BlackCat and Cl0p groups are claiming responsibility for the two unrelated ransomware compromises specifically. Worse, both ransomware groups have what they claim to be Estée Lauder data up for grabs on their leak portals.

If you’re unfamiliar with such sites, they’re places where ransomware groups store stolen data. The compromised organisation is then threatened with the data being made public, traded, or sold off to the highest bidder unless a ransom is paid. This is a common tactic in so-called “double extortion” ransomware, where the encrypting of devices is merely the first step to extracting money.

The Cl0p group claims to have somewhere in the region of 131GB of data to hand. Meanwhile BlackCat is complaining of the lack of communication from Estée Lauder, sending multiple emails but receiving no replies. It also claims to still have network access despite various attempts to secure the network.

Supposedly, the information taken could “impact customers, employees, and suppliers”. There are no further details on the contents at this time. Regular readers will know that these attacks typically target confidential information, company secrets, personal data, payroll, and identity scans. The attackers could be bluffing, or it really could be as bad as they claim. We’ll have to wait and see.

The Cl0p compromise is said to have made use of a MOVEit Transfer vulnerability to gain access to the target systems. Both Cl0p and BlackCat tend to feature heavily in our ransomware review posts. In our June post, Cl0p was the most active group around with BlackCat falling suspiciously quiet. Perhaps it was focusing on heavy-hitter attacks such as this the whole time.

How to avoid ransomware

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; disable or harden remote access like RDP and VPNs; use endpoint security software that can detect exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like Malwarebytes EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.

Malwarebytes EDR and MDR removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW

[ad_2]
Source link

Galaxy Tab Active 4 Pro bags Samsung’s July update globally

0
[ad_1]

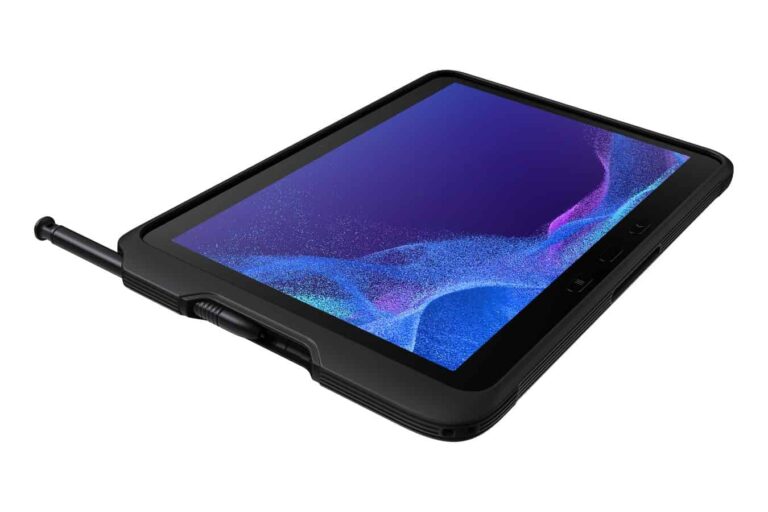
The Galaxy Tab Active 4 Pro is the latest Samsung device to receive the July 2023 Android security patch. The rugged tablet is picking up this month’s security update widely around the world. The Korean firm has already pushed the new SMR (Security Maintenance Release) to dozens of other Galaxy devices.

First reportedly by SamMobile, the July SMR is available for both Wi-Fi and cellular (5G) variants of the Galaxy Tab Active 4 Pro. The Wi-Fi model (SM-T630) is receiving the update in Europe and the USA with the firmware build number T630XXS3BWG2, the publication confirms. The device doesn’t seem to be getting additional goodies. Samsung is only pushing the latest security fixes to the tablet.

For users with a 5G-enabled Galaxy Tab Active 4 Pro, the July update comes with varying build numbers depending on the market. The South Korean version of the tablet (SM-T636N) sees its firmware version bumped to T636NKOS3BWG1 with this release. In Europe (SM-T636B), it’s T636BXXS3BWG2. Finally, users in Latin America (SM-T636B) are getting the July SMR with the firmware build number T636BXXS2BWF2.

Like the Wi-Fi variant, the Galaxy Tab Active 4 Pro 5G also doesn’t get anything apart from the latest security fixes with this update. Samsung has already confirmed that the July SMR for Galaxy devices contains 90 patches. This is a combined total of Android OS patches coming from Google and Galaxy patches coming directly from the Korean firm. At least three security flaws patched this month were critical issues.

If you’re using the Galaxy Tab Active 4 Pro and have yet to receive the July update from Samsung, your wait should end soon. Be on the lookout for a notification in the coming days. It will prompt you to download the OTA (over the air) update. You can also manually check for updates from the Settings app on your rugged Samsung tablet. Navigate to Settings > Software update and tap on Download and install.

The Galaxy Tab Active 4 Pro will get Android 14

Samsung launched the Galaxy Tab Active 4 Pro in August 2022. The device came running Android 12 out of the box. It has since picked up Android 13 as well. And the tablet is also eligible for Android 14. The Korean firm is expected to launch Android 14 beta programs later this month, with the stable update likely arriving in October. The Galaxy Tab Active 4 Pro may get the big update in late 2023 or in 2024. Stay tuned for more information about Samsung’s Android 14 plans.


[ad_2]
Source link

Samsung is developing a foldable display technology for Apple

0
[ad_1]

According to Sammobile, Samsung has somehow confirmed that it’s working on a foldable display technology intended for Apple products.

When it comes to rivalry in the smartphone market, Apple and Samsung are the first names that come to mind. The American giant and the Korean OEM have been tough rivals in the market. But it’s no surprise to know that Samsung produces over 70% of the OLED panels used in the iPhone 14 series. The partnership between Apple and Samsung might now expand to foldable displays.

The information comes from an image taken at the SID Review Workshop in Seoul. The image shows Samsung Display is developing a large foldable screen for Apple. However, this foldable panel might be used on a laptop instead of a smartphone. So maybe it’s not far-fetched to picture the next generations of MacBook with a foldable display.

Samsung SID Review Workshop foldable panels

Samsung is working on a foldable display for Apple

The Korean OEM is doing its best to meet Apple standards for a foldable display. The slide in the SID Review event suggests that the new foldable technology will bring more durability to the screens, making them impact-proof to increase their resistance. The lack of confidence in foldable displays is maybe one of the reasons that Apple has not yet launched a foldable iPhone.

A Samsung executive noted that it’s “necessary” for Apple to commercialize a foldable product. Which could lead to the success of the whole market. It remains to be seen if Samsung’s next-generation foldable display will be used in a MacBook or iPhone. However, foldable devices are the latest trends in the market, and all reports confirm Apple’s desire to launch a foldable device.

Of course, Samsung has already revealed the inclination among laptop manufacturers to launch a “full display” foldable product. Given that Samsung is one of Apple’s biggest display suppliers, it may be giving clues about a foldable MacBook. We should probably wait until Apple approves the durability of foldable displays made by third-party manufacturers.


[ad_2]
Source link

T-Mobile will now charge you $5 to pay your bill in stores

0
[ad_1]

T-Mobile in-store bill payments are about to cost you. Not in any sort of figurative way either. They will quite literally cost you more money out of your pocket. This week T-Mobile announced it would be charging people more money (a $5 fee) if they wanted to make in-store bill payments.

That seems like an odd thing to do to customers who just want to hand over their money for services rendered, doesn’t it? Well, maybe. But not if you think about the potential reasons behind it. Sure, T-Mobile is a wireless service company. It charges you a monthly fee for that service and you need to pay that fee somehow, and the people who work in T-Mobile stores can certainly process in-store payments. They’ve been trained to do so, and have been completing that task for many years.

Here’s the thing. T-Mobile store employees are also sales reps. Where T-Mobile’s main job is to provide you with cell service, a T-Mobile store employee’s main job is to sell you things. Whether that’s new lines of service, phone upgrades, accessories or what have you. And if they’re tied up with a customer processing a bill payment, that means they aren’t actively selling. Especially if the bill processing request takes a long time. As some of them can. So T-Mobile’s answer to this is charging a $5 fee to customers who still prefer to walk into a store and pay their bill in person. In hopes they won’t want to come to the store unless it’s to buy stuff.

T-Mobile is hoping to curb in-store bill payments

It’s an interesting strategy that the company no doubt hopes will help boost sales for reps across the board. And thereby the company itself. A win-win for both sides of the company. But what about the customer? Well there are still ways to pay the bill without paying the $5 fee.

You just won’t be able to do that in stores anymore. The obvious answer (or at least it should be) is to set up autopay. Not only does this relieve you of having to actively complete the bill payment, but T-Mobile will even take money off your bill if you set it up.

Your other options, as Droid Life points out, are to pay the bill online in your T-Mobile account, or to pay in the T-Mobile app on your phone. All three methods work, and you don’t have to go anywhere. Plus, you aren’t stuck with an extra $5 charge.


[ad_2]
Source link

ChatGPT will soon have an official Android version available

0
[ad_1]

ChatGPT is getting an official Android app, and you’ll be able to use it on your phone sooner than you think. Makers of ChatGPT OpenAI just finished announcing some new features for the AI tool and it’s now announcing that Android users will be able to access it through an app on their mobile devices.

Making it kind of a big week for the company. OpenAI says the app will begin rolling out to users next week. But there’s no set day for arrival just yet. For eager fans of the tool, maybe you’ll get lucky and it’ll land sooner rather than later.

After all the iPhone app is already available and iOS users have been enjoying it for free since earlier this year.

You can pre-register for the ChatGPT Android app right now

While you wait for the app to arrive, you can pre-register for it over on the Google Play Store. And most users should know by now that if you pre-register, you’ll get a notification when the app is available to install.

Of course none of that will matter if you don’t pay attention to your notifications. The ChatGPT Android app will be free just like the iOS version and it’ll sync your history across devices, OpenAI says. More importantly though, you won’t have to use the website in your mobile browser. Which wasn’t exactly a user-friendly experience. OpenAI also confirms that the app will feature the company’s newest model improvements. So whatever you can already use on the website, you’ll be able to use in the app. At least judging by OpenAI’s statement.

For OpenAI and ChatGPT fans, this app’s impending release is good news. Especially since Google doesn’t have an Android app available for Bard. This gives OpenAI a chance to potentially gain some new users if they’d prefer to use an app for this kind of thing on the go.


[ad_2]
Source link