Malwarebytes Premium stops 100% of malware during AV Lab test

0
[ad_1]

Malwarebytes Premium has maintained its long-running, perfect record in protecting users against online threats by blocking 100% of the malware samples deployed in the AV Lab Cybersecurity Foundation’s “Advanced In-The-Wild Malware Test.”

For its performance in the May 2024 evaluation, Malwarebytes Premium also received a certificate of “Excellence.”

According to AV Lab, such certificates “are granted to solutions that are characterized by a high level of security, with a rating of at least 99% of blocked threats in the Advanced In-The-Wild Malware Test.”

Every two months, the cybersecurity and information security experts at AV Lab construct a series of tests to compare cybersecurity vendors against the latest malware that is currently being used by adversaries and threat actors.

For the May evaluation, AV Lab tested 521 unique malware samples against 13 cybersecurity products. Malwarebytes Premium Security detected 521/521 malware samples, with a remediation time of 44 seconds—well below the 52-second average determined by AV Lab in its most recent testing.

Three cybersecurity vendors failed to block 100% of malware tested: ESET, F-Secure, and Panda.

To ensure that AV Lab’s evaluations reflect current cyberthreats, each round of testing follows three steps:

  1. Collecting and verifying in-the-wild malware: AVLab regularly collects malware samples from malicious and active URLs, testing the malware samples to understand their impact to networks and endpoints.
  1. Simulating a real-world scenario in testing: To recreate how a real-life cyberattack would occur, AVLab uses the Firefox web browser to engage with the known, malicious URLs collected in the step prior. In the most recent test, AVLab emphasized the potential for these URLs to be sent over instant messaging platforms, including Discord and Telegram.
  1. Incident recovery time assessment: With the various cybersecurity products installed, AVLab measures whether the evaluated product detects a malware sample, when it detects a sample, and how long it took to detect that sample. The last metric is referred to as “Remediation Time.”

Malwarebytes is proud to once again achieve a 100% score with AVLab’s Advanced In-The-Wild Malware Test, a trusted resource that proves our commitment to user safety.


[ad_2]
Source link

Moto G85 launches under the shadow of Motorola’s new foldables

0
[ad_1]

Motorola announced two new flip phones, but that’s not all. A budget phone arrived with them too, the Motorola Moto G85. The thing is, this phone did not launch in the US with the Motorola Razr+ 2024 and Razr 2024.

The Motorola Moto G85 is now official in both Europe and China

The Moto G85 launched in Europe and China. It’s called the Moto S50 Neo in China, actually. This is a budget smartphone, and chances are it won’t be making its way to the US… but it remains to be seen.

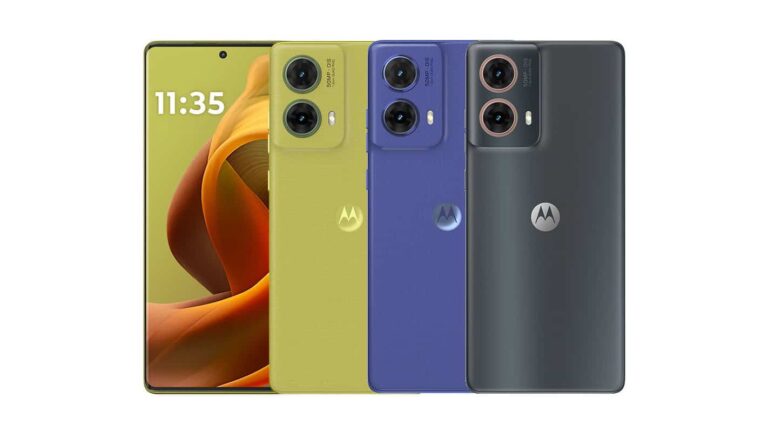
The Moto G85 does look really nice, however. It has a curved display with thin bezels and a centered display camera hole. Two vertically-aligned cameras are included on the back. They are located in the top-left corner, and that camera island does blend really well with the rest of the phone’s back.

This smartphone includes a 6.7-inch fullHD+ (2400 x 1080) pOLED display. That is a 10-bit display with a 120Hz refresh rate and a 360Hz touch sampling rate. It offers up to 1,600 nits of brightness.

Motorola Moto G85 image 3

Qualcomm’s mid-range chip fuels the device

The Snapdragon 6s Gen 3 fuels this phone, Qualcomm’s 6nm chip. Motorola included 12GB of RAM here, and 512GB of internal storage. In China, more RAM and storage options are available. Do note that the storage is also expandable.

A 5,000mAh battery sits inside the device, and 30W fast charging is supported. Android 14 comes pre-installed, with Motorola’s skin, while there are two nano SIM card slots included and a separate microSD card slot.

A 50-megapixel main camera (Sony’s IMX882 sensor, f/1.8 aperture, OIS) sits on the back, along with an 8-megapixel ultrawide unit (f/2.2 aperture, macro, depth camera). A single 32-megapixel unit (f/2.45 aperture) sits on the front.

It is water resistant, and has an in-display fingerprint scanner

The phone does include a set of stereo speakers, and Dolby Atmos is also supported. Two microphones are included on the phone, while the device is IP54 rated for water resistance. Bluetooth 5.1 is also supported, while the phone has an in-display fingerprint scanner too.

The Moto G85 measures 161.91 x 74.06 x 7.59mm, while it weighs 171 grams. There’s vegan leather on its back, by the way, but one additional variant will be available too, probably with glass on the back, we’re still not sure.

Motorola Moto G85 image 2


[ad_2]
Source link

Medusa Android banking trojan returns to the US with new capabilities

0
[ad_1]

After nearly a year of lying low, the Medusa banking trojan for Android has resurfaced on security researchers’ radar. Cybersecurity firm Cleafy Threat Intelligence recently detected fresh campaigns targeting users in Europe and North America, including the US. The attackers have deployed more compact variants of the malware, allowing them to operate more stealthily.

New Medusa banking trojan campaigns pose grave threats to Android users

Medusa, aka TangleBot, is an Android banking trojan operating as a malware-as-a-service (MaaS). Discovered in 2020, the malware provides attackers with powerful tools to remotely initiate unauthorized financial transactions from infected phones. It boasts features such as keylogging—it can track key presses when you type, allowing threat actors to steal logging credentials. The malware can also control the screen and manipulate text messages.

The latest Medusa Android banking trojan campaigns began in May 2024, or at least that is when Cleafy researchers started tracking the new activities. This is the first activity of the trojan since July 2023, the cybersecurity firm reports. As pointed out by Bleeping Computer, the banking trojan is different from “the ransomware gang and the Mirai-based botnet for distributed denial-of-service (DDoS) attacks” of the same name (Medusa).

According to Cleafy, the new campaigns deploy upgraded variants of the banking trojan. These variants are more compact and require fewer permissions to perform the same malicious activities on an infected Android phone. They also boast new features such as full-screen overlaying and screenshot capturing, which make the trojan more powerful than ever. It can initiate fraudulent transactions directly from the device without the user’s knowledge.

Clefy discovered the activities of the Medusa banking trojan in Canada, France, Italy, Spain, Turkey, the UK, and the US. The criminal minds behind the campaigns rely on smishing (SMS phishing) to trick Android users into side-loading the malware. They distributed the malware through dropper apps, with the security firm identifying 24 campaigns delivering malicious apps via five separate botnets (UNKN, AFETZEDE, ANAKONDA, PEMBE, and TONY).

Dropper apps include a fake Chrome browser

Among the dropper apps used in these Medusa banking trojan campaigns are a fake Chrome browser and a fake streaming app called 4K Sports. The latter appears to be a well-planned bait as the UEFA EURO 2024 football/soccer championship is currently underway in Europe. Unsuspecting users would install it hoping to watch the championship live on their phone, only to potentially fall prey to devastating malware attacks that could wipe out their bank accounts.

Medusa Android banking trojan 2

Despite a reduced footprint—the malware authors removed 17 commands and several permission requests from the previous version—Medusa banking trojan still requires access to Android’s Accessibility Services and retains its capability to send text messages and access the contact list. Overall, it has become more powerful and more difficult to detect. The malware’s target scope has gotten bigger, potentially opening it up to wider deployment.

As of this writing, Cleafy Threat Intelligence hasn’t discovered any dropper app for the Medusa banking trojan on the Google Play Store. Google’s security measures seem to be doing their work effectively. This means you are safe as long as you don’t download and install dubious apps from the web, particularly from links received in messages from unknown numbers. You should download apps only from official app stores and official company websites.

Medusa Android banking trojan 1


[ad_2]
Source link

FireTail Unveils Free Access for All to Cutting-Edge API Security Platform

0
[ad_1]

McLean, United States of America, June 26th, 2024, CyberNewsWire

  • FireTail announces a free version of its enterprise-level API security tools, making them accessible to developers and organizations of all sizes.
  • FireTail’s unique combination of open-source code libraries, inline API call evaluation, security posture management, and centralized audit trails helps eliminate vulnerabilities and protect APIs in real-time.
  • The free plan covers up to 5 APIs, includes 1M API call logs per month, offers 7 days of data retention, and provides clear developer support.

FireTail, a disruptor in API security, unveils free access for all to its cutting-edge API security platform. This initiative opens the door for developers and organizations of any size to access enterprise-level API security tools. 

Today, over 80% of all internet traffic is computer-to-computer communication via APIs. Every mobile app, IoT device, and most modern software applications use APIs, creating a broad attack surface for potential threats. FireTail’s hybrid approach to API security blends open-source code libraries with a feature-packed cloud platform and equips businesses with a unique suite of tools to eliminate API vulnerabilities and provide robust runtime API protection. 

“API security is essential for modern applications, and every developer and tech team should have access to effective security tools,” said Jeremy Snyder, CEO and Co-Founder of FireTail. “Security through obscurity is no longer a viable approach. We’re on a mission to secure all of the world’s APIs and our new free plan ensures ongoing access to an API security platform that delivers genuine insight into the most pressing attack vectors – design flaws in APIs. It’s perfect for smaller organizations striving for stronger API protection, and a great way for individuals or teams within larger organizations to get started.”

Riley Priddle, Co-Founder and CTO at FireTail, added, “We’re excited to help organizations of all sizes to better protect their APIs. We want FireTail to become the de facto standard when it comes to API security. Just because you have a small number of APIs, it doesn’t mean they aren’t critical. We want everyone to have access to the best, enterprise-level API security tools. That’s why we offer both this free tier, as well as our open source libraries.”

For developers and small to medium-sized organizations needing to secure up to 5 APIs, FireTail’s free tier includes comprehensive API security features such as discovery, inventory, assessment, detection and response, and inline runtime protection. Key features include:

  • Protection for up to 5 APIs
  • 1M API calls per month
  • 7 days of logging retention

Thomas Martin, Founder at NephoSec, shared “We’ve been working with FireTail from the outset as both a customer and a distribution partner. Having proven that the platform works for even the largest enterprises with the most complex API security requirements, it’s great to see the team opening that technology up to everyone. This will enable us to solve API security challenges for organizations of all shapes and sizes.”

To access the FireTail API security platform, users can visit https://www.firetail.app or join the team on Tuesday, July 2nd for an in-depth look at what FireTail’s free tier can do.

About FireTail

FireTail allows customers to solve all the most critical problems facing APIs today with a hybrid approach, bringing together cloud, application and code with full blocking capabilities to solve the root causes of API data breaches – flaws at the application and business logic layer in authentication, authorization and data handling. Headquartered in McLean, VA, with offices in Dublin, Ireland, and Helsinki, Finland, FireTail is backed by leading investors, including Paladin Capital, Zscaler, General Advance, and SecureOctane. Users can learn more at https://www.firetail.io.

Contact

Marketing Director
Alan Fagan
FireTail
[email protected]


[ad_2]
Source link

HONOR intros AI Defocus Eye Protection & AI Deepfake Detection

0
[ad_1]

HONOR has just introduced AI Defocus Eye Protection and AI Deepfake Detection. The company claims that this is the industry’s first. This was introduced at MWC Shanghai, in case you were wondering.

HONOR has announced AI Defocus Eye Protection & AI Deepfake Detection features

The company did reach out in order to offer a bit more information on both of these. The AI Defocus Eye Protection tech is supposed to transform smartphone displays into ‘defocus glasses’ in order to provide vision relief for the first time.

HONOR says that this tech has been shown to decrease users’ transient myopia by “13 degrees on average after reading for 25 minutes, with some users experiencing a maximum reduction of 75 degrees”.

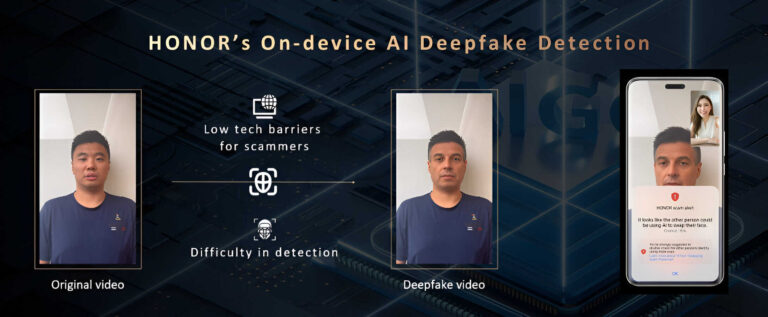
On the flip side, the AI Deepfake Detection authenticates users’ faces during video calls to make sure you’re not talking to a deepfake instead. This is a neat security feature, a useful one, considering the times we live in.

HONOR says that its AI Deepfake Detection has been trained through “a large dataset of videos and images related to online scams, “enabling the AI to perform identification, screening, and comparison within three seconds”.

The company’s CEO says that AI is “revolutionizing our lives”

George Zhao, the CEO of HONOR, said the following: AI is revolutionizing our lives and driving the smartphone industry forward, but much of the industry has focused on cloud-based AI, which is just a part of the puzzle. On-device AI, which is run on smartphones that understand us better than any other devices, is uniquely positioned to deliver services that are tailored to us and our preferences”.

Features like these are always useful to have, needless to say. They can benefit users, that’s the whole point of AI. HONOR has been utilizing AI in interesting ways already. It remains to be seen what we’ll get in the future.

We still don’t know when will these two AI features become available on the company’s phones. We also don’t know which phones will they be available on.


[ad_2]
Source link

Navigating the complexities of datacenter proxy integration in businesses

0
[ad_1]

Datacenter proxies have grown in importance as a tool for businesses looking to differentiate themselves in a competitive market. However, navigating the complexities of their integration in a business setting can be challenging. Despite the obvious complexities of datacenter proxies, efficiently integrating them can allow companies to obtain an edge over the competition by being able to pull massive data sets from the internet. This article provides insights into the benefits of leveraging datacenter proxies to enhance your business operations.

What is a datacenter proxy?

A datacenter proxy, like any other proxy, is a gateway that connects a device to the internet and the website being browsed. When a device connects to the internet, the gateway software substitutes its IP address with one temporarily leased from a data center. By doing so, the proxy user gains a high level of anonymity and can even change how they seem on whatever page they visit.

Datacenter proxies differ from residential and mobile proxies in terms of physical presence. All proxy services replace or obscure an original IP address with another IP; however, unlike a physical residence or a number from a cloud of mobile IPs, a datacenter proxy’s IPs originate from a data center containing several servers. In many instances, this means datacenter proxies run faster and with lower latency. This type of proxy, which assumes the IP address of a data center, effectively makes users seem as if they are connecting from an altogether different location.

How do datacenter proxies work?

A datacenter proxy functions similarly to any other proxy. Let’s break down how they work:

– The user purchases and installs the proxy’s gateway software on their device.

– When accessing the internet, the device connects to the data center and receives an IP address from one of their servers.

– The new IP address allows users to visit their site anonymously.

This method can be used on almost any device with the software installed. Some companies provide this service for free, but the majority operate on a paid membership basis or by offering to lease addresses in bulk for users that require many IPs.

What are data center proxies used for?

Datacenter proxies typically provide internet anonymity at high speeds and low cost, and they have a wide range of uses. While these proxies give anonymity, they are not unlawful or intrinsically dangerous. However, practically all possible uses entail masking identifiable data in order to bypass a domain’s existing safety protocols. Applications of datacenter proxies include:

Market research

Many organizations will employ a datacenter proxy to run market research tools, typically web scrapers. These programs visit certain websites and scan and copy information for analysis. Common data scraping tasks include comparing the costs of a single commodity across multiple markets, finding news articles, and tracking changes on rival websites.

Accessing geo-restricted websites

Certain websites and services only allow users from specific locations to view their content. An easy workaround is to lease an IP address from a datacenter proxy located within the authorized region. Datacenter proxies should correctly mask a user’s IP address, so a user that was blocked from a website may be able to access it again. This is a lawful strategy that people can employ to manage multiple social media accounts under the same IP address.

Protect against possible cyber threats

By masking internet activity, datacenter proxies protect against possible cyber threats. Gathering and interpreting data is a frequent activity for companies. Datacenter proxies are crucial for enterprises handling large amounts of data because of the protection they bring to this endeavor.

Businesses need trustworthy proxies now more than ever as they collect and evaluate bigger data sets to make informed decisions. Because of their faster speeds, increased anonymity, and optimal data throughput, datacenter proxies outperform residential IPs when it comes to scraping.

Boost your data collection efforts

Progress in today’s data-rich environment depends on proficient data collection and processing. To fully realize the potential of big data and advance your company, datacenter proxies are a crucial tool. They create a strong basis for data-driven decision-making that ensures future growth by providing unparalleled speed, security, and flexibility. Companies can also improve their goods and services by gathering input, client testimonials, and behavioral patterns. Innovative solutions will be made possible by increased customer satisfaction and loyalty.

Final thoughts

Begin your data-driven journey right now and connect with others who have harnessed the power of proxy datacenter solutions to elevate their pursuits. As you embark on your business journey, monitor, learn, address, and respond to all challenges that arise. Remember, with the right proxy companions, no insight is out of reach.

Featured image source


[ad_2]
Source link

As Beats Pill returns, the Beats Android app gets an upgrade

0
[ad_1]

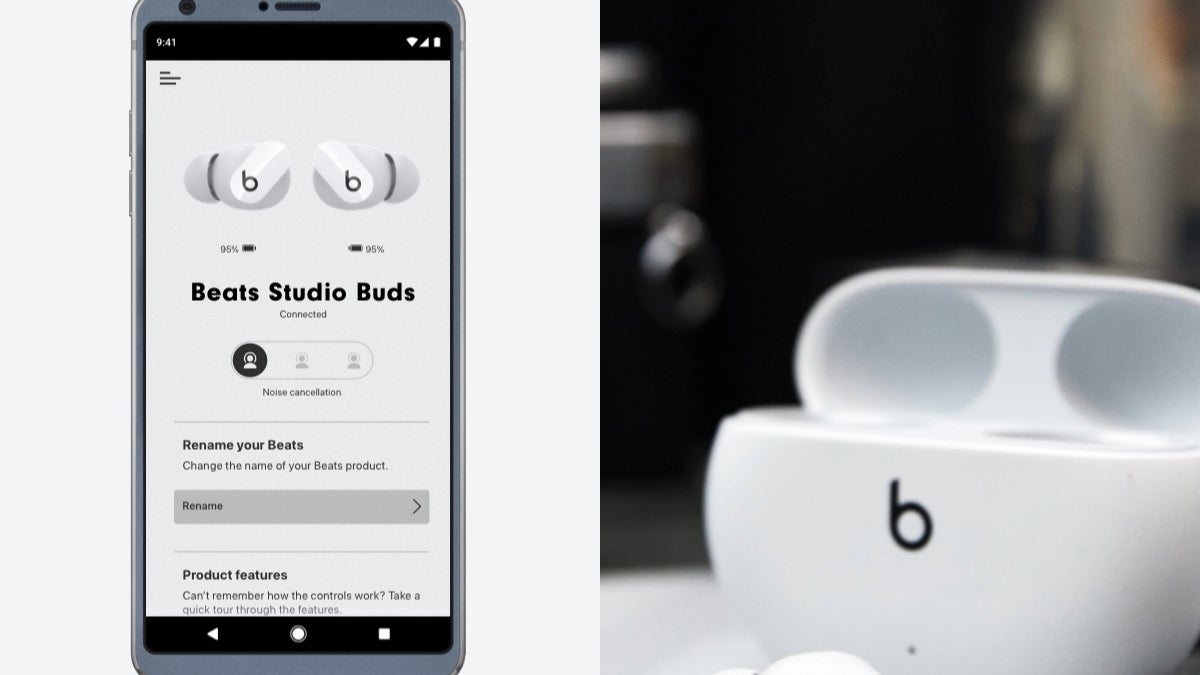
The Android app update brings support for the new Beats Solo Buds and the Beats Pill.

The Beats app lets Android users easily pair and manage all their Beats accessories. It offers controls for Sound Profiles, Equalization, Noise Cancellation, real-time location tracking, and more.For example, with the Beats app, you can select your preferred listening mode on your headphones or earphones. Activate Noise Cancellation to block out external noise, or switch to Transparency mode to stay aware of what’s happening around you.

You can also use the Beats app to connect a second Pill speaker to boost your sound. Or, for an even cooler experience, set one speaker to play the left audio channel and the other to play the right, giving you true stereo sound.

It’s worth noting that the Beats app on Android allows users to install new firmware updates for Beats accessories as they become available, unlike iOS, which doesn’t offer a way to trigger firmware updates for Beats accessories manually. iPhone and iPad users have to wait for the system to automatically download and install updates, similar to how firmware updates are handled for AirPods.

The newly enhanced Beats Pill is now available for $149.99, featuring three vibrant color options. This price is significantly lower than the original $199 price tag of the first-generation Beats Pill from 2012. And it’s not often that Apple enhances the battery life and overall performance of a popular product, all while reducing its starting price.

With the increasing demand for speakers driving steady industry growth, it’s no wonder a new version of the Beats Pill has surfaced, as it is the sole wireless speaker in the Apple-owned company lineup – for now, at least.

In May 2014, Apple made headlines by acquiring Beats Electronics for $3 billion, marking it as its priciest acquisition at the time.


[ad_2]
Source link

Microsoft Announced Copilot for Security TI in Defender XDR

0
[ad_1]

Microsoft has announced the general availability of Copilot for Security threat intelligence embedded experience in the Defender XDR portal.

This AI-powered tool aims to revolutionize the way organizations access, operate on, and integrate Microsoft’s threat intelligence data.

Enhancing Threat Intelligence with Copilot

Microsoft Copilot for Security enables customers to access and utilize Microsoft’s threat intelligence through natural language prompts.

These prompts allow users to ask critical questions about the data and content provided by Microsoft Defender Threat Intelligence (MDTI) and Threat Analytics.

The answers returned are always up-to-date, including information on indicators of compromise (IoCs), intelligence articles, intel profiles, and guidance.

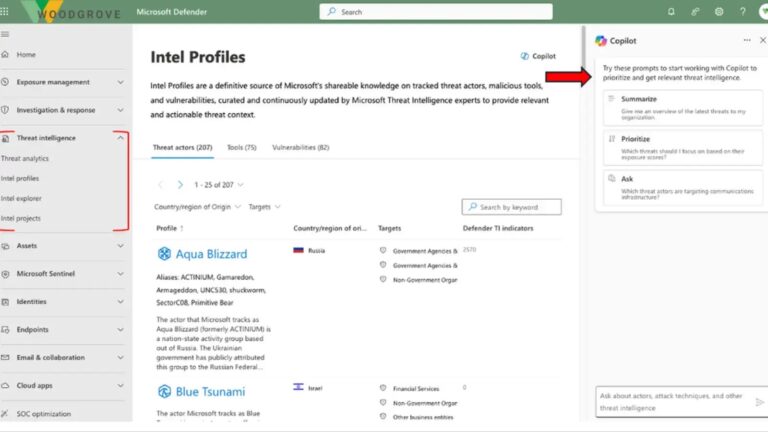
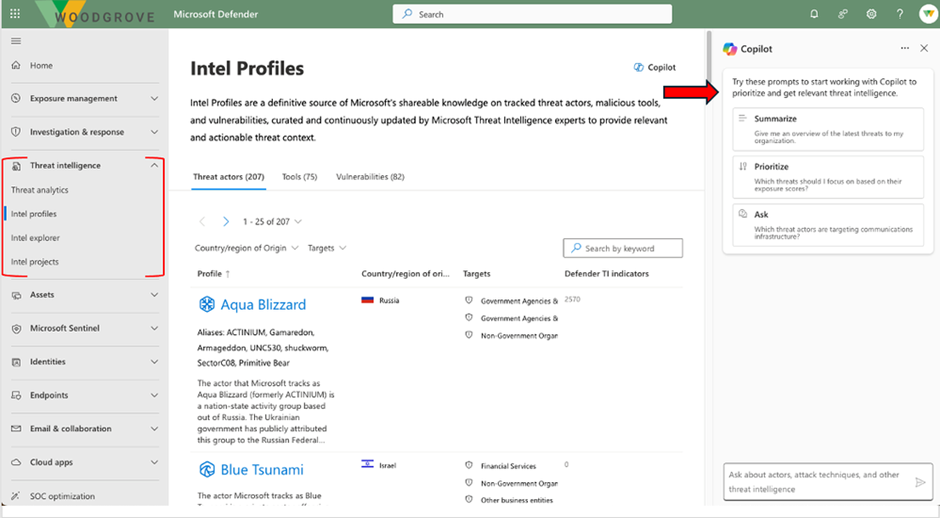
The embedded experience on the right-hand side of the Defender XDR portal has an open prompt bar and a guided experience with three pre-populated prompts.

Scan Your Business Email Inbox to Find Advanced Email Threats - Try AI-Powered Free Threat Scan

The embedded experience, located on the right-hand side of the Defender XDR portal, offers an open prompt bar and a guided experience with three pre-populated prompts.

This feature empowers different security personas to defend against threats at machine speed and scale.

Key Capabilities of the Threat Intelligence Embedded Experience

The Copilot threat intelligence embedded experience in Defender XDR acts as a research assistant, pulling, contextualizing, and summarizing relevant intelligence at machine speed.

Customers can evaluate artifacts and correlate MDTI and Threat Analytics content with other security information from Defender XDR to assess vulnerabilities and understand the scope of an attack.

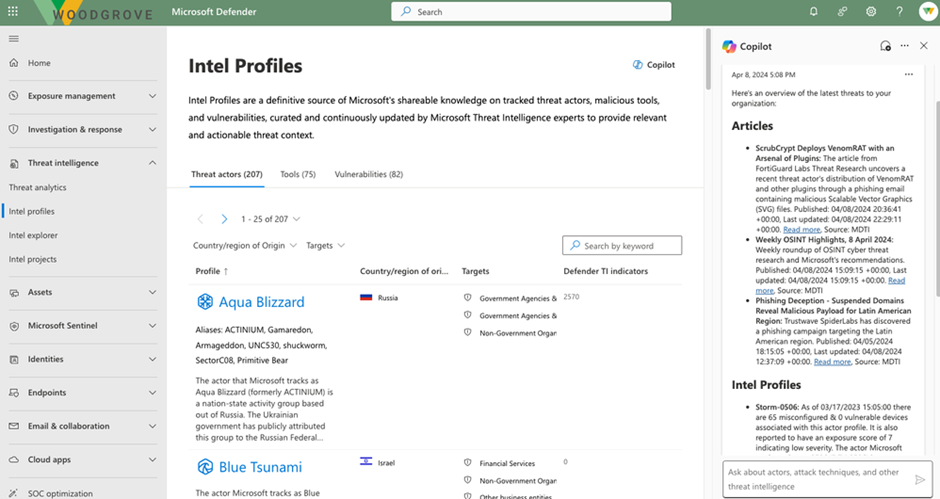
The first pre-populated prompt returns and summarizes intelligence most relevant to your organization.

By clicking on the pre-populated prompt “Give me an overview of the latest threats to my organization,” Copilot returns the latest Intel Profiles and Activity Snapshots, which contain mentions of vulnerabilities, tactics, techniques, and procedures (TTPs) related to the organization’s infrastructure, industry, and region.

Prioritizing Threats and Understanding Risk

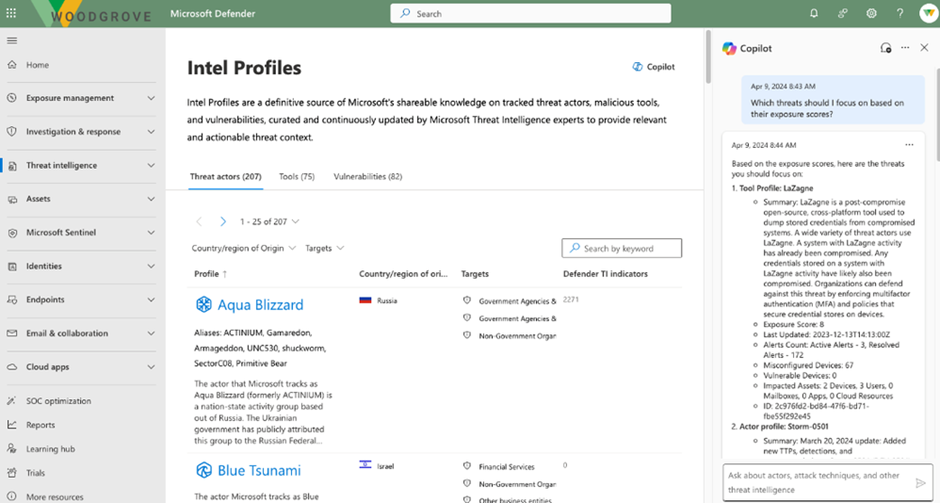
Copilot queries Threat Analytics and MDTI to deliver the most relevant intelligence based on an organization’s exposures and vulnerabilities across their attack surface.

By clicking the pre-populated prompt “Which threats should I focus on based on their exposure score,” customers can quickly retrieve information on indicators, such as IP addresses and domains, to enrich artifacts and understand the risk they pose.

The second pre-populated prompt returns the most critical threat intelligence

Furthermore, Copilot can reason over vulnerability intelligence in MDTI and Threat Analytics to deliver a customized, prioritized list based on a customer’s unique security posture.

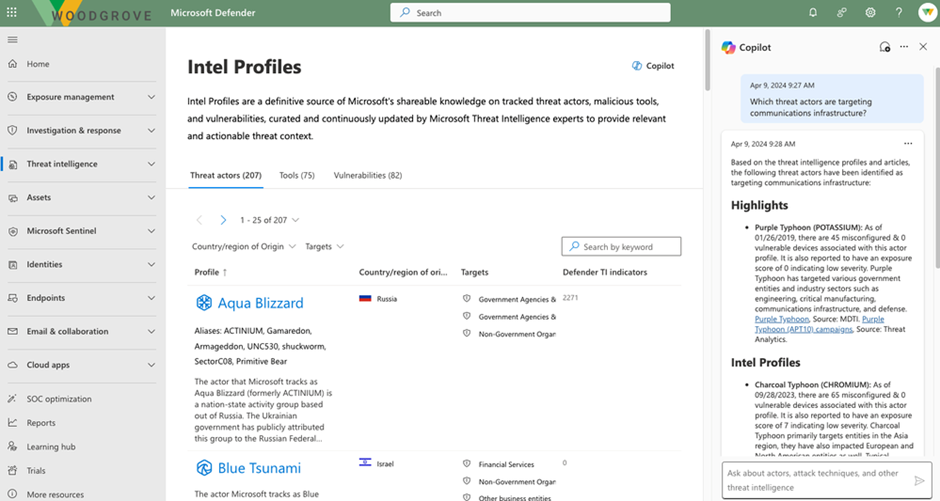
By clicking on the pre-populated prompt “Which threat actors are targeting infrastructure in my industry?” Copilot returns summaries of the top threat actors implicated in attacks involving the customer’s industry.

The third pre-populated prompt offers intelligence relevant to your organization based on industry and other factors.

The launch of Copilot for Security threat intelligence in Defender XDR marks a significant step forward in Microsoft’s commitment to providing cutting-edge cybersecurity solutions.

With its AI-driven capabilities and user-friendly interface, Copilot empowers organizations to stay ahead of the ever-evolving threat landscape and protect their critical assets more effectively.

Free Webinar! 3 Security Trends to Maximize MSP Growth -> Register For Free


[ad_2]
Source link

Critical Vulnerability in MOVEit Transfer Let Hackers Gain Full Files Access

0
[ad_1]

A critical security vulnerability, CVE-2024-5806, has been identified in MOVEit Transfer, a widely used managed file transfer software. The vulnerability poses significant risks to organizations relying on the software for secure data transfers.

The vulnerability is rooted in improper validation of user-supplied input during the authentication process. It can be exploited by sending specially crafted requests to the MOVEit Transfer server, bypassing authentication checks, and gaining administrative access.

The affected versions include MOVEit Transfer 2023.0.0 to 2023.0.10, 2023.1.0 to 2023.1.5, and 2024.0.0 to 2024.0.1.

Progress strongly urges all MOVEit Transfer customers using the affected versions to immediately upgrade to the latest patched version. The patched versions are as follows:

  • MOVEit Transfer 2023.0.11
  • MOVEit Transfer 2023.1.6
  • MOVEit Transfer 2024.0.2

Researchers at Rapid7 confirmed they could reproduce the exploit and achieve an authentication bypass against vulnerable, unpatched versions of MOVEit Transfer and MOVEit Gateway. 

Free Webinar! 3 Security Trends to Maximize MSP Growth -> Register For Free

Impact and Mitigation

The Improper Authentication vulnerability in MOVEit Transfer’s SFTP module can allow attackers to bypass authentication mechanisms and gain unauthorized access to the system. This could potentially lead to data breaches, theft of sensitive information, and other malicious activities.

Researchers at watchTowr initially disclosed the vulnerability and published a detailed technical analysis.

To mitigate the risk, customers are advised to upgrade to the patched versions of MOVEit Transfer using the full installer. The upgrade process will cause a system outage while running.

This vulnerability does not affect MOVEit Cloud customers, as the patch has already been deployed to the cloud infrastructure. Additionally, MOVEit Cloud is safeguarded against third-party vulnerability through strict access controls on the underlying infrastructure.

To mitigate the third-party vulnerability, Progress recommends the following steps:

  1. Verify that public inbound RDP access to MOVEit Transfer servers is blocked.
  2. Limit outbound access from MOVEit Transfer servers to only known trusted endpoints.

Progress will make the third-party vendor’s fix available to MOVEit Transfer customers once released.

Progress has acknowledged the severity of CVE-2024-5806 and is working closely with customers to ensure the vulnerability is addressed swiftly. The company has also provided detailed guidance on applying the patch and securing affected systems.

Progress encourages customers to sign up for the Progress Alert and Notification Service (PANS) to receive email notifications for future product and security updates. Customers can log into the Progress Community Portal to subscribe to PANS.

Customers can refer to Progress’s FAQ page for information and frequently asked questions about Progress Alert Notifications.

Scan Your Business Email Inbox to Find Advanced Email Threats - Try AI-Powered Free Threat Scan


[ad_2]
Source link

U.S. Android users’ financial accounts are at risk with the return of this banking trojan

0
[ad_1]
The Medusa banking trojan has returned to Android after a year off researchers’ radar screens. According to BleepingComputer, new campaigns have been spotted in the U.S., France, Italy, Canada, Spain, the United Kingdom, and Turkey. The new activity started back in May and is potentially serious because the malware can initiate unapproved transactions from infected phones. 

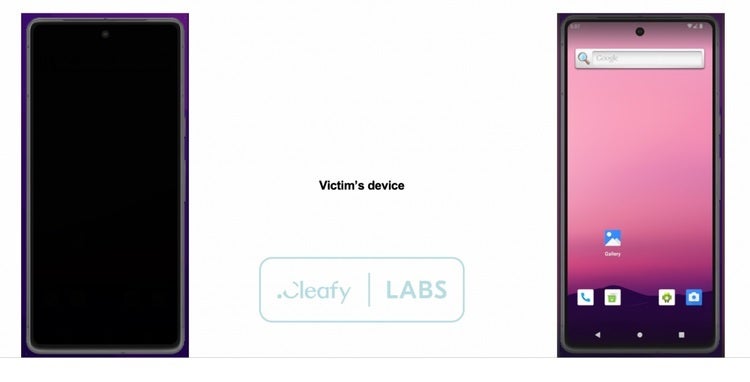
Medusa also can track the keys you type, control the screen, and manipulate text messages. Medusa will also capture screenshots and place overlays across the full screen in order to trick potential victims. As BleepingComputer says, “Overall, the Medusa mobile banking trojan operation appears to expand its targeting scope and be getting stealthier, laying the ground for more massive deployment and higher number of victim counts.” The current campaigns are targeting users of the best Android phones in the aforementioned countries.

Making matters worse, the new version of Medusa is a lighter, more compact version that requires fewer permissions to wreak havoc. According to online fraud management company Cleafy, those who wrote Medusa removed 17 commands from the previous version of the malware and added five.  The apps used to drop the malware onto Android phones include a fake Chrome browser, a 5G connectivity app, and a streaming app called 4K Sports. If you have any of these apps on your phone, delete them immediately.

Luckily, none of the dropper apps used to distribute the malware have been spotted in the Google Play Store; one could make the case that Medusa was allowed to drain financial accounts of Android users because Android allows users to sideload apps. But more worrisome is that Cleafy sees more cybercriminals joining this Android malware-as-a-service (MaaS) operation allowing newer and harder-to-detect ways to distribute the malware to be discovered and created. An MaaS operation is one in which the hacker pays a fee for using the trojan

And when you think about the ways that Medusa can take a screenshot of your phone, read your typing keytaps, or use overlays on the screen to trick you into typing your password where one doesn’t really belong, this is a serious threat that security firms need to continue to monitor. An overlay can also turn your phone’s screen black leaving you thinking that your phone is off while nefarious actions are taking place in the background.

The first thing you can do to help yourself is to stop sideloading apps. Even though Google hasn’t always been able to protect the Play Store from malware, your chances of becoming a victim to a trojan like Medusa expand when you sideload apps on your Android device.

[ad_2]
Source link