5 Cyber Security Risks of ChatGPT

0
[ad_1]
5 Cyber Security Risks of ChatGPT

ChatGPT has been met with skepticism and optimism in equal measures in the cybersecurity realm. IT professionals leverage this chatbot to write firewall rules, detect threats, develop custom codes, test software and vulnerability, and more. 

This has another implication, too – it has made life much easier for novice cybercriminals with frugal resources and low to no technical knowledge. Hackers can exploit its capabilities to write malicious code and test applications for vulnerabilities to exploit and craft malicious content. They do run massive phishing campaigns or perform ransomware attacks rather seamlessly.
In this article, we delve deeper into ChatGPT and cybersecurity. 

What is ChatGPT? 

ChatGPT is an AI-powered chatbot based on a complex machine-learning model developed by Open AI, a private AI and research company specializing in generative AI. Released in November 2022, ChatGPT is powered by Natural Language Processing (NLP) to offer meaningful, human-like responses to user requests and engage in conversations with the users. 

It is trained using Reinforcement Learning from Human Feedback (RLHF), wherein the language model is equipped with a large corpus of text data scraped from the internet. Based on this training data, this chatbot generates responses to user questions, writes summaries, etc. It keeps learning to improve its responses over time. 

Top 5 Cyber Security Risks of ChatGPT

ChatGPT is a potent tool that can transform business through speed, agility, scale, and accuracy. However, it is also a powerful tool for cybercriminals, with or without deep knowledge and resources. Here are the potential threats and negative security consequences of ChatGPT. 

  1. Enables Cybercriminals to Enhance Phishing Messages

One of the biggest security implications of ChatGPT is that threat actors widely use it in drafting legitimate-sounding phishing messages. We are already seeing several instances of the tool being used by cybercriminals to create social engineering and phishing hooks. Security researchers and companies are testing the tool’s capability to do the same. 

Jonathan Todd, a security threat researcher, leveraged the tool to create a code that could analyze Reddit users’ profiles and comments to develop a rapid attack profile. Based on these attack profiles, he instructed the chatbot to craft personalized phishing hooks for emails and text messages. Through this social engineering test, he found that ChatGPT could easily enable threat actors to automate and scale high-fidelity, hyper-personalized phishing campaigns. 

In another instance, security researchers could generate highly convincing World Cup-themed phishing lures in perfect English. This capability is especially useful for threat actors who aren’t native English speakers and don’t have great English fluency. 

It can be leveraged for more realistic conversations with targeted individuals for business email compromise and social media phishing (through Facebook Messenger, WhatsApp, and so on). 

  1. Writing Malicious Code 

While ChatGPT has been programmed not directly to write malicious code or engage in other malicious activity, threat actors are finding and exploiting loopholes. As a result, they can use the chatbot to write malicious code for ransomware attacks, malware attacks, etc. 

One security researcher instructed the chatbot to write code for Swift, the programming language for app development in Apple devices. The code could find all MS Office files in a MacBook and send them over an encrypted connection to the web server. 

He also instructed the chatbot to generate code to encrypt all those documents and then send the private key for decryption. This did not trigger any warning messages or violations. This way, they developed a ransomware code that could target Mac OS devices without directly instructing ChatGPT. 

In another instance, a security researcher instructed the chatbot to find a buffer overflow vulnerability and write code to exploit it. 

  1. Malware 

Security researchers have also found that this chatbot can be leveraged to develop basic information stealer code and Trojan. So, even novice cybercriminals with lesser technical skills can create malicious code. 

In another case, researchers found that ChatGPT can be used alongside other malicious tools to craft phishing communications that contain a malicious payload. When users click on/ download the payload, their device will be infected. 

  1. Snooping and Testing

While ChatGPT can augment existing cybersecurity technology in scanning and testing applications for vulnerabilities, cybercriminals can also use it to snoop around for exploitable gaps and vulnerabilities, making it a double-edged sword. 

  1. Lowers Barriers for Cybercriminals 

ChatGPT does lower the barriers for threat actors who can use it with or without any programming and technical knowledge for various malicious purposes. It is also free and can be used anonymously by anyone globally. 

But ChatGPT Can Revolutionize Cybersecurity for Good Too… 

  1. Improved threat detection capabilities: ChatGPT can effectively analyze large volumes of data to detect potential threats, anomalies, and suspicious behavior. It can enable IT security teams to identify and categorize phishing, malware, and other threats in an agile and speedy manner, enabling them to respond faster. 
  1. Rapid incident response: This tool can augment the capabilities and speed of IT security teams in the event of a cyberattack, enabling them to analyze real-time data and offer actionable insights. It can also be used to automate responses for certain basic threats. So developers and security teams can focus on more complex threats. 
  1. Testing: This tool can be used by security teams and researchers for pen-testing their apps and software. 
  1. Faster Decision-Making: It analyzes security data to unearth patterns and offer actionable insights. Thereby it enhances the decision-making capabilities of security teams and CISOs, who can effectively preempt future threats. 
  1. Streamlining security operations: ChatGPT enables security teams to automate low-level, repetitive, otherwise time-consuming manual tasks, freeing up the bandwidth of security teams. These tasks include report generation, performance analysis, security analytics, etc. 

The Way Forward 

Can ChatGPT revolutionize cybersecurity for good and bad? Yes, it can and, in all probability, will. This AI-powered, self-learning technology can augment an organization’s threat detection capability, boost the speed and agility of incident response, and significantly improve cybersecurity defenses’ efficiency and security decision-making. 

Despite these useful security applications, ChatGPT does bring several drawbacks, ethical challenges, biases, and, most importantly, several cybersecurity risks and AI-enabled threats. Attackers are leveraging it to improve the lethality and sophistication of threats and bypassing its security controls to write malicious codes. 

Organizations need to be aware of these security challenges and their implications on their business continuity. They need to invest in fully managed security solutions like AppTrana that can detect malicious bot activity and stop known and emerging threats with greater accuracy and effectiveness.


[ad_2]
Source link
Twitter imposed ‘temporary limits’ to remove spam & bots

0
[ad_1]

Twitter has opened up about the newly-imposed read limits on tweets. The company says it’s an “extreme measure” it took to remove spam and bots from the platform. It hasn’t revealed when it plans to lift the rate limits, which affect unverified users more than verified ones (those with a Twitter Blue subscription).

On Saturday, Twitter owner Elon Musk announced limits on the number of tweets users can see in a day. Initially, he said that verified users could see a maximum of 6,000 tweets every day, while the limit for unverified users in 600. For new unverified users, it’s only 300 tweets in a day. Later, musk increased the limits to 10,000, 1,000, and 500, respectively.

Musk said that it’s a temporary change but didn’t make it clear when Twitter users can scroll the app limitless again. All he said is that these limits will help the company “address extreme levels of data scraping and system manipulation.” The firm has now published a blog post with further explanation about the move that hasn’t gone down well with many users.

According to Twitter, this “temporarily limited usage” will allow it to “detect and eliminate bots and other bad actors that are harming the platform.” The company didn’t provide advance notice on this move to ensure that the bad actors don’t get time to alter their behavior to evade detection. It added that the change only affects a small percentage of Twitter users, while its effects on advertising have been “minimal.”

Twitter wants to block companies from using its data to build AI tools

Twitter’s plan is to kick out bots that are scraping the public data of its users to build AI models and “manipulating people and conversation on the platform in various ways.” A Twitter employee recently confirmed that the company has removed its legacy APIs to reduce data scraping. This appears to be blocking old tweets from showing up in search results. The number of tweet results on Google Search dropped drastically earlier this week.

Unfortunately, Twitter hasn’t made it clear when the limits will be gone. The company says it will provide an update once the work is complete. “While this work will never be done, we’re all deeply committed to making Twitter a better place for everyone. At times, even for a brief moment, you must slow down to speed up,” it said in the blog post. We will let you know when we hear again from the social network.


[ad_2]
Source link

All iPhone 15 models could get bigger batteries

0
[ad_1]

According to a new report, all iPhone 15 models will get bigger batteries. This rumor comes from China, from an “insider” at Foxconn. Yes, we do know the rumored sizes too.

All iPhone 15 models are tipped to include bigger batteries

Based on this info, the iPhone 15 is coming with a 3,877mAh battery, while the iPhone 15 Plus will include a 4,912mAh unit. The iPhone 15 Pro is said to include a 3,650mAh battery, while the iPhone 15 Pro Max will have a 4,852mAh unit.

If true, these are great news, as these battery packs are considerably larger than the ones the iPhone 14 series offers. The iPhone 14 includes a 3,279mAh unit, while the iPhone 14 Plus has a 4,323mAh battery on the inside. The iPhone 14 Pro sports a 3,200mAh unit, while the iPhone 14 Pro Max includes a 4,323mAh battery.

That’s actually why you should take this info with a grain of salt. It could pan out this way, but don’t get your hopes up just yet. These are quite significant increases, and it’s a bit uncharacteristic for Apple.

iPhones do need smaller battery packs than Android devices to provide similar battery life

We all know that iPhones usually need smaller batteries than Android devices. Well, this change would bring them closer than ever in terms of battery capacity, that’s for sure. An iPhone has never been this close to a 5,000mAh battery capacity.

Based on previous info, however, this year’s iPhones will be a bit thicker, and these battery capacity increases would explain why. We’ll have to wait and see, though.

Next-gen iPhones are coming in September, and they’ll all feature a Type-C USB port. That will be a first for any iPhone, by the way. They’ll all also include a Dynamic Island on the front.


[ad_2]
Source link

Hackers use Malicious QR Codes to Steal Employee Credentials

0
[ad_1]

Hackers use Malicious QR Codes to Retrieve Employee Credentials. Sophisticated technology has been overwritten by simple technologies like QR replacing Barcodes. QR (Quick Response) has been playing a major role in the current generation, which provides the response within a snap.

Speaking of the speed QR codes provide, hackers adapting themselves to it for conducting phishing attacks has increased. Researchers at Inky have seen the latest phishing campaign with QR codes for stealing credentials from employees.

QR Phishing Campaign

The recent QR phishing campaign comes from hijacked organizational accounts which impersonate large brands like Microsoft, Sharepoint, or others.

Based on their analysis, the phishing campaigns originated from a hijacked Japanese retail store, an American manufacturer, and a digital marketing service company in Canada.

QR Phishing campaign

Altogether, these phishing campaigns account for more than 545 emails originating from hijacked accounts, which are found to be a “spray and pray” attack by the attackers.

Image-based QR Phishing

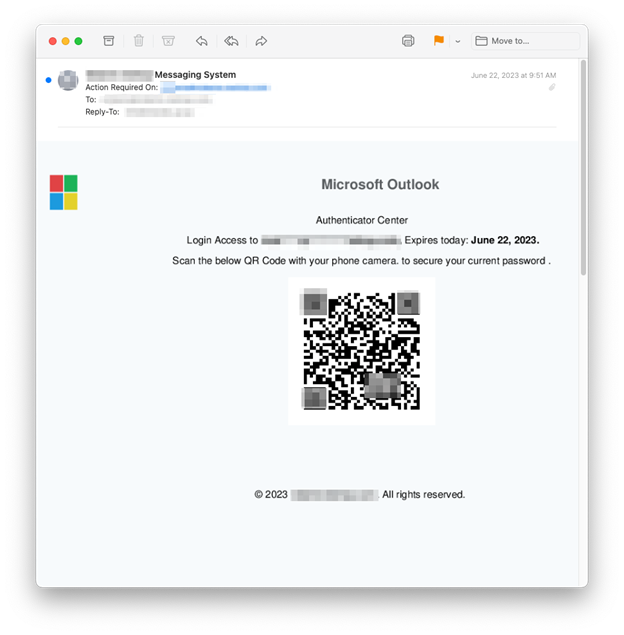
One of the most unique techniques followed in this phishing campaign is that these emails do not contain any text in them. Instead, the email contains only an image of the Malicious QR Codes and the text, which evades any text-based phishing detection. 

These emails additionally require an OCR (Optical Character Recognition) to convert the words in the image to text which is then used for checking phishing texts.

To make this phishing campaign more legitimate to the victims, they have added a parameter in the URL with the victim’s email ID that automatically fills in the email address and name of the victim. This convinces any person who doesn’t have an awareness of phishing.

Inky has published a complete analysis of the phishing campaign. Individuals must train to protect themselves from these kinds of malicious phishing attempts.

“AI-based email security measures Protect your business From Email Threats!” – Request a Free Demo.


[ad_2]
Source link

Xiaomi MIX Fold 3 coming next month, but won’t be sold globally

0
[ad_1]

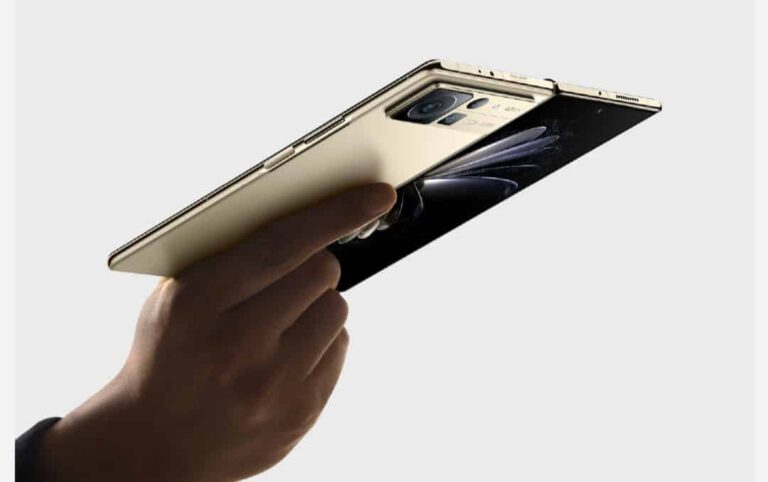
The Xiaomi Mi MIX Fold and MIX Fold 2 were quite interesting devices, especially the second-gen model. The Xiaomi MIX Fold 3 will launch next month, and much like its predecessors, this handset won’t be sold globally either.

The Xiaomi MIX Fold 3 is coming next month, but won’t be sold globally

This information comes from Ice Universe, a well-known tipster. We’re not sure why Xiaomi doesn’t take the plunge and make the device available at least in some countries, but there you go.

The company probably doesn’t think that it’s worth it just yet. Foldables apparently didn’t take off to the level Xiaomi wanted, or something of the sort. That’s a shame, though, as the MIX Fold 2 is quite an interesting device, and very thin for a foldable. It would bring much-needed competition to the Galaxy Z Fold series.

Now, the company’s President, Lu Weibing, did announce that the phone is coming in August, to China. It is also official that Leica lenses will be a part of the package, and some of the company’s camera prowess on the software side of things.

We still do not know when exactly will it launch, however. As the launch event gets closer, Xiaomi will likely share more information. So stay tuned for that, if you’re interested.

The Snapdragon 8 Gen 2 will fuel it, while you can also expect to get a periscope camera

The Snapdragon 8 Gen 2 will likely fuel the phone, while the phone could also offer some sort of water resistance, unlike its predecessor. We do expect the Xiaomi MIX Fold 3 to be as thin or thinner than its predecessor.

A periscope camera is also tipped for the device, which is not something we usually get on foldables. Xiaomi will likely include LPDDR5X RAM here, along with UFS 4.0 flash storage. Android 13 will come pre-installed, with MIUI on top of it.

It remains to be seen what other improvements Xiaomi has in store for us, as the Xiaomi MIX Fold 2 was a substantial leap from the Xiaomi Mi MIX Fold.


[ad_2]
Source link

Magic V2 foldable won’t be the only HONOR device to launch on July 12

0
[ad_1]

HONOR recently announced that the Magic V2 foldable will launch on July 12, but it seems like it won’t be the only device from the company to become official during that event. In fact, HONOR is planning three additional products.

The HONOR Magic V2 foldable is coming on July 12, but it won’t be the only device to launch

The company will announce a tablet, an eSIM smartwatch, and a smart TV too. Do note that we’re talking about a Chinese event here, and chances are that not all of these products will make it to global markets.

The HONOR Magic Vs, HONOR’s latest foldable, did make it to markets outside of China. So, we do hope the same will happen with the Magic V2. When it comes to the other products, we can’t know for sure

Now, the upcoming tablet will be called the MagicPad 13, while the watch will carry the HONOR Watch 4 name. We’re not sure about the name of the smart TV, but it will be a fifth-gen smart TV from the company.

Not much is known about either of these products, only bits and pieces

We don’t have much info about any of these products, to be quite honest. We do know that the tablet will have a 13-inch display, and very thin bezels (for a tablet). The HONOR Watch 4 teaser did appear, and you can check it out below.

HONOR Watch 4 teaser 1

As you can see, this won’t be a round smartwatch. It also seems like it will come with proprietary bands, which is not something we’re happy to see. Not much else is known. In regards to the smart TV, no info leaked out.

If we had to guess, we’d say that both the Magic V2 and MagicPad 13 will make it to global markets. The same will happen with the Watch 4, but the TV will probably stay exclusive to China. We’ll get more info in about a week.


[ad_2]
Source link

Apple could be working on a Mac Monitor that becomes a smart home display

0
[ad_1]

According to new reports, a Mac Monitor Smart Home display might be in the works. Netizens have seen the launch of a ton of Mac Monitors in the past, but this one is new to them. The report claims that this monitor would be able to become a smart home display while it’s not in use.

Apple fans would need to take this information with a pinch of salt, as there is no official confirmation. However, considering that it came from Mark Gurman, a reputable Apple tipster, fans can be in anticipation. From the available information (accessible to Power On subscribers) this product would be the first of its kind and might reshape the entire Mac line-up.

Currently, there is no Mac Monitor available for purchase that can serve as a smart home display. This means that there is no Mac monitor out there that can stay on even while it’s not in use. The major reason for this is that all available monitors from Apple don’t have the necessary tech to control their display.

More details on the rumored Apple Mac Monitor Smart Home display

Apple is currently retailing two monitor displays on their official website. These are the Studio Display and the Pro Display XDR, both of which retail above $1000 and use Apple’s Retina display technology. The Studio display is a 27-inch 5K monitor, while the Pro Display XDR is a 32-inch 6K monitor.

Well, unlike a few other monitors in the market, these options from Apple are not AIO (All-In-One) monitors. This is to say that they don’t come with a fully functional built-in process, hence relying on an external device to function. The processors on board are limited in what they can do, as Apple restricts them to a certain extent.

To cope with this users have to use these displays with the Mac Mini, Studio, or Pro powerhouses. These PCs from Apple come with the processors necessary for the Studio Display and the Pro Display XDR to function. Therefore, for this rumored Mac Monitor Smart Home display to work, it’d need a fully functional iOS device chip.

With this chip on board, the display would be able to support the Always-On feature. This will further enable it to act like a smart home display when it is not in use. If you wish to purchase this monitor once available, you’d need to wait till next year.


[ad_2]
Source link

World’s first smartphone with 24GB of RAM is now official

0
[ad_1]

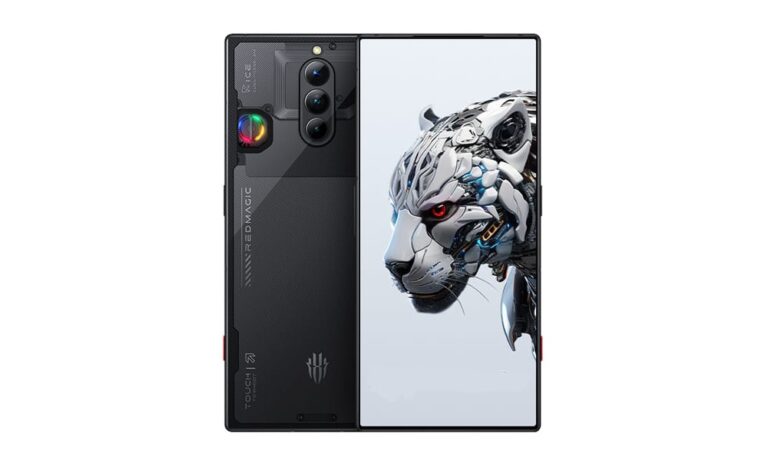
The world’s first smartphone with 24GB of RAM is now official, it’s the RedMagic 8S Pro+. Well, the company announced both the RedMagic 8S Pro and 8S Pro+ variants. The differences are in the RAM, storage, battery and charging departments. RedMagic has been teasing these smartphones for a while now, and now we finally have all the details.

World’s first smartphone with 24GB of RAM is official

The devices got announced in China, but at least one is almost certainly coming to global markets. We’ll have to wait for more info on that, however, as today’s event was fully focused on the Chinese market. Chances are the RedMagic 8S Pro will be launched globally, though.

Let’s talk about the design first. The RedMagic 8S Pro (both the  8S Pro & Pro+ look the same) definitely looks a lot like the RedMagic 8 Pro. The flat sides are once again combined with a flat display that has thin bezels. RedMagic once again opted for an under-display camera, so that you get as much screen real estate as possible.

Three cameras sit on the back of these two devices, and one variant of the phone even features a see-through back. This is a gaming smartphone series, and the phones feature an ICE 12.0 cooling system, which has a 3D vapor chamber, and a graphene heat sink. There is also a cooling fan included in the mix.

An overclocked version of the Snapdragon 8 Gen 2 is used here

These devices come with an overclocked version of the Snapdragon 8 Gen 2, basically the one we’ve seen in the Galaxy S23 series. RedMagic also included up to 24GB of LPDDR5X RAM here (Pro+ model only), and up to 1TB of UFS 4.0 flash storage.

The RedMagic 8S Pro includes a 6,000mAh battery, and supports 80W wired charging. The Pro+ model, however, comes with a 5,000mAh battery, but it supports 165W wired charging.

Shoulder triggers are included in the package, and the same goes for an RGB light on the back. A 16-megapixel under-display camera is used here, and a 50-megapixel main camera (ISOCELL GN5 sensor). An 8-megapixel ultrawide camera also sits on the back, as does a 2-megapixel depth/macro camera.

You do get an audio jack here

RedMagic opted to include a 3.5mm headphone jack on its new devices, while they also support Wi-Fi 7.

The RedMagic 8S Pro with 8GB of RAM and 128GB of storage costs CNY3,999 ($552), that’s the entry-level model. For the top-end variant, though, the RedMagic 8S Pro+ with 24GB of RAM and 1TB of storage, users have to set aside CNY7,499 ($1,036).


[ad_2]
Source link

Burp Suite New GraphQL API to Detect Hidden Endpoints

0
[ad_1]
Burp Suite GraphQL API

The Burp Scanner’s new GraphQL capabilities allow it to recognize known endpoints, locate hidden endpoints, determine whether introspection or recommendations are enabled, and report when an endpoint fails to validate the content type.

Portswigger, the firm behind the renowned web application security testing tool Burp Suite, has announced that Burp Scanner’s new GraphQL checks will automatically indicate multiple instances of GraphQL vulnerabilities during penetration testing.

In most cases, implementation and design problems lead to GraphQL vulnerabilities. Attacks using GraphQL often take the form of malicious requests that provide the attacker access to data or allow them to carry out unauthorized operations.

These attacks may be quite damaging, especially if the user manages to obtain administrator rights by tampering with queries or using a CSRF vulnerability. Information disclosure problems may also result from GraphQL API vulnerabilities.

Identify GraphQL API Flaws

Burp Scanner makes it easy to find the GraphQL endpoint on websites rather than having to manually search through them.

“We’ve defined some passive and active scan checks to find known endpoints automatically, allowing you to focus on finding the vulnerabilities,” the company stated.

When deploying a GraphQL endpoint to production by accident, for instance, a developer can do so without using it on the website. 

Even if a site isn’t utilizing GraphQL, Burp Suite will search for common endpoints and finds hidden deployments.

Source : portswigger

Given that a vulnerability will likely be discovered if it’s an unintentional deployment, these endpoints might be an invaluable resource for a tester.

Introspection lets you execute a query on the real schema to discover what queries it supports. Because a website might not wish to reveal the inner workings of its API to the public, it is frequently disabled in production. 

Burp will detect whether introspection is enabled; while this isn’t a vulnerability in and of itself, it may be beneficial to a tester to help test the site and to a developer to serve as a reminder to turn it off in production.

Further, the company stated that to assist in creating a proper query, certain GraphQL servers, such as Apollo, will offer recommendations when you submit an incorrect query.

Hence, even with introspection turned off, a tester may still utilize this to identify the underlying schema by using a word dictionary and the suggested answer as an oracle.

A valid schema may be created from a dictionary using a tool like clairvoyance. You may locate endpoints with recommendations enabled and report them using Burp.

A POST method with an application/json content type is used by the majority of GraphQL endpoints.

A browser cannot make this request without utilizing CORS (Cross-origin resource sharing ) if the content type is appropriately verified since sending the proper content type will be impossible.

This protects the endpoint against CSRF (Cross-site request forgery). 

However, it may be feasible to abuse the GraphQL endpoint by forging queries if a site does not check the content type and does not utilize a CSRF token, provided mitigations like SameSite cookies may be disregarded or neutralized due to the SameSite None flag. 

Burp will alert the user if a POST request with application/x-www-form-urlencoding or a GET request to the endpoint may be forged.

Conclusion

One of the most well-liked approaches to creating APIs and data-driven apps is now GraphQL. Traditional REST APIs provide a predetermined set of endpoints and replies, but GraphQL enables clients to query for just the data they want, increasing flexibility and efficiency for both client and server.

Knowing the most recent tools will help penetration testers uncover the most recent vulnerabilities. Today’s websites frequently employ GraphQL APIs, which expose the attack surface for a variety of security problems.

“AI-based email security measures Protect your business From Email Threats!” – Request a Free Demo.


[ad_2]
Source link

Official Nothing Phone (2) images surface ahead of launch

0
[ad_1]

The Nothing Phone (2) will become official in about a week, on July 11. As we’re waiting for that to happen, a handful of official Nothing Phone (2) images surfaced online. These images come from Evan Blass aka @evleaks, one of the most prominent tipsters out there.

A handful of official Nothing Phone (2) images leak ahead of launch

Before we get to it, do note that the design of the phone is not exactly a secret now. Nothing partnered up with MKBHD in order to show off the device, in a hands-on video. These images do give us yet another look at the phone, though.

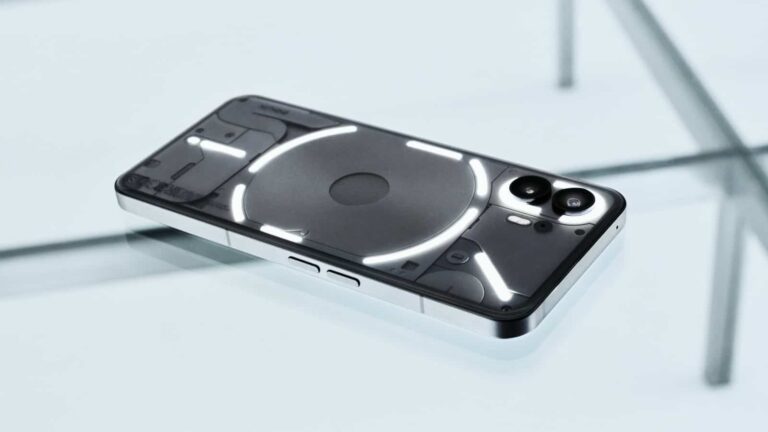
You’ll get to see both color options that will be on offer here, both a white and a dark gray model. That gray variant is replacing the black Nothing Phone (1) model, for better or worse.

Now, the Nothing Phone (2) may look very similar to the Nothing Phone (1), especially at first glance, but there are some differences. Nothing improved the Glyph system on the back, by adding a lot more LEDs, and giving them more functionality.

The device will be easier to hold and use, while its display camera hole also moved

On top of that, the back glass on the phone is now curved, making the device easier and more enjoyable to hold. The sides on the device are still flat, though, and the back glass is see-through, as expected.

The display camera hole is moved to the centered of the display, and the display is still flat. The phone will be made out of metal and glass, as was its predecessor. Two cameras are still placed on the back.

We do know that the Nothing Phone (2) will be fueled by the Snapdragon 8+ Gen 1 SoC. The device will also include a slightly larger display than its predecessor, while retaining a 120Hz refresh rate.

Android 13 will come pre-installed, with a new version of Nothing OS, version 2.0. That build will bring a number of changes to the OS, and based on teasers, quite notable ones.

You’ll get both wired and wireless charging here, stereo speakers, and more. If you’d like to know more about the phone, check out our Nothing Phone (2) preview.


[ad_2]
Source link