However, alongside the ad-supported plan, Netflix also has a basic plan without ads. Now, it seems this plan will be no more, reports 9to5Mac. At least in Canada, Netflix has quietly removed the plan from the subscription options. This way, you can either choose an ad-supported tier or go for a more expensive tier.
Netflix has removed its Basic plan without ads in Canada
Right now, Netflix’s website in Canada doesn’t offer the basic plan without ads as an option for new subscribers. There’s no information right now on whether or not this is a permanent decision or a temporary one, but it looks pretty permanent. It also isn’t clear what happens to the subscribers who currently have the basic plan without ads. In most countries, the streaming service is available with four options: Basic with ads, Basic, Standard, and Premium. On the basic plans, you can watch movies and TV shows in 720p resolution, and you can use a single device only. The Standard plan allows for 1080p resolution and two devices. Premium gives you access to 4K content, and support for up to four different devices.
In Canada, the “Basic with ads” plan has now been rebranded as “Standard with ads”. It supports 1080p resolutions and two devices.
Prices in Canada right now are as follows:
5.99 CAD / month for Standard with ads plan
16.49 CAD / month for the Standard plan
20.99 CAD / month for the Premium plan
The Basic plan without ads (which now does not exist) used to cost 9.99 CAD. This change pretty much means that if you don’t want to watch ads, you’ll have to pay extra.
For now, in the U.S., Netflix plans have remained Standard with ads for $6.99 / month, Basic: $9.99 / month, Standard: $15.49 / month, and Premium: $19.99 / month. It is unclear whether Netflix plans to remove the Basic plan in other countries at the moment and when. When we know more, we’ll let you know.
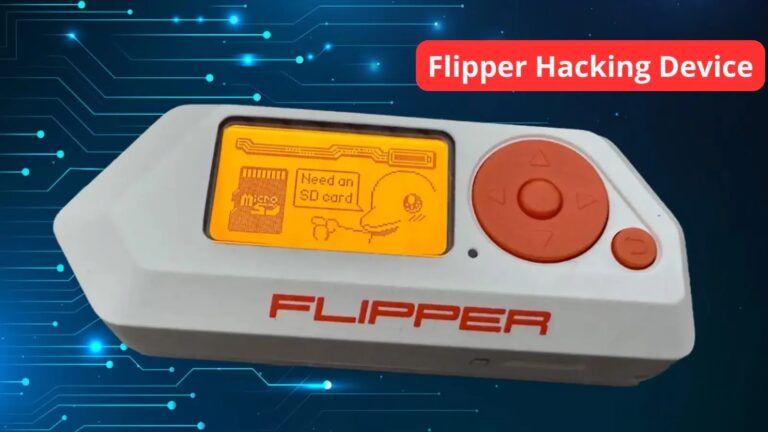
The Flipper Zero hacking device plans on selling $80 million worth of gadgets this year, up from preorders on Kickstarter that totaled over $5 million. It also claims to have sold $25 million of the devices last year.
The business, established in Russia in 2020, departed the nation at the outbreak of the conflict and has since relocated. It claims to no longer be connected to Russia.
What is a Flipper Zero?
Flipper Zero is a “portable gamified multi-tool” designed for anybody interested in cybersecurity, including penetration testers, intellectual people on the internet, students, and anyone with deeper motives.
The tool offers a variety of ways to control your environment, such as wireless devices (like garage openers), RFID card systems, remote keyless entry systems, Flipper Hacking Devices, key fobs, and barrier access. In essence, you may program it to mimic a variety of lock systems.
Additionally, it’s a fun experimentation tool that reveals how insecure the majority of the globe is in reality. The company also emphasizes that the firmware is open source and available for anybody to review.
“Current events will not affect the Flipper Zero production in any way, and all ordered devices will be shipped to backers and those who have pre-ordered, though there may be delays for customers from the CIS countries [the Commonwealth of Independent States] due to logistics disruptions in the region,” the company said in an Instagram post.
Flipper Devices, a firm that employs both Ukrainians and Russians, released a statement in which it declared that it strongly objects to the continuing “special military operation” and that neither of our team members supports it.
The firm is not Russian, according to a corporate representative. Its CEO and more than 10% of the crew are both Ukrainian.
According to TechCrunch report, the Flipper Zero device is on track to sell $80 million worth of its products this year
Further, Flipper Devices is a distributed business that is expanding its London headquarters. Additionally, it adds that Flipper Gadgets works to relocate all of its personnel outside of Russia, doesn’t hire there, and doesn’t export gadgets to Russia.
Some of their workers may travel there to visit family or for other personal reasons as they hold Russian passports.
Tech Specifications of the Tool
ARM Cortex-M4 32-bit 64 MHz (application processor)
ARM Cortex-M0+ 32 MHz (network processor)
Flash: 1024 KB
SRAM: 256 KB
1.4-inch 128 x 64 LCD monochrome display
5-button joystick with back button
2000 mAh rechargeable battery
Sub-1 GHz frequencies: 315 MHz, 433 MHz, 868 MHz, and 915 MHz (depending on regions)
iButton 1-Wire support (Dallas DS1990A/CYFRAL compatible)
USB 2.0 port, type C
Finally, it’s one of the simplest, most affordable methods to use RFID and NFC. It’s also an excellent instructional tool that introduces individuals of all ages to cybersecurity.
“AI-based email security measures Protect your business From Email Threats!” – Request a Free Demo.
Download your games from trusted sources or you may get more than you bargained for…
Researchers have reported how popular game installers like Super Mario Games are being used to deliver malware. The malicious components include cryptominers, the SupremeBot mining client, and the open-source Umbral stealer.
The game installers route offers some very distinct advantages to the cybercriminals:
The games are very popular and downloads are highly sought after, which increases the chances of people downloading them
Game installers are large files which means they can’t be uploaded to most online malware scanners
The game install finishes, so the user trusts the installer did what it promised to do and the extras get ignored
The targeted systems are high performance machines suitable for playing games. Which means they can be expected to be useful in the intended mining activity
The researchers looked at a trojanized version of a Super Mario game installer which came as an NSIS installer. NSIS (Nullsoft Scriptable Install System) is a professional open source system to create Windows installers. In this case it was used to combine three executable files, one of which was the legitimate Super Mario Forever game.
But while the victim is going through the steps of the installation wizard for their game, in the background two secretly dropped files are executed by the same installer.
An XMR (Monero) miner which operates stealthily in the background to mine cryptocurrency for the cybercriminal without authorization and while using system resources in amounts that could be harmful
SupremeBot, a mining client which also downloads a file from a Command & Control (C2) server. In this case an information-stealer identified as the Umbral Stealer
The SupremeBot malware uses some techniques to stay under the radar. First it creates a copy of itself called Super-Mario-Bros.exe and drops that in a randomly named subfolder of the ProgramData folder. It also creates a new scheduled task that runs every 15 minutes to run that copy. When that persistence is set up it kills the process and deletes the original file.
The new copy sends the victim system’s CPU and GPU versions as identifiers to a C2 server to verify if the client is registered. If not, the new client is added and receives XMRig CPU and GPU mining configuration details from the C2 server.
When all that is set up it downloads a Themida packed file. Upon execution, this file unpacks itself and loads the Umbral Stealer into the process memory. The Umbral Stealer is a Windows-based information stealer, which is available on GitHub as an open-source project. It uses Discord webhooks to send collected data to the cybercriminal.
The collected data is obtained from the affected system by:
Capturing screenshots
Retrieving browser passwords and cookies
Capturing webcam images
Obtaining telegram session files and discord tokens
Acquiring Roblox cookies and Minecraft session files
Collecting files associated with cryptocurrency wallets
Advice
To prevent falling victim, here are some guidelines:
Only download from trusted sources
Monitor your system for high CPU usage and other performance issues
Use an updated and real-time anti-malware protection
C2 servers:
silentlegion[.]duckdns[.]org
shadowlegion[.]duckdns[.]org
Malwarebytes EDR and MDR remove all remnants of ransomware and prevent you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.
In your journey to customize your listening experience, you’ve probably made quite a few playlists in your day. You can do the same thing easily on YouTube’s music streaming platform, but the company made a slight change. YouTube Music will automatically save songs to your most recent playlist, according to 9To5Google.
Adding playlists to YouTube Music is an easier affair. When you find the song that you want, simply tap on the three-dot menu to summon some options. About halfway down the menu, you’ll see the Add to playlist button. When you do that, you’ll see a UI with previously created playlists.
The most recently created ones will appear at the top in a carousel while the others will sit below in an alphabetical list. If there aren’t any, tap on the + New Playlist button on the bottom right of the screen. You can also add an entire album to a playlist in the very same way.
YouTube Music will automatically save songs to your most recent playlist
If you’re on a spree and you’re adding songs to a specific playlist, then this feature will make the process just a little bit faster. When you tap the Add to playlist option, that song or album will be sent to your most recent playlist. Instead of opening up the playlist selection UI, you’ll just see a little notification at the bottom of the screen telling you what playlist it was saved to.
If you didn’t want to save it to that playlist, you can tap on the Change button on that notification. Then, you’ll be able to choose another playlist.
If this functionality sounds familiar, it’s the same way that things are handled on the main YouTube app. It seems that the company wants to make for a more consistent experience. This is the same thing for both the web version of YouTube Music and the mobile apps.
There’s a difference, however. Using the website, you’re able to toggle functionality from the settings. As for the app, there’s no setting. It’s on by default.
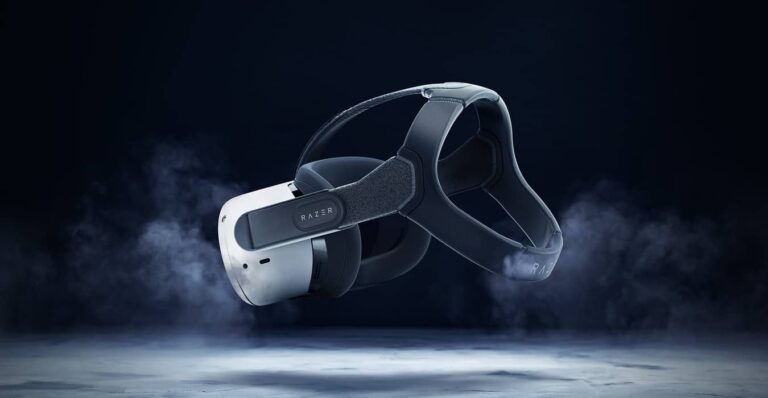
Who doesn’t like free stuff? According to a report from a Redditor (via Techradar), it seems that Meta is giving a certain Meta Quest 2 accessory away to its users. You might be able to get a free Elite Strap.
Since this wasn’t officially announced by the company, you’ll want to take this news with a grain of salt. We’re not sure if the company accidentally sent this out or if it’s an early promo meant for a certain region. We expect the company to eventually say something about it if this was a mistake.
Quest 2 users might get a free Elite Strap
The Redditor in question posted a screenshot of an email from the company to the r/oculus community. It shows an image of the strap along with the text “Get a free Meta Quest 2 Elite Strap, no strings attached.”
Under that, it just gave the user the code to redeem on the website. That’s it; there was nothing else the user needed to do. It seems odd that the company just came out of the blue and presented this offer. If this is a gradual rollout of a promotion, then we expect to see more people getting this email.
If you do get the email, then you’ll have until August 4th to redeem the code. According to the email, you’ll want to log in to your account and go to the Elite Strap order screen. When you check out, the promo code will be automatically applied, knocking your price down to $0.
You’ll want to be on the lookout for an email from Meta. Check your primary inbox and your Updates inbox. If you don’t see anything, take a look at your spam inbox. If you still don’t see the email, then you might just want to wait a few days. There’s still the chance that this email was sent out in error.
Podcasts have become really popular, with over 4 million different ones available to stream. And, of course, these podcasts need a place where people can find them. Well, now one of the podcast apps, Stitcher, is getting out of the game.
As 9to5Google reported, the popular podcasting app will shut down on August 29th after being around for 15 years and attracting millions of listeners in the US. Stitcher changed hands a few times over the years and ended up being owned by SiriusXM, who bought it for $325 million.
Two years after acquiring Stitcher, SiriusXM decided to shut down the platform with both the app and web listening going down.All Stitcher subscribers can use the SiriusXM app to continue listening to their favorite podcasts. If you already have a Stitcher subscription, you should know that starting from June 27, 2023, they won’t automatically renew any Premium subscriptions. If you’re an annual subscriber and your renewal date is after August 29, 2023, you’ll get a refund after the platform shuts down.
Stitcher also suggests that you follow your favorite podcasters on social media or other places to find out where they’ll continue podcasting if they decide not to continue with SiriusXM. There are lots of other podcast platforms available, but the most popular ones are Spotify and Apple Podcasts. They not only have the most listeners but also offer a wide range of shows.
With over 160 million monthly podcast listeners in the US, Stitcher accounted for approximately 6% of the market share, a significant figure in its own right. The platform served as a home for popular podcasts like Conan O’Brien Needs a Friend, Comedy Bang Bang, LeVar Burton Reads, Quentin Tarantino’s Video Archives podcast, and many others.
The latest research discovered Andariel, a part of the Lazarus group, introduced several new malware families, such as YamaBot and MagicRat, updated versions of NukeSped and DTrack.
Andariel group executed the Maui ransomware attack using the DTrack backdoor by exploiting the Log4j vulnerability to gain access.
US Cybersecurity and Infrastructure Security Agency (CISA) reported that Maui ransomware targets mainly companies and government organizations in the US healthcare sector.
As a result, researchers uncovered a previously undocumented malware family and an addition to Andariel’s set of TTPs.
DTrack Backdoor
Andariel infects Windows machines by executing a Log4j exploit that downloads further malware from the C2 server.
The Andariel group’s primary tool is the long-established malware DTrack. It collects information about a victim and sends it to a remote host.
DTrack collects browser history and saves it to a separate file. The variant used in Andariel attacks sends the harvested information to the cybercriminals’ server via HTTP and stores it on a remote host in the victim’s network.
Kaspersky found most of the commands during the attack was executed manually; it did not leave any ransom notes on victim machines.
Also, it found a set of off-the-shelf tools, Andariel, that were installed and run during the command execution phase and then used for further exploitation of the target. Below are some examples:
Supremo remote desktop
3Proxy
Powerline
Putty
Dumpert
NTDSDumpEx
ForkDump
Early RAT
Andariel also uses Early RAT to target the victim machine delivered through phishing emails. The malicious attachment delivers a warning message to the users to enable macros.
Once the user has enabled the macros, it executes a command to ping a server associated with the HolyGhost / Maui ransomware campaign.
EarlyRat, just like many other RATs (remote access Trojans), collects system information upon starting and sends it to the C2 using the following template:
The request has two different parameters: “id” and “query.” Next, the “rep0” and “page” parameters are also supported. They are used in the following cases:
id: unique ID of the machine used as a cryptographic key to decrypt value from “query”
query: the actual content. Is Base64 encoded and rolling XORed with the key specified in the “id” field.
rep0: the value of the current directory
page: the value of the internal state
There are several high-level similarities between EarlyRat and MagicRat. Both are written using a framework: QT is used for MagicRat and PureBasic, for EarlyRat. Also, the functionality of both RATs is very limited.
Although an APT group, Lazarus is notorious for carrying out traditional cybercrime operations, such as executing ransomware, which complicates the cybercrime scene. The gang also employs various unique tools, frequent updates and creates new viruses.
Concentrating on TTPs reduces attribution time and aids in the early detection of attacks. With the aid of this knowledge, preventive efforts can be taken to avert incidents. Andariel APT Group uses weaponized Word Documents to Drop new Malware.
Look for Best Business Email Protection? Try Trustifi, An AI-Based Email security Solution – Request a Free Demo.
ChatGPT may have already hit its public perception wall, according to a Malwarebytes survey that showed high levels of distrust and concern in the tool’s trustworthiness and safety.
Seven months after ChatGPT burst into our lives, it seems the lustre of the chatbot-that’s-going-to-change-everything is starting to fade. A new survey by Malwarebytes exposes deep reservations about ChatGPT, with optimism in startlingly short supply. Of the respondents familiar with ChatGPT:
81% were concerned about possible security and safety risks.
63% don’t trust the information it produces.
51% would like to see work on it paused so regulations can catch up.
The concerns expressed in the survey mirror the trajectory of the news about ChatGPT since its introduction in November 2022.
ChatGPT is a type of Artificial Intelligence (AI) developed by the organization OpenAI. Trained on vast amounts of text data, it can generate human-like responses to prompts or questions. And just in case you don’t know what that means, you should know that the last sentence you read was written by ChatGPT as part of a response to a request to “Describe ChatGPT in a single paragraph.” This is the whole text it generated:
ChatGPT is a powerful language model developed by OpenAI, based on the GPT-3.5 architecture. Trained on vast amounts of text data, it can generate human-like responses to prompts or questions. With its deep learning capabilities, ChatGPT understands context and produces coherent and contextually relevant text. It can assist with various tasks such as answering questions, providing explanations, and offering suggestions. Although it’s not a human and lacks real-time awareness, ChatGPT’s ability to generate text across multiple languages makes it a versatile tool, albeit one that should be cross-verified with reliable sources for accuracy.
When people explored its capabilities in the days and weeks after its launch, it seemed almost miraculous—a wonder tool that could do everything from creating computer programs and replacing search engines, to writing students’ essays and penning punk rock songs. Its release kick-started a race to disrupt everything with AI, and integrate ChatGPT-like interfaces into every conceivable tech product.
But those that know the hype cycle know that the Peak of Inflated Expectations is quickly followed by the Trough of Disillusionment. Predictably, ChatGPT’s rapid ascent was met by an equally rapid backlash as its shortcomings became apparent.
Chief among them is ChatGPT’s propensity to “hallucinate”, the euphemism that data scientists give to untruths created by machine learning models. Perhaps the best example of just how consequential hallucinations can be is Mata v. Avianca, Inc, a court case in which a lawyer found himself in serious hot water after citing numerous non-existent legal cases hallucinated by ChatGPT when he used it as a research tool.
Against that backdrop, Malwarebytes decided to poll its vast pool of newsletter subscribers to see how they felt about ChatGPT, six months after its launch.
Despite all the hype and hooplah surrounding it, only 35% of our tech-savvy respondents agreed with the statement “I am familiar with ChatGPT,” significantly less than the 50% that disagreed.
Those who claimed to be familiar with ChatGPT did not have a rosy outlook. This is what they told us.
Not accurate or trustworthy
The first issue for ChatGPT is that our respondents don’t trust that it’s accurate or trustworthy. Only 12% agreed with the statement “The information produced by ChatGPT is accurate,” while 55% disagreed, a huge discrepancy.
Responses to “The information produced by ChatGPT is accurate” by respondents familiar with ChatGPT
The responses were similarly bleak for the statement “I trust the information produced by ChatGPT,” with only 10% agreeing and a huge 63% disagreeing.
Responses to “I trust the information produced by ChatGPT” by respondents familiar with ChatGPT
A risk to security and safety
Not only was ChatGPT seen as untrustworthy, it was also perceived as a negative influence on safety and security, with few seeing it as a tool that will improve safety, and an overwhelming majority seeing it as a source of risk.
51% disagreed with the statement “ChatGPT and other AI tools will improve Internet safety,” dwarfing the tiny percentage that see it as a positive for safety.
Responses to “ChatGPT and other AI tools will improve internet safety” by respondents familiar with ChatGPT
Worse still, an extraordinary 81% were concerned about the possible security and/or safety risks.
Responses to “I am concerned about the possible security and/or safety risks posed by ChatGPT” by respondents familiar with ChatGPT
They aren’t alone. In March a raft of tech luminaries signed a letter that said “We call on all AI labs to immediately pause for at least 6 months the training of AI systems more powerful than GPT-4.” The letter pulled no punches on the “profound risks” posed by “AI systems with human-competitive intelligence”:
Should we let machines flood our information channels with propaganda and untruth? Should we automate away all the jobs, including the fulfilling ones? Should we develop nonhuman minds that might eventually outnumber, outsmart, obsolete and replace us? Should we risk loss of control of our civilization?
The letter calls for the pause to be used to “jointly develop and implement a set of shared safety protocols for advanced AI design and development that are rigorously audited and overseen by independent outside experts.”
We put the idea to our respondents and 52% of those familiar with ChatGPT agreed, while less than half that number disagreed.
Responses to “Work on ChatGPT and other AI tools should be paused until regulations can catch up” by respondents familiar with ChatGPT
Conclusion
Our survey showed that an overwhelming number of respondents familiar with ChatGPT were concerned about the risks it poses to security and safety. They also don’t trust the information it produces, and would like to see a pause in development so that regulation can catch up. What remains to be seen is whether this is simply a singular moment of anxiety or a trend that will persist.
An AI revolution has been gathering pace for a very long time, and many specific, narrow applications have been enormously successful without stirring this kind of mistrust. For example, at Malwarebytes, Machine Learning and AI have been used for years to help improve efficiency, to identify malware, and improve the overall performance of many technologies.
ChatGPT is a different beast though. It is a generalized AI tool that could help or supplant humans across a broad range of knowledge work, from coding and composing songs to making malware and spreading misinformation.
The uncertainty around how ChatGPT will change our lives, and whether it will take our jobs, is compounded by the mysterious way in which it works. It is an unknown quantity to everyone, even its creators. Machine learning models like ChatGPT are “black boxes” with emergent properties that appear suddenly and unexpectedly as the amount of computing power used to create them increases.
Real world emergent properties have included the ability to perform arithmetic, take college-level exams, and identify the intended meaning of words. The ability to perform these tasks could not be predicted from smaller models, and today’s models cannot be used to predict what the next generation of larger models will be capable of.
That leaves us facing a very uncertain future, both individually and collectively. The continuum of view points held by serious commentators ranges—quite literally—from those who think AI is an existential risk to those who think it will save the world. Given the stakes, the caution of our respondents is no surprise.
Malwarebytes EDR and MDR removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.
TikTok has been making great strides as a video-sharing app, but it’s looking to expand. After trying to bring an online shopping experience to the States via live streams, the company is back with another e-commerce idea. According to Semafor (via Engadget) TikTok is working on bringing an online store.
The video-sharing app was able to combine e-commerce and shopping in other markets. Creators would hold live streams, and viewers would be able to buy items that they promote.
This is an interesting idea that the company was looking to bring to the States. However, it was not able to gain much traction. The company swiftly discontinued this initiative.
Now, TikTok could bring an online store
According to the report, TikTok is readying to launch a dedicated online store for the US audience. The company already has tried e-commerce initiatives in the past, but this one will be different. Before, TikTok would just link customers to other stores where they could buy products. Those stores would handle the shipping and handling of the item.
For this new TikTok store, all of that will be handled by TikTok. There is even talk about TikTok planning on developing fulfillment centers so that it could handle the products. This would put TikTok in competition with services like Amazon and eBay.
At this point, there’s still a lot of information in the air. We’re not sure what kind of items we should expect from the store. We can expect TikTok-branded merchandise, of course. While that may be the case, we can’t rule out the company partnering with different brands to sell their items on the platform. Who knows if TikTok will partner with small businesses as well?
We’re also not sure when the company is going to launch this store. The rumor has it that it could launch as soon as next month. That’s not a long time to wait seeing as it’s already June 28th.
TikTok will be launching this store on shaky ground. The company is still at war with the American government. The US is still pushing to ban the app over national security concerns. We’ll just have to wait to see how this pans out.
Samsung has announced that it is on track to begin mass production of 2nm semiconductor chips for mobile processors in 2025. The company plans to manufacture 2nm chips for HPC (High-Performance Computing) in 2026 and automotive applications in 2027. It will also start producing 1.4nm chips in 2027.
The Korean tech giant is the world’s second-largest semiconductor foundry after TSMC. Both firms started producing 3nm chips last year and have long planned to move to 2nm solutions in 2025. At its 6th annual Samsung Foundry Forum last year, Samsung shared its semiconductor roadmap for the next five years. The roadmap included improvements for 3nm chips as well as production plans for 2nm and 1.4nm solutions.
Samsung reiterated those timelines at this year’s Samsung Foundry Forum, the US edition of which concluded recently (the company will also hold the conference in South Korea in July and expand to Europe and other major Asian markets later this year). The event was attended by over 700 industry guests, while 38 companies showcased the latest foundry technology trends to the attendees.
During the event, Samsung revealed that its 2nm process (SF2) is already promising notable improvements over its 3nm process (SF3). The company is claiming a 12 percent increase in performance, a 25 percent increase in power efficiency, and a 5 percent decrease in chip area. It isn’t yet ready to share more details about 1.4nm chips, though. Those solutions are probably still in the very early stages of development.
Samsung will also launch its 5nm RF process for 6G technology in 2025
Samsung Foundry has more big plans for 2025. The company already has a 5nm Radio Frequency (RF) process under development, which it aims to launch in the first half of 2025. The new solutions will bring a 40 percent increase in power efficiency and a 50 percent decrease in chip area compared to the 14nm process. This will come in time for 6G wireless technology.
The Korean behemoth also plans to begin foundry services for 8-inch gallium nitride (GaN) power semiconductors in 2025. Moreover, it will add automotive applications to its 8nm and 14nm RF processes. Mass production of these solutions is currently limited to mobile applications. Of course, these expansions will require a higher production capacity. To that end, Samsung is expanding its chip factories in South Korea and the US.
Samsung is building new manufacturing lines at its Pyeongtaek campus in South Korea. Line 3 will be ready for mass production of foundry products for mobile and other applications later this year. The construction of its new chip plant in Taylor, Texas, is also in full swing and going according to plan. It will be finished by the end of this year, with operations beginning in the second half of 2024. Samsung says its clean room capacity will increase by 7.3 times between 2021 and 2027.

.png
)