Instagram introduced Reels in 2020, and since then, this feature’s popularity has grown, reaching over 2.35 billion monthly active users. Now, Instagram is rolling out a new feature for its users in the US.
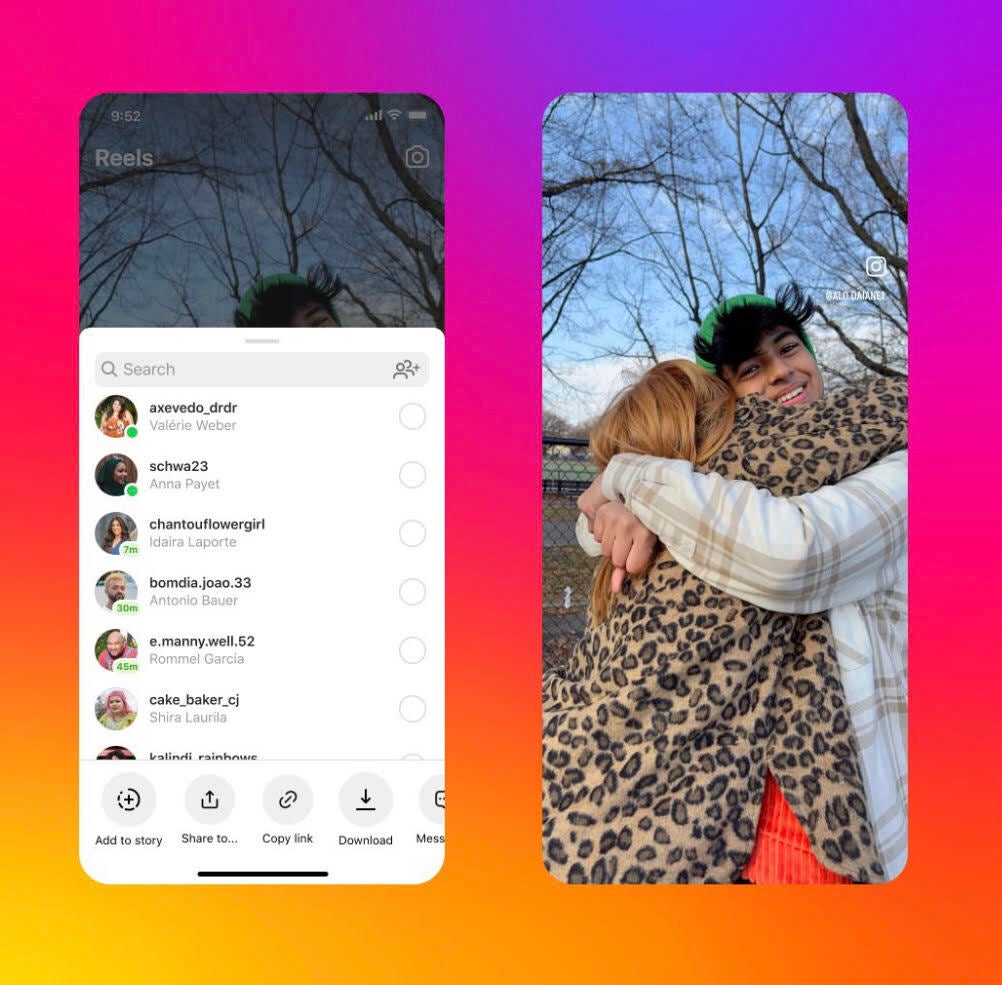
As reported by TechCrunch, Adam Mosseri, CEO of Instagram, announced on his broadcast channel that the company will allow users to download Reels to their camera roll. The process is simple: just tap the share button and select the download option.
It’s important to note that only Reels from public accounts can be downloaded, and even if you have a public account, you can choose to turn off the Reel download option.
Mosseri did not mention whether the downloaded Reels would have watermarks, but based on the picture he uploaded, it is safe to assume that downloaded Reels will indeed bear watermarks, much like they do right now.
Image Credit– Adam Mosseri/Instagram
Currently, every Instagram user can download and share their own Reels on different platforms. However, with this new feature, users will also be able to share other people’s Reels on platforms like TikTok, for example.
TikTok has had this feature for years, and videos with the TikTok logo are now prevalent on various social platforms, contributing to the Chinese video-sharing app’s increasing popularity.
It’s worth noting that although videos with TikTok’s logo are no longer promoted by Instagram’s algorithms, their number on the platform remains substantial. With this new update, there is a chance for Instagram’s logo to appear frequently on its rival platforms as well.
While it is likely that this feature will eventually be available for users worldwide, the exact timeline for its global release remains unknown. We will have to wait and see when that happens.
Stealthy SMS Side-Channel Attack Exposed. When you send an SMS, delivery reports let you know if your message reached the recipient.
But here the most interesting thing is that they also have the potential to provide the location of the receiver.
Researchers have revealed that when you receive a silent SMS message, the sender can easily figure out where you are and it’s possible by looking at when you receive the messages.
The development of this covert SMS side-channel attack involved researchers from multiple colleges working together.
Here below we have mentioned the name researchers along with their colleges:-
Evangelos Bitsikas from Northeastern University
Theodor Schnitzler from Research Center Trustworthy Data Science and Security
Christina Pöpper from New York University Abu Dhabi
Aanjhan Ranganathan from Northeastern University
SMS Side-Channel Attack
By analyzing the message timing, a sender can guess the receiver’s location in multiple countries with around 96% accuracy.
This attack primarily focuses on exploiting the main vulnerabilities of the GSMA network, which powers SMS technology. Since this side-channel attack targets GSMA, so, most of the cell phone networks worldwide get covered.
Although there are other communication options like 3G and 4G, the researchers selected to study SMS, as it is widely used by the general public for 2G communication.
The researchers noticed that receiving SMS Delivery Reports after getting an SMS message activates a timing attack vulnerability.
The SMS Delivery Reports feature operates in a way that the recipient cannot prevent its misuse because they have no control over it.
The attacker’s ML model will give more accurate location predictions during the attack if they have precise information about their targets’ whereabouts.
By sending multiple SMS messages to the target, the attacker can collect the data.
To make them discreet, they can present them as marketing messages that the target would likely dismiss or deploy silent SMS messages.
When a silent SMS is sent, it appears as an empty message on the target device without triggering any notifications, but it is still acknowledged as received by the device’s SMSC.
The researchers sent sets of 20 silent SMS messages every hour using ADB for three days to various test devices located in:-
The United States
The United Arab Emirates
Seven European nations
Ten different operators were included in this experiment, which aimed to analyze a wide collection of communication technologies and variations based on different generations.
Network Delay Factors
Here below we have mentioned all the network delay factors:-
UE Processing
Propagation Delay
Routing Delay
Processing Delay
To perform this attack, the attacker only needs to know the victim’s cell phone number.
Although it takes time, an attacker can uncover a new or unknown location of their target by collecting and analyzing the timing patterns of the user.
While in this case, the time interval between sending and receiving an SMS message can be beneficial significantly.
Today, Amazon has its stunning Omni QLED Series 65-inch TV back on sale, and it’s down to its lowest price ever. Which we last saw in December of last year. So today, you can pick it up for just $599. That’s going to save you $200 off of its regular price, and there’s no promo codes, or coupons you need to clip to get this pice either.
If you want a larger size, the 75-inch Omni QLED TV is also on sale for $899, that’s going to save you $200 as well, ahead of Prime Day in July.
This QLED TV is running on Fire TV. So that means, inside this TV, you’re going to get access to all of your favorite apps. That includes Amazon Prime Video, Hulu, Netflix, YouTube TV and much more. There’s also Alexa support here, and that includes hands-free Alexa.
This TV comes with a few ports as well. There’s an ethernet port, a cable/antenna, USB, IR emitter, headphone, optical, two HDMI 2.0 ports and a HDMI 2.1 port available. So those with a PlayStation 5 or Xbox Series X, you’ll be able to use 4K120 with this TV. That’s definitely good news.
So this is a QLED TV from Amazon. Which is going to provide you with some really fantastic viewing angles and color reproduction. You won’t see a lot of grays where it should be black, since QLED is not backlit like an LED TV would be. While we’re talking about the display here, Amazon has also included Dolby Vision IQ. Which is going to look amazing on this large TV. There’s also support for HLG and HDR10 standards.
You can pick up the new Amazon 65-inch Omni QLED Fire TV today by clicking the link down below. This is likely a very limited stock sale, so you’ll want to be quick.
During the MWC 2023 event held early this year, the ZTE nubia Neovision Glass found its way to the stage. This pair of intelligent AR glasses took the internet by storm and also got lots of attention from netizens. After months of waiting, this product is now available for purchase as the company makes known its price and the regions where it will retail.
Unlike other smart glasses currently available for purchase, this option coming from nubia stands out. It is not only stylish, but also the first of its kind to grace the world of smart wearable devices. ZTE’s nubia division also boasts that this product can also be used during everyday activity thanks to its build and design style.
By simplifying the bulky design of most smart glasses out there, nubia achieved an easy-to-use product. From its specifications to its design, the new ZTE nubia Neovision Glass is unique. Let’s now have a look at what this pair of smart glasses from ZTE have to offer.
Details and pricing of the new ZTE nubia Neovision Glass
If you aren’t aware, nubia is a subdivision of ZTE’s business and they also produce smart devices. Most netizens might remember the brand because of its gaming smartphone line-up, the RedMagic series. Asides from manufacturing gaming smartphones and monitors, they also recently stepped into the smart AR glasses industry.
At MWC 2023 the brand launched its first pair of smart glasses, the Neovision and they became a hit. But, this product didn’t go on sale immediately after its launch. Some impressive features of this product include a 120-inch Micro-OLED screen for projection.
This projection is only visible to the one wearing smart AR glasses. It has a PPI of 3500, an HD resolution of 1080P on both lenses, 1800 nits of brightness, and a 43-degree viewing angle. The ZTE nubia Neovision Glass are also the world’s first smart AR glasses to launch with Hi-Res Audio Quality certification and TÜV Rheinlan certification.
These features ensure a great visual and audio experience for the user. Those who purchase this product can enjoy lossless sound quality thanks to the dual omnidirectional speakers. ZTE nubia also offers users a wide range of swappable magnetic lenses to rock this pair of smart AR glasses, and there’s even a privacy lens option.
Weighing in at just 79g, users won’t find it hard to wear this pair of smart AR glasses as they go about their daily activities. For its pricing, nubia is retailing this product at $529, and it is currently available for purchase in Europe, Asia, the Middle East, and South Africa. The ZTE nubia Neovision Glass is compatible with devices from ZTE, nubia, Xiaomi, Honor, Vivo, Huawei, Samsung, and Apple, just to mention a few. It’s also compatible with gaming consoles like the PS4, PS5, Xbox Series S/X, and the Nintendo Switch.
The development of cryptocurrency technology has resulted in a proliferation of cryptocurrency apps. Alongside the legitimate ones, there has been a troubling surge in fake apps designed to deceive users and unlawfully obtain their money, and one of those was able to bypass the App Store safety checks. Rafael Yakobi, a member of The Crypto Lawyers, a team of lawyers dedicated to helping developers, investors, and organizations with legal representation related to cryptocurrency technology, took to Twitter to warn users about a fake version of Trezor Suite Lite that managed to climb to the top of the App Store search results.
The fraudulent app goes by the name Trezor Wallet Suite, and Yakobi revealed that it had been available for weeks. This means that thousands of people might have unknowingly installed it and become victims of the scam.If you have recently installed a Trezor Wallet app, verifying whether it is legitimate Trezor Suite Lite or the fake Trezor Wallet Suite is crucial. The fake app has already been removed from the App Store.
In his tweet, Yakobi cautioned that the fake app prompts users to provide their seed phrases, granting the app’s operators access to all the victim’s cryptocurrency holdings. And as we can see from some comments on the tweet, this has already happened to at least one user.
Seed words or a seed phrase is a set of words necessary to recover Bitcoin funds “on-chain.” If someone knows these words, they can take control of the user’s Bitcoins. Therefore, Trezor advises users to never enter their seed words on a website and emphasizes the need to safeguard them.
The authentic, open-source wallet developed by Trezor appears in mobile app stores as Trezor Suite Lite. You should know that Trezor is a legitimate cryptocurrency wallet.However, how and why Apple failed to detect this scam remains unclear. Let’s hope that not many individuals have fallen victim to this scheme and lost their money, as in a case two years ago with a similar scam involving the Trezor name.
Multinational accounting firms PricewaterhouseCoopers (PwC) and Ernst & Young (EY) are among the seemingly ever-growing list of victims linked to a cyber security incident that originated with data transfer service, MOVEit.
A supply chain cyber attack launched at MOVEit by ransomware gang Clop has resulted in a series of data breaches for a large number of high-profile brands including Health Service Ireland (HSE) and payroll services provider Zellis. The breach of Zellis has also led to further breaches of their clients, which include the British Broadcasting Company (BBC), airline British Airways and health and beauty retailer Boots.
A spokesperson for PwC said that the firm was “aware that MOVEit, a third party transfer platform, has experienced a cybersecurity incident which has impacted hundreds of organisations including PwC”. They went on to say that while the firm uses MOVEit software for a “limited number of client engagements”, once the cyber attack against MOVEit was discovered, the firm stopped using the software and launched their own investigation into the cyber security incident.
PwC has said they believe the breach will have a “limited impact” and that the company’s network had not been affected by the data breach.
Likewise, EY said they immediately halted all use of MOVEit software once its critical vulnerability came to light. The company has launched its own internal investigation also, and says it has taken steps to secure and protect any data that may have been accessed during the cyber attack.
An EY spokesperson said that while the vast majority of systems which use MOVEit within EY are “secure and were not compromised”, the company will be contacting all those affected, as well as the relevant authorities.
What happened during the MOVEit cyber attack?
The cyber attack against MOVEit saw ransomware gang Clop exploit a critical zero-day vulnerability in MOVEit’s infrastructure. This allowed the malicious actors to break into multiple company networks and steal data.
The vulnerability was flagged by security researchers and the US government on June 1. The US Cybersecurity and Infrastructure Security Agency (CISA) urged all MOVEit clients to check for indications that malicious actors had gained unauthorized access to their networks over the past 30 days and to download and install the software patch released by MOVEit to address the issue.
Ransomware gang Clop later took ownership of the cyber attack by attempting to exploit its victims. In a post on the gang’s Telegram channel, the malicious actors demanded victims pay them by June 14, or their data would be released.
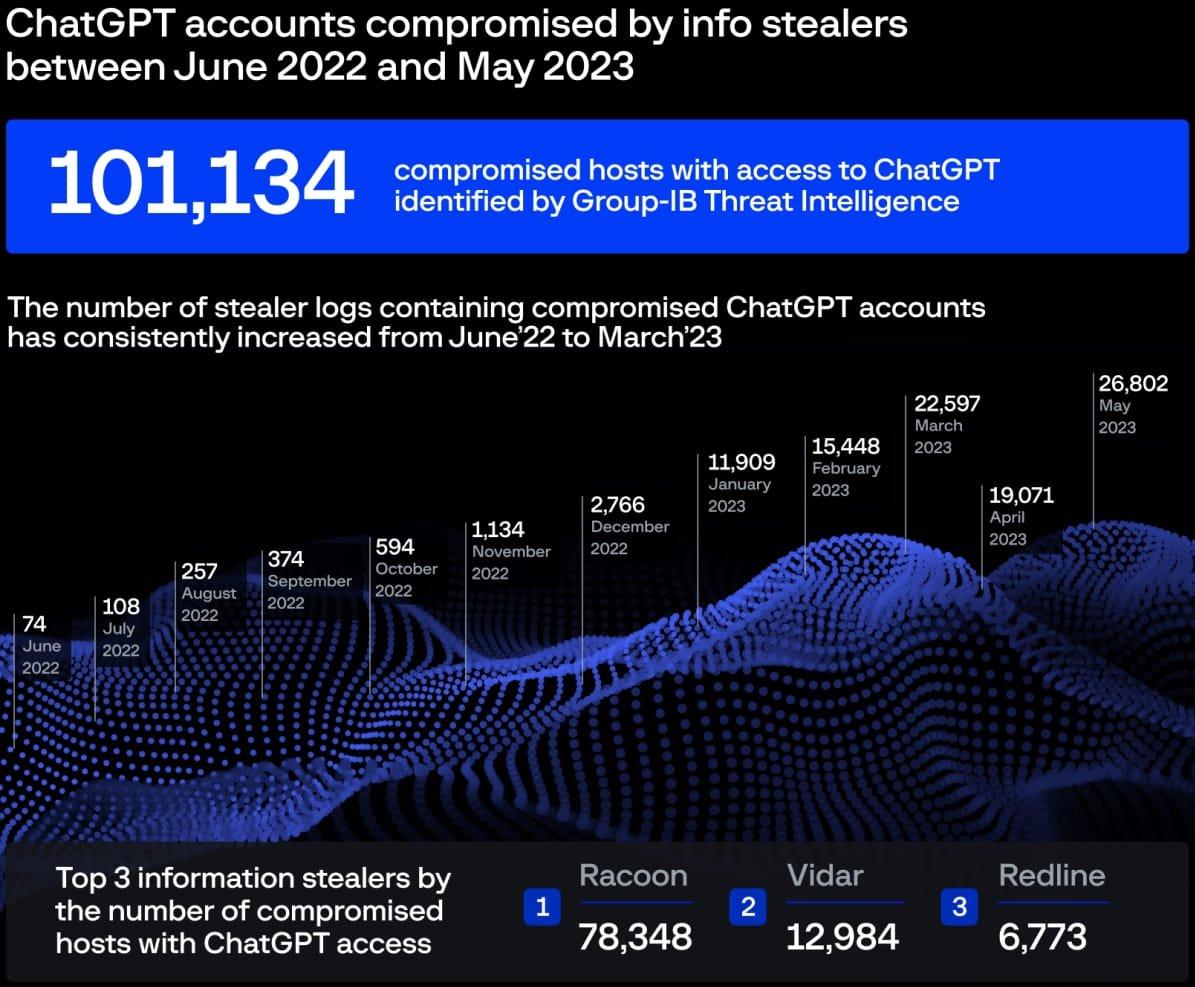
On illegal Dark Web Markets, more than 101,000 hacked accounts of the OpenAI language model ChatGPT were discovered.
These hacked credentials were found in the logs of information-stealing malware sold on illegal dark web markets.
Reports say in May 2023, there were 26,802 logs accessible that contained hacked ChatGPT accounts.
Info stealers are a sort of malware that gathers information from installed browsers on infected machines, including cookies, browsing history, bank card information, credentials saved in browsers, and other information, before sending it all to the malware operator.
Along with extensive information on the victim’s device, hackers can also gather information from emails and instant messengers.
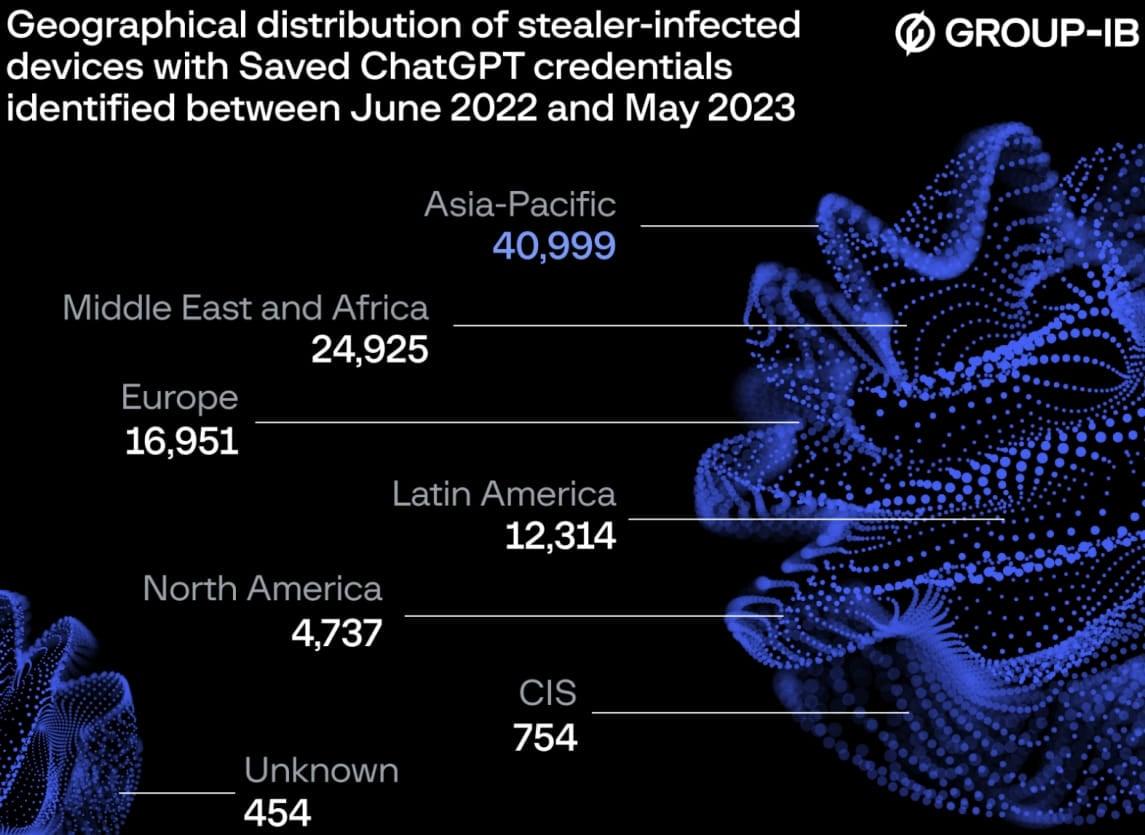
Cyber intelligence firm, Group-IB says that most ChatGPT credentials for sale over the past year have been listed in the Asia-Pacific region.
Rise of Compromised ChatGPT Accounts
Many employees are using chatbots to streamline their job, whether it be company communications or software development.
ChatGPT, by default, keeps a record of all user inquiries and AI responses.
As a result, unauthorized access to ChatGPT accounts may reveal private or sensitive information that can be used to launch attacks specifically against businesses and their employees.
“Many enterprises are integrating ChatGPT into their operational flow.
Employees enter classified correspondences or use the bot to optimize proprietary code”, said Group-IB’s Dmitry Shestakov.
“Given that ChatGPT’s standard configuration retains all conversations, this could inadvertently offer a trove of sensitive intelligence to threat actors if they obtain account credentials.”
According to the information shared with Cyber Security News, a significant number of logs, including ChatGPT accounts, have been compromised by the infamous Raccoon information stealer.
Information stealers frequently exchange logs that include compromised data on dark web marketplaces.
The domain lists discovered in the logs and the information on the hacked host’s IP address are additional details about logs that are accessible on such markets.
Between June 2022 and May 2023, the Asia-Pacific area had the highest percentage (40.5%) of ChatGPT accounts that information stealers compromised.
Consider disabling the platform’s chat saving option if you use ChatGPT to input sensitive data or delete such chats manually as soon as you’re done using the service.
Even if you do not save discussions to your ChatGPT account, the malware infection might still result in a data leak because many information stealers take screenshots of the compromised machine or carry out keylogging.
For this reason, people handling particularly sensitive data should only use solutions securely constructed locally and housed on their servers rather than entrusting any cloud-based services with it.
We take a look at news that data stolen from Reddit may be leaked soon unless the site pays a cool $4.5m to keep it offline.
The ramifications of a Reddit breach which occurred back in February are now being felt, with the attackers threatening to leak the stolen data. The February attack, billed as a “sophisticated phishing campaign” by Reddit, involved an attempt to swipe credentials and two-factor authentication tokens.
One employee was tricked into handing over details, and then reported what had happened to Reddit. Its security team locked things down and began investigating.
The employee’s credentials were reportedly used to gain access to “some internal docs, code, as well as some internal dashboards and business systems”, which exposed “limited contact information” for company contacts and employees, and information about advertisers.
Reddit advised users that their passwords were safe, and so there was no need to alter login details. There were also “no signs” that the breach impacted “the parts of our stack that run Reddit and store the majority of our data, or any of your non-public data”. At the time, Reddit received praise for the clarity of the messaging. “This happened, that didn’t, your login is fine” is somewhat unusual in these situations and messaging is often confusing or even simply absent for far too long.
It seems we’re finally about to find out how on the money Reddit’s assessment of the situation was. Bleeping Computer reports that the Black Cat ransomware group is claiming responsibility for the attack. Worse, its threatening to drop roughly 80GB of data online after supposed attempts to claim a ransom of $4.5m were ignored.
Here’s what Black Cat—also known as ALPHV—has to say about this one:
…I am very happy to know that the public will be able to read all about the statistics they track about their users and all the interesting confidential data we took. Did you know they also silently censor users?
Bold claims indeed, but nobody will know for sure how much of the claims is true or simply bluster until and unless the files are leaked. Interestingly, Black Cat is also demanding that Reddit alters its controversial API pricing changes.
Bleeping Computer notes that nothing was encrypted in this attack; it appears that this was “just” about grabbing as much data as possible and using it to extort money from the victim. A double threat ransomware attack without the ransomware, if you will. Even so, this still presents a major headache for Reddit even without having to worry about encrypted devices.
At this point, nobody knows what exactly may leak when the data drop comes (if it ever does). There is no suggestion from the Black Cat group that passwords were grabbed, so that’s one plus point for Reddit users. As for the rest of it, this seems like a mess for the Reddit CEO and team to deal with.
Black Cat is definitely one of the more prominent ransomware players in recent times, with a string of high-impact and notable attacks. Lehigh Valley Health network in Pennsylvania was hit hard in February of this year, with an understandable furore over photos of breast cancer patients. Elsewhere, the dedicated leak site continues to play to its strengths as we can see with the current Reddit story. As you can see from our June Ransomware review, Black Cat is always close to the top of the pile where infections are concerned. Time may be running out for Reddit as far as the above breach goes, but with a little bit of pre-planning your organisation doesn’t have to meet the same fate.
Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
Stop malicious encryption. Deploy Endpoint Detection and Response software like Malwarebytes EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.
Malwarebytes EDR and MDR removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.
WhatsApp is readying a nifty new trick that will help you keep better track of your media selections when sharing multiple files at once. Instead of a checkmark indicating selected files, the app will now use numbers (1, 2, 3, …). Selected files are numbered in the order of their selection, giving you a better idea of which files should come next. The new update also slightly increases the exposure of the thumbnail to make it easily noticeable.
Numbered thumbnails will let you keep track of your media selections
WhatsApp is the most widely used messaging app around the world. More than two billion people use the Meta-owned service to communicate with their friends, families, and colleagues globally. The app is already quite feature-rich to make these conversations feel complete. But that doesn’t mean there’s no room for improvement. The company frequently pushes new updates to the app to give users a better messaging experience and more features to enjoy every day.
These numbered thumbnails for selected media files are certainly something that most of us didn’t realize we were missing. WhatsApp currently lets you send up to 100 photos and videos at once, many more than the previous limit of 30 files. When selecting files to share, the app uses checkmarks to indicate your selections. A counter at the top of the screen tells you how many files you have selected, while selected files line up in their order of selection at the bottom.
However, that bottom row only fits a maximum of seven tiny thumbnails. It’s difficult to track the order of your selection if you want to share more files unless you repeatedly swipe through it to check the order of selected files or make a mental note of the sequence. With numbered thumbnails, you now get a much better track of the sequence of your media selections in WhatsApp. This will help you decide which file to pick next when sharing multiple photos and videos.
This feature can be found in the latest beta build
This new feature is currently available to users with WhatsApp beta version 2.23.13.6 for Android. If you are in the beta program and want to try it out, install the latest update for the app. Others will have to wait until WhatsApp brings this update to the stable channel. Interested users can join the beta program from here for early access to this improved media picker. WhatsApp beta also gives you early access to many other upcoming features, including circular video messages and redesigned emoji keyboard.
Phone number lookup services have been around for quite some time, but it wasn’t until the advent of mobile phones that they really started to become popular. With the introduction of smartphones, these services became even more accessible and convenient. With the ever-growing popularity of smartphones and mobile applications, it’s no surprise that more and more people are turning to their phones for various tasks. But regarding reverse phone number lookup access, which is better to use – a smartphone or a website?
Comparing usage of mobile apps or websites for reverse phone number lookup
When it comes to reverse phone number lookup, both mobile apps and websites have their own advantages. Mobile apps are usually more convenient to use since they can be accessed from anywhere, anytime. Also, if looking for more specific information, such as criminal records or background checks related to a certain phone number, then utilizing free reverse phone lookup with name might be preferable since many such services have access to the relevant databases. They also tend to be faster than websites.
On the other hand, using a website may be the best option if you’re looking for basic information such as name, address, and other contact details associated with a particular phone number. Most websites offer comprehensive databases that provide detailed results in seconds. Ultimately though, both options can provide valuable results depending on what type of data you need from your search. It all boils down to personal preference and how much time and effort you want to put into finding the necessary information about any given phone number.
Considerations for choosing a paid or free phone reverse lookup
When it comes to choosing a phone reverse lookup service, you have the liberty to choose between paid services or free services. Free services may be limited in the amount of information they provide, while paid services typically offer more comprehensive results. To add to that, some free services may require you to sign up for an account before you can access their data. It’s important to read the terms and conditions of any service before signing up. Another factor to consider is the accuracy of the data provided by the service. Paid services often have access to more reliable databases than free services, so it’s important to research and ensure that your chosen service is reputable and trustworthy. Finally, consider how quickly you need access to the information. Some paid services offer faster turnaround times than free ones, so it may be worth investing in a paid service if you need quick results.
How to use different types of mobile reverse phone number lookup usability features
Mobile reverse phone number lookup services are a great way to find out who is calling you, even if the caller’s number is not listed in your contacts. To make the most of these services, it’s essential to understand their different usability features. For instance, some services allow you to search for a person by name or address, while others provide more detailed information, such as background checks and criminal records. Moreover, some services offer caller ID blocking and other privacy features that can help protect your personal information. It’s also important to consider how easy using the service on your mobile device is. Some services may require downloading an app or using a web browser, while others may be accessible directly from your phone’s home screen. Finally, make sure that the service you choose offers customer support in case you have any questions or need help using the service. By understanding these features and taking advantage of them, you can ensure that you get the most out of your mobile reverse phone number lookup experience.
Balancing safety and convenience with phone number lookups
Where phone number lookups are concerned, it’s essential to balance safety and convenience. On the one hand, you want to ensure the service is secure and your personal information is protected. On the other hand, you also want to ensure that looking up a phone number is as easy and straightforward as possible. To achieve this balance, start by ensuring that the service provider you choose has robust security protocols. Look for features such as two-factor authentication or encryption of data stored on their servers. It is also important to ensure that they have a clear privacy policy in place so you know exactly how your data will be used and shared with third parties. Finally, look for services that offer an intuitive user interface so you can quickly find what you’re looking for without going through too many steps or menus. Such precautions followed carefully will ensure that you enjoy both safety and convenience when using phone number lookup services.


.png
)