Meta’s latest project is so dangerous that even it doesn’t want to release it

0
[ad_1]
Welcome to 2023, also known as “The Age of AI”. Well, in all honesty, we’ve been in an age of AI for awhile now, as some of the best phones rock AI-fueled features. What we’re currently defining as “growth” is likely to be just the start of a super-boom, but still: the hype is real.

As it turns out, everyone has an AI project nowadays. ChatGPT showed its superior capabilities to immensely entertain the minds of several generations and it can even boost your productivity if you use it right! And that’s how the fad became fact. 

So it basically took no time at all for Microsoft and Google to rush out AI platforms of their own. Shocking, Samsung won’t be doing that — outside of its internal tool, but that drama was slightly different. But someone is missing.

Where’s Meta in all of this? Well, you asked just in time. The company unveiled its latest AI-fueled project and… refused to release it to the public? Like, not make a profit? 

Huh. Wow.

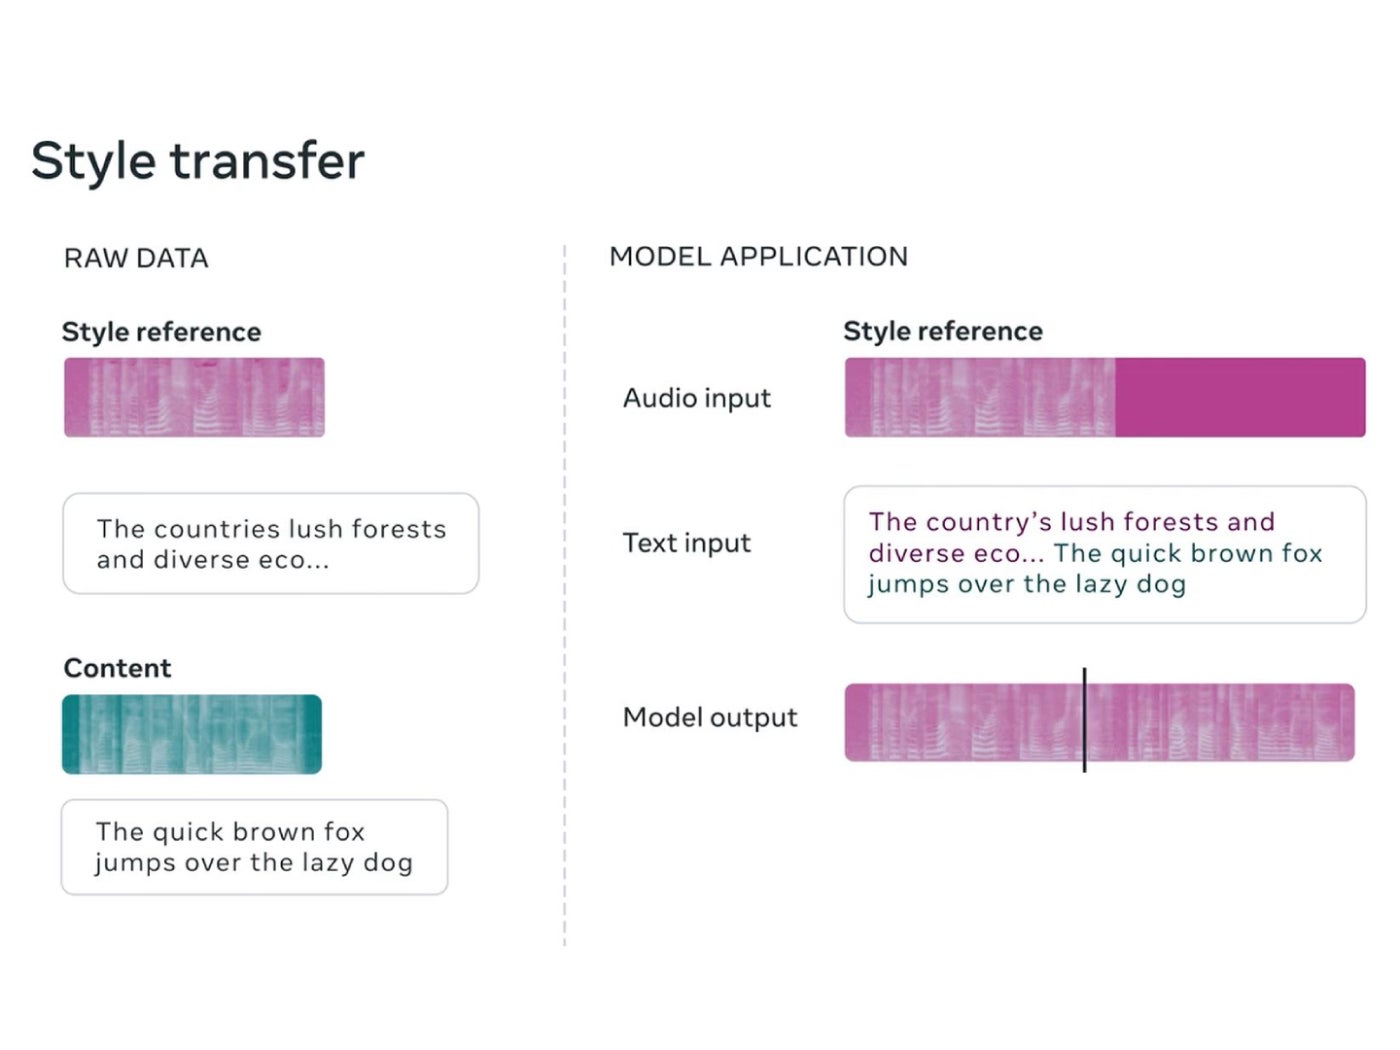
Okay, before we all continue with this series of shocked gasps, let’s elaborate on what the AI even does. Meta’s take differs from the text-based platforms we’ve become witness to thus far, as “Voicebox” is basically capable of generating speech.

Alright, cool, it does text-to-speech. Where’s the scary part? Well, according to Meta’s own research, the platform vastly outperforms other tools from the category. In fact, it is capable of going beyond what it has been trained to accomplish.

Whew, sounds like Meta saved us from an early AI-pocalypse.

But since it’s really fun to see how that might’ve turned out, let’s check on what Voicebox can do anyway. Currently, it is capable of reproducing accurate text-to-speech replication of a person’s voice in six European languages.

So, this may sound pretty harmless. But then the accuracy, precision and detail with which the AI platform executes the task become apparent. And it starts getting Goosebumps-y.

But still, the real surprise here doesn’t come from the fact that Voicebox is outperforming its programming. This was bound to happen sooner or later and Meta is part of Big Tech, so no shocks there. But the company’s choice to effectively not earn money from this platform is absolutely inspiring.

And while this won’t stop existing voice machines from almost-perfectly creating voice clips that sound eerily similar to prolific public figures and political actors, it still raises our faith in humanity just a bit. Before the eventual AI-pocalypse sequel comes, at least.


[ad_2]
Source link

What you need to know

0
[ad_1]

We take a look at some of the options available for your baby’s monitor setup. Is Wi-Fi or something else the best fit for you and your family?

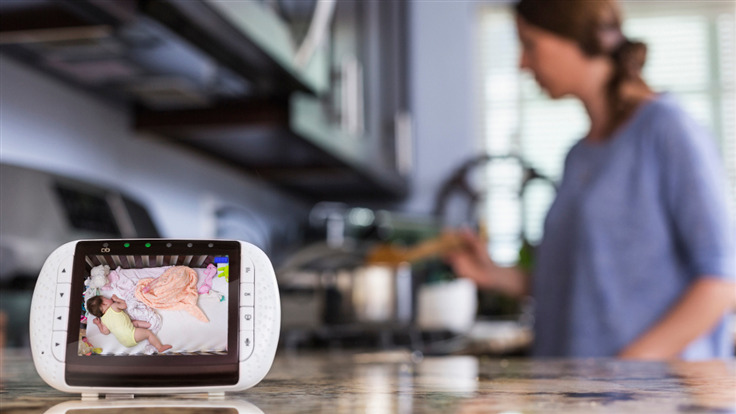
Do you have an impending new arrival in your family of the small and very noisy variety? If so, you’re probably going to invest in a baby monitor for peace of mind both at night and during the day. But do you know what kind of monitor you’re going to buy? Will it be audio only, or have images? Will it be Wi-Fi, or the non Wi-Fi kind? Did you know there’s a non Wi-Fi kind?

As it happens, you don’t have to buy an internet connected device for one of the most private areas of your home. There’s plenty of cheap Internet of Things (IoT) baby monitors out there with default passwords baked in, insecurely stored data, and an alarming amount of compromise stories in the news. If you wish, you can bypass this problem almost completely and go for a device entirely lacking in internet functionality.

The trade-off in this situation is that the device you buy won’t have as many features as a Wi-Fi product, such as the ability to check in on your baby on an app on your phone if you’ve got a babysitter for the evening. However, if all you really care about is monitoring your baby when you’re not in the same room as them, then you can probably go for something more basic.

Non-internet connected baby monitors come with a standalone screen. These screens connect back to the camera in your child’s room. Instead of Wi-Fi, they use other technologies called Digital Enhanced Cordless Telecommunications (DECT) and Frequency Hopping Spread Spectrum (FHSS).

FHSS is one alternative to smart home networks and IoT devices. It rapidly switches frequency when in operation, which can mean a very low chance of someone trying to compromise the device. This isn’t to say a non Wi-Fi camera is unhackable, but given the short range of transmission for these devices, someone would have to be very close to your home to begin poking around. Much the same can be said with baby monitors that use DECT. 

An internet-connected baby monitor is more out of your control. Even if you lock things down at your end with secure passwords it could go wrong if the company you use reveals that footage of your child was stored on an open server somewhere.

In fact, the data doesn’t need to be accidentally stored on an open server at all. Sometimes, the people responsible for keeping your information safe have other ideas in mind. Amazon’s Ring was recently fined by the FTC after it was discovered that every employee had previously had access Ring videos, with some abusing that power to look through users’ personal videos. The FTC also highlighted lack of proper security precautions related to warding off attacks, such as credential stuffing.

If you sign up to a home IoT system managed by one organisation, this is what you might be facing from the very entities you’re entrusting with the most personal details of your living space. It’s probably low risk, but it’s a risk all the same. With this in mind, if you want to go down the Wi-Fi route, here are some tips for securing your baby monitor.

Tips for keeping your baby monitor safe

  1. Change your password: Some cheap devices may ship with passwords that cannot be changed, ever. If this is the case, those passwords are almost certainly available online for anyone to see. Avoid those at all costs and get one where you can change the password. Then change the password as soon as you set up your monitor.
  2. Make your password strong: A weak password could let someone into your baby monitor and allow them to view videos, or even speak over the monitor.
  3. Use multi-factor authentication (MFA): Pick a baby monitor that allows you to use multi-factor (or 2-factor) authentication. This means that even if someone manages to guess your password, they won’t be able to get into your account.
  4. Keep your videos stored locally: There are perhaps specific reasons why you may want recordings from your child’s room stored somewhere. If so, go for a product which allows local saving. It’s simply not worth the risk of footage making its way into the cloud, and other people’s hands.
  5. Turn it off: If you don’t need a camera enabled in your baby’s room, then consider powering it down when not needed. The window of opportunity for breaking into a device is made even smaller if nobody can access it, so when your baby is elsewhere just flip that switch.

As with all digital toys, really have a think about what you need in a device. If you don’t need to see your baby over an app when you’re away from home, then maybe there’s no need for an internet enabled monitor. The more connected you make your home, the more potential security risks you introduce.


We don’t just write about threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.


[ad_2]
Source link

Galaxy S22, S20 & Fold 2 bag Samsung’s June update in the US

0
[ad_1]

Samsung‘s June 2023 update is available for a bunch of Galaxy devices in the US. The company has released the new security patch for the Galaxy S22 series, Galaxy S20 series, and Galaxy Z Fold 2 stateside. The new SMR (Security Maintenance Release) is also widely rolling out to the Galaxy Note 20 series and the Galaxy S21 FE. These devices have already picked up the June update in global markets.

The June SMR is available for both carrier-locked and unlocked units of the Galaxy S22 series in the US. The update comes with firmware build numbers S90*USQU2CWE7 and S90*U1UEU2CWE8, respectively. The rollout appears to be limited to devices on select networks currently, including T-Mobile, Dish, MetroPCS, US Cellular, Nextech, and Bluegrass Cellular. But a wider release shouldn’t be too far off.

This update doesn’t bring any notable new features to the Galaxy S22, Galaxy S22+, and Galaxy S22 Ultra. Samsung’s official changelog mentions updated Software and Terms & Conditions, some system stability and reliability improvements, and the latest security fixes. The June SMR contains more than 60 vulnerability patches. At least three of those are fixes for critical Android OS issues.

For the Galaxy S20 series, the rollout has begun with unlocked units. Samsung is pushing the June SMR to the 2020 flagships with the build number G98*U1UES5HWE1, SamMobile reports. The update is already available for users on pretty much every network. The devices aren’t getting anything more than this month’s security patches. The company should soon cover carrier-locked variants of the Galaxy S20 trio with the June SMR in the US.

The Galaxy Z Fold 2 is another Samsung device that recently started receiving the June update stateside. Samsung has released the new SMR for both carrier-locked and unlocked units of the foldable. The updated firmware build numbers are F916USQU3JWF1 and F916U1UEU3JWF1, respectively. The device is getting a similar changelog as the Galaxy S22 series, including updates to Software and Terms & Conditions.

The June update is widely available for the Galaxy Note 20 series in the US

The Galaxy Note 20 series was the first to receive Samsung’s June update globally. The rollout began in the US early this month but only for unlocked units. The company has now released the new SMR for carrier-locked variants as well. Users are getting the build number N98*USQU4HWF1. Once again, there appear to be some changes to Samsung’s Software and Terms & Conditions with this update.

Last but not least, the June update is now available for the carrier-locked variants of the Galaxy S21 FE in the US. It follows last week’s release for factory-unlocked units. The new build numbers for this phone are G990USQU7EWE3 and G990U1UES7EWE3, respectively. It’s the same changelog as the Galaxy Note 20, Galaxy S22, and Galaxy Z Fold 2, at least for carrier-locked units. If you’re using a Galaxy smartphone, you can check for new updates from the Settings app.


[ad_2]
Source link

Nokia is set to transform 5G with network slicing

0
[ad_1]

It’s no surprise that the advent of 5G has truly changed the telecommunication landscape, enabling internet speeds that seemed impossible just ten years ago. However, this landscape could change even further, as Nokia recently announced a new feature that would allow Android 14 users to purchase and activate network slices directly from their operators.

What exactly is Network Slicing?

The concept of network slicing involves dividing a physical network infrastructure into multiple virtual networks, thereby enabling customized and optimized services for different applications. For example, one 5G network slice can offer improved network performance and reduced latency for cloud gaming enthusiasts, while another can enable spectators at live sporting events to access video replays and real-time statistics. Additionally, network slicing would help significantly reduce network congestion, a common issue faced by public networks.

Although implementing this feature might seem costly and time-consuming, Nokia has devised a monetization strategy in which wireless providers will offer these specialized 5G network slices to subscribers in specific regions, thus creating new revenue streams and establishing a sustainable business model.

However, it’s important to note that Nokia isn’t the only company that has developed network slicing. This is because Ericsson, Oppo, and Qualcomm have previously tested 5G enterprise network slicing on commercially available smartphones, laying the groundwork for broader adoption of this technology.

Launching with Android 14

Nokia first tested the on-demand network slicing in Finland, where the tests demonstrated seamless compatibility with all 4G and 5G devices. As a result, the company aims to launch the feature with the release of Android 14, providing users with much faster speeds and reliability.

Speaking about the achievements, Ari Kynäslahti, Head of Strategy and Technology at Nokia Mobile Networks, stated, “This trial of the on-demand slicing solution for Android smartphone users is another step towards our goal of supporting new monetization opportunities for our operator partners. Slicing unlocks new 5G business possibilities for mobile operators, allowing them to provide premium services and enhance customer experiences.”


[ad_2]
Source link

Domino’s app has a new feature that will deliver pizza to places without an address

0
[ad_1]

So let’s say you’re at a nondescript park playing in a pick-up softball game and after the game is over, you want to reward your teammates (and maybe the other team) by ordering a few pizza pies. However, there is a little problem. The park you’re at doesn’t have a name and there isn’t an address for it that you know of. Well, if you order your pizza from the Domino’s app, you’re still okay even if you don’t have an address to accompany your order.

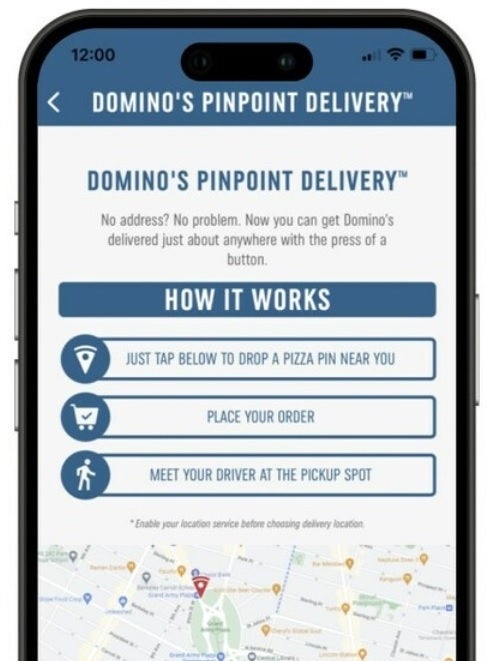
That’s because Domino’s Pizza announced today a new feature called Pinpoint Delivery that when selected as a delivery option on the Domino’s app will allow the user to drop a pin on a map. This will allow the world’s largest pizza company to deliver a Pizza to a park (like our example), a baseball field (also part of our example), the beach, a pool, a campfire and other locations. If you don’t mind sharing your pizza with seagulls, this could prove to be a great idea.
Christopher Thomas-Moore, Domino’s senior vice president – chief digital officer, said, “Domino’s is proud to be the first quick-service restaurant brand in the U.S. to deliver food to customers with the drop of a pin. We’re always striving to make customers’ experiences even better and more convenient, and Domino’s Pinpoint Delivery does exactly that.” The Pinpoint Delivery feature allows Domino’s to deliver to “a countless number of dynamically created hyper-local spots without a typical address.”

While using this feature, consumers will still be able to track their order using Domino’s Tracker, see the GPS location of the driver, and have an ESTPA (estimated time of pizza arrival). When the driver arrives at the pickup spot, the customer will receive an alert. After the alert is received, the customer will activate a visual signal on his phone to help the driver spot him.

Domino’s says “Domino’s Pinpoint locations are delivery locations without traditional addresses selected by customers who order online, pre-pay with credit, debit, or Domino’s gift cards, and agree to receive up to five text notifications that provide updates on their order. Customers and delivery experts will meet at specific locations designated in the Domino’s app that may be adjacent to places like parks, baseball fields, and beaches. Message and data rates may apply.”

So the next time you’re lying on a towel at the beach and you get a message from your stomach that it wants you to order a pizza, using the Domino’s app and Pinpoint Delivery can make it happen. You can download the Domino’s app for iOS by tapping on this link, or for your Android phone by clicking on this link.

[ad_2]
Source link

Update now! ASUS fixes nine security flaws

0
[ad_1]

ASUS has released firmware updates for several router models fixing two critical and several other security issues.

ASUS has released firmware updates for several router models fixing two critical and several other security issues.

The new firmware with accumulated security updates is available for the models GT6, GT-AXE16000, GT-AX11000 PRO, GT-AXE11000, GT-AX6000, GT-AX11000, GS-AX5400, GS-AX3000, XT9, XT8, XT8 V2, RT-AX86U PRO, RT-AX86U, RT-AX86S, RT-AX82U, RT-AX58U, RT-AX3000, TUF-AX6000, and TUF-AX5400.

You will find the latest firmware available for download from the ASUS support page or the appropriate product page. ASUS has also provided a link to new firmware for selected routers at the end of their security advisory.

When in doubt you can find the model number on the sticker which can usually be found on the back side of the router.

screenshot of a sticker on an ASUS routerExample: the model RT-AX86U which is on the list
General instructions on how to update router firmware can be found here

The Common Vulnerabilities and Exposures (CVE) database lists publicly disclosed computer security flaws. The new firmware incorporates the following security fixes:  CVE-2023-28702, CVE-2023-28703, CVE-2023-31195, CVE-2022-46871, CVE-2022-38105, CVE-2022-35401, CVE-2018-1160, CVE-2022-38393, and CVE-2022-26376.

The critical CVEs patched in these updates are:

CVE-2022-26376: A memory corruption vulnerability exists in the httpd unescape functionality of Asuswrt prior to 3.0.0.4.386_48706 and Asuswrt-Merlin New Gen prior to 386.7.. A specially-crafted HTTP request can lead to memory corruption. An attacker can send a network request to trigger this vulnerability.

The Asuswrt-Merlin New Gen is an open source firmware alternative for Asus routers. The unescaped function in this firmware assumes that after a % there are always at least two characters. If this is not the case, one of the instructions in the function cause an out-of-bounds read. Out of bounds reads can lead to crashes or other unexpected vulnerabilities, and may allow an attacker to read sensitive information that they should not have access to.

CVE-2018-1160: Netatalk before 3.1.12 is vulnerable to an out of bounds write in dsi_opensess.c. This is due to lack of bounds checking on attacker controlled data. A remote unauthenticated attacker can leverage this vulnerability to achieve arbitrary code execution.

Netatalk is a free, open-source implementation of the Apple Filing Protocol (AFP). It allows Unix-like operating systems to serve as file servers for Macintosh computers running macOS or Classic Mac OS.

This is a 5 year old vulnerability for which several exploits are publicly available.

Since many, especially home users will shy away of applying firmware, it is important to heed the advice offered by ASUS that says:

“Please note, if you choose not to install this new firmware version, we strongly recommend disabling services accessible from the WAN side to avoid potential unwanted intrusions. These services include remote access from WAN, port forwarding, DDNS, VPN server, DMZ, port trigger.”

General instructions on how to disable the WAN access can be found here under point 7.


We don’t just report on vulnerabilities—we identify them, and prioritize action.

Cybersecurity risks should never spread beyond a headline. Keep vulnerabilities in tow by using Malwarebytes Vulnerability and Patch Management.


[ad_2]
Source link

Samsung pulled back the June update for Galaxy S23 due to bugs

0
[ad_1]

Samsung seems to have pulled back the long-awaited June update for the Galaxy S23 series. The original build reportedly contained some bugs that the company needs to fix first. It will push a new build after the bugs have been fixed. There’s no timeline available for its release.

The Galaxy S23 series was long rumored to get a major update in June. Samsung had announced multiple new camera features for the latest flagships. After a slight delay, the update arrived last Friday with most of the promised goodies and an OTA (over the air) size of around 2.2GB. The rollout began in a handful of Asian countries, including Indonesia, Malaysia, Thailand, the Philippines, and Vietnam. However, it didn’t make it to any other country.

While it was unclear why Samsung was taking so long to bring this update to other markets, turns out the company has halted the rollout. According to noted tipster Ice Universe on Twitter, some users who installed the big June update on their Galaxy S23 found bugs in the new build. The tipster couldn’t provide further details on the bugs discovered by users but suggested that Samsung has pulled the update from its servers because of those bugs. It would release a new build after fixing the issues.

One Galaxy S23 user commented that they haven’t noticed anything wrong with their phone since updating it to the June firmware build. However, the issue seems to be big enough for Samsung to stop the rollout. The company is already working on a new June build (AWF3). The original build number ends with AWF1. Hopefully, it wouldn’t take much longer to push the new build. Galaxy S23 users have already waited a long for the June update. We will let you know when the rollout begins.

The June update for the Galaxy S23 series brings a lot of changes

An OTA update of 2.2GB is pretty big, and that means a lot of changes. The June update for the Galaxy S23 series brings a 2x zoom option for Portrait Mode in the stock camera app. The latest Samsung flagships currently let you capture portrait shots in 1x and 3x zoom only. Additionally, the Korean firm is pushing improvements to the Night mode, camera autofocus, haptic feedback, and system animations and transitions. There may be more changes but we will have to wait until Samsung resumes the rollout for confirmation.


[ad_2]
Source link

Apple’s iPhone 15 to feature Upgraded UWB chip for Vision Pro Headset

0
[ad_1]

The upcoming Apple iPhone 15 is set to get a major upgrade. In the form of a newly upgraded ultrawide band chip. No, this isn’t going to give you better 5G speeds or reception, this is a different form of ultrawide band, which Ming-Chi Kuo says will be included to allow for better optimized integration with the new Vision Pro headset.

Kuo also mentioned the that this new UWB chip would move from the 16nm process, down to a much more advanced 7nm process. This is going to allow for improved performance or reduced power consumption for nearby interactions.

Ultrawide Band is not new to the iPhone

Apple actually first added Ultrawide Band to the iPhone with the iPhone 11. It has used the U1 chip to do all sorts of location-based features, like Find My, Precision Finding and AirDrop. Apple also included the U1 chip in the Apple Series 6 and later, as well as the HomePod Mini, second-generation HomePod, AirTags and much more.

Ultrawide band is something that we’ve seen make its way into a lot of Android phones too, for much the same use-case. It’s a lot more accurate at precise location than just GPS.

Kuo also mentioned that the iPhone 16 coming in 2024, would feature WiFi 7 support. Kuo mentions that “which will be more conducive to Apple’s integration of hardware products running on the same local network and provide a better ecosystem experience.” WiFi 7 is set to be the next big upgrade for WiFi, with it being able to provide speeds of “at least 30 gigabits” per second. And in optimal environments it could hit 40Gbps.

It’s not surprising to see Apple planning this for the iPhone 16, in fact, they are likely already in the early planning stages for the iPhone 17 and 18 at this point. Smartphone makers need to think many years ahead, with their phones.


[ad_2]
Source link

Google apps like Maps, Translate, Calendar and Lens are getting integrated into the iOS Chrome app

0
[ad_1]
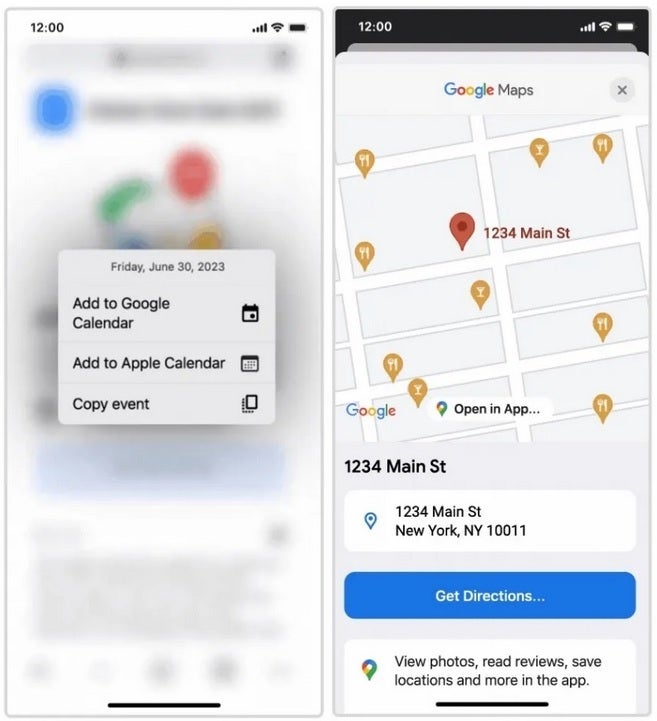
Per 9to5Google, there are some changes being made by Google to the iOS version of Chrome in order to “help you quickly get more done from your browser.” Google notes that Chrome is using “AI to detect addresses on webpages.” Press on an address inside of a webpage and you’ll see an option to “View with Google Maps in Chrome.” Tapping on this option will reveal a mini Google Maps in Chrome that will allow you to “Get Directions” to the address on the webpage that you tapped, or open the full Google Maps app.

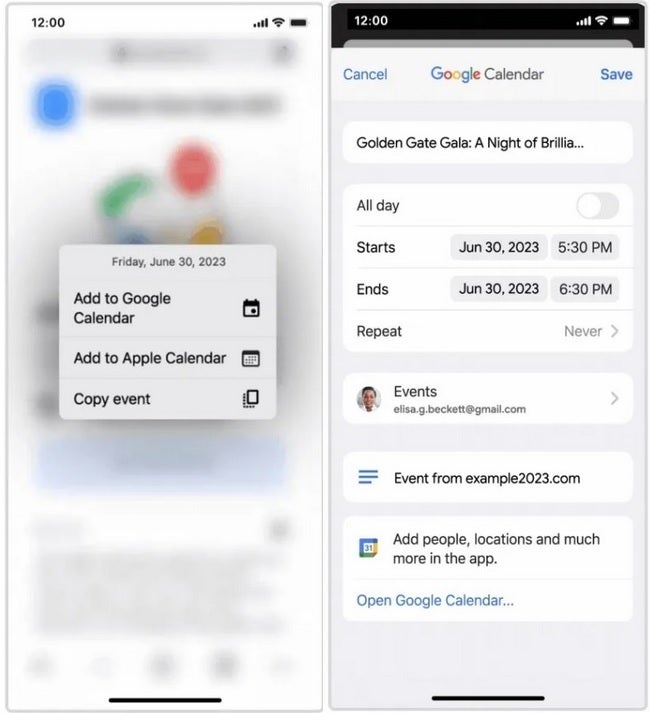
Tap on a date listed on a webpage in the iOS version of Chrome and you’ll see two options: one to add that date to the Google Calendar app, and one to add that date to Apple Calendar. If you choose to add it to Google Calendar, contextual information will be used to fill out some of the blanks and you can adjust some of the information to meet the particulars of the appointment you are adding to the calendar.

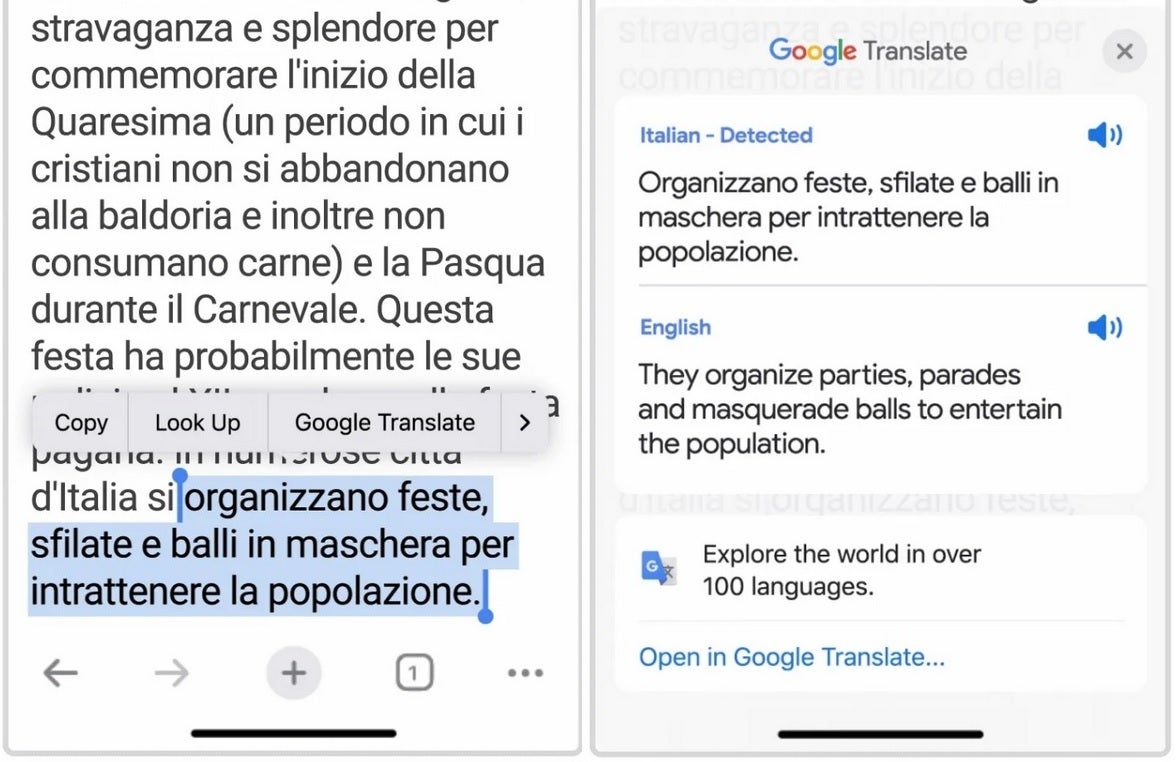
Now here’s another cool feature coming to the iOS version of Chrome. Tap on a passage found on a website written in a foreign language and a toolbar will appear on the display that includes a “Google Translate” option. Tap on it and the section of the webpage you wanted to be translated will appear in English (or your home language).

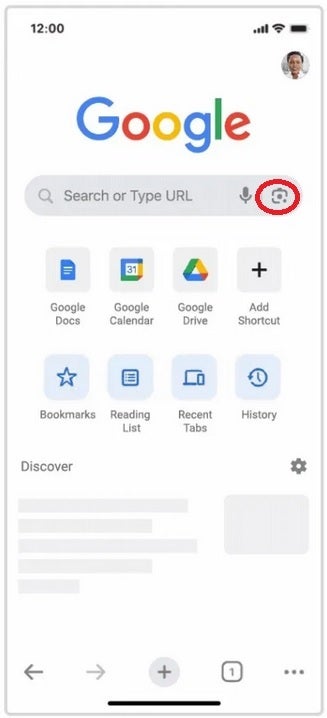
And in the coming months, the search/URL bar at the top of the iOS version of Chrome will include the iconic Google Lens camera icon on the right side of the bar found near the top of the screen. Tap on it and you can “use your camera to search with new pictures you take and existing images in your camera roll.” Think of Lens as another way to access Google’s search engine using photos to input what you want to search for. Currently, an icon for Lens can be found in the search bar near the top of the iOS Google Search app.

It isn’t clear when these new features are coming to the iOS version of Chrome so it will be a matter of trial and error until you find that each of these new features is available on your iPhone.


[ad_2]
Source link