US dangles $10 million reward for information about Cl0p ransomware gang

0
[ad_1]

Rewards for Justice (RFJ) is offering a reward of up to $10 million for information the Cl0p ransomware gang is acting at the direction or under the control of a foreign government.

The US Department of State’s national security rewards program, Rewards for Justice (RFJ), is offering a reward of up to $10 million for information linking the Cl0p ransomware gang, or any other malicious cyber actors targeting US critical infrastructure, to a foreign government.

This is not really new. RFJ’s statutory authorities offers rewards for information in four broad categories and one of them is:

Malicious Cyber Activity For information that identifies or locates any individual who, while acting at the direction or under the control of a foreign government, aids or abets a violation of the Computer Fraud and Abuse Act  (“CFAA”), 18 U.S.C. § 1030. This includes foreign election interference.

But the Tweet explicitly mentioning Cl0p is new. The gang is thought to be behind a recent ransomware spree that compromised a large number of organizations by exploiting a zero-day flaw in Progress’ MOVEit Transfer software.

With as many as 2,500 targets exposed on the Internet, the number of potential victims could be in the hundreds. Some of them have already confirmed, either by the firms themselves or by  being mentioned on the Cl0p leak site.

Campaigns like Cl0p’s abuse of the MOVEit vulnerability, or high profile attacks like the one on Colonial Pipeline in 2021, can trigger an extra focus on the specific ransomware group responsible. Perhaps aware of this, Cl0p took to its website to preemptively promise that it was not going to use data stolen from government organizations and would delete it instead.

It seems that was not enough to avoid getting in the cross-hairs of the US federal government, as we predicted just hours before. The tweet appeared shortly after our own Cybersecurity Evangelist, Mark Stockley, expressed his doubts that Cl0p’s plan would help them avoid unwanted attention from law enforcement.

“Cl0p’s approach supposes that the US government would react more strongly to sensitive data being leaked than it would to multiple simultaneous breaches by the same criminal organisation. This ignores the fact that by using zero-days to attack hundreds of targets simultaneously, including parts of the federal government, Cl0p has already made itself ransomware’s squeakiest wheel.”

And don’t think that all these ransomware operators sit safely out of reach, behind what used to be an iron curtain. The recent arrest of Ruslan Magomedovich Astamirov, a ransomware actor associated with LockBit, in Arizona, shows that the cybercriminals think they can hide anywhere if they are careful enough.

US Attorney Philip R. Sellinger for the District of New Jersey said:

“Astamirov is the third defendant charged by this office in the LockBit global ransomware campaign, and the second defendant to be apprehended. The LockBit conspirators and any other ransomware perpetrators cannot hide behind imagined online anonymity. We will continue to work tirelessly with all our law enforcement partners to identify ransomware perpetrators and bring them to justice.”

Also, some criminals can’t help themselves and need to show off how rich they are or how clever they think they are. The best example may be Mark Sokolovsky. This Ukrainian national and alleged cybercriminal loved posting selfies with fistfuls of cash. When the Russian invasion of Ukraine caused him to flee the country, his girlfriend posted pictures of the couple’s journey on her Instagram account. Sokolovsky was arrested in the Netherlands and is awaiting extradition to the US, accused of being a key player in the cybercrime operation behind Raccoon Stealer.

So, if you’re in the market for a $10 million reward, happy hunting. And for anyone eligible, I’m throwing in a free copy of Malwarebytes Premium. You’ll need it.


Malwarebytes EDR and MDR removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

The Google Home redesign has disappeared for some users

0
[ad_1]

Not too long ago, Google pushed a new design to Google Home, and it made for a better user experience. However, some people are opening the app to see that the Google Home redesign has suddenly disappeared.

Google was testing this new UI with users via an early access program, and it just hit the public this May. So far, it’s been going well. The new design gives the app a look more consistent with the modern Google app look. This means that it employs the Material You design language. However, if you haven’t updated your app to the new design, then you might want to wait until the next update hits the app.

The Google Home redesign is disappearing for some users

This issue is affecting users across both Android and iOS. People are starting up the app to find that it had reverted back to the old design. This is a weird thing to happen, but so are all software bugs.

We’re not sure what the reason behind this is, but there are some common threads. For starters, this issue seems to be tied to the latest version of the app to land. Version 3.2 was just released last week, so the issue might be within the latest update. If you haven’t updated, you might want to skip this version.

For some reason, this issue might be tied to the data that the app saves on your device. According to 9To5Google, if you go into the app’s settings and clear the storage, it will go back to the new UI. However, it will eventually revert back to the older version after some time.

There may be an actual solution

One common thread we’re seeing among the reports is that most of the people experiencing this problem signed up for the early access program. This is the beta program that allows people to try out new features early.

Leaving the program seems to solve the problem absolutely. We’re not seeing reports of the app reverting back after leaving it. If you’re enrolled in the program, and you’re experiencing this issue, try leaving it. After you leave it, you might want to uninstall and reinstall the app. If you’re still having the issue, then you might want to wait for the next update.


[ad_2]
Source link

Apple could be working on an AR/VR headset for iPhones

0
[ad_1]

Apple could be working on an AR or VR headset for the iPhone. The company just secured a patent for a Head Mounted Display device that you can slot iPhones into. According to a new report from ZDNet.

The patent, which Apple was awarded this week, describes how users could take their iPhone or iPad and place it in the head-mounted display to be worn like a VR headset. The accessory would have an adjustable strap for fastening the device to the wearer’s head. It’s also state that the patent describes the user’s iPhone or iPad should be able to detect that it’s being placed in the accessory to create a wireless connection.

This sort of design is an all-too common one these days as both Samsung and Google have been down this road. Samsung’s Gear VR series of devices and Google’s Daydream View worked in much the same way. You slot your phone into the headset and its screen acts as the display for the VR and AR experiences. Google also experimented with Google Cardboard before the Daydream headsets were released.

An iPhone-powered VR headset from Apple could be a lot cheaper

Phone-powered VR headsets weren’t exactly the most exciting. At least compared to what we have now. But there’s no denying they helped pave the way for today’s VR hardware. Even if only in small ways.

Gear VR and Google Daydream View walked so Apple’s potentially upcoming phone-powered VR headset could run so to speak. If it ever gets made. Securing the patent doesn’t necessarily mean Apple will use it. Or that a headset would make it to a production phase.

But another reason why phone-powered VR headsets might have their place is because they tend to be much less expensive than current options. Maybe not by leaps and bounds now with Quest 2 back down to $299. But for those in the Apple ecosystem, a VR headset powered by your iPhone would be a lot less than Apple’s recently announced Vision Pro. Which sits at a whopping $3,499.


[ad_2]
Source link

YouTube’s New 1080p Premium option starts showing up for Android and Google TV users

0
[ad_1]
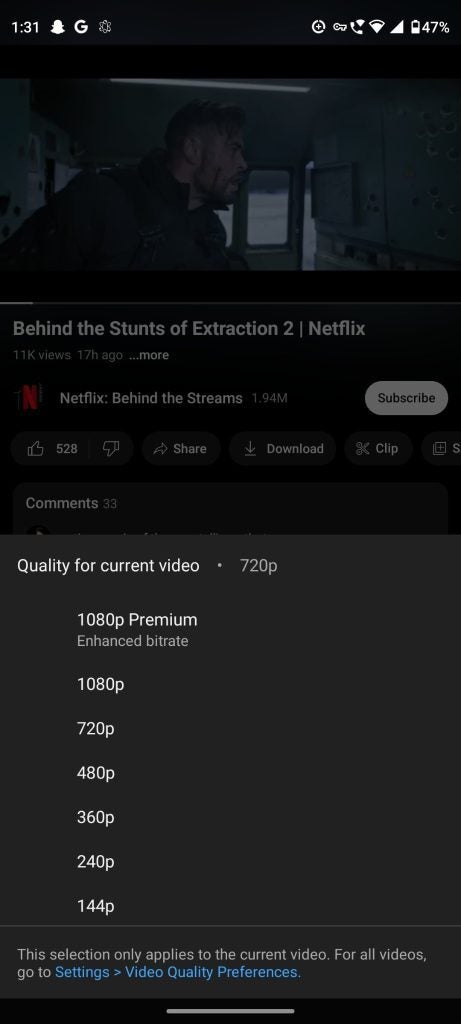
YouTube is testing a new 1080p Premium tier with a enhanced bitrate for Android and Google TV users. This is a feature that is exclusive to YouTube Premium members and delivers videos in extra crisp quality.
The new tier was first spotted earlier this year when the option showed up for several users. It turned out that the feature was being tested for selected iOS users, which is the operating system that Google chose as a playground for this and several other features.
At the time, this sparked rumors that YouTube had plans to lock 1080p playback to its premium subscribers. It turns out, as confirmed by Google, that this feature is simply a perk that is being offered for premium subscribers.

The 1080p Premium tier offers a higher bitrate than the standard 1080p option, which means that videos will play with a higher quality and less buffering. This is especially beneficial for users with high-speed internet connections and large TVs.

Now, it appears that the feature is finally moving on from iOS and propagating to Android and Google TV devices, as reported by 9to5Google based on posts on Reddit and Twitter. However, it also looks like this is only live for a few select users at the moment.
It is clear that this feature is another way in which Google can promote subscriptions to YouTube Premium. That service in particular underwent a significant increase last year on the price of its family plan, which I can only imagine prompted some cancellations.


The introduction of the 1080p Premium tier, and the fact that it is now being expanded beyond iOS, is a sign that YouTube is committed to providing its users with the best possible viewing experience. It remains to be seen whether the new tier will be successful, but it is a welcome addition to the YouTube lineup.


[ad_2]
Source link

This Side-Channel Attack Exploits SMS Delivery Reports To Retrieve Location

0
[ad_1]

SMS delivery reports not only let the sender know about the message receipt, but can also leak the recipient’s location. This is what researchers have demonstrated in their recent study, showing how receiving a silent SMS message triggers a side-channel attack, letting the sender deduce the recipient’s location via message timings.

Retrieving Location Data Via SMS Delivery Reports

Researchers from different universities teamed up to devise a novel side-channel attack, exposing users’ location via SMS.

According to the details shared in their research paper, the attack method involves exploiting the SMS delivery reports. Using the stats obtained from these message timings, a sender can determine the recipient’s location across different countries with up to 96% accuracy.

About the attack

This attack primarily involves exploiting the GSMA network’s underlying weaknesses that drive the SMS message technology. Since it typically affects GSMA, this side-channel attack impacts almost all cellular networks across the globe.

SMS enticed the researchers for this study, given its popularity among the masses as a 2G communication method, despite the presence of 3G and 4G communication alternatives. The researchers observed that the inevitable SMS Delivery Reports generated upon receiving an SMS message trigger a timing-attack vector.

If a sender has enabled SMS Delivery Reports, knowing the timings of message delivery and calculating the time lapse during message sending and receiving can help the sender determine the recipient’s location. Since SMS Delivery Reports feature works beyond the recipient’s control, the recipient user cannot prevent the malicious use of this feature.

The technique basically leverages the timing signatures for a certain location. An adversary can collect various timing signatures by sending SMS messages to the target user at different timings and locations. Analyzing them later can let the sender deduce the receiver’s location.

Conducting this attack merely requires the adversary to know the target user’s mobile phone number. While tedious, a careful collection and analysis of these timing signatures can even empower the adversary to determine a previously unknown or new location of the target user. This works regardless of whether the user is in a domestic location or overseas. The time lapse between SMS sending and delivery can help here.

Attack Limitations And Countermeasures

While the researchers achieved much accuracy while performing this side-channel attack, it still has some limitations. That’s because numerous factors may impact the empirical measurements in a real-world exploit. Nonetheless, the yet-achievable >90% accuracy, even in a closed-world scenario, still poses a privacy threat.

Regarding the countermeasures, the researchers explained that the existing countermeasures to prevent related attacks do not apply on this novel side-channel attack. To tackle UE processing delays, possible countermeasures include not sending Delivery Reports or manipulating them with a random delay.

As for the network-based delays, altering SMS timings, deploying spamming filters on the core network, or at least disabling silent messages can help minimize the potentialities of such attacks. Nonetheless, disabling the delivery reports feature can be the only viable countermeasure.

Before making this study public, the researchers responsibly disclosed the matter to the GSMA. In turn, GSMA acknowledged their findings (identified as CVD-2023-0072) and considered numerous countermeasures.

Let us know your thoughts in the comments.


[ad_2]
Source link

June update widely available for Galaxy Note 20, Fold 3 & more

0
[ad_1]

Samsung is widely rolling out the June 2023 security update to the Galaxy Z Fold 3, Galaxy Z Flip 3, Galaxy Note 20 series, and Galaxy S21 FE. The latest monthly Android security patch is also available for the Galaxy A71 5G in some markets. This month’s SMR (Security Maintenance Release) contains more than 60 vulnerability patches.

The Galaxy Z Fold 3 and Galaxy Z Flip 3 foldables started receiving the June SMR last week. Samsung initially released the update for the US versions of the devices, with both carrier-locked and unlocked units getting it simultaneously. In recent days, the Korean firm has expanded the rollout to its homeland South Korea as well as a few other markets. The Fold model is getting the update in the UK while the Flip model is picking it up in the UK, Brazil, and Argentina.

If you’re using the Galaxy Z Fold 3 or Galaxy Z Flip 3 in any of these markets, watch out for new updates with firmware build numbers F926BXXU4EWF1 or F711BXXU5EWF1, respectively. Samsung’s official changelogs state that the foldables are getting some system stability improvements along with this month’s security fixes. For users in South Korea, the update brings improvements to Safety and Emergency features as well. The build numbers are F926NKSU2FWE8 and F711NKSU3FWE8, respectively.

Samsung’s June update for the Galaxy Note 20 series was also initially released in the US. The N0te phones were the first to pick up the June SMR globally. The Korean behemoth is now rolling out the update to the devices in more markets, including South Korea, Europe, and Latin America. The new build number for the former market is N98*NKSU2HWE8, while that for the latter two is N98*BXXU7HWF3. The changelogs are pretty much the same as that for the 2021 foldables, including the Safety and Emergency improvements in South Korea.

Samsung’s June update is reaching more Galaxy devices around the world

The story is the same for the Galaxy S21 FE as well. The device initially received the June SMR in the US. Samsung is now rolling out the update globally. Meanwhile, the rollout for the Galaxy A71 5G has just begun. The new security patch for this mid-range phone is currently only available in the UAE, SamMobile reports. The updated firmware build number is A716BXXU8FWE1. Samsung isn’t pushing any major new features or improvements to the device with the June update. A wider rollout of the June SMR for the Galaxy A71 5G should be just around the corner.


[ad_2]
Source link

Biden administration announces $930 million in grants to expand internet access

0
[ad_1]

For people living in cities and suburban areas, high-speed internet became common a few years back. However, the same thing cannot be said for the people living in rural areas, for whom, even in this digital age, high-speed and reliable internet is still a luxury. Now, in an effort to solve this digital divide, the Biden administration has recently announced the allocation of $930 million in grants to enhance broadband internet access in rural areas.

These grants are part of the Department of Commerce’s “Enabling Middle Mile Broadband Infrastructure Program” and will enable companies to deploy over 12,000 miles of new fiber optic cable across 35 states and Puerto Rico, thus addressing the disparities in areas such as education, employment, healthcare, and social engagement. Additionally, the Biden administration expects grant recipients to contribute an additional $848.46 million, effectively doubling the program’s impact.

Commerce Secretary Gina Raimondo has applauded this new initiative, stating, “Much like how the interstate highway system connected every community in America to regional and national systems of highways, this program will help us connect communities across the country to regional and national networks that provide quality, affordable high-speed internet access.”

Benefits of the new initiative

It’s no secret that high-speed and affordable internet would be a lifeline for students and educators, enabling remote learning, access to online resources, and virtual collaboration. It would also create new opportunities for remote work, granting individuals the flexibility to pursue employment regardless of their geographic location. Furthermore, high-speed internet would enable telemedicine, allowing people to communicate with doctors in big cities.

The White House is Aiming for Success

To ensure the success of the program, the Biden administration has already partnered with 20 prominent internet service providers, including Verizon, Spectrum, AT&T, and Optimum, who are offering high-speed internet access for $30 or less per month. Moreover, qualifying households will have the opportunity to access the service at no cost.

Among the grant recipients, one Alaska-based telecommunications company received a substantial $89 million pledge to establish fiber-optic networks in areas where 55% of residents currently lack internet access. Similarly, a California company will receive a grant of $73 million, while a Michigan-based telecom company will receive $61 million. However, it is important to note that each company will have five years to fulfill their promises.


[ad_2]
Source link

Data Breach at New BreachForums: 4,000 members’ data leaked

0
[ad_1]

BreachForums disclosed that the data breach was carried out by a rival hacker forum, which exploited a zero-day vulnerability in MyBB, the free and open source forum software.

In a recent exclusive report by Hackread.com, it was revealed that BreachForums has made a comeback under the control of the notorious ShinyHunters hackers, who are collaborating with the original moderator team from the original BreachForums.

This comes after the old forum was seized by the FBI and its alleged owner, PomPomPurin (real name: Conor Brian Fitzpatrick), was arrested in New York. Fitzpatrick was arrested by a team of investigators at his home in Peekskill, New York and charged with a single count of conspiracy to commit access device fraud.

Now, the revived forum has fallen victim to data breach, resulting in the exposure of personal information belonging to more than 4,000 registered members. Initially, the identity and motives of the hackers behind this breach were unclear, given the complex dynamics involving security agencies and the past and current administrations of BreachForums.

Hackers vs. Hackers

However, during a communication on Telegram, one of the forum’s administrators known as “Weep” confirmed the occurrence of a cyber attack. Weep addressed the members of BreachForums and attributed the data breach to a rival forum called OnniForums, which prides itself as a dark web forum focused on security and anonymity.

Weep urged the forum members to reset their passwords and disclosed that the breach was facilitated by exploiting a zero-day vulnerability in MyBB. It is important to note that the BreachForums had been offline since the early morning of Monday, June 19th, 2023, but at the time of writing, the forum was back online.

Meanwhile, tweets allegedly from the official Twitter account of OnniForums have claimed responsibility for the attack. Another tweet from the same forum’s handle asserts their involvement in breaching another hacker forum known as “Exposed.” Notably, in May 2022, a partial database containing details of 460,000 members from the now-seized RaidForums was leaked on ExposedForum.

Data Breach at New BreachForums: 4,000 members' data leaked
On left, BreachForums admin Week addressing the members – On right, OnniForum claiming the breach (Image: Hackread.com)

The Leaked Data

While uncertainties persist, initial analysis suggests the authenticity of the leaked data. The compromised information includes the following:

  • Login keys
  • Usernames
  • Email addresses
  • IP addresses
  • Password hashes
  • Registration dates
  • Members’ last visits and posts.
  • Number of posts and, last activity
  • Social media handles with profile links and more.

BreachForums, notorious for its role in facilitating discussions and trade of stolen data, has once again become a focal point for cybersecurity concerns. The return of the forum, coupled with this recent breach, underscores the ongoing challenges faced by online communities in safeguarding user information and preventing unauthorized access.

Data Breach at New BreachForums: 4,000 members' data leaked
Emails, IP address and other data analysed by Hackread.com

Impact

If the personal data of cybercriminals is leaked online, it can have several potential outcomes. First and foremost, their identities and activities may be exposed to law enforcement agencies, making it easier for authorities to track and apprehend them. This can significantly impede their ability to continue engaging in illegal activities anonymously.

Furthermore, their reputation within the cybercriminal community may be tarnished, resulting in diminished trust and collaboration with other hackers. The leaked data could also provide valuable insights and intelligence to cybersecurity professionals, allowing them to better understand cybercriminal tactics and develop stronger defence mechanisms.

Overall, the leakage of personal data belonging to cybercriminals can have a substantial impact on their operations and make it more difficult for them to operate clandestinely.

  1. Nulled.IO Hacking Forum Hacked, Trove of Data Stolen
  2. Russian hacking forums warming up to Chinese hackers
  3. US Marshals Service Data Sold on Russian Hacker Forum
  4. BidenCash Market Leaks 2M Credit Cards in Birthday Blitz
  5. OGUsers hacker forum hacked for 4th time; database leaked

[ad_2]
Source link

YouTube is expanding its 1080p Premium quality

0
[ad_1]

A little while back, YouTube got a lot of flack for reportedly making 4K resolution a premium-exclusive perk. While the company has since rolled back that change, it’s still introducing a video quality setting only for premium subscribers. YouTube is expanding its 1080p premium video quality setting to Android TV and Google TV.

This doesn’t mean that YouTube is going to make the 1080p quality setting exclusive to premium subscribers. Instead, the company is going to offer a higher-quality version of 1080p with a higher bit rate.

YouTube is expanding its 1080p Premium quality to Google TV and Android TV

The news that YouTube’s testing this quality isn’t new. The company has been testing this video quality on iOS and on Apple TV. It didn’t get as much traction as the 4K debacle, and it seems to be more widely accepted.

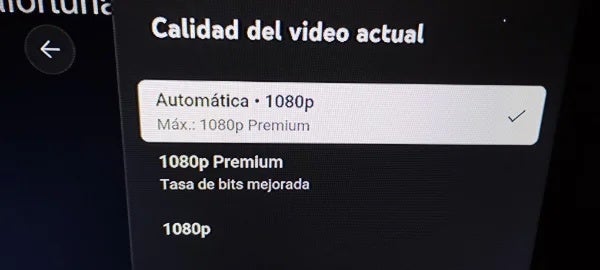
According to 9To5Google, Google TV and Android TV users are seeing the new video quality option on their devices. Some of these users posted screenshots of the new option. Instead of replacing the regular 1080p options, it will sit right above it.

One example shows the option on a TV, and the other one is, allegedly, from a Motorola smartphone. This points to this feature nearing an official release.

At this point, we don’t know just when the company is going to release this feature to the public. In any case, we know that it’s going to be much better received than locking the 4K quality behind the paywall. That caused a ton of YouTube watchers to become upset.

We’re familiar with YouTube bringing certain premium features and putting them behind the paywall, but 4K video quality is something that people have had access to for a long time. Reaching in and taking away a feature that we’ve been freely enjoying wasn’t going to go over well.


[ad_2]
Source link

YouTube TV’s Zen Breaks are now Full of Ads

0
[ad_1]

One way that YouTube TV really differentiates itself from its competitors, is by injecting these “Zen Breaks”. While you’re watching live TV, during a commercial break, you’ll sometimes see a Zen break. Which will play some calming nature sounds for a few seconds, or longer, depending on the ad break.

It was a really cool feature, but as Reddit users are starting to notice, YouTube TV is now turning them into ads. So the ad-free Zen break is now an ad. Kind of ironic.

According to Reddit, users are seeing things like “This break brought to you by Progressive”, among other sponsors. From what we’re seeing, this is not audio, just text over the screen. So if you’re not really paying attention – maybe on your phone during the ad-break – you probably won’t see it.

It’s an ad, but less of an ad

Typically, for an hour of live TV, you’ll have to sit through almost 20 minutes of ads. That’s nearly a third of your time. So naturally, we’ve all become a bit annoyed with the number of ads and commercials we see. And this ad from the Zen Break is still an ad, but it’s one that you’re more likely to be less annoyed by.

Since it is not (yet) interrupting your moment of Zen, it’s just some text on the screen. It’s not as bad as some of the ads you’ll see on Hulu or even Netflix, thankfully.

Now, yes, it is quite annoying to be seeing more ads on a service that you already pay at least $72.99 per month for. But don’t forget that Cable costs even more than that. A comparable package is around $120, without the other fees like the sports fee and equipment fee. And you’ll see just as many ads if not more there, due to the Zen breaks not being included in Comcast or Spectrum.

On the other hand, these sponsored Zen Breaks could be used to help offset some of the price hikes that YouTube TV might have otherwise needed to add. Now while it has doubled in the last number of years, YouTube TV is still an incredible value for what you get.

YouTube TV Zen Mode sponsored


[ad_2]
Source link