Google Wallet app goes through another design change with the same functionality

0
[ad_1]
Google Wallet is getting a new, more compact design that will make it easier to navigate. The new design will do away with some unnecessary white space and images, and present payment methods and loyalty cards in a more streamlined manner.
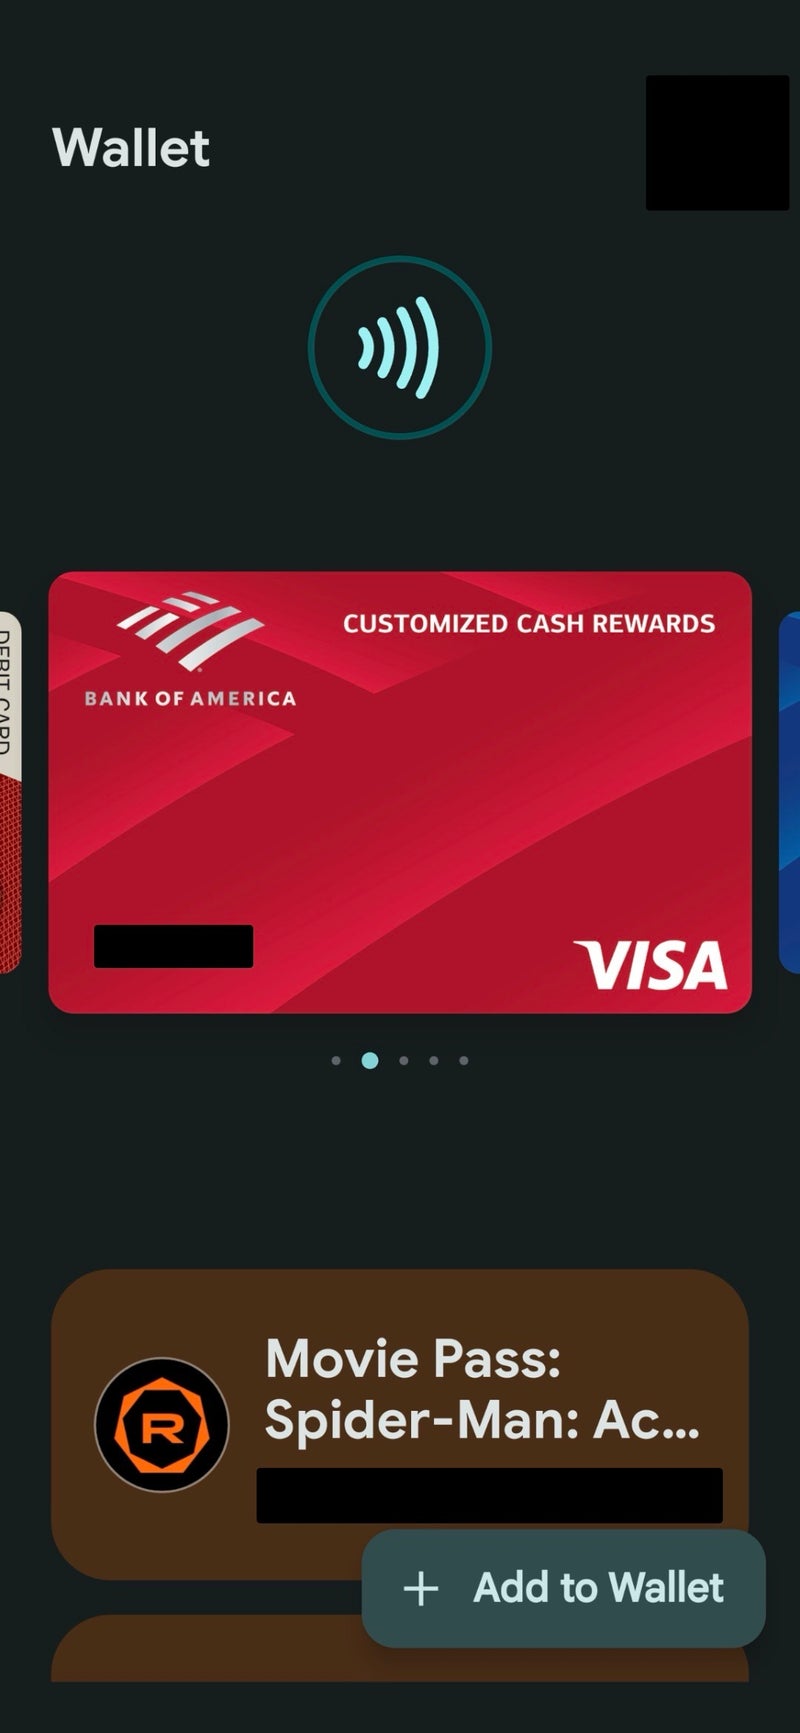
As reported by 9to5Google, this current redesign has been spotted on version 2.193.x of the Google Wallet app, but it has not yet rolled out to everyone running this version. Although not a huge difference as far as the UI is concerned, the subtle differences can be seen when compared side by side with the old design.
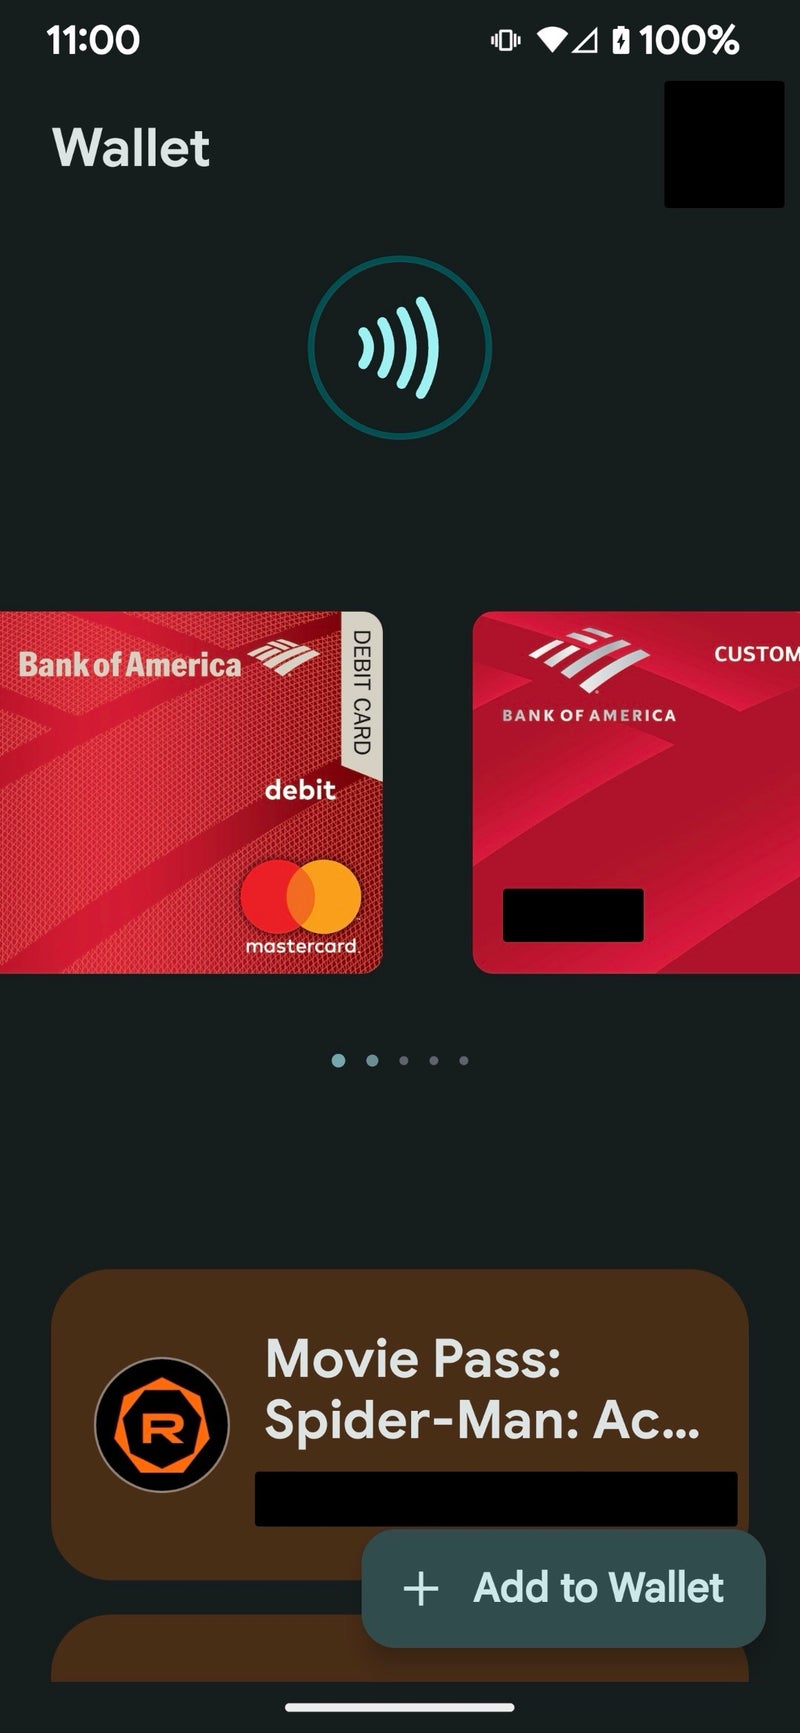
The first noticeable change is the removal of the NFC logo and animation at the top. This removal has allowed for the carrousel of payment cards to be moved up in position, showing them front and center as soon as you open the app.
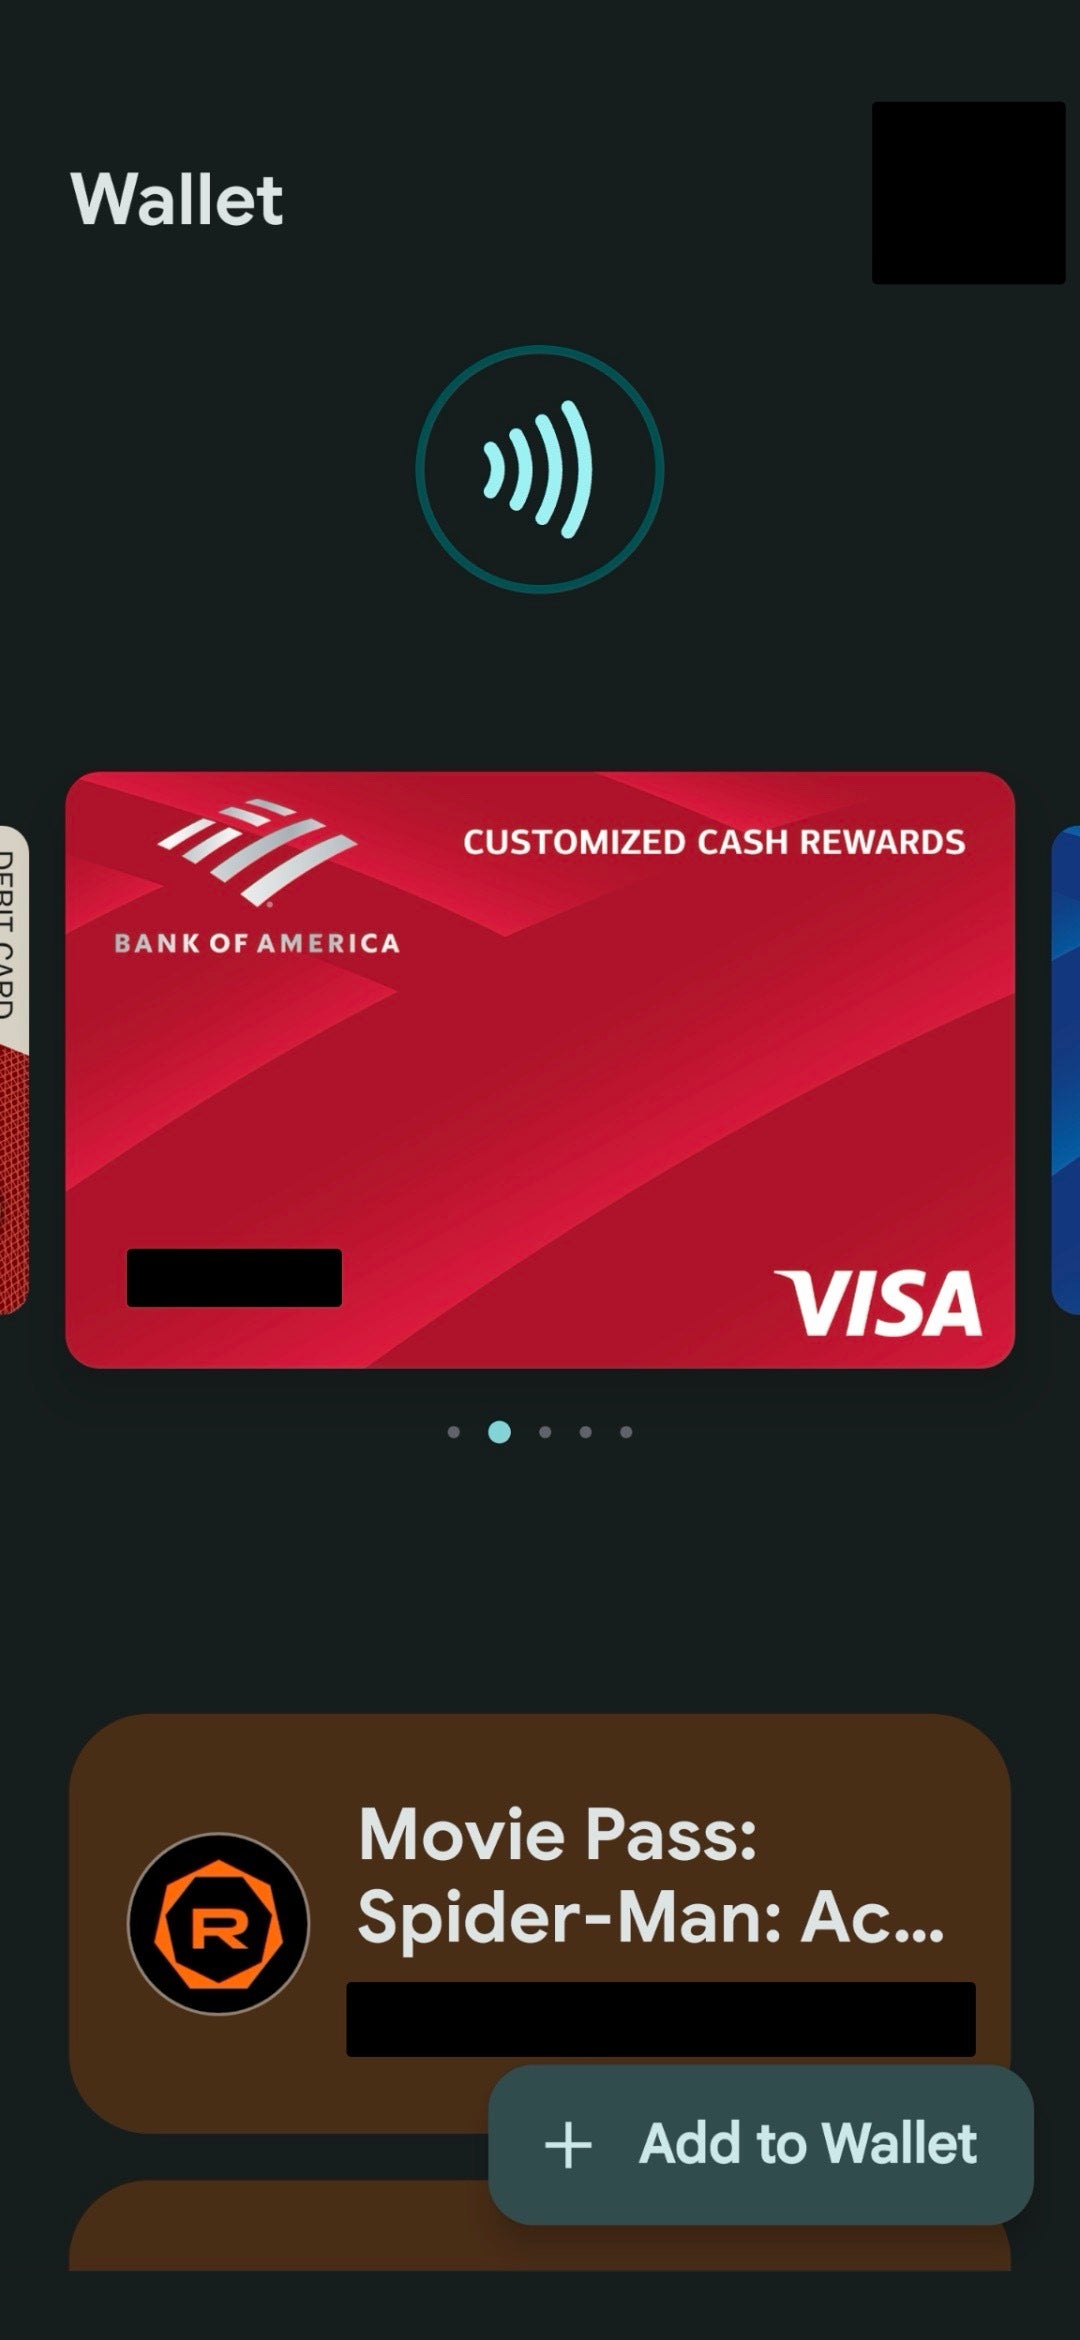
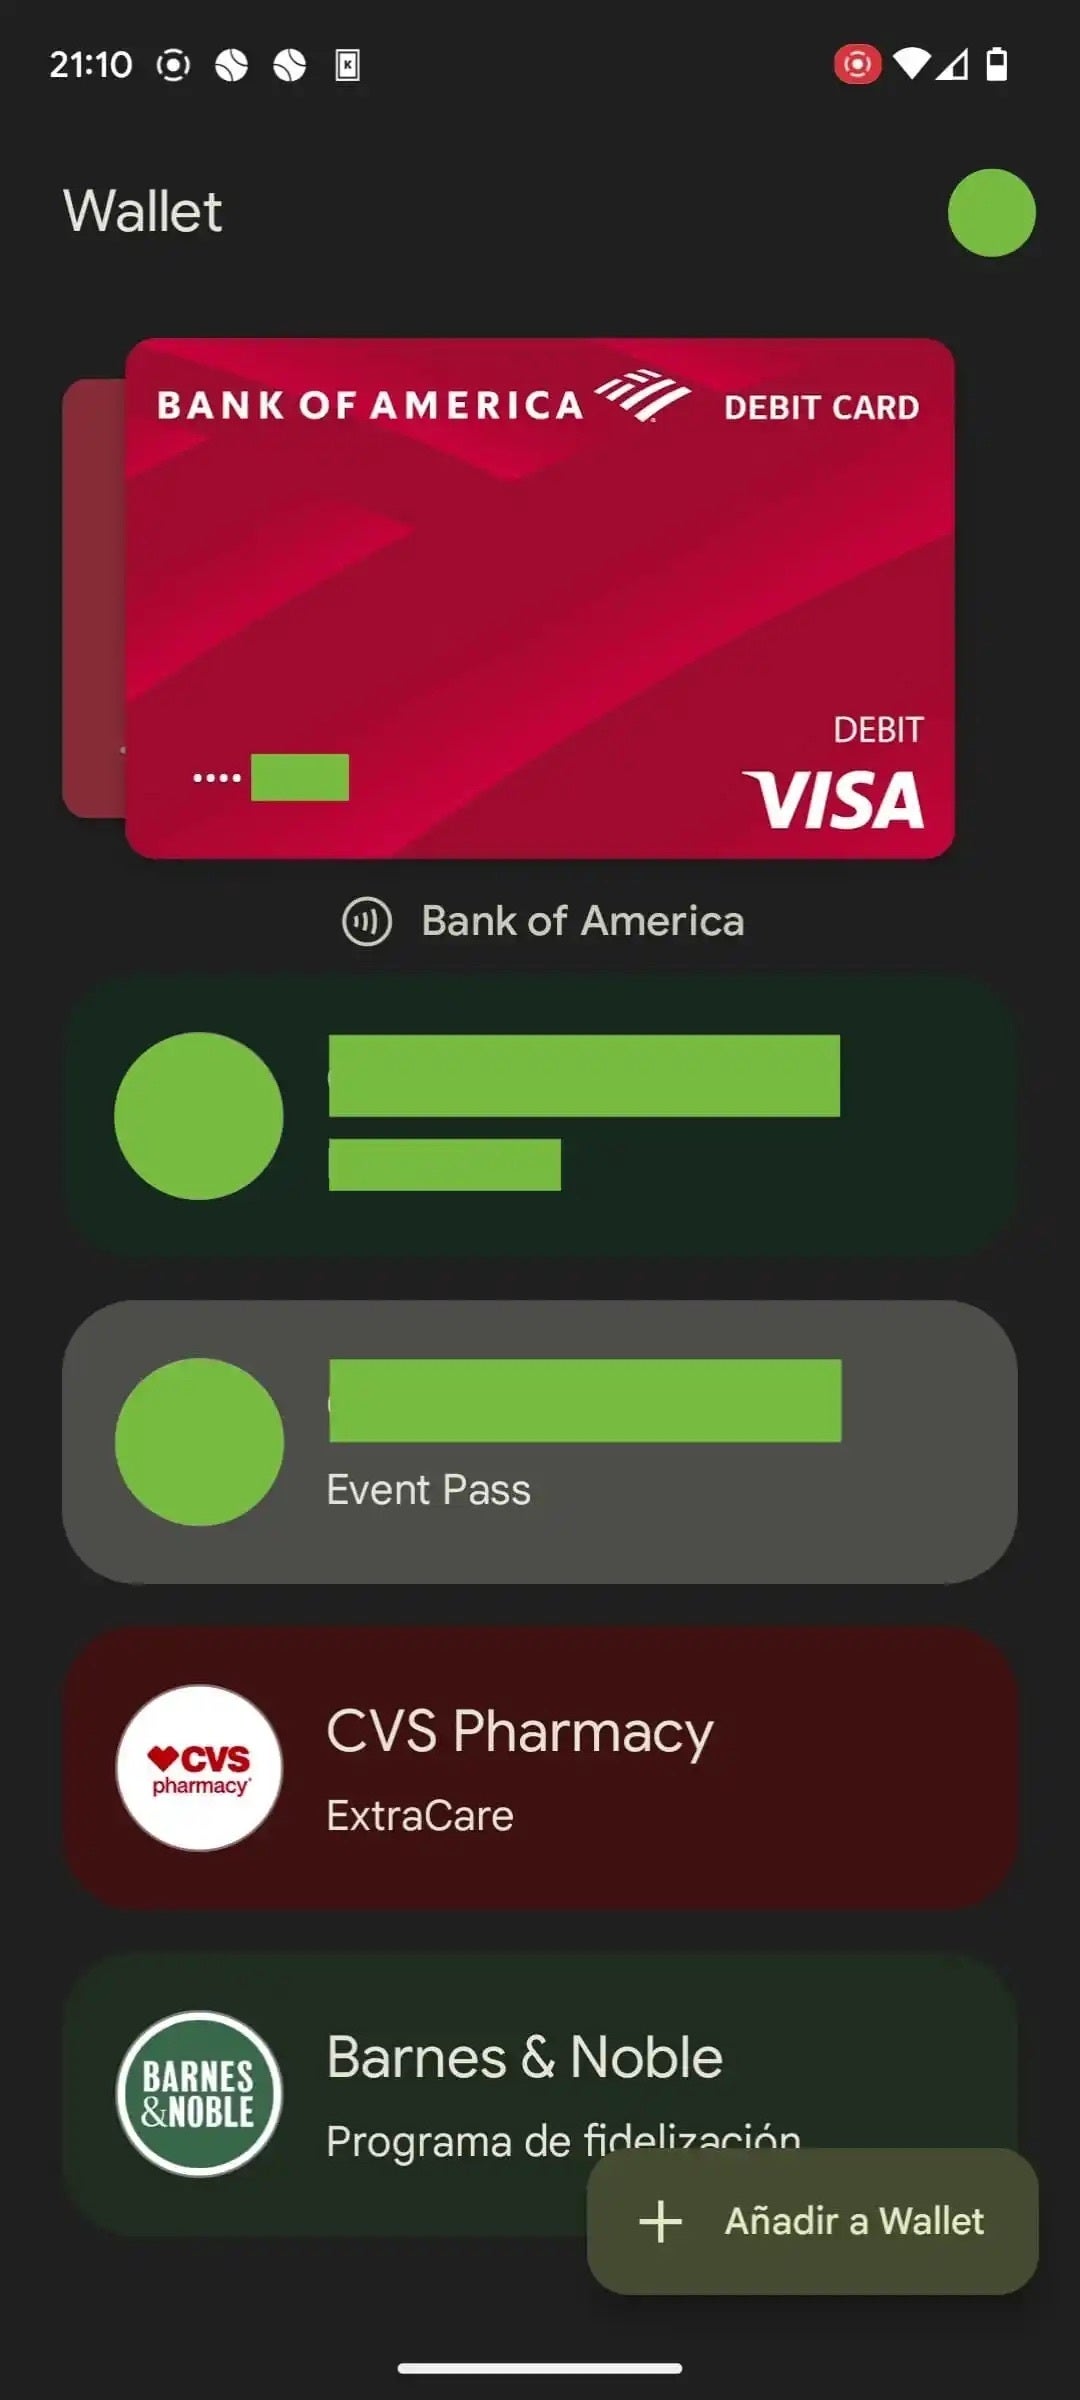
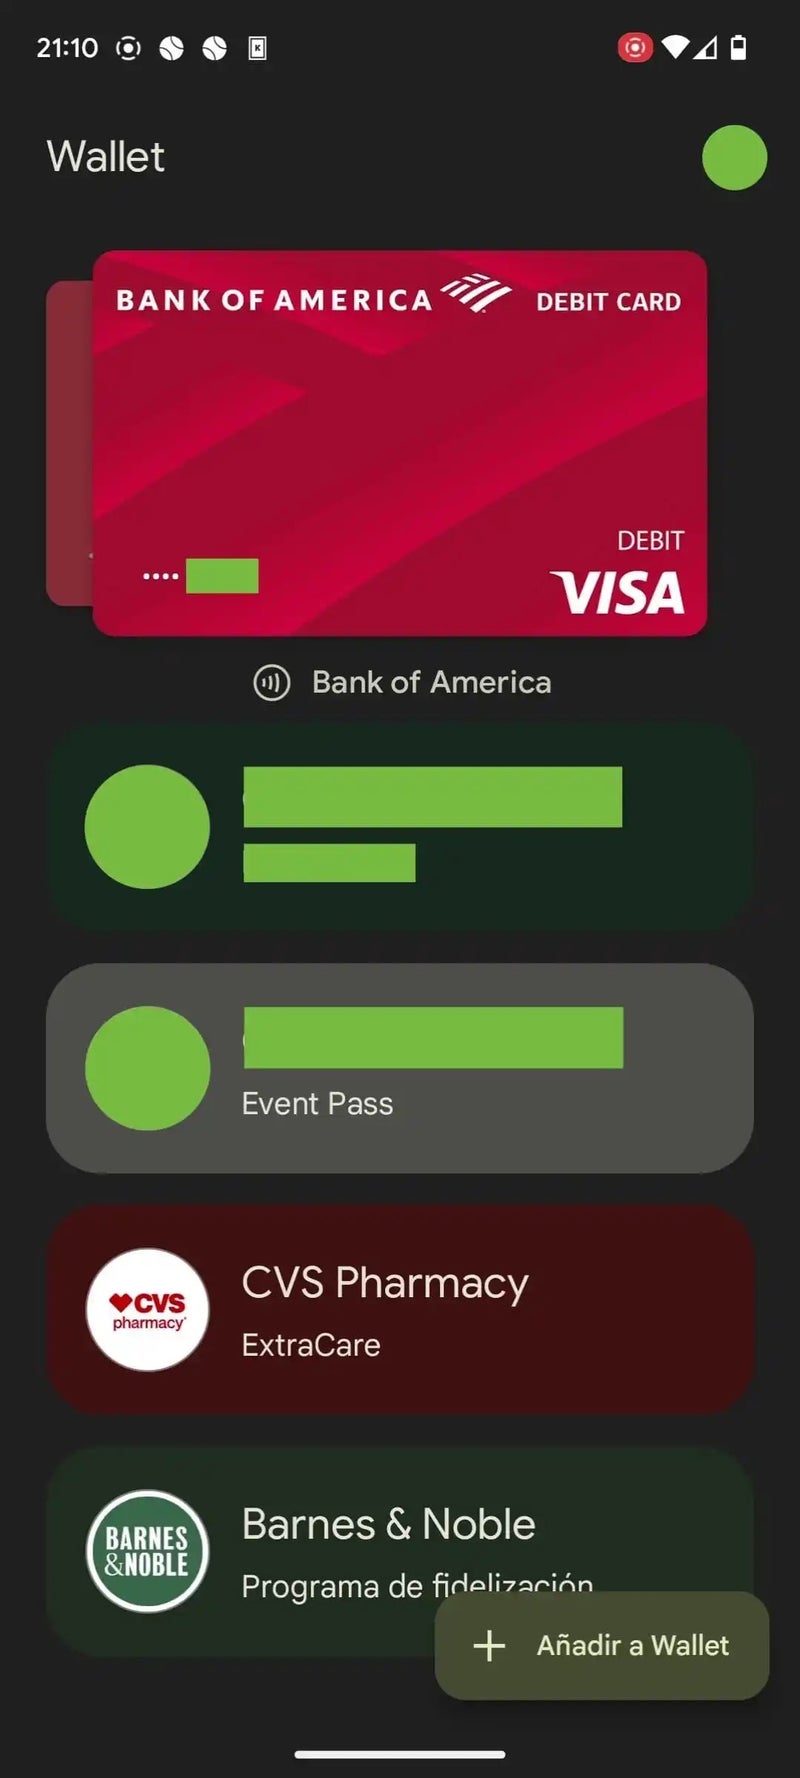
Old Design (Image via Phone Arena) vs Redesign (Image via 9to5Google)

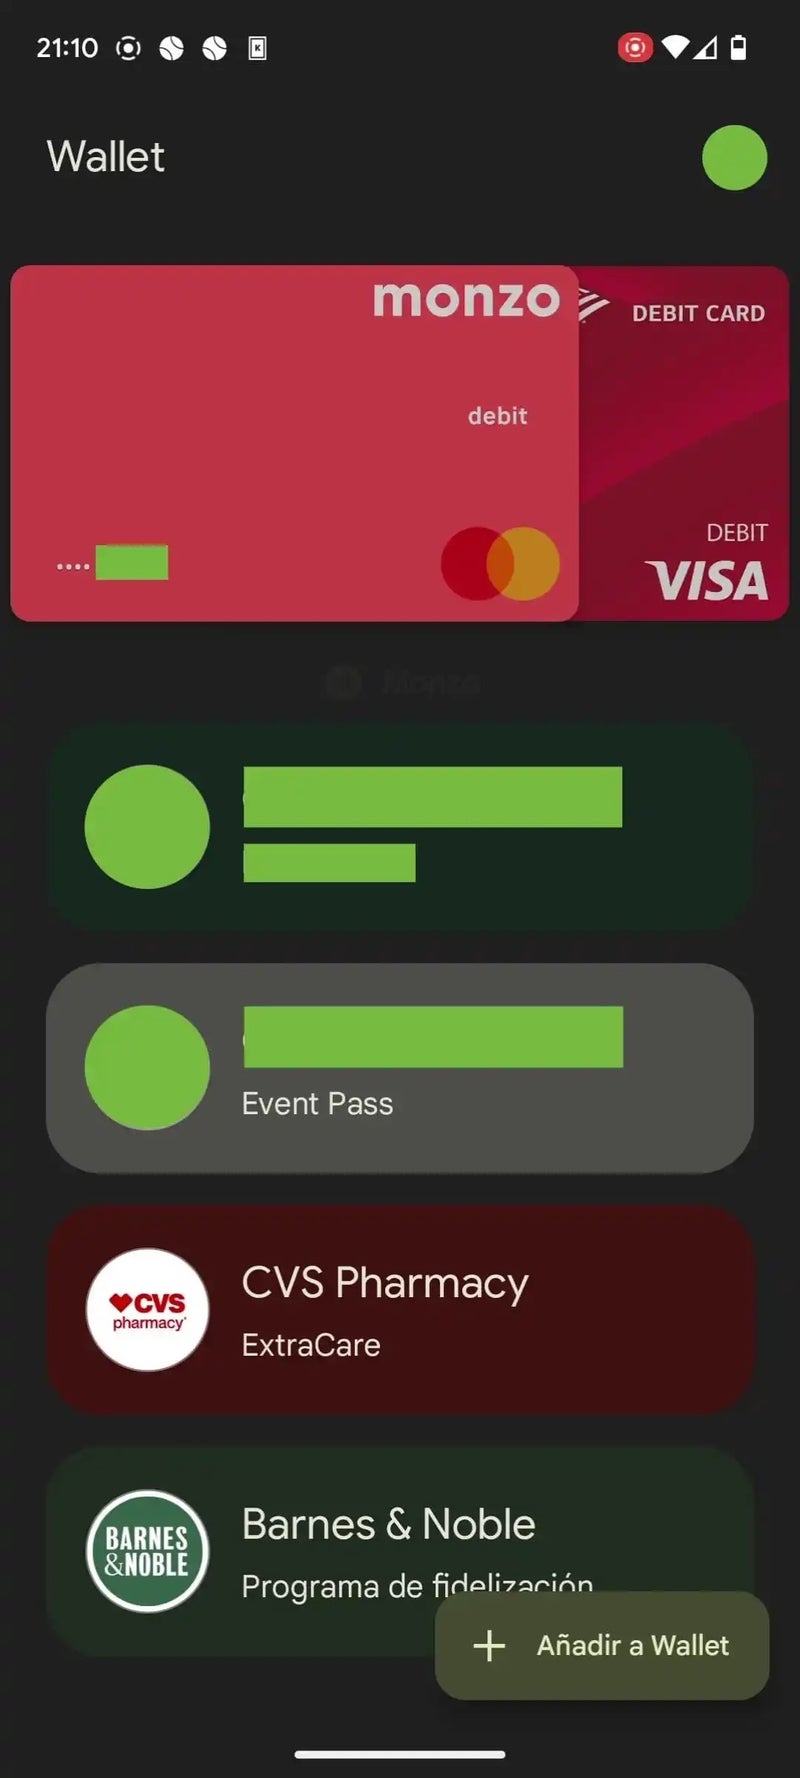
In addition, the carrousel of payment cards now display the cards behind one another, so you can clearly see at a glance the cards you have added. This is in contrast to the old design, which had the cards shown side by side and the amount of cards left to sift through represented by dots underneath. Said dots are now also gone and replaced with the name of the cards you are currently looking at, preceded by a small NFC logo.
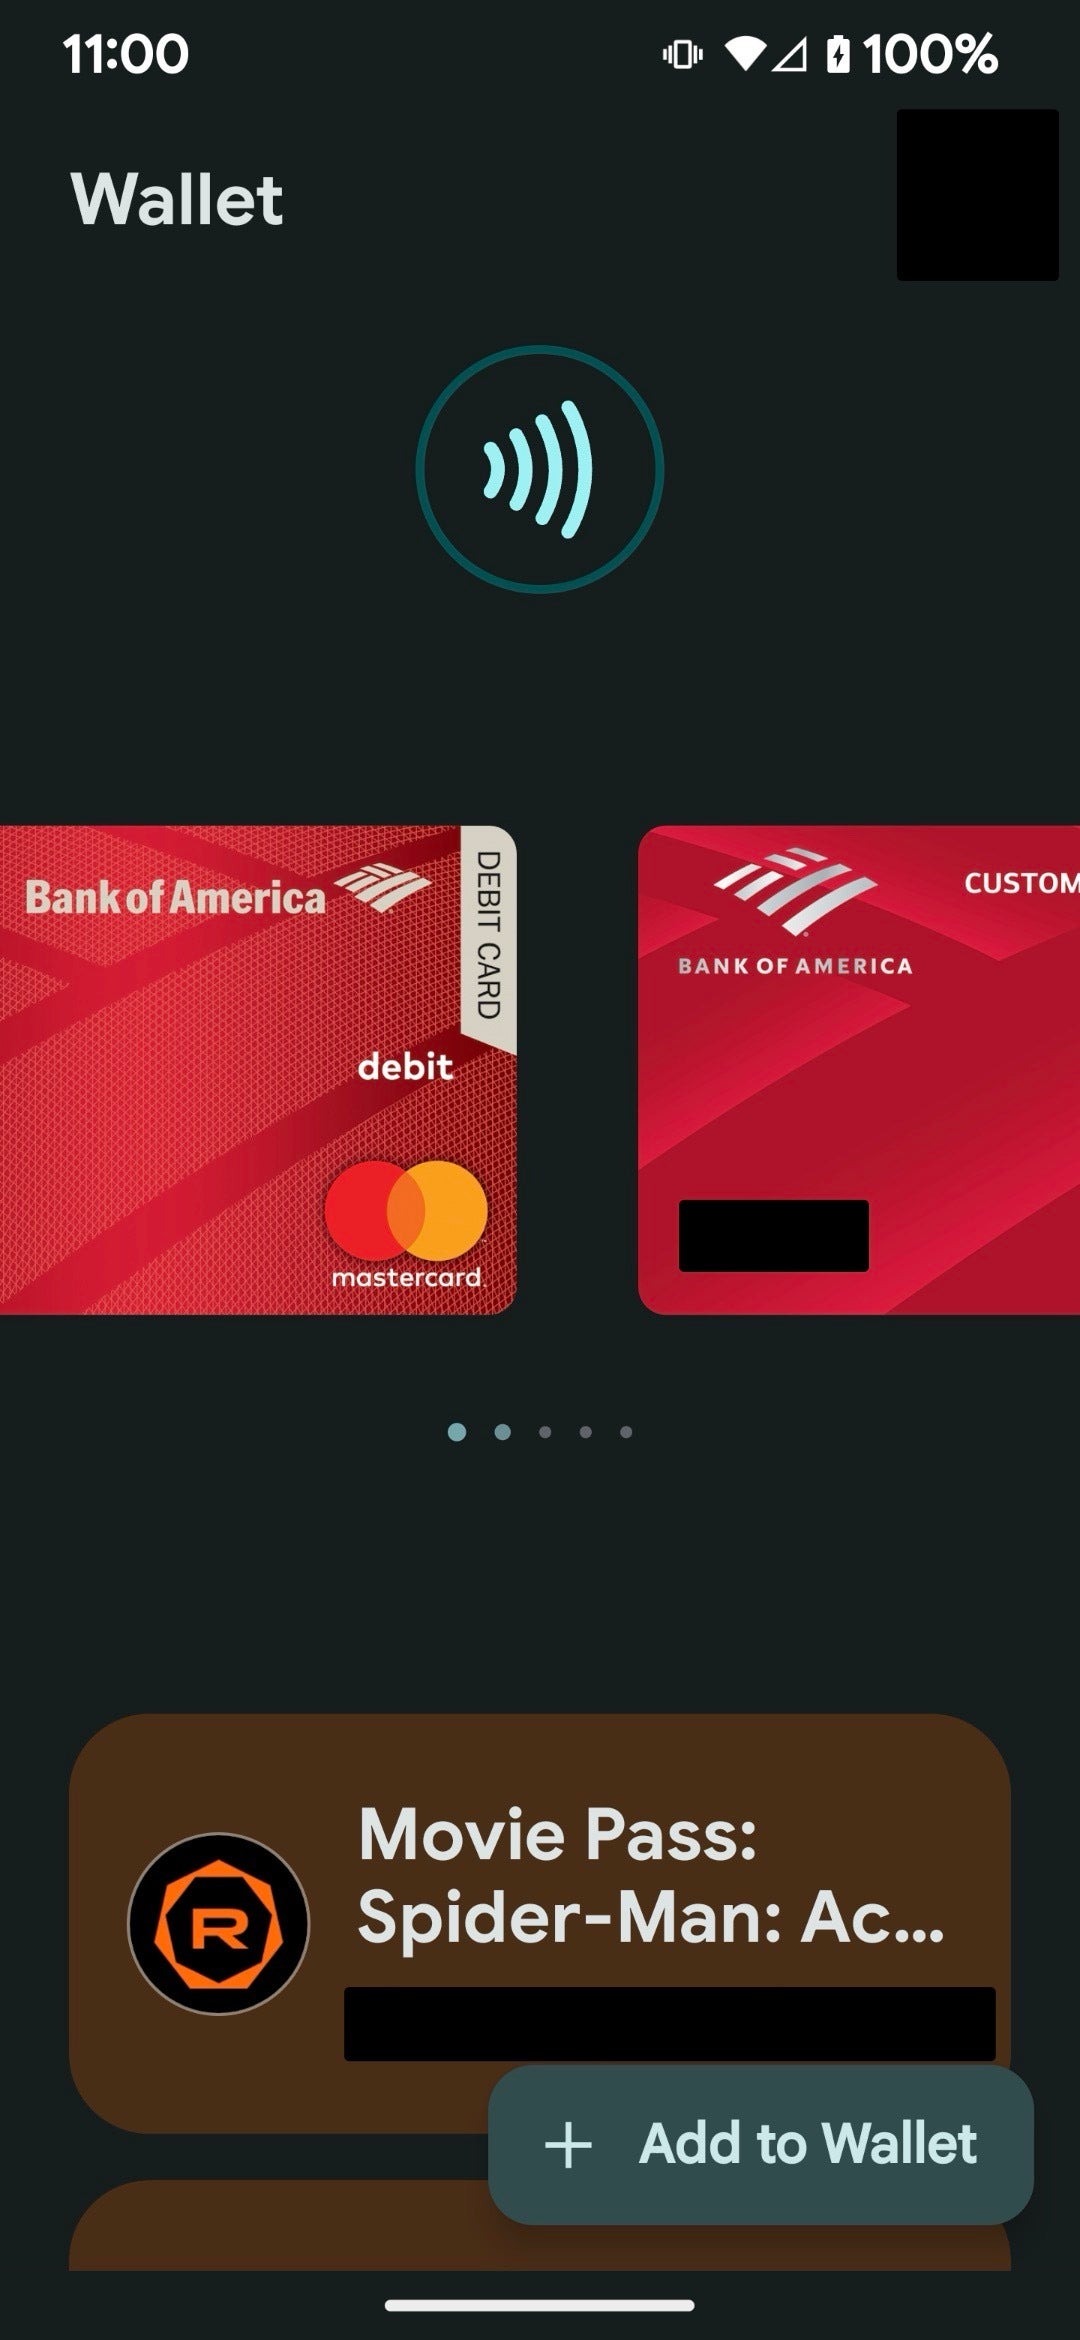
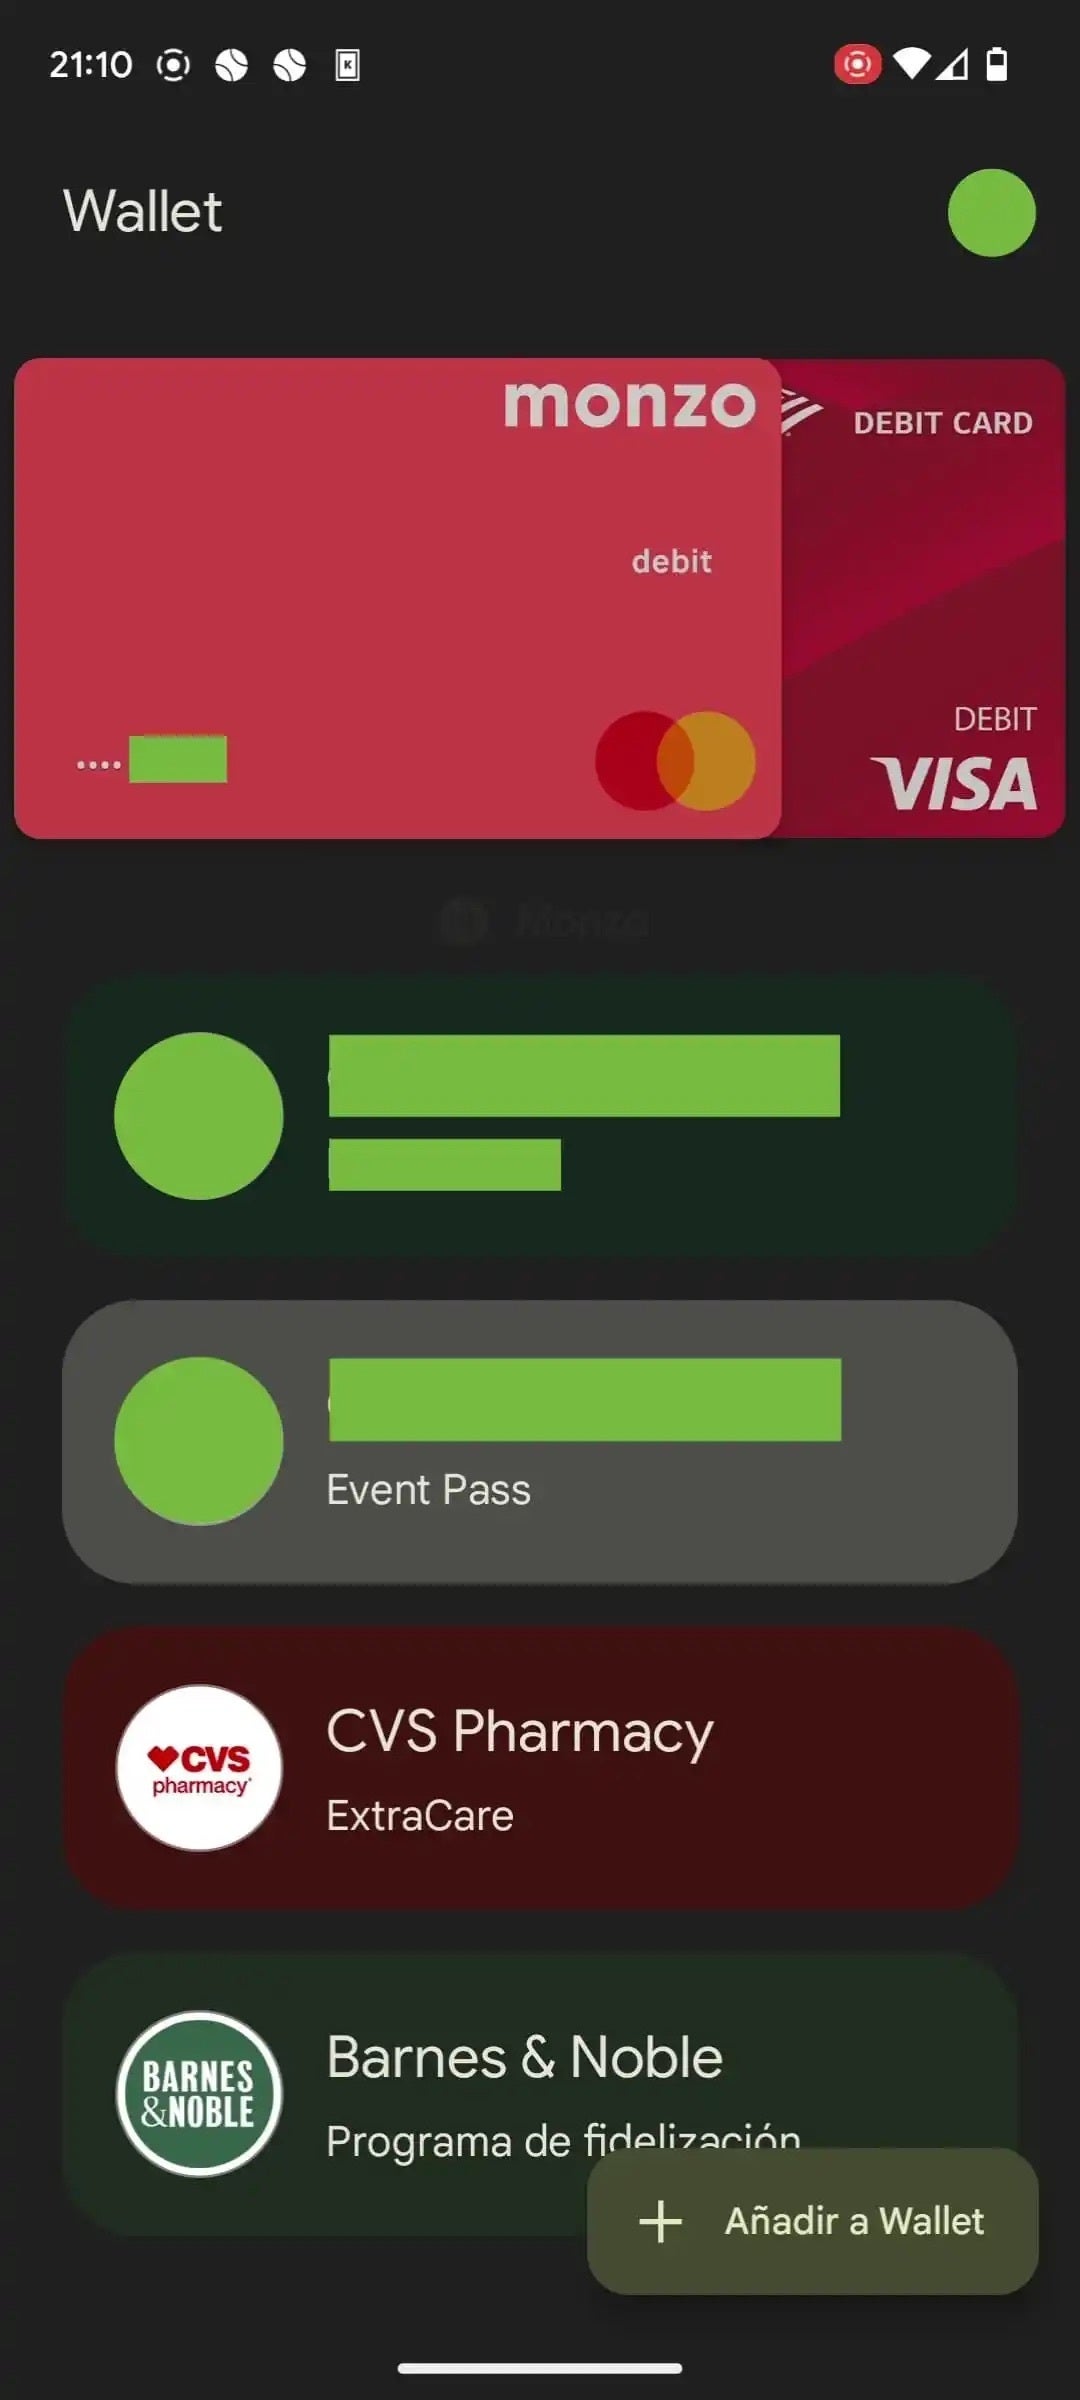
Old Design (Image via Phone Arena) vs Redesign (Image via 9to5Google)

Some smaller design tweaks also seen are the removal of unnecessary spacing between the payment cards carrousel and the list of loyalty cards. This will allow for more loyalty cards to be seen at a time, instead of having to do more scrolling to find them.
This isn’t the first redesign, or rebranding for that matter, that Google Wallet has gone through. Google reimagined and revived Google Wallet last year, causing tons of confusion in regards to what the difference was between this app and Google Pay as we knew it. Fortunately, it looks this time like Google Wallet in its current form is here to stay (for now) but will continue evolving with more design and functional tweaks.

[ad_2]
Source link
Google Wallet redesign makes it feel less empty

0
[ad_1]

Google Wallet is the company’s main payment platform, and the app comes with all the Material You flair that you’d expect. Thus, the app has a ton of empty space. Well, it looks like Google acknowledges this and it’s making some changes. The company is going to push a new redesign to Google Wallet that will get rid of the empty space.

Google Wallet is looking to replace the leather wallet in your pocket. You’re able to load a plethora of different cards onto your account so that you can easily use the app instead of taking out your wallet. People can load their credit/debit cards, rewards cards, gift cards, and more into the app.

Currently, Google is trying to push the ability to add legitimate forms of identification to your wallet. This means that people could be able to add their driver’s license, I.D., and passports to their accounts. This is in testing in a few states at the moment, so you can’t do it just yet.

Google Wallet just got a new redesign that gets rid of the empty space

The Google Wallet app, as it is now, is pretty simple and almost minimalistic. When you open the app, you’re greeted with a pretty barren sight with your profile picture up top, a large NFC logo, a carousel of your cards, your rewards cards, and the Add to Wallet button on the bottom.

There’s an ocean of space between all of these elements which, while it gives the UI a clean look to it, means that there’s a lot of wasted space.

Well, according to 9To5Google, the app is getting a facelift that will solve this issue. We have some screenshots of what the app is going to look like after the redesign.

google wallet redesign

Looking at the screenshot provided, we will see that just like in the current version, your profile picture is still going to be on the top right of the interface. However, there will be no NFC logo. Your profile picture will immediately be followed by your credit cards. Immediately under your credit cards, you will see the name of the company that issued it.

Right under your cards, you will see your list of rewards cards and gift cards. The list will be pretty tight with not much space in between them. While this redesign does change the overall look of the app, it will still retain the Material You aesthetic.

This is a good move on Google’s part, as there’s more information displayed on the screen. So, you’ll be spending less time searching through your cards while at the cashier. It just makes things easier and more convenient.


[ad_2]
Source link

Hybrid Meta-Optics technology could revolutionize smartphone photography

0
[ad_1]

It’s no secret that over the past few years, smartphone cameras have remained largely unchanged due to the constraints of housing all the components in a thin smartphone body. However, all this could change in the near future as scientists have now unveiled a new hybrid meta-optics technology that enables smartphone users to capture high-grade photos without the bulkiness of traditional cameras.

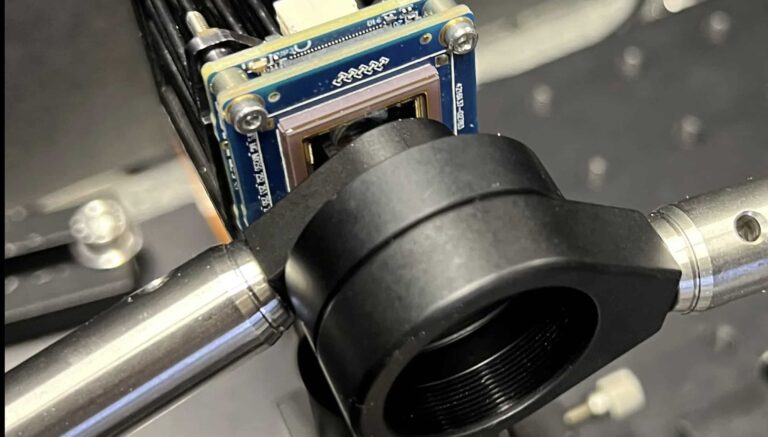
Similar to professional-grade cameras that use interchangeable lenses, this new technology utilizes flat optics made from meta structures to manipulate light and capture high-quality images while maintaining a compact form factor. This approach not only solves the limitation of smartphones relying on multiple cameras for different focal lengths but also reduces the need for excessive processing, thus resulting in a more natural output.

Addressing the challenges

While the concept of using meta-material-based optics seems straightforward, researchers encountered significant challenges in modelling the complex interactions between light and various optical components, which consequently resulted in the designs falling short of the desired image quality according to conventional standards.

However, to overcome these issues, researchers adopted the “hardware-in-loop strategy” and conducted experiments using physical lenses and sensors, thus significantly reducing memory demands while improving overall performance.

Following the changes, the team was able to produce images comparable to those taken with Sony’s flagship offering, the Sony Alpha 1 III, paired with an 85mm f/1.8 lens. Furthermore, the total volume of the hybrid meta-optics system was less than 1% of the size of the Sony setup, making this innovation even more impressive.

Looking ahead

Vladimir Katkovnik, a senior research fellow at Tampere University in Finland and co-author of the study, emphasized the importance of this innovation and its potential applications. He highlighted the usefulness of this technology in developing a new generation of customized smartphone cameras, particularly in fields such as biomedicine.

Moreover, the team also believes that this hybrid meta-optics technology could be integrated into regular smartphones, bringing us closer to a future where smartphone photos rival those captured by DSLR cameras.


[ad_2]
Source link

Layer 7 DDoS Attacks on Microsoft

0
[ad_1]
Microsoft Confirms Hacking

Recently, it’s been confirmed by Microsoft that the current outage problems experienced by the following services of Microsoft were due to intentional Layer 7 DDoS attacks:-

The credit for the attacks goes to a threat actor called Storm-1359 (aka Anonymous Sudan), as per Microsoft’s findings.

Microsoft observed a rise in web traffic targeting specific services starting in early June 2023, resulting in temporary availability issues.

Without any delay, Microsoft instantly started monitoring the ongoing DDoS attacks thoroughly by launching a quick investigation.

Layer 7 DDoS Attacks

Rather than targeting layer 3 or layer 4, the recent DDoS attacks have primarily targeted layer 7.

OSI Layers

To enhance customer protection against similar DDoS attacks, Microsoft strengthened layer 7 defenses by optimizing Azure Web Application Firewall (WAF).

Microsoft discovered that Storm-1359 could use different cloud services and open proxies to launch DDoS attacks using several botnets and tools.

Moreover, here below, we have mentioned the main focuses of Storm-1359:-

  • Causing disruptions
  • Attracting public attention

In a report published recently, Microsoft provided an introductory analysis of the root cause, suggesting DDoS attacks as the potential reason behind the Azure outage, highlighting a noticeable surge in network traffic.

In a Layer 7 DDoS attack, threat actors specifically direct their efforts towards the application level, aiming to overload services by flooding them with excessive requests.

This huge flood of requests overwhelms the services, causing them to become unresponsive since they cannot handle the load.

The threat actors employ multiple DDoS methods to overpower a web service, exhausting its connection pool and causing it to accept new requests.

Types of DDoS Attack Traffic

Here below, we have mentioned all the types of layer 7 DDoS attack traffic:-

  • HTTP(S) flood attack
  • Cache bypass
  • Slowloris

Recommendations

Here below, we have mentioned all the recommendations offered by Microsoft:-

  • To protect web apps, make sure to use layer 7 protection services like Azure Web Application Firewall (WAF).
  • Stay protected against known bad bots by implementing the bot protection managed rule set.
  • Make sure to block the IP addresses and ranges that you identify as malicious.
  • Unknown and suspicious traffic should be blocked.
  • To block and limit the HTTP or HTTPS attacks automatically that have known signatures, create custom WAF rules.

Looking For an All-in-One Multi-OS Patch Management Platform – Try Patch Manager Plus


[ad_2]
Source link

New Malware targets WhatsApp Backups, steals sensitive data

0
[ad_1]

Another day, another malware scare. This time, it’s targeting WhatsApp backups as well as some other sensitive data.

It comes from a hacking group called SpaceCobra, who has developed an instant messaging app, which is able to steal a lot of sensitive information from the target device. And it appears that the threat actor also knows exactly who they want to target. Since researchers have been unable to download the app.

The news comes from ESET, some of their cybersecurity researchers have recently discovered two messaging apps called BingeChat and Chatico, were actually serving GravityRAT, a remote access trojan. The RAT is able to exfiltrate plenty of sensitive information from compromised endpoints. This includes information like call logs, contact list, SMS messages, device location, basic device information and files with specific extensions for pictures, photos and documents.

The apps cannot be found in the Play Store either

This is a pretty sophisticated malware app. Typically, you can find them in the Play Store and download them. But that’s not the case here. The apps cannot be found on the Play Store, nor other app stores. Instead, they can only be downloaded by visiting a special website, and opening an account.

Researchers from ESET could not open up an account on the site, as registrations were showing as “closed” when they visited. This leads the researchers to believe that hackers are being very precise about who to attack. Potentially looking at specific locations or IP addresses.

It appears that the majority of victims seem to be from India. Which sounds about right, since WhatsApp is very popular in that country. The attackers are also from Pakistan. And apparently the campaign has been active since last year.

So how can you protect yourself? Well, since this app needs you to register an account, do not register an account on any fishy looking websites. Especially one that wants your WhatsApp login credentials. That’s just asking for bad news.


[ad_2]
Source link

Googlers try to convince us that Pixel Fold is different from other Foldables

0
[ad_1]

On the eve of Google’s Pixel Fold launching, Engadget got the chance to sit down with a few Google Designers to talk about the new foldable. Which is a first for Google. While Apple is typically late to market with new products and technology, Google is pretty late here too. After all, the first foldables started to land on store shelves back in 2019.

Google is aiming to help and explain why their foldable isn’t just another foldable. Starting off with the shape of the Pixel Fold. It’s one of the wider foldables on the market. Compared to the Galaxy Z Fold 4 which has a very skinny front display, Google’s is actually more of a regular phone size. And George Hwang, one of Google’s product managers on the Pixel Fold, said that this design choice was on purpose, and wanted it to be shaped more like a passport. Hwang said that when they “talk about the Pixel Fold, we often talk about the outer display first.”

Hwang continued on by saying that their “focus on form factor was critical and quite intentional to make sure that we offered a usable exterior display, such that you could use the phone like you want to.” That might sound kind of odd, but with other foldables, that outer display is tall and skinny. Making it tough to use for every app. But this outer display is a 17.4:9 aspect ratio, making it even wider than most smartphones these days. Many are 21:9 or 20:9 in 2023.

Google explains how software can be tricky on a foldable

As you might expect, software can be tricky on a foldable. Particularly a book-style foldable like the Pixel Fold. Because, not only does Google need to build in phone and tablet software to take advantage of the cover display and the main display, but also how the main display is opened. If it’s opened completely flat, or at an angle.

Google’s other product manager that Engadget talked to, Andrea Zvinakis, stated that they “wanted there to be a user benefit to unfolding the device rather than just seeing an expanded phone layout. That’s why we created things like dual shade for notifications that leverage both sides of the display.”

Of course, this new style can also unlock other potentials, like the dual-screen interpreter mode that Google showed off at I/O last month. Allowing two people to see what’s being said, in different languages. Making this really useful for traveling to foreign countries where your language might not be the main language spoken.

Sadly, Google wasn’t able to offer a lower price for the Pixel Fold. It still starts at $1,799, the same price as Samsung’s competitor. But that should change in the coming years as foldables become more mainstream and the components get cheaper.


[ad_2]
Source link

GravityRAT Spyware WhatsApp

0
[ad_1]

Since August 2022, a recently discovered Android virus named “GravityRAT” has rapidly circulated through a new Android malware campaign. 

It gains access to phones by disguising itself as a fraudulent chat app called ‘BingeChat‘ in order to steal users’ sensitive data.

BingeChat

ESET researcher Lukas Stefanko discovered that the latest version of GravityRAT now steals WhatsApp backup files.

The creation of WhatsApp backups is intended to facilitate the migration of users’ message history, media files, and data to different or new devices.

While it’s crucial to be aware that these backups may include unencrypted sensitive data like:-

Technical analysis

Since 2015, GravityRAT has been active and in operation, but it shifted its focus to Android devices in 2020 for the very first time.

The spyware is exclusively utilized by ‘SpaceCobra,’ its operators, for selected operations with specific targets.

The spyware disguises itself as a chat application called ‘BingeChat,’ which claims to offer:-

  • End-to-end encryption
  • A user-friendly interface
  • Advanced functionalities
powerful features

The delivery of the app occurs through the website “bingechat[.]net” or other available platforms.

However, downloading it requires an invitation, prompting visitors to register a new account or provide sensitive data like credentials.

download

Presently, registrations are closed, and this method is employed solely for the purpose of targeting specific people with the distribution of malicious apps.

In 2021, the operators of GravityRAT once again employed the tactic of promoting malicious Android APKs to their targets.

This time, they utilized a chat app called ‘SoSafe,’ while a previous app named ‘Travel Mate Pro‘ was used before that.

Stefanko discovered that the app is a modified version of OMEMO IM, which is an authentic open-source instant messaging application for Android but is now infused with a trojan.

It was revealed by an ESET analyst that SpaceCobra employed a fraudulent app called “Chatico.”

This app was distributed to targeted individuals through the website “chatico.co[.]uk” during the summer of 2022.

Permissions asked

Upon installation on the target’s device, BingeChat requests permissions that pose potential risks. The permissions include access to the following:-

  • Contacts
  • Location
  • Phone
  • SMS
  • Storage
  • Call logs
  • Camera
  • Microphone

As instant messaging apps commonly require these permissions, they are unlikely to trigger suspicion or seem strange to the targeted individual.

When a user attempts to register on BingeChat, the app transfers the following details automatically to a C2 server operated by the threat actor:-

  • Call logs
  • Contact lists
  • SMS messages
  • Device location
  • Basic device information

As a safety measure, it is advised that users must avoid downloading any APKs from other unknown or unreliable sources.

Additionally, it is important to exercise caution and be vigilant regarding app permissions during installation.

Looking For an All-in-One Multi-OS Patch Management Platform – Try Patch Manager Plus


[ad_2]
Source link

BlackCat threatens to leak 80GB of Reddit data

0
[ad_1]

Ransomware gang ALPHV, most commonly known as BlackCat, is allegedly responsible for the theft of 80GB of data from social media site Reddit. 

The allegation comes directly from the ransomware gang, who have claimed responsibility for a data breach that happened in February of this year. In a post on the gang’s data leaks site, BlackCat claimed to have stolen 80GB of compressed data during the attack and are planning on selling it. 

The malicious actors claimed to have contacted Reddit on both April 13 and June 16, demanding the site pay them US$4.5 million to delete the data, but received no response. BlackCat said that as they are “very confident that Reddit will not pay any money for their data”, they will be selling it.

The threat actors said that they are “very happy to know that the public will be able to read about all the statistics they track about their users and all the interesting confidential data [they] took”. The gang also claimed that Reddit “silently censor” users. 

Source: BleepingComputer

Cyber security news site, BleepingComputer, said that it was able to confirm that the attack referenced by BlackHat was the phishing attack against Reddit in February of this year.

The February phishing attack against Reddit

The breach occurred on February 5, after a phishing attack was launched at Reddit employees. The site said the attack contained “plausible-sounding prompts pointing employees to a website that cloned the behavior of our intranet gateway, in an attempt to steal credentials and second-factor tokens”. 

After obtaining an employee’s credentials, the malicious actors were then able to gain access to Reddit’s internal systems. This meant that the hackers accessed Reddit’s internal business systems, dashboard, documents and source code.  

After being alerted to the phishing attack by the employee whose account was accessed, Reddit said it “removed the infiltrator’s access” and launched an investigation into the breach. The site noted that “similar phishing attacks” had been reported recently. 

The data accessed in the breach included “limited contact information for (currently hundreds of) company contacts and employees (current and former), as well as limited advertiser information”, but Reddit confirmed that “user passwords and accounts are safe”.

The site also reported that there was “no evidence” any of its primary production systems being accessed, or that any of its users’ “non-public data” had been accessed or posted online.

Reddit launched an internal investigation into the breach, as well as enhancing its security systems. Additionally, it urged users to enable multi-factor authentication and use a password manager both to set up complex passwords and to prevent themselves from being phished. 


[ad_2]
Source link

Galaxy Z Fold 5 & Flip 5 pricing info may surprise you

0
[ad_1]

The Samsung Galaxy Z Fold 5 and Flip 5 are coming next month, and some pricing information just surfaced. This info comes from Revegnus, a tipster, but the exact price tags are not revealed here.

The Galaxy Z Fold 5 & Flip 5 pricing info just surfaced

Still, the tipster did share some useful info. He said that the Galaxy Z Flip 5’s price tag will be on the same level as it was for last year’s model. In other words, you can expect a similar price tag as for the Flip 4.

For those of you out of the loop, the Galaxy Z Flip 4 launched with a $999 price tag. So, the Galaxy Z Flip 5 will either cost exactly $999, or its price tag will be really close to that.

What about the Galaxy Z Fold 5? That handset will be even more affordable than the Galaxy Z Fold 4, it seems. The tipster claims that the device will see a “slight reduction in price compared to its predecessor”.

The Galaxy Z Fold 4 launched with a price tag of $1,799. That was for the 256GB storage model of the device. The 512GB and 1TB iterations were more expensive of course.

The Galaxy Z Fold 5 will be a bit more affordable than the Fold 4

The Galaxy Z Fold 5 will cost less than $1,799, it seems. Will we get a $1,699 price tag, or will Samsung be able to pull off something even more affordable than that? Well, it remains to be seen.

Truth be said, this is not all that surprising. The Galaxy Z Fold 5 will look very similar to its predecessor. It will have the same form factor, pretty much. It will, however, include a different hinge, and fold flat as a result.

The crease control won’t be much better than it was on the Galaxy Z Fold 4, though, based on rumors. Samsung is taking a similar path with the Fold 4, so it’s not surprising it managed to lower its price a bit.


[ad_2]
Source link

Zoom calls are coming to Sony Bravia TVs soon

0
[ad_1]

It’s no secret that over the past few years, working from home has become a popular alternative for employees as it not only gives them more time with their family members but also helps the company save operational costs. Now, in an effort to make the virtual meeting experience more immersive, Sony has announced that its Bravia TVs will be the first to support Google’s new Zoom for TV app, offering a seamless and convenient way to participate in virtual meetings from the comfort of your living room couch.

This move by Sony follows Apple’s integration of FaceTime into Apple TV, and although it is a significant development, Bravia TVs do not come with built-in webcams. Therefore, users will need to purchase a $200 accessory called Bravia Cam to complete the setup. However, it is important to note that the Bravia Cam not only facilitates Zoom calls but also adjusts sound and picture settings based on the user’s position and distance from the TV.

Additionally, the accessory features a proximity alert system that detects when children are sitting too close to the TV and ensures that kids maintain a safe viewing distance. Moreover, the cam also includes a power-saving mode that automatically dims the TV when no one is watching, saving energy and prolonging the TV’s life.

Not available yet

While Sony has announced the new features and the Bravia cam accessory, the Zoom for TV app will be available for Bravia TVs “by early summer.” Shusuke Tomonaga, the head of Bravia product design at Sony, expressed enthusiasm about the partnership, stating, “This partnership will allow our customers to enjoy more realistic video communication on a big screen in the living room, enabling them to be more connected to the people they care about, whether they are working from home, studying remotely, or simply catching up with friends and family.”


[ad_2]
Source link