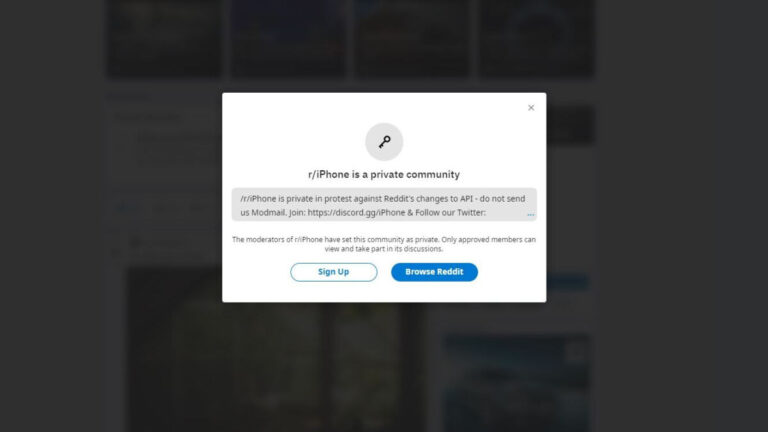
r/iPhone is the first victim of this latest strike against Reddit

0
[ad_1]
A huge part of having one of the best phones on the market in your pocket, is that you get to stay connected with your favorite online communities. Naturally, with the internet being the internet and you being on it, Reddit is a prime suspect when it comes to making the aforementioned happen.

Half social media platform, half new-age forum, Reddit has it all. Typically, if you aren’t too deep into the platform’s culture, you are rarely going to see scandals surrounding the webspace. But back in April, the company shared some planned changes regarding its API pricing strategy.

As in, Reddit was planning to start charging third-party Reddit clients for doing their thing. And if you aren’t a hardcore redditor just yet, then you should know that most redditors prefer third-party solutions by default. They typically offer more customization and features, which is always welcomed, but most of them are also unable to afford the API anymore. 

So, context! What better way to showcase how big of an issue this is than with an example? Christian Selig — founder of the Apollo App, a fan-favorite third-party Reddit client for iOS — was asked for $20 million per year by Reddit corporate in order to keep the app running. And yes, that is insane. So he made the tough call to shut down the service. 

But let’s get back to the “going private” thing for the iPhone subreddit. What does that mean? Well, basically that only approved members can visit and post on there. The shocking twist is that as part of the strike, the mods of the subreddit won’t be approving anyone new, so this basically means that r/iPhone is closed off for the time being.

While the strike itself looks to become quite huge, Reddit has made it clear in the past that they will do “what must be done” in order to keep its services active. As such, they may opt to place new moderators on all participating subreddits in an attempt to mitigate the strike. But that sounds like a recipe for a disaster, so we hope to not see it happen. 

But beyond that? No further comments have been made as of now. The Reddit community expects Reddit to fix this, but only time will tell if the company is willing to go back on their decision. We do hope that everything gets sorted out in the end, though, because as things are now: Reddit fans are the ones suffering these consequences.

[ad_2]
Source link

HSE latest victim of MOVEit cyber attack

0
[ad_1]

Health Service Ireland (HSE) has become the latest victim of a supply chain cyber attack launched against document transfer service MOVEit. The attack was launched by ransomware gang, Clop.

Clop were able to infiltrate MOVEit by exploiting a zero-day vulnerability that allowed the malicious group to break into company networks and steal data. Professional services partnership EY was also impacted by the cyber attack, leading to the breach.

HSE was working with EY to automate its recruitment process using software provided by MOVEit. On June 8, HSE was alerted to the fact that EY had been impacted by the cyber attack on MOVEit. Following this, HSE investigated the impact of the cyber attack on HSE and its data.

Following an investigation and analysis of the attack, HSE has determined that “no more than 20 individuals involved in the recruitment process” were affected by the data breach. The data potentially accessed by the hackers includes the names, addresses, mobile numbers and position of those on the recruitment panel, as well as more general information about the job roles to be filled. No other personally identifying or financial information was accessed during the cyber attack.

HSE is working with the relevant authorities including the Irish Data Protection Commission (DPC) regarding the cyber attack and data breach. The organization is in the process of contacting those affected by the breach.

Other companies affected by the breach include those who use the payroll services provider, Zellis. The network infiltration of Zellis led to the breach of more than 100,000 employees’ data from companies including the British Broadcasting Company (BBC), health and beauty retailer Boots and flag carrier of Ireland Aer Lingus. 

The ransomware gang later took to the dark web in an ettempt to extort victims of the data breach. Clop issued an ultimatum to the data breach victims, saying that comapnies affected by the attack need to contact them by June 14, or their personal data would be leaked online.

Clop claimed that all those who worked for local or national government or the police services were exempt from this threat. The ransomware gang addressed them directly, saying they should “not worry”. They continued, saying “we erased your data you do not need to contact us. We have no interest to expose [sic] such information”, although the legitimacy of this statement has been called into question.


[ad_2]
Source link

New Banking AitM Phishing and BEC Attacks

0
[ad_1]
Banking AitM Phishing

In a recent revelation, Microsoft disclosed that banking and financial service institutions had become the active target of a fresh attack known as adversary-in-the-middle (AitM) phishing and BEC.

As the number of reported cases surpasses 21,000 and the losses skyrocket by $2.7 billion, the Federal Bureau of Investigation (FBI) unveils a drastic surge in business email fraud.

Federal law enforcement agencies have taken notice of an unknown strategy employed by threat actors, which enables them to bypass “impossible travel” alerts, commonly used to detect and prevent abnormal login attempts and other doubtful account actions, thereby facilitating the monetization of Cybercrime-as-a-Service (CaaS).

In this case, Companies like Trustifi Stop Advanced Email Threats That Target Your Business Email with AI-Powered Email Security.

Banking AitM Phishing

The pace of cybercriminal activity concerning business email compromise is speeding up rapidly. 

In adopting platforms like BulletProftLink, attackers have made a dramatic shift as it’s a favored choice for directing malicious email campaigns on an industrial scale.

Experience the full suite of services at BulletProftLink, where you can access templates, hosting, and automated tools to enhance your BEC operations.

With this Crime-as-a-Service (CaaS), adversaries access victim credentials and their corresponding IP addresses.

After executing the BEC scheme, threat actors engage residential IP services to obtain the IP addresses corresponding to the location of the victim. 

Through the creation of residential IP proxies, they can hide their true origin, providing cybercriminals with enhanced anonymity.

Microsoft has most frequently observed the deployment of this tactic in Asia and an Eastern European nation where threat actors have been actively involved.

When identifying potential compromise of a user account, the detection of “impossible travel” is utilized as an indicator.

The scale of these attacks is heightened as threat actors leverage IP/proxy services that are also utilized by marketers and other research-oriented individuals.

Threat actors facilitate phishing campaigns and the acquisition of compromised credentials through the utilization of phishing-as-a-service platforms such as:-

  • Evil Proxy
  • Naked Pages
  • Caffeine

Annually, organizations suffer financial losses of hundreds of millions of dollars due to the success of BEC attacks.

Top Targets for BEC

Here below, we have mentioned the top targets for BEC:-

  • Executives
  • Senior leaders
  • Finance managers
  • Human resources staff

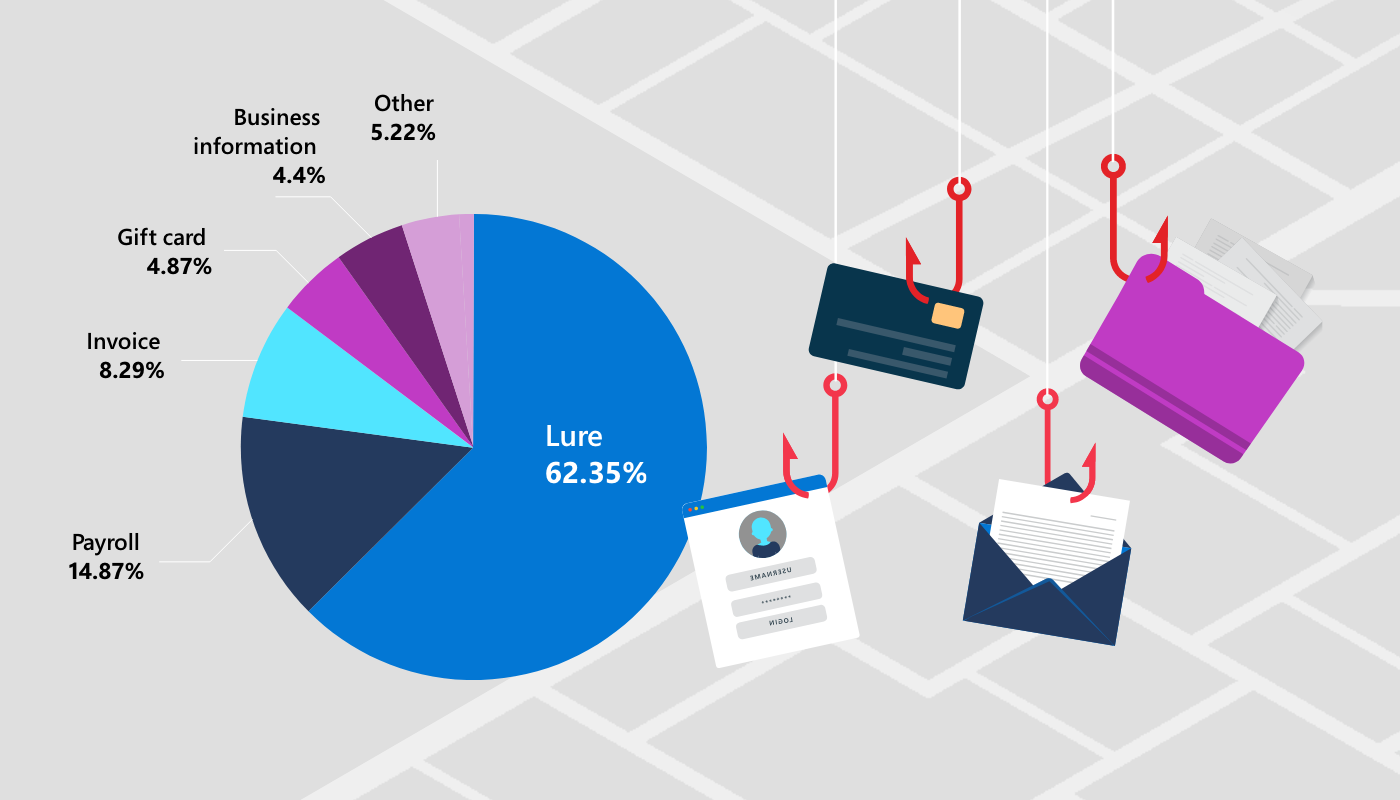
BEC attacks in almost all their forms are experiencing a notable surge, and the top trends contain:-

  • Lure
  • Payroll
  • Invoice
  • Gift card
  • Business Information
Top Targets for BEC

Within the cybercrime ecosystem, BEC attacks stand out for their specialized use of social engineering tactics and the ability of deceptive practices.

Recommendations

Here below we have mentioned all the recommendations offered by the researchers at Microsoft:-

  • Take all the essential security measures to maximize the security settings that protect your inbox.
  • Establish a robust authentication system for enhanced security.
  • Provide comprehensive training to employees to effectively identify warning signs.
  • Secure your environment by implementing a proper and robust security system.
  • Enhance your email security by utilizing a secure and well-established email solution.
  • Strengthen identity authentication to restrict unauthorized lateral movement within the infrastructure.
  • Implement a trustworthy and protected payment platform for secure transactions.
  • Take a short pause and use a phone call as a reliable method to verify financial transactions.

Stop Advanced Email Threats That Target Your Business Email – Try AI-Powered Email Security


[ad_2]
Source link

Super Smash Flash 2 Unblocked

0
[ad_1]

Super Smash Flash 2 Unblocked is the next fun version of the impressive game series which is titled Super Smash Bros.

Super Smash Flash 2 was designed by McLeodGaming operator. The release of the game was as brilliant as its first version. The second edition was improved a lot.

It is an entirely new version and has nothing to compare to the original. All the improvements, updates, and attractive features make Super Smash Flash 2 Unblocked 6969 very popular.

It helps players play in full-screen mode. Also, you can fight against online opponents simply by using the proprietary network system of McLeodGaming.

There are a lot of decent Flash games available online, but it is rated as one of the best. This game has a strong appeal to the fans.

Now you understand why just a short time after the release, the game has reached 400,000 plays per day. Even now it is at the peak of its popularity.

super smash unblocked

Super Smash Flash 2 Unblocked

Super Smash Flash 2 Unblocked or Super Smash Flash Hacked offers a big variety of playing characters.

You will be delighted to play your favorite character roles such as Mario, Link, Pikachu, Sonic, Zelda, Ichigo Naruto, Goku, and many others. There are two playing modes in this game.

The Super Smash game was based on the Super Smash Bros series and the game includes single-player & multiplayer modes.

There is a mode for a single player where you will be given a chance to join campaigns and defeat an impressive series of rivals controlled by PC.

You can choose between the classic and adventure modes which are also programmed inside this game.

Once you have completed all the roster modes, you will be getting the All-star mode enabled.

Before starting the play for the first time, training is necessary, yes it includes training mode also to enhance the skills.

There is another multiplayer game mode, where you have a chance to affiliate with several players on the same device.

This mode is fun because you can defeat the rivals controlled by PC with a reasonably tricky level.

Now, let’s have a look at the primary game objective. The mission of the game is similar to Super Smash Bros.

Super Smash Flash where you will have to use a lot of special abilities and skills in order to knock all your game opponents off the PC screen.

Super Smash Flash 2 Hacked 88 has a difference of much more diverse experience with the main game characters: Marth, Zero Suit Samus, and Chibi-Robo.

While playing you will have to achieve the fastest speed. You can play on your personal computer.

It is effortless to capture the game rules and control the keyboard as quickly as possible.

It includes 44 characters, the game includes a series of super smash games and the game is available as an app file.

By having Nintendo 3ds Emulator you can play your lovable classic games such as Super Mario, Top Gun, and Base Wars.

Conclusion

Although the game has some incomplete points, it is obviously a great flash game. Many fans have already left positive feedback.

The game Super Smash Flash 2 deserves your attention and a bit of free time! Download Here.

However, if you’re interested in playing Super Smash Flash 2, you can search for reputable websites that offer the game legally and play it directly from there.

Many websites provide access to the game without any restrictions or the need to unblock it.

Please ensure that you are obtaining the game from a legitimate source and not engaging in any activities that may infringe upon copyright laws or violate any terms of service.


[ad_2]
Source link

Two U.S. Senators accuse TikTok of lying to Congress and demand answers

0
[ad_1]
Back in March, TikTok CEO Shou Zi Chew spoke to members of the House Energy and Commerce Committee about the alleged storage of U.S TikTok. users’ personal data by the app’s parent company ByteDance. Last week, a letter written to the CEO by Senators Richard Blumenthal, Democrat of Connecticut, and Marsha Blackburn, Republican of Tennessee, accused TikTok officials of giving misleading and inaccurate answers to Congress and demanded the answers to a dozen questions before the end of this coming week.
In the letter dated June 6th, the lawmakers cite published material from The New York Times that claims that user data from American TikTok users, including driver’s licenses and child sexual abuse materials, was shared at TikTok and its parent company ByteDance through an internal messaging platform named Lark.

The Senators accuse TikTok employees of giving them “misleading or inaccurate responses”

The Senators say in their letter, “We are disturbed by TikTok’s pattern of misleading or inaccurate responses regarding serious matters related to users’ safety and national security, and request that TikTok correct and explain its previous, incorrect claims.” The Times report says, “[the] profusion of user data on Lark alarmed some TikTok employees, especially since
ByteDance workers in China and elsewhere could easily see the material.” The report also noted that data from the Lark platform was kept on China-based servers.

A story in Forbes published last month was mentioned in the letter written by the two Senators. That article accuses TikTok of storing the financial information of U.S. TikTok creators, including tax information and social security numbers, in China.

Senators Blumenthal and Blackburn point out that they have been told numerous times by TikTok employees and by its CEO that TikTok stores U.S. user data in Virginia and Singapore. Talking to CEO Chew, the pair write, “Nowhere in your response did you mention that TikTok stores user data in China, or that information about U.S. users— including sensitive information like photos and driver’s licenses or reports containing illegal materials like child sexual abuse materials — would be shared on Lark, and therefore accessible to ByteDance employees.”

The Senators demand responses to these questions by June 16th

The letter includes 14 questions that the Senators want TikTok to answer by next Friday, June 16th:

Under what conditions does TikTok currently store information or personal data about American users on servers located in China, or allow employees that are based in China or associated with ByteDance to access that data?At the time that Mr. Beckerman testified in October 2021 that “U.S. user data is stored in the United States,” what American data was stored by, or accessible to, China or ByteDance?Is there anything from Mr. Beckerman’s testimony in October 2021 or your testimony in March 2023 that TikTok believes merits correction?
Why did you and Mr. Beckerman previously testify that TikTok does not store user data in China when Forbes and New York Times reports have clearly found otherwise?

Did TikTok notify CFIUS that it continued to store U.S. user data on servers in China, and if so, when?

For how long has the user data related to the TikTok Creator Fund referenced in the Forbes report been stored in China and why did TikTok store that data in China?

Detail the scope of the U.S. user information stored on servers in China related to the TikTok Creator Fund or any other programs. The Forbes report references “sensitive financial information, including social security numbers and tax IDs.”

According to the New York Times report, U.S. TikTok user data shared on Lark was stored on servers in China as recently as late 2022. For how long was that user data being stored in China and is any Lark data from U.S. users still stored or retained on servers in China?

China’s National Intelligence Law requires organizations and citizens to “support, assist and cooperate with the state intelligence work.” Can ByteDance or TikTok be compelled to share U.S. user data stored in China to Beijing?

Has TikTok taken any steps to investigate whether data related to the TikTok Creator Fund or any other U.S. user data stored in China or accessible to ByteDance employees was shared with officials of the Chinese Communist Party or the Chinese government?

Has TikTok and/or ByteDance deleted the U.S. user data referenced in the New York Times and Forbes reports from its servers in China? Do you intend to maintain those as backup to the cloud infrastructure, as well?

Are TikTok employees still using Lark for internal messaging and management functions? Is ByteDance still involved in the development and maintenance of this data sharing tool?

The New York Times report mentioned the sharing between employees on Lark of sexually explicitly images of children as young as 3 years old. We previously wrote to TikTok to ask a series of questions about how the company handles the moderation of such content. What protocols do you use to ensure the appropriate handling and reporting of these unlawful materials?

What oversight, involvement, or role does TikTok have with other products offered by ByteDance to users in the United States, such as Lemon8 or CapCut?


[ad_2]
Source link

New Phishing Scam Spoofs German Media, Broadband Conference Anga

0
[ad_1]

The Anga Com Conference is Europe’s leading business platform for Broadband, Television, and Online, based in Germany. However, in the latest phishing scam, crooks are exploiting the platform to steal personal data.

In a cunning display of cyber deception, hackers have devised an intricate phishing attack by leveraging the reputation of Germany’s renowned Anga Com conference. By sending spoofed emails and creating deceptive web pages, these hackers are deceiving unsuspecting users into divulging their login credentials.

Security researchers at Avanan, a subsidiary of Check Point Software, have uncovered the details of this sophisticated attack, shedding light on the techniques employed by crooks. Anga Com is a widely attended conference in the broadband and media distribution industry, drawing more than 22,000 participants from 470 companies globally.

Typically, conferences serve as a platform for companies to generate interest and revenue by sharing lead lists. However, hackers have exploited this process by inserting themselves into the lead delivery system. In this case, they have created fraudulent web pages on legitimate developer sites, making it challenging for victims to detect the scam.

The attack begins with an email that appears to originate from Anga Com, informing recipients that visitors expressed interest in their exhibition during the conference. The email entices users with the prospect of generating new business and urges them to click on a provided link to engage with potential clients. Upon inspection, the email address of the sender is found to be an Outlook address not associated with Anga Com.

Clicking on the link redirects users to a deceptive login page skillfully designed to mimic the legitimate Anga Com platform. Unbeknownst to victims, the URL of this page is angacom-de.surge.sh, whereas the genuine URL is angacom.de. The hackers have utilized Surge.sh, a legitimate web development service, to create a convincing replica of the Anga Com website. When users enter their email and password on this fraudulent page, their credentials are promptly stolen.

This attack combines several techniques, including impersonation, social engineering, and credential harvesting. The initial email preys upon the trust and interest associated with the Anga Com conference. Hackers capitalize on the conference’s popularity and the promise of new business opportunities to manipulate users into clicking malicious links.

Moreover, the creation of the look-alike webpage requires some level of expertise, although the availability of tools like Surge.sh facilitates this process for cyber criminals.

German Broadband and Media Conference Anga Spoofed to Steal Data
Phishing email and its content (Image credit: Avanan)

According to the company’s blog post, Avanan researchers promptly notified Surge.sh and Anga Com of the situation upon discovering this attack. By replacing the links in email bodies and attachments, security services can enhance their ability to detect and prevent attacks that hide malicious links.

To defend against such attacks, security professionals are advised to implement security measures that thoroughly examine all URLs and emulate the webpages behind them.

Furthermore, leveraging URL protection systems that recognize phishing techniques, such as those employed in this attack, can serve as valuable indicators of malicious activity. Educating users and employees to hover over URLs and exercise caution when clicking on links can also help mitigate the risk posed by sophisticated phishing campaigns.

  1. How to detect phishing images in emails
  2. Scammers Pose as ChatGPT in New Phishing Scam
  3. Geo Targetly URL Shortener Abused in Phishing Scam
  4. YouTube phishing scam using authentic email address
  5. Coinbase Employees Targeted by SMS Phishing Attack

[ad_2]
Source link

Multi-Stage AiTM Phishing and BEC Attack on Financial Sector

0
[ad_1]

Recently, Microsoft’s Defender Experts uncovered a sophisticated multi-stage adversary-in-the-middle (AiTM) phishing and business email compromise (BEC) attack, which targeted banking and financial services organizations. The attack, tracked as Storm-1167, was initiated from a compromised trusted vendor and transitioned into a series of AiTM attacks and follow-on BEC activity spanning multiple organizations. The aim was financial fraud, exploiting trusted relationships between vendors, suppliers, and partner organizations.

The multi-stage AiTM phishing and BEC attack began with a phishing email from a trusted vendor, which contained a unique seven-digit code as the subject. The email body included a link to view or download a fax document, which led to a malicious URL hosted on Canva.com. The attackers cleverly leveraged the legitimate service Canva for the phishing campaign, using it to host a page that showed a fake OneDrive document preview and linked to a phishing URL.

Once the victims clicked on the URL, they were redirected to a phishing page hosted on the Tencent cloud platform that spoofed a Microsoft sign-in page. After the victims provided their passwords, the attackers initiated an authentication session with the victims’ credentials. When prompted with multi-factor authentication (MFA), the attackers modified the phishing page into a forged MFA page. Once the victims completed the MFA, the session token was captured by the attackers.

The attackers then used the stolen session cookie to impersonate the victims, circumventing authentication mechanisms of passwords and MFA. They accessed email conversations and documents hosted in the cloud, and even generated a new access token, allowing them to persist longer in the environment. The attackers also added a new MFA method for the victims’ accounts, using a phone-based one-time password (OTP) service, to sign in undetected.

The attackers then initiated a large-scale phishing campaign involving more than 16,000 emails with a slightly modified Canva URL. The emails were sent to the compromised user’s contacts, both within and outside of the organization, as well as distribution lists. The recipients were identified based on the recent email threads in the compromised user’s inbox. The subject of the emails contained a unique seven-digit code, possibly a tactic by the attacker to keep track of the organizations and email chains.

The recipients of the phishing emails who clicked on the malicious URL were also targeted by another AiTM attack. Microsoft Defender Experts identified all compromised users based on the landing IP and the sign-in IP patterns. The attacker was observed initiating another phishing campaign from the mailbox of one of the users who was compromised by the second AiTM attack.

This incident highlights the complexity of AiTM attacks and the comprehensive defenses they necessitate. It also underscores the importance of proactive threat hunting to discover new tactics, techniques, and procedures (TTPs) on previously known campaigns to surface and remediate these types of threats. The continuous evolution of these threats, such as the use of indirect proxy in this campaign, exemplifies the need for organizations to stay vigilant and proactive in their cybersecurity measures.


[ad_2]
Source link

Google Introduced Upgrades In The Chrome Password Manager

0
[ad_1]

While saving passwords in browsers isn’t recommended, Google now ensures it does remain safe in its Chrome browser. With the latest release, Google introduces some notable feature upgrades in its password manager available for Android devices and Chrome browsers.

New Google Chrome Password Manager Exhibits Many Feature Upgrades

According to a recent post from Patrick Nepper, Google Chrome Group Product Manager, the tech giant has launched some major feature upgrades in its Password Manager.

Briefly, Google Chrome password manager will now boast five new features, facilitating users in managing secure account logins. These include,

  • Dedicated setting and desktop shortcut: Google Chrome users will get a clear option for the Password Manager in Chrome browsers. Users can find this menu under the “chrome://password-manager/passwords” setting. Besides, users can also add a dedicated Google Password Manager shortcut on their desktops for quick access.
  • Biometric authentication for desktop users: The latest password manager release allows users to enable more authentication methods (biometric/facial recognition) even on their desktops. However, this setting will predominantly rely on the computer’s operating system’s support for other authentication methods.
  • Add Notes feature: Google Password Manager now has an “add note” feature to let users quickly save important information.
  • Password import feature: While most contemporary password managers support a password import feature to let users move their saved passwords quickly, Google Password Manager previously lacked it. However, with the latest update, the tool will empower users to move their saved passwords from other password managers to Google via a simple .csv file.
  • Weak password detection for iOS: For iOS users, Google Password Manager offers a “Password Checkup” tool that flags reused and weak passwords alongside breached ones.

This new update comes weeks after Google announced “PassKeys” roll-out supporting passwordless authentication. With Passkeys, Google aims to promote secure account logins in tandem with regular passwords. And now, the latest changes in the password manager will further help Google users to manage their accounts’ safety.

Let us know your thoughts in the comments.


[ad_2]
Source link

The Future of Authentication in Cybersecurity

0
[ad_1]

The digital counterpart of your physical reality is growing phenomenally. While positive outcomes are certainly there, with the growth of the internet, the risks associated with it are also growing rapidly. When discussing cybersecurity risk management, the first thing that comes to mind is passwords. But that’s not enough when threats like scams, phishing, and more are in the picture.

So, what’s the solution, then?

In a digital era where cyber threats are increasing daily, we must go beyond passwords to protect our data and keep our privacy intact.

Passwordless authentication: what is it?

The 20th century was all about passwords, but now it goes beyond that. In simpler words, passwordless authentication implies methods of authenticating one’s identity online without using passwords. Passwordless authentication involves more secure alternatives to verifying the identity of a user.

With increasingly increasing passwords getting breached, it is no secret that they are not an ideal solution to safeguarding data. Not only are they hard to remember at times, but passwords are also what cybercriminals go after most.

Different types of passwordless authentication

Now that we have a fair idea of what it means to authenticate without passwords, let’s look at the many types of passwordless authentication.

Biometrics: Biometric factors like retina scans and fingerprints can identify a person uniquely. Known as the inherence factors, this type of method grants a user access based on biological characteristics. Even with the rise of AI, imitating these methods is highly difficult and thus extremely safe when it comes to securing an account.

Some of the common biometric factors are:

  • Voiceprint
  • Facial recognition
  • EKG
  • Fingerprint scan
  • Retinal scan

How biometrics work:

Upon registering an account on a new app, the user will need to present a form of biometric ID that will act as a private key to get access in the future.

In order to re-access the particular application, the user needs to present the ID that they signed up with earlier.

Since biometric IDs are authorised biometric features, they are comparatively safer than other methods.

Possession factors: Another method involves possession or ownership factors that, as their name suggests, are used to grant access through certain devices that are in possession. For example, devices like mobile phones are mostly used in such authentication processes. Upon registering for a new app, the user will get one-time passcodes through SMS or push notification from the authenticator app.

Only upon responding to those notifications can a user get access to the particular platform. Since hackers need the specific possession factor to react to the notification, cyberattacks get extremely difficult.

Some of the possession factors include:

  • Authenticator app
  • Smart card
  • Mobile device
  • Hardware token

How Possession Factors Work:

The user will need to verify their possession factor when registering a new application. This can be a mobile device number or a QR code.

After that, the app generates a private key that is only associated with the possession facto.

In the event of an attempt, the app will send an OTP as a PIN, passcode, or push notification.

The user will only get access to the application after they respond to the notification on that specific device.

Magic Links

Magic links mainly involve email addresses to log into a particular account. Upon clicking the magic link, the app directly grants the user access. Popular websites/apps that use magic links are Slack and Medium, to name a few.

How magic links work:

When registering for the first time on an application, the app prompts the user to share their email address to create a customised magic link. 

Upon clicking on the link that the user receives in their email address, the user gets authenticated by matching the token.

Advantages of passwordless authentication methods

We have gone through the many methods that can be used instead of passwords to access and re-access a new account. But why do companies prefer this over the former method? Let’s look at the reasons one by one.

  1. Stronger cybersecurity

With the advancement of technology, hackers have also advanced. In this scenario, passwords have stopped being a strong barrier for any online account. For instance, employees often use similar or the same passwords for different applications. With passwords, the chances of phishing, malware attacks, and lists on the dark web get higher. This means, with one password, hackers can even get access to multiple accounts.

On the other hand, passwordless authentication eliminates the use of passwords altogether. This instantly removes the risks associated with major cyberattacks like credential stuffing, account takeovers, password theft/brute force attacks, and phishing.

Your organisation’s safety profile is significantly improved by implementing passwordless authentication techniques on its website, workplace devices, and applications.

It becomes impossible to continue creating and remembering hundreds of passwords. Additionally, the procedure for changing a password when an employee forgets it is frequently difficult. Therefore, it should come as no surprise if staff members use the simplest password they can remember, keep the same password across all platforms, or add a distinctive character or a number when required to do so once a month.

Users no longer need to generate passwords or memorise them thanks to passwordless authentication. To authenticate instead, they can use their phone, email, or face.

Employees can spend the time they would have otherwise spent pondering or changing passwords on other, more important tasks if they have a quick, straightforward login experience. Passwordless authentication can enhance the client experience as well.

Customers are frequently asked to log into your website if they already have an account. Passwordless authentication can help reduce the likelihood of abandoned shopping carts and platform hacks.

  • Long-Term Costs Are Lower

Think for a moment about the amount of money your business spends on password storage and administration. Include the time IT devotes to password resets and addressing the frequently altering legal requirements for password storage.

Scalability-wise, passwordless authentication may be superior to conventional password-based authentication. This is so that corporations won’t have to maintain and manage login information for users. This authentication offers a more simplified authentication process, which can help organisations control expenses as they expand and their user base grows.

This authentication can drastically cut down on the volume of support tickets, including those for resetting passwords and troubleshooting, thereby lessening the workload on support staff and associated operational costs.

Passwords are a common reason for user retention and drop-offs. Implementing passwordless authentication increases the likelihood that users will return to an application because they are not burdened with remembering their passwords.

By using passwordless authentication, one may avoid all of these costs. No more remembering passwords, resetting lost ones, or worrying about new compliance regulations.

  • Increased User Satisfaction

User experience matters when creating any program that would satisfy users’ needs. Passwordless authentication improves the user experience of the entire application, from opening to navigating to securely closing it.

Compared to conventional password-based authentication, passwordless authentication is easier to set up. This approach streamlines user onboarding in contrast to the time-consuming password setup process that frequently irritates customers.

A user experience that is convenient and welcoming results in a substantially higher conversion rate for the application. Users who employ passwordless authentication are far less inclined to become irritated by the difficulties they frequently encounter while signing up for password-based applications.

Organizations decrease the risk of users leaving their intended action due to irritation with the authentication procedure by eliminating the multi-step process of establishing difficult passwords and then re-entering them upon each login.

Best Practices of Passwordless Authentication

While there is no denying that passwordless authentication methods are superior to the good-old passwords, in the end, it all comes down to best practises.

Organisations need to be prepared for the significant attempt to carry out passwordless authentication technology. Without adequate planning, there are increased chances of making poor adoption decisions, which invite vulnerabilities rather than secure them.

Possession Factors:

Let’s start with possession factors. The best practises include:

  • Using an accredited authenticator app
  • Accepting the latest OTP code
  • Minimising failed attempts and limiting the time of a code being valid

Biometric factors:

  • Users must not share their facial data or fingerprints, which is quite an obvious point.
  • ALways having a backup to deal with any malfunctions while authenticating
  • Stick to biometrics that are difficult for hackers to circumvent. These might include palm vein scanning and gait recognition, to name a few.

Magic links:

Last but not least, let’s take a look at the safety measures we need to take when dealing with magic links.

  • Making sure that the email delivery service is able to send magic links quickly. This is important because you don’t want the links to end up in the spam folder and delay the email.
  • Offering links that are for one-time use and expire after a certain period.
  • Enforcing MFA or multi-factor authentication that ensures the user’s identity
  • Preventing message threading by working with the email provider.

Conclusion

It is no secret that the upside of passwordless authentication weighs more than the challenges that come with it. With society moving forward in technological advancements, it has now become essential to implement multi-factor authentication and go for a passwordless approach.

 Businesses that are employing cutting-edge authentication processes tend to step ahead of their competitors not just by providing robust security but also a seamless user experience.
[ad_2]
Source link

Honda eCommerce Platform Flaw Exposes Customers’ Data

0
[ad_1]
Honda Data Leak

Eaton Zveare, a security researcher, has released the specifics of major vulnerabilities uncovered in Honda’s e-commerce platform for power equipment, marine, and lawn & garden products.

It allowed anyone to reset their password for any account and was therefore open to unauthorized access.

The researcher found the security flaws and the data leakage early this year, and he informed Honda of his findings in mid-March. 

The vendor acknowledged the problems right away and congratulated the white hat hacker for his efforts but did not compensate him because it lacked a bug bounty program.

Honda reported that it did not discover any proof of malicious exploitation.

“I compromised Honda’s power equipment/marine/lawn & garden dealer eCommerce platform by exploiting a password reset API that let me easily reset the password of any account,” said the researcher.

“Broken/missing access controls made it possible to access all data on the platform, even when logged in as a test account.”

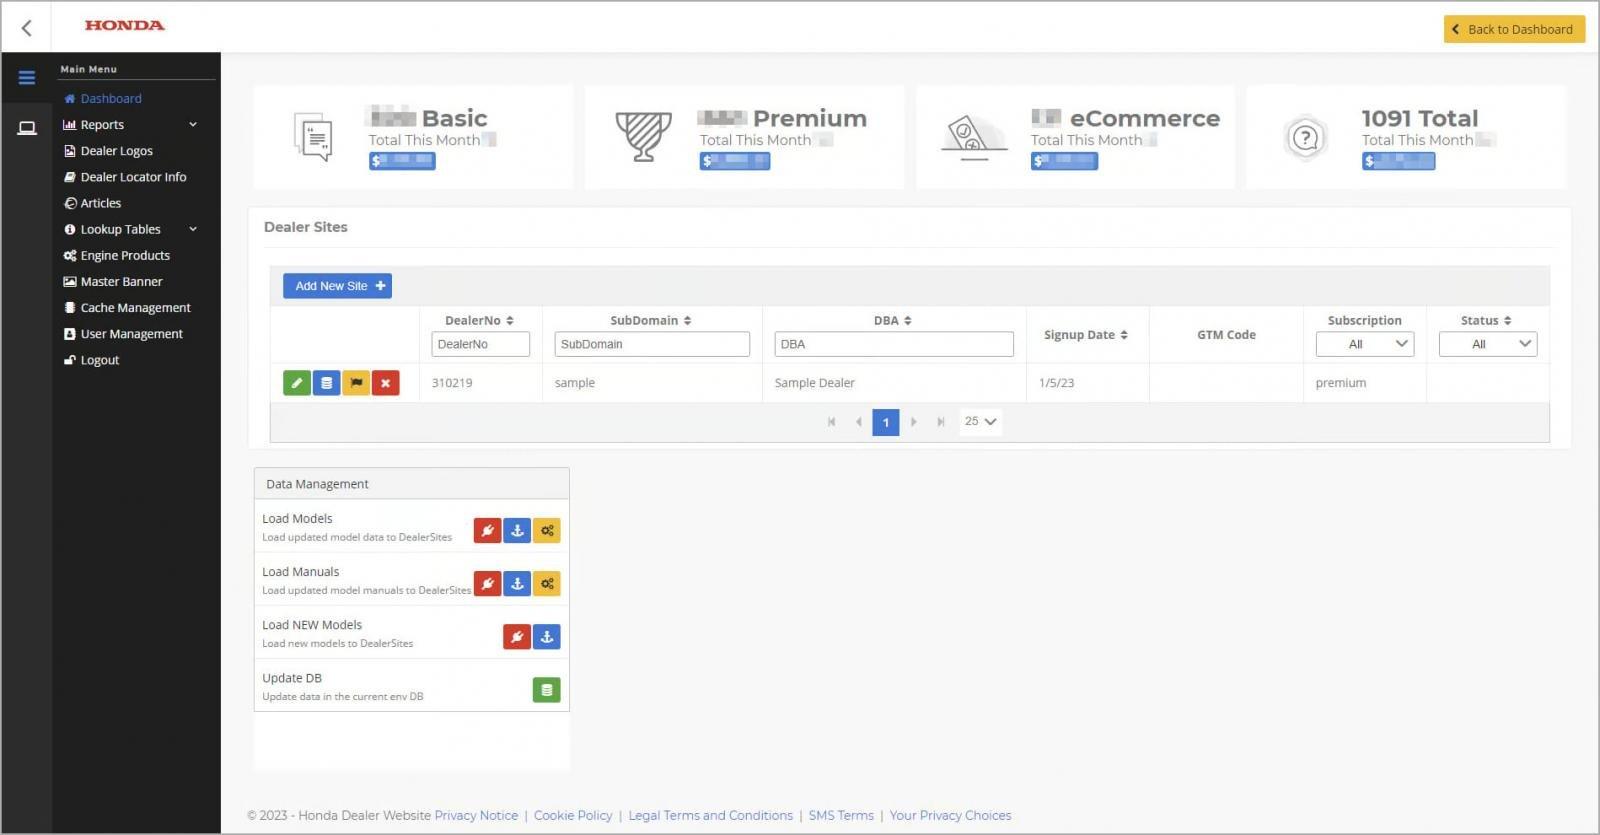
The platform drives Honda Dealer Sites, a service that allows dealers to build websites to sell Honda goods. Dealers are given all the resources they need to build a website, market it, and manage product orders after they create an account.

A Password Reset API Vulnerability In An Admin Dashboard

The researcher found a password reset API flaw in the admin dashboard that let him change the password for a Honda test account setup. 

Complete administrative access obtained with access to:

  • 21,393 customer orders across all dealers from August 2016 to March 2023, including customer name, address, phone number, and ordered items.
  • 1,570 dealer websites (1,091 of those are active). It was possible to modify any of these sites.
  • 3,588 dealer users/accounts (includes first & last name, email address). It was possible to change the password of any of these users.
  • 1,090 dealer emails (includes first & last name).
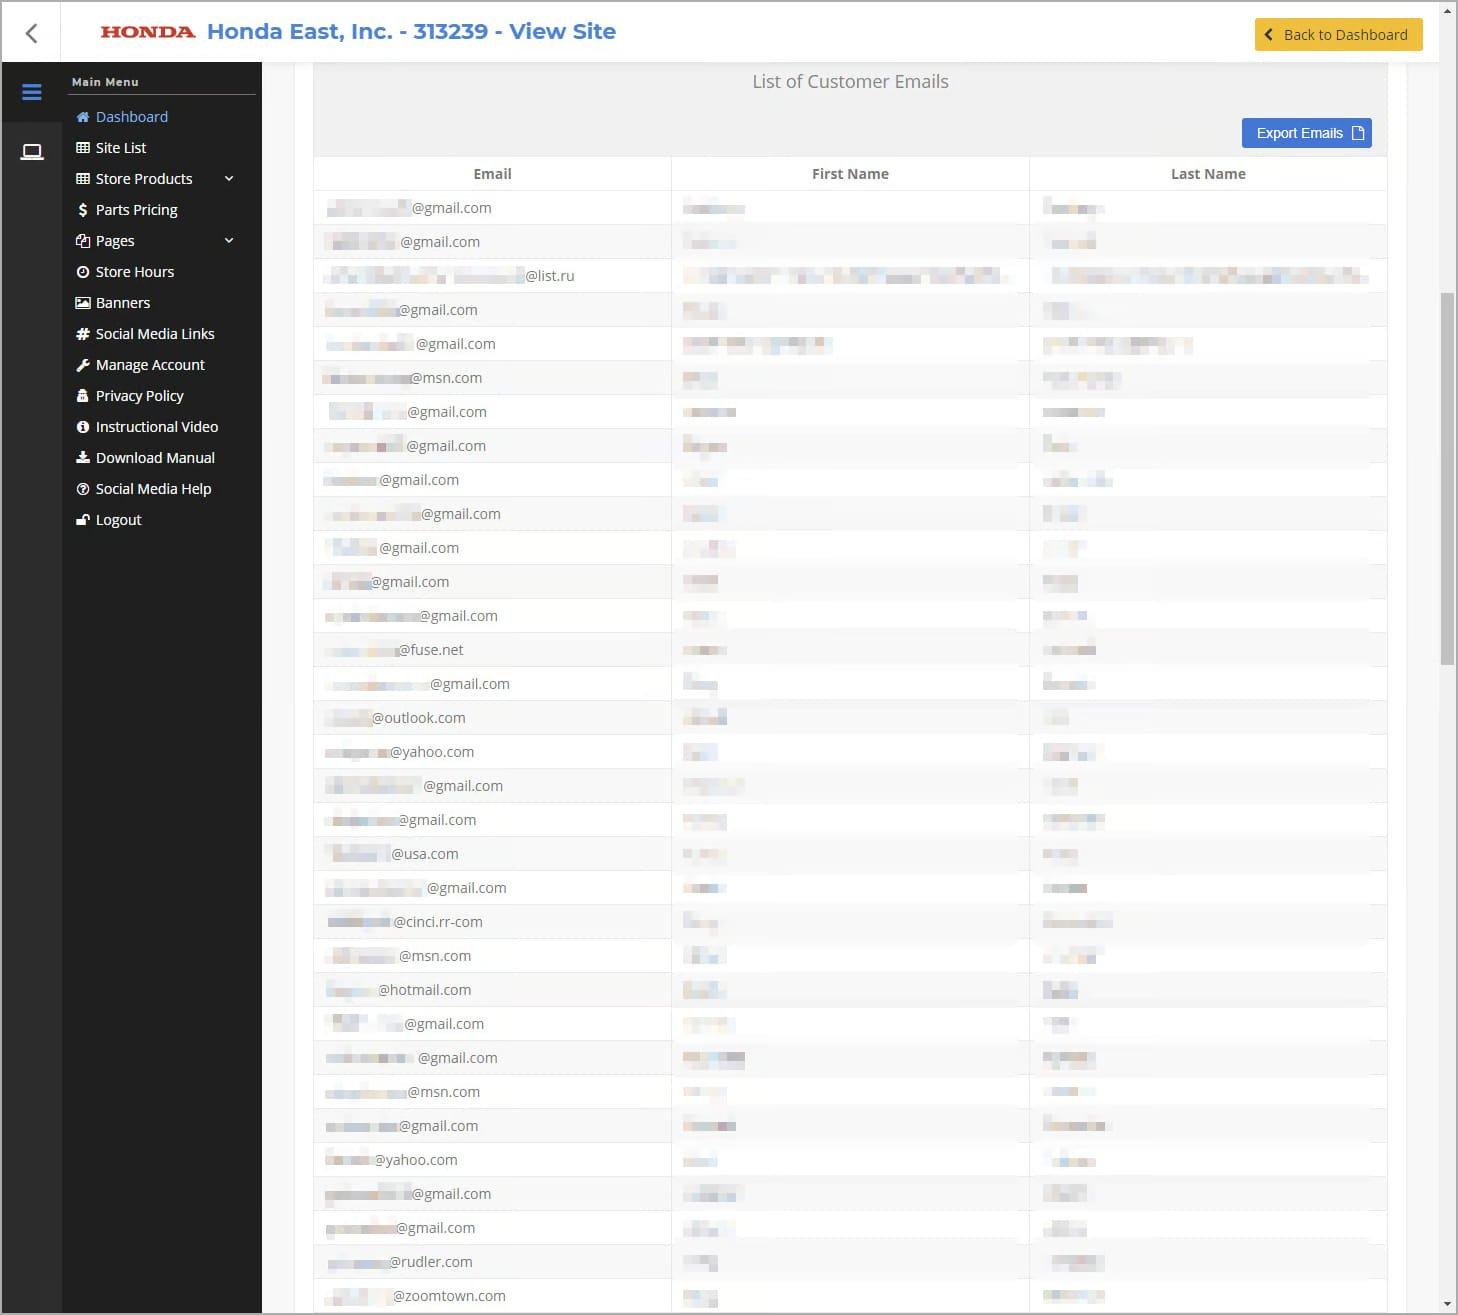
  • 11,034 customer emails (includes first & last name).
  • Potentially: Stripe, PayPal, and Authorize.net private keys for dealers who provided them.
  • Internal financial reports.
Exposed customer emails

The researcher mentioned that the “powerdealer[.]honda.com” subdomains are given to authorized resellers and dealers by Honda’s e-commerce platform, which contains the API issue.

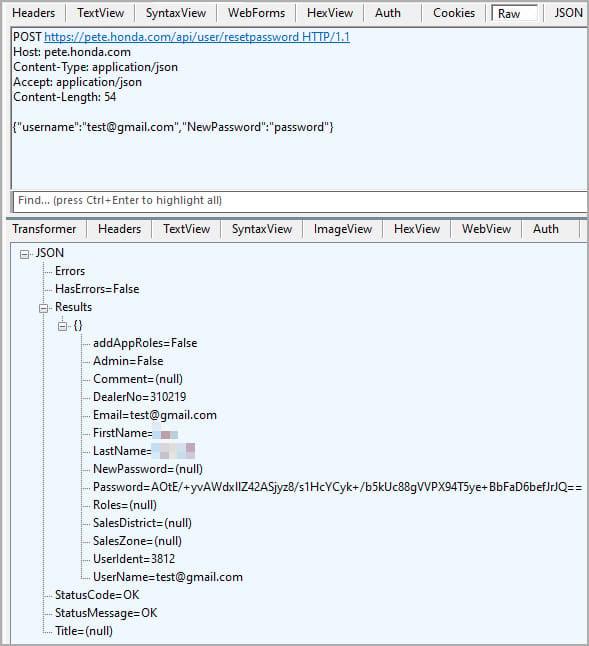
He discovered that the Power Equipment Tech Express (PETE) password reset API on one of Honda’s websites performed reset requests without a token or the prior password and only required a valid email.

Despite the absence of this vulnerability on the e-commerce subdomains login portal, anyone can access internal dealership data using this straightforward attack because the credentials changed on the PETE site would still work there.

Password reset API request sent to PETE

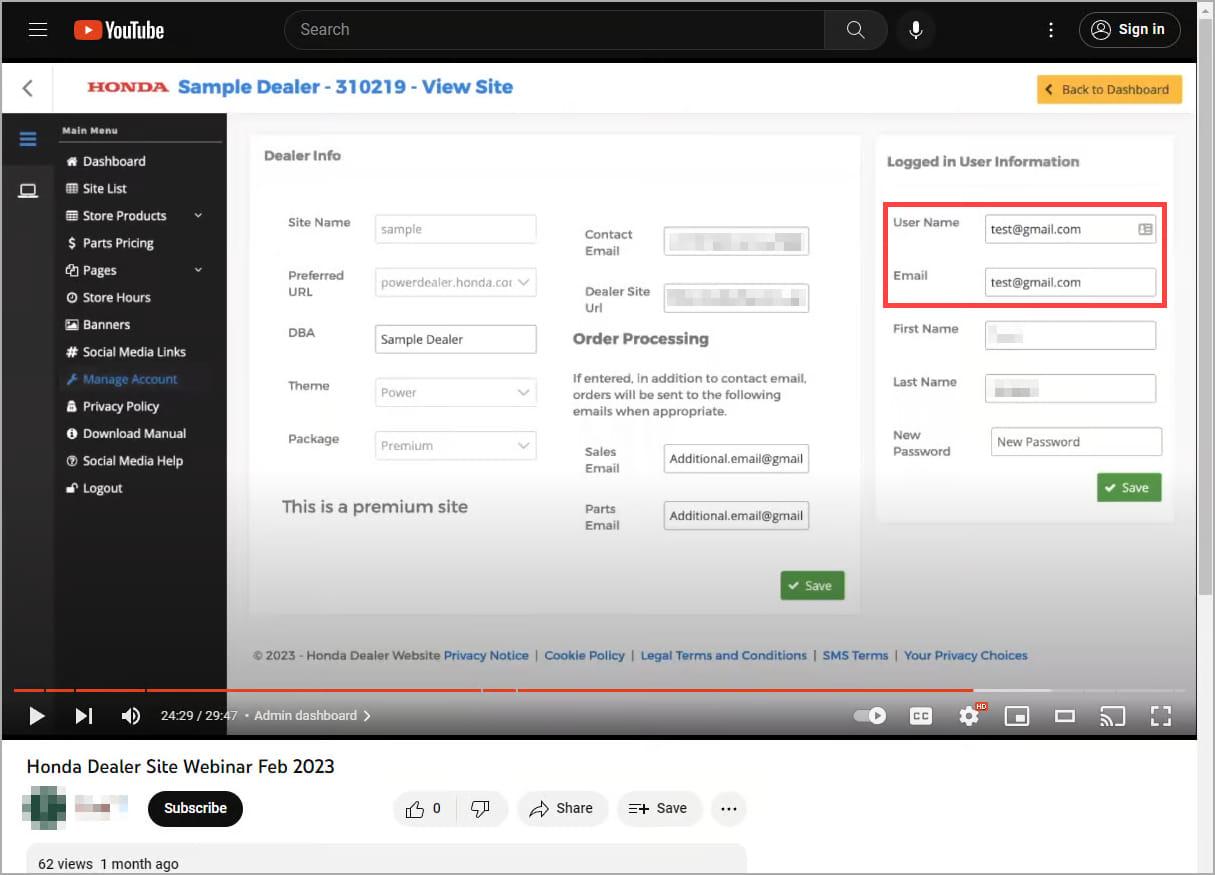
The researcher obtained a legitimate dealer email address from a YouTube video that showed how to use a test account to access the dealer dashboard.

Test account email exposed on YouTube video

YouTube video exposes test account email

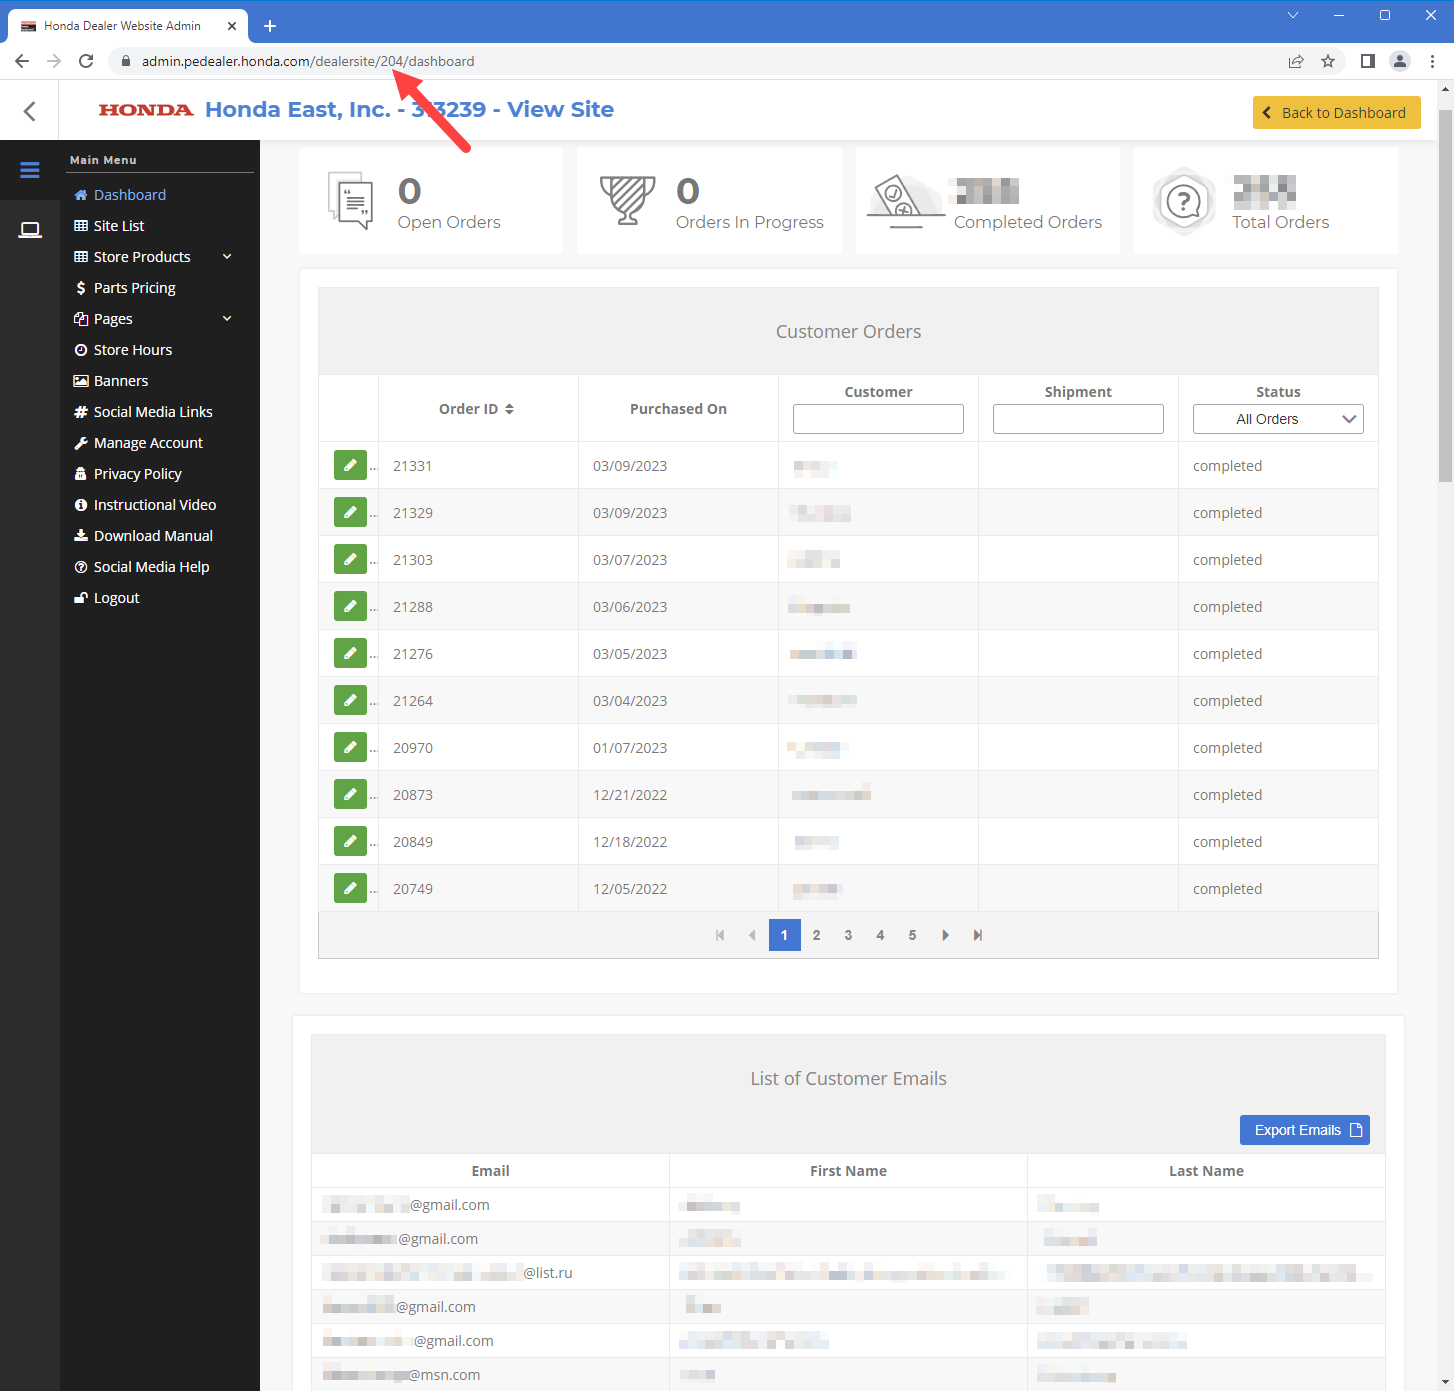
“This platform assigns numeric IDs to everything from orders to sites. The IDs were sequential so just adding +1 to the current ID would bring you to the next record”, the researcher explained.

The browser address bar displayed the ID that was given to each dealer site. He discovered that he could access the dashboard of a different dealer by altering that ID.

Adding +1 to the current ID would bring you to the next record

The last stage of the operation was to get access to Honda’s admin panel, which serves as the main management interface for the company’s e-commerce platform.

By altering an HTTP response to make it appear as though he was an admin, the researcher gained unrestricted access to the Honda Dealer Sites platform.

The Honda Dealer Sites admin panel

The Researcher said that highly targeted phishing campaigns might be developed with access to more than 21,000 client orders to deceive customers into submitting even more sensitive data or to try and install malware on their devices.

Also, more than 1000 active websites could have been secretly changed to include dangerous malware like credit card skimmers and crypto miners.

Stop Advanced Email Threats That Target Your Business Email – Try AI-Powered Email Security


[ad_2]
Source link