Apple Music Gets Crossfade, Collaborative Playlists, and More in iOS 17

0
[ad_1]

With the announcement of iOS 17 on Monday, Apple also made some big updates to Apple Music. It brings along Crossfade, Collaborative Playlists and a new music player.

It might sound odd that a new version of iOS brings a new version of Apple Music, but on iOS, stock apps are built into the system. Versus on Android where they can be updated via the Play Store.

Keep in mind that, to be able to use these features you will need to be on the iOS 17 beta. Which you can install here.

New Apple Music features in iOS 17

There’s three big features that are part of Apple Music in iOS 17. Let’s start with Crossfade. This will allow you to fade songs into each other. Instead of stopping and then a second later another song playing. It’s a simple feature, and honestly, a bit surprising that it took Apple Music this long to add it.

Next up is Collaborative Playlists. Again, another feature that other services have had for a while. This will basically allow you and your friends, or maybe family members, to create a playlist. This could be good for roadtrips and such. There will be a button at the top of the screen for adding and removing people from the playlist. This feature actually won’t be available until later this year. So it’s likely that this will be part of iOS 17.1.

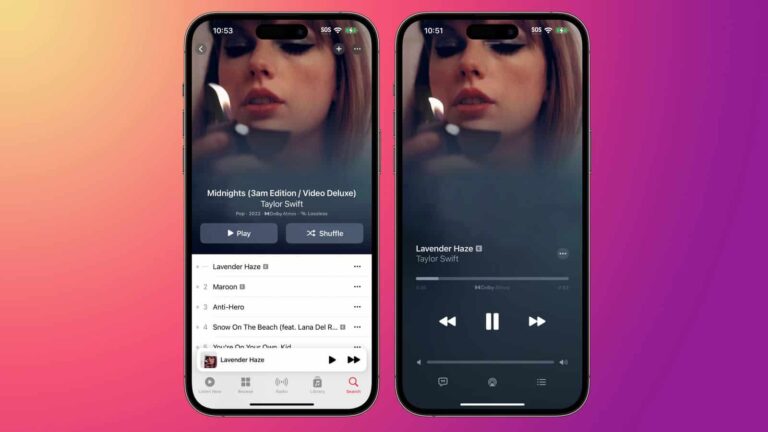
With iOS 17, Apple also introduced a new music player, and honestly, it looks pretty slick. Albums are now blended seamlessly into the bottom of the music player where the controls are. It looks sleeker than the current look of it just being in a box in the center of the screen. On playlists, and album screens, it will also blend into the list of songs. It looks much nicer now and much more modern.


[ad_2]
Source link

T-Mobile lays off almost 70% of its notable customer service team

0
[ad_1]

Several tech companies are dropping their workers like ballasts as they struggle to take on the diminishing economy. Job cuts are affecting major companies like Microsoft, Google, Meta, Etc. T-Mobile is no stranger to this as the company has dropped several hundred more employees. According to The Mobile Report, T-Mobile laid off nearly 70% of its notable T-Force customer service team.

If you are unfamiliar with what T-Force is, it’s T-Mobile’s very notable team of customer service specialists. They were introduced back in 2018 when John Legere was the CEO.  The consisted of several call centers full of waiting customer service representatives to help people with their troubles.

T-Mobile laid off the majority of the T-Force team.

This story includes the increasingly common reality of people clocking into work only to find that they’ve been locked out of their accounts. Since this is such a big layoff, that’s a lot of accounts being locked. In fact, the number of people laid off appears to be around 1,000.

That’s not huge relative to the company, but it’s a major problem because it affects only one division. Before the layoff, there were 17 call centers that T-Force employees worked in. However, the number was reduced to only five. As you can imagine, this put the entire department in chaos. They’re working with a staff that’s been reduced by 67%. So, if you are in need of customer assistance from T-Mobile, there may be a change in the service that you get. Just be patient.

As for the workers who are laid off, there is a silver lining to this story. Those who are laid off have a choice between two options. The first option is to be relocated to another department. This means that they won’t have to go job hunting or risk a lapse in payment.

The other option is to leave and accept the severance package. If they choose that option, They will receive paychecks up until August 4th. Also, They will receive 10 shares of T-Mobile stock which is valued at $1,322. Those affected workers have until June 12th to decide.


[ad_2]
Source link

Take matters into your own hands and delete these malicious new Android apps before Google

0
[ad_1]
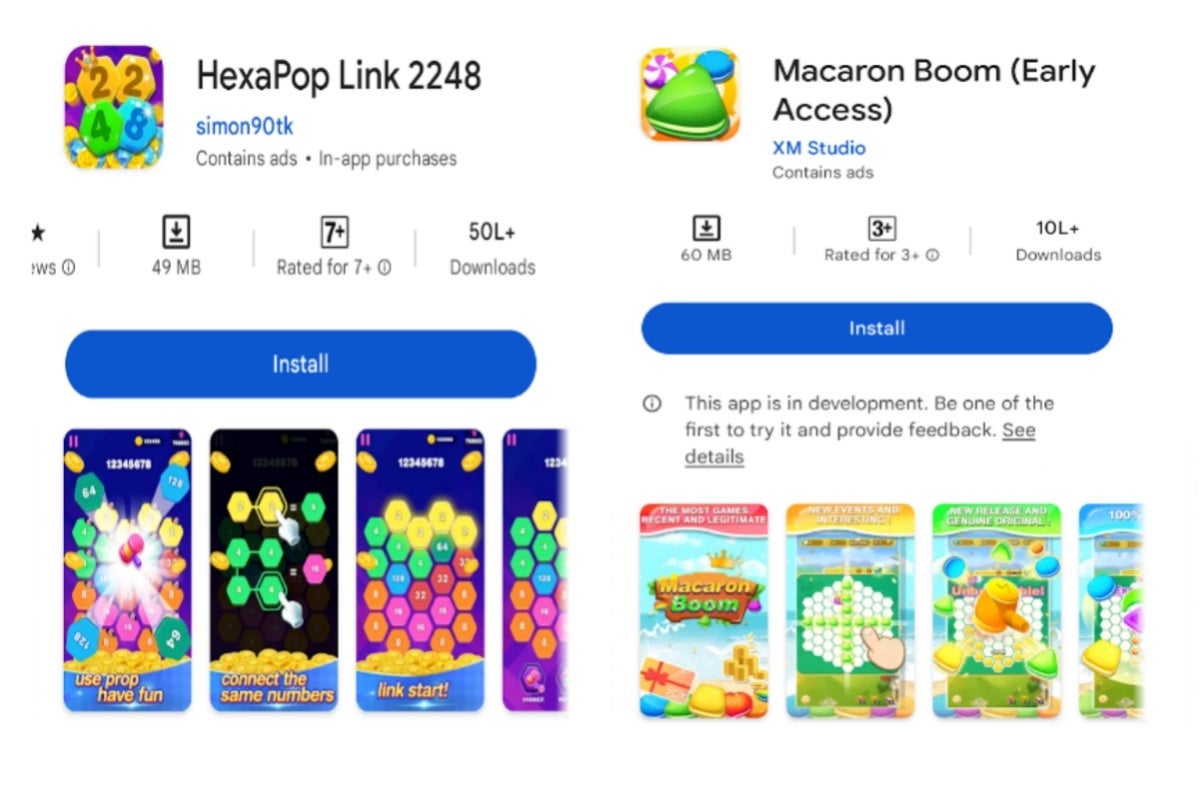
Remember that latest Android security threat concerning a large group of malicious apps left unattended by Google in its Play Store to wreak havoc upon millions of users around the world? No, we’re not talking about the one discovered just a little over a couple of weeks ago. Or the one from less than a couple of weeks prior to that. Or the one from a week before that.
Dubbed SpinOk by the firm’s cybersecurity experts, the spyware module attached to those shockingly popular apps is even more widespread than initially shown. Believe it or not, another company that claims to “predict cyber threats” has found an additional 193 (!!!) apps capable of snooping on their users, although for what it’s worth, this malicious conglomerate is thought to have amassed “just” around 30 million installations… so far.
The bigger problem is perhaps that a number of these newly surfaced spyware-injecting apps have yet to be deleted from Google Play, so the victim count could still rise. It’s unclear exactly why Google is not taking faster and more decisive action against all of these apps, leaving some of the most popular titles on the list below available for new downloads, but whether or not the search giant will do the right thing (eventually), you need to uninstall the following from your phones ASAP:

If you missed last week’s mobile security alert, you should know that SpinOk is among the most insidious types of malware discovered of late, infiltrating your Android phones through marketing SDKs (software development kits) that even app developers might confuse as innocuous.

The end goal, however, is often to gather personal data and files from unsuspecting users and transfer all that to remote servers for various shady purposes. Under no circumstance you should keep any of the apps listed above installed on your mobile device, even if you have reason to believe developers have removed the spying code via recent updates. After all, you know what they say about people who are fooled twice by the same wrongdoer.


[ad_2]
Source link

MOVEit Hack – BBC, British Airways Employees Data Exposed

0
[ad_1]
MOVEit Hack

A major MOVEit Hack has impacted many businesses, notably the BBC, British Airways, Boots, and Aer Lingus.

The organizations acknowledged that tens of thousands of British Airways, Boots, and BBC staff had their personal information compromised due to a large-scale breach that targeted a popular file transfer tool. 

The compromise was discovered at Zellis, the payroll supplier for BA, the BBC, and Boots. The Nova Scotia provincial government in Canada was also struck.

“We have been informed that we are one of the companies impacted by Zellis’s cybersecurity incident, which occurred via one of their third-party suppliers called MOVEit,” said an airline representative.

The data from Zellis and the Nova Scotia government was exposed as a result of their use of the MOVEit file transfer tool, according to separate statements from both organizations.

Zellis declined to indicate how many clients were affected. 

The Breach’s Stolen Information

According to the Daily Telegraph, which initially reported the hack, an email issued to BA workers stated that the exposed information included names, addresses, national insurance numbers, and banking information. BA stated that the hack affected employees paid through BA payroll in the UK and Ireland.

Additionally, employees were told that the data included in the hack included their names, surnames, employee numbers, dates of birth, email addresses, the first lines of their home addresses, and national insurance numbers.

The BBC believes the leak did not involve employee bank information.

“We are aware of a data breach at our third-party supplier, Zellis, and are working closely with them as they urgently investigate the extent of the breach. We take data security extremely seriously and are following the established reporting procedures,” the spokesperson said.

Zellis stated that a “small” number of its customers were affected by a vulnerability in MOVEit, the company’s file transfer technology.

“We can confirm that a small number of our customers have been impacted by this global issue, and we are actively working to support them,” the company stated, adding that the UK data protection agency and the National Cyber Security Centre had been notified. 

It is believed that the incident affected eight Zellis customers in the United Kingdom and Ireland.

Microsoft’s threat intelligence team ascribed the MOVEit assaults to a group known as Lace Tempest.

It said the organization was notorious for ransomware activities and maintaining an “extortion site” with data collected from Clop ransomware attacks.

Microsoft added: “The threat actor has used similar vulnerabilities in the past to steal data and extort victims.”

MOVEIt has been at the center of security industry concerns since its maker, Massachusetts-based Progress Software, discovered a weakness last week that might have allowed hackers to intercept data being transferred through the program.

MOVEit said on Monday that it addressed the vulnerability exploited by the hackers and was working with specialists to analyze the issue “and ensure we take all appropriate response measures.”

Struggling to Apply The Security Patch in Your System? – 
Try All-in-One Patch Manager Plus


[ad_2]
Source link

Release date, specs, price & more

0
[ad_1]

The Google Pixel 8 is one of two smartphones Google will announce later this year. This phone is actually a part of the company’s flagship lineup, it’ll launch alongside its ‘Pro’ sibling. We’ll get more and more information about the device as we’re getting closer to the launch date. That’s why this article will be updated accordingly.

We already have plenty of information about the Pixel 8, and we’ll do our best to relay that information to you below. The phone is set to come in a smaller chassis than last year, with a shiny new processor, and much more. It’ll differentiate from the ‘Pro’ model, of course, hence the separate preview article.

This article will be regularly updated with new information on the Google Pixel 8 (this is a preview article) — both official teasers and credible leaks, rumors, and insider claims — as it becomes available in the run-up to the release of the upcoming Android smartphone. The last update was made on June 6 (original publishing date).

When will the Google Pixel 8 be released?

Google is expected to announce its Pixel 8 series in either September or October this year. The Pixel 7 series arrived on October 6 last year. Chances are that it’ll happen in October this time around too, but we cannot be sure. Google will announce the launch event later in the year, so we’ll have to wait and see. Both smartphones are expected to ship in around a week after the launch, though.

What models are coming?

If the Pixel 7 is any indicator, the Pixel 8 will come with a single RAM setup, and more than one storage option. If we had to guess, we’d say that 128GB and 256GB storage variants will be available, at least. It’s also possible Google will ditch the 128GB storage model entirely, we’ll have to wait and see. The device is expected to offer 12GB of RAM. The ‘Pro’ variant will be entirely different than the vanilla model, and we’ll talk about it in a separate article.

How much will the Google Pixel 8 cost?

The Pixel 8 price tag did not surface just yet. Google managed to surprise us with the Pixel 7 price, however. The Pixel 7 launched with a $599 price tag, so it was considerably more affordable than its ‘Pro’ sibling. If Google manages to keep a similar price tag for the Pixel 8, that would be great, of course. Even if it ends up being slightly more expensive, that’s doable. Google should be able to pull that off, as the Pixel 8 won’t be a huge change design-wise. It will include a number of new components, and that, along with some other factors, could boost its price tag. We’ll have to wait and see.

What will the Google Pixel 8 look like?

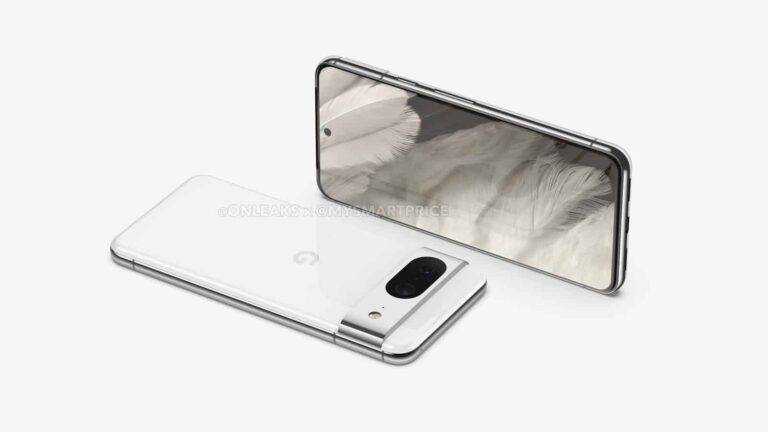
The Google Pixel 8 will retain the Pixel 7’s design language. It will look a bit different, however. The Pixel 7 was a squarish phone, while the Pixel 8 will be a bit more curved. The camera sensors inside the camera visor will also look a bit different, at least based on the CAD-based renders that surfaced (shown at the end of this section). The bezels on the device will be truly thin, though they probably won’t be uniform. It would be great if Google could pull it off, though, as it did with the Pixel 5.

The camera visor will once again protrude on the back quite a bit, while the phone will be made out of metal and glass. The camera visor will connect to the phone’s frame on the sides, as it did on the Pixel 7. A flat display is expected on the front, with a centered display camera hole at the top. All the physical buttons will sit on the right-hand side of the phone. The power/lock key will sit above the volume up and down buttons, as we’re used to seeing from Pixel phones.

This handset will be smaller than its predecessor. It is tipped to feature a 6.16-inch display. The Pixel 7 included a 6.3-inch display, officially, at least it was marketed as such. It’s possible this panel will be marketed as a 6.2-inch panel, we’ll see. The good thing is, there will be more of a size difference between the Pixel 8 and Pixel 8 Pro than it was between their predecessors. The Pixel 7 and Pixel 7 Pro were not that different size-wise. The Pixel 8 will cater more to people who want a more compact phone.

What specs will the Google Pixel 8 have?

The Google Pixel 8 will be fueled by the Google Tensor G3 processor. That is the third-gen processor from Google, and it’ll bring some notable improvements over the first two generations. This chip will offer a 1+4+4 layout, with a single big core, the Cortex-X3. The cores will get a boost across the board, a considerable boost over the original Tensor and Tensor G2. UFS 4.0 will also be supported, and more.

The phone will offer either 8GB or 12GB of RAM, and we’re expecting LPDDR5X RAM this time around, though such info did not leak yet. We’ll be able to choose between at least two storage options, most likely 128GB and 256GB storage variants. The phone will include a 6.16-inch display on the front. That will be a 120Hz panel, and it’ll most likely be a fullHD+ AMOLED display. The display will be flat.

A rumor suggested that the Pixel 8 Pro could include a new main camera sensor, but it did not say anything about the regular Pixel 8. Google will either stick with the ISOCELL GN1 inside this phone, or switch to the GN2. The second camera on the back will be an ultrawide unit, and Google could stick with the same unit as in the Pixel 7. One thing is for sure, that will be an ultrawide camera, but the sensor is still a mystery.

The phone’s battery size did not surface just yet. What did surface, however, is the fact that Google won’t improve wireless charging here. The Pixel 8 will support wireless charging, but don’t expect high charging speeds to be on offer.

Should you wait to buy the Google Pixel 8?

Should you wait for the Pixel 8, or buy the Pixel 7 instead? Well, considering that we’re already in June, and considering the improvements the Tensor G3 will bring… you’re probably better to wait for the Pixel 8. Based on the rumored info, at least, the Tensor G3 will be a major improvement compared to the Tensor G2. Not only that, but the Pixel 8 will be spruced up from the design’s standpoint, and should be able easier to use with one hand, on top of everything. There’s always the Pixel 7a option, if your budget is not high enough. If it is, however, you’re advised to wait and see what the Pixel 8 will bring.
[ad_2]
Source link

Apple shows off new products & features via official videos

0
[ad_1]

Apple announced a bunch of new products and features during WWDC 2023, and it decided to show them off via official videos. Those videos got shared on YouTube, and we’re here to talk about them.

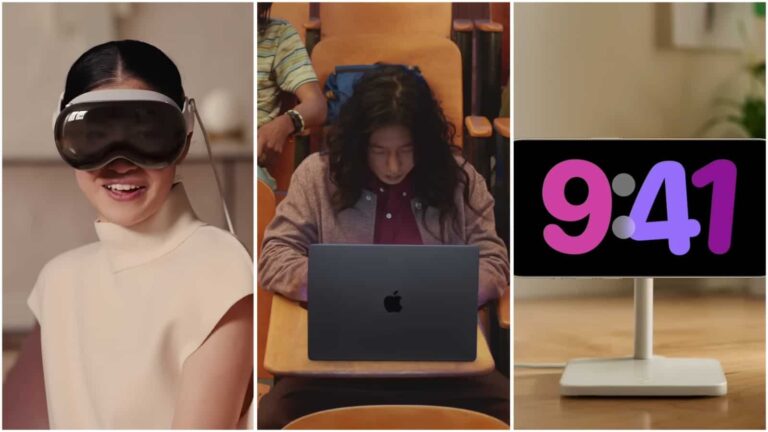
The showpiece of the event was the Apple Vision Pro, Apple’s mixed-reality headset. It was the ‘One more thing’ announcement for Apple, and it’s an extremely expensive piece of tech at $3,499.

Apple shared several videos to show off its new products & features

This device will become available to purchase early next year, and you can check it out in the video provided below. This video actually has a duration of almost 10 minutes. Why? Well, there’s a lot to talk about here.

This video shows you how the device works exactly, not in general, but with specific content. It shows you how the device works while you’re watching movies, in a work environment, with FaceTime, and more.

The company also announced the very first 15-inch MacBook Air

One of the company’s hardware announcements was also the 15-inch MacBook Air. The video included below this paragraph will show you the device. This one is much shorter than the previous video, at approximately two and a half minutes.

This is the very first 15-inch MacBook Air, and it comes with Apple’s M2 chip. Apple also claims it can offer up to 18 hours of battery life, and has six speakers included with Spatial Audio support. Watch the video to find out more.

Various iOS 17 features got announced, including NameDrop, Contact Posters, and more

The last video we’ll talk about is focused on iOS 17 and connected features. It has a duration of two and a half minutes as well, and it’s embedded below.

Apple talked about various new features during the keynote. One of the most notable ones is ‘NameDrop’. This is a new AirDrop-like feature that allows you to swap contact information with ease, by bringing two iPhones close together.

It also touches upon ‘Contact Posters’ that you’ll be able to design yourself, and FaceTime’s ability to record a message if someone is not picking up. There are a ton of additional features mentioned here, though, we’ve only scratched the surface.


[ad_2]
Source link

Google Chat update streamlines conversation experience

0
[ad_1]

Google recently announced a small yet important update that’s supposed to make the further improve the conversation experience. A new feature will be rolled out to Google Chat users that should make it easier to find their most relevant conversations.

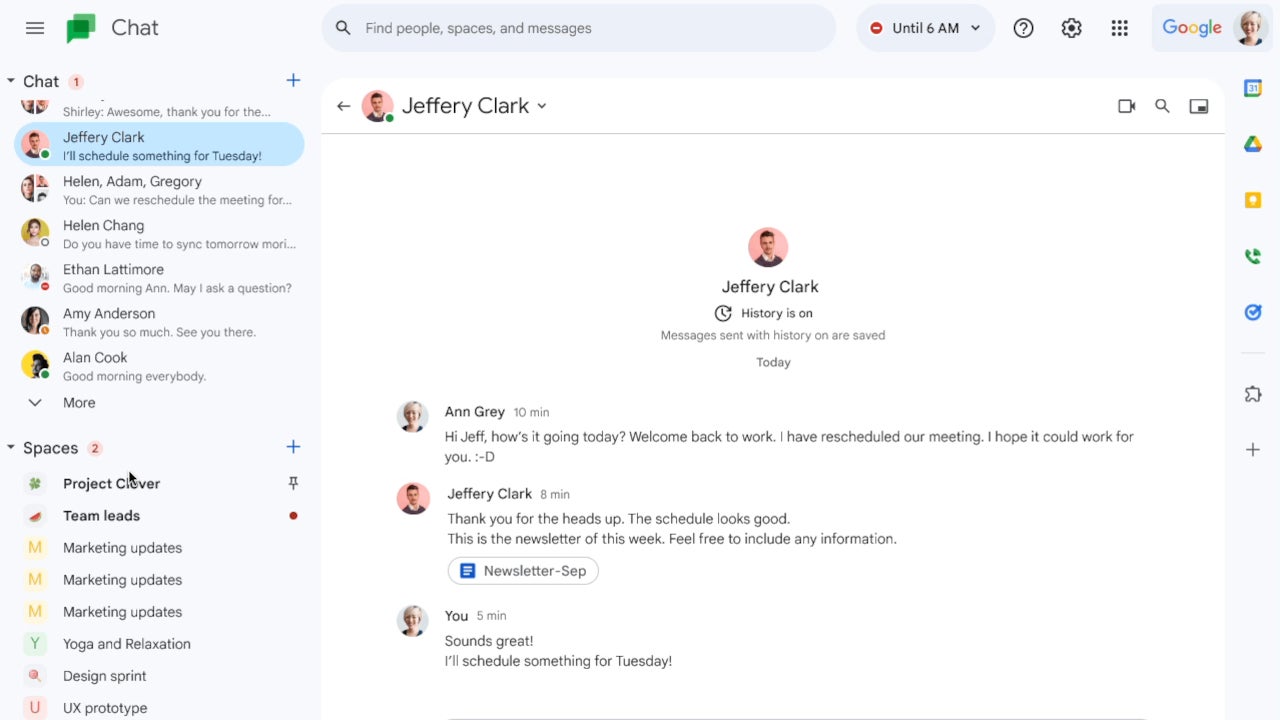
The new “chat declutter” feature automatically hides direct messages and conversations that have been inactive for the last 7 days. However, this feature won’t kick in until a section has more than 10 conversations. More importantly, Google says that the new feature will not affect pinned conversations, so you will keep seeing them at the top even when it’s active.

It’s important to mention that even with the new feature enabled, you will still be able to see your older direct messages and spaces if you want to. To do that, simply toggle the “More” button to view and access the entire list of your Chat conversations.

According to Google, the latest Chat update will be rolled out gradually and it should take up to 15 days for everyone to get it. Speaking of which, the new feature will be available to all Google Workspace customers and users with personal Google Accounts.

This is the second small update that Google Chat users are getting in less than a month, after Google rolled out “message quoting” in early May.

[ad_2]
Source link

BBC affected by malware gang attack

0
[ad_1]

A cyber attack against document transfer app MOVEit has resulted in data breaches of several high-profile UK organizations and businesses. Those affected includes the British Broadcasting Company (BBC), health and beauty retailer Boots and UK-based airline British Airways. 

The attack involved the exploitation of a critical vulnerability in MOVEit’s infrastructure which allows malicious actors to break into company networks and steal data. The vulnerability was flagged by security researchers and the US government on June 1. The US Cybersecurity and Infrastructure Security Agency (CISA) urged all MOVEit clients to check for indications that malicious actors had gained unauthorized access to their networks over the past 30 days and to download and install the software patch released by MOVEit to address the issue. 

On June 5, payroll provider Zellis issued a statement that its third-party provider, MOVEit, had been the victim of a cyber attack, leading to data breaches for some of its customers. Zellis’ customers include a number of high-profile companies such as Dyson, Harrods, Sky, Land Rover and Jaguar. According to Zellis, however, only a “small number of [its] customers [were] impacted by this global issue”. 

Once Zellis became aware of the attack, the company disconnected its server that utilizes MOVEit software and engaged an external cyber security company to conduct a forensic investigation into the cyber attack and to further monitor its systems. The Information Commissioner’s Office (ICO), the Data Protection Commission (DPC) and the National Cyber Security Center (NCSC) in both the UK and Ireland have also been contacted regarding the cyber security incident.

The attack against MOVEit was allegedly carried out by ransomware gang Clop. Clop ransomware was first identified in February 2019. The gang has appeared to be getting more active in the past few months, with more victims’ details posted to the Clop malware leaks site, including a cyber attack carried out against cyber security company Fotra GoAnywhere.


[ad_2]
Source link

KeePass Vulnerability Could Expose Master Password In Plaintext

0
[ad_1]

The popular password manager KeePass had a severe security vulnerability exposing users’ master passwords in cleartext. Following the bug report, the service patched the flaw with the subsequent KeePass release, along with numerous other feature upgrades.

KeePass Vulnerability Could Leak Master Passwords

A security researcher with alias “vdohney” found a serious security issue affecting the KeePass password manager. Specifically, exploiting the vulnerability could let an adversary to gain access to KeePass master passwords in plaintext.

As explained in the researcher’s bug report, the default KeePass settings could allow a user to extract the master password from the process memory dump. Executing this activity didn’t require code execution, nor did it receive any impact from the memory source.

Given a process memory dump, I am able to reconstruct the master password. It doesn’t matter whether the workspace is locked or not, it works regardless. The memory source also isn’t important – for example, it can be a pagefile (swap) or the hibernation file. No code execution is needed, just the memory alone.

Also, the security flaw would remain there even after locking the workspace. The researcher noted this phenomenon as violating KeePass’s claim to close the database file after locking the workspace.

Specifically, the issue existed with the SecureTextBoxEx class. After a user typed the KeePass master password, the tool would expose the master password characters in leftover strings.

Alongside sharing the details in the report, the researcher also demonstrated the flaw (CVE-2023-32784) in the proof-of-concept shared on GitHub.

KeePass Patched The Flaw

While the vulnerability seemed severe, interestingly, it didn’t affect passwords when pasted from the clipboard. Instead, it only worked with passwords typed manually. (Though, copying passwords and leaving them on the clipboard is another bad security practice.) Also, the vulnerability didn’t expose the first character of the master password but rather the following characters only.

Nonetheless, to eliminate any security risks, Dominik Reichl, KeePass’ creator and developer, addressed the issue with the latest release. As explained in his response to vdohney, KeePass now uses the Windows API functions for “getting/setting the text of the text box” instead of creating managed strings. Also, the tool now creates dummy fragments in the process memory to prevent determining the correct fragments.

The developers released these fixes with KeePass version 2.54. Besides this bug fix, the new password manager version includes several improvements and feature upgrades.

Some noteworthy changes include the storage of Triggers, global URL overrides, password generator profiles, and other settings to the enforced configuration file, adding a dialog with the “Enforce Options” setting, and enhancing the Export confirmation dialog boxes.

Now that both the vulnerability PoC and the respective patch have arrived publicly, all KeePass users must update their devices immediately with the latest KeePass releases to remain safe from potential attacks.

Let us know your thoughts in the comments.


[ad_2]
Source link

Hublot intros a $5,400 smartwatch with Wear OS 3

0
[ad_1]


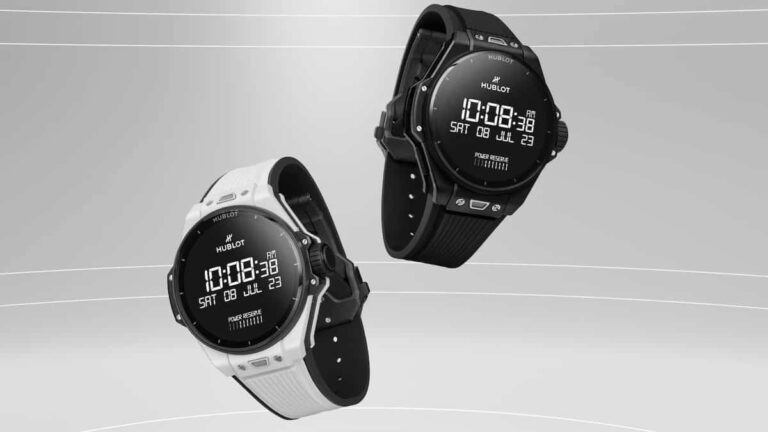
Hublot has announced yet another ultra-expensive smartwatch, this one costs $5,400, and it comes with Wear OS 3 pre-installed. The watch is called the Hublot Big Bang E Gen 3, which is a mouthful.

The Hublot Big Bang E Gen 3 is a $5,400 Wear OS smartwatch

Hublot kicked off this smartwatch series in 2020, and this is the latest offering. This is a 44mm watch, and it’s built using “microblasted and polished ceramic”, as the company wanted to achieve a textured look. Ceramic is well-known for its durability, and it is also considered a premium material in today’s tech products.

This is a circular smartwatch, with a button on the right-hand side. That button doubles as a rotating crown, and it does protrude quite a bit. The watch comes in black and white colors, as you can see in the provided images.

The Snapdragon Wear 4100+ SOC fuels this smartwatch, which is a bit surprising. That SoC is quite dated at this point, and we expected to see something newer on the inside, especially considering the price tag. The Snapdragon W5+ would be nice to see.

It has all the sensors you’d expect

You will get a heart rate monitor here, an accelerometer, a gyroscope, an ambient light sensor, and more. Bluetooth is also a part of the package, of course, as is Wi-FI connectivity, an NFC chip, and a GPS module.

There is a 1.39-inch 454 x 454 AMOLED screen included on the front here. That display has a 327 PPI, and it’s protected by ‘sapphire crystal’. There are 11 digital watch faces included here.

The Hublot Big Bang E Gen 3 is water resistant (it’s 3 ATM rated), but don’t go swimming with it. A 400mAh battery is also included here, and considering what SoC the company used here, and that battery capacity, this smartwatch will hardly go over a day’s worth of battery life. We do hope Hublot manages to surprise us, though.

This watch comes in two color variants

A rubber strap is also included in the package, with a ‘One Click’ system from Hublot. The black variant is officially called ‘Black Magic’, while the white one has a ‘White Ceramic’ name.

The Hublot Big Bang E Gen 3 is already available to purchase in the US. You’ll have to part with $5,400 in order to get it, though.

Buy the Hublot Big Bang E Gen 3 (Hublot)


[ad_2]
Source link