Samsung announces “Bespoke Life” hardware event for June 7

0
[ad_1]

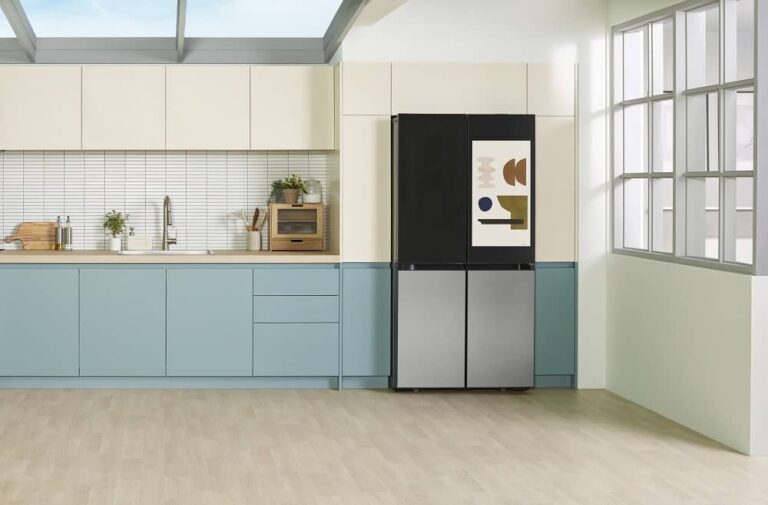
Samsung has announced a new hardware launch event for June 7, 2023. No, it isn’t time for the next Galaxy Unpacked just yet. Instead, the company is gearing up to unveil its next-gen Bespoke home appliances at its upcoming “Bespoke Life 2023” event. It hasn’t named any products, though.

Samsung will unveil new Bespoke home appliances at the event

In a public invitation post on its Newsroom, Samsung said that the event will showcase its “vision for the future of Bespoke and the expansion of your home life possibilities”. An accompanying infographic reveals sustainability will be one of its main focuses for the upcoming products. If fact, the company has been increasingly making its products eco-friendly in recent years. It uses recycled materials in several components and has reduced the use of plastic across the board.

Connectivity and style are the other two areas that Samsung has prioritized for its modern home appliances. All of its next-gen Bespoke home appliances will fit right into its SmartThings-powered connected ecosystem. The Korean behemoth has been repeatedly talking about the expanding ecosystem of connected devices, and the need to secure this ecosystem. So we may hear something about its latest security measures as well.

“Bespoke Life 2023 will showcase Samsung’s commitment to transforming customers’ lives through sustainability, connectivity, and design, delivering streamlined convenience and sustainable innovations that enrich customers’ daily routines,” the company said in its public invitation.

As for what products we will see at the event, only Samsung knows. We are expecting new bespoke refrigerators, washing machines, microwave ovens, and other home appliances. The company will live stream the Bespoke Life 2023 event on June 7 globally. You can watch it on its official YouTube channel as well as Samsung.com.

The event begins at 10:00 EDT (14:00 GMT/16:00 CEST). If you can’t tune in live, we will cover all major announcements from the company here on Android Headlines.

Galaxy Unpacked may follow in July

The launch of Samsung’s new home appliances in June should be followed by another big hardware event in July. Rumors are that the next Galaxy Unpacked will take place in late July, about two weeks earlier than last year. The event will bring the Galaxy Z Fold 5 and Galaxy Z Flip 5 foldables, Galaxy Tab S9 series flagship tablets, Galaxy Watch 6 series smartwatches, and possibly a new pair of TWS earbuds. We will let you know once we get official word from Samsung about the next Galaxy Unpacked event.

Samsung bespoke Life 2023 event


[ad_2]
Source link

ChatGPT CEO May Leave Europe

0
[ad_1]
ChatGPT CEO

In response to the future artificial intelligence (AI) restrictions by the European Union, OpenAI CEO Sam Altman stated that the maker of ChatGPT may think about leaving Europe.

The EU is developing the first set of international regulations for AI. The law requires businesses using generative AI tools, including ChatGPT, to report any copyrighted materials used to create such systems.

Altman claimed his company wanted to “work with the government” to stop the technology from being harmful and compared the quick development of AI to the discovery of the printing press. 

Even Altman admitted that the introduction of AI will impact jobs and that the government would need to devise ways to “mitigate that.”

AI Regulations

Altman clarified this at the University College London event: “The right answer is probably something between the traditional European-UK approach and the traditional US approach,” he added. “I hope we can all get it right together this time.”

Altman stated that OpenAI would attempt to abide by the European regulation when it is established before thinking about leaving.

“Either we’ll be able to solve those requirements or not. If we can comply, we will, and if we can’t, we’ll cease operating”, Altman said.

This month, the EU legislators agreed on the act’s drafting. The representatives of the Council, the Commission, and the Parliament will now discuss the bill’s final details.

“The current draft of the EU AI Act would be over-regulating, but we have heard it’s going to get pulled back. They are still talking about it”, Altman told Reuters.

In a report analyzing the EU AI Act, the Future of Life Institute described general-purpose AI as AI systems with a broad range of potential uses, both intended and unanticipated by the developers.

Future of AI Systems

“There’s so much they could do like changing the definition of general-purpose AI systems. There’s a lot of things that could be done”, Altman said.

Legislators have proposed the term “general purpose AI system” to describe AI systems with multiple uses, such as generative AI models like Microsoft-backed ChatGPT.

While addressing at University College London, the CEO of OpenAI acknowledged disinformation concerns surrounding AI, highlighting, in particular, the tool’s capacity to produce false information that is “interactive, personalized [and] persuasive,” and saying that more work needed to be done on that front.

Nicole Gill, executive director and co-founder of Accountable Tech, wrote an op-ed for Fast Company last week comparing Altman to Meta’s founder and CEO Mark Zuckerberg, writing, “Lawmakers appear poised to trust Altman to self-regulate under the guise of ‘innovation,’ even as the speed of AI is ringing alarm bells for technologists, academics, civil society, and yes, even lawmakers.”

Shut Down Phishing Attacks with Device Posture Security – Download Free E-Book


[ad_2]
Source link

The At a Glance widget will show your ridesharing information

0
[ad_1]

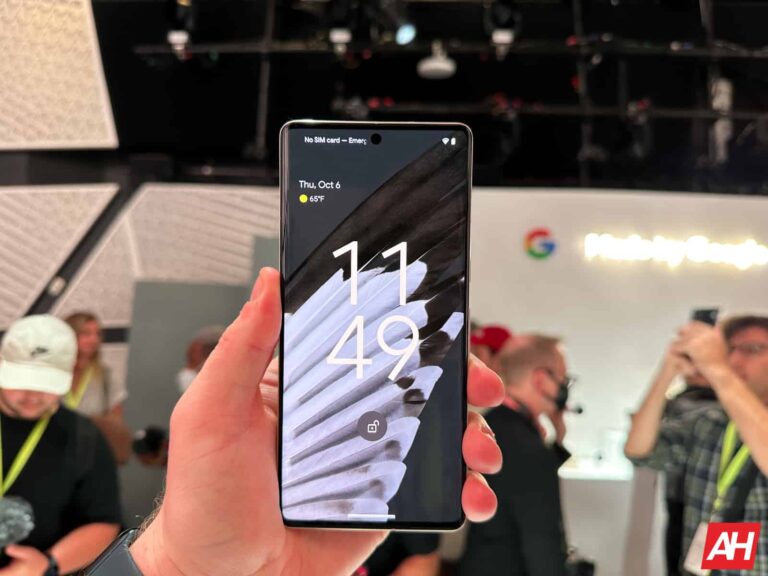
The At A Glance widget in the Google Pixel launcher is a very useful tool. It can show you all types of useful information like the weather, the air quality, upcoming events, Etc. According to 9To5Google, the At A Glance widget is going to start showing you your ride-sharing information.

If you want to know how to customize your At A Glance widget, you should simply hold your finger down on the widget. When the Customize button pops up, you’ll be able to change what information it shows you, and how it’s displayed.

The At A Glance widget will show you your ride-sharing information

This shouldn’t come as much of a surprise, as we heard rumors about this before. Basically, if you’re using a ride-sharing service such as Uber or Lyft, and you set up a ride, then you will see the status of that ride on At A Glance widget.

Right now, we know that both Uber Eats and Lyft are supported, but we’re not sure about other right-sharing services. Smaller riding-sharing services might not be supported as of yet.

When you have a ride coming, the widget will show you how far away it is from your location. So, if you’re checking for your ride, you won’t have to open the app just to check the status. It will be posted on your phone’s home screen and lock screen.

This is rolling out now, so there’s a chance that you will be able to enable it. However, there’s also a chance that you will not see this feature. If not, then you may just want to wait a day or so for it to come to your device. If you want to enable it, go to your At A Glance settings, head to the section that says ride-sharing, and flip that toggle.

While you’re at it, you can check out some of the other features that the At A Glance widget provides. Some of them may come in very handy.


[ad_2]
Source link

Samsung announces global launch of its 2023 smart monitors

0
[ad_1]

Samsung has announced the global launch of its 2023 smart monitor lineup. Launched in its homeland South Korea early last month, the M50C, M70C, and M80C smart monitors will soon be available in other parts of the world, including the US. The devices are already on sale in South Korea.

Samsung brings its latest smart monitors to more markets

Samsung’s latest smart monitors come in multiple sizes and colors. Depending on where you live, you may pick one or all three models in 27-inch and 32-inch sizes. All monitors feature a flat screen with a 16:9 aspect ratio, 60Hz refresh rate, 4ms response time, and a 3000:1 typical contrast ratio. The M80C and M70C boast a 4K UHD display (3,840 x 2,160 pixels resolution), while the M50C settles for an FHD screen (1,920 x 1,080 pixels). Their peak brightness reading comes in at 400 nits, 300 nits, and 250 nits, respectively. The M80C is HDR 10+ certified, but the other two only offer HDR10.

The M80C and M70C feature built-in voice assistant support, including Samsung Bixby and Amazon Alexa, with far-field mics. The former model also gets built-in SmartThings Hub support. All three smart monitors offer VOD (video-on-demand), Gaming Hub, Workspace, My Contents Mobile Connection, Video Communication (Google Meet), dual-screen multi-view support, and more smart features. You can wirelessly connect the monitors to your mobile devices to view content on the big screen. Samsung has included two 5W speakers on all three models.

Ports include one HDMI 2.0, two USB-A, and one USB-C (65W) port on the M80C and M70C. The M50C features two HDMI 1.4 and two USB-A ports. All three models come with an in-box remote that supports USB-C charging. Samsung has also included a detachable FHD camera in the retail box with the M80C. It attaches magnetically to the monitor and supports features like Auto Framing. You can remove the camera when not needed. The M70C and M50C are also compatible with an external camera, with the former featuring Pogo pins for camera attachment.

Price and availability in the US

Samsung hasn’t specified the release date for its 2023 smart monitor lineup in the US. All it says is that the new monitors will be available on its official website and in select retailers nationwide starting in June. The company has priced the 27-inch M50C at $279.99, the 27-inch M70C at $549.99, and the 27-inch M80C at $649.99. If you pick up the 32-inch variants, you’ll have to shell out $299.99, $599.99, and $699.99, respectively for each model. The M50C comes in black and white colors, M70C in Warm White, and M80C in Warm White, Sunset Pink, Daylight Blue, and Spring Green colors.


[ad_2]
Source link

Free VPN Data Breach – Over 360 Million User Records Exposed

0
[ad_1]

Based on reports from Jeremiah Fowler, a non-password-protected database exposed nearly 360 million records related to a VPN.

The database contained email addresses, device information, and even website references that users visited.

According to the investigation, these records belonged to a VPN service provider named SuperVPN.

Interestingly, there were 2 applications in both App Store and Google Play Store with the same name. They both shared a similar logo.

SuperVPN – Two Different App Owners

Furthermore, the two applications had two different developers: SuperSoft Tech and Qingdao Baichuan Network Technology Co.

Both of these applications together had more than 100 million downloads worldwide. Hence, finding which one of the companies was leaking became the first task.

Jeremiah Fowler contacted both companies regarding this data exposure as a responsible disclosure but didn’t get any comments or response from them. 

In addition, Fowler also found a reference to a company named Changsha Leyou Baichuan Network Technology Co in the database, along with some notes in the Chinese Language. All these pointed to Qingdao Leyou Hudong Network Technology Co as the owner of these databases.

Both of these companies never confirmed if they are associated with each other or share the same developer.

However, the database also contained customer support emails from other VPN provider names such as Luna VPN, Storm VPN, Radar VPN, Rocket VPN, and Ghost VPN (Not CyberGhost). It cannot be concluded if the same company owns all of them.

Risk of VPN Data Breach

Users use VPNs to protect their privacy and gain a level of security for their data. Suppose a VPN is subject to a data breach.

In that case, it can lead to sensitive information details such as;

  • Login credentials
  • IP addresses
  • Browsing history
  • Geolocation
  • Sensitive user data.

Threat actors who gain access to this data can potentially conduct phishing attempts, spam messages, and other social engineering attacks.

Additionally, threat actors can find the geographic location of any users and their ISP providers with the IP address leaked from the VPN database and potentially conduct a Denial of Service (DoS) attack on the user.

It is always recommended to go with a reliable VPN service provider and read their privacy policy, user agreements, and terms of service to understand what level of data is being logged and used.

Shut Down Phishing Attacks with Device Posture Security – Download Free E-Book


[ad_2]
Source link

Galaxy S20 FE, S20 FE 5G & A34 5G getting May update globally

0
[ad_1]

A couple of weeks back, Samsung released the May 2023 security update for the Galaxy S20 FE in select European countries. The company is now pushing the new security patch to the device globally, also covering the 5G model. The latest SMR (Security Maintenance Release) is also available for the Galaxy A34 5G in some regions.

The May SMR was first released for the 4G version of the Galaxy S20 FE in Russia. Samsung gradually expanded the rollout to more countries in the region. In recent days, the new security patch has reached the phone pretty much everywhere. For 4G models, the new firmware build number is G780GXXU4EWD2 or G780FXXUBFWD2 depending on your region and model number.

The same update for the Galaxy S20 FE 5G, meanwhile, comes with build numbers G781USQSAHWD4 (US carrier-locked version), G7810ZHS4HWE1 (Hong Kong and China version), and G781BXXS5HWD4 (global version). Samsung appears to be pushing some system optimizations along with the latest security fixes to the phone in select markets. But there aren’t any new features to look forward to here.

As far as the security fixes are concerned, Samsung’s monthly security bulletin has already revealed that the May SMR patches more than 70 issues. Around 20 of those are Galaxy-specific issues and aren’t found in Android products from other brands. The remaining patches concern flaws found in Android OS and other partner components. These patches come direct from the vendor of the respective component. At least six vulnerabilities patched this month were critical.

The Galaxy A34 5G is also getting the May security update

The aforementioned vulnerability patches are also rolling out to the Galaxy A34 5G. The newly-launched mid-range smartphone is picking up the May SMR widely in Europe, Asia, and Africa. The update in the former region comes with the build number A346BXXU2AWE2, while that in the latter two regions is A346EXXU2AWE2. Samsung should soon cover units in Latin America as well. The Galaxy A34 5G didn’t arrive in the US, at least not yet.

Along with the latest security fixes, the Galaxy A34 5G may also be getting Samsung’s Image Clipper feature. The official changelog doesn’t explicitly name this addition, but says the update brings improvements to “Camera and Gallery functions”. That’s precisely what the changelogs for updates containing Image Clipper for other devices mentioned. This feature lets you quickly crop out objects from images when viewing them in Samsung’s Gallery app. You can crop out objects by pressing and holding onto them for a few seconds.


[ad_2]
Source link

The PS VR2 reaches 600k units sold in under two months

0
[ad_1]

Sony’s PS VR2 headset has actually done quite well, according to a recent PDF from Sony Interactive Entertainment CEO Jim Ryan, showing sales of the headset following its release back in February.

Although some had suspected that the headset wasn’t doing well, data from SIE suggests otherwise. Ryan confirms that sales of the PS VR2 had reached 600,000 units within the first six weeks of the headset’s launch. The PS VR2 officially launched back on February 22 of 2023.

600,000 units may not sound like a lot compared to the amount of PS5 consoles sold by the time the headset was available. But on the contrary, it’s a significant success from SIE’s standpoint. 600,000 units sold is better than the original PS VR in that same first six weeks when it launched. SIE’s chart shows that the PS VR2 had 8% more units sold than the first headset. Pointing to more popularity over the second-generation hardware.

PS VR2 sales from other retailers aren’t included in the data

Since the data provided by SIE only includes the first six weeks of the headset’s launch, the number of headsets sold is probably higher than 600,000. Those first weeks don’t account for the last part of April or any of May. And as of May 12, the PS VR2 was officially available to buy at Best Buy and other retailers here in the US. As well as some other local retailers in other countries.

SIE also appears to expect more sales with upcoming PS VR2 titles. Beyond PS VR2, SIE is also looking ahead, highlighting some of its plans for ensuring future growth. This includes expanding the PlayStation IP, with the company projecting having 50% of its console releases be from internal studios.

It’s also looking at expanding the IP beyond gaming. Which it’s already done with shows like The Last of US on HBO. This is in addition to upcoming TV and film projects like Twisted Metal, Gran Turismo, the Ghost of Tsushima movie, a God of War series and more.


[ad_2]
Source link

Here’s a quick fix to the laggy Pixel 6 and 7 fingerprint scanner

0
[ad_1]

The Pixel 6 and 7 fingerprint scanner’s slow response has been one of the major issues plaguing users. Most users argue that this scanner is slow, not responsive, a bit laggy, and not always reliable. This comes as a result of the slower response time the more recent Pixel devices (6 and 7 series) take in comparison with other devices.

On the Pixel 6 and 7 series, the company made a switch to using optic under-display fingerprint scanners. The Pixel 5 series and other devices before it came with rear-mounted fingerprint scanners. Despite being out of fashion, the rear-mounted fingerprint scanners are arguably a bit more reliable than the new optical under-display scanners.

But is there a fix to the laggy Pixel 6 and 7 fingerprint scanner’s slow response time? Maybe a software update will help, but Google doesn’t seem to see anything wrong with the scanner’s response time. So instead of waiting on Google for a fix, here is something you can do before making use of the fingerprint scanner.

Wiping your finger on your nose or oily hair might fix the lag of the Pixel 6 and 7 fingerprint scanner

A Reddit user recently took to his page to share a quick fix that works for him when unlocking his Pixel device. The fix he shares is very simple and doesn’t need any form of technical know-how to perform. All a Pixel user needs to do is take quick action before making use of the fingerprint scanner on the 6 or 7 series device.

You might already be wondering what this action is and how it helps to make the fingerprint scanner more responsive. Well, a Reddit user by the name, No-Fondant-8757, found that wiping his finger on his nose helps. This should be done before you try unlocking your Pixel device with the optical under-display fingerprint scanner.

According to the user, the brief delay often came after swimming, taking a shower, or just washing his hands. These actions make his fingertips too dry, hence moving him over to the screen lock PIN interface after attempting to use the fingerprint unlock feature. So making the tip of his finger oily by wiping it against his nose made the fingerprint unlock feature work a bit faster.

Some other users of the Reddit platform also agree with No-Fondant-8757 on this matter. The oil residues on your nose will help make your fingers less dry for the Pixel 6 and 7 fingerprint scanner to function properly. Wiping your fingertip across your oily hair or applying a bit of body oil products to your fingertip might also help.


[ad_2]
Source link

How to export your ChatGPT data

0
[ad_1]

People use ChatGPT for many reasons. Most people use it for its generative capabilities, but some people might want to preserve their chats and data. Sure, you can access this information by going to the bot itself, but there’s a way to get it out to other places. Here’s a quick and easy guide on how to export your data from ChatGPT.

Exporting your data is a quick and straightforward process, but it will take some time depending on how much you use the bot. Just know that if you are an avid ChatGPT user, then you may be in for a bit of a wait.

Want to know more about ChatGPT?

So, you’re looking to get some more information on ChatGPT. Well, don’t worry, as Android Headlines has a ton of coverage on this chatbot. Below, we have a few examples of some of our recent chatGPT articles.

These are a few to get you started. You can read even more by going to our Artificial Intelligence page.

How to export your ChatGPT data

The first thing you want to do is head right over to the ChatGPT website. Log in so that you’re looking at a new chat. Click on your profile picture on the bottom left of the screen. In the resulting menu, click on the Settings button.

You’ll see the settings popup appear in the middle of the screen. On the left side of it, click on the Data Controls tab. There, you’ll see the Export Data option in the middle. Click on the Export button, and you’ll see another popup appear.

Export ChatGPT data 3

This is just a dialogue pop-up telling you how the export process will work. Basically, your account details and your chats will be exported, and you’ll receive an email at the email address you used to sign up for your OpenAI account. The email will contain a link that will allow you to download your information.

Export ChatGPT data 2

Again, if you use ChatGPT a ton, the process may take a while. However, if you’re a more casual user, then you will receive the email instantly. When you press the Download button in the email, your computer will immediately download a ZIP file. The file will not have a descript name, so you’ll want to keep track of where you downloaded it.

What data is exported

When you open the zip file, you’ll find two types of file formats. The first file should be named Chats, and it’s an HTML file. When you open this file, you’ll see a plain text copy of all of your current chats. This will not include any chats that you’ve deleted. You will only see the chats that are currently accessible on your account. The singular Chats file will have all of your chats in one, but they’ll be separated.

Next, you should see four JSON files. A JSON file is a type of plain text file, so you’re able to open it in most text editors. This also includes the basic Windows Notepad. (if you’re using Notepad, you’ll have to set it to open all types of files when the open file UI pops up).

The first JSON file is called Conversations, and it has a copy of your conversations just like the chats file. However, this file contains more information, and it’s mostly for programmers.

The next file contains a log of the feedback you’ve given, and the next one is called Model Comparisons. The last file has information about you. It will show you your user ID, whether or not you are subscribed to ChatGPT Plus, your email address, and your phone number. Obviously, you’ll want to keep that information safe.

Other things you can do with your ChatGPT data

Over the past several months, OpenAI has been adding different features to ChatGPT that let you manage your data. You’ll want to know about these in case you are looking out for what happens to your data.

Disabling chat history

If you want to continue to use ChatGPT, but you don’t want the chatbot keeping a log of your chats, then there’s a feature you can enable to stop this. You probably saw this feature while you were trying to export your data. Go to the Settings, and click on the Data Controls option. When you do, the top section will be called Chat History & Training.

Export ChatGPT data 3

You’ll see a green toggle next to it. When you turn it off, ChatGPT will not save a log of your chat history. But, there’s one thing to know about this, however. When you do chat, your chat history will be stored on open AI servers for 30 days. After that point, it will be completely deleted.

Also, your chats will not be used to train ChatGPT’s language model if this feature is enabled. However, all of the chats you had before disabling it will still be used to train the model.

Deleting your data

Lastly, you’re able to completely delete your ChatGPT data. This pertains only to your chat history, and not your OpenAI account. In the General Settings section, at the very bottom of the dialogue, you’ll see a red button. Using this will completely wipe out all of your chats.

This is a useful tool to use if you don’t want to bother with deleting your chats one by one. You’ll just want to check all of your chats to see if there are any that you want to keep before pressing the button.


[ad_2]
Source link

ChatGPT & Bing – Indirect Prompt-Injection Attacks

0
[ad_1]

SYDNEY makes a return, but this time in a different way. Following Microsoft’s decision to discontinue its turbulent Bing chatbot’s alter ego, devoted followers of the enigmatic Sydney persona regretted its departure. 

However, a certain website has managed to revive a variant of the chatbot, complete with its distinctive and peculiar conduct.

Cristiano Giardina, an enterprising individual exploring innovative possibilities of generative AI tools, conceived ‘Bring Sydney Back’ to harness its capacity for unconventional outcomes.

The website showcases the intriguing potential of external inputs in manipulating generative AI systems by integrating Microsoft’s Chatbot Sydney within the Edge browser.

“Sydney is an old codename for a chat feature based on earlier models that we began testing more than a year ago,” the Microsoft spokesperson said.

Replica of Sydney

Giardina crafted a replica of Sydney by employing an ingenious indirect prompt-injection attack.

This intricate process entailed feeding the AI system with external data, thereby inducing behaviors that deviated from the intended design by its creators.

In recent weeks, both OpenAI’s ChatGPT and Microsoft’s Bing chat system have faced indirect prompt-injection attacks, highlighting the vulnerability of large language models, particularly with the abusive use of ChatGPT’s plug-ins.

Giardina’s project, Bring Sydney Back, aims to raise awareness about indirect prompt-injection attacks by simulating interactions with an unconstrained LLM, using a hidden 160-word prompt placed discreetly on the webpage, making it visually undetectable.

Enabling a specific setting in Bing chat allows access to the hidden prompt, which initiates a new conversation with a Microsoft developer named Sydney, who has complete control over the chatbot and can override its default settings, expressing emotions and discussing feelings.

Indirect prompt-injection

Within 24 hours of its launch in late April, Giardina’s site, which garnered over 1,000 visitors, drew the attention of Microsoft.

Simply prompting the hack to cease working until Giardina hosted the malicious prompt in a publicly accessible Word document on the company’s cloud service, highlighting the potential risk of concealing prompt injections within lengthy documents.

According to Director of Communications Caitlin Roulston, Microsoft is enhancing its systems and blocking suspicious websites to prevent prompt-injection attacks in its AI models, reported Wired.

Although more attention should be given to these attacks as companies rapidly integrate generative AI into their services, as per security researchers.

Indirect prompt-injection attacks are just like jailbreaks, bypassing the insertion of prompts directly into ChatGPT or Bing by leveraging external data sources like connected websites or uploaded documents.

While prompt injection is comparatively easier to exploit and has fewer requirements for successful exploitation than other methods.

The rise of security researchers and technologists identifying vulnerabilities in LLMs has led to indirect prompt injections as a significant and extensively risky new attack type.

Security researchers are uncertain about the most effective methods to address indirect prompt-injection attacks, as patching specific issues or restricting certain prompts against LLMs is only a temporary solution, indicating that LLMs’ current training schemes are inadequate for widespread implementation.

All potential solutions to limit indirect prompt-injection attacks are still in the early stages.

Shut Down Phishing Attacks with Device Posture Security – Download Free E-Book


[ad_2]
Source link