Motorola Edge 40 series detailed specs leak ahead of launch

0
[ad_1]

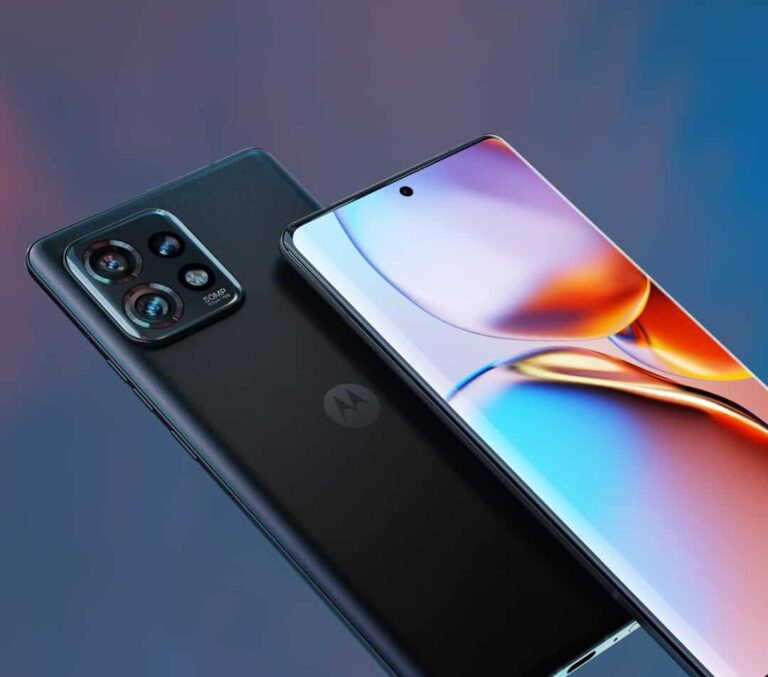
Motorola‘s long-rumored Edge 40 and Edge 40 Pro flagship smartphones have been subject to another major leak. MySmartPrice has exclusively revealed the detailed specs of the new phones. The devices still don’t have an official launch date, though Motorola debuted the Chinese version of the latter back in December 2022.

The Motorola Edge 40 is a rebranded Moto X40

Leaks about the Motorols Edge 40 series have been coming for a few months now. The Pro model is the global version of the Moto X40 that launched in China late last year, so we already know what to expect from it. But the Lenovo-owned company is also readying a stripped-down model to accompany it in global markets. According to the new report, the two devices will share very few specs.

The Motorola Edge 40 Pro will feature a 6.67-inch Full HD+ display (1080×2400 pixels) with a staggering 165Hz refresh rate. It is a 10-bit pOLED panel with HDR10+ support, Dolby Vision, and 1,300 nits of peak brightness. The handset gets a quad-curved design with anti-glare and anti-fingerprint coated 3D Corning Gorilla Glass Victus panels on the front and back, sandwiching a Sandblasted aluminum frame.

Powering this phone is Qualcomm’s latest Snapdragon 8 gen 2 processor with 12GB of LPDDR5X RAM and 256GB of UFS 4.0 storage. For photos, we have a 50MP primary camera at the back with OIS (optical image stabilization) support. It is flanked by a 50MP ultrawide lens and a 12MP 2X telephoto zoom camera. On the front, we have a 60MP selfie camera. The handset also features four microphones and Dolby Atoms-tuned stereo speakers.

The Motorola Edge 40 Pro will pack a 4,600mAh battery with 125W of fast wired charging support. It also supports 15W wireless charging and 5W wireless power share (reverse charging). Other highlights include an under-display fingerprint scanner, IP68 rating for dust and water resistance, Wi-Fi 7, Bluetooth 5.3, linear x-axis vibration motor, and Android 13.

The base model gets a MediaTek processor, fewer cameras, and slower RAM

The base Motorola Edge 40, on the other hand, gets a 6.55-inch display of the same resolution but a 144Hz refresh rate and 1,200 nits of peak brightness. Motorola is equipping it with a less powerful MediaTek Dimensity 8200 processor, with 8GB of LPDDR4X RAM and 128GB/256GB of UFS 3.1 storage. The primary rear camera seemingly carries over unchanged but the Motorola Edge 40 gets a 13MP ultrawide lens and 32MP selfie camera. There’s no zoom camera here.

Elsewhere, it misses out on Wi-Fi 7 and gets only three microphones, though we still have Dolby Atoms-tuned stereo speakers. You’ll also find an under-display fingerprint scanner and IP68 rating for dust and water resistance here. But the Motorola Edge downgrades to a 4,400mAh battery with 68W wired charging and 15W wireless charging. It lacks reverse wireless charging, and seemingly a linear x-axis vibration motor too. Stay tuned for the official launch of the Motorola Edge 40 series.

Motorola Edge 40 series detaile specs leak


[ad_2]
Source link

Apple releases iOS 16.4, complete with more Emoji

0
[ad_1]

On Monday, Apple released the latest update to iOS 16, and that’s iOS 16.4. After a few beta releases, it is finally available to everyone.

This actually turned out to be a rather large update for iOS 16, which is surprising since we are only a couple months away from iOS 17 debuting at WWDC.

The update is available now on the iPhone, as well as iPadOS 16.4 rolling out. Apple also rolled out macOS Ventura 13.3 and watchOS 9.4.

What’s new in iOS 16.4?

So what’s new in iOS 16.4? Well, the biggest feature is definitely new Emoji. I’m only half joking. But there are new emoji coming in this update. There’s 21 new emoji including animals, hand gestures and objects.

Apple is also allowing websites to do notifications through Web Apps when added to the home screen. Apple has also added Voice Isolation for cellular calls that will prioritize your voice and block out ambient noise around you. This has actually been available on FaceTime for a while.

Additionally, VoiceOver support is available for maps in the Weather app now. Most of the rest of the changes here are bug fixes. Here’s the changelog from Apple:

This update includes the following enhancements and bug fixes:

– 21 new emoji including animals, hand gestures, and objects are now available in emoji keyboard
– Notifications for web apps added to the Home Screen
– Voice Isolation for cellular calls prioritizes your voice and blocks out ambient noise around you
– Duplicates album in Photos expands support to detect duplicate photos and videos in an iCloud Shared Photo Library
– VoiceOver support for maps in the Weather app
– Accessibility setting to automatically dim video when flashes of light or strobe effects are detected
– Fixes an issue where Ask to Buy requests from children may fail to appear on the parent’s device
– Addresses issues where Matter-compatible thermostats could become unresponsive when paired to Apple Home
– Crash Detection optimizations on iPhone 14 and iPhone 14 Pro models

As mentioned, you can download the update on your iPhone and iPad now, as well as macOS Ventura 13.3 on your Mac and watchOS 9.4 on your Apple Watch.


[ad_2]
Source link

Hackers Exploited Critical Microsoft Outlook Vulnerability

0
[ad_1]
Microsoft Outlook Vulnerability

In response to a recent vulnerability identified in Outlook, Microsoft recently published a proper guide for its customers to help them discover the associated IoCs.

That Outlook vulnerability in question has been tracked as “CVE-2023-23397” with a CVSS score of 9.8 and marked as Critical.

As a result of this flaw, NTLM hashes can be stolen, and without any user interaction, they can be reused to execute a relay attack.

The threat actors use specially crafted malicious emails to exploit the vulnerability and manipulate the victim’s connection. As a result, this allows them to get control of an untrusted location.

The attacker can authenticate as the victim with the Net-NTLMv2 hash leaked to the untrusted network.

Microsoft patched the flaw

In the Patch Tuesday updates for March 2023, Microsoft fixed the vulnerability in order to prevent the possibility of any further attacks.

The problem is that this approach was taken after it was weaponized by Russian threat actors and used as a weapon against the following sectors in Europe:

  • Government
  • Transportation
  • Energy
  • Military

It was reported in April 2022 that Microsoft’s incident response team had found evidence that the shortcoming could be exploited.

Attack chain & threat hunting Guidance

It has been identified that a Net-NTLMv2 Relay attack allowed a threat actor to gain unauthorized entry to an Exchange Server in one attack chain.

By exploiting this vulnerability, the attacker could modify mailbox folder permissions and maintain persistent access, posing a significant security risk.

The adversary used the compromised email account in the compromised environment to extend their access. It has been discovered that this is done by sending additional malicious messages through the same organization to other members.

CVE-2023-23397 can lead to credential compromise in organizations if they do not implement a comprehensive threat-hunting strategy. 

As a first step, running the Exchange scanning script provided by Microsoft is important to detect any malicious activity. However, it’s imperative to note that for all scenarios, this script is not capable of providing any visibility into messages that are malicious in nature.

Multiple mailboxes can be opened at the same time by Outlook users. Messages received through one of the other services will still trigger the vulnerability if a user configured Outlook to open mailboxes from multiple services. The scanned mailboxes do not contain that message.

If a user wishes to move a message to a local file, they can do so. Finding evidence of a prior compromise in Archived messages may be possible in some cases.

You can no longer access your Exchange messages if they have been deleted from Exchange. It is recommended that incident responders review the security telemetry collected from all available channels in order to confirm the presence of IP addresses and URIs obtained from the PidLidReminderFileParameter values. 

There are a number of data sources that can be used to gather data, including:-

  • Firewall logs
  • Proxy logs
  • Azure Active Directory sign-in logs for users of Exchange Online
  • IIS Logs for Exchange Server
  • VPN logs
  • RDP Gateway logs
  • Endpoint telemetry from endpoint detection and response (EDR)
  • Forensic endpoint data

Recommendations

Here below we have mentioned all the recommendations:-

  • To mitigate the issue, make sure to update Microsoft Outlook immediately.
  • Ensure that defense-in-depth mitigations are active in organizations leveraging Microsoft Exchange Server on-premises.
  • The script should be used to remove either the messages or just the properties if suspicious or malicious reminder values are observed.
  • In the event that a targeted or compromised user receives suspicious reminders or initiates incident response activities, they should be instructed to reset their passwords.
  • To mitigate the impact of possible Net-NTLMv2 Relay attacks, it is recommended that you use multifactor authentication.
  • On Exchange, you should disable unnecessary services that you don’t need.
  • Block all IP addresses except those on an allowlist from requesting connections on ports 135 and 445.
  • If your environment has NTLM enabled, you should disable it.

Searching to secure your APIs? – Try Free API Penetration Testing

Related Coverage


[ad_2]
Source link

ESPN+ announces April 2023 MLB Season streaming schedule

0
[ad_1]

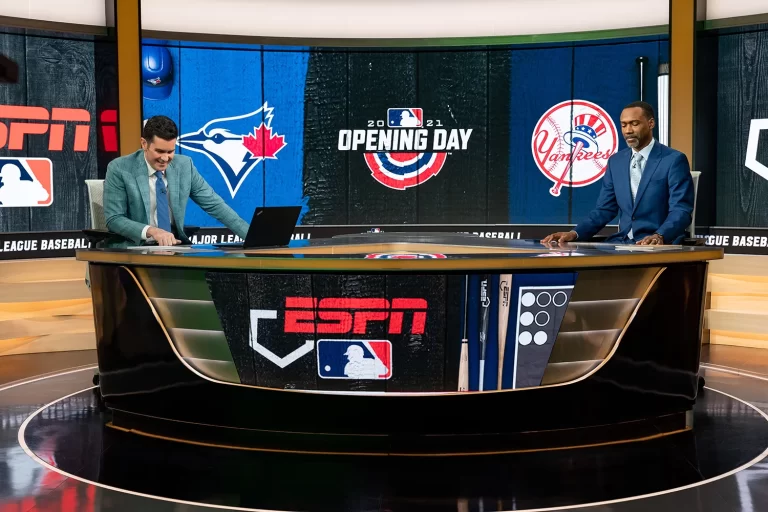
Opening Day is just a few days away for the Major League Baseball 2023 season. And while we’ve already seen Apple TV+ announce their schedule for the first half of the season, now it’s time for ESPN+ to do the same thing. ESPN+ is only announcing the schedule for April 2023, at this time. Since they have games on every single day, the schedule is still quite long.

In the first month on ESPN+, there’s a good number of games that are going to be pretty entertaining to watch. There’s going to be two appearances by the New York Yankees and Aaron Judge. As expected, the reigning World Series champs, Houston Astros will only be on ESPN+ once in the first week. That’s because they are a hotter commodity and likely on other networks and streaming services.

This year, the MLB will be broadcast on quite a few national networks. Outside of the usual RSNs that get all of the games for these teams. We’ll also see them on MLB Network, ESPN, ESPN+, TBS/TNT, Apple TV+ and Peacock. So there’s plenty of ways to watch some Baseball this year.

Here’s the schedule for April 2023

Without further ado, here’s the schedule for the first month, which is mostly April but a couple of games in March as well.

DateTime (ET)Game
Thu., March 304 p.m.Philadelphia Phillies vs. Texas Rangers
Fri., March 3110 p.m.Arizona Diamondbacks vs. Los Angeles Dodgers
Sun., April 21:30 p.m.San Francisco Giants vs. New York Yankees
Mon., April 37:45 p.m.Atlanta Braves vs. St. Louis Cardinals
Tue., April 410 p.m.Colorado Rockies vs. Los Angeles Dodgers
Wed., April 51:30 p.m.New York Mets vs. Milwaukee Brewers
Thu., April 61 p.m.Boston Red Sox vs. Detroit Tigers
Fri., April 74 p.m.Chicago White Sox vs. Pittsburgh Pirates
Sat., April 87 p.m.St. Louis Cardinals vs. Milwaukee Brewers
Sun., April 91 p.m.Cincinnati Reds vs. Philadelphia Phillies
Mon., April 107 p.m.Cincinnati Reds vs. Atlanta Braves
Wed., April 126:30 p.m.Boston Red Sox vs. Tampa Bay Rays
Thu., April 131 p.m.Oakland Athletics vs. Baltimore Orioles
Fri., April 149:30 p.m.Milwaukee Brewers vs. San Diego Padres
Sat., April 159:30 p.m.Colorado Rockies vs. Seattle Mariners
Sun., April 161:30 p.m.Tampa Bay Rays vs. Toronto Blue Jays
Mon., April 178 p.m.Toronto Blue Jays vs. Houston Astros
Tue., April 186:30 p.m.Cleveland Guardians vs. Detroit Tigers
Wed., April 197 p.m.Minnesota Twins vs. Boston Red Sox
Thu., April 209:30 p.m.San Diego Padres vs. Arizona Diamondbacks
Fri., April 2110:15 p.m.New York Mets vs. San Francisco Giants
Sat., April 221 p.m.Toronto Blue Jays vs. New York Yankees
Sun., April 234 p.m.Kansas City Royals vs. Los Angeles Angels
Mon., April 246 p.m.Colorado Rockies vs. Cleveland Guardians
Tue., April 259:45 p.m.St. Louis Cardinals vs. San Francisco Giants
Wed., April 261:30 p.m.Detroit Tigers vs. Milwaukee Brewers
Thu., April 271 p.m.Seattle Mariners vs. Philadelphia Phillies
Fri., April 286:30 p.m.Chicago Cubs vs. Miami Marlins
Sat., April 291 p.m.Baltimore Orioles vs. Detroit Tigers
Sun., April 304 p.m.St. Louis Cardinals vs. Los Angeles Dodgers

[ad_2]
Source link

Samsung launches Exynos Modem 5300 with 10Gbps speeds

0
[ad_1]

Samsung has launched a new flagship 5G cellular modem for smartphones. The Exynos Modem 5300 is a 4nm chipset that supports both Sub-6GHz and mmWave 5G networks. The new modem chip will power the next generation of mobile internet experience starting this year.

Samsung Exynos Modem 5300 specifications

The Exynos Modem 5300 is built by Samsung Foundry using its 4nm EUV (Extreme ultraviolet) lithography technology. The chipset supports FR1, FR2, and EN-DC (E-UTRAN New Radio – Dual Connectivity) cellular connectivity technologies to deliver ultra-low latency and blazing-fast speeds. The Korean firm claims test-proven download speeds of up to 10Gbps (Gigabits per second). It claims up to 3.87Gbps of upload speeds as well.

This modem chip boasts cross-generation network connectivity to ensure reliable cellular connection everywhere. On LTE networks, the peak download and upload speeds max out at 3.0Gbps and 422Mbps (Megabits per second), respectively. The Exynos Modem 5300 supports both SA (standalone) and NSA (non-standalone) 5G modes. “More network access and support enable better connectivity without compromising the user experience,” Samsung says.

A 4nm built means the Exynos Modem 5300 is extremely power-efficient too. It offers an improved 5G experience without taking a toll on your phone’s battery life. Samsung has obtained verification from multiple global mobile network operators for the chip, ensuring seamless integration with smartphone processors. It also supports 3GPP’s (3rd Generation Partnership Project) 5G NR Release 16.

The Exynos Modem 5300 is a complete modem chipset featuring a modem, supply modulator, clock buffer, phase array, PMIC (power management integrated circuit), and antenna module. It also features a built-in PCIe (peripheral component interconnect express) for a connection with the mobile processor. Integrated key components allow manufacturers to focus on other areas of product development.

Pixel 8’s Tensor 3 processor may feature this Samsung modem

Samsung usually launches new cellular modems with its latest flagship Exynos processors. However, the company didn’t debut a new Exynos processor with the Galaxy S23 series this year. The latest Galaxies ship with a Snapdragon processor globally. It has now separately unveiled the Exynos Modem 5300 without an accompanying Exynos processor.

However, rumors are that the Tensor 3 chipset powering Google’s next-gen Pixel 8 series flagship smartphones will be a modified version of the Exynos 2300 that Samsung was supposed to launch this year. By the looks of it, the new modem chip will sit inside the upcoming Pixels. The Korean firm will also supply the Exynos Modem 5300 to other vendors, though. You can expect more rumors and leaks about the Pixel 8 series in the coming months.

Samsung Exynos Modem 5300 2


[ad_2]
Source link

Drive for Tablets is the latest app to get a fresh coat of paint

0
[ad_1]
So, you’ve likely heard about this little cloud storage app called Google Drive. It’s one of the most popular choices when it comes to online storage solutions and that might be in part because the service comes free with every Google account and, as such, Android phone.

Drive has kept its look consistent for many years now, but Google is on a roll as of late when it comes to redesigning its core apps and services. Docs and Sheets have already gotten the same treatment, which included an updated look for their desktop, mobile web and app versions. But you know what is really cool? Seeing a further tweaked redesign come to Drive on Android tablets in particular.

This is part of Google’s aim to bring all of their solutions under the same design philosophy. The campaign initially started when Material You was introduced on Android 12. It began with stock ‘droid apps and settings, but now we’re seeing this extend beyond Google’s OS.

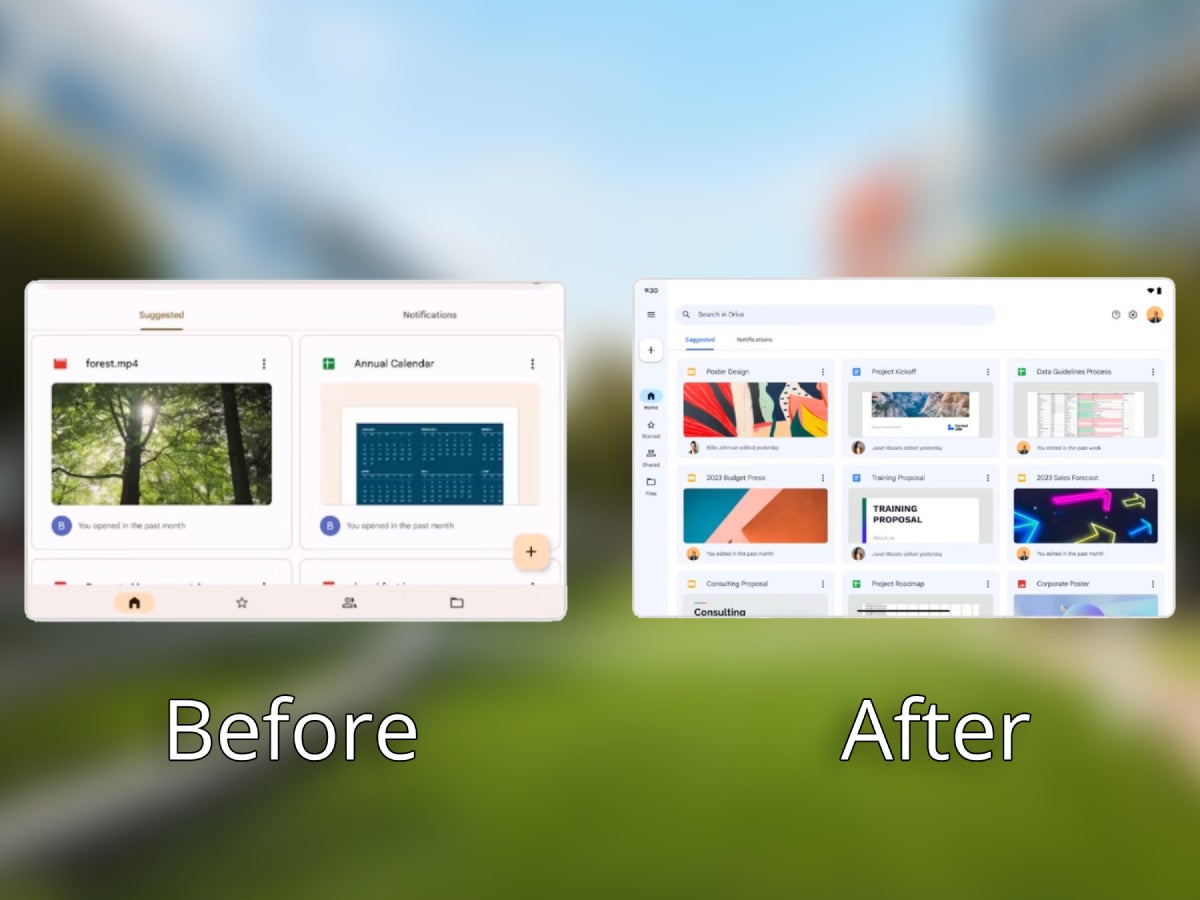
But what has exactly changed with Drive? Well, before this redesign, the navigation bar — a series of quick-access buttons that take users to different sections of Drive — has been moved from the bottom of the screen to the left side. At first glance, this appears similar to the desktop version of Drive, but after a detailed inspection, we can see that it’s not a simple copy-paste job.

The design has been carefully crafted in a way, which makes more sense on a bigger, yet still mobile screen. There is a clear focus on contrast and clarity, which is boosted further by the implementation of color accents. Users have also been granted the ability to collapse the now left-sided navigation panel, so that they can focus on browsing.

This is an expected, but welcomed update that will likely be most appreciated by productivity enthusiasts. Sure, Drive was useful before, but now users on tablets can see more files, which enables them to interact with them faster and that is always a win.


[ad_2]
Source link

Critical Vulnerability Fixed In WooCommerce Payments WP Plugin

0
[ad_1]

A serious authentication vulnerability existed in the WordPress plugin WooCommerce Payments, exploiting which could allow rogue access to admin privileges. The plugin developers patched the vulnerability, making WordPress force install plugin updates.

WooCommerce Payments Plugin Vulnerability Received Sneaky Fix

Security researcher Michael Mazzolini of GoldNetwork caught an authentication bypass vulnerability in the WooCommerce Payments WordPress plugin.

The plugin currently boasts over 500,000 active installations, which suggests any vulnerabilities in the plugin threaten the security of thousands of websites.

As elaborated in a post from the plugin developers, the researcher reported the vulnerability through their HackerOne program, prompting the developers to patch the flaw.

While the developers released the vulnerability patch with the WooCommerce Payments plugin version 5.6.2, they didn’t explain the details in the changelog besides mentioning a two-word “Security update” description.

However, Wordfence dived into the details and elaborated on the flaw. As explained in their post, the plugin had a critical severity authentication bypass issue that could let an unauthenticated adversary impersonate any site user. Once done, the attacker could gain elevated privileges on the site, including admin access, which could threaten the target site’s security. The attacker could execute various actions or take over the site with admin access.

As the report gained traction, WooCommerce Payments plugin developers shared details via their own post, explaining that the issue affected plugin versions 4.8.0 through 5.6.1. Hence, the developers rolled out the fix with version 5.6.2, ensuring auto-updates to site users after working with WordPress.org Plugins Team. So while the site admins running the vulnerable plugin versions will automatically receive the updates, the developers still urge the users to update their sites quickly to avoid exploits.

Team Wordfence also stated that the vulnerability could severely threaten websites’ security if a PoC becomes available.

Alongside updating websites, the plugin developers urge users to update their admin account credentials and rotate Payment Gateway and WooCommerce API keys to eliminate risks.

Let us know your thoughts in the comments.


[ad_2]
Source link

OnePlus 11 Jupiter Rock Limited Edition launch confirmed

0
[ad_1]

Last week, OnePlus teased a new special edition OnePlus 11 with some sort of connection to Jupiter, the largest planet in the solar system. The company’s President for the Chinese market Li Jie said it will be a “unique” device featuring “unprecedented materials and craftsmanship”. While Li didn’t share further details, we won’t have to wait much longer to know what the Oppo sub-brand is readying. The OnePlus 11 Jupiter Rock Limited Edition will launch this Wednesday, March 29th at 2:30 pm Chinese time (2:30 am ET/6:30 am GMT).

OnePlus revealed the launch date of the upcoming device in a recent post on the Chinese social media platform Weibo (via). The company reiterated that the OnePlus 11 Jupiter Rock Limited Edition will be “unique”; every unit will have its own individual design.

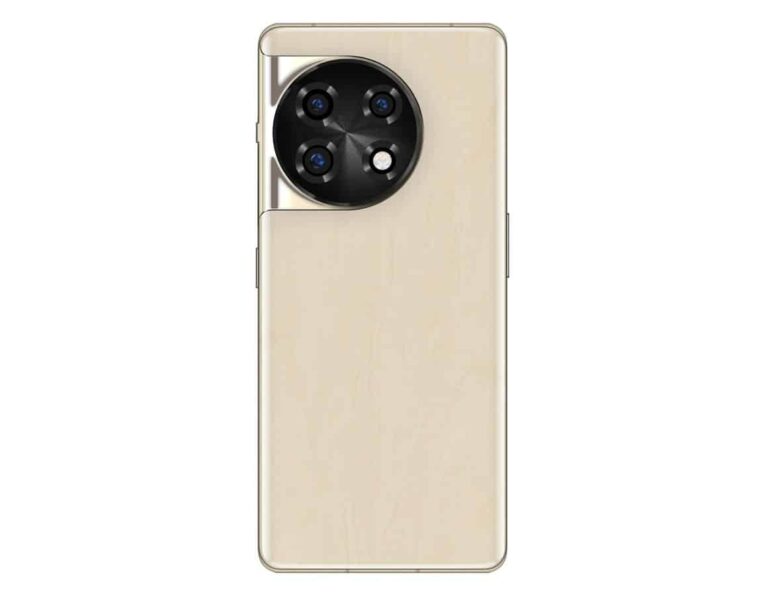
The so-called “unprecedented materials” that it features are not known, though. Early rumors have pointed to a marble back, though a leaked render showed the handset will have a monotonous beige/cream finish as opposed to unique marble patterns. Thankfully, everything will be official in just a couple of days.

This limited edition OnePlus 11 will pack the same internals

OnePlus launched the OnePlus 11 earlier this year. The device first debuted in China with the global launch following in February. It is currently available in Black and Green colors with a glass front and back and an aluminum frame. The upcoming special edition will be its third variant. But, unlike the former two, it will likely be available in limited quantity. The device will also probably cost more than the regular model’s starting price of $699.

However, don’t expect OnePlus to ship the phone with upgraded internals. The OnePlus 11 Jupiter Rock Limited Edition will be nothing but a “unique” OnePlus 11 with new materials on its external surface. The display, chipset, battery, cameras, and all other internal components will remain unchanged. In our review, we found the OnePlus 11 to be a compelling flagship smartphone. You can read the full review to know more about its everyday performance.

For a quick rundown, the OnePlus 11 features a 6.7-inch Fluid AMOLED display with a QHD+ resolution (1440 x 3216 pixels) and a 120Hz refresh rate. It is a 10-bit panel with HDR10+ and Dolby Vision support and up to 1300 nits of peak brightness.

Qualcomm’s latest Snapdragon 8 Gen 2 processor powers the phone with up to 512GB of storage and 16GB of RAM. The device has a 50MP primary camera with 8K video recording support, stereo speakers, an under-display fingerprint scanner, and Wi-Fi 7. It is fueled by a 5,000mAh battery with support for 100W/80W fast charging.

OnePlus 11 Jupiter Rock Limited Edition launch teaser


[ad_2]
Source link

Parts of the Twitter source code were leaked on GitHub

0
[ad_1]

Source code leaks and ransomware attacks have become increasingly common over the past few years, with many companies falling victim to these cyber threats. Now, Twitter has found itself amidst another challenge, as a threat actor leaked pieces of its computer code online without permission. The threat actor named “FreeSpeechEnthusiast” shared excerpts of the company’s source code on the software collaboration platform GitHub, prompting Twitter to issue a subpoena to GitHub to identify the individual responsible for the leak.

While the ramifications of the Twitter leak are not clear, a DMCA takedown request shared by GitHub indicated that the leaked code contains “proprietary source code for Twitter’s platform and internal tools.” This suggests that the leak may have jeopardized the security of Twitter’s algorithmic systems and exposed sensitive information to potential cyber threats.

Musk making Twitter’s source code public

Despite the severity of the leak, Elon Musk, Twitter’s CEO, announced that the company will be making its code transparent and open source from March 31. Musk argues that this move will improve the quality of tweet recommendations and boost users’ confidence in the platform. However, this decision may also pose new security challenges for Twitter.

“People will discover many silly things, but we’ll patch issues as soon as they’re found! Providing code transparency will be incredibly embarrassing at first, but it should lead to rapid improvement in recommendation quality. Most importantly, we hope to earn your trust,” said Musk.

Ever since Musk took over Twitter last year, the company has faced numerous challenges, including a data breach affecting over 200 million users. This incident and the subsequent layoffs have raised concerns about Twitter’s security and reliability. While Musk’s commitment to transparency is a positive step, it remains unclear whether it will be enough to rebuild user trust and confidence in the platform’s ability to protect their privacy and data.


[ad_2]
Source link

Google Keep update on Wear OS brings watch face complications

0
[ad_1]

Google Keep for Wear OS is adding watch face complications. The latest update for the smartwatch version of the app brings watch face shortcuts for “Add list” and “Add note”. The company announced this update at MWC 2023 in Barcelona last month.

First reported by 9to5Google, version 5.23.102.03 of Google Keep for Wear OS adds the two watch face complications. They use the same icons as the Google Keep Tile that the company enabled with version 5.22.322.03.97 of the app in August last year. On tapping the shortcut, you get to choose whether to add a note or list via voice input or type it out.

Note that you can’t access your notes or lists through these complications. These are only shortcuts to add new items. You must directly open the Google Keep app on your watch to see all of your added items. That’s how the tile works as well. But if you frequently use Google Keep, these additions make things convenient. You can begin right from your watch face.

This update should reach all eligible Wear OS devices globally over the next few days, including Samsung’s Galaxy Watch 4 and Galaxy Watch 5 series and Google’s Pixel Watch. You can check for updates from the Manage apps menu in the Play Store app on your watch. To add complications, long-press on your watch face and select customize. Alternatively, you can use the companion app on your smartphone to customize your watch faces.

Google Keep has picked up several updates of late

This is the latest in a string of updates for Google Keep across platforms. As said earlier, Google added a Wear OS Tile for its note-keeping app in August last year. It was followed by a richer note feed in smartwatches in December. Around the same time, the app also gained a dual-pane view on bigger screens, including foldables and tablets. This update was first spotted rolling out in September but most people received it in December.

Last month, Google announced another set of updates for Keep. Firstly, it promised a single-note widget for the Android app, which arrived earlier this month. Now, the promised Wear OS watch-face complications are rolling out as well. The company has also been spotted preparing for adding dynamic color support to Wear OS. It may arrive with a major platform update in the coming months, maybe with Android 14. We will make sure to keep you posted on it.


[ad_2]
Source link