Redmi plans to make 300W charging available to consumers

0
[ad_1]

About a month ago, Redmi demoed its 300W fast charging to the world. The company proved that it can charge a smartphone with a 4,100mAh battery in only 5 minutes. We had no idea when the company plans to utilize its 300W charging in a consumer phone, but it seems like it plans to make it available to consumers soon.

Redmi plans to make its 300W charging available to consumers

Based on a new post by Digital Chat Station, a Chinese tipster, Redmi plans to go ahead with mass production. We’re not sure what phone will utilize it, nor when exactly will it come, but it’s coming.

At the moment, the Realme GT3 is the world’s fastest-charging phone. It supports 240W charging, and it can fully charge its 4,600mAh battery in 9 minutes and 30 seconds. Needless to say, that’s immensely fast, but Redmi will trump that.

Many people would argue that even 67W charging is plenty fast these days, or perhaps even less than that. Some companies really did a great job when it comes to implementing its fast-charging solutions in phones, so there’s really no reason why we couldn’t have faster charging on the table.

OPPO, Xiaomi & Vivo have been pushing the charging speed limits

OPPO and Xiaomi have been including 67W and 120W charging in its devices for a while now. The same goes for a number of other companies. Vivo’s latest flagship also supports 120W charging, for example.

Those devices charge immensely fast despite the fact they have rather beefy batteries. Well, Redmi will push things even further. It uses the fourth-gen GaN (gallium nitride) solution in order to make this happen.

The company is using a customized 6:2 charge pump chip with a maximum conversion efficiency of 98%. The company demoed 300W charging on a special version of the Redmi Note 12 Pro+. That variant of the phone is not available to purchase, of course, it is just a demo device.


[ad_2]
Source link
ChatGPT Exposes Email Address of Other Users

0
[ad_1]
ChatGPT Exposes Email Address

There were a number of users whose email addresses were exposed accidentally by ChatGPT’s website recently. While OpenAI asserted that the cause was a bug in the Redis client open-source library.

In ChatGPT, users can browse all their query history from the sidebar of the ChatGPT window on their web browser. From this sidebar, you can browse all the past queries you have made or even use them to regenerate the responses.

However, many users reported an unusual issue on Monday morning. The reports from the users claim that they could see information about chat queries from other users listed in their query history.

There have also been several reports from ChatGPT Plus subscribers reporting that they came across other people’s email addresses on their subscription pages.

When OpenAI became aware of the incident, they acted quickly with the intent of shutting down ChatGPT to analyze the situation.

Open-Source Bug

The ChatGPT service was exposed as a result of an error in the Redis client open-source library that caused the chat queries and email addresses of other users to be exposed to other users of the platform.

An estimated 1.2% of ChatGPT Plus subscribers had their personal details exposed, which included their chat queries and email addresses. As a result, ChatGPT Plus subscriptions have been suspended, and OpenAI has removed the sidebar for chat histories.

The OpenAI team immediately contacted the Redis maintainers after identifying the issue and provided them with a patch to fix it.

Data Exposed

Several types of information have been exposed, including:

  • Subscriber name
  • Email address
  • Payment address
  • Last four digits of the credit card number
  • Credit card expiration date

OpenAI estimates that many individuals may have had their data exposed in this data breach. It is important to note that to access this information, ChatGPT Plus subscribers had to do one of the following:-

  • Check your email for a confirmation email sent between 1 am and 10 am Pacific time on Monday, March 20, which confirms your subscription.
  • On Monday, March 20, between 1 am and 10 am Pacific time, click “My account” and then “Manage my subscription.”

ChatGPT asserted that they are in the process of contacting all users whose payment information has been compromised due to this security breach.

Actions Taken

As part of OpenAI’s efforts to improve its systems, the following actions have been taken:-

  • To fix the underlying bug, OpenAI has extensively tested the fix.
  • The data returned by the Redis cache will be checked twice to ensure that the data returned matches the information retrieved by the requester.
  • Thoroughly programmatically analyzed the logs to ensure that only the appropriate users could access all messages.
  • To notify the affected users, the company has done several data sources correlations to identify them precisely.
  • A more comprehensive logging system has been implemented to identify when this occurs and confirm that it has been resolved.
  • To reduce the possibility of connection errors under extreme load, the company has improved its robustness and scaled its Redis cluster as well.

Searching to secure your APIs? – Try Free API Penetration Testing

Related Coverage:


[ad_2]
Source link

Musk values Twitter at $20 billion, less than half of what he paid for the platform

0
[ad_1]

Elon Musk is taking a huge bath on his purchase of Twitter. Musk, who paid $44 billion for the social media site in October, now values the platform at $20 billion. This new valuation is based on equity grants that Twitter made to key employees. But Elon is not looking to divest himself of Twitter and in an email sent to employees he writes, “I see a clear, but difficult, path to a >$250B valuation.” For that to happen, Twitter’s valuation would have to rise by more than 10 times the current value that Musk has placed on the platform.

Of course, when it comes to Elon Musk, nothing should be taken at face value. Per The Street, Musk might have devalued Twitter in order to present key talent with equity grants that have a huge upside. This would help Twitter retain personnel that it cannot afford to lose. Morale can’t be high and Musk has already let go of important Twitter employees. The new equity grants will vest over four years and will be allowed to sell their stock holdings during liquidity events “every six months, based on a third party valuation.”

The number of Twitter employees has declined sharply under Musk

When Musk took over Twitter, the company had 7,500 employees which he cut in half during one day in November. Those who kept their jobs were asked to work longer days or leave the company. CNBC reported that Twitter was down to only 1,300 employees by late January. Musk himself corrected the report saying that there were approximately 2,300 active, working employees at Twitter not that Musk’s corrected number was much better.

Shortly after the purge at Twitter, Mush tweeted, “Going forward, to build a breakthrough Twitter 2.0 and succeed in an increasingly competitive world, we will need to be extremely hardcore. This will mean working long hours at high intensity. Only exceptional performance will constitute a passing grade. If you are sure that you want to be part of the new Twitter, please click yes on the link below. Anyone who has not done so by 5 pm ET tomorrow will receive three months of severance.”

Since Musk took over Twitter, the social media site has opened its arms to those who spread misinformation, post racist tweets, and traffic in hate speech. This can’t give advertisers the peace of mind they need to continue spending on Twitter. Advertising accounted for 91% of Twitter’s revenue during the second quarter of 2022, the last time period that such data is available. Since Twitter is no longer a public company, Musk no longer has to publicly release financial data.

In an email to Twitter employees, Musk urged them to look at Twitter as an “inverse startup.” He said that radical changes had to be made to avoid bankruptcy and says that the company could be in the black as soon as the second quarter.

Musk has high hopes for Twitter’s bottom line during the second quarter

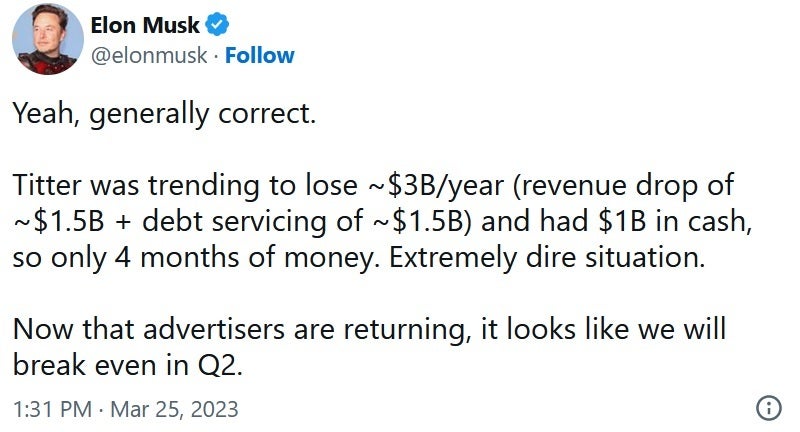
In a tweet he posted a couple of days ago, Musk said, “T(w)itter was trending to lose ~$3B/year (revenue drop of ~$1.5B + debt servicing of ~$1.5B) and had $1B in cash, so only 4 months of money. Extremely dire situation. Now that advertisers are returning, it looks like we will break even in Q2.”

Tweetbot wrote in a tweet to @TwitterDev, “Tweetbot has been around for over 10 years, we’ve always complied with the Twitter API rules. If there’s some existing rule that we need to comply with, we’d be happy to do so, if possible, But we do need to know what it is…” What is happening is that Musk wants those using a third-party Twitter app to use Twitter’s own app instead.

[ad_2]
Source link

Apple’s Mixed Reality Headset Reportedly Demoed to Top Executives

0
[ad_1]

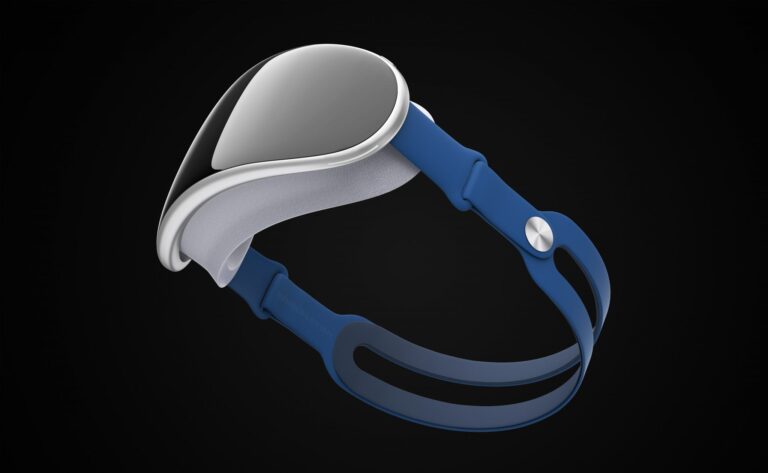
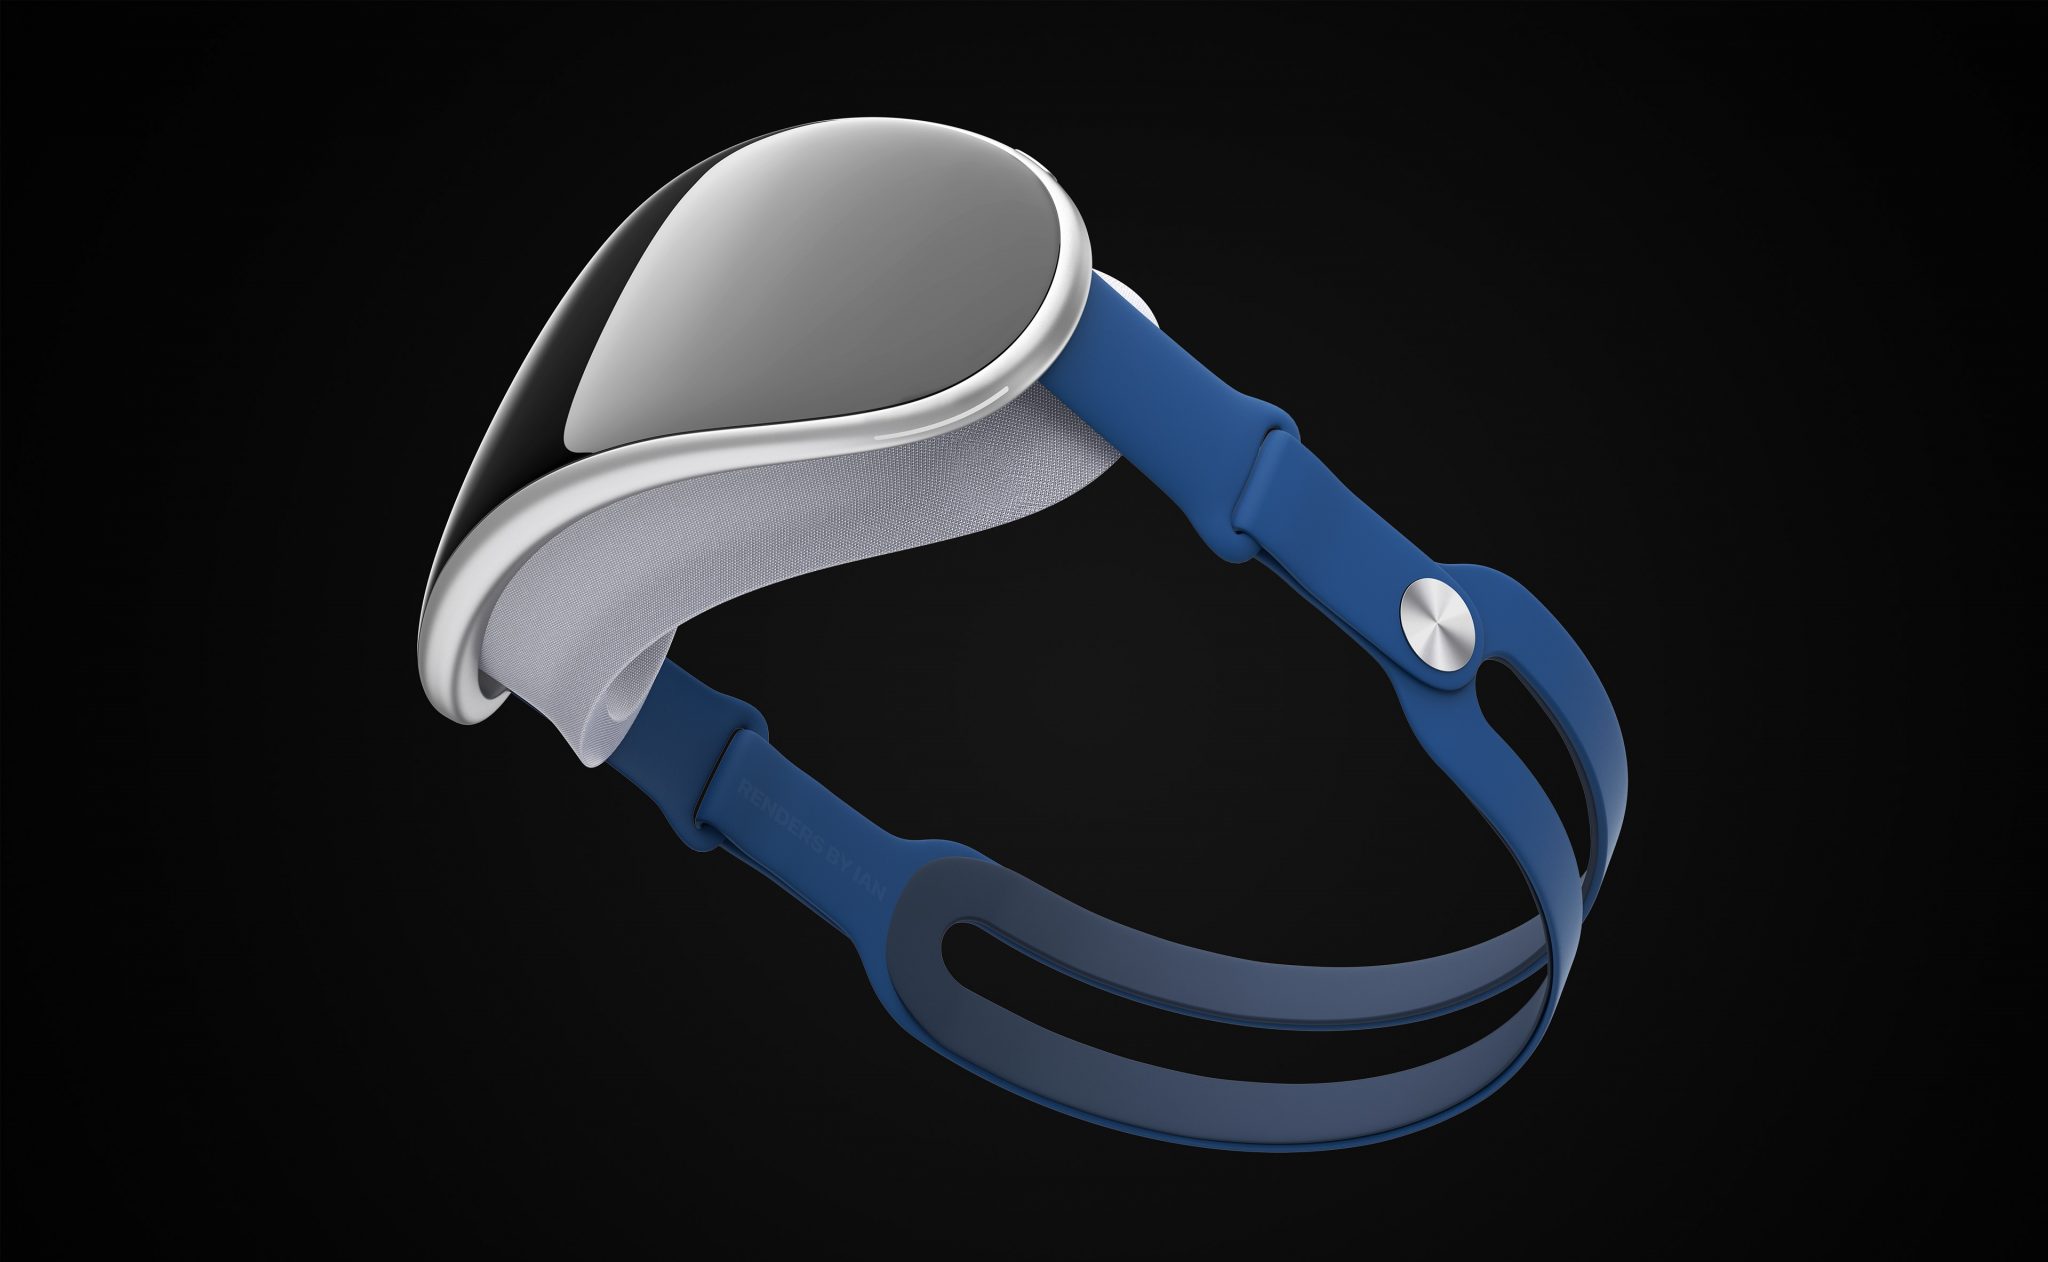
Apple Mixed Reality Pro Headset

Apple reportedly showcased a “polished” demo version of its upcoming Mixed Reality headset to its top 100 executives in a recent gathering at the Steve Jobs Theater.

The Cupertino giant is rumored to launch its Mixed Reality headset in June at its annual WWDC event. In addition to revealing details about the upcoming iOS 17 software update, Bloomberg’s Mark Gurman has revealed that Apple held a private showcase for its top executives at the Steve Jobs Theater last week to demo the device to top executives. The report describes the preview as “polished, glitzy, and exciting” and a “key milestone” ahead of the product’s public announcement.

However, despite the hype surrounding the device, Apple executives are doubtful about its potential success. Gurman reports that the headset is likely to launch with several potential issues, including a $3,000 price tag, a lack of a clear killer app, a requirement for an external battery that needs to be replaced every couple of hours, and a design that some testers have found uncomfortable. Moreover, the device is expected to launch with limited media content.

As a result, Apple executives are said to be “striking a realistic tone” with the understanding that the product won’t be an instant hit. Gurman likens the device’s trajectory to that of the Apple Watch, which initially looked like a “dud” but eventually became a market leader. Apple is already said to be working on a cheaper version of the Mixed Reality Headset that will appeal to the masses. 

Source: Power On


[ad_2]
Source link

New Backdoor Attack Uses Russian-Ukrainian Conflict Phishing Emails

0
[ad_1]

The primary targets of this phishing campaign are located in the Ukrainian regions of Crimea, Donetsk, and Lugansk, which were annexed by Russia in 2014.

Threat actors have launched a new spear phishing campaign in which they install a PowerShell-based PowerMagic backdoor and CommonMagic framework, according to a report by Kaspersky’s Global Research and Analysis Team.

The attackers send phishing emails containing malicious documents that lead to the installation of the backdoors. The primary targets of this campaign are located in the Ukrainian regions of Crimea, Donetsk, and Lugansk, which were annexed by Russia in 2014.

The emails are designed around the Russian-Ukrainian conflict, indicating that the attackers may have a specific interest in the regional geopolitical situation.

Russian-Ukrainian Conflict Themed Phishing Emails Used in New Cyber Attack
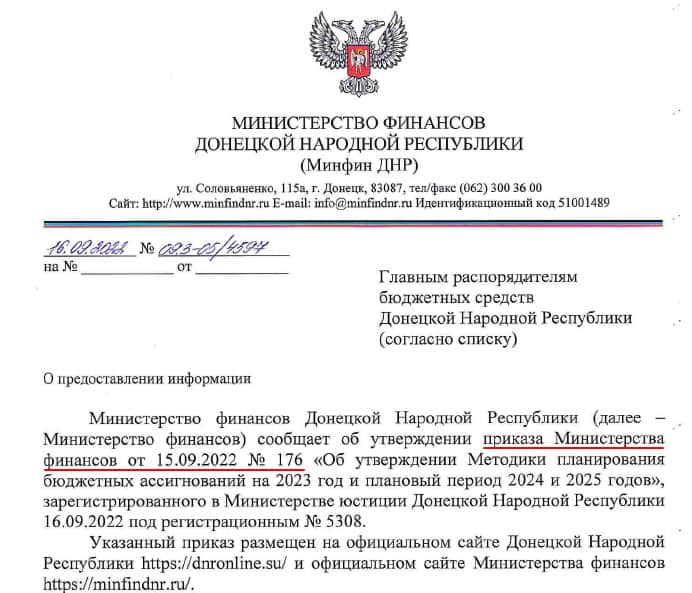
Example of the phishing email (Image credit: Kaspersky)

Kaspersky researcher Leonid Besverzhenko stated that the campaign is primarily an espionage operation targeting administrative, agricultural, and transportation organizations to steal sensitive data.

The phishing emails contain a URL that directs the victim to a ZIP archive containing a malicious LNK file disguised as a PDF. When the victim launches the file, their network is infiltrated, and PowerMagic establishes a connection with its C2 server using OneDrive and Dropbox folders, triggering infection through CommonMagic, a previously undiscovered “malicious framework.”

The CommonMagic framework includes separate modules for different tasks, such as encryption/decryption, screenshot capturing, and document stealing. It can also use plugins for stealing a wide range of files, including DOC, DOCX, XLS, XLSX, RTF, ODT, ODS, ZIP, RAR, TXT, and PDF from USB devices.

Additionally, it can take screenshots every three seconds by abusing the Windows Graphics Device Interface (GDI) API. Both malware have been in active use since September 2021, and Kaspersky discovered the campaign in October.

However, researchers have not yet been able to associate this campaign with a previously known actor. They do believe that an advanced threat actor is behind this campaign.

  1. Ukraine thwart Russian Industroyer 2 malware attack
  2. 34 Russian hacking gangs stole 50m user passwords
  3. DDoS app meant to hit Russia infected Ukrainian phones
  4. CryWiper disguised as ransomware to hit Russian courts
  5. Data of Millions of Russians & Ukrainians Exposed Online

[ad_2]
Source link

Zero-day spells disaster for Bitcoin ATM

0
[ad_1]

We look at a $1.5m heist of cryptocurrency via compromised Bitcoin ATMs.

Bitcoin ATMs have experienced a severe bout of cash drain after a zero-day bug was exploited to steal a total of $1.5 million in digital currency. The ATMs, located in various convenience stores, function along the lines of regular banking ATMs except your dealings are all in the cryptocurrency realm.

As Ars Technica notes, a particular feature of the affected ATMs is the ability to upload video. It’s not mentioned what these videos are used for (presumably security cameras), but the master server interface allowing for the video uploads is where things went horribly wrong.

From the General Bytes statement regarding the March 18 incident:

The GENERAL BYTES Cloud service and other standalone servers run by operators suffered security breaches. We noticed the first signs of a break-in on Friday night, right after midnight on Saturday, 18 March (UTC+1). We notified customers to shut down their CAS servers as soon as possible. The attacker could upload his java application remotely via the master service interface used by terminals to upload videos and run it using BATM user privileges. As a result, the attacker could send funds from hot wallets, and at least 56 Bitcoins were stolen before we could release the patch. The patch was released within 15 hours.

To make use of the exploit, the attacker uploaded a custom made application to the ATM application server used by the administration interface. In a nod to the evergreen security tip “Don’t allow things to autorun if you don’t need them to”, the application server allowed applications to start by default.

With this in place, the attacker was able to perform the below:

  • Ability to access the database.
  • Ability to read and decrypt API keys to access funds in hot wallets and exchanges.
  • Send funds from hot wallets.
  • Download user names and their password hashes, and turn off 2FA.
  • Ability to access terminal event logs, which can include private keys at the ATM.

56 bitcoins are currently worth a cool $1.5 million. It is very unlikely all of the stolen coins belonged to one person, but this is scant consolation for anyone affected. For now, General Bytes is collecting information on everyone affected to “validate losses”. It remains to be seen if anyone is able to recover their funds, but losing money in any cryptocurrency scenario is always a very risky business because  they are generally, by design, unable to roll back fraudulent transactions.

Interestingly, the affected company has a call to any security companies and individuals who feel they can assist in making the product safer.

Keeping your hot wallet safe

Your cryptocurrency wallet type is an article all to its own, but in most cases you’re going to have a wallet which is hot or cold. A cold wallet is not connected to the Internet and is therefore the safest possible choice. A hot wallet comes with some form of connectivity built in, which is much more convenient. You’re able to send funds, for example, and engage with cryptocurrency exchanges. In this case, the compromised wallets are considered to be hot. Without this functionality, the ATM would be rather useless for the user’s needs.

You can’t prepare for every eventuality. If an exchange (or, in this case, a connected ATM) is compromised then your funds could still vanish no matter what security plans you have in place. Even so, here’s what you can do from your end to keep things secure.

  • Enable two-factor authentication. If it’s available for your flavour of wallet, then make sure to turn it on. Hardware keys are safest, then authenticator apps, and lastly SMS.
  • Keep your recovery passphrase safe. Never hand over your recovery phrase to any site or individual, this is a common scam deployed by phishers.
  • Be sceptical of airdrops. This is another way to entice potential victims with phishing tactics. As per the above, asking for your recovery phrase is the ultimate aim.

Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

USB bombs sent to news organizations

0
[ad_1]

USB sticks repurposed as explosive devices provide a dramatic reminder of how little you know about unknown USB devices.

We’ve warned about the possible dangers arising from plugging in unknown USB sticks before, but the dangers we’re concerned with are normally confined to your data.

However, this week we learned a far more serious threat. No fewer than five different news agencies in Ecuador were sent parcels containing a USB stick. In the one instance where a stick was plugged into a PC by a journalist, the device exploded, injuring a presenter in the news room. At least one of the devices had been loaded with a “military type explosive“.

Law enforcement is currently investigating, but for now we have to hope that no additional devices were sent out, just waiting to be inserted into a PC. While this scenario is almost guaranteed to be one that you will not face, that doesn’t mean there aren’t USB stick related perils out there in the wild.

A sticky malware threat

Malware authors are big fans of sending out infected USB sticks to potential victims. Just last year, slick looking Microsoft boxes supposedly containing Office 365 loaded onto USB sticks were sent out by tech support scammers. When inserted into a PC, a phone number would appear and callers would find themselves asked to install remote access tools on their devices. Elsewhere, infected USB Sticks came bearing the gift of ransomware.

USB sticks are also easy to lose: Sometimes people find them lying around in the street, full of potentially sensitive data, as opposed some kind of horrible malware.

Our willingness to insert sticks into computers is helped along by USB sticks being a commonplace giveaway at events, conferences, and even a staple of certain performance art pieces. If you have children, your school may well hand out digital copies of school photographs on USB sticks. Many people will insert those sticks into their computer without a second thought because they’re from a trusted source, the school. Even so, the stick is actually from a totally unrelated third party photographer. Can we guarantee that the photographer is following safety rules, if they even exist?

We never really know for sure, and that can be a problem. However, there are a few things you can do to help keep yourself safe from USB harm.

Tips for USB security

  • Don’t autorun files. If Autorun is enabled on your device, it’s time to consider turning it off.
  • Restrict access. If people in your workplace don’t need to use USB sticks, turn off USB access on their devices and block the USB ports.
  • Occasional access. For times when someone needs to use a USB stick, consider using those sticks on a non-networked PC running a virtual machine.
  • Fire up those security tools. Always scan the contents of a USB stick. Your Endpoint Detection and Response should be equipped to deal with USB threats.

Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

Fans of third-party YouTube apps should watch out for Nexus banking malware

0
[ad_1]

It first appeared in June last year and is now being openly advertised by its creators on hacker forums to increase its reach. Nexus’ primary targets are 450 banking and cryptocurrency apps. 

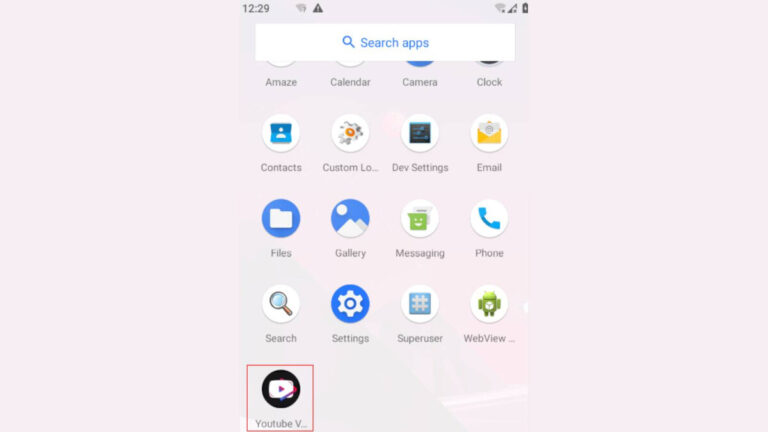
It’s being distributed through phishing websites posing as legitimate websites of YouTube Vanced, a discontinued third-party YouTube app. It uses all the tricks in the books to gain your banking info and take over your financial accounts.

Nexus asks for 50 permissions and abuses at least 14 of them

It is capable of performing overlay attacks, i.e. replicating a legitimate interface to trick you into entering your credentials, and uses keylogging to record your keystrokes. It can even steal SMS messages to get access to two-factor authentication codes and can abuse Accessibility Services to steal information from crypto wallets, 2-Step Verification codes generated by Google Authenticator, and website cookies. The trojan can also delete messages received by you.

After it’s installed on a device, Nexus connects to its command-and-control (C2) server. C2s are used by cybercriminals to control malware, launch attacks, and receive stolen data.

Nexus is said to be in the beta stage but it’s already being used by many threat actors to carry out nefarious activities. Cybercriminals who do not know how to make their own malware can rent it for $3,000 a month.

It looks like the developer is from a CIS (Commonwealth of Independent States) country and has prohibited the trojan’s use in Azerbaijan, Armenia, Belarus, Kazakhstan, Kyrgyzstan, Moldova, Russian Federation, Tajikistan, Uzbekistan, Ukraine, and Indonesia.

Nexus is capable of updating itself and Cleafy thinks it is a real threat and can infect hundreds of Android devices in the world.

To protect yourself from infections, try to only download apps from Google Play and enable Google Play Protect. Use strong passwords and enable biometric security features where possible and be very careful when granting permissions.


[ad_2]
Source link

ChatGPT leaks bits of users’ chat history

0
[ad_1]

ChatGPT suddenly started showing users the titles of other users’ chats.

New gadgets and software come with new bugs, especially if they’re rushed. We can see this very clearly in the race between tech giants to push large language models (LLMs) like ChatGPT and its competitors out the door. In the most recently revealed LLM bug, ChatGPT allowed some users to see the titles of other users’ conversations.

LLMs are huge deep-neural-networks, which are trained on the input of billions of pages of written material.

In the words of ChatGPT itself:

“The training process involves exposing the model to vast amounts of text data, such as books, articles, and websites. During training, the model adjusts its internal parameters to minimize the difference between the text it generates and the text in the training data. This allows the model to learn patterns and relationships in language, and to generate new text that is similar in style and content to the text it was trained on.”

We have written before about tricking LLMs in to behaving in ways they aren’t supposed to. We call that jailbreaking. And I’d say that’s fine. It’s all part of what could be seen as a beta-testing phase for these complex new tools. And as long as we report the ways in which we are able to exceed the limitations of the model and give the developers a chance to tighten things up, we’re working together to make the models better.

But, when a model spills information about other users we stumble into an area that should have been sealed off already.

To understand better what has happened, it is necessary to have some basic working knowledge about how these models work. To improve the quality of the responses they get, users can organize the conversations they have with the LLM into a type of thread, so that the model, and the user, can look back and see what ground they have covered and what they are working on.

With ChatGPT, each conversation with the chatbot is stored in the user’s chat history bar where it can be revisited later. This gives the user an opportunity to work on several subjects and keep them organized and separate.

message saying history is unavailable
The history was unavailable for a while

Showing this history to other users would, at the very least, be annoying and unacceptable, because it could be embarrassing or even give away sensitive information.

title of chat says Wife Valentine's Day Gift?
Did I ask ChatGPT what to get my wife for Valentine’s Day?

Nevertheless, this is exactly what happened. At some point, users started noticing items in their history that weren’t their own.

Although OpenAI reassured users that others could not access the actual chats, users were understandably worried about their privacy.

According to an OpenAI spokesperson on Reddit the underlying bug was in an open source library.

post on Reddit by Sam Altman

OpenAI CEO Sam Altman said the company feels “awful”, but the “significant” error has now been fixed.

Things to remember

Giant, interactive LLMs like ChatGPT are still in the early stages of development and, despite what some want us to believe, they are neither the answer to everything nor the end of the world. At this point they are just very limited search engines that rephrase what they found about the subject you asked about, unlike an “old-fashioned” search engine that shows you possible sources of information and you can decide which ones are trustworthy and which ones aren’t.

When you are using any of the LLMs, remind yourself that they are still very much in a testing phase. Which means:

  • Do not feed it private or sensitive information about yourself or your employer. Other leaks are likely and may be even more embarrassing.
  • Take the results with more than just a grain of salt. Because the models don’t provide sources of information, you can’t know where it’s ideas came from.
  • Make yourself familiar with the LLM’s limitations. It helps to understand how up to date the information it uses is and the subjects it can’t converse freely about.

Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

Hackers Inject Weaponized JavaScript (JS) on 51,000 Websites

0
[ad_1]

Researchers from Unit 42 have been monitoring a widespread campaign of harmful JavaScript (JS) injections. The campaign aims to redirect unsuspecting victims to dangerous content, including adware and fraudulent pages.

Websites continue to be infected by this threat in 2023, as it was active throughout 2022. The malicious JS code was discovered on over 51,000 websites, with several hundred appearing in Tranco’s top 1 million ranked websites.

The potential impact of this campaign is significant, as the presence of affected websites in Tranco suggests a widespread reach.

The campaign’s complexity lies in its multi-stage injection process, which precedes redirecting harmful web pages as an additional means of evading detection, obfuscation, and benign append attacks were employed.

Impact of the campaign on user

Experts have identified multiple versions of a campaign involving malicious JS code injection into websites by threat actors. During the year 2020, the campaign was observed for the first time.

170,000 URLs and 51,000 hostnames have been identified as part of this campaign since its inception in 2022.

A peak of over 4,000 daily URLs was generated as a result of this campaign between May and August 2022. 

The impact of this campaign has been substantial, with hundreds of infected websites appearing in Tranco’s top one million ranked sites, indicating a potentially wide reach among internet users.

In January 2023, approximately 240,000 website sessions were prevented across 14,773 devices due to blocking measures taken against these websites.

Technical analysis

A malicious payload was hidden in the injected JS code, which was obfuscated to bypass detection and remain undetected. A malicious JS is loaded from a URL obscured by the obfuscated code. 

As part of the code, the malicious JS is dynamically added to the DOM structure, which is also included in the code.

On certain websites, obfuscated JS snippets have been found to be injected into commonly used utility JS files, as per observations. Appending malicious code to extensive sections of benign code, also called a benign append attack, is a common tactic malware authors employ.

It can be used by malware authors to avoid detection by security crawlers and remain undetected. In each JS code snippet, the injected JS code appends external malicious JS code through DOM manipulation.

A malicious payload can be changed in this manner, providing the attacker greater flexibility. In its more recent version, this campaign injects malicious JS code into a website for malicious purposes.

Upon executing the final payload, users are redirected to various websites before reaching a destination webpage, often consisting of adware or a fraudulent page.

This page displays false information that may deceive individuals into granting permission for a malicious website to send browser notifications under the control of an attacker.

The researchers at Unit 42 believe that many websites are susceptible to security breaches due to vulnerabilities in one or more CMS plugins.

The researchers at Sucuri have discovered that exactly the same technique was used to exploit CMS plugins in a similar campaign. The threat actors responsible for creating malware have produced multiple variations of the harmful JavaScript code they injected into websites during this campaign.

Detecting different variants of the same attack is a robust characteristic of deep learning techniques often used to detect intrusions.

In order to prevent malicious JS injections, deep learning techniques could be applied to increase the detection rate.

Searching to secure your APIs? – Try Free API Penetration Testing


[ad_2]
Source link