Snapdragon 7+ Gen 2 is official with a 50% faster CPU, improved GPU

0
[ad_1]

Qualcomm has announced its new mid-range processor, the Snapdragon 7+ Gen 2. This is a direct successor to the Snapdragon 7 Gen 1, by the way. We’re not really sure why Qualcomm used the ‘+’ moniker here, as there was no Snapdragon 7 Gen 2, but there you go.

The Snapdragon 7+ Gen 2 is a 4nm processor that brings a 50% performance improvement

This processor has a 1+3+4 architecture, and it’s a 4nm chip. There is 1 Kryo Prime CPU (Cortex X2-based), three Kryo Performance CPUs (Cortex A710-based), and four Kryo Efficiency CPUs (Cortex A510 based).

The company has a Kryo CPU that will seemingly offer a 50% performance improvement. The Adreno GPU, on the other hand, also comes with a performance boost, as it will offer a 2x performance improvement over the Snapdragon 7 Gen 1.

It offers a considerable power efficiency boost

Furthermore, you’ll also be getting a power efficiency boost here. Qualcomm says this chip is 13% more power efficient compared to the Snapdragon 7 Gen 1.

The company also included some gaming features here. Features such as Auto Variable Rate Shading (VRS), Volumetric Rendering and Snapdragon Sound with Qualcomm aptX.

The Qualcomm AI Engine, on the other hand, offers a 2x improved AI performance. You’re also getting a 40% better performance per Watt than its predecessor. The AI Super Resolution can also upscale game scenes and photos quite a bit (from 1080p to 4K).

It comes with an 18-bit Triple ISP

The Snapdragon 7+ Gen 2 comes with an 18-bit Triple ISP, which offers support for up to 200MP photo capture and staggered HDR video capture.

The Snapdragon X62 5G modem is also a part of the package. 4G/5G Dual-SIM Dual Active (DSDA) is supported too. The same goes for Wi-Fi 6E and Bluetooth 5.3.

This processor has support for LPDDR5 RAM up to 3,200MHz. It also supports Qualcomm Quick Charge 5 technology, and displays up to QHD+ resolution with a 120Hz refresh rate.


[ad_2]
Source link

Ransomware attack hits ANOTHER school

0
[ad_1]

Wymondham College is operating as normal, with a few expected distruptions that may be minimal but lasting.

In what is likely Vice Society’s handiwork, the UK’s largest state boarding school Wymondham College has announced it has become the victim of a “sophisticated cyberattack”. The school didn’t provide additional information, but Jonathan Taylor, chief of the school’s parent company Sapientia Education Trust, has revealed the school is yet to receive a ransom note.

In an email to The Record, Taylor said:

“We are not aware of any data breach. A number of the College’s systems have been impacted, including access to some files and resources.” 

Taylor said the school remains open, saying the priority is “to ensure continuity of educational provision”. The Norwich Evening News reports disruption will likely continue until the Easter holidays as the attack targeted the College’s IT system.

Wymondham College is working with the National Cyber Security Centre (NCSC), the UK’s authority for cyber incidents, to ensure an appropriate response. Taylor says the Department of Education has also been notified.

The NCSC has warned the UK education sector about increasing targeted ransomware attacks toward schools, colleges, and universities. However, latest research from the London Grid for Learning (LGfL) reveals that only 53 percent of UK schools feel prepared for a cyberattack. 

How to avoid ransomware

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; disable or harden remote access like RDP and VPNs; use endpoint security software that can detect exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like Malwarebytes EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.

Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

Grab an Apple Watch SE for its lowest price yet, only $219

0
[ad_1]

Amazon has the Apple Watch SE down at its lowest price yet, just $219. Both models, the 40mm and the 44mm are on sale for the same $30 off. So while the 40mm SE is down to $219, the 44mm is down to $249. Definitely a good price, and a great way to get into the Apple Watch ecosystem.

The Apple Watch SE is the cheapest model of Apple’s current generation of Watch. The reason why this is important, is that it is going to continue to get updates longer than say a Series 6 or Series 7 that you might be able to get for less. Apple does already support its products far longer than most of its competitors, but it’s still a good idea to get the latest and greatest.

Apple Watch SE does skip out on some of the features of the regular Apple Watch. Like the Always-on Display, ECG and a few more. But for most people, it’ll get the job done. The underside is also plastic, versus glass. This actually makes it feel lighter, and also makes it more durable, if you did drop it.

With the Apple Watch SE, you’ll be able to use all of your favorite apps, including Gmail, Spotify, Apple Music and much more. Many apps on iOS do have Apple Watch apps. Apple Wallet also works great on the Watch. Making it easier to pay for things without pulling out your wallet.

Of course, there’s also Apple Fitness. Which takes a different approach versus the competitors out there. While others might track your steps each day as your primary goal, Apple does not. Instead it has three rings. A Stand ring, move ring and exercise ring. These are all customizable to your goals, and do take into account other exercises, even if you can’t walk as much as others.

You can pick up the Apple Watch SE from Amazon today by clicking here.

Apple Watch SE – Amazon


[ad_2]
Source link

Enduradata explains: what is file synchronization?

0
[ad_1]

Whether you’re working with your Android device on the fly, collaborating with other team members around the world, or all in one location, it is not so much of a Geekly thing as it is a necessity to know about file synchronization.

Are you tired of constantly emailing files to your team to ensure everyone has the latest version? Have you ever lost important documents due to a hard drive crash or accidentally deleted a file? As EnduraData explains – these problems can be solved with file synchronization!

What is File synchronization? It’s a powerful method of keeping your files updated and stored in multiple locations. This method is crucial for remote teams who need access to the same files in real time. File syncing software, such as Dropbox, is commonly used for backup and mobile file access. In this article, we’ll explore the different types of file synchronization and their benefits, so you can keep your team organized and efficient.

Types of File Synchronization

Synchronization can be “one-way” or “two-way.” or even “multi-way”.

1. Two-Way synchronization (bi-directional synchronization)

It is a type of synchronization in which files are copied in both directions to reconcile changes as they occur. If a file in Location A is newer, it will be copied to Location B. If a file in Location B is newer, it will be copied to Location A. Similarly, deleting a file from Location A deletes it from Location B, and vice versa.

2. One-Way synchronization (file backup/mirroring/file replication)

The synchronization process only transfers files in one direction. Files are pushed from source to target in only one direction. For example, if a file in Location A (source) is more recent, it will be copied to Location B. (target). Similarly, deleting a file from Location A causes it to be deleted from Location B. On the other hand, a file deleted in Location B is restored using the file in Location A.

How does file synchronization work, and how to implement it?

Your needs will dictate how you implement file synchronization. You can also use a variety of file-syncing techniques. These can include, for example, using a hosted system, developing your sync system, or a third-party tool.

The best file-syncing solutions simplify copying and backing your files across multiple devices, whether at work, at home or on the go. In addition to storing and syncing data, most syncing solutions allow you to manage your saved data, user access and permissions. These are good for file sharing and collaboration with stored files.

Benefits of File Synchronization

1. Encourages collaboration

Having consistent data sets across multiple locations fosters healthy collaboration when working with others. Everyone will have the same information about the project under consideration. When you make changes to your data source, the changes are reflected in the applications of the other team members.

2. Prevents data Loss

Data synchronization prevents data loss by providing updated multiple data sets in different locations. If you lose data in one application, don’t worry because you have the same data in several other places.

3. Improve data accessibility

Because data synchronization ensures that your data in different locations is accurate, you can use the most convenient and available Location at any given time. You can access your data locally if your network fails or goes down.

4. Controlling secure access

You must be aware of who has access to your data so that they do not alter or compromise it in any way. File synchronization allows you to make specific data sets available to network users in a separate application without granting them full network access. Another aspect that must be mentioned is the compliance with laws such as HIPPA or other federal requirements. Does the solution support installation on premise, the cloud or both? Does the solution have safeguards for data leaks? Does data leave the customer’s site? If so the consequences of a data leak or breach can be very costly and may violate certain laws. One question to always ask, what is the value of the data, its secrets and do you trust all system administrators that have access to the data on the remote sites?

5. Automating massive data transfers

Some file synchronization vendors more than others automate file sync more than others. It is critical that attention be paid to automation of the large file transfers and the amount of data to be transferred. Some solutions are for small businesses or home users but are not for the enterprise.

Final Thoughts

A significant portion of our work in the digital space revolves around files. You can use file synchronization to keep all of your data sets up to date. Furthermore, by implementing a single file synchronization software across multiple applications, you can improve the security of your data assets. You will save valuable resources, such as time, in the long run and boost efficiency of your business operations. But beware that some solutions are for home users but do not respond to the needs of the enterprise or government agencies. We also suggest you read more here about secure data transfers.
[ad_2]
Source link

Hackers threaten to leak STALKER 2 assets if devs don’t heed demands

0
[ad_1]

The developers of first-person shooter game, STALKER 2, have revealed assets related to the game were stolen and used for blackmail and intimidation.

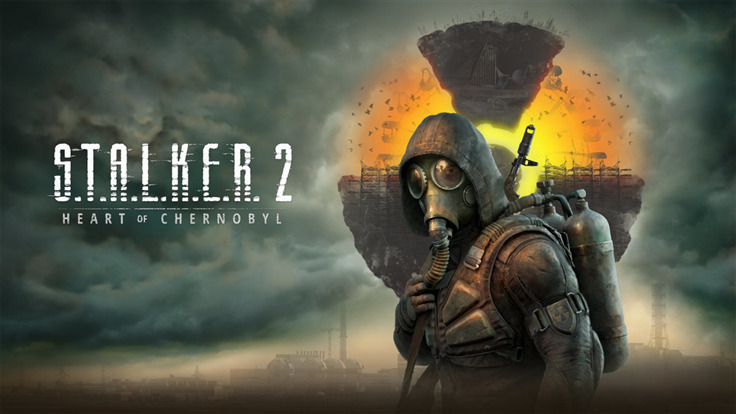
Ukrainian game developer GSC Game World has announced it was breached by Russian hacktivists who stole assets related to the much-awaited game STALKER 2: Heart of Chernobyl. 

According to GSC, the hacktivists accessed an employee’s image app account and stole STALKER 2’s full story, cut scenes, various concept art, global maps, and more. The company said these assets are being used for blackmail and intimidation.

“We have been enduring constant cyberattacks for more than a year now,” the GCS Game World Team said in its.

“We have faced blackmail, acts of aggression, attempts to hurt players and fans, and efforts to damage the development process of the reputation of our company.”

A group named Vestnik TSS has claimed responsibility and has given the devs an ultimatum: Do as we say, or we’ll leak all stolen STALKER 2 assets.

“Nick Frost”, a Vestnik TSS administrator, posted the group’s demands on the Russian social media site VK.com. Below is a screenshot of the English-translated post:

Vestnik TSS wants GSC to apologize to players in Russia and Belarus for its perceived “unworthy attitude” towards them, un-ban certain Russian accounts on its official Discord server, and bring back the Russian localization of STALKER 2. The group gave the developers until March 15, Wednesday, to make these changes.

It appears, however, that Vestnik TSS leaked some files that they stole before yesterday’s deadline. The group’s VK page is awash with concept art, which includes an overview of mutant NPCs, bits of the game world’s map, and artifacts. On Tuesday, alias “Daniel Nexus”, likely another admin, posted more STALKER 2 assets archived and kept behind a password.

GSC Game World is yet to respond to the demands; and by the tone of its message, I suspect the developers have no intention of complying. Instead, the team has pleaded for the STALKER community to refrain from watching or distributing the leaked materials.

“Outdated and work-in-progress materials may dilute the impression of the final idea that we have put into the game. We encourage you to stay patient and wait for the official release for the best experience possible. We believe that you will love it.”


Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

March update live for all recent Samsung foldables in the US

0
[ad_1]

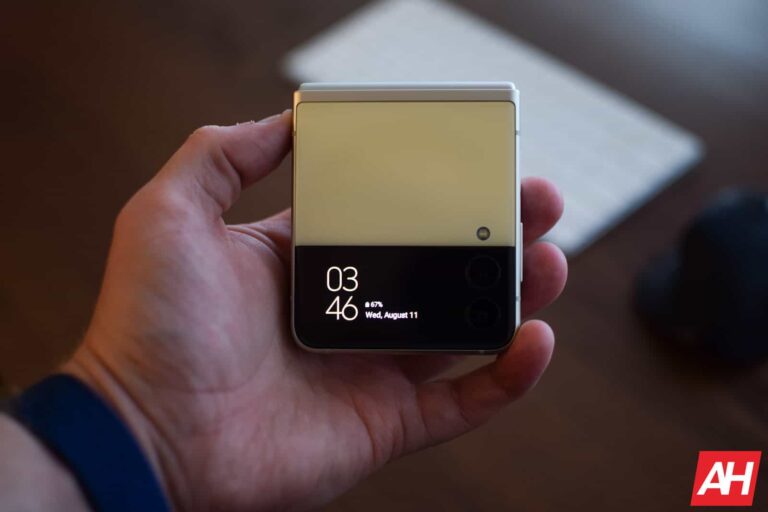
Samsung is updating pretty much all of its foldable smartphones to the March 2023 Android security patch in the US. The latest security update is rolling out to the Galaxy Z Fold 4, Galaxy Z Fold 3, Galaxy Z Flip 4, Galaxy Z Flip3, Galaxy Z Flip 5G, and Galaxy Z Flip. The first-gen Galaxy Fold and the Galaxy Z Fold 2 are the only models still missing the March SMR (Security Maintenance Release) stateside.

The March security update is available for both carrier-locked and unlocked units of the Galaxy Z Fold 4 in the US. The update comes with firmware versions F936USQS2CWB1 and F936U1UES2CWB1 for the two variants, respectively. It is rolling out widely on all major networks. As you can see in the official changelog here, Samsung isn’t pushing any new features or user-facing changes to the foldable. The latest firmware release is all about this month’s security patch.

The same goes for the Galaxy Z Flip 4 as well. The March update for the latest clamshell foldable is rolling out widely for everyone in the US. The updated firmware versions are F721USQS2CWB1 (carrier-locked) and F721U1UES2CWB1 (unlocked). Once again, Samsung’s changelog doesn’t mention anything apart from the latest security patch, which contains more than 60 vulnerability fixes.

The story is slightly different for the Galaxy Z Fold 3 and Galaxy Z Flip 3. As of this writing, Samsung is only pushing the March SMR to the unlocked variants of its 2021 foldable duo in the US. The new firmware build number for the former is F926U1UES2FWB3, while that for the latter is F711U1UES3FWB3. The update is live for users on pretty much every wireless network stateside. There are no new features in tow here as well.

Galaxy Z Flip & Flip 5G are also getting the March update in the US

Samsung is also pushing the March SMR to the original Galaxy Z Flip and its 5G model in the US. As of this writing, the update is only available for the unlocked variants. The new firmware build numbers for the two models are F700U1TBS5IWC2 and F707U1UES3HWC1, respectively. Users with a carrier-locked Galaxy Z Flip, Galaxy Z Flip 5G, Galaxy Z Fold 3, and Galaxy Z Flip 3 in the US should get the latest security update in the coming days.

As said earlier, the March SMR patches more than 60 vulnerabilities in Galaxy devices. These include at least five critical Android OS patches from Google. Samsung will push the latest security update to more eligible Galaxy devices in the coming days. As usual, you can check for updates from the Software update menu in the Settings app. Your phone may also notify you about new updates.


[ad_2]
Source link

Next fastest charging smartphone coming in Q3 2023, here are the details

0
[ad_1]

The Realme GT3 launched at the end of last month, and it became the world’s fastest charging smartphone. Well, it seems like the next fastest charging smartphone is coming in Q3 this year, and we have the details.

Before we get down to it, let’s just say that the Realme GT3 supports 240W wired charging. Redmi announced 300W charging around the same time, but we don’t know when we can expect a device to actually support it.

The next fastest charging smartphone is coming from Infinix, and will launch in Q3

The phone we’re talking about here is the Infinix GT 10 Pro. That device will utilize the company’s 260W wired charging that was announced recently. The company also announced 110W wireless charging, but we’re not sure if it will support that as well.

The details about this phone have been revealed by Paras Guglani, who partnered up with MySmartPrice. This phone will include a 5,000mAh battery, which will be rechargeable with such insanely fast charging.

The phone will be fueled by the MediaTek Dimensity 9000 SoC. It will also include a 120Hz AMOLED display, which will be curved, and measure 6.8 inches. A 200-megapixel camera was also mentioned by the tipster.

It will ship with Android 13, and include 12GB of RAM

You’ll get 12GB of RAM inside of this phone, along with 256GB of storage. Android 13 will come pre-installed on the device. The Infinix GT 10 Pro will arrive in two color options, but we don’t know what they are just yet.

That’s basically everything the tipster shared thus far. It’s obvious that this will be a well-specced phone, but its main appeal will definitely be 260W charging. We do hope that Infinix will also include 110W wireless charging that it announced. The rest of its specifications are also nothing to scoff at, quite the contrary.


[ad_2]
Source link

Facebook illegally processed user data, says court

0
[ad_1]

Two European privacy watchdogs have won cases against Meta. The rulings may have serious consequences for European website owners.

The Amsterdam court has ruled that Facebook illegally processed user data in a case started by the Dutch Data Privacy Stichting (DPS), a foundation that acts on behalf of victims of privacy violations in the Netherlands.

According to the ruling, Facebook used personal data for advertising purposes in the period April 1, 2010, to January 1, 2020, when this was not allowed. The same ruling also says that Facebook shared personal data with third parties without any legal basis to do so, and without informing the users themselves. Without properly informing users there can be no consent.

The DPS and the Dutch Consumentenbond—a consumers association with over 400,000 members—filed a class-action suit against Facebook Ireland, which is the European subsidiary of Meta that oversees the processing of Dutch user data. This ruling doesn’t mean damages can yet be claimed by the 185,000+ people that are represented in the class-action suit, but it’s one step closer. Based on this ruling, the group now hopes to sit down with Facebook to negotiate a settlement. Any of the roughly 10 million Dutch people who used Facebook during the relevant period can join if the case moves to a damages phase.

The main complaints were that Facebook used personal data for advertising and shared data like sexual preferences and religion with third parties. The data in question were both provided by the users themselves and derived by Facebook from the users’ browsing behavior outside of Facebook itself. Facebook not only shared users’ personal data with third parties but also the personal data of their Facebook friends.

Facebook was cleared of the complaint that it placed cookies on third party websites. The court ruled that it transferred the responsibility for those cookies to the website owners, and had the right to do so. Facebook was also cleared of enrichment charges as the court found not enough proof that Facebook’s monetary gain from these actions resulted in direct damages to the users.

A spokesperson for Meta said the company was “pleased” with parts of the decision but would appeal others, noting that some of the claims date back more than a decade.

Austria

In Austria, the Datenschutzbehörde (DSB) ruled that a complaint that Meta’s tracking pixels by the privacy organization noyb were conflicting with European GDPR rules was partially upheld. The website owner was found in conflict with GDPR regulations because personal data of users (at least unique user identification numbers, IP address and browser parameters) were transferred to the USA in a data transfer without ensuring an adequate level of protection.

Last year the Austrian privacy watchdog ruled against Google Analytics as being in conflict with GDPR regulations. According to noyb, the same rules apply to Facebook Login and Meta Pixel because these tools also send data to the US.

Together these rulings may have serious consequences for all European based website owners. Because of the transferred responsibility the website owners take on by using these tools, they can be held liable for the fact that Meta and Google send data to the US without ensuring an adequate level of protection.


Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

Galaxy S23, Galaxy S20 & A53 5G get March update in the US

0
[ad_1]

Samsung‘s March update is available for more Galaxy devices in the US. The Galaxy S23 series, Galaxy S20 series, and the Galaxy A53 5G are picking up the latest security patch stateside. They join the Galaxy S22, Galaxy S21, Galaxy Note 20, and all recent Galaxy Z series foldables in the party.

The March SMR (Security Maintenance Release) for the Galaxy S23, Galaxy S23+, and Galaxy S23 Ultra is available widely for both carrier-locked and unlocked variants in the US. The updated firmware build number for the former is S91*USQS1AWBM while that for the latter is S91*U1UES1AWBM. Samsung doesn’t seem to be pushing any new features to the devices with this release. That isn’t surprising, though. The handsets have just arrived on the market. You can expect feature updates for the phones in the coming months.

Likewise, the Galaxy S20, Galaxy S20+, and Galaxy S20 Ultra are fresh from the One UI 5.1 update and are only getting the latest security update today. As of this writing, Samsung is pushing the March SMR to the factory-unlocked variants of its 2020 flagships in the US. The new firmware version for the phones is G98*U1UES3HWB5. Carrier-locked units should follow in the coming days. The update for the unlocked units is rolling out widely on most wireless networks stateside, including AT&T, T-Mobile, and Verizon.

This month’s security update is also available for the Galaxy A53 5G in the US. The rollout began recently for carrier-locked models. The handset is getting the update with the firmware build number A536USQS4CWC2. Users with an unlocked unit of the 2022 premium mid-ranger can expect to receive this software release in the coming days. Don’t expect any new features, though. Like the Galaxy S20 series, your phone also recently picked up the One UI 5.1 update with a host of goodies. The latest release is all about vulnerability fixes.

March update for Galaxy devices contains several dozen security patches

Samsung has been rolling out the March update for its Galaxy smartphones and tablets since early last week. It has already pushed the new SMR to most of its recent flagship models and a few mid-rangers. The update contains patches for more than 60 vulnerabilities that affect various system components across the Galaxy lineup. About 20 of those are Galaxy-specific vulnerabilities while the remaining flaws affect the entire Android ecosystem. You can go to Settings > Software update on your Galaxy smartphone and tap on Download and install to check for new updates.


[ad_2]
Source link

Microsoft laid off an AI ethics team

0
[ad_1]

According to Arstechnica (via Platformer), Microsoft has just axed an AI ethics team following the mass layoffs within the company that affected 10,000 employees. The team was responsible for monitoring and reducing the social harms caused by Microsoft AI products.

Microsoft has been making the headlines in recent months for its initial investment in ChatGPT parent company OpenAI and integrating it into its Bing search engine. While all companies that incorporate AI into their products and services have a team to examine the possible associated dangers, Microsoft just laid off its AI ethics team members.

The team reportedly developed a “responsible innovation toolkit” for Microsoft that helped the company’s engineers to predict and eliminate the risks generated by the AI. Former team members say they had a key role in mitigating AI risks in Microsoft products.

Microsoft AI ethics team left the company following recent layoffs

In response to the news, Microsoft announced it remains “committed to developing AI products and experiences safely and responsibly, and does so by investing in people, processes, and partnerships that prioritize this.”

The company also says it has focused on building its Office of Responsible AI in the past six years. This team remains in place and works with the Aether Committee and Responsible AI Strategy in Engineering to mitigate AI risks.

Microsoft’s decision to lay off an AI ethics team coincides with the launch of OpenAI’s most advanced AI model, GPT-4. This model is added to Microsoft Bing, which can stoke even more interest in Google’s rival.

Microsoft started forming its AI ethics team in 2017, and the team reportedly had 30 members. The Platformer reports that the company later scattered the members into different departments as AI competition with Google was heating up. Finally, Microsoft downsized the team to only seven people.

The former employees also claim Microsoft didn’t listen to their recommendations for AI-driven tools like Bing Image Creator that copied artists’ work. The axed employees are now concerned about the possible dangers that AI can expose to users when there’s no one in the company to say “no” to the potentially irresponsible designs.


[ad_2]
Source link