The Texas Rangers want to break up with Bally Sports

0
[ad_1]

Just yesterday, we reported that Bally Sports owner, Diamond Sports Group, officially filed for Chapter 11 Bankruptcy. If DSG thought that calm the nerves of the teams it has rights too, they thought wrong. Now, the Texas Rangers are looking to break up with DSG and Bally Sports.

The Rangers notified DSG that in the event of the company’s insolvency, it would have a right to terminate its contract and that the company’s bankruptcy filing could trigger that termination right. Diamond is hoping to keep the Rangers on their network, and has said that it has never missed a scheduled rights payment to the Rangers. DSG and ARC Holdings – which is the company that oversees Bally Sports Southwest – have made it pretty clear that they will do whatever it takes to hold onto the Rangers.

It’s up to the courts

Now, it’s going to be up to the courts, whether or not the bankruptcy creates the ability for the Rangers to legally terminate the deal. But, the Rangers have said their games will continue to air on Bally Sports Southwest in the meantime.

The team said in a prepared statement that “we expect that there will be no disruption in the televising of Texas Rangers games for the upcoming season. We are confident that a long-term solution will be accomplished for the RSN issue.”

DSG already gave up its rights to four MLB teams earlier this week – Arizona Diamondbacks, Cincinnati Reds, Cleveland Guardians and the San Diego Padres. So if they lose the Texas Rangers too, that would be roughly half of their teams gone. That won’t help DSG turn a profit anytime soon.

Could this happen with other teams? It’s possible. While we don’t know if other teams have the same contracts with DSG or Fox Sports before it, it’s likely that they are all very similar. This really feels like the end of RSNs, in the US. But what could the future mean?


[ad_2]
Source link

Nothing sub-brand Particles by XO nears the launch of its first product

0
[ad_1]

Nothing is gearing up to launch its first-ever second-generation product next week. The Nothing Ear (2) TWS earbuds will debut on Wednesday, March 22. It appears the company will follow up with another pair of TWS earbuds shortly afterward. It has obtained Bluetooth certification for an unannounced audio product that may arrive under its alleged sub-brand Particles by XO.

Nothing is fairly new to the tech industry. That’s evident by the fact that it has yet to launch a second-gen product. However, rumors about it forming a sub-brand have already been doing rounds for the past few months. In December 2022, leaks showed us a new pair of TWS earbuds featuring a “Particles by XO” branding on the case. The source linked the product to Nothing. It was unclear whether “Particles by XO” was the name of the sub-brand or if “Particles” was the name of the product and “XO” was the brand name.

While the mystery was unsolved all this while, the leaked TWS earbuds have now popped up on the Bluetooth SIG certification portal. The listing says it’s a wireless earphone from Nothing and doesn’t mention “Particles by XO” anywhere. However, the model number (B154) is the same as what we saw back in December. This confirms the link between Nothing and Particles by XO. The latter looks certain to be the sub-brand of the new company founded by former OnePlus co-founder Carl Pei.

The Particles by XO TWS earbuds will boast ANC

This certification listing reveals that the new TWS earbuds from Particles by XO will boast Bluetooth 5.2. That’s all we get to know about it today. However, the original leak in December mentioned support for LHDC (Low Latency High-Definition Audio Codec) and ANC (Active Noise Cancellation). By the looks of it, Nothing is targeting the sub-brand at the premium segment while it plays in the cost-sensitive area of the market.

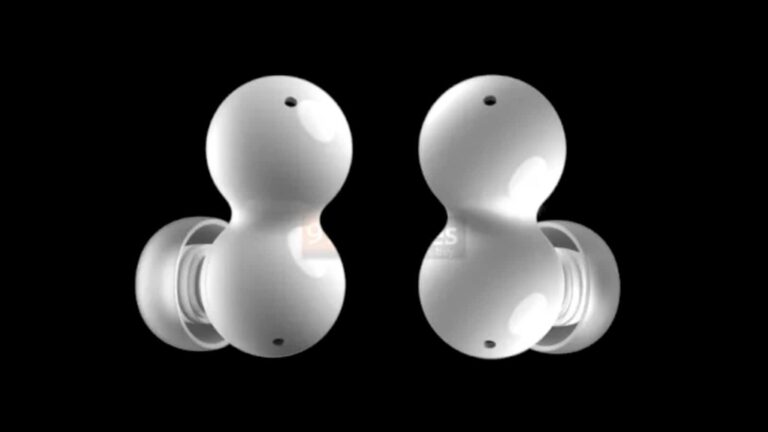
The design of these earbuds is also a massive shift from the company’s current portfolio of semi-transparent products. The upcoming wireless earphones feature a peanut-shaped design. It’s like a glossy plastic peanut dangling out of your ear. Each bud has at least two microphones: one each at the top and bottom. That’s all we know about the first product from Nothing sub-brand Particles by XO. With Bluetooth certification now done, the company may be planning to release the product sooner than later. We will let you know as soon as we have more information about these earbuds.

Nothing sub brand Particles by XO TWS earbuds Bluetooth


[ad_2]
Source link

New Foxconn Factory in India to Manufacture AirPods

0
[ad_1]

AirPods Pro Unsplash

Foxconn has cracked a deal with Apple to produce AirPods in India. The news comes after it was rumored that Apple will start manufacturing AirPods and Beats in India. 

This will be the first time that AirPods will be manufactured in a country outside China. Foxconn is investing $200 million in a new factory in the state of Telangana, India, to manufacture the wireless earbuds. The facility is expected to start construction in the second half of 2023 and begin production by the end of 2024 at the earliest.

The decision to produce AirPods in India is part of Apple’s efforts to diversify its supply chain away from China. Apple’s dependence on China has become increasingly precarious due to the US-China trade war, repeated COVID-19 lockdowns, and others. Apple has accelerated its plans for supply chain diversification to reduce its dependence on China and to mitigate risks associated with geopolitical events.

Foxconn officials reportedly debated internally for months about whether to assemble AirPods, given the relatively low-profit margins, but ultimately decided to go ahead with the deal to “reinforce engagement” with Apple. The decision to set up production in India was requested by Apple, highlighting the company’s commitment to diversifying its supply chain.

It is not clear which model of AirPods will be produced at the Telangana facility, but there is a high chance they will include a USB-C connector instead of a Lightning connector. The move by Foxiconn is also expected to create job opportunities, and could also result in AirPods prices going down in India.

Source: Reuters


[ad_2]
Source link

Memix is the ultimate app for personalizing memes

0
[ad_1]

If you’ve been on the lookout for an app that will help you create memes, check out Memix. This application is very simple, and yet really useful if you’re into memes.

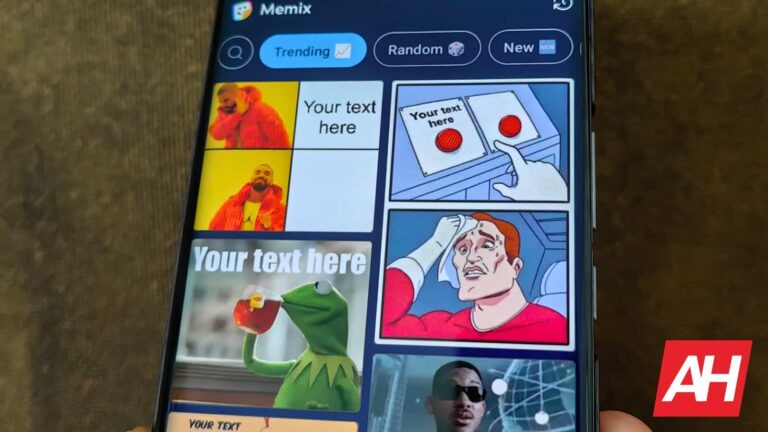
Memix allows you to personalize well-known memes and share them with your friends

So, how does it work? Well, it has a huge collection of well-known meme templates, and also those obscure ones. You can easily search for what you’re interested in, and then add your text to those memes, thus making them your own.

Once you do that, and see the change in real time, you’ll be able to share what you’ve created. A share menu will pop up, with a ton of well-known apps on it. You can, alternatively, save your creation to your phone, if you’d like to share it later or something.

That’s basically it. That’s all there is to it, and yet it may be an incredibly appealing app to some of you. People simply love to send memes these days, and that’s completely understandable, in most casual situations.

Memix has an excellent score in the Google Play Store too. It holds a 4.6-star rating at the moment. If you like creating memes, this app is a must. If you simply love sharing existing memes without personalizing them, well, then you can avoid it. An integrated GIF service in a messaging app will do.

This app is completely free to use, and ad-free

Memix is free to use, and it doesn’t include any ads, which is always nice to see. A download link is included below, and it will take you to Memix’s Google Play Store listing. I’ve also included some official images for the app in the gallery below. You can check those out too, before downloading the app.

Memix app (Google Play Store)


[ad_2]
Source link

T-Mobile is purchasing Mint Mobile

0
[ad_1]

Mergers and acquisitions in the mobile carrier world are not uncommon. Most of the brands powering your device’s service are owned by larger parent companies. T-Mobile just announced that it’s purchasing Mint Mobile for a hefty chunk of change.

You’ve probably seen all of the comedic advertisements for Mint Mobile featuring actor Ryan Reynolds. This is the company that offers you mobile service for as low as $15/month. The thing is that you buy your service in three-month installments for $45.

Ryan Reynolds has been the owner since 2019. Meanwhile, T-Mobile was in the process of merging with Sprint. This process eventually wrapped up in 2020 with Sprint being dissolved.

Now, T-Mobile is purchasing Mint Mobile

In merging with Sprint, T-Mobile sold off Boost Mobile to Dish so that Dish could be a major carrier of its own. So, it looks like Mint Mobile might fill the void left by this transaction.

T-Mobile is purchasing Mint Mobile, in part, using cash and the rest in stocks. 31% will be in cash and the remaining 69% will be done in stocks. In total, the deal weighs in at $1.35 billion. While that’s a lot of money, that’s around 5% of the cost of the Sprint Merger.

So, people are wondering what will change with this deal. Ostensibly, there won’t be a change in the signal quality because Mint Mobile has been using T-Mobile’s towers since it was created. So, you shouldn’t expect any change in that department.

When it comes to the price, that’s something that people are worried about. However, in the announcement, both companies stated that Mint Mobile will keep its $15/month price. Now, we can’t rule out any changes in the overall user experience. So, if you’re a Mint Mobile user, be on the lookout for any emails from the company telling you about the acquisition.

If there are going to be any changes, you shouldn’t expect them to happen just yet. The deal will be finalized later this year.


[ad_2]
Source link

TikTok gets banned on UK government devices

0
[ad_1]

It appears that almost the whole world is against TikTok these days. As you probably know, TikTok is currently banned on government-owned devices in the US, and the European Commission recently banned the app on employees’ devices as well. And now, the ByteDance-owned app receives another blow, this time from the UK government.As Bloomberg reported, the UK government just banned TikTok from phones and other devices used by government ministers and civil servants due to security concerns. As Cabinet Office Minister Oliver Dowden said to Members of Parliament, the ban is a “precautionary move” and comes after a review, which revealed that certain platforms might pose a risk in terms of accessing and using sensitive government data.A TikTok spokesperson stated that TikTok is disappointed by the government’s decision and shared that the company believes the ban is based on fundamental misconceptions and influenced by wider geopolitical factors that TikTok and its UK users are not involved in.

TikTok claims it doesn’t hand users’ data to the Chinese government. But as you probably know, Chinese intelligence laws require companies to aid the Chinese government when asked. Because of this policy, critics fear that the data on devices used by political leaders and officials could fall into the hands of the Chinese government.

However, if you are already addicted to TikTok and want to watch videos on a brand-new smartphone, feel free to visit our best Virgin Media phone deals, best O2 phone deals, and best Vodafone phone deals articles, where you can find amazing deals on some of the best smartphones on the market.


[ad_2]
Source link

Scammers are using AI to create malware infected YouTube videos

0
[ad_1]

Ever since the launch of ChatGPT and its integration into various Microsoft services, Artificial Intelligence (AI) has become an increasingly prevalent technology in our daily lives. This potential has prompted many businesses to integrate AI into their workflow, allowing for increased productivity and the elimination of repetitive tasks. However, according to a report from CloudSEK, a cyber threat management platform, cybercriminals are now leveraging AI to lure unsuspecting users on YouTube to click on links that lead to malware file downloads.

According to the report, the number of YouTube videos inviting people to click on links embedded in video descriptions has increased by 200-300% month-on-month. These videos use screen recordings or audio walkthroughs to describe the steps on how to download and install cracked software like Adobe Premiere Pro and AutoCAD. Additionally, to make these videos appear more authentic, scammers even use platforms like Synthesia and D-ID to create AI-generated avatars and target channels with over 100k subscribers to help the videos reach millions of users.

Once an unsuspecting user clicks on the link in these AI-generated YouTube videos, scammers use info stealer malware such as Vidar, RedLine, and Raccoon to steal passwords, credit card information, bank account numbers, and other confidential data.

How to stay safe from these videos?

To avoid falling victim to these videos, users should look out for red flags such as an AI-generated voice or avatar claiming that premium software like Adobe Premiere Pro can be downloaded without registration or torrents. Further, such videos will often contain instructions on how to troubleshoot issues with downloading files, notes on how to disable antivirus programs, and will prompt users to click on links that may use genuine URL shorteners like bit.ly and cutt.ly and contain a passkey.

Moreover, users should never download anything from unidentified sources and should always verify the authenticity of a site by searching for the domain name on Google. If there is not much information available, it could be a fraudulent site. However, if you have downloaded a file from an unverified source, always run an antivirus before opening it.


[ad_2]
Source link

Samsung is preparing for mass production of third-gen 4nm chips

0
[ad_1]

Samsung is reportedly preparing to begin mass production of third-gen 4nm semiconductor chips within the next few months. According to the Korean media, the company plans to start churning out new advanced semiconductors in the first half of 2023. It has been working on improving the yield rates of the 4nm solutions for the past several months.

Samsung will use a 2.3-generation process for its third-gen 4nm chips, Business Korea reports. The publication says that the company has been able to improve the power consumption and performance of the chips while it worked on solving the yield problem, something that has been haunting it for a while. The Korean tech behemoth recently achieved 60 percent yield rates for 4nm semiconductors, which it considers good enough for beginning mass production.

Samsung improves its 4nm yield rates, prepares for third-gen mass production

Yield rates are a measure of total usable chips out of every 100 produced. A 60 percent yield rate means Samsung will be able to sell 60 out of every 100 chips it manufactures. The higher the yield rate, the lower the waste and hence the cost. Lower yield rates also affect the production capacity as fewer units are usable. Earlier reports say that the Korean firm could only achieve a yield rate of around 35 percent for its first-gen 4nm chips.

This is reportedly the primary reason for Qualcomm switching to TSMC for the production of the Snapdragon 8+ Gen 1 and Snapdragon 8 Gen 2. The Taiwanese firm has had much healthy yield rates of about 70-80 percent since the beginning. Samsung got the contract for the Snapdragon 8 Gen 1 but the American chipmaker went with TSMC for its recent chipsets. TSMC is also expected to get the manufacturing contract for the Snapdragon 8 Gen 3.

Samsung, on the other hand, remains focused on further improving the yield rates of advanced semiconductors. The company has had similar problems with 3nm chips as well. Many of its big clients are switching to TSMC due to this problem. That’s despite the Korean firm beginning mass production of 3nm solutions ahead of its Taiwanese rival. It launched the new chips in June last year, while TSMC announced mass production in December.

Neither firm has started making 3nm processors for smartphones yet. Meanwhile, both Samsung and TSMC are constructing new chip factories in the US with plans to manufacture advanced semiconductors. The former’s plant is located in Taylor, Texas while the latter is building it in Phoenix, Arizona. Both new factories could be operational in the first half of 2024.


[ad_2]
Source link

US Federal Agency Hacked Using Telerik Vulnerability in IIS Server

0
[ad_1]
US Federal Agency Hacked

As a result of a joint effort of the CISA, FBI, and MS-ISAC, a public advisory was published recently.

This public advisory claims that between November 2022 and the beginning of January 2023, attackers gained access to the server of the US Federal Agency Telerik vulnerability.

The joint CSA has provided all the TTPs used to IT, and infrastructure defenders, in order for them to detect and protect against similar, successful CVE-2019-18935 exploits.

At least two threat actors have exploited this Telerik UI vulnerability (CVE-2019-18935) to gain remote control over the unpatched server.

Threat Actor Activity

APT threat actors have been identified by CISA and authoring organizations as a part of the ongoing investigation.

The APT actors include a group known as Threat Actor 1 (TA1) and a group with a history of conducting cybercrime under the name XE Group.

It has been shown that threat actors uploaded malicious dynamic-link library (DLL) files to the directory C:/Windows/Temp when exploiting the vulnerability.

While the threat actors do not only name the files in the Unix Epoch time format, but they also use the date and time that are recorded on the target system to identify the files.

According to the security researchers’ analysis of full packet data capture and reverse engineering of malicious DLL files, the w3wp.exe process does not execute any other malicious processes or sub-processes.

A CISA investigation observed that error messages were being sent to the command and control server of the threat actors when permission restraints prevented the service account from executing the malicious DLLs and creating new files.

IIS server left exposed to attacks

It should be noted that the binding operational directive (BOD 22-01) was issued in November 2021.

In spite of this, it still requires federal agencies to apply recommended actions based on the CISA’s KEV list to which recently the CVE-2019-18935 Progress Telerik UI security vulnerability has been added.

The patch should have been released no later than May 3, 2022, which is the earliest possible date.

However, it appears that the U.S. federal agency failed to secure its Microsoft IIS server by the due date because, based on the IOCs associated with the breach, the due date for securing the server had passed.

Mitigations

In order to minimize the threat of other attacks targeting this vulnerability, CISA, the FBI, and MS-ISAC recommend a number of mitigation measures:-

  • After proper testing of all Telerik UI ASP.NET AJAX instances, you should upgrade all instances to the latest version.
  • Using Microsoft IIS and remote PowerShell, monitor and analyze activity logs generated by these servers.
  • The permissions that can be granted to a service account should be kept at a minimum in order to run the service.
  • It is imperative that vulnerabilities on systems that are exposed to the internet are remedied as soon as possible.
  • Implementing a patch management solution is an efficient and effective way to ensure that your systems are always up-to-date in terms of security patches.
  • It is very important to ensure that vulnerability scanners are configured in such a way as to cover a comprehensive range of devices and locations.
  • In order to separate network segments according to a user’s role and function, network segmentation should be implemented.

Malicious actors exploited a vulnerability in the Microsoft Internet Information Services (IIS) web server used by a federal civilian executive branch agency (FCEB) and were able to execute remote code on the server successfully.

As a result of this advisory, the CISA, FBI, and MS-ISAC encourage you to continuously test your security program in a production environment for optimum performance versus the MITRE ATT&CK techniques.

Indicators of Compromise

  • 11415ac829c17bd8a9c4cef12c3fbc23095cbb3113c89405e489ead5138384cd (1597974061[.]4531896[.]png)
  • 144492284bcbc0110d34a2b9a44bef90ed0d6cda746df6058b49d3789b0f851d (1666006114[.]5570521[.]txt)
  • 508dd87110cb5bf5d156a13c2430c215035db216f20f546e4acec476e8d55370 (xesmartshell[.]tmp)
  • 707d22cacdbd94a3e6dc884242c0565bdf10a0be42990cd7a5497b124474889b (1665130178[.]9134793[.]dll)
  • 72f7d4d3b9d2e406fa781176bd93e8deee0fb1598b67587e1928455b66b73911 (1594142927[.]995679[.]png)
  • 74544d31cbbf003bc33e7099811f62a37110556b6c1a644393fddd0bac753730 (1665131078[.]6907752[.]dll)
  • 78a926f899320ee6f05ab96f17622fb68e674296689e8649c95f95dade91e933 (1596686310[.]434117[.]png)
  • 833e9cf75079ce796ef60fc7039a0b098be4ce8d259ffa53fe2855df110b2e5d (1665128935[.]8063045[.]dll)
  • 853e8388c9a72a7a54129151884da46075d45a5bcd19c37a7857e268137935aa (1667466391[.]0658665[.]dll)
  • 8a5fc2b8ecb7ac6c0db76049d7e09470dbc24f1a90026a431285244818866505 (1596923477[.]4946315[.]png)
  • a14e2209136dad4f824c6f5986ec5d73d9cc7c86006fd2ceabe34de801062f6b (1665909724[.]4648924[.]dll)
  • b4222cffcdb9fb0eda5aa1703a067021bedd8cf7180cdfc5454d0f07d7eaf18f (1665129315[.]9536858[.]dll)
  • d69ac887ecc2b714b7f5e59e95a4e8ed2466bed753c4ac328931212c46050b35 (1667465147[.]4282858[.]dll)
  • d9273a16f979adee1afb6e55697d3b7ab42fd75051786f8c67a6baf46c4c19c2 (SortVistaCompat)
  • dedf082f523dfcb75dee0480a2d8a087e3231f89fa34fcd2b7f74866a7b6608f (1665214140[.]9324195[.]dll)
  • e044bce06ea49d1eed5e1ec59327316481b8339c3b6e1aecfbb516f56d66e913 (1667465048[.]8995082[.]dll)
  • e45ad91f12188a7c3d4891b70e1ee87a3f23eb981804ea72cd23f1d5e331ff5a (1596835329[.]5015914[.]png)
  • f5cafe99bccb9d813909876fa536cc980c45687d0f411c5f4b5346dcf6b304e4 (1665132690[.]6040645[.]dll)
Additional Files
  • 08375e2d187ee53ed263ee6529645e03ead1a8e77afd723a3e0495201452d415 (small[.]aspx)
  • 11d8b9be14097614dedd68839c85e3e8feec08cdab675a5e89c5b055a6a68bad (XEReverseShell[.]exe)
  • 1fed0766f564dc05a119bc7fa0b6670f0da23504e23ece94a5ae27787b674cd2 (xesvrs[.]exe)
  • 5cbba90ba539d4eb6097169b0e9acf40b8c4740a01ddb70c67a8fb1fc3524570 (small[.]txt)
  • 815d262d38a26d5695606d03d5a1a49b9c00915ead1d8a2c04eb47846100e93f (XEReverseShell[.]exe)
  • a0ab222673d35d750a0290db1b0ce890b9d40c2ab67bfebb62e1a006e9f2479c (Multi-OS_ReverseShell[.]exe)
Domains
  • hivnd[.]com
  • xegroups[.]com
  • xework[.]com
IPs
  • 137[.]184[.]130[.]162
  • 144[.]96[.]103[.]245
  • 184[.]168[.]104[.]171
  • 45[.]77[.]212[.]12

Findings

144492284bcbc0110d34a2b9a44bef90ed0d6cda746df6058b49d3789b0f851d

Network Security Checklist – Download Free E-Book

[ad_2]
Source link

Pixel 7a shows up at Bluetooth SIG with Bluetooth 5.3

0
[ad_1]

The Google Pixel 7a has just made another step closer towards its launch. The Pixel 7a appeared over at Bluetooth SIG to get its Bluetooth credentials. It turns out the phone will offer Bluetooth 5.3, as expected.

The Google Pixel 7a will support Bluetooth 5.3 standard

Now, this certification did reveal that the PIxel 7a will have the following model numbers: G0DZQ, GWKK3, GHL1X, and G82U8. That is basically all the information that the site shared, unfortunately.

Pixel 7a Bluetooth SIG image 1

The Pixel 7a did surface a number of times lately. Someone managed to get ahold of a prototype unit, and we’ve already seen plenty of real-life images of the device.

The Pixel 7a will look a lot like the Pixel 7, but it will be a bit smaller. It will allegedly include a 6.1-inch display, just like its predecessor. That display will be a 90Hz panel, though, while the Pixel 6a included a 60Hz panel. And yes, it will be a flat OLED display.

The Google Tensor G2 SoC is expected to fuel the phone. That is Google’s flagship processor at the moment, actually. The Pixel 7a will, of course, be a mid-range phone, so that’s nice to see.

The device will include 8GB of RAM, and a 64-megapixel main camera

The phone will allegedly incorporate 8GB of LPDDR5 RAM and 128GB of UFS 3.1 flash storage. The storage will not be expandable, by the way, so keep that in mind.

A 64-megapixel main camera is tipped to be included. That would be a first for Google. In addition to that, a 12-megapixel ultrawide camera will sit on the back of this phone.

Android 13 will, of course, come pre-installed on the device, while 5W wireless charging was also mentioned. That would be a first for the ‘Pixel a’ series phones. Do note that a charging brick will not be included in the box.

If you’d like to know more about the Pixel 7a, as we’re waiting for the phone’s launch, check out our preview.


[ad_2]
Source link