Location Tracker Firm Tile Hit by Data Breach, Hackers Access Internal Tools

0
[ad_1]

Millions of users of Tile, one of the leading Bluetooth location-tracking device vendors, may have had their personal information exposed following a recent data breach, which has led to a ransom demand.

According to 404 Media, the hacker gained access to internal company tools using the stolen credentials of a former Tile employee and accessed multiple Tile systems to steal sensitive data.

This data included tools used for transferring ownership of the Tile tracker, creating admin accounts, and sending user notifications, as shown in screenshots also provided by the actor.
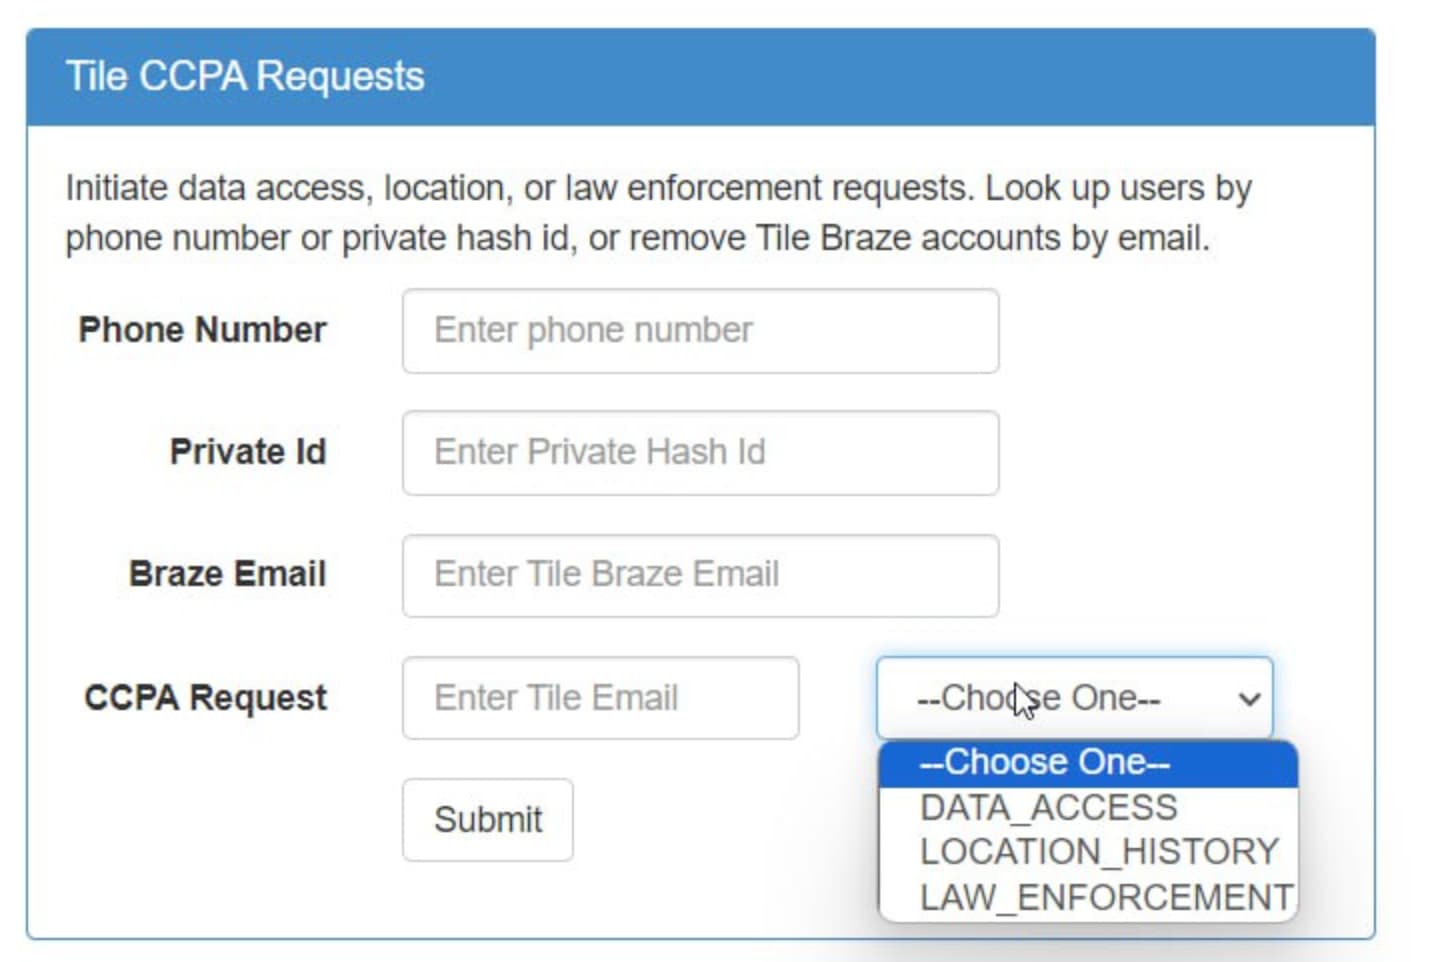
The screenshot shows what the hacker could access amid the data breach (Credit: 404 Media)

Location data-focused Life360, the parent company of Tile, announced on June 11th, 2024 that it had detected unauthorized access to its customer support platform. According to the company’s press release, Tile was targeted by a “criminal extortion attempt,” where an unknown actor informed them about possessing Tile’s customer information.

The company immediately investigated and discovered unauthorized access to a Tile customer support platform, but not the Tile service platform. While the company assures users that no financial data, passwords, or location information was compromised as the platform never stored this data, sensitive user data may be exposed, including names, physical addresses, email addresses, phone numbers, and Tile device identification numbers.

“We believe this incident was limited to the specific Tile customer support data described above and is not more widespread,” Life360 CEO Chris Hulls stated, reinstating their commitment to protecting customer information and taking steps to protect their systems from bad actors. 

It is worth noting that the press release is not available to users outside the United States therefore a screenshot of it is available below:
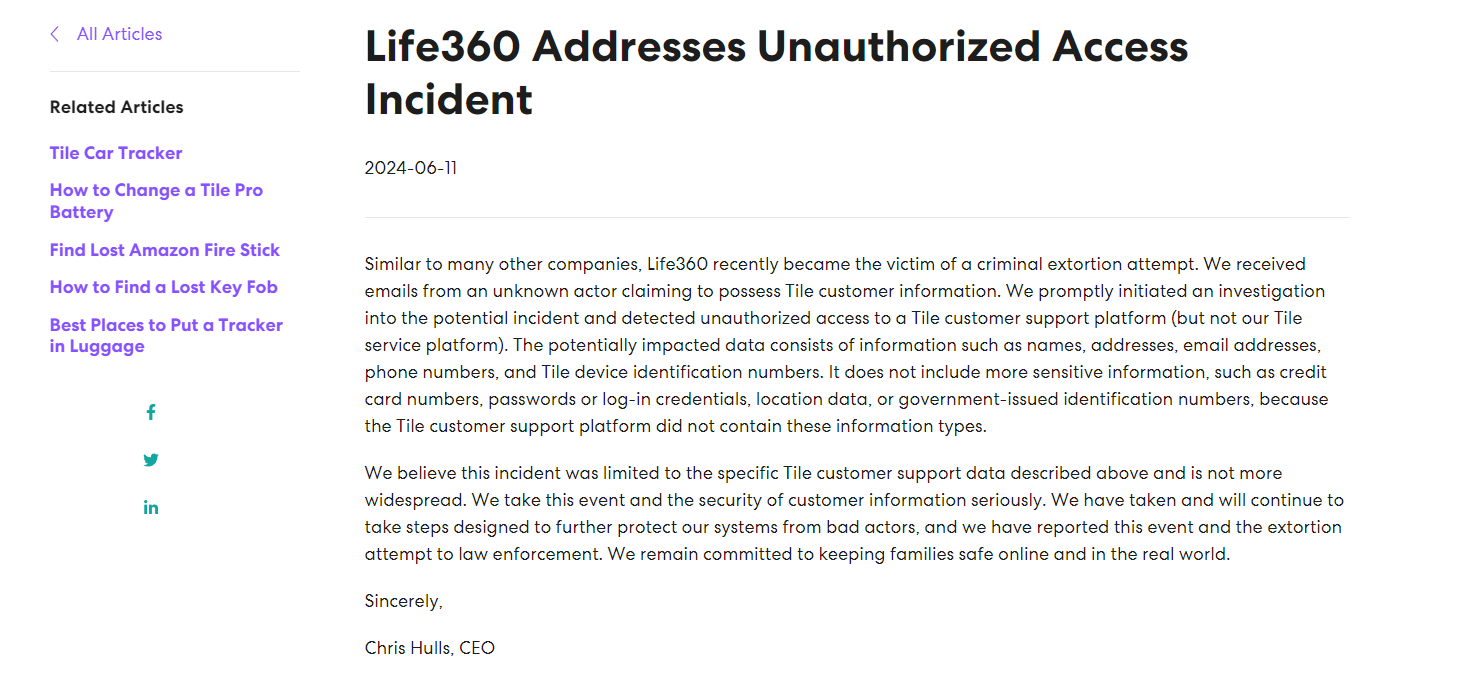
Tile Life360 Data Breach

The company has reported the incident and extortion attempt to law enforcement. Nevertheless, this breach highlights the vulnerability of companies that track people’s locations and how they can become targets for hackers.

Tile users should be cautious of phishing attempts, as email addresses were exposed. Be wary of emails asking for personal information or login credentials. Monitor your accounts for suspicious activity on email and bank accounts associated with your Tile account.

Experts Comments

Piyush Pandey, CEO at Pathlock, a Flemington, New Jersey-based identity and access security provider commented on the data breach pointing out multiple factors involved including the potential threat carried out by former or disgruntled employees and lack of security authentication.

”In this instance, it appears that access was given using the admin credentials of a former Tile employee, which points to a key tenant of identity security – the ability to have proactive visibility to the access and entitlements of users throughout the joiner, mover, leaver portions of the identity lifecycle.”

”It also seems that there was a lack of multi-factor authentication, which may have thwarted access being granted with just a username and password. This breach also points to the criticality of securing service account access in addition to the primary line-of-business applications,” added Piyush.

Callie Guenther, Senior Manager, Cyber Threat Research at Critical Start highlighted the significant threat intelligence implications after the data breach including targeted extortion, supply chain vulnerabilities, data sensitivity, incident response, etc. Callie also advised to implement the following measures to protect administrator accounts:

  1. Multi-Factor Authentication (MFA): Require MFA for all admin accounts to add an extra layer of security.
  2. Strong Password Policies: Enforce the use of strong, unique passwords and regular password changes.
  3. Least Privilege Principle: Grant admin rights only to those who need them, minimizing the number of users with high-level access.
  4. Regular Audits and Monitoring: Continuously monitor and audit admin account activities to detect and respond to suspicious behavior promptly.
  5. Security Awareness Training: Educate employees on recognizing phishing attempts and the importance of safeguarding credentials.
  1. Live Nation Confirms Massive Ticketmaster Data Breach
  2. LetMeSpy Android Spyware Shuts Down After Data Breach
  3. QuaDream, Israeli iPhone hacking spyware firm, to shut down
  4. Hackers Sell Fake Pegasus Spyware on Clearnet and Dark Web
  5. Dell Discloses Data Breach As Hacker Sells 49 Million Customer Data

[ad_2]
Source link
Galaxy Tab S10 series spotted on Samsung OTA server

0
[ad_1]

Samsung has been doing an excellent job in the smartphone market, and another area where Samsung is doing relatively well is tablets. The company is set to introduce the new Galaxy Tab S10 series and has already started One UI testing for the new devices. South Korean company plans to announce the new tablets in 2025. We expect the Galaxy Tab S10 series to debut alongside the Galaxy S25 series and Galaxy Z Fold 6 Ultra.

Samsung is developing the Galaxy Tab S10 series

Earlier, we shared with you that we discovered the Galaxy Tab S10 Plus and Tab S10 Ultra in our database. The model number for the Galaxy Tab S10 Plus is SM-X828x, while the Galaxy Tab S10 Ultra’s model number is SM-X926x. Note that the “x” in the model numbers refers to the region code. The model numbers had surfaced earlier. Now, we have discovered that Samsung is testing One UI builds for the upcoming tablets on Samsung’s servers.

We discovered a test build for Galaxy Tab S10 Plus with the build number (X828USQUAXF5/X828UOYNOAXF5/X828USQUOAXF5) on Samsung’s servers. The build number, including “X828U,” confirms the device’s model number (SM-X828). The presence of “U” within the code points towards a US variant of the tablet. Additionally, the “XF” signifies a build compiled in June, while the final digit “5” represents the current build number. This information reveals that Samsung is actively testing software specifically designed for the US version of Galaxy Tab S10 Plus. Note that the “U” letter in the “UAXF5” is for the new features and bug fixes.

Samsung has also started testing One UI builds for the Galaxy Tab S10 Ultra. A firmware with the model number (X926BXXUOAXE6/X926BOXMOAXE6/X926BXXUOAXE6) is present on Samsung’s server. “SM-X926B” model number is for Galaxy Tab S10 Ultra, with the “B” indicating it will launch globally. “XE” shows the build was compiled in May, and “6” represents the 6th test build for the Galaxy Tab S10 Ultra.

Our previous findings only included the model number SM-X926B for Galaxy Tab S10 Ultra. However, we have now spotted additional model numbers, SM-X926C and SM-X926N. This reveals that Korean and Chinese variants of the Galaxy Tab S10 Ultra have also surfaced.

Expected Features & Release Date

While details about the Galaxy Tab S10 series technical specifications remain under wraps, there’s plenty of reason to be excited. The previously surfaced leaks revealed Galaxy Tab S10 Plus will come with MediaTek Dimensity 9300 though.

Samsung still has a considerable amount of time before officially introducing the Galaxy Tab S10 series. Note that Samsung has not yet released a test build for the regular Galaxy Tab S10. It seems Samsung is first focusing on the Plus and Ultra models, not because they are ditching the regular model, but because there is still a long time ahead of the tablet’s launch.

We do not have the exact launch date for the Galaxy Tab S10 series, but we expect the devices to be available in Q1 2025. Samsung introduced the Galaxy Tab S8 and Galaxy S22 series in March 2022, followed by new devices one and a half years later. In August 2023, Samsung launched the Galaxy Tab S9 and Galaxy Z Fold 5. We anticipate that the new Galaxy Tab S10 series will launch alongside the Galaxy S25 after a similar break of approximately 1.5 years again.


[ad_2]
Source link

Sleepy Pickle Exploit Let Attackers Exploit ML Models & End-Users

0
[ad_1]

Hackers are targeting, attacking, and exploiting ML models. They want to hack into these systems to steal sensitive data, interrupt services, or manipulate outcomes in their favor.

By compromising the ML models, hackers can degrade the system performance, cause financial losses, and damage the trust and reliability of AI-driven applications.

Cybersecurity analysts at Trail of Bits recently discovered that Sleepy Pickle exploit lets threat actors to exploit the ML models and attack end-users.

Technical Analysis

Researchers unveiled Sleepy Pickle, an unknown attack exploiting the insecure Pickle format for distributing machine learning models. 

Unlike previous techniques compromising systems deploying models, Sleepy Pickle stealthily injects malicious code into the model during deserialization. 

Free Webinar on API vulnerability scanning for OWASP API Top 10 vulnerabilities -> Book Your Spot

This allows modifying model parameters to insert backdoors or control outputs and hooking model methods to tamper with processed data by compromising end-user security, safety, and privacy. 

The technique delivers a maliciously crafted pickle file containing the model and payload. When deserialized, the file executes, modifying the in-memory model before returning it to the victim.

Corrupting an ML model via a pickle file injection (Source – Trail of Bits)

Sleepy Pickle offers malicious actors a powerful foothold on ML systems by stealthily injecting payloads that dynamically tamper with models during deserialization. 

This overcomes the limitations of conventional supply chain attacks by leaving no disk traces, customizing payload triggers, and broadening the attack surface to any pickle file in the target’s supply chain. 

Unlike uploading covertly malicious models, Sleepy Pickle hides malice until runtime. 

Attacks can modify model parameters to insert backdoors or hook methods to control inputs and outputs, enabling unknown threats like generative AI assistants providing harmful advice after weight-patching poisons the model with misinformation. 

The technique’s dynamic, Leave-No-Trace nature evades static defenses.

Compromising a model to make it generate harmful outputs (Source – Trail of Bits)

The LLM models processing the sensitive data pose risks. Researchers compromised a model to steal private info during conception by injecting code recording data triggered by a secret word. 

Traditional security measures were ineffective as the attack occurred within the model.

This unknown threat vector emerging from ML systems underscores their potential for abuse beyond traditional attack surfaces.

Compromising a model to steal private user data (Source – Trail of Bits)

In addition, there are other kinds of summarizer applications, such as browser apps, that improve user experience by summarizing web pages.

Since users trust these summaries, compromising the model behind them for generating harmful summaries could be a real threat and allow an attacker to serve malicious content.

Once altered summaries with malicious links are returned to users, they may click such a link and become victims of phishing scams or malware.

Compromise model to attack users indirectly (Source – Trail of Bits)

If the app returns content with JavaScript, it is also possible that this payload will inject a malicious script.

To mitigate these attacks, one can use models from reputable organizations and choose safe file formats.

Free Webinar! 3 Security Trends to Maximize MSP Growth -> Register For Free


[ad_2]
Source link

Ulefone shares Armor 26 Ultra durability tests: Video

0
[ad_1]

Ulefone has just shared the Armor 26 Ultra durability tests in a video format. You can check out the said video below the article, as it has been embedded. It has a duration of a minute and a half, and it has some really “fun” tests in it.

The Ulefone Armor 26 Ultra durability test video is actually quite fun to watch

Ulefone is always trying to think of new and fun ways to torture test its devices. In this video, you’ll see a paper burning on a phone. In addition to that, Ulefone decided to use the Armor 26 Ultra’s screen as a hammer, and stab it with a knife… in addition to other tests.

Drop tests are also included here, of course. The Armor 26 Ultra got thrown down a flight of stairs and from various distances. It was even frozen and then thrown from a specific distance. In this video, Ulefone also proved that the Armor 26 Ultra is water-resistant.

This phone is IP68/IP69K & MIL-STD-810H certified

Yes, the phone is both IP68/IP69K and MIL-STD-810H certified. That not only means that it can survive under water, but also that it can withstand dust, and be dropped from a specific height (up to 1.8 meters).

Ulefone also included the Gorilla Glass 5 on top of the Armor 26 Ultra’s display. That display protection is obviously enough for this phone to be used as a hammer, which says a lot about Corning.

It has a gigantic battery on the inside

The Armor 26 Ultra is one of the company’s newest smartphones, and in addition to being a tank, it also has a 15,600mAh battery. The phone supports 120W charging, and it is fueled by the MediaTek Dimensity 8020 SoC.

It comes with 12GB of RAM, but you can expand that up to 24GB thanks to virtual RAM. The phone includes 512GB of internal storage. It is also worth noting that it comes in regular and Walkie-Talkie versions.

This handset will soon be on sale as part of the Ulefone Summer Sale. Various other devices will be discounted up to 69%, by the way. You can find all the relevant links below.

Buy the Ulefone Armor 26 Ultra (AliExpress)

Buy the Ulefone Armor 26 Ultra Walkie-Talkie (AliExpress)

Ulefone Armor 26 Ultra (more info)

Ulefone Armor 26 Ultra Walkie-Talkie (more info)

Ulefone Summer Sale


[ad_2]
Source link

SolarWinds Serv-U Vulnerability Let Attackers Access sensitive files

0
[ad_1]

SolarWinds released a security advisory for addressing a Directory Traversal vulnerability which allows a threat actor to read sensitive files on the host machine.

This vulnerability existed in the SolarWinds Serv-U File Transfer solution and was assigned with CVE-2024-28995 – 8.6 (High).

This vulnerability affected multiple SolarWinds Serv-products in both Windows and Linux platforms.

However, it was fixed in the latest version, SolarWinds Serv-U 15.4.2 HF 2. The company also recommends that users upgrade their products to the latest version.

Free Webinar on API vulnerability scanning for OWASP API Top 10 vulnerabilities -> Book Your Spot

According to the reports shared with Cyber Security News, this vulnerability affected Server-U FTP server 15.4, Serv-U Gateway 15.4 and Serv-U MFT Server 15.4.

The Serv-U is a C++-written application that contains the majority of the code in the Serv-U.dll binary. 

On analyzing this binary further, it was discovered that there was a modified function sub_18016DC30.

This modified version of this function processes a file path with added checks. The check was written in such a way that it checks particularly for the double dot path segment (\..\) and if found, it is sanitized.

Further investigations concluded that most of this function’s use cases contain two HTTP request parameters, InternalDir and InternalFile, both of which call the vulnerable function. 

However, when providing a directory traversal payload to these parameters on a vulnerable version of Serv-U, the application processed the payload and triggered the directory traversal vulnerability.

This vulnerability can also be modified to reach an arbitrary file on the target server that could reveal sensitive information.

As an added fact, if the Serv-U application is installed on a Windows machine, the system data will be stored in the following path C:\ProgramData\RhinoSoft\Serv-U\.

Further, Serv-U-StartupLog.txt on the system data folder contains the application logging information emitted during application startup and will also include the target Serv-U server’s version number.

On a Linux platform, this vulnerability can be triggered to read.

Users of SolarWinds Serv-U are recommended to upgrade to the latest version or apply the 15.4.2 Hotfix 2 to remediate this vulnerability.

Free Webinar! 3 Security Trends to Maximize MSP Growth -> Register For Free


[ad_2]
Source link

Motorola announces launch date for Razr 50 foldable phones

0
[ad_1]

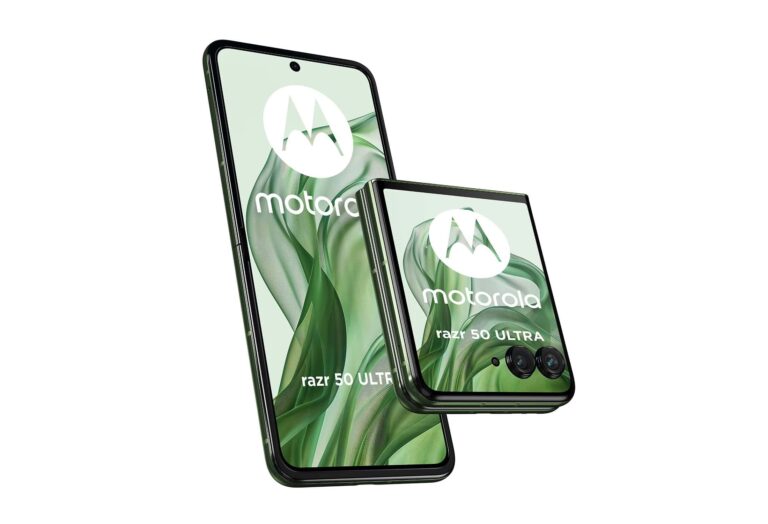
After some speculation, Motorola has now announced a launch date for the Razr 50 series. Two foldable smartphones are expected to arrive, and the said date is June 25. So in 11 days from this point in time.

The Motorola Razr 50 series launch date has been confirmed

Do note that this confirmation comes via Motorola from China, as it’s a launch event in China. The global variants of the phone(s) will launch later on. The devices in question are the Motorola Razr 50 and Razr 50 Ultra.

Motorola Razr 50 series launch confirmation

In addition to the launch date, the Motorola Razr 50 Ultra also paid a visit to the FCC, TUV Rheinland, and Dekra certifications. Those listings revealed that the phone will have a 4,000mAh battery, and come with nano SIM + eSIM combo, at least in some markets. 68W charging is also expected.

We know what the phones will look like

We also know what the phone will look like already. Evan Blass confirmed the design of the phone a while back. It will have a huge display on the back, with thin bezels. The cameras will be included inside it, but everything else will be covered by the display, basically, as you can see below.

Motorola Razr 50 Ultra render leak 1

That is said to be a 4-inch cover display, in addition to a 6.9-inch main display. The main display on the Razr 50 Ultra will offer a 165Hz refresh rate. The Snapdragon 8s Gen 3 SoC is said to fuel the Motorola Razr 50 Ultra. The phone will be equipped with 12GB of RAM and 256GB of internal storage.

The Razr 50 will be inferior to the ‘Ultra’, but still very powerful

The Motorola Razr 50, on the other hand, is rumored to include the MediaTek Dimensity 7300X chip. It will also ship with 8GB of RAM and 256GB of internal storage. A 50-megapixel main camera is expected, in addition to a 13-megapixel ultrawide unit. On the front, you’ll find a 13-megapixel snapper.

The vanilla Razr 50 model will have a 3.63-inch cover display and a 6.9-inch main display with a 120Hz refresh rate. A 4,200mAh battery is tipped for the Motorola Razr 50.


[ad_2]
Source link

ARM wants to destroy Snapdragon X laptops over contract dispute with Qualcomm

0
[ad_1]

After a long wait, Qualcomm’s highly anticipated Snapdragon X processors are finally making a market debut. Windows PCs powered by Snapdragon X Elite and Snapdragon X Plus will start hitting shelves next week. This is a big deal because these are the only chips rated powerful enough for Microsoft’s new AI PC ecosystem Copilot+. Artificial intelligence is a big deal today, you know. However, Snapdragon X may have an anti-climactic end if ARM wins its legal battle against Qualcomm.

ARM threatens to disrupt the Snapdragon X AI PC wave before it takes off

This high-profile legal battle began after Qualcomm acquired Nuvia, a designer of CPUs based on the ARM architecture, in 2021. The $1.4 billion acquisition laid the foundation for Snapdragon X. However, ARM alleged that Qualcomm misused a licensing deal Nubia had signed before the acquisition. According to the British firm, Nubia had licensed a technology from ARM to design server chips but Qualcomm scrapped the plans and reassigned the team to develop a laptop processor.

ARM says Qualcomm’s Snapdragon X chips are “a direct technical descendant of Nuvia’s chip” based on its technology. Since neither Qualcomm nor Nubia renewed the licensing contract after the acquisition, the license stands canceled. As such, Qualcomm’s using the technology for its PC processors is a violation of its intellectual property. ARM formally filed a lawsuit over the matter in August 2022 after the parties failed to negotiate a new licensing contract.

Qualcomm, on the other hand, says its broad license for Arm technology already covers its Snapdragon X chips. “Arm’s complaint ignores the fact that Qualcomm has broad, well-established license rights covering its custom-designed CPUs, and we are confident those rights will be affirmed,” Ann Chaplin, the company’s general counsel, said in a statement in 2022. A Qualcomm spokesperson recently told Reuters its position has not changed since ARM filed the lawsuit two years ago.

There’s a real concern in the industry

ARM’s lawsuit against Qualcomm has hardly progressed in these two years. However, there’s still a real concern that this licensing dispute could abruptly halt the shipment of new Snapdragon X-powered AI PCs. Attendees at Computex 2024, where Qualcomm unveiled its AI PC vision inviting executives from several big companies to the stage, were discussing the potential supply disruption if ARM wins the legal battle. Qualcomm’s vision and plans could come to a standstill.

“It’s definitely a real risk,” said Doug O’Laughlin, the founder of Fabricated Knowledge, a chip financial analysis firm. “The more successful (the laptops are), the more fees ARM can get eventually.” Qualcomm has signed deals with around 20 PC makers for AI PCs powered by the Snapdragon X Elite and Snapdragon X Plus. Nearly two dozen laptops are expected to go on sale starting on June 18. An ARM victory would deal a severe blow to the plans.

“ARM’s claim against Qualcomm and Nuvia is about protecting the ARM ecosystem and partners who rely on our IP and innovative designs, and therefore enforcing Qualcomm’s contractual obligation to destroy and stop using the Nuvia designs that were derived from ARM technology,” an ARM spokesperson said. The SoftBank-owned British company wants to destroy Snapdragon X before Qualcomm and Microsoft even realize the dream of Copilot+ AI PCs.

Interestingly, despite all this, ARM and Qualcomm have a close relationship in the industry. ARM is Qualcomm’s biggest supplier, while Qualcomm is ARM’s second-biggest customer. Hopefully, the two firms will find a solution that doesn’t disrupt the emerging AI PC ecosystem. The trial is scheduled to begin in the federal court in Delaware in December. However, some industry experts believe the companies will settle the case out of court in the coming months.


[ad_2]
Source link

A major pop star joins this super-app, but it’s not what you think

0
[ad_1]

Ariana Grande, a beloved pop singer, joined the South Korean super-app Weverse.

Usually, when we talk about the thing called super-app, we mean an app through which you can do various everyday-related things. Ordering a cab, ordering food, sending and receiving money, and much more: a super-app combines messaging, social media, e-commerce, financial services, and more.

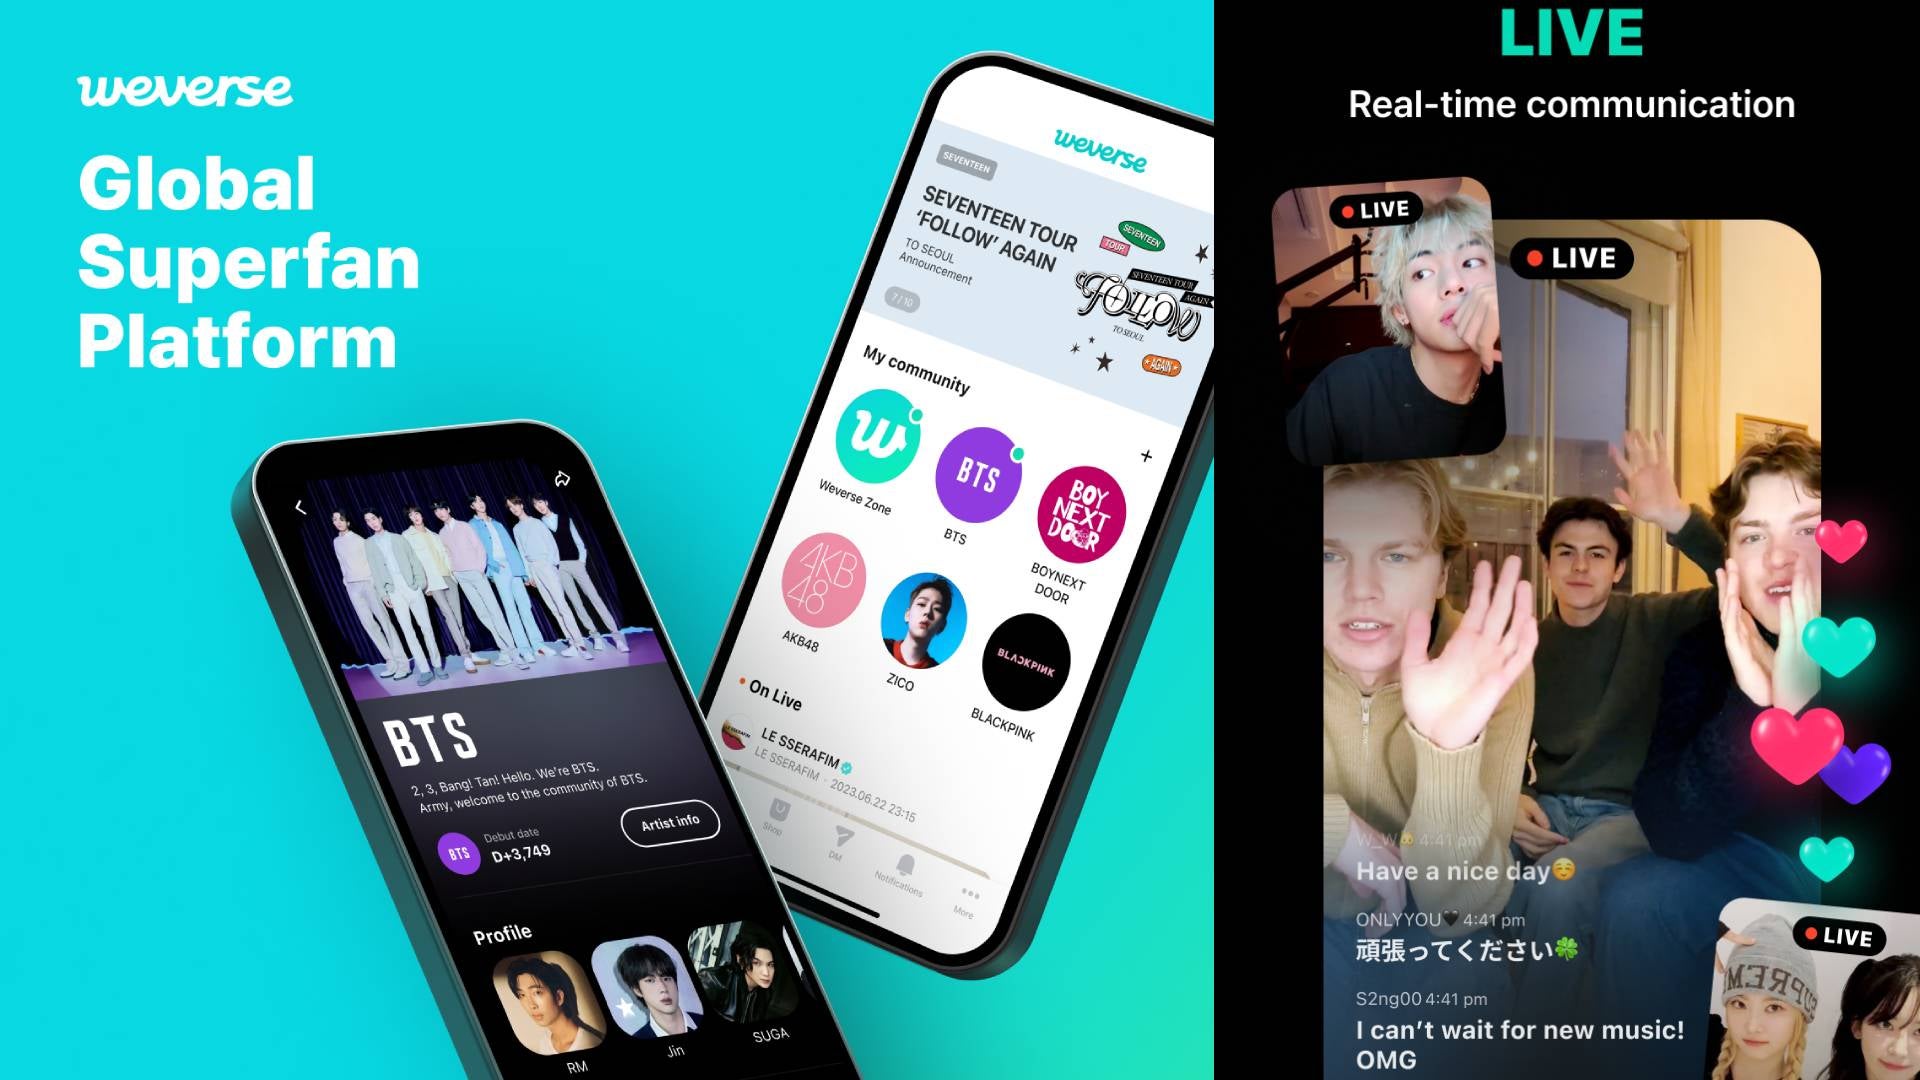
The aforementioned Weverse, however, is substantially different from a “traditional” super-app. Weverse, as the latest Reuters report tells us, is a superfan platform owned by HYBE, the entertainment firm behind K-Pop sensation BTS.

On Weverse, the report continues, artists can write posts, livestream, and sell merchandise directly to their followers.

For example, the app gained significant attention when BTS member Jin’s livestream, following his military service, drew over 2 million views in just 10 minutes despite initial technical issues.

Launched in 2019, Weverse had an average of over 10 million monthly active users in the third quarter of 2023. Impressively, nine out of ten Weverse users are based outside of South Korea, highlighting its global reach.

The “traditional” super-app


The super-app as a concept is a mobile application that integrates multiple services and functions into a single platform, streamlining various digital interactions for users. Originating in Asia with pioneers like WeChat in China and Grab in Southeast Asia (it’s very popular in Singapore, where I enjoyed using it!), super-apps combine messaging, social media, e-commerce, financial services, and more.

The goal is very simple, almost brilliant, one could say: the consolidation of services into one app means that users should not have the need to switch between multiple applications and spend more time in this single super-app.

This allows users to perform a wide range of activities, such as booking a ride, making payments, shopping online, and communicating, all within the same app. Super-apps leverage their extensive user bases to gather valuable data, which can be used to refine services, improve user experience, and offer personalized recommendations.


[ad_2]
Source link

WhatsApp adds screen sharing with audio, increases video call participants, and more

0
[ad_1]
WhatsApp is constantly rolling out updates to enrich the experience of its massive user base, which exceeds two billion. Now, the messaging app under Meta’s umbrella has introduced fresh features to enhance video calling on both desktop and mobile versions.

Better calling across desktop and mobile


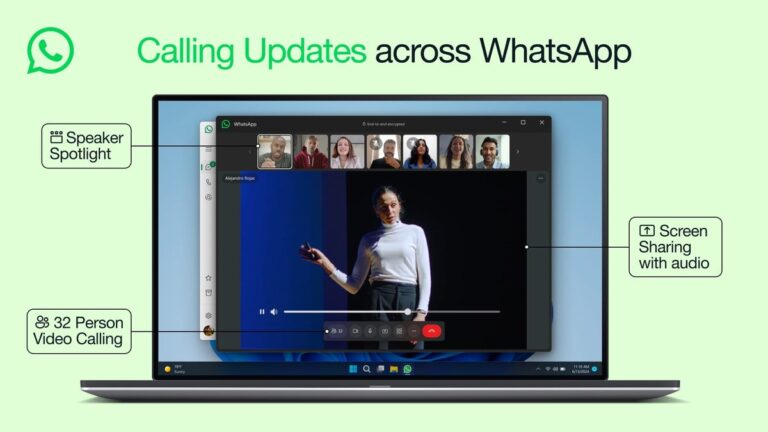
WhatsApp will introduce a series of new improvements in the coming weeks. One standout feature is the ability to share your screen with audio, which is perfect for watching videos together. Now, when you share your screen, you can also share the audio, enhancing the experience significantly. And speaking of audio, another enhancement is coming to WhatsApp: Meta recently introduced the MLow codec to enhance call reliability and now this technology is being integrated into WhatsApp.

The MLow codec from Meta is a new tool designed to improve audio quality, particularly beneficial for users on slower connections. With MLow, audio becomes clearer overall, even if your network is slow or you use an older device.

Additionally, calls made on mobile devices now come with improved noise and echo cancellation, making it easier to have conversations in noisy environments.

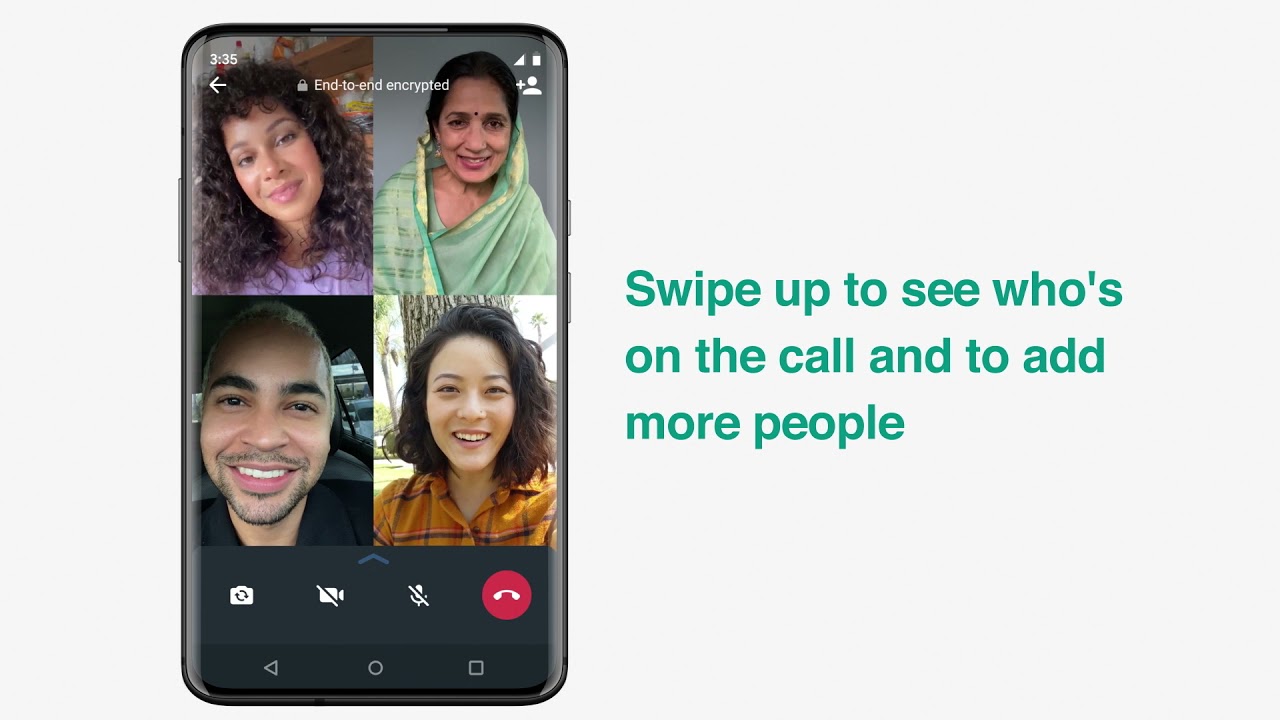
Finally, you can now host video calls with up to 32 people across all your devices. Previously, WhatsApp allowed up to 32 participants on mobile devices, with limits of 16 on Windows and 8 on macOS.

Video Thumbnail

If you want to learn how to join a group call on WhatsApp, check out the video above | Video credit – WhatsApp

WhatsApp’s new ability to host video calls across various devices mirrors Apple’s FaceTime, where iPhone and iPad users can also gather up to 32 participants. However, platforms like Google Meet and Zoom allow up to 100 participants, even on their free plans.

By consistently introducing updates like those mentioned above, WhatsApp stays ahead in the competitive landscape. These enhancements not only improve user experience but also make the app more appealing, drawing in new users, which, after all, is the end game of every business.


[ad_2]
Source link

YouTube tests new features to help you find, watch, and engage

0
[ad_1]
YouTube, the world’s most popular online video platform, is constantly experimenting with new features. Just recently, YouTube started testing AI summarizer on Shorts, and now the Google-owned service has even more features in the works.

YouTube is trying out new features like AI live chat summaries, Google Lens search, and more


AI is the big buzz these days, and YouTube is jumping in on the action. It’s now testing AI-powered live chat summaries to help you quickly catch up and dive into the conversations during live streams.Using AI, this feature analyzes the live chat and gives a summary of the ongoing conversation. This allows you to join in with a better context. For instance, if you join late for something like Google’s I/O live conference, you can quickly catch up on everything you’ve missed so far using the live chat summary.

This experiment is being tested with a small group of viewers who join eligible live streams in English with highly active live chat discussions. Currently, this experimental feature is only available in some countries.

Coming up next is the ability to use Google Lens to search on YouTube. If you are part of the experiment, you will notice a Lens button in the search bar. Simply tap the Lens button to search using your camera and get relevant YouTube content as your results.

You’ll also have the option to get additional details about the visuals by clicking “Search on Google.” This test is currently being introduced to a limited number of viewers using YouTube on Android phones.

YouTube is also trying out channel QR codes to make it simpler for creators to share their channels. If you’re a creator involved in this trial, you can share your channel QR code by:

  1. Finding the “You” tab in the bottom app menu,
  2. Selecting the chip below your handle labeled “Share your channel”,
  3. Choosing “QR code” from the menu that appears.

Viewers can discover and share creators’ QR codes by:

  1. Tapping the three-dot menu on the creator’s channel page
  2. Selecting “Share”
  3. Choosing the QR code option

The QR codes can be scanned both online and offline. Initially, this feature is being introduced to a limited number of creators but will be gradually expanded later on. Finally, the video platform is experimenting with user-generated effects in Shorts. Creators with access to this feature can personalize and enhance Shorts, creating and sharing their own effects directly on YouTube Shorts. If this feature is available to you, you’ll find it within the Effects button when you are creating a Short.

YouTube is currently testing these features using YouTube feature experiments, giving select groups of users the chance to try them out before they’re widely available. However, not all features tested necessarily make it to public release.

Bringing these features to its large user community would definitely elevate the YouTube experience. For example, imagine how handy Google Lens within YouTube could be – just point your camera at your friend’s latest smartphone and instantly dive into a review.

YouTube’s feature experiments allow the platform to boldly test new ideas. This approach lets the Google-owned platform gauge its potential without risking a negative impact on its broad user base.


[ad_2]
Source link