How Residential Proxies Enable It 

0
[ad_1]

In a world where Internet and global connectivity is everything, it is essential for access to information and content to be unrestricted by borders. However, geographical limitations frequently restrict individuals’ access to web pages, services, and information based on their location, which frustrates users seeking open access to global content.

One such example is China, where Google and Facebook are still banned in 2024. Nevertheless, residential proxies provide a secure method for users to circumvent these restrictions with ease.

What Are Residential Proxies? 

Residential proxies are intermediary servers that give you another IP address assigned by a real Internet Service Provider (ISP) to an actual device. Consequently, when you use a residential proxy server, websites receive your requests as if they come from somewhere else which is in fact the location of the proxy itself anywhere across the globe. This not only helps one avoid geo-restrictions but also boosts privacy and security while online.

Breaking Down Geo-Restrictions 

Geo-blocking or geo-restrictions refer to limiting contents’ accessibility using geographical locations of its users by certain companies. This is usually witnessed on streaming platforms, news pieces as well as in retail where products/services vary depending on a user’s location. By hiding your true identity behind one’s own IP address using residential proxies, it enables locational-based contents such as news portals be accessed abroad as if it were local.

Benefits of Using Residential Proxies for Accessing Global Content

The benefits of having residential proxies do not just stop at watching shows that are restricted geographically in Netflix or viewing country-specific news websites. Here are some key advantages:

  • Better Privacy and Anonymity: Your original IP address gets hidden with residential proxy redirecting your internet connection which protects your identity together with personal data from possible cyber threats.
  • More Diverse Content Availability: Whether it is a video-sharing platform, social media network or online library, there might be fewer limitations imposed by residential proxies, thus giving a more varied and richer online experience.

Choosing the Right Residential Proxy Provider 

Choosing the most suitable residential proxy provider is crucial to having reliable and effective access to worldwide contents. Consider the following:

  • Reliability and Speed: Always find those providers with stable connections and high speeds for smooth browsing as well as streaming.
  • Range of Locations: Providers who offer a wide selection of countries/cities can help you globalize your internet experience in essence.
  • Ethical Considerations: Prefer providers who acquire IP addresses legally and transparently so as not to come across legal issues.

Case Studies: Success Stories with Residential Proxies

Expanding Global Research Capabilities

One market research company based in Canada used residential proxies to gain access to streaming content in more than 30 different countries. This was important for their project on analyzing global trends in streaming service preferences and viewership behaviors. Utilizing residential proxies helped to avoid geo-blocking that would prevent accessing regional-specific content portals by the firm.

As a result, some of their findings contributed to improving the content offerings and promotional strategies for a major streaming service across various markets, leading to increased subscriptions in several key regions.

Enhancing Real-Time Data Accessibility for Financial Services

Another example would be of a financial analysis corporation who went for proxies in order to get real-time information regarding stock markets from different parts of the world. They adopted residential proxies so that they could appear like locals in areas where before they had to put up with huge delays and denied access due to being flagged as bots. This made it easier for them to have access to such crucial finance reports like market prices instantly, which enabled them to make better-informed investment decisions and offer improved services for their clients.

Localized Testing That Enhances E-commerce Strategies

The reason why an e-commerce platform used residential proxies was because they wanted to test their websites all over the world and optimize them at various locations. The software developers of this website used this kind of proxy so that while designing, it would display the site just like it appears on other people’s computers across the globe.

For instance, malfunctioning currency exchange rates, limited use of languages and specific region user interfaces are some localization problems these staff were able to detect. As a result, there was a remarkable increase in user interaction within previously unproductive markets.

Social Media Management Without Borders

A social media management company relied on residential proxies for managing numerous accounts in different countries without violating any rules or regulations leading to bans or restrictions by social networks. It was especially important considering their regional targeting strategy as well as localized content creation tactics.

Thus, these servers were key in handling customer accounts based in Europe, Asia and the US through customization using content and engagement strategies that reflected culture peculiarities and preferences of each area respectively. Therefore, followership growth rate increased significantly, translating into increased client engagement level.

Content Compliance and Verification

In its bid to ensure compliance with various countries’ laws, a media house drew upon residential proxies. By doing this it allowed its compliance division members to be accessing content as viewers from those respective nations making sure that anything that is published meets local requirements set by law firms. This way the company managed to avert possible lawsuits and maintained its reputation as a culturally sensitive and responsible firm.

Conclusion

The unlimited advantages of residential proxies are that they provide access to worldwide internet content. They do not only eliminate geographical constraints, but also enhance security and privacy when surfing the net.

Residential proxies are gateways through which you can achieve more openness on the web whenever you need, be it for personal or business needs. Consider leveraging these tools for access to global content.

Through residential proxies, both corporate bodies and individuals can embrace innovation by broadening their horizons, gaining deep insights into everyday operations while at the same time optimizing online experiences.

Whether one is a market researcher or financial analyst, an e-commerce entrepreneur or social media manager or even just a content creator of whatever kind, these techniques provide endless opportunities for accessing international content in today’s digital era.

  1. Tools for Testing Your Proxy Servers
  2. Proxy or VPN for Netflix – Which is Best?
  3. Can You Secure Your Smartphone with a Proxy?
  4. Almost Every Major Free VPN Service is a Glorified Data Farm
  5. What is Dark Web, Search Engines, What Not to Do on Dark Web

[ad_2]
Source link

April update live for Galaxy A54, A53, A34 & more devices

0
[ad_1]

Following a US release earlier this month, Samsung‘s April update for the Galaxy A54 and Galaxy A53 is now live in international markets. The new security patch is also rolling out to the Galaxy A34 and Galaxy Tab S9 FE series. The company has already updated dozens of other Galaxy devices.

Galaxy A54, A53, and other devices get the April update

The Galaxy A53 was one of the first Samsung devices to receive the April security update. The company began the rollout in the US. Last week, the US version of the Galaxy A54 also joined the party. Both devices are now getting the update in international markets, starting in Europe. A global rollout should follow soon.

The April update for the Galaxy A54 comes with the firmware build number A546BXXS7BXD1 in Europe. That for the Galaxy A53 is A536BXXS9DXD1. Neither phone is getting anything more than the latest SMR (Security Maintenance Release), i.e., this month’s security patch. It contains over 40 vulnerability fixes.

These security fixes are also rolling out to the Galaxy A34 in Europe. The device is getting the build number A346BXXS6BXD1. The changelog is identical to the aforementioned two A-series devices. Samsung didn’t release the Galaxy A34 in the US, but users in other regions can expect to receive this update in the coming days.

The Galaxy Tab S9 FE and Galaxy Tab S9 FE+ are also picking up Samsung’s April SMR. The update for these two mid-range tablets is widely available in Europe and Latin America with build numbers ending in BXD6 (last four characters). As you might expect, the update is all about the latest security fixes.

All of these devices will get One UI 6.1

The Galaxy A54, Galaxy A53, Galaxy A34, and Galaxy Tab S9 FE series are all currently running on Android 14-based One UI 6.0. Samsung will soon update these devices to One UI 6.1. The new version debuted with the Galaxy S24 series and has already made its way into a few older flagships, including the Galaxy S23 series.

These mid-range products are unlikely to get the new AI features, though. Samsung has already confirmed that its 2021 flagships will only receive Circle to Search and Chat Assist with One UI 6.1. At best, these devices will get the same two AI features. Do not expect Live Translate, Interpreter, Generative Edit, and other AI-powered tools. We will let you know when we have more information.


[ad_2]
Source link

Top tech brands have insufficient ad transparency tools

0
[ad_1]

Many of us are familiar with ads across the internet, but not many people know where they come from. Sure, you conveniently see ads for products and services that you recently Googled, but that doesn’t really tell you much. Well, according to a new report, many of the big brands serving us ads have insufficient ad transparency tools.

Knowing where ads come from and other information about them is crucial in order to trust the ads themselves. It’s also important to know the target audience, reach, and who paid for them.

One shining example of this has to do with four major elections going on in the year 2024. These are the US, European, Mexican, and Indian elections. Advertisements are meant to sway people in one direction or another, so it’s very likely for people to create advertisements chock-full of misinformation and manipulative rhetoric to artificially push people to vote for one person over the competition.

Knowing more information about the source of ads is a surefire way to know whether or not the sources are trustworthy.

The top tech brands are criticized for having insufficient ad transparency tools

Mozilla and CheckFirst performed extensive research into 11 major tech brands’ ad tools. These companies are AliExpress, Apple App Store, Bing, Booking.com, Alphabet (owns Google and YouTube), LinkedIn, Meta, Pinterest, Snapchat, TikTok, X, and Zalando.

Ad transparency table

Worst of the worst

Of all of the companies, it appears that X’s performance was the worst. In fact, Mozilla’s EU Advocacy Lead, Claire Pershan, said that “X’s transparency tools are an utter disappointment,”. Accessing the ads is complicated, and can only be done through a CSV export file. Its repository has no filtering or sorting capabilities whatsoever, and the content of the ads is not disclosed. People are only given URLs to the ads. This is something that frustrated the researchers, as it shows clear disregard on X’s part.

Better, but still bad

In the report, AliExpress, Bing, Snapchat, and Zalando were in a similar boat. Their ad tools like certain vital data and functionality that would make it easy for people to find information about where the ads come from.

Next up, Alphabet’s, Booking.com’s, and Pinterest’s tools, according to the report, offer the bare minimum data and functionality. So, they fared better, but not by much.

The best… but still bad

Lastly, the Apple App Store’s, LinkedIn’s, Meta’s, and TikTok’s tools seem to be the best off on this list. However, even those tools had some major gaps in the data and functionality that they offered.

Hopefully, governmental bodies will push these companies to offer better tools. While it’s important that we get sufficient ad tools during election years, it’s also important that we get them regardless of what year it is.

Advertisements pervade pretty much every aspect of our internet experience, from gaming to video watching to web surfing. So, we’re constantly inundated with ads. It’s crucial that we have access to tools to let us know where these ads are coming from and whether or not we can trust them.


[ad_2]
Source link

North Korean Hackers Abuse DMARC To Legitimize Their Emails

0
[ad_1]

DMARC is targeted by hackers as this serves to act as a preventative measure against email spoofing and phishing attempts. 

They compromise DMARC (Domain-based Message Authentication Reporting and Conformance) so that they can evade email authentication protocols, consequently enabling them to mimic authentic senders and mislead recipients. 

This way they can put up more conceivable and advantageous phishing campaigns that lead to either making money or stealing data.

Cybersecurity researchers at ProofPoint recently discovered that North Korean hackers are actively abusing the DMARC to legitimize their illicit emails.

DMARC Abuse

Proofpoint tracks the North Korean state-aligned group TA427 (aka Emerald Sleet, APT43, THALLIUM, Kimsuky), which conducts phishing campaigns targeting experts on U.S. and South Korean foreign policy for the Reconnaissance General Bureau. 

Since 2023, TA427 has directly solicited opinions from foreign policy experts on nuclear disarmament, U.S.-ROK policies, and sanctions via innocent conversation-starting emails.

Free Live Webinarfor DIFR/SOC Teams: Securing the Top 3 SME Cyber Attack Vectors - Register Here.

Researchers observed a steady and sometimes increasing stream of this activity.

While TA427 consistently relies on social engineering and rotating email infrastructure, in December 2023, it began abusing lax DMARC policies for persona spoofing and incorporated web beacons for target profiling in February 2024.

Volume of TA427 phishing campaigns (Source – ProofPoint)

TA427 is a skilled social engineering threat actor likely supporting North Korean strategic intelligence collection on U.S. and South Korean foreign policy initiatives. 

By engaging targets over extended periods through rotating aliases and innocent conversations, TA427 builds rapport to solicit opinions and analysis, especially around foreign policy negotiation tactics. 

Leveraging customized, timely lure content and spoofing familiar DPRK researchers, TA427 requests targets share thoughts via email, papers, or articles rather than directly delivering malware or credential harvesting. 

This direct input approach may fulfill TA427’s intelligence requirements while the correspondence insights improve future targeting and connection building for additional engagement.

The goal appears to be augmenting North Korean intelligence to inform negotiation strategies.

Timeline of real-world events based on international press reporting (Source – ProofPoint)

Their lures include invitations to events on North Korean affairs, inviting perspectives on deterrence policies, nuclear programs, and possible conflicts.

It involves moving conversations between email addresses, such as those of individuals being targeted and their workplaces.

TA427 masks itself in a number of ways as think tanks, non-governmental organizations (NGOs), media outlets, educational institutions, and governmental bodies utilize DMARC abuse, typosquatting, and free email spoofing for legitimization

Timeline of real-world events based on international press reporting (Source – ProofPoint)

A different tactic from early February 2024 performs reconnaissance over the victim’s active email as well as the recipient environment through web beacons. 

One of the most frequently seen actors tracked by Proofpoint is TA427 which constantly adapts its modus operandi, infrastructure elements or even avatars to tactically target experts to steal information or gain initial access for intelligence purposes rather than profit maximization.

IoCs

Looking to Safeguard Your Company from Advanced Cyber Threats? Deploy TrustNet to Your Radar ASAP.


[ad_2]
Source link

Phones running Snapdragon 8 Gen 4 may require larger batteries

0
[ad_1]

Smartphone processors are getting more and more power efficient. But the demand for computing power is also increasing at a rapid pace. As SoC manufacturers like Qualcomm and MediaTek are aiming to increase their performance, the power consumption is also increasing even with the latest and more efficient process nodes.

Snapdragon 8 Gen 4 may require larger batteries

Previous rumors hinted at a performance leap for the upcoming Snapdragon 8 Gen 4 flagship chipset. Now the latest news comes from Weibo tipster Digital Chat Station. According to him, Qualcomm may face problems in managing the power efficiency of the Snapdragon 8 Gen 4. As a result, Smartphone manufacturers may opt for even higher battery capacity to compensate for a higher power consumption. But it will also come with certain compromises to the user experience. The Snapdragon 8 Gen 4 could arrive in October during the Snapdragon Summit.

Notably, this upcoming chip utilizes TSMC’s improved 3nm N3E process node. While theoretically, it means lower power consumption than the Snapdragon 8 Gen 3 which is based on TSMC’s 4nm process, we should also consider the change in core clusters and their clock speeds.

Qualcomm’s chief marketing officer, Don McGuire has confirmed that the Snapdragon 8 Gen 4 chipset will use Qualcomm’s Oryon CPU. Rumors suggest that the chipset lacks efficiency cores and features a configuration of “2+6” performance-focused Oryon cores.

For those unfamiliar, the company’s upcoming Snapdragon X Elite chip for Windows-on-Arm also utilizes the Oryon CPU cores. Although he didn’t confirm much about the core cluster of the Snapdragon 8 Gen 4, previous rumors suggest that the company was testing the chipset with a clock speed as high as 4.3 GHz. For context, the Cortex-X 4 super core of last year’s Snapdragon 8 Gen 3 chipset reaches a significantly lower 3.3GHz clock speed. A higher clock speed also means a higher power consumption.

Three phones with 5500 mAh batteries were being tested with the Snapdragon 8 Gen 4

The tipster Digital Char Station notes that three phones were being tested with the Snapdragon 8 Gen 4 to check and manage the performance and power efficiency. Reportedly all three devices boast a bigger 5500 mAh battery. Previously the OnePlus 13 was rumored to be the first flagship to equip the Snapdragon 8 Gen 4.

Since the OnePlus 12 also comes with a 5500 mAh battery, it won’t be a surprise to see the same on its successor. Nonetheless, as the tipster suggests, smartphone manufacturers may opt for high-density batteries with customized core materials for the Snapdragon 8 Gen 4-powered flagships. It should help the flagships remain slimmer.


[ad_2]
Source link

Oracle Releases Critical Patch Update 2024 With The Fix for 372 Vulnerabilities

0
[ad_1]

Oracle has released its April 2024 Critical Patch Update (CPU), addressing 372 security vulnerabilities across multiple Oracle products. This comprehensive update fixes critical flaws that could allow remote code execution, data manipulation, and unauthorized access to systems.

Affected Products and Patches

Oracle strongly recommends that users apply the necessary patches as soon as possible to mitigate the risk of potential attacks. The affected products include:

  • Oracle Database
  • Oracle Fusion Middleware
  • Oracle PeopleSoft
  • Oracle Siebel CRM
  • Oracle Java SE
  • Oracle MySQL
  • Oracle Retail Applications
  • Oracle Financial Services Applications

Users can access the patch updates and detailed information about the vulnerabilities through the Oracle Support port

Free Live Webinarfor DIFR/SOC Teams: Securing the Top 3 SME Cyber Attack Vectors - Register Here.

Key Highlights

  • The April 2024 CPU resolves 372 security vulnerabilities in Oracle products.
  • 34 vulnerabilities are classified as “Critical,” with a CVSS score of 9.8 or higher.
  • The affected products include Oracle Database, Fusion Middleware, PeopleSoft, Siebel CRM, and Java SE.

Critical Vulnerabilities with 9.8 CVSS Score

The update addresses several critical vulnerabilities with a CVSS score of 9.8, indicating the highest level of severity. These include:

CVE-2024-21234 – Oracle WebLogic Server Remote Code Execution Vulnerability

  • Description: Allows remote attackers to execute arbitrary code on vulnerable Oracle WebLogic Server installations.
  • CVSS Score: 9.8 (Critical)
  • Affected Products: Oracle WebLogic Server versions 12.2.1.4 and earlier.
  • Recommendation: Apply the available patch or upgrade to a version that includes the fix.

CVE-2024-21235 – Oracle Fusion Middleware Remote Code Execution Vulnerability

  • Description: Allows remote attackers to execute arbitrary code on vulnerable Oracle Fusion Middleware installations.
  • CVSS Score: 9.8 (Critical)
  • Affected Products: Oracle Fusion Middleware versions 12.2.1.4 and earlier.
  • Recommendation: Apply the available patch or upgrade to a version that includes the fix.

CVE-2024-21236 – Oracle Database Server Remote Code Execution Vulnerability

  • Description: Allows remote attackers to execute arbitrary code on vulnerable Oracle Database Server installations.
  • CVSS Score: 9.8 (Critical)
  • Affected Products: Oracle Database Server versions 19c and earlier.
  • Recommendation: Apply the available patch or upgrade to a version that includes the fix.

Addressing a Diverse Range of Vulnerabilities

The 372 vulnerabilities addressed in this CPU cover a diverse range of security issues, including:

Database Security Enhancements

The update includes fixes for several vulnerabilities in the Oracle Database, including issues related to SQL injection, privilege escalation, and denial-of-service attacks.

Middleware Vulnerability Resolutions

The CPU also addresses vulnerabilities in Oracle’s Fusion Middleware suite, which includes components such as WebLogic Server, Oracle Identity and Access Management, and Oracle SOA Suite.

Application-Specific Patches

The update includes security patches for various Oracle enterprise applications, including Oracle E-Business Suite, PeopleSoft, and JD Edwards EnterpriseOne.

Oracle strongly recommends that its customers apply these security patches as soon as possible to mitigate the risks associated with the identified vulnerabilities. Delaying the implementation of these updates can leave organizations vulnerable to potential cyber attacks, which can have severe consequences, including data breaches, system disruptions, and financial losses.

“We urge our customers to prioritize the deployment of this Critical Patch Update to ensure the continued security and reliability of their Oracle-based systems,” said Ravi Kumar, Oracle’s Chief Security Officer. “By working together to address these vulnerabilities, we can collectively strengthen the overall security posture of the Oracle ecosystem.”

Customers are advised to refer to the Oracle Security Alert Advisory for more information on the specific vulnerabilities addressed and the recommended actions for deployment.

If Are you from SOC and DFIR Teams, Analyse Malware Incidents & get live Access with ANY.RUN -> Start Now for Free.


[ad_2]
Source link

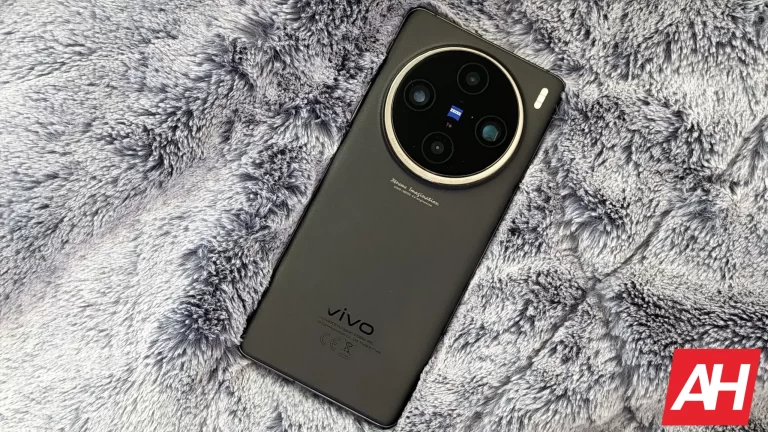
Vivo X100 Ultra could use Samsung’s new 200MP camera

0
[ad_1]

The Vivo X100 Ultra is the company’s upcoming flagship, and it could use Samsung’s new 200MP camera. In fact, this camera is not even official, but it’s expected to launch in the near future.

The Vivo X100 Ultra is expected to use Samsung’s new 200MP camera

This is based on a report by Digital Chat Station, one of the best-known tipsters around. He claims that the Vivo X100 Ultra will use the Samsung S5KHP9 camera, which is a 200MP camera.

The tipster did not go into specifics on it, but the tipster says that “the specifications are quite good”. He also said that this sensor can be used for both primary and secondary cameras. Chances are that Vivo will use it for the periscope telephoto camera, though, or something like that. Well, if it ends up using it at all.

The Vivo X100 Pro is the company’s current flagship and a truly powerful smartphone. The Vivo X100 Ultra is expected to trump it, though. It’s expected to ship with four rear-facing cameras.

This smartphone will be a “professional camera that can make calls”

The company’s Vice President of Product, Huang Tao, recently said that the company’s upcoming smartphone will be a “professional camera that can make calls”. He was almost certainly referring to the Vivo X100 Ultra.

The device is tipped to use the Sony LYT-900 camera sensor for its main camera. A 200-megapixel periscope telephoto camera will likely be included, and Samsung’s S5KHP9 sensor used. The other two cameras will likely be telephoto and ultrawide units. Well, unless Vivo ends up opting for two periscope telephoto cameras like the OPPO Find X7 Ultra.

The Snapdragon 8 Gen 3 will almost certainly fuel the Vivo X100 Ultra. We’re expecting a large AMOLED display with a 120Hz refresh rate, and a large battery too. Blazing fast charging will also be included, as will fast wireless charging.

This handset is expected to launch next month, but Vivo hasn’t really confirmed anything just yet.


[ad_2]
Source link

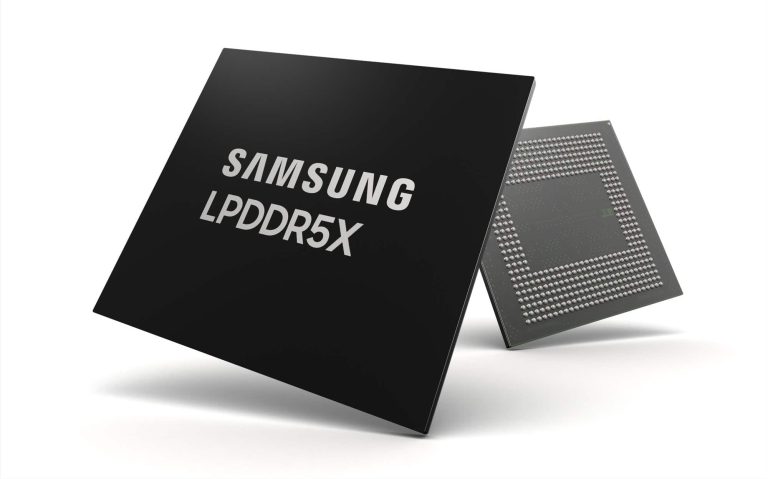
Samsung unveils the fastest LPDDR5X DRAM for AI Applications

0
[ad_1]

Samsung has developed the industry’s fastest LPDDR5X DRAM capable of reaching data transfer speeds of up to 10.7Gbps. Optimized for AI applications, the chip offers improved performance, power efficiency, and higher capacity. It will enter mass production in the second half of 2024.

Samsung makes the industry’s fastest LPDDR5X DRAM

Samsung is the world’s largest memory chip maker. The Korean tech giant has led this industry for years. In October 2022, it achieved a data transfer speed of 8.5Gbps (gigabits per second) with its latest LPDDR5X DRAM (Dynamic Random Access Memory) chip. The company has now improved the speed by 25% to set a new record.

According to Samsung, the new solution is fabricated on a 12nm process node. This ensured a compact size—the fastest LPDDR5X DRAM is also the smallest among existing LPDDRs—for enhanced power efficiency. It makes the chip ideal for on-device AI applications, which require low-power, high-performance LPDDR memory. Samsung used specialized power-saving technologies to achieve 25% higher efficiency than the previous generation.

The new chip incorporates technologies such as optimized power variation. It adjusts power according to workload. Additionally, Samsung expanded low-power mode intervals to extend energy-saving periods. These improvements lower energy usage when processing data, helping extend the battery life of mobile devices. In server applications, a higher power efficiency helps lower the total cost of ownership as energy consumption is less.

On-device AI applications also demand high-capacity memory solutions. To that end, Samsung’s new LPDDR5X DRAM chip offers 30% more capacity, including up to 32GB of single package capacity of mobile DRAM. The Korean firm has tailor-made the new chip for modern use cases. It plans to expand LPDDR DRAM to various device categories beyond mobile phones and continue optimizing its chips for the new era of generative AI.

“As demand for low-power, high-performance memory increases, LPDDR DRAM is expected to expand its applications from mainly mobile to other areas that traditionally require higher performance and reliability such as PCs, accelerators, servers, and automobiles,” said YongCheol Bae, an Executive Vice President at Samsung. “Samsung will continue to innovate and deliver optimized products for the upcoming on-device AI era through close collaboration with customers.”

Mass production begins later this year

Samsung seems to have begun sampling its 10.7Gbps LPDDR5X DRAM with industry partners. The chip will enter mass production following this verification with mobile AP (application processor) and mobile device providers sometime in the second half of the year. It could be commercially available by the end of 2024 or in early 2025, in time for the Galaxy S25 series.


[ad_2]
Source link

Cyberattacks Surge 325% in Philippines Amid South China Sea Standoff

0
[ad_1]

The Philippines faces a surge in cyberattacks as tensions rise in the South China Sea. Hacktivists and misinformation campaigns target government websites, spread fake news, and disrupt critical infrastructure. Learn why the Philippines is a cyberwarfare hotspot and how the country can defend itself.

Resecurity reports a 325% increase in cyberattacks targeting the country in Q1 2024 compared to the same period last year. Cyberattacks involving hacktivist groups and foreign misinformation campaigns have nearly tripled with multiple attacks staged by unknown threat actors in Q2 2024, combining ideological motivations with nation-state-sponsored propaganda. 

The Philippines, located near the South China Sea, is facing tensions due to China’s assertive actions and its role as a Major Non-NATO Ally (MNNA). The island nation’s maritime trade routes and proximity to Taiwan make it a potential staging ground for military operations in a larger conflict, prompting adversaries to disrupt the country’s infrastructure.

Resecurity found numerous hacktivist groups  targeting the Philippines, including the pro-China Mustang Panda, DeathNote Hackers, and Exodus Security. In February, Exodus Security staged targeted DDoS attacks, leaking stolen data from various countries, including the Philippines, and announced partnerships with Cyber Operation Alliance, Robin Cyber Hood, Arab Anonymous, and Sylnet Gang-SG to broaden their activities. 

In addition, local hacking groups, including Philippine Hacking University, Excommunicado, CyberMafia Philippines, Philippine Cyber Alliance, Bisaya Cyber Army, and LizardSquad Philippines, are also using hacking as a form of protest. 

Recently, threat actor “KryptonZambie” claimed to have stolen over 152 gigabytes of Philippine citizen identity card data from unnamed sources whereas the Philippine Department of Science and Technology (DoST), was targeted by a cyberattack likely orchestrated by threat actors involved in a broader misinformation campaign.

It’s noteworthy that KryptonZambie was also responsible for the data breach of the widely-used CutOut.Pro AI Tool, leading to the exposure of personal details of over 20 million users on the infamous cybercrime and hacker forum Breach Forums.

The threat actor has recently claimed responsibility for data breaches at LeadSquared, an Indian software platform, and WeRize, India’s inaugural socially distributed full-stack financial services platform. Allegedly, the stolen data amounts to over 1.3 terabytes collectively.

These groups use hacktivist-related monikers to avoid attribution and create a perception of social conflict online. They also use tactics like website defacement, data breaches, and misinformation campaigns to disrupt essential services and embarrass the government. They may also hijack government or critical infrastructure websites, steal sensitive data, and create public distrust through social media and online forums. 

Cyberattacks in the Philippines have significant implications beyond immediate disruption. They can erode public trust, escalating tensions between the country and China, and disrupt the economy by affecting critical infrastructure.

To counter these threats, the Philippines needs a multifaceted approach. This includes upgrading cybersecurity infrastructure, investing in threat intelligence, and fostering public-private partnerships.

  1. Chinese APT Posing as Cloud Services to Spy on Cambodia
  2. Unsecured Database Leaks 153 GB of Filipino Student, Family Data
  3. Chinese Scammers Exploit Cloned Websites in Vast Gambling Network

[ad_2]
Source link