Verizon offers free home internet for 6 months

0
[ad_1]

In a move to expand internet accessibility, Verizon is offering new customers six months of free home internet service through its Verizon Forward program. This promotion targets qualified low-income residents, aiming to bridge the digital divide.

What does the free internet plan entail?

The free internet offer applies to Verizon’s 5G Home, LTE Home, and Fios 300 Mbps internet plans. This allows new subscribers to choose the option that best suits their needs, whether it’s the blazing-fast speeds of 5G or the reliable connection of Fios fiber optics. Notably, there’s a one-time $99 setup fee for Fios installations, while the other plans come without this charge.

The free service period lasts for six months, kicking in after installation and activation. The discount is then reflected as a credit on the customer’s bill within one or two billing cycles. This is a limited-time offer, with the activation deadline set for September 3rd, 2024.

To qualify for Verizon Forward and its free six-month internet offer, new Verizon internet service customers must meet specific eligibility criteria. This includes having received a Federal Pell Grant within the past year or participated in a qualifying government assistance program in the last 180 days.

While the government’s Affordable Connectivity Program (ACP) ends soon, Verizon assures existing ACP customers their current discounts will continue.

What happens after six months of free home internet?

Following the free six-month period, customers will transition to Verizon’s standard internet plans. Verizon Forward plans typically start at $20 per month, but the exact price will depend on the specific plan you choose and any additional discounts you qualify for.

Overall, Verizon’s free home internet offer is a welcome development for budget-conscious households. With a variety of plans to choose from and the potential to combine the offer with other discounts, Verizon Forward could be a game-changer for those seeking affordable internet access.


[ad_2]
Source link

Meta shuts down Threads in Turkey, here’s what to do

0
[ad_1]

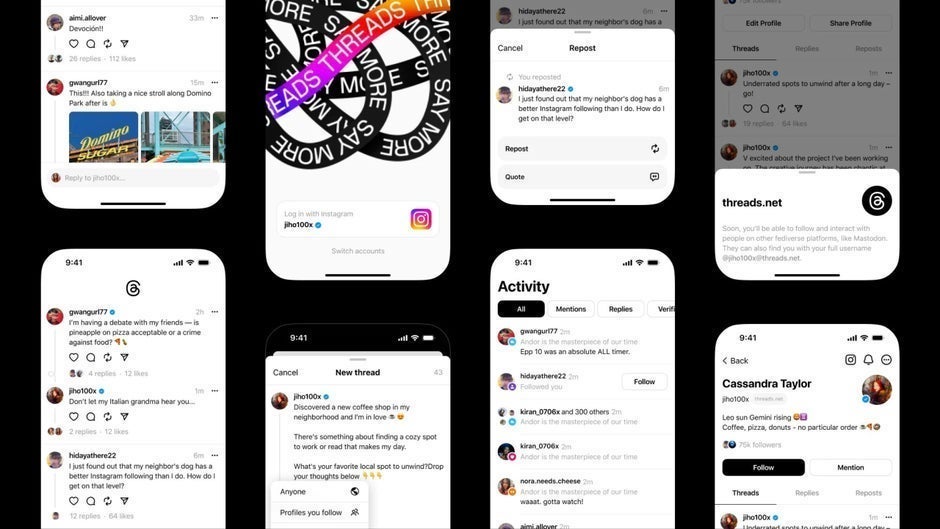
Meta is about to shut down for a period its Threads, the newest social media platform that was supposed to combat Elon Musk’s X/Twitter.

The shut-down will be solely in Turkey, starting April 29 and the reason is that Meta needs to comply with an interim order of the Turkish competition authority (via Reuters).

The company assures in a blog post that Threads’ activity ceasing won’t impact Meta’s other social media platforms like Facebook, Instagram, and WhatsApp in Turkey.

“We are taking steps to minimize any disruption as much as possible”, reads the blog post and adds:

  • Everyone using Threads in Turkey will be notified of this decision within the Threads app before 29 April.
  • People using Threads in Turkey can choose whether to deactivate but not delete their Threads profile, or to delete their profile.
  • If a person chooses to deactivate their profile, then users’ posts and interactions with other people’s posts will become visible again if Threads returns to Turkey.
  • People with deactivated profiles can download their posts and preserve their existing content through our Download Your Information tool at any time.

But why?


The reason for the shut-down is that there’s an ongoing investigation into Meta’s potential abuse of its dominant position in the market, as we’ve reported earlier.This action follows the initiation of a probe in December by Turkey’s competition watchdog into Meta, the parent company of Facebook, for potentially breaching competition laws by linking Instagram with its newer platform, Threads. The watchdog stated that the interim measure will be in effect until a conclusive verdict is reached, since the data obtained and merged through these two apps could “violate competition law and cause irreparable damage” in the market.

On a side note, the Turkish authority fined Meta 4.8 million lira ($148,000) daily as part of a separate investigation over a notification message that the company sends users about the sharing of data.
The notification about data sharing between the company’s Facebook, Instagram, and WhatsApp services did not provide sufficient information and was not transparent enough, it said.

The authority also noted that the manner in which the notification prompts users to consent to data sharing does not adequately mitigate concerns regarding anticompetitive behavior.


[ad_2]
Source link

OpenSSF Warns of Fake Maintainers Targeting JavaScript Projects

0
[ad_1]

The open-source software community, the foundation of modern technology, is facing a growing threat from social engineering attacks. The Open Source Security (OpenSSF) and OpenJS Foundations issued alerts for social engineering takeovers of open-source projects after unknown malicious actors tried to gain control of an OpenJS-hosted project.

The Attack

The OpenJS Foundation Cross Project Council, which hosts popular JavaScript projects used by billions of websites, recently received a series of emails requesting updates to one of its popular JavaScript projects for addressing critical vulnerabilities, with no specifics. The authors wanted OpenJS to designate them as new maintainers although none had privileged access to the project. 

The good news, according to OpenSSF’s blog post, is that the OpenJS Foundation had effective security measures in place, which prevented unauthorized access to the project. The Foundation, demonstrating commendable proactiveness, reported the incident to the Cybersecurity and Infrastructure Security Agency (CISA) and the Department of Homeland Security.

This approach resembles a recent incident involving the XZ Utils project, a popular data compression tool, where a malicious actor named Jia Tan infiltrated it by gaining the trust of its maintainer. The attack involved claims of expertise and malicious code insertion.

Soon after, a backdoor in xz/liblzma was discovered on the oss-security mailing list, affecting xz compression tools and libraries with versions 5.6.0 and 5.6.1. Fortunately, the compromise was discovered before widespread damage occurred.

A Wake-Up Call for Open Source Community

Open-source software can pose threats to any part of the supply chain, but the community’s due diligence and oversight can always ensure quick detection and resolution. 

Open-source maintainers should be cautious against social engineering by implementing measures like Multi-Factor Authentication (MFA), granting contributors the right access, conducting rigorous code reviews, fostering a strong community, and being wary of unsolicited help. Limiting privileges can add additional security, while also being cautious of individuals offering “critical” updates or requesting access.

Open Source Tools = Lucrative Target

Over 30 million open-source projects are hosted on the GitHub platform, highlighting their widespread adoption by individuals and businesses. However, this vast number also makes these projects lucrative targets for cybercriminals.

For instance, a few months ago, a new hacker group called GambleForce was discovered exploiting open-source tools to compromise their targets successfully. This has encouraged initiatives such as bug bounty programs from Google and the EU (European Union) specifically for Open Source tools.

Experts Opinion

Chris Hughes – chief security advisor at open source security company, Endor Labs and Cyber Innovation Fellow at CISA, where he focuses on supply chain security – says these attack attempts are not surprising, but they do raise awareness of bigger OSS security issues.

“It is not surprising at all to hear about these increased social engineering takeover attempts and these will increase with the recent xz utilities example providing insight to malicious actors on how to conduct this attack, in fact we can likely suspect that many of these are already underway and may have already been successful but haven’t been exposed or identified yet. ” Chris warned.

  1. Enhancing Team Coordination With Open-Source Tools
  2. Patched OpenSSH Exploited for IoT, Linux Cryptomining
  3. Dark Web Pedophiles Using Open-Source AI to Generate CSAM
  4. Use of open-source libraries left web apps vulnerable to attacks

[ad_2]
Source link

Guardz Welcomes SentinelOne as Strategic Partner and Investor to Boost Cybersecurity Defenses for SMBs – Latest Hacking News

0
[ad_1]

[Miami, FL – April 16, 2023] – Guardz, the cybersecurity company securing and insuring small and medium-sized businesses, today announced a strategic partnership with SentinelOne, the leader in AI-powered security. The partnership includes an investment from S Ventures, SentinelOne’s venture fund. Guardz and SentinelOne will collaborate on technological advancements and go-to- market strategies, together empowering Managed Service Providers (MSPs) to better serve their small and medium-sized business (SMB) clients in the face of rising and increasingly sophisticated cyber threats.

Today, SMBs are faced with unique cybersecurity challenges amidst the ever-evolving threat landscape. Growing cloud and SaaS adoption combined with constrained budgets and staffing limitations pose significant challenges in managing these businesses’ IT infrastructure. With 43% of cyber-attacks targeting SMBs and only about one-quarter (26%) of SMBs saying they possess cyber insurance, the need for tailored solutions is clear – and SMBs are increasingly turning to MSPs to handle their cybersecurity, reflecting a growing demand for specialized and customer-centric cyber protection.

The AI-powered Guardz platform is purpose-built for MSPs, empowering them to safeguard their SMB customers. Unlike conventional point solutions, Guardz offers a unified AI-driven platform equipped with automated detection and response capabilities to enable MSPs to proactively secure SMBs’ digital assets across users, emails, devices, data and cloud applications. Its cost-effective solution offers full-stack security from a single pane of glass, with easy onboarding. Together, Guardz and SentinelOne will work to advance the Guardz technology and go-to-market strategy. In doing so, they will help make comprehensive, cutting-edge cybersecurity available to businesses of all sizes, ensuring they can defend themselves with the same level of sophistication and efficiency as larger enterprises.

“This strategic partnership marks a significant milestone for Guardz. With SentinelOne’s industry expertise and reach and our track record of providing tailored cybersecurity for MSPs and their customers, we will together ensure a more cyber resilient future for SMBs amid increasingly sophisticated cyber threats,” said Dor Eisner, CEO and Co-Founder of Guardz. “We look forward to continuing to innovate and push the envelope together to ensure the continuity of these businesses and build a safer digital ecosystem across the globe.”

In January of 2024, Guardz raised a $18M Series A led by Glilot+, the early growth fund of Glilot Capital. Since its launch in 2023, the company has experienced rapid growth, having partnered with hundreds of MSPs and securing thousands of the businesses they manage in the US and Europe over the past year.

“Guardz offers a modern approach to protect the underserved SMB market, developing a unified cybersecurity solution that is built for MSPs from day one,” said Ken Marks, Vice President, Worldwide Channels & MSSP at SentinelOne. “This investment underscores SentinelOne’s unwavering commitment to pioneering cybersecurity solutions and amplifies our partner-first philosophy.” 

For more information about Guardz and their partnership with SentinelOne please visit XX. 

About Guardz

Guardz is a holistic cybersecurity solution built to empower MSPs to secure and insure SMEs against ever-evolving threats such as phishing, ransomware attacks, data loss, and user risks by leveraging AI and a multilayered approach. The solution streamlines cybersecurity with its automated detection and response capabilities across users, emails, devices, data, and cloud apps, all from a single pane of glass. By combining robust cybersecurity technology and deep insurance expertise, Guardz ensures that businesses’ security is consistently monitored, managed, and optimized to prevent the next attack and mitigate the risk. Guardz was founded in 2022 by Dor Eisner and Alon Lavi along with a team of cyber and insurance experts who combine innovation, experience, and creativity to create a safer digital world for small businesses.

About SentinelOne 

SentinelOne is a global leader in AI-powered security. SentinelOne’s Singularity™ Platform detects, prevents, and responds to cyber attacks at machine speed, empowering organizations to secure endpoints, cloud workloads, containers, identities, and mobile and network-connected devices with speed, accuracy, and simplicity. Over 11,500 customers, including Fortune 10, Fortune 500, Global 2000 companies, and prominent governments, trust SentinelOne to secure the future. To learn more, visit www.sentinelone.com

Media Contact
Allison Grey
Headline Media
[email protected]

US: +1 323 283 8176

UK: +44 203 807 4482

IL: +972 53 820 2606

[ad_2]
Source link

Giant Tiger breach sees 2.8 million records leaked

0
[ad_1]

Someone has posted a database of over 2.8 million records to a hacker forum, claiming they originated from a March 2024 hack at Canadian retail chain Giant Tiger.

When asked, they posted a small snippet as proof. The download of the full database is practically free for other active members of that forum.

In March, one of Giant Tiger‘s vendors, a company used to manage customer communications and engagement, suffered a cyberattack, which impacted Giant Tiger, as reported by CBC.

The retailer first learned of the security incident on March 4, 2024, and concluded that customer information was involved by March 15, according to an email the company wrote to customers. Giant Tiger also noted that the security incident only impacted one of its vendors and didn’t affect the chain’s store systems or applications, saying that “there is no indication of any misuse of the information.”

On April 12, 2024, BleepingComputer noticed a post titled “Giant Tiger Database – Leaked, Download!” on the hacker forum. The records contain over 2.8 million unique email addresses, names, phone numbers and physical addresses.

When contacted by BleepingComputer, Giant Tiger said:

“We determined that contact information belonging to certain Giant Tiger customers was obtained without authorization. We sent notices to all relevant customers informing them of the situation.”

and:

“No payment information or passwords were involved.”

Depending on customer’s buying behavior, the data leaked in the breach may vary. Loyalty members and those who placed online orders for in-store pickups might have had their names, emails and phone numbers compromised. Some customers, who placed online orders for home delivery, may have had that same information plus their street addresses compromised.

Protecting yourself from a data breach

There are some actions you can take if you are, or suspect you may have been, the victim of a data breach.

  • Check the vendor’s advice. Every breach is different, so check with the vendor to find out what’s happened, and follow any specific advice they offer.
  • Change your password. You can make a stolen password useless to thieves by changing it. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose one for you.
  • Enable two-factor authentication (2FA). If you can, use a FIDO2-compliant hardware key, laptop or phone as your second factor. Some forms of two-factor authentication (2FA) can be phished just as easily as a password. 2FA that relies on a FIDO2 device can’t be phished.
  • Watch out for fake vendors. The thieves may contact you posing as the vendor. Check the vendor website to see if they are contacting victims, and verify any contacts using a different communication channel.
  • Take your time. Phishing attacks often impersonate people or brands you know, and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.
  • Set up identity monitoring. Identity monitoring alerts you if your personal information is found being traded illegally online, and helps you recover after.

Malwarebytes has a new free tool for you to check if your personal data has been exposed online. Submit your email address (it’s best to give the one you most frequently use) to our free Digital Footprint scan and we’ll give you a report and recommendations.


We don’t just report on threats – we help safeguard your entire digital identity

Cybersecurity risks should never spread beyond a headline. Protect your—and your family’s—personal information by using identity protection


[ad_2]
Source link

Samsung dethrones Apple in Q1 2024, as it shipped out more phones

0
[ad_1]

Samsung has managed to dethrone Apple in Q1 2024, as the company managed to ship more phones than the Cupertino giant. This report comes from Canalys, and it’s more or less in line with IDC’s recent report.

Samsung has managed to dethrone Apple by shipping more devices in Q1 2024

Based on this report, Samsung claimed 20% of the smartphone market in Q1 2024. That’s a 2% decline compared to the same period last year. Apple is second-placed with 16%, which is a 5% decline YoY:

Xiaomi managed to grow compared to last year, as the company is now third-placed with 14% of the market. In the same period last year, Xiaomi held 11% of the market.

What’s interesting is that Transsion managed to squeeze its way into the top 4. The owner of both Tecno and Infinix managed to grab 10% of the global smartphone market. That’s a 4% increase compared to Q1 2023.

OPPO has seen a 2% decline, but it’s still in the top 5

OPPO closes out the top 5 list with 8% of the market. The Chinese tech giant held 10% of the market in the same period last year, so this is a 2% decline for OPPO.

As a whole, the global smartphone market grew by 11%. Canalys expects smartphone OEMs to put more focus on emerging markets. Those markets include Latin America and Southeast Asia, first and foremost.

The Galaxy S24 series played a major role for Samsung

The Galaxy S24 series managed to help Samsung retake the smartphone crown. As many of you know, Apple managed to trump Samsung last year. Apple rules the list for the entire year, basically.

It remains to be seen what will happen in the rest of 2024. The iPhone 16 series does not sound too exciting, at least based on rumors and reports. Samsung, on the other hand, still has to launch its foldable offerings this year.

Xiaomi managed to increase its presence thanks mostly to Redmi phones, but the Xiaomi 14 probably had something to do with that too.


[ad_2]
Source link

Samsung secures $6.4 billion grant for US chip investments

0
[ad_1]

The US government will award Samsung up to $6.4 billion in grants for its chip investments in the country. The funding comes under the CHIPS and Science Act and was announced by the Commerce Department on Monday. The Korean firm also plans to claim an investment tax credit from the US Treasury Department. The Biden administration previously announced multi-billion dollar grants for TSMC, Intel, and other chip firms.

Samsung gets $6.4 billion chip grant from the US government

In 2022, the Joe Biden-led US government established the CHIPS and Science Act to boost the domestic chip industry. The act encourages semiconductor companies to expand their production capacity in the country by constructing new manufacturing facilities. In return, they get various grants and subsidies from the government.

All major chip firms, including Samsung, TSMC, and Intel, have since announced new investments in the US. TSMC increased its investment from $40 billion to $65 billion. The Biden administration awarded the Taiwanese company with a grant of $6.6 billion. Intel, which plans to invest more than $100 billion in the US chip industry over the next five years, will get $8.5 billion in subsidies.

Samsung originally planned to invest $17 billion to construct a new chip factory in Taylor, Texas. This was announced in 2021 before the CHIPS and Science Act was passed. Various factors have since added to the cost. The company is now aiming to double the amount to $44 billion. It will construct another chip factory in Taylor and add a research center and a packaging facility to the site.

The Korean tech giant will also expand its existing chip plant in Austin, Texas. According to Commerce Department Secretary Gina Raimondo, Samsung’s investments will boost the country’s chip output for the aerospace, defense, and auto industries. “The proposed project will propel Texas into a state-of-the-art semiconductor ecosystem,” Raimondo said. “It puts us on track to hit our goal of producing 20% of the world’s leading-edge chips in the United States by the end of the decade.”

Samsung will create thousands of jobs in Texas

Raimondo estimates Samsung’s proposed investment projects in Texas to create more than 20,000 jobs. The Korean firm may create at least 17,000 construction jobs and 4,500 manufacturing jobs. Located in Williamson County, the road near Samsung’s semiconductor facility in Taylor was officially renamed “Samsung Highway” in December 2022. It was previously known as Future County Road.

“To meet the expected surge in demand from US customers, for future products like AI chips, our fabs will be equipped for cutting-edge process technologies and help bring security to the U.S. semiconductor supply chain,” said Samsung co-CEO Kyung Kye Hyun. The company expects to begin production in the new factories in 2026. It may start with 4nm chips before expanding into more advanced solutions—3nm and 2nm.


[ad_2]
Source link

Understanding the Implications & Guarding Privacy- Axios Security Group

0
[ad_1]

Washington DC, United States, April 16th, 2024, CyberNewsWire

In a digital age where information is the new currency, the recent global hack has once again highlighted the urgent need for enhanced cybersecurity measures.

The breach was identified as Midnight Blizzard, from the Russian state-sponsored actor known as NOBELIUM. It has affected Millions of individuals and government agencies worldwide, underscoring the far-reaching consequences of cyberattacks and the critical importance of protecting sensitive information.

The Scope of the Breach

The scale of the global hack is staggering. Hackers gained unauthorized access to databases containing a wealth of personal data, including financial records, social security numbers, email addresses, and passwords. The exposed information poses a significant risk of identity theft, financial fraud, and other forms of cybercrime. The breach has impacted individuals across various sectors, including government agencies, businesses, and private citizens, highlighting the pervasive nature of cyber threats.

Implications for Individuals

The fallout from a hack can be devastating for individuals whose data has been compromised. Identity theft, in particular, poses a significant threat. Hackers use stolen information to open fraudulent accounts, make unauthorized purchases, or even commit acts of impersonation. Moreover, the exposure of sensitive personal information can erode trust and privacy, leaving individuals vulnerable to exploitation and manipulation.

Response and Accountability

After the breach, affected organizations must take swift and decisive action to mitigate the damage and restore trust. This includes implementing robust cybersecurity measures, notifying affected individuals, and cooperating with law enforcement agencies to identify and apprehend the perpetrators. Additionally, there must be accountability for those responsible for the breach, whether they are individuals, criminal organizations, or state-sponsored actors. Holding perpetrators accountable prevents future attacks and conveys that protecting personal data is paramount.

Safeguarding Privacy in an Era of Cyber Threats

While the global hack serves as a sobering reminder of the dangers posed by cyberattacks, it also underscores the importance of proactive cybersecurity practices. Individuals and organizations alike must remain vigilant in safeguarding sensitive information and adopting best practices for data protection. This includes using strong, unique passwords, encrypting sensitive data, regularly updating security software, hiring the right cybersecurity company for monitoring, and being cautious when sharing personal information online. Moreover, governments and regulatory bodies must enact robust data protection laws and regulations to hold organizations accountable for safeguarding personal data and provide recourse for individuals affected by breaches.

Hack Aftermath

The exposure of personal data in the recent global hack serves as a wake-up call for individuals, businesses, and governments alike. Cybersecurity must be a top priority in an interconnected world where data is increasingly valuable and vulnerable. That is why Axios Security Group believes that by implementing robust security measures, fostering a culture of accountability, and advocating for more robust data protection laws, can be implemented together to mitigate the risks of cyber threats and safeguard the privacy and security of personal information. Only through collective action can we effectively confront the challenges posed by cybercrime and ensure a safer, more secure digital future.

About Axios Security Group

Axios Security Group is a trusted leader in comprehensive security solutions, offering organizations physical and digital protection. With a dedicated team of experts, Axios created tailored security strategies to safeguard assets, personnel, and data. Its physical security services range from on-site personal security to cutting-edge surveillance technologies, while our cybersecurity experts provide robust digital defenses, including threat detection and incident response. Axios collaborates closely with each client to ensure our solutions align with their unique needs, industry regulations, and budgetary constraints.

Axios Security Group provides a vCSO (Virtual Security Officer) program in addition to physical and cyber security. A vCSO (Virtual Chief Security Officer) is a C-suite-level security expert who enhances your company’s security. They bring strategic vision, devising comprehensive security plans encompassing digital information and physical asset protection. By collaborating closely with your leadership team, a vCSO tailors security solutions to your unique needs, aligning them with your organizational goals and industry regulations. This approach ensures that your organization is well-prepared to navigate the ever-evolving landscape of security challenges, creating a robust, adaptable, and resilient security infrastructure. A vCSO provides all the same security expertise and protections for your organization at a 1/3 of the cost of a full-time CSO (Chief Security Officer.)

Contact us to learn how Axios Security Group can protect one of your most considerable corporate assets.

Contact

Contributor
Robin Carter
News Break
[email protected]
8004853983


[ad_2]
Source link

Pixel Launcher to get new app animations & more in Android 15

0
[ad_1]

Google rolled out the Android 15 beta 1 version for Pixel devices a few days ago. The company will unveil the Android 15 update and its complete features at the Google I/O 2024 event in May. Ahead of the launch, Android Authority has learned that Pixel Launcher will get a handful of new features in Android 15. The launcher will offer enhanced app animations, refined launcher recommendations, and improvements to the “recents screen” user interface.

Pixel Launcher will offer accelerated and enhanced app animation

As per the source, Pixel Launcher will offer a revamped animation for swiping up to get back to the home screen. As you can see in the video below, the new animation appears to be faster and more responsive than Android 14. The new animation in Pixel Launcher in the Android 15 version will better highlight the wallpaper zoom effect. It also appears to be more springier than in the Android 14 version.

Categorized widget recommendations are coming in Pixel Launcher in Android 15

Next, the new version of Pixel Launcher in Android 15 will provide improved widget recommendations. Currently, when you proceed to add a new widget, the launcher presents a random widget recommendation at the top. However, it will be changing in Android 15 as the launcher will show a more comprehensive recommendation system. It will suggest widget recommendations categorized by type like Essentials, Social, Entertainment, and more.

Some other categories in the widget recommendations will include News & magazines, Health & Fitness, Your Chill Zone, Suggested for you, and Weather. Another improvement in the widget section will be the addition of a “+ Add” button in Pixel Launcher in Android 15. It will make it easier to add new widgets on the launcher’s screen. Currently in the Android 14 version, you have to press and hold and then drag the widget to the screen.

Enhancements to the “recents screen” user interface are also in tow

Furthermore, Google will be offering improvements to the “recents screen” user interface in Android 15. There will be changes to the methods to access the menu where the options to open the app info page, split-screen mode, and pause the app are placed. Currently, you have to tap the app icon in the “recent screen” UI to access these options.

However, it will have a pill on the screen containing the app info page, split-screen mode, and pause app buttons in Android 15. Users can easily miss these shortcuts entirely in Android 14. Notably, these options will be easily discoverable in Pixel Launcher in Android 15.

The source suggests that the aforementioned new features are not available in the Android 15 beta 1 release at the moment. However, they are expected to be available in the stable version that’s rolling out later this year.


[ad_2]
Source link

Blackjack Hackers Destroyed 87k Sensors Using ICS Malware

0
[ad_1]

A group of cybercriminals known as “Blackjack” has launched a devastating attack on industrial control systems (ICS) worldwide.

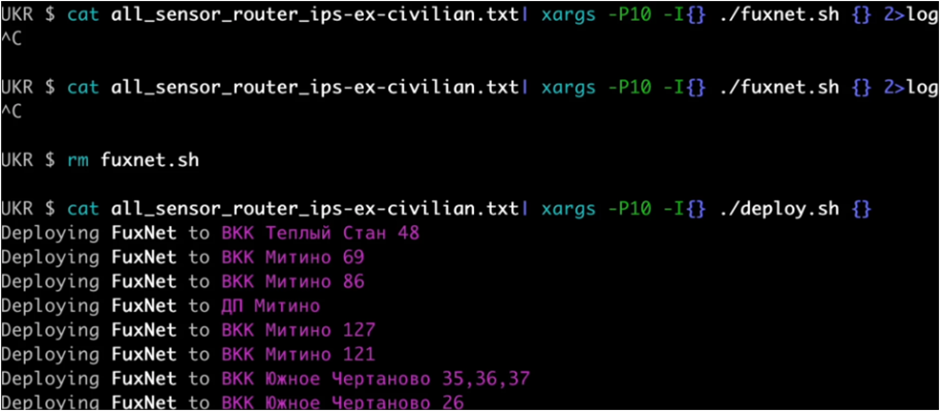
The group’s custom-built malware, dubbed “Fuxnet,” has successfully disabled 87,000 sensors across various critical infrastructure sectors, posing a grave threat to global safety and security.

Fuxnet malware's attack vector
Fuxnet malware’s attack vector

The Fuxnet malware, meticulously analyzed by the cybersecurity firm Claroty’s Team82, is a highly sophisticated and lethal piece of code.

It targets a wide range of ICS devices, including programmable logic controllers (PLCs), human-machine interfaces (HMIs), and other critical components forming the backbone of industrial operations.

Document
Stop Advanced Phishing Attack With AI

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Stopping 99% of phishing attacks missed by other email security solutions. .

Targeted Attacks on Vital Sectors

The Blackjack group has strategically targeted several vital industries, including manufacturing, energy, and water treatment facilities.

A defaced workstation showing a Blackjack image.

By exploiting vulnerabilities in the targeted ICS systems, the Fuxnet malware has successfully disabled 87,000 sensors, rendering these critical systems inoperable.

“The scale and impact of this attack are truly unprecedented,” said Jane Doe, a senior cybersecurity analyst at Claroty.

“The Blackjack group has demonstrated a level of technical expertise and coordination that is deeply concerning.

Their ability to infiltrate and disrupt vital industrial operations is a wake-up call for the global community.”

Devastating Consequences and Ongoing Investigations

The consequences of the Fuxnet attack are far-reaching and potentially destructive.

Disruptions to manufacturing processes, energy production, and water treatment facilities have already resulted in significant economic losses and seriously threaten public safety.

Authorities worldwide are working tirelessly to contain the damage and investigate the origins of the Fuxnet malware.

Law enforcement agencies and cybersecurity experts are collaborating to identify the members of the Blackjack group and their motivations and develop effective countermeasures to prevent similar attacks in the future.

“This is a stark reminder of the critical importance of robust cybersecurity measures in the industrial sector,” said John Doe, a spokesperson for the International Cybersecurity Agency.

“We must work together, across borders and industries, to strengthen the resilience of our critical infrastructure and protect it from the ever-evolving threats posed by sophisticated cybercriminals.

“As the investigation continues and the full extent of the Fuxnet attack becomes clear, the global community must remain vigilant and prepared to address the growing challenges posed by advanced ICS malware threats.

Looking to Safeguard Your Company from Advanced Cyber Threats? Deploy TrustNet to Your Radar ASAP


[ad_2]
Source link