Palo Alto RCE Zero-day Vulnerability Actively Exploited in the Wild

0
[ad_1]

In a recent security bulletin, Palo Alto Networks disclosed a critical vulnerability in its GlobalProtect Gateway, identified as CVE-2024-3400. This flaw, rooted in the PAN-OS operating system, has already been exploited in a limited number of attacks, raising alarms across the cybersecurity community.

CVE-2024-3400 is classified under CWE-77, which pertains to the improper neutralization of special elements used in a command (‘Command Injection‘).

This vulnerability allows attackers to execute arbitrary OS commands on the affected system, posing a significant risk to the network’s integrity and security.

Impact on Users

Exploiting this vulnerability can lead to unauthorized access and control over the affected systems, potentially resulting in data theft, system compromise, and disruption of operations.

Given the critical role of GlobalProtect Gateway in securing remote access to networks, the impact of this vulnerability is particularly concerning for organizations relying on Palo Alto Networks’ solutions for their cybersecurity needs.

Palo Alto Networks has acted swiftly in response to the discovery of CVE-2024-3400, announcing hotfix releases for the affected versions of PAN-OS.

The fixes will be accessible in PAN-OS 10.2.9-h1, PAN-OS 11.0.4-h1, and PAN-OS 11.1.2-h3, and they should be available by April 14.

Organizations are urged to apply these updates as soon as they become available to mitigate the risk associated with this vulnerability.

Additionally, users are advised to review their system logs for any signs of compromise and strengthen their network defenses by following best cybersecurity practices.

Document
Stop Advanced Phishing Attack With AI

Analysis of 1.3M Emails Unveils Hidden Threats Missed by Other Email Security Solutions

Expert Opinions

Cybersecurity experts emphasize the seriousness of CVE-2024-3400, highlighting the potential for widespread disruption and harm if left unaddressed. “This vulnerability underscores the importance of rigorous security protocols and timely updates,” stated one expert, urging organizations to remain vigilant and proactive in their cybersecurity efforts.

In light of the ongoing threat landscape, the discovery of CVE-2024-3400 serves as a stark reminder of the need for constant vigilance and swift action in the face of emerging vulnerabilities.

As Palo Alto Networks works to address this critical issue, organizations worldwide are called to reinforce their defenses and protect their networks against potential exploitation.

Stay tuned for further updates on this developing story and ensure your systems are promptly updated to safeguard against this significant security threat.

Secure your emails in a heartbeat! To find your ideal email security vendor, Take a Free 30-Second Assessment.


[ad_2]
Source link
LastPass Dodges Deepfake Scam: CEO Impersonation Attempt Thwarted

0
[ad_1]
LastPass Dodges Deepfake Scam: CEO Impersonation Attempt Thwarted

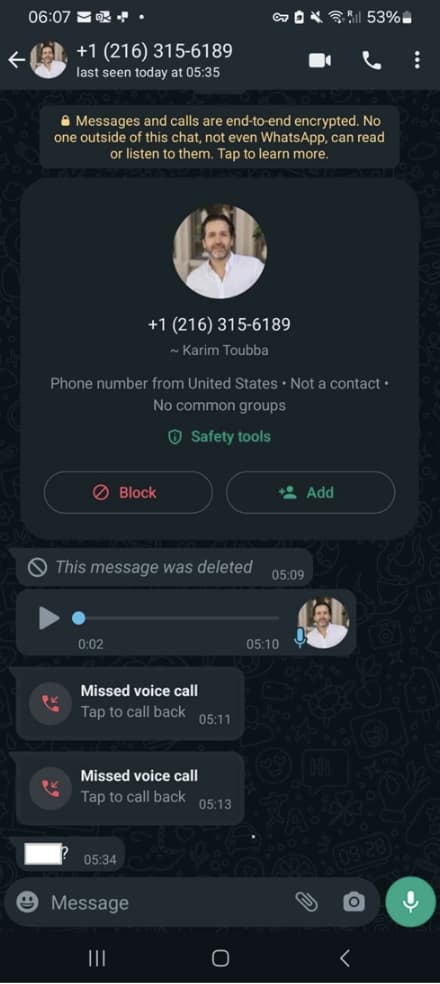
Password management giant LastPass narrowly avoided a potential security breach after a company employee was targeted by a deepfake scam. The incident, detailed in a blog post by LastPass, involved an audio deepfake impersonating CEO Karim Toubba attempting to contact the employee via WhatsApp.

Deepfake technology, which can manipulate audio and video to create realistic forgeries, is increasingly being used by cybercriminals in elaborate social engineering schemes. In this instance, the scammer used a voice-altering program to impersonate Toubba’s voice, likely aiming to create a sense of urgency or trust with the employee.

LastPass Dodges Deepfake Scam: CEO Impersonation Attempt Thwarted
Screenshot of actual WhatsApp scam and attempted contact using deepfake audio as part of LastPass CEO impersonation (Credit: LastPass)

However, not everyone is as fortunate as LastPass. In February 2024, an employee of a multinational company’s Hong Kong branch was tricked into paying out HK$200 million (approximately US$25.6 million) after scammers utilized an AI-generated CFO with deepfake technology.

In another incident reported in August 2022, scammers utilized an AI-generated deepfake hologram of Binance’s chief communications officer, Patrick Hillmann, to deceive users into participating in online meetings and to target Binance clients’ crypto projects.

As for LastPass, the company commended the employee’s vigilance in recognizing the red flags of the situation. The unusual use of WhatsApp, a platform not commonly used for official communication within the company, coupled with the impersonation attempt, encouraged the employee to report the incident to LastPass security. The company confirmed that the attack did not impact its overall security posture.

Toby Lewis, Global Head of Threat Analysis at Darktrace commented on the issue highlighting the risks of Generative-AI, “The prevalence of AI today represents new and additional risks. but arguably, the more considerable risk is the use of generative AI to produce deepfake audio, imagery, and video, which can be released at scale to manipulate and influence the electorate’s thinking.“

“While the use of AI for deepfake generation is now very real, the risk of image and media manipulation is not new, with “photoshop” existing as a verb since the 1990s,” Toby explained. “The challenge now is that AI can be used to lower the skill barrier to entry and speed up production to a higher quality. Defence against AI deepfakes is largely about maintaining a cynical view of material you see, especially online, or spread via social media,“ he advised.

Nevertheless, this attempted scam goes on to show how sophisticated cybercriminals have become in their attacks. On the other hand, LastPass emphasized the importance of employee awareness training in mitigating such attacks. Social engineering tactics often rely on creating a sense of urgency or panic, pressuring victims into making rushed decisions.

The incident also highlights the potential dangers deepfakes pose in the corporate domain. As the technology continues to develop, creating ever-more convincing fakes, companies will need to invest in robust security protocols and employee training to stay ahead of these sophisticated scams.

While deepfake scams targeting businesses are still relatively uncommon, the LastPass incident stresses the growing threat. The company’s decision to publicize the attempt serves as a valuable cautionary tale for other organizations, urging them to heighten awareness and implement preventative measures.

  1. AI Generated Fake Obituary Websites Hit Grieving Users
  2. Deepfakes are Circumventing Facial Recognition Systems
  3. Fake Lockdown Mode Exposes iOS Users to Malware Attacks
  4. Deepfake Attack Hits Russia: Fake Putin Message Broadcasted
  5. QR Code Scam: Fake Voicemails Hit Users, 1000 Attacks in 14 Days

[ad_2]
Source link

April update available for Galaxy S22, S20 FE, Flip 4 & more

0
[ad_1]

Samsung‘s April update is quickly spreading to all eligible models worldwide. The company has just released the latest security patch for the Galaxy S22 series, Galaxy S20 FE, Galaxy Z Flip 4, Galaxy Z Fold 3, and Galaxy A52 in several global markets. Most of these devices have already received the update in the US.

The Galaxy S22 series gets the April update globally

Yesterday, Samsung released the April SMR (Security Maintenance Release) for the US versions of the Galaxy S22, Galaxy S22+, and Galaxy S22 Ultra. The update is now rolling out in Europe. It comes with the firmware build number S90*BXXS8DXD2. Users in other regions such as Latin America, Africa, Australia, and Asia should also soon receive the update.

This new SMR comes without any additional goodies. The 2022 Samsung flagships are picking up 40-odd security fixes and nothing more. They will get AI features and other improvements with the One UI 6.1 update in May. The Korean firm has already confirmed that the Galaxy S22 series will get most of the new AI features found on the Galaxy S24 lineup.

This month’s security patch is also rolling out to the Galaxy S20 FE, which is done getting feature updates. The rollout has begun in Europe. Both 4G and 5G versions of the phone are getting the update. According to SamMobile, the new build numbers are G780GXXS9EXC6 and G781BXXSAHXC6, respectively. A global rollout should follow soon.

The Galaxy Z Flip 4 and Galaxy Z Fold 3, which have already received the April SMR in the US, are also now getting it in other regions. The update for the former is available globally with the build number F721BXXS5EXD1. The latter, meanwhile, is currently only picking up the new security patch in Europe. The new build number for this phone is F926BXXS6GXD1.

Note that the Galaxy Z Fold 4 and Galaxy Z Flip 3 have received this update in several global markets recently. If you haven’t got it wait, fret not. Samsung will gradually cover all units. This applies to other Galaxy devices as well. Since updates are released in batches, some users may receive them later than others. The changelogs mostly remain unchanged.

The Galaxy A52s is also getting the April SMR

The Galaxy A52s is another Samsung phone that recently started picking up the April SMR. This phone had a limited release (didn’t arrive in the US) and the company is currently updating it in Europe. You will get the update with firmware version A528BXXS7FXC8. The device will get One UI 6.1 in May or June, though it is unlikely to get new AI features.


[ad_2]
Source link

Galaxy S22, S21 & others will get One UI 6.1 AI features in May

0
[ad_1]

Samsung‘s new AI features will trickle down to the Galaxy S22, Galaxy S21, flagship tablets, and foldables launched in 2021 and 2022. The confirmation comes from an official community forum moderator. The 2022 lineup will get most of the features but only a handful will make it into the 2021 models. The One UI 6.1 rollout for these devices will begin in May.

Samsung confirms Galaxy AI for the Galaxy S22 and S21 series

According to the Samsung representative, the Galaxy S22 series, Galaxy Z Fold 4, Galaxy Z Flip 4, and Galaxy Tab S8 series will get the same AI features as the Galaxy S23 FE. This means these phones will receive everything except for Instant Slo-mo. This feature lets you instantly slow down any video by pressing and holding the screen when viewing it in Gallery or the built-in video player.

The feature is probably too resource-hungry for the Galaxy S23 FE or older Galaxy flagships to run smoothly. As such, Samsung decided to skip it. The Galaxy S21 series, Galaxy Z Fold 3, and Galaxy Z Flip 3 will also miss out on it—these devices will only get two Galaxy AI features. One of those is Circle to Search, which is essentially a Google feature. It lets you draw around anything on the screen to search for it on Google.

The other is Magic Rewrite, aka Chat Assist. Available via Samsung Keyboard, this tool allows you to quickly rewrite any given text to change its tone and style. 2021 Samsung flagships, including foldables, won’t get Live Translate, Generative Edit, or other AI features introduced with the Galaxy S24 series. It is unclear if the Galaxy S21 FE will get any Galaxy AI features with the One UI 6.1 update.

The rollout begins in early May

Galaxy AI has been grabbing headlines since its debut on the Galaxy S24 series earlier this year. It is even helping drive the sales of the new Samsung flagships. A recent survey showed that 27% of Galaxy S24 buyers picked the phone for AI features. This enabled the Korean behemoth to post healthy smartphone sales figures in the first quarter of 2024.

Samsung is gradually bringing Galaxy AI to older models. The Galaxy S23 series, Galaxy S23 FE, Galaxy Z Fold 5, Galaxy Z Flip 5, and Galaxy Tab S9 series have already picked it up with the One UI 6.1 update. The rollout for other eligible models will begin in early May. 2022 Galaxy flagships will get it first, followed by the 2021 lineup. We will let you know when the update arrives.


[ad_2]
Source link

6-year-old Lighttpd Flaw Impacts Intel And Lenovo Servers

0
[ad_1]

The software supply chain is filled with various challenges, such as untracked security vulnerabilities in open-source components and inconsistent update uptake. 

The lighttpd vulnerability was silently fixed in 2018 without any CVE assignment in a single instance of vulnerability detection.

As a result, critical security patches are often lost on downstream software that relies on these elements.

Consequently, it is very difficult to trace every modification for possible problems without designated security advisories and CVE assignments, which creates gaps in vulnerability management across the supply chain.

Binary cybersecurity researchers recently discovered that Lighttpd, a 6-year-old security flaw, has impacted Intel and Lenovo servers.

6-year-old Lighttpd Flaw

While studying BMC safety, Binarly encountered a heap out-of-bounds read vulnerability (BRLY-2024-002) in the Lighttpd module of a discontinued Intel Server System product. 

The unpatched flaw, which was fixed silently multiple years ago without CVE, would not be addressed as it was no longer under support. 

This complexity and insecurity of firmware and software supply chains are well illustrated by the existence of vulnerabilities in third-party components that are left isolated for years, leading to long-term risks with destructing consequences for different sectors. 

Document
Stop Advanced Phishing Attack With AI

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Stopping 99% of phishing attacks missed by other email security solutions. .

While the expected life cycle reactions make sense, there is an underlying issue regarding ungoverned exposures in the supply chain that needs to be addressed promptly by taking proactive measures.

The finding also shows contradictions in the firmware supply chain, as some of the latest versions contain outdated third-party components that create additional risks for users.

Further research confirmed that Lenovo BMC firmware for HX3710, HX3710-F, and HX2710-E servers was similarly affected by this vulnerability.

Like Intel, their response noted that these servers had become end-of-life, making it difficult to release future security updates.

Coverages (Source – Binarly)

This situation highlights a more general problem of unpatched vulnerabilities in older products caused by the complexity of firmware supply chains and lifecycle management.

The silent fix does not include an advisory or CVE identifier to facilitate patch management processes that further complicate the problem. 

No prompt, significant information on security fixes makes effective handling of firmware and software supply chains impossible. 

Binary assigned identifiers BRLY-2024-002 and BRLY-2024-003 for the affected Intel and Lenovo BMC firmware, while BRLY-2024-004 was given to the vulnerable Lighttpd build.

This indicates that better vulnerability disclosure and coordination are required across the complicated supply chain ecosystem.

Secure your emails in a heartbeat! To find your ideal email security vendor, Take a Free 30-Second Assessment.


[ad_2]
Source link
Google Pixel 8a Leaks in all 4 colors

0
[ad_1]

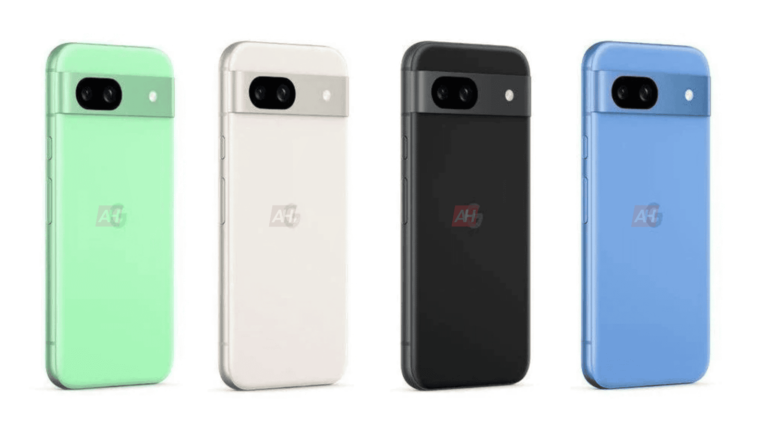
This is the Google Pixel 8a.

The Google Pixel 8a will come in four colors: Obsidian, Mint, Porcelain, and Bay. These are all colors we’ve seen before on previous Pixel models; in fact, the Pixel 6a came in Mint, while the Pixel 8 Pro came in Bay. The Pixel 8a is expected to be announced at Google I/O in May and will be available shortly after that.

It appears that the Pixel 8a will be very close to the design of the Pixel 8 released last fall. Complete with a matte-textured back. We’re expecting the Google Pixel 8a to sport a 6.1-inch FHD+ 90Hz display once again, with the Tensor G3 processor that debuted in the Pixel 8 last fall, along with a 4,500mAh capacity battery. The camera front should include a 64-megapixel main camera and a 13-megapixel ultrawide sensor. Google massively upgraded the cameras on the Pixel 7a last year, so we don’t expect to see any major hardware upgrades for the cameras this year.

Releasing at Google I/O

For the most part, Google’s Pixel A-series has always been released at Google I/O in May, except for the Pixel 4a and 5a, which were a bit delayed due to the pandemic. However, the Pixel 6a and Pixel 7a were released at Google I/O in 2022 and 2023. So, we’re expecting the same thing for the Pixel 8a this time around.

Last year, we did see a price increase for the Pixel 7a, which brought it closer to the price of the Pixel 8. The Pixel 7a’s MSRP is $499; we’d expect the price to either stay the same or go up to $549. In the past few years, Google has been increasing its prices by $50 each year for the a-series. Things are set to take a turn this fall, with Google reportedly launching three Pixel 9 models: Pixel 9, Pixel 9 Pro, and Pixel 9 Pro XL. So it’s possible that Google could keep the Pixel 8a under $500, which would be an incredible value.


[ad_2]
Source link

Huawei’s new MateBook X Pro 2024 ultrabook is ‘lighter than light’

0
[ad_1]

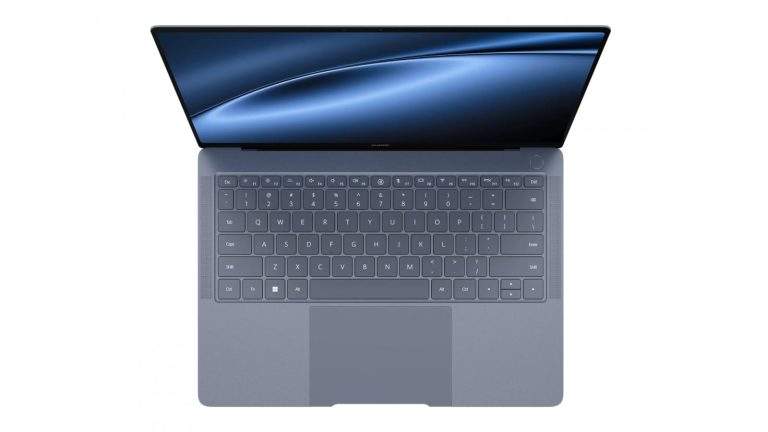
Huawei has announced a new ultrabook in its homeland, the MateBook X Pro 2024. This device was announced in China, though it will likely be coming to way more markets. That was the case with its predecessors, at least.

This is the most powerful laptop Huawei will announce this year. The Matebook X Pro series is the company’s top-end lineup. This laptop has a sizzling price tag, but it also has a lot to offer.

The Huawei MateBook X Pro 2024 is lighter than basically all of its direct competitors

The Huawei MateBook X Pro 2024 weighs only 980 grams (2.16lbs). It is 30% lighter than last year’s model, and that one was quite light. On top of that, the laptop is very thin at only 13.5mm when folded. Huawei’s CEO actually said that the device is “lighter than light”.

This laptop has a 14.2-inch display and weighs 980 grams (2.16lbs). For comparison’s sake, the Apple MacBook Pro has a 14.2-inch display too, and weighs 1.55kg (3.4lbs) to 1.62kg (3.6lbs), depending on the model. Huawei’s new ultrabook is even lighter than a 13-inch MacBook Air which weighs 1.24kg (2.7lbs).

Despite its lightweight and thin design, this ultrabook has a lot to offer. The new Intel Ultra 9 (185H) chip is included, and it’s 60% faster than the Core i7 (1360P) that was included in the previous model.

Its top-end configuration includes the Intel Ultra 9 SoC

Do note that the Intel Ultra 9 chip is included in the top-end model, the more affordable variant comes with the Intel Ultra 7 (155H) chip, which is also quite powerful. Both 16GB RAM and 32GB RAM models are available, and the storage goes from 1 to 2TB, depending on the model.

A 14.2-inch 3120 x 2080 display is included, and it supports touch input up to 10 fingers. It is an OLED display with 120Hz support, and its brightness goes up to 1,000 nits, which is outstanding for a laptop.

140W charging is also supported here, and it goes through a USB-C port

A truly gigantic trackpad is included, and a 70Wh Li-Po battery. The Huawei MateBook X Pro 2024 also supports 140W fast charging. Needless to say, that will get it up and running in no time. You’ll be charging it via a USB-C port.

There are two Thunderbolt 4 ports included as well, while Wi-Fi 6 (ax) and Bluetooth 5.3 are supported. There are four microphones here, and 6 speakers.

The Huawei MateBook X Pro 2024 comes in Inkstone Black, White, and Clear Blue Snow colors. Its pricing starts at CNY11,000 ($1,520), and goes up to CNY15,000 ($2,073) for the top-end model.

As mentioned already, the device will likely be making its way to more markets in the near future.


[ad_2]
Source link

TikTok tests AI ad creators: Are virtual influencers on the horizon?

0
[ad_1]

If you have been following tech news, you have probably noticed that artificial intelligence (AI) is everywhere these days. Tech companies are all about integrating AI into their products and services, and social media platforms are right there with them. Take TikTok, for example – it is testing AI for ads, where AI-powered avatars could soon be making sponsored content for brands.

AI vs human influencers


The tech and business news outlet The Information (via The Verge) says that TikTok is planning to add an AI creator feature that could compete with the ads made by human influencers on the platform.


The idea is for TikTok to develop virtual influencers who can promote and sell products on the platform. These AI avatars would use scripts written by advertisers or sellers from TikTok Shop. However, it is still early days, and the feature isn’t live yet, so it might change as the company tests things out.


The Information’s sources have said that TikTok’s team has tested these AI avatars but found they are not quite ready to go live and haven’t pulled in as many e-commerce sales as human influencers. However, TikTok thinks these AI creators could still work well alongside their human creators.

What does this mean for TikTok’s human creators?


It is still a big question how TikTok will manage the money side of things, like how it will split sponsorship dollars between virtual influencers and real ones or how it will make sure that using AI doesn’t take away opportunities from real people.


If TikTok decides to roll this out, it will need to be careful not to upset its users, especially since it just asked them to help fight off a potential ban by Congress in the US. 

In March 2024, the US House of Representatives passed a bill titled the “Protecting Americans from Foreign Adversary Controlled Applications Act.” This legislation aims to compel ByteDance, the China-based parent company of TikTok, to sell its US operations. If ByteDance fails to comply, TikTok could face a ban from US app stores and might even be completely blocked from operating in the US.

[ad_2]
Source link

DuckDuckGo Launches Privacy Pro: 3-in-1 service With VPN

0
[ad_1]

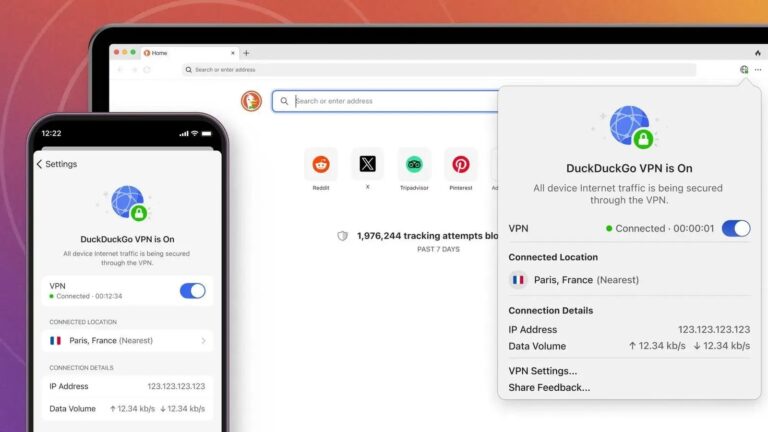
DuckDuckGo has launched Privacy Pro, a new subscription service that promises to enhance user privacy across the web.

This innovative offering combines a VPN service with additional privacy features integrated into DuckDuckGo’s existing privacy-focused browser.

A Closer Look at Privacy Pro’s Features

DuckDuckGo’s Privacy Pro is not just another VPN.

It’s a comprehensive privacy solution that protects users from various online threats.

Here’s what subscribers can expect:

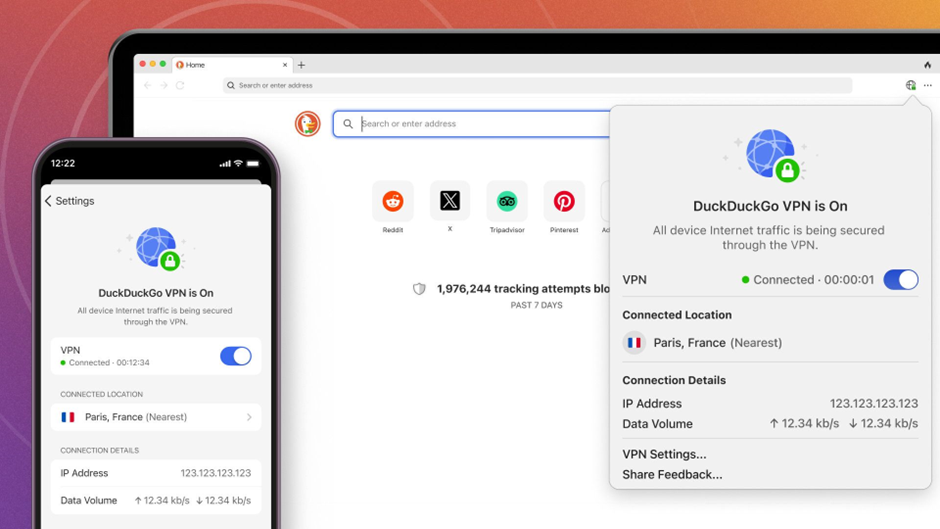
Privacy Pro includes an anonymous VPN service built for speed, security, and simplicity.

Users can secure their internet connection with just one click, effectively hiding their location and device IP address from the sites they visit.

The VPN offers full-device coverage and can be used simultaneously on up to five devices.

In addition to the VPN, Privacy Proactively seeks out and removes users’ details from data broker sites.

Document
Stop Advanced Phishing Attack With AI

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Stopping 99% of phishing attacks missed by other email security solutions. .

These sites are known for storing and selling personal information, which can lead to identity theft and unwanted spam.

By removing this information, Privacy Pro helps users take control of their digital footprint.

Spread Privacy, a leading online privacy website, recently published a blog post announcing the launch of DuckDuckGo’s Privacy Pro. This 3-in-1 service includes a Virtual Private Network (VPN) and other privacy features.

Should the worst happen and a user’s identity be stolen, Privacy Pro provides a dedicated advisor to assist in restoring stolen accounts, recovering financial losses, and correcting credit reports.

This level of support is a significant addition to the service, offering peace of mind in the face of identity theft.

non-logging VPN secures your Internet connection on up to five devices at once

DuckDuckGo has priced Privacy Pro competitively at $9.99 per month or $99.99 per year.

Since obtaining these services separately could cost over $30 per month, Privacy Pro offers significant savings.

It’s a strategic move that positions DuckDuckGo as a cost-effective option in the privacy service market.

Comparison With Other Services

Compared to other privacy services, DuckDuckGo’s Privacy Pro stands out for integrating multiple privacy tools into one platform.

Most VPN services do not offer additional features like personal information removal or identity theft restoration.

Furthermore, DuckDuckGo’s commitment to not logging or storing data that can connect users to their online activity sets it apart from competitors who may not have such stringent privacy policies.

Identity Theft Restoration is standing by to help

Currently, Privacy Pro is available exclusively to residents of the United States.

However, DuckDuckGo has plans to expand the service to other regions in the future. Interested users can sign up at duckduckgo.com/pro.

DuckDuckGo’s unwavering commitment to user privacy is at the core of Privacy Pro.

Privacy Pro is designed with data minimization in mind. It ensures that users’ VPN activities are not logged and cannot be tied to their identities or other activities on DuckDuckGo.

With the launch of Privacy Pro, DuckDuckGo continues to build on its reputation as a privacy-centric company.

By offering a multi-faceted service that goes beyond the capabilities of a standard VPN, DuckDuckGo is providing users with a powerful tool to protect their online privacy.

As digital threats evolve, services like Privacy Pro could become essential for internet users who value privacy and security.

Secure your emails in a heartbeat! To find your ideal email security vendor, Take a Free 30-Second Assessment.


[ad_2]
Source link
5 Best CAPTCHA Plugins for WordPress Websites

0
[ad_1]
5 Best CAPTCHA Plugins for WordPress Websites

As of 2024, the internet hosts over 1.89 billion websites, with approximately 835 million utilizing WordPress as their Content Management System (CMS). This represents about 43.3% of all websites globally.

Not only do these stats represent the expanding reach of the internet, but they also make WordPress a lucrative target for cybercriminals and spammers. While WordPress security tips are widely discussed to keep cybercriminals at bay, spamming is something not every website owner, especially newbies, is familiar with.

In this article, we will discuss five CAPTCHA solutions for WordPress and how a CAPTCHA plugin works.

Here’s an updated list of five effective CAPTCHA plugins for WordPress that can help enhance the security of your website by preventing spam and bot activities:

  1. Captcha Plus: This plugin offers multiple CAPTCHA (Completely Automated Public Turing test to tell Computers and Humans Apart) options, including image-based, math-based, and Google reCAPTCHA. It’s known for its high performance and ease of customization, although it may be a bit overwhelming for beginners.
  2. Google reCAPTCHA: Perhaps the most well-known, this plugin uses advanced technology to differentiate humans from bots without disrupting the user experience. It’s seamlessly integrated into your forms and is supported by major form builders like WPForms.
  3. Really Simple CAPTCHA: As the name suggests, this plugin keeps it straightforward. It’s not as feature-rich as others, but it’s highly effective at blocking spam and is compatible with many form plugins​.
  4. hCaptcha: Offers a robust bot detection system and comes in both free and pro versions. The pro version includes advanced features like custom challenge creation and detailed analytics. It integrates well with a variety of forms and page builders, making it a versatile choice​.
  5. Securimage-WP: Great for those who prioritize a balance between strong security measures and maintaining user-friendliness. It integrates easily with popular form plugins like Contact Form 7 and Gravity Forms​.

Honorable Mention: Akismet Anti-spam: Spam Protection

Although not a CAPTCHA plugin, Akismet Anti-spam is a plugin designed to protect websites, particularly those using WordPress, from spam. Developed by Automattic, the same company behind WordPress.com, Akismet works by filtering out spam comments and form submissions.

It uses automated algorithms and community feedback to identify and block spam, helping keep websites clean and free from unwanted content. Akismet effectively reduces the time and effort needed to moderate spam, allowing website owners to focus on creating and managing content rather than dealing with spammy submissions.

How does a CAPTCHA plugin work

A CAPTCHA plugin works by presenting a challenge to website users to verify that they are human and not automated bots. Typically, this challenge involves completing a task that is easy for humans to do but difficult for bots to replicate, such as identifying distorted text, selecting certain images, or solving a simple puzzle.

The plugin then validates the user’s response, allowing access to the website if the challenge is completed correctly. This helps prevent automated bots from engaging in activities such as spamming forms, creating fake accounts, or launching malicious attacks on the website including DDoS attacks.

  1. New AI tool aims to make CAPTCHA a thing of the past
  2. Facebook captcha wants users to upload a clear photo of them
  3. Proton CAPTCHA: Privacy-First CAPTCHA Defense Against Bots

[ad_2]
Source link