The New York Times to use automated voices to read articles

0
[ad_1]

Right now, the New York Times is in a heated legal battle against Microsoft and OpenAI. While that is the case, that’s not to say that the publication is against AI technology in general. According to a new report, the New York Times is planning on using automated voices to narrate its articles.

The legal battle is still going on, as the New York Times claims that scraping its articles constitutes copyright infringement. Right now, we’re still waiting for the results of this case. The results of the case could have major implications for AI companies going forward.

The New York Times will use automated voices for its articles

The New York Times is one of the biggest publication companies in the U.S., and it’s looking to further extend its appeal to more users. We all have to admit that not everyone wants to sit still and read long articles. This is why the company publishes audio recordings of its articles.

So far, the company actually published more than 2,300 audio recordings in 2023, and this includes podcasts. We can’t argue with the convenience of being able to casually listen to an article while getting ready for work or cleaning rather than reading it.

This is why the company is looking to take this a step further. The New York Times will use automated voices to narrate its articles. Starting this week, people who use the news app and audio app will be able to use voice narration to listen to their articles. This is going to be a gradual rollout because about 10% of its users will gain access initially.

Since these are automated voices, they don’t require a human contributor to read and record the audio. We’re not sure what AI platform the New York Times contacted for this automated voice. However, we do know that narrations will be available in about 75% of articles that the publication has published. That will make a ton of articles more accessible to users. It has plans to expand it to all of its articles at some point.

Limitations

If you’re not logged in to the New York Times website/app or if you have not subscribed, you will not have access to unlimited voices. Also, Android users will not be able to use this feature for the time being. It’s currently only available to people using devices from Apple. However, the company plans to bring this functionality to everyone over time.


[ad_2]
Source link
Google’s new Gemini AI model can now listen directly to audio files

0
[ad_1]

Okay, so for the past year and a half we’ve witnessed the rapid growth of generative AI (is it taking over the world?) and AI models are gaining more and more knowledge as we speak. Now, Android Headlines reports that Google’s new AI model, Gemini 1.5 Pro can now listen to audio.

Gemini can now listen to and understand audio files


Maybe you know but the more data you feed AI, the better it becomes (and freakier, if you’re one of the more skeptical people). At first, the training of the AI models was basically done via text – especially important for chatbots. However, AI models then learned to process image data, and can now be used to reconstruct an image (or create a whole new image upon your prompt). Gemini (which used to be called Bard for those of you who don’t know) has been able to process images, and now it’s growing towards audio format. The version that does that, Gemini 1.5 Pro, is currently in testing. This opens up a world of possibilities – like summaries of a long keynote, conversation, earnings call, lectures, and similar things. You’ll be able to upload the file to Gemini.

Tools to summarize long calls exist. But what they do is transcribe the call first and then summarize it. However, Gemini will listen to the call.

Don’t be quick to get excited though – for now, this won’t be available as a public release. For you to use it, you will need Google’s development platform Vertex AI or if you’re using AI Studio. It’s bound to make it to the public as well, but we don’t know when. All in all, witnessing the growth of AI is seriously exciting. If you’re one of the people who fear it will rule the world one day – don’t be too scared. The way I see it – it’s here to make our lives easier and give us more space to fulfill our potential as intelligent and also intuitive and creative human beings. It will just ensure we won’t have to waste precious time with the boring stuff (like listening to a long earnings call, you know).

[ad_2]
Source link

Poisoning WebDAV+URL+LNK to Deliver Malicious Payloads

0
[ad_1]

WebDAV incidents simulate an offensive attack employing a WebDAV server to distribute malware to a client PC. Attackers store malicious payloads and attract users into downloading and executing them.

It then analyzes a real-world scenario involving AsyncRat/Purelogs malware to understand defense mechanisms using ANY.RUN interactive malware sandbox and discusses methods to detect such attacks, including the creation of detection rules. 

See how ANY.RUN can benefit your organization. You can get free access for your security team.

Successful connection to the attacker’s host

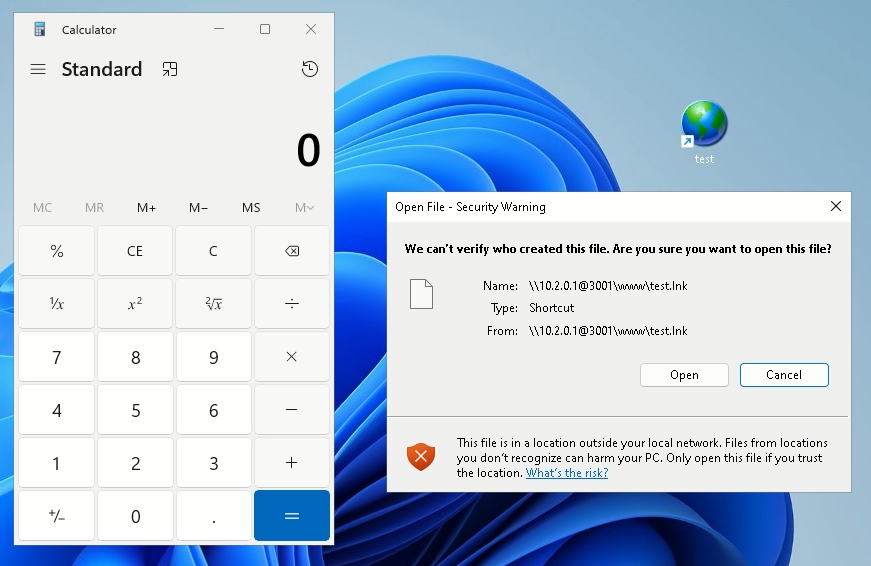
To simulate a client-side WebDAV exploit, they set up a Kali Linux attacker machine and a Windows target machine, then create an LNK shortcut that launches the calculator, upload it to a WebDAV server, and use a URL file as a proxy to initiate a download and execution on the target machine. 

The attack involves establishing network connectivity, creating malicious files, starting a WebDAV server, and executing the URL file on the target, successfully launching the calculator while logging a connection on the server.

Result of executing the command

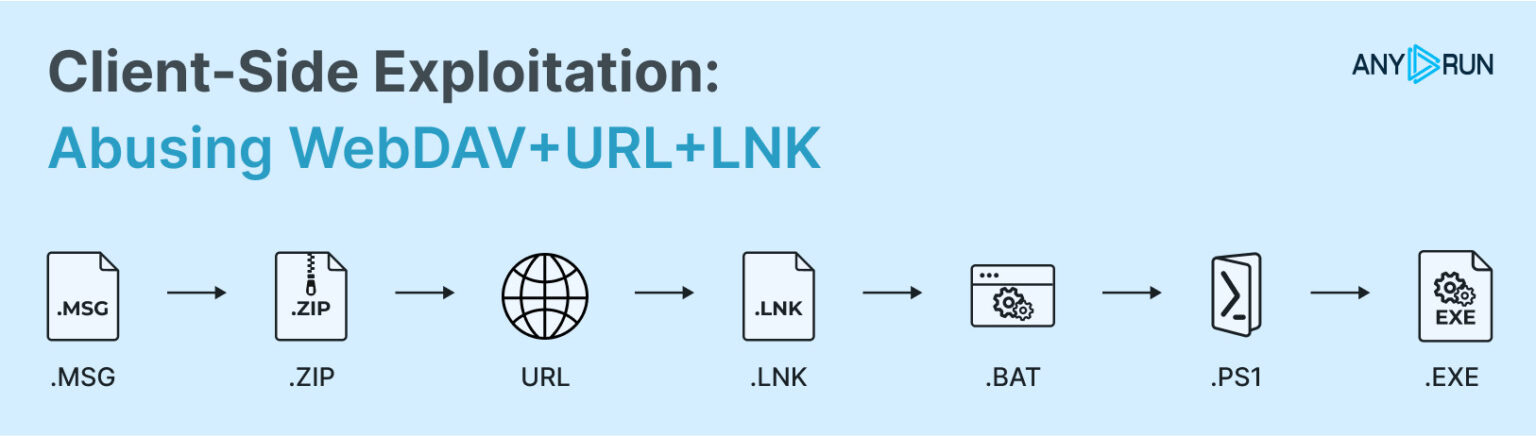
An attacker uses a phishing email to deliver a malicious URL file, which links to a malicious LNK file hosted on a WebDAV server. When the user launches the URL file, the LNK downloads a malicious BAT file and executes it. 

Visualization of the execution chain 

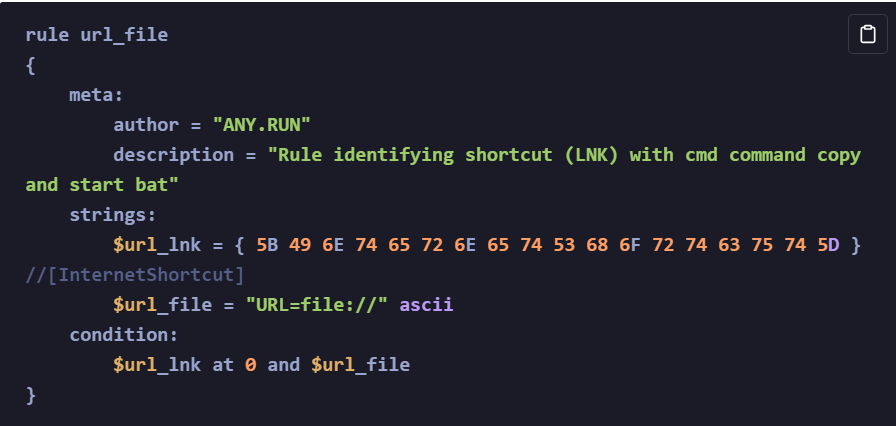
The YARA rule identified the URL file, the YARA hunting rule detected the LNK file on disk, and the SIGMA rule recognized the specific command line used during execution. 

YARA Rule

The Suricata rule identified the network connection to the WebDAV server and by combining these detection methods, ANY.RUN effectively defends against WebDAV exploitation attacks.  

Blocking URL execution 

Defenders can block URL file execution attacks by blocking these files from running within Windows settings. Threat intelligence and analysis of detected artifacts aid in identifying the attack vector. 

Blocking URL Extension

Regular expressions on the command line or URL filters can be used to search for malicious patterns, while Suricata, a network security monitoring tool, can be employed to detect triggered rules that might indicate such attacks.

By implementing these methods, defenders can proactively prevent URL file execution attempts. 

SURICATA Rule

Researchers investigated client-side exploits that use WebDAV servers and LNK files to send malware. They made rules that looked for malicious URL/LNK files, strange activity on the command line, and connections to WebDAV servers.

Disabling LNK/URL execution in Windows settings can also be a preventative measure, which likely uses a threat analysis sandbox like ANY.RUN allows security professionals to analyze malware samples in a controlled environment. 

About ANY.RUN 

ANY.RUN’s flagship product is an interactive malware sandbox that helps security teams efficiently analyze malware. 

Every day, a community of 400,000 analysts and 3000 corporate clients use our cloud-based platform to analyze Windows and Linux threats. 

Integrate ANY.RUN Threat Intelligence in Your Organization: Contact Sales

Key advantages of ANY.RUN for businesses: 

  • Interactive analysis: Analysts can “play with the sample” in a VM to learn more about its behavior. 
  • Fast and easy configuration. Launch VMs with different configurations in a matter of seconds. 
  • Fast detection: Detects malware within roughly 40 seconds of uploading a file. 
  • Cloud-based solution eliminates setup and maintenance costs. 
  • Intuitive interface: Enables even junior SOC analysts to conduct malware analysis. 

Are you from SOC and DFIR Teams? – Analyse Malware Incidents & get live Access with ANY.RUN -> Start Now for Free.


[ad_2]
Source link
DOJ’s blockbuster lawsuit against Apple gets a new judge

0
[ad_1]

Last month, the United States Department of Justice (DOJ) filed a massive lawsuit against Apple, accusing the company of anti-competitive business practices. Expected to be a lengthy courtroom battle spanning several years, the case has been reassigned to a new judge. US District Judge Julien Xavier Neals will preside over the case, a court filing has revealed. It was originally assigned to Judge Michael E. Farbiarz.

A new judge will preside over the DOJ’s lawsuit against Apple

According to a new court filing on Wednesday, April 10, Farbiarz’s recusal in the DOJ’s blockbuster lawsuit against Apple was necessary under the Code of Conduct for United States Judges. His “disqualification is mandatory and cannot be remitted by the parties,” an official order by Chief Judge Renee Marie Bumb states. As such, Neals will preside over this case and all related cases in the future.

The order doesn’t precisely explain why Farbiarz is ineligible to oversee the case. His recusal also seems to have come without any request from either party, Apple or the DOJ. However, the specific rule of the Code of Conduct for United States Judges mentioned in the filing — Canon 3(C)(1)(d) — a judge would be disqualified from overseeing a case if their “impartiality might reasonably be questioned.”

This suggests either Farbiarz or someone he is related to, like a family member, has a close connection or financial tie with this case. Neals seemingly has no potential conflict of interest over the matter. As such, he replaces Farbiarz as the judge of this blockbuster case. As Reuters noted, US President Joe Biden nominated both judges to the US District Court. Neals has served since 2021, while Farbiarz has served since last year.

The hearing will take place from a US District Court in New Jersey

Filed on March 21, the DOJ’s blockbuster lawsuit against Apple targets many products and services. The government agency has pointed out flaws in almost every business the company does. The complaint highlights anti-competitive business practices everywhere, from iPhones and Apple Watches to CarPlay, digital keys, and more. It also blames Apple for the failures of Amazon Fire Phone and Microsoft Windows Phone.

Unsurprisingly, Apple disagrees. It said the lawsuit is “wrong on the facts and the law” and threatens the principles that set its products apart in fiercely competitive markets. The company added that the lawsuit could affect its ability to create the kind of technology it offers to consumers. This case has all the ingredients to become a lengthy courtroom battle. The hearing will take place from a US District Court in New Jersey.


[ad_2]
Source link
Bytedance’s earnings leap 60%, TikTok’s divestiture could get a reprieve

0
[ad_1]

2023 was a very good year for TikTok’s parent company, ByteDance, which saw its profit jump roughly 60%. The company’s earnings hit more than $40 billion last year, from about $25 billion in 2022.

2024 – now that’s a challenging year for TikTok! On March 13, by a stunningly huge margin, the House passed a bill that could ban TikTok in the U.S.

The goal is ByteDance to sell its interests in the viral short video app, or face a ban in the US. If everything goes to plan (the bill passes the Senate and Joe Biden signs it), ByteDance will have a 165-day deadline to divest from TikTok. Should it not pass the control of TikTok to an American-based company, US app stores (like Apple’s, Google’s and Samsung’s) would be prohibited from offering TikTok in the country.Now, Maria Cantwell, Chair of the U.S. Senate Commerce Committee, says that lawmakers could extend to one year the proposed deadline to force TikTok’s parent company to divest (via Reuters).

According to her, the idea of extending the deadline to one year is okay:


The longer deadline would put any potential TikTok ban well into 2025 and beyond the November presidential election. On Monday, Cantwell told reporters she will meet with Senate Democratic Leader Chuck Schumer and Senate Intelligence Committee chair Mark Warner and “then we will have a game plan on how to proceed.”

On Wednesday, Cantwell said it was still “possible” the Senate could take up the House bill but she reiterated that senators want to make the bill stronger and put it on a better legal footing. She noted that attempts by former President Donald Trump’s administration and the state of Montana failed to ban TikTok.

The plan to take on Instagram


Meanwhile, TikTok sticks to the plan to take on Instagram with a new app for sharing photos. It’s going to launch in the not so distant future, and it’d be called Notes, allowing users to share photos much like Instagram.

Judging by teasers, so far TikTok’s Notes seems to offer Polaroid-looking posts featuring a still photo and caption.

“Notes”? Well, it’s hard not to be salty, but… this is as an unimpressive app name as it gets. TikTok should try better, in my personal opinion.


[ad_2]
Source link
Fortra For Windows Vulnerability Let Attackers Escalate Privilege

0
[ad_1]

Fortra’s Robot Schedule Enterprise Agent permits a low-privileged user to elevate privileges to the local system level. 

The problem arises from the agent’s failure to adequately secure its service executable, which an attacker can exploit by swapping out the executable for a malicious one.

As a result, the malicious code will run with elevated privileges when the service restarts, allowing unauthorized access to the system.

In versions of Fortra’s Robot Schedule Enterprise Agent for Windows prior to version 3.04, there is a vulnerability known as CVE-2024-0259 that allows a low-privileged user to overwrite the service executable with their own malicious code and also allows for enhanced privileges. 

It is also crucial since it gives the attacker considerable control over the system.

Upon service restart, the overwritten executable executes with local system privileges, giving the attacker escalated privileges on the system.

Secure your emails in a heartbeat! To find your ideal email security vendor, Take a Free 30-Second Assessment.

Privilege Escalation Vulnerability

An attacker with low privileges can exploit the vulnerability to gain complete control over the system. 

The agent’s service executable is vulnerable to overwriting, which is the source of the vulnerability.

An attacker can deceive the system into executing their code with the highest level of privileges (local system) when the service restarts by substituting a malicious executable for the original one, giving the attacker full access to all of the system’s resources. 

Details of the Vulnerabilities

In Windows versions before 3.04, Fortra’s Robot Schedule Enterprise Agent is susceptible to privilege escalation. This vulnerability enables a user with low privileges to replace the service executable with malicious code. 

When the service restarts, the overwritten program runs with local system privileges, giving the attacker elevated access to the compromised system.

This vulnerability, which falls under CWE-276: Incorrect Default Permissions, underscores the significance of establishing suitable access controls for executables. 

Fortra’s Robot Schedule Enterprise Agent for Windows versions before 3.04 was found to have a critical privilege escalation vulnerability (CVE-2024-0259) on December 7th, 2023. 

The vulnerability has a high exploitability and potential impact, earning it a CVSSv3.1 score of 7.3.

An attacker with low privileges could use it to overwrite a legitimate service executable and then run arbitrary code with system privileges. 

Fortra released version 3.04 on March 20th, 2024, which addresses this vulnerability.

To mitigate the risk, system administrators should update all vulnerable agents to version 3.04 or higher as soon as possible. 

Are you from SOC and DFIR Teams? – Analyse Malware Incidents & get live Access with ANY.RUN -> Start Now for Free 


[ad_2]
Source link
New Harry Potter smartphone just got announced by Xiaomi

0
[ad_1]

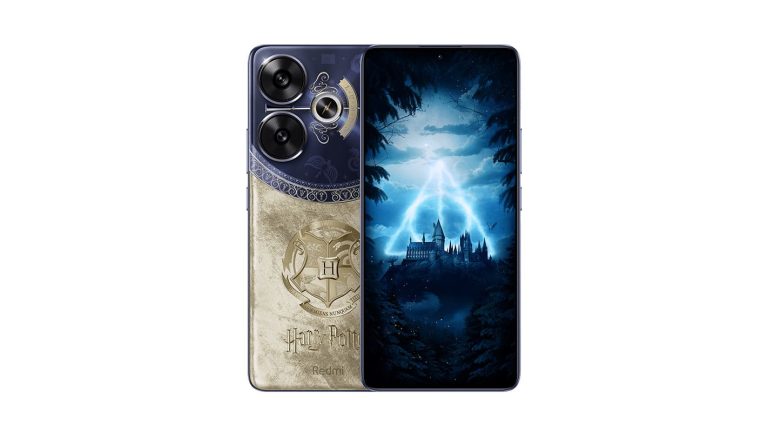
Xiaomi has announced yet another Redmi smartphone, the Redmi Turbo 3, which comes in a Harry Potter variant too. More on the Harry Potter model later on. This handset has been rumored lately, and it has been made official in the company’s homeland.

The Redmi Turbo 3 come with a flat display, two rear cameras & thin bezels

The Redmi Turbo 3 is made out of metal and glass, and it boasts a flat display with thin bezels and a centered display camera hole. There are two cameras on its back, and they’re located in the top-left corner.

The phone’s sides are flat, with chamfered edges. Its cameras on the back do protrude a bit, and the Redmi logo sits in the bottom-left corner of the phone’s back side.

There is a 6.7-inch 2712 x 1220 OLED display included on this phone. It offers a 120Hz refresh rate, and a 480Hz touch sampling rate. The brightness goes up to 2,499 nits at its peak. HDR10+ is also supported, as is Dolby Vision.

The Snapdragon 8s Gen 3 fuels this handset

The Snapdragon 8s Gen 3 fuels this smartphone. The Redmi Turbo 3 got announced in both 12GB and 16GB LPDDR5X RAM variants. You can also choose between 256GB, 512GB, and 1TB UFS 4.0 flash storage options.

There are two SIM card slots available here, both of which accept nano SIM cards. Xiaomi’s HyperOS comes pre-installed on top of Android, and the phone is IP64 certified (splash resistant).

A 50-megapixel main camera (Sony’s LYT-600 sensor, f/1.59 aperture, OIS) is backed by an 8-megapixel ultrawide camera (f/2.2 aperture, Sony IMX355 sensor). On the front, you’ll find a 20-megapixel OmniVision unit.

The phone has an infrared sensor at the top, and an in-display fingerprint scanner too (optical). A 5,000mAh battery is also a part of the package. The phone supports 90W wired charging, and a charger is included in the package.

A Harry Potter variant of the Xiaomi Redmi Turbo 3 includes added goodies in the box

Xiaomi also announced a Harry Potter variant of this smartphone. The full name is the Redmi Turbo 3 Harry Potter Limited Edition. You can check out that model below this paragraph. Xiaomi says that this variant is inspired by the ‘Seven Horcruxes’. In the second picture, you can see what sits inside the package, as there are a number of goodies included.


[ad_2]
Source link

The Google Maps custom share sheet is replaced by the native Android 14 version

0
[ad_1]

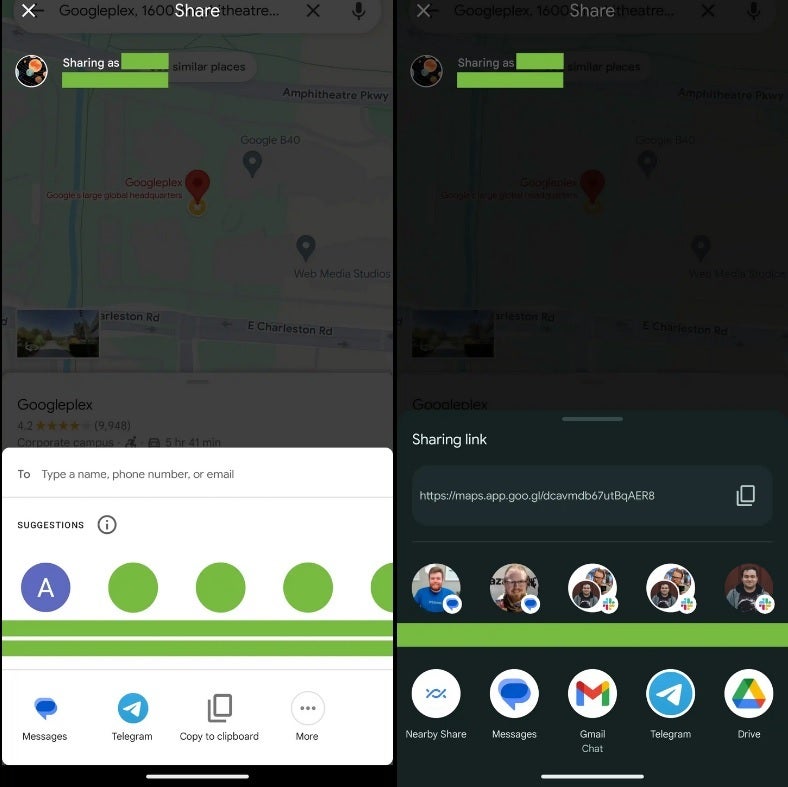
Now Google Maps, that Swiss Army Knife of an app for global travelers, has become the latest Google app to swap its custom share sheet with the native Android share sheet. The old custom version of the Google Maps share sheet had a space to type in the name or phone number of the person you wanted to share something with and icons on the bottom allowed you to share with someone that you speak with on Google Messages or Telegram. You could also add what you wanted to add to your clipboard or see what was in the three-dot “More” icon.

The new Google Maps share sheet includes a sharing link and one-row containing images of people that the user shares with the most. Those who receive shared images over social media will have a small icon attached to their photo showing the social media platform associated with that person. In one example shared by 9to5Google, we can see that some of these recipients are getting these images through Google Messages while others receive shared images over Slack.
The row directly below that one includes icons of apps that the user shares to the most. In this example, we can see that the user favors Nearby Share, Google Messages, Gmail, Telegram, and Drive. The new Google Maps share sheet has yet to appear on my Pixel 6 Pro running Google Maps version 11.124.0101. The phone is running Android 14 QPR3 Beta 2.1. Still, it’s possible that you have the new version. Check it out by sharing something from Google Maps.

[ad_2]
Source link

Microsoft’s April 2024 Patch Tuesday includes two actively exploited zero-day vulnerabilities

0
[ad_1]

The April 2024 Patch Tuesday update includes patches for 149 Microsoft vulnerabilities and republishes 6 non-Microsoft CVEs. Three of those 149 vulnerabilities are listed as critical, and one is listed as actively exploited by Microsoft. Another vulnerability is claimed to be a zero-day by researchers that have found it to be used in the wild.

Let’s first have a look at the two zero-days. The Common Vulnerabilities and Exposures (CVE) database lists publicly disclosed computer security flaws. The CVEs for these two vulnerabilities are:

CVE-2024-26234 (CVSS score 6.7 out of 10): a proxy driver spoofing vulnerability that Microsoft listed as “Exploitation detected” hours after it initially listed it as non-exploited.

In fact, the patch is a revocation of a Microsoft Windows Hardware Compatibility Publisher signature that was used to sign a file which contained a backdoor using an embedded proxy server to monitor and intercept network traffic on an infected Windows machine. Apparently, the software, designed to remote-control phones, was used to make them act like online bots, collectively liking posts, following people on social media, and posting comments.

CVE-2024-29988 (CVSS score 8.8 out of 10): a SmartScreen prompt security feature bypass vulnerability. Microsoft still has this listed as “Exploitation More Likely” and acknowledges the fact that functional exploit code is available. Which means that the exploit code works in most situations where the vulnerability exists.

One reason for the contradiction could be that the exploitation requires some form of user interaction. It requires an attacker to get the victim to click on a link or open a file. If the victim falls for that, the bug allows the attacker to bypass the SmartScreen security feature in Windows that’s supposed to alert users to any untrusted websites or other threats.

Researchers said that attackers are using the weakness to send targets exploits in a zipped file which bypasses the Mark of the Web (MotW) warnings, a warning message users should see when trying to open a file downloaded from the internet.

The exploit for the vulnerability was called “trivial” and “embarrassingly easy” by the researchers that wrote about it.

A few applications that deserve some of your attention if you’re using them are SQL Server (38 vulnerabilities), and Windows Remote Access Connection Manager (9).

Other vendors

Other vendors have synchronized their periodic updates with Microsoft. Here are few major ones that you may find in your environment.

The Android Security Bulletin for April 2024 contains details of security vulnerabilities for patch level 2024-04-05 or later.

Google also updated Chrome to patch a zero-day vulnerability.

SAP has released its April 2024 Patch Day updates.


We don’t just report on vulnerabilities—we identify them, and prioritize action.

Cybersecurity risks should never spread beyond a headline. Keep vulnerabilities in tow by using ThreatDown Vulnerability and Patch Management.


[ad_2]
Source link

Senator Wyden proposes Teams and Slack to work together (and encrypted)

0
[ad_1]

That’s what the Secure and Interoperable Government Collaboration Technology Act draft, proposed by Senator Ron Wyden, reads.

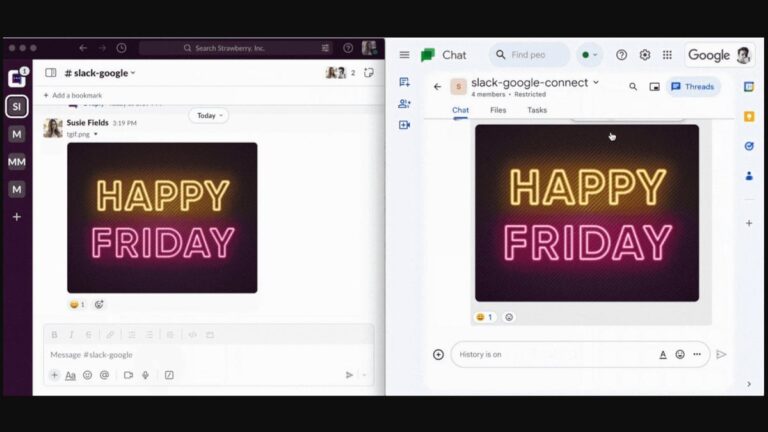
In other words, Senator Wyden wants to see the popular platforms in an “interoperability” mode.

Interoperability stands for “the ability to work together with other systems or pieces of equipment”, as put by the Cambridge Dictionary. Applied to the mobile tech world, that means it enables cross-platform communication and data exchange between two different apps.

In even simpler terms, interoperability is when Person 1 (a Facebook Messenger user) texts Person 2 (a Telegram user) directly. There’s no need for Person 1 to download and use Person 2’s app of choice (in this example – Telegram).

More about the bill


As reported by The Verge, the newly-introduced idea is aimed at improving how the federal government uses technology for meetings and messages. Senator Wyden’s proposal suggests that all communication tools the government uses, like video calls and messaging apps (from different companies), should work together seamlessly. Apart from allowing users to interconnect between apps easily, under the Act these tools would have to meet strict security measures, including end-to-end encryption, to keep conversations private and safe from unwanted spying.

While the proposed idea would only apply to government tools for now, it might encourage similar changes in the wider tech industry, making it easier for everyone to connect regardless of the app they use.

To make this happen, the proposal instructs the General Services Administration (GSA) to list important features needed for government work, like video calls, messaging, sharing files, scheduling, and editing documents together in real time.

The National Institute of Standards and Technology (NIST) would then set up rules to ensure these tools can work together, focusing on strong encryption to protect the data and making sure these systems keep proper records as required by law.

Companies making these tech tools would have four years to update their products to meet these new standards if they want to keep selling to the government.

Additionally, the proposal calls for regular check-ups on the tech used by the government to suggest any needed updates and for the Department of Homeland Security to conduct security reviews on these tools.

This effort comes after concerns about the risks of relying too heavily on single tech vendors, highlighted by a security mishap involving Microsoft that could have been prevented. Senator Wyden argues that it’s time to reduce the reliance on big tech firms by encouraging competition and setting higher security standards.

This move is supported by various groups advocating for digital rights and secure communication technologies.


[ad_2]
Source link