Google’s graveyard keeps growing, Google Podcasts is the latest victim

0
[ad_1]

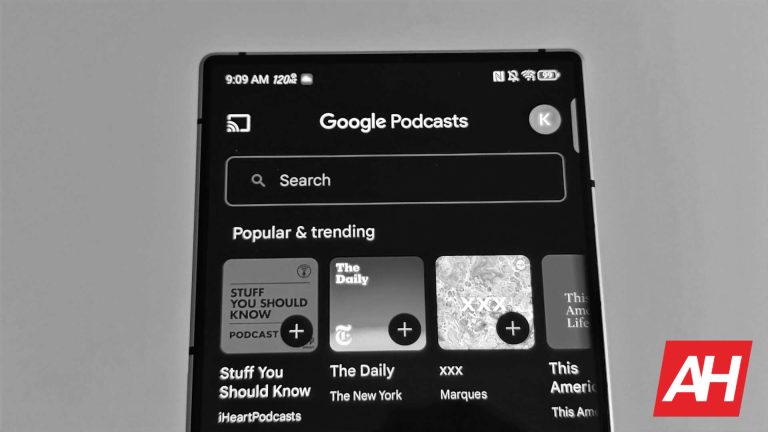
Google’s graveyard keeps growing, as Google Podcasts becomes the company’s latest victim. The application is going away today, April 2. At the time of writing this article, it was still around, but it’ll be gone by the end of the day.

Google Podcasts is the latest app/service to join Google’s graveyard

If you still didn’t grab your data, don’t fret, as you have until July to do so. Google granted its users until then to export any subscriptions they may have on the service. We presume that the vast majority of users already switched to other podcasting services/apps.

Why? Well, we knew that Google Podcasts is going away since September last year. So users had plenty of time to think about where will they switch to. Needless to say, the news regarding the shutdown of the app managed to ruffle some feathers.

Google Podcasts was the company’s third podcasting service

What’s even more interesting is that Google Podcasts is the third podcasting service Google launched. It follows Google Listen (2009-2012) and Google Play Music Podcasts (2016-2020).

Why is Google killing off Google Podcasts? Well, Google wants to pin podcasting under the YouTube umbrella. So, get ready for the podcasting app number 4, YouTube Podcasts.

AH Google Podcasts 2024 image 3

In case you were wondering, Google Podcasts has been around for 8 years. It had the longest time span of any podcasting service Google released thus far, by far. Some people really liked that app, but not many enough to convince Google to leave it alone, apparently.

Google Podcasts came to life in a rather odd way, though. It started off as an embedded player within Google Search results, basically. It worked on google.com and Android’s search app. Later on threw a proper app to the table.

It joins a long list of services Google killed off over time

Either way, Google Podcasts joins a long list of apps/services Google killed off over the years. People are quite used to it by now, as Google has become well-known for it.

Many people still can’t get over the fact Inbox got killed off by Google, and the same goes for Google+, some users really lowed that social media network. Those are just some examples, the list is really, really long.


[ad_2]
Source link
More smartphones will get 5.5G support soon

0
[ad_1]

It was announced quite recently that the OPPO Find X7 Ultra has 5.5G support. The OPPO Find X7 was said to follow soon, and now more smartphones are set to get 5.5G support.

More smartphones will get 5.5G support very soon

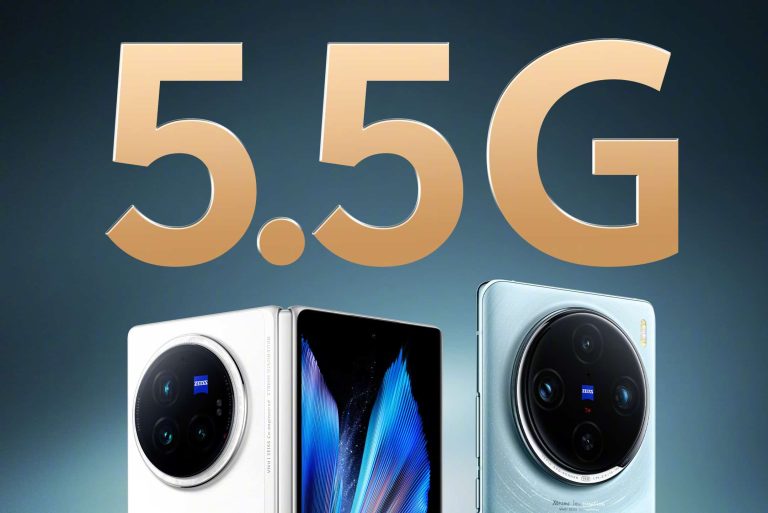
The devices in question come from Vivo, OPPO’s sister company. The Vivo X Fold 3 series will get 5.5G support, and so will the Vivo X100 series. The company says that the support will come in the form of an OTA (Over-The-Air) update.

Vivo X100 Pro 5 5G image 1

On top of that, the IQOO 12 series and iQOO Neo 9 series phone will also get the support for 5.5G. That’s not surprising as iQOO is basically Vivo’s sub-brand, so… there you have it.

5.5G stands for 5G-Advanced, in case you’re wondering. China Mobile is the first carrier to officially offer support for 5.5G. 5G-Advanced is rated at up to 10 Gbps downlink, and 1 Gbps uplink speeds.

China Mobile aims to offer 5.5G in over 300 cities by the end of the year

China Mobile mentioned some other benefits too. The carrier mentioned millisecond latency and improved network stability. 5.5G is currently rather limited in China, but China Mobile intends to expand it to over 300 cities by the end of the year.

5.5G will be covering huge metropolitan areas such as Beijing, Shanghai, and Guangzhou by the end of 2024, if everything goes according to plan. China Mobile is still the only carrier to offer 5.5G support.

We’re expecting to see more carriers join the fold, though it remains to be seen when will that happen. It will also be interesting to see how long will it take other companies to catch up.

Needless to say, 5.5G aka 5G-Advanced is basically a checkpoint on the way to 6G. We won’t be seeing 6G anytime soon, so 5.5G is the best we’ve got until that happens.


[ad_2]
Source link

YouTube Music will now be giving you a recap of new features once a quarter

0
[ad_1]

YouTube Music is usually one of the apps that gets updated quite often and we are used to getting info about the new additions every two months. However, now Android Headlines reports that this is going to change with the app moving to quarterly feature recaps.

YouTube Music will now be getting quarterly feature recaps instead of on a bi-monthly basis


Previously, YouTube Music had a bi-monthly feature recap schedule. Basically, that means that every two months, we would get a recap of the new features added to YouTube Music. Now the recaps will be available once a quarter. However, this doesn’t mean there won’t be as many new features as what we’ve been used to.

Alongside this announcement, YouTube provided a recap of the past couple of months. First off, you now have a little moving equalizer animation playing when you enjoy music. It will move to the beat of your music and will look just like an actual equalizer.

YouTube Music also recently got a new Samples shelf, which provides TikTok-style portrait slices of music videos. These are great for discovering new music and music videos.

Additionally, YouTube Music has gotten a revamp on the Now Playing screen, trying to find the best look. The buttons have been moved around and the overall look and feel have been changed in the past few months.

On top of all that, with Google recently saying goodbye to the Google Podcast app, maybe more people will be moving to YouTube Music to enjoy their podcasts over there. All in all, YouTube Music has even more reasons now to focus on improving the experience. So regular updates will remain a thing, despite the fact that you won’t get recaps of them as often as you’re probably used to.


[ad_2]
Source link

xz-utils Backdoor Affects Kali Linux Installations

0
[ad_1]

A critical vulnerability has been identified in the xz-utils package, versions 5.6.0 to 5.6.1, which harbors a backdoor capable of compromising system security.

This vulnerability, cataloged under CVE-2024-3094, poses a significant threat to the Linux ecosystem, including the widely used Kali Linux distribution, known for its robust security and penetration testing tools suite.

The Vulnerability: CVE-2024-3094

The backdoor discovered in the specified versions of xz-utils could allow an attacker to bypass sshd authentication, thereby gaining unauthorized remote access to the affected system.

Document
Run Free ThreatScan on Your Mailbox

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Try Trustifi Free Threat Scan with Sophisticated AI-Powered Email Protection .

Given the ubiquity of xz-utils across various Linux distributions, the potential for widespread compromise was alarmingly high.

Fortunately, the issue was identified and addressed swiftly, mitigating the potential damage.

The vulnerability has been patched in Debian, from which Kali Linux derives much of its software base, thereby rectifying the issue for Kali users.

Impact on Kali Linux

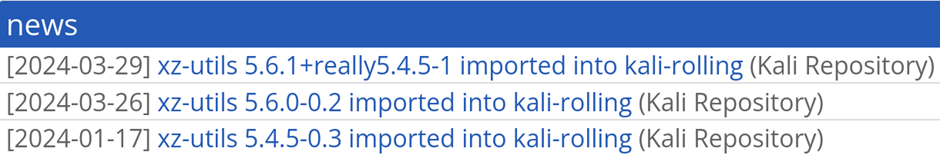
For Kali Linux users, the vulnerability window was narrow but critical. The affected xz-utils version, 5.6.0-0.2, was available in the Kali repositories from March 26th to March 29th.

backdoor vulnerability

Users who updated their Kali Linux installations within this timeframe are at risk and must take immediate action to secure their systems.

If your Kali Linux system was not updated during this period, you are not at risk from this specific vulnerability.

However, staying informed and vigilant about system updates is always advisable to maintain security.

How to Check for Infection and Update

To determine if your Kali Linux system is affected, you can execute the following command in the terminal:

kali@kali:~$ apt-cache policy liblzma5 

liblzma5: 

 Installed: 5.4.5-0.3 

 Candidate: 5.6.1+really5.4.5-1 

 Version table: 

    5.6.1+really5.4.5-1 500 

       500 http://kali.download/kali kali-rolling/main amd64 Packages 

*** 5.4.5-0.3 100 

       100 /var/lib/dpkg/status

If the output indicates the installed version as 5.6.0-0.2, your system is vulnerable, and you must upgrade to the latest version, 5.6.1+really5.4.5-1. This can be achieved with the following commands:

kali@kali:~$ sudo apt update && sudo apt install -y --only-upgrade liblzma5
...
kali@kali:~$

For those seeking more detailed information on this vulnerability, several resources are available:

  • Help Net Security provides a summarized post on the details of the vulnerability.
  • Openwall features the initial disclosure of the vulnerability.
  • The National Vulnerability Database (NVD) entry for CVE-2024-3094 offers comprehensive information on the specifics of the vulnerability.

This incident serves as a reminder of the constant vigilance required in the digital age to protect against evolving cybersecurity threats.

Users are encouraged to promptly apply updates and stay informed on the latest security advisories.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

OnePlus unveils Nord CE4 with 120Hz display, Snapdragon 7 Gen 3 SoC

0
[ad_1]

A new OnePlus phone is here, the Nord CE4. This handset was announced in India, and it’s a mid-ranger, in case you were wondering. Its spec sheet is nothing to scoff at, and it also looks very nice.

The OnePlus Nord CE4 has been announced with one of Qualcomm’s best mid-range chips

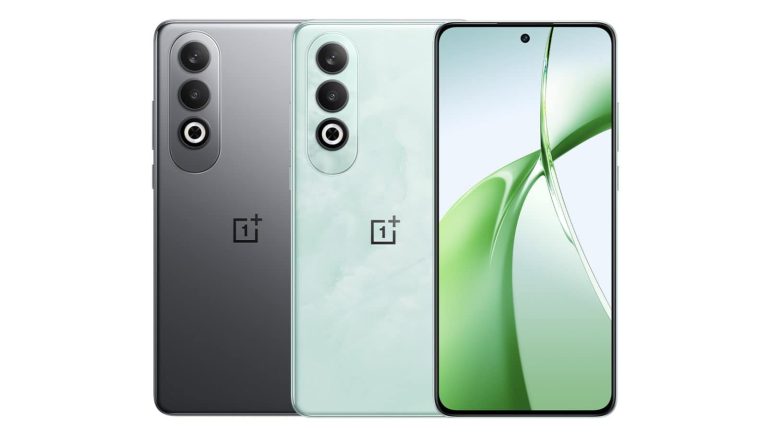
As you can see in the provided images, the device has a flat display, with rather thin bezels. A centered display camera hole is included, while all of its physical keys are located on the right side.

There are two cameras placed on the back, and they’re vertically aligned. They are a part of the same camera island which sits in the top-left corner of the phone’s back. OnePlus’ logo is also located on the back.

It has a 120Hz display, and offers expandable storage too

The OnePlus Nord CE4 features a 6.7-inch fullHD+ (2412 x 1080) AMOLED display with a 120Hz refresh rate. That panel also offers a 240Hz touch sampling rate and a 2,160Hz PWM dimming. Its display brightness goes up to 1,100 nits.

The Snapdragon 7 Gen 3 fuels the OnePlus Nord CE4. The phone is also equipped with 8GB of LPDDR4X RAM and 128GB/256GB of UFS 3.1 flash storage. Its storage is expandable up to 1TB via a microSD card.

A 5,500mAh battery sits inside of this phone. The OnePlus Nord CE4 supports 100W SuperVOOC charging. Android 14 comes pre-installed on the device, along with OnePlus’ OxygenOS 14.

Two rear-facing cameras are included, and the phone is IP54 certified

A 50-megapixel main camera (Sony’s LYT-600 sensor, f/1.8 aperture, OIS) is located on the back. It’s backed by an 8-megapixel ultrawide camera (120-degree FoV, Sony’s IMX355 sensor, f/2.2 aperture). On the front, you’ll find a 16-megapixel selfie shooter (f/2.4 aperture).

The OnePlus Nord CE4 is IP54 certified, it’s dust and splash-resistant. A hybrid dual SIM card slots is included here. In other words, you can either use two SIM cards at the same time, or a SIM card and a microSD card.

The phone has an optical in-display fingerprint scanner. It measures 162.5 x 75.3 x 8.4mm, and weighs 186 grams. The OnePlus Nord CE4 comes in Dark Chrome and Celadon Marble colors. The latter has a marble look on the back.

The pricing of the OnePlus Nord CE4 starts at INR24,999 ($300). The phone is already available for pre-booking in the country, and there are also some pre-order perks included, like a free pair of OnePlus Nord Buds 2r.


[ad_2]
Source link

US Congress reportedly bans the use of Microsoft Copilot for staff members

0
[ad_1]

Generative AI is now almost everywhere and has been growing in popularity in the past year and a half. Almost all tech companies now have an AI bot and the features offered using Generative AI on phones are growing as we speak.

However, a report from Axios states that the US Congress isn’t particularly fond of Microsoft’s solution, Copilot. It has reportedly banned the AI app for members of the House over security concerns.

US Congress reportedly bans Copilot for members of the House citing security concerns

Reportedly, Congress’ Chief Administrative Officer, Catherine Szpindor, stated that Copilot is “unauthorized for House use” because of security concerns. Basically what this means is that the AI may leak information shared by House staff.


Meanwhile, Microsoft stated that they are working on government-friendly AI solution that would be able to meet strict security requirements. Reportedly, once this version is ready Congress will be checking it out and deciding whether to allow it for use or not. Last June, the House restricted staff members from using ChatGPT. They are allowed to use the paid version, but the free version is banned.

Microsoft Copilot is a helpful generative AI tool that also has a paid version. The paid version can be integrated with Word, Excel, Outlook, and PowerPoint. For now, though, congressional staff is banned from using it. If it were to leak government data, that would be a huge risk and could potentially cause enormous issues to arise.


[ad_2]
Source link

Pentagon Releases Cybersecurity Strategy To Strengthen DIB

0
[ad_1]

The DoD DIB Cybersecurity Strategy is a three-year plan (FY24-27) to improve cybersecurity for defense contractors that aims to create a secure and resilient information environment for the Defense Industrial Base (DIB). 

It will be achieved through collaboration between DoD and DIB, focusing on four key goals: strengthening DoD’s cybersecurity governance, enhancing contractor cybersecurity posture, ensuring critical capabilities are cyber-resilient, and improving collaboration with the DIB. 

The strategy is in line with national strategies and makes use of the National Institute of Standards and Technology’s Cybersecurity Framework. 

FY 2024 – 2027 DoD DIB Cybersecurity Strategy

DoD relies on the DIB to develop advanced technologies and maintain critical infrastructure, as DIB companies are vulnerable to cyberattacks from foreign adversaries and non-state actors, which could result in unauthorized access to sensitive data and disruption of critical business operations.

Document
Run Free ThreatScan on Your Mailbox

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Try Trustifi Free Threat Scan with Sophisticated AI-Powered Email Protection .

The DoD has established a multi-pronged approach to improving DIB cybersecurity, including collaboration with industry associations and public-private partnerships. 

The strategy will inform future updates to DoD’s DIB cybersecurity plan and focus on protecting DoD information, ensuring DIB supplier continuity of operations, and making the DIB more cyber-secure.

Current DoD and DIB Cybersecurity Efforts

The Department of Defense (DoD) will strengthen its governance structure for Defense Industrial Base (DIB) cybersecurity by fostering collaboration among stakeholders and developing regulations. 

It includes establishing a DIB Cybersecurity Executive Steering Group (ESG) to coordinate policies and a DoD DIB Cybersecurity Program to implement a DoD-wide strategic approach. 

It also works with DIB and interagency stakeholders to improve information sharing and develop a governance framework for subcontractor cybersecurity by improving the cybersecurity posture of the Defense Industrial Base (DIB) through a number of initiatives. 

The initiatives include requiring DIB contractors to implement cybersecurity best practices and undergo assessments, sharing threat intelligence with DIB contractors, and improving the ability to recover from cyberattacks.

It will also work with DIB contractors to evaluate the effectiveness of cybersecurity regulations and policies.

DoD DIB Cybersecurity Strategic Alignment

The Department of Defense needs to prioritize the cybersecurity of critical Defense Industrial Base (DIB) production capabilities, which is achieveable by working with the DIB Sector Coordinating Council (SCC) to identify critical suppliers and facilities and setting clear policies on cybersecurity for them. 

The DoD, as the Sector Risk Management Agency (SRMA) for the DIB, should focus government-led protection efforts on these critical assets, which will ensure that limited resources are directed towards the most impactful activities. 

According to the Media Defense, DoD will collaborate with DIB to improve cybersecurity posture by leveraging commercial cybersecurity service providers, improving communication channels, and expanding information sharing. 

NSA will share threat intelligence with DIB, and DIB SCC will collaborate with DoD to improve information sharing and also develop cyber incident scenarios and response playbooks to improve DIB’s resilience.

NIST Cybersecurity Framework 2.0 Core

The DoD DIB Cybersecurity Strategy outlines a collaborative effort between DoD and DIB to strengthen cybersecurity posture, which emphasizes information sharing, education, and baseline security requirements. 

DoD will leverage expertise from the NSA, DC3, and USCYBERCOM to improve detection and response, which aims to continuously improve DIB cybersecurity through collaboration and resource coordination by ensuring the resilience of critical defense suppliers and producers against evolving cyber threats.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

Nubia Flip will launch in Europe on April 9, it’s official

0
[ad_1]

Nubia showed off its first flip phone at MWC 2024. At the time, we had no idea whether the device would actually launch in Europe. Well, we’re glad to say it will. The Nubia Flip 5G will launch in Europe on April 9, the company has confirmed.

The Nubia Flip will launch in Europe on April 9

The press event will kick off at 1 PM CET / noon BST / 7 AM EST / 4 AM PST. If you’re interested in getting the device, you can get a €15 discount. All you have to do is sign up for emails on the official Nubia Flip event website. You will also be eligible to win a free Nubia Flip if you do that.

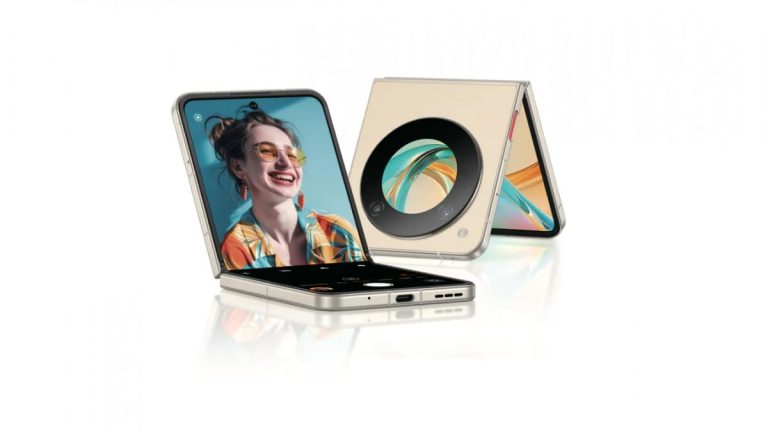
The Nubia Flip is made out of metal and glass, and it has a circular cover display on the back. There is also a black circle around it which hosts the phone’s main cameras. That circle reminds us of some of HONOR’s designs, to be quite honest, like the HONOR Magic6 Lite.

On the inside, you’ll find a large display with a centered display camera hole. That display is, of course, flat, and the phone folds right down the middle. The sides of the device are flat, and all the physical buttons sit on the right-hand side.

Nubia Flip 5G image 2

The phone has a 6.9-inch OLED display with a 120Hz refresh rate

The Nubia Flip features a 6.9-inch 2790 x 1188 OLED display with a 120Hz refresh rate. That is its main panel. The cover display measures 1.43 inches, and it has a resolution of 466 x 466.

A 50-megapixel main camera sits on the back, and it’s backed by a 2-megapixel depth unit. A 16-megapixel camera is included on the main display. The phone has been certified for 200,000 folds, by the way.

33W wired charging is supported, while the Snapdragon 7 Gen 1 fuels the device

The Nubia Flip has a 4,310mAh battery, and it supports 33W wired charging. Wireless charging is not supported here, in case you were wondering. The phone is fueled by the Snapdragon 7 Gen 1 chip.

Despite the fact the phone hasn’t launched yet, we already know what to expect on the pricing side of things. The Nubia Flip will set you back $599 should you choose to be it. That makes it one of the most affordable foldable smartphones on the market.

The Nubia Flip will arrive in Black and Gold colors. We still don’t know in which markets exactly will it become available, though.


[ad_2]
Source link

TikTok casts its educational STEM feed to Europe

0
[ad_1]

TikTok’s critics often highlight the difference in the way the virulent app behaves and operates in the Far East and in the west. Namely, there are grave concerns with the “western” TikTok’s algorithm and the content it feeds to kids and young users.

Now, TechCrunch reports that TikTok is bringing its dedicated STEM feed to Europe – meaning that the popular short video app will be more educational (in theory).

The ByteDance-owned company announced the expansion of its specialized STEM (science, technology, engineering and mathematics) feed to Europe, beginning with the UK and Ireland. This initiative first took off in the US last year.

For users under 18, the STEM feed will be displayed automatically along with the “For You” and “Following” feeds. Those users that are past the age of 18 can activate the STEM feed through the app’s “content preferences” feature, which offers English-language content with auto-translate subtitles.

Since its US debut, 33% of TikTok users have activated the STEM feed, with a third of teenagers accessing it weekly. The US has witnessed a 24% increase in STEM content since the feed’s introduction. Globally, TikTok hosts nearly 15 million STEM-focused videos, posted over the last three years.

This development follows criticism of TikTok for exposing young users to potentially harmful content and accusations of using design tactics that promote virtual addiction. The European Union, in February, began an inquiry to determine if TikTok violates the Digital Services Act by allowing minors access to unsuitable content and encouraging addictive behaviors.


[ad_2]
Source link

Live Forensic Techniques To Detect Ransomware Infection On Linux Machines

0
[ad_1]

Ransomware, initially a Windows threat, now targets Linux systems, endangering IoT ecosystems.

Linux ransomware employs diverse encryption methods, evading traditional forensics. 

Still developing, it shows potential for Windows-level impact. Early awareness allows for assessing IoT security implications.

The following cybersecurity analysts from Edinburgh Napier University recently unveiled live forensic techniques to detect ransomware infection on Linux machines:-

  • Salko Korac
  • Leandros Maglaras
  • Naghmeh Moradpoor
  • Bill Buchanan
  • Berk Canberk

Live Forensic Techniques Ransomware

However, the increased use of IoT technologies has brought about interconnected devices without man’s intervention making them susceptible to ransomware attacks, especially in Linux-based IoT systems.

Document
Run Free ThreatScan on Your Mailbox

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Try Trustifi Free Threat Scan with Sophisticated AI-Powered Email Protection .

Although there have been efforts against paying ransomware and shifting cyber-criminal activities due to political issues, ransomware is still a significant concern with new ways of evading countermeasures. 

Due to this reason proactive security measures are necessarily vital in protecting the IoT environments from this growing threat.

Response chain (Source – Arxiv)

There 24 major execution experiments were performed with retest across 12 combinations, involving three samples of ransomware on two Linux OS with two permission levels.

In balancing realism and effort, virtual machines simulated cloud environments to external memory dumps and network captures without the ransomware being detected.

Originally designed to be very realistic, the initial design led to lengthy forensic investigations that called for retesting environments to validate unforeseen results as well as removing disturbing elements.

Playbook for experiment execution (Source – Arxiv)

Replacing the Windows ransomware’s lateral movement and encryption of file shares and web server files that also provide user logins, Linux ransomware was not able to achieve very damaging results.

User files were encrypted by Cl0p and Icefire, thereby disabling GUI logins, while Blackbasta malware was aimed at /vmfs/volumes.

Most importantly, none of them used administrative permission adequately, hence MySQL/Sybase, SSH, FTP, or any Samba sharing were all left unharmed although they had been running as root.

Contrary to this approach, in companies where external storage is preferred to be on home or root directories, it might have resulted in less observable impact.

Ransomware activities exhibited by Linux are determined by those observed in Windows.

The research provides insights into the implications of Linux ransomware for the IoT industry.

Instead of encrypting data, criminals may block operations temporarily until payment is made through cyber-attacks on IoT gadgets. 

Linux ransomware requires a lot of work and doesn’t scale well as it has to be specifically developed for each individual target, unlike modular Windows variants. 

IoT solutions with strong security and low market visibility have less threat. The most scalable among these can attack either endpoints, gateways, or cloud infrastructure. 

Further discoveries indicate that encryption techniques like RC4, ChaCha20 as well as AES are used by attackers which makes live forensics challenging compared to Windows platforms. 

Recommendations

Presently, Linux ransomware causes limited harm, but it is expected to change in the future.

Risk management measures are suggested to secure Linux systems to enable risk evaluation and mitigation in the IoT industry.

Here below we have mentioned the recommendations:-

  • Avoid HOME directories
  • Separate and restrict permissions and data access
  • Avoid using privileged users
  • Focus on identifying backdoors
  • Shut down first

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link