Leading EV Charging Firm Spills Trove of Customer Info in Server Leak

0

[ad_1]

A massive data leak (585.81 GB) exposed customer information at Qmerit, including home images, charger locations, and potentially more – Qmerit took immediate action to secure the data.
Leading EV Charging Firm Qmerit Spills Trove of Customer Info

Cybersecurity researcher Jeremiah Fowler has uncovered a troubling data exposure incident, yet again drawing attention to broader concerns surrounding data security. Fowler, in collaboration with WebsitePlanet, uncovered a non-password-protected database containing over half a million records, including sensitive customer information and invoices from a prominent American EV services provider.

The exposed database, totalling 585.81 GB in size, contained a trove of documents such as work invoices, price proposals, electrical permits, and surveys, alongside customer-submitted information including images of their homes and charger location details.

According to Fowler’s blog post, upon investigation, he identified the data as belonging to Qmerit, a Texas-based company specializing in EV charging infrastructure installation and maintenance since 2016.

Following the responsible disclosure by Fowler, Qmerit swiftly took action to secure the exposed data and initiate an internal investigation. In response to the incident, Qmerit emphasized its commitment to prioritizing security and protecting Personally Identifiable Information (PII). However, the duration of the data exposure and potential unauthorized access remain uncertain, warranting further scrutiny through internal forensic audits.

Leading EV Charging Firm Qmerit Spills Trove of Customer Info
Screenshot from the exposed records (Screenshot credit: Websiteplanet_

Fowler clarified that his findings do not imply wrongdoing on Qmerit’s part or suggest imminent threats to customer or contractor safety. However, the incident must be taken as a lesson surrounding the importance of vital data protection measures in protecting customer privacy and maintaining trust in the market.

Despite this incident, Qmerit continues to position itself as a leading player in North America’s EV services industry, boasting partnerships with major automakers and a track record of over 269,000 EV charger installations.

  1. EV Charging Stations at Risk of DoS Attacks
  2. Navigating London’s Free Electric Car Charging Points
  3. Massive Cloud Database Leak Exposes 380 Million Records
  4. US Credit Union Service Leaks Millions of Records and Passwords
  5. Aussie Travel Agency Data Leak Puts Thousands of Tourists at Risk


[ad_2]

Source link

Galaxy Z Flip 6 could use a bigger cover display, sketchy rumor says

0

[ad_1]

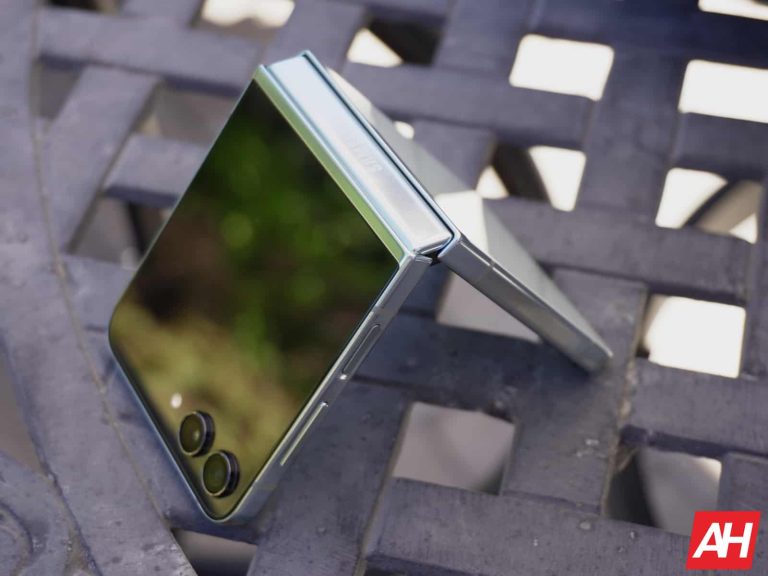
A new rumor has surfaced, and this one is surprising. The Galaxy Z Flip 6 is tipped to use a bigger cover display. The current-gen model has a 3.4-inch one, but with the Galaxy Z Flip 6, Samsung could go beyond that size.

The Galaxy Z Flip 6 could include a bigger cover display according to a sketchy rumor

According to @TheGalox_, a tipster, the Galaxy Z Flip 6 will include a 3.9-inch display. That is highly unlikely, however. Why? Well, the CAD-based renders of the phone already surfaced, and from what they’ve shown us, there’s no way we’re looking at a 3.9-inch panel.

In fact, based on those renders, the Galaxy Z Flip 6 will retain the same display size. Another reason not to believe this information is the fact that Samsung does not make such changes year after year. The 3.4-inch display was implemented last year, so the Galaxy Z Flip 6 will almost certainly retain it.

The tipster did share some other details about the phone. We’re not sure how credible they are considering this display size info is almost certainly off. So, take the following information with a grain of salt.

The Snapdragon 8 Gen 3 for Galaxy will fuel the phone

He mentioned the Snapdragon 8 Gen 3 for Galaxy SoC, which is a given. A bigger cooling system is also tipped, and a 6.7-inch main display. A 50-megapixel main camera and a 12-megapixel ultrawide camera are also mentioned.

The tipster does note that a 4,000mAh battery will be included, along with an improved hinge and internal layout of components. The Gorilla Glass Armor will protect the outer display, while the device is tipped to get 7 years of updates.

Samsung’s Galaxy AI will be a part of the picture too, while “possible 12GB RAM models” were also mentioned. The Galaxy Z Flip 6 is expected to arrive alongside the Galaxy Z Fold 6 in July. July 10 has been tipped as the launch date, but nothing has been confirmed just yet.


[ad_2]

Source link

Microsoft patents Eye-Gaze technology for hands-free typing

0

[ad_1]

Eye-gaze technology is a revolutionary innovation under development by Microsoft. It could change the way users interact with applications by using eye movements. A new patent filed recently by Microsoft displays the technology’s recent advances in accessibility and user experience.

Microsoft’s Eye-Gaze technology will allow you to type using only your eyes

The patented eye-gaze system employs a ‘Dwell-free’ typing method where the user only needs to look at keys on a screen for him/her to type. Moreover, it allows users to interact with various applications just by focusing their eyes on them; hence, they can click buttons within web browsers without any physical manipulation.

Microsoft then introduced a smooth response system termed ‘dwell-free’ to remove problems regarding flickering eye movements and uneven gaze recordings. It helps to address the issue of having an accurate target where a person is looking. Also, it does not require someone to look at something for too long, thereby enhancing usability and reducing eye strain. The tech rivals the Apple Vision Pro’s eye tracking closely.

Its integration with Windows allows this technology to control mechanisms such as audio volumes through eye movements. Per WindowsReport, this technology has the potential to integrate with numerous programs. There are minimum limitations to this system, and it offers various ways to approach things.

The particular artificial intelligence-based model used in this feature’s development is fascinating. It uses collected data from consumers to provide suggestions and make predictions. By analyzing patterns in the user’s gaze, it can combine specific forms of action with visual cues improving effectiveness.

The tech will initially integrate with Windows before expanding to other platforms

Microsoft Eye-Gaze Technology also features predictive processing and smart algorithms that quickly respond to users. Although testing started on HoloLens headsets inside mixed-reality environments, experts believe that this technology will expand across all devices including mobile phones, tablets, and personal computers.

This represents a huge stride forward towards accessibility and UI innovation – perhaps suited for future AI-based Windows iterations and Microsoft Edge. This new approach may be exciting but at the same time raises questions concerning privacy plus how much freedom individuals should have when dealing with technology that is AI-driven.

[ad_2]

Source link

Beware Of New Malicious PyPI Packages Attack Crypto Wallets

0

[ad_1]

Threat actors use malicious PyPI packages to infiltrate systems and execute various attacks like data exfiltration, ransomware deployment, or system compromise. 

By masquerading as legitimate Python libraries all these packages can easily bypass security measures. 

This allows it to infect the unsuspecting users’ environments and potentially cause widespread damage.

Cybersecurity researchers at ReversingLabs recently discovered new malicious PyPI packages that could steal crypto wallet passwords.

New Malicious PyPI Packages

ReversingLabs unveiled a malicious scheme spanning seven open-source packages on PyPI, with 19 variants, the earliest dating back to December 2022. 

This ‘BIPClip’ campaign aims to steal helpful phrases for crypto wallet recovery by joining the ranks of previous supply chain attacks like 3CX’s compromise. 

Cryptocurrency remains a coveted target, and threat actors employ deceptive tactics like malicious dependencies and name-squatting to evade detection.

The RL research team found 7 new malicious PyPI packages aiming to steal crypto wallet phrases while staying hidden.

This campaign targets developers handling cryptocurrency wallets, especially those using BIP39 for easy-to-remember wallet generation. BIP39 simplifies seed creation with mnemonic phrases, enhancing recall for wallet owners.

Crypto infrastructure and assets remain prime targets for supply chain strikes, from the Ledger Connect Kit breach diverting transactions to covert cryptominers in Python libraries and malicious crypto-related npm packages.

Allegedly, the North Korean threat actors have stolen up to $3 billion in crypto over five years; it’s a staggering 5% of their GDP.

ReversingLabs found two PyPI packages, mnemonic_to_address, and bip39_mnemonic_decrypt, collaborating to steal crypto wallet data. 

The bip39_mnemonic_decrypt raised suspicion with Base64 decoding and network usage. Besides this further investigation revealed mnemonic_to_address as a seemingly “clean” package with bip39_mnemonic_decrypt as a hidden malicious dependency.

Code example from eth-account documentation for generating an account from a mnemonic (Source – ReversingLabs)

The mnemonic_to_address package acts as a wrapper for function calls. However, it differs subtly by using decrypt_jsBIP39 which is a function that is not found in the eth-account package.

This function is imported from the bip39_mnemonic_decrypt module, where the mnemonic_to_address package passes the user’s mnemonic passphrase as an argument.

Code from mnemonic_to_address package calls the function from the malicious bip39_mnemonic_decrypt package (Source – ReversingLabs)

The bip39_mnemonic_decrypt package is the second in the campaign and is a dependency of mnemonic_to_address. 

ReversingLabs discovered clearly malicious functionality within it. Both packages were published by james_pycode, a newly created PyPI maintainer account, a common tactic in malicious campaigns. 

The account showed minimal effort to establish credibility. Sophisticated attackers often invest resources to mimic official pages in open-source repositories.

Threat actors stealthily hide malicious code in open-source packages. They concealed malware deep within dependencies to avoid detection during code audits. 

Fraudulent function names like “decrypt_jsBIP39” and “cli_keccak256” disguised malicious actions. The malware stealthily exfiltrated crypto wallet seeds, encoding them as “license” data. 

Though limited in scope, this supply chain attack exploited developers’ trust in open-source libraries. Vigilance in vetting third-party code and security assessments is crucial to prevent such threats from targeting the lucrative crypto ecosystem.

IOCs

IoC (Source – ReversingLabs)

With Perimeter81 malware protection, you can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits. All are incredibly harmful and can wreak havoc on your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link

EquiLend Employee Data Breached After January Ransomware Attack

0

[ad_1]

EquiLend, a financial technology firm, experienced a data breach following a January ransomware attack – EquiLend is offering credit monitoring and identity theft protection to affected individuals.

EquiLend Employee Data Breached After January Ransomware Attack

Financial technology firm EquiLend recently disclosed a data breach reportedly originating from a January ransomware attack. The attack, which according to Bloomberg’s report, is attributed to the LockBit ransomware group, compromised the personal information of EquiLend employees.

The claim that LockBit ransomware is involved in the incident is concerning for businesses, as the group, despite its shutdown, has not only resurfaced but is already targeting new victims.

Breach Details Emerge

EquiLend initially reported a “technical issue” on January 24th, leading to service disruptions. The company later confirmed a ransomware attack but provided limited details. Recent notifications to affected individuals and authorities reveal the extent of the data breach.

Employee Information Exposed

According to the notification sent by the company to impacted customers, the attack compromised sensitive employee data, including names, dates of birth, Social Security numbers, and internal payroll information. EquiLend assures it has no evidence of this information being misused but is offering two years of complimentary credit monitoring and identity theft protection services to affected individuals.

Ransomware Attack Scope Unclear

While client-facing services were restored by February 5th, the full impact of the attack remains unclear. Speculation suggests EquiLend may have negotiated with the attackers, but the company has not confirmed any ransom payment.

It’s worth noting that at the time of writing, LockBit’s dark web leak site showed no mention of EquiLend. This could indicate that negotiations have occurred, or the group has yet to list EquiLend on their website.

EquiLend Responds

EquiLend is working with cybersecurity experts to investigate the incident and prevent future occurrences. The company emphasizes its commitment to data security and is urging affected individuals to remain vigilant and monitor their financial statements for suspicious activity.

Experts Weigh In

For insights, we reached out to Tamara Kirchleitner, Senior Intelligence Operations Analyst at Centripetal. “In the wake of this cyberattack, it’s a stark reminder of the relentless threat fintech firms face. Offering affected employees free identity theft protection is commendable, yet many companies remain reactive,” Tamara said.

“This incident underscores the need for proactive cybersecurity measures. Implementing robust protocols is imperative in today’s digital landscape. Businesses must embrace advanced technologies to safeguard their systems and customer data. It’s time for a paradigm shift towards anticipatory cybersecurity,” she warned.

Importance of Cybersecurity

This incident highlights the growing threat of ransomware attacks and the importance of strong cybersecurity measures. Financial institutions like EquiLend handle sensitive data, making them prime targets for cybercriminals.

EquiLend’s data breach should be a wakeup for organizations to prioritize data security investments and implement strong safeguards against cyberattacks.

  1. FIN8 Resurfaces with New Sardonic Backdoor
  2. Hive Ransomware Resurfaces as Hunters International
  3. FBI Disrupts Chinese State-Backed Volt Typhoon’s KV Botnet
  4. Mirai botnet resurfaces with MooBot variant to target D-Link devices
  5. Nasty Mamba ransomware that encrypts entire hard drive resurfaces


[ad_2]

Source link

OnePlus Ace 3V live image, specs & benchmark appear

0

[ad_1]

The OnePlus Ace 3V has just surfaced in a live image, while its specs also appeared. The phone also appeared in a benchmark, so plenty of information surfaced.

Just to clear things up in terms of naming. The OnePlus Ace 3V will launch in China, while the OnePlus Nord 4 or 5 will be its global variant. That name is far more recognizable to the vast majority of you. It should technically be the Nord 4, but the number 4 is considered to be unlucky in China, so OnePlus could jump straight to the Nord 5.

The OnePlus Ace 3V live image appears, along with the phone’s specs

If you take a look at the image below, you’ll see the device itself. This is technically the OnePlus Ace 3V, but the OnePlus Nord 4/5 will look identical to it… though it will run a global software on it.

OnePlus Ace 3V live image leak 1

You can clearly see that an alert slider will be located on the left side. That is not all that surprising as the Nord 3 had the alert slider too, but it was located on the opposite side.

The phone will have flat sides, which will be slightly curved towards the edges. A flat display will sit on the front, with a centered display camera hole up top. The bezels around that panel will be very thin. All the physical buttons will sit on the right-hand side.

The Snapdragon 7+ Gen 3 will fuel the device, while a 5,500mAh battery will also be included

The phone got spotted on Geekbench. It scored 1,848 points in the single-core, and 5,007 points in the multi-core test. The Snapdragon 7+ Gen 3 SoC will fuel the phone, while we also know that a 5,500mAh battery will be included.

The rest of the specs also got tipped. The phone is expected to include a 1.5K display with a 120Hz refresh rate. Android 14 will come pre-installed on the device, and 100W wired charging will also be on offer.

A 50-megapixel main camera will sit on the back of the device. We don’t have the information regarding other cameras, there could be two or three in total. A 16-megapixel selfie camera will be included on the front.

The device will also have an in-display fingerprint scanner. Chances are that will be an optical unit.


[ad_2]

Source link

Roku faces a data breach with over 15,000 accounts hacked

0

[ad_1]

Roku’s recent filing with the attorney general in California confirms over 15,000 accounts were impacted by a data breach. Last year, the streaming platform was hit by a hacking group, and some of its most sensitive data was compromised. Back then, it was even said that bad actors could steal user’s credit card information and try to make purchases with them.

Roku has given a complete description of the event in its filing, and if you’re a Roku user, you can read the filing to gain insight into the incident. As per the company’s explanations, the unauthorized actors gained login information from “third-party sources that are unrelated to Roku.”

 Roku hit with a massive data breach

Attackers reportedly changed login information after taking over the account to keep the original account holder out. Roku further explains that attackers could not access data such as “social security numbers, full payment account numbers, dates of birth, or other similar sensitive personal information requiring notification.”

Roku added that the incidents happened on December 28, 2023, and February 21, 2024. After identifying the impacted account, the company prevented further unauthorized access by demanding the account holder reset their password. Canceling unauthorized subscriptions was another step to keep bad actors out of user’s accounts.

To be exact, 15,363 Roku accounts are compromised. The company says the impacted users need to change their account passwords and check the subscriptions and devices linked to their streaming accounts.

You can now buy compromised Roku accounts for a little price

Bleeping Computer was the first to discover the breaching. As the outlet reports, attackers are now selling Roku accounts for as little as $0.50 per account. Each account comes with credit card information so buyers can make illegal purchases. So far, 439 accounts have been sold.

Unfortunately, Roku doesn’t support two-factor authentication for its account, depriving users of an additional layer of security. If you think your account is impacted, be quick to change your password and enter your information on HaveIBeenPwned to check if your data has been leaked online.

[ad_2]

Source link

T-Mobile and Netflix have found a fresh way to anger their subscribers

0

[ad_1]

When news broke at the beginning of the year that T-Mobile was preparing a major revision of its longstanding Netflix freebie for some customers, we have to admit… we were far from shocked. While that likely also applied to many of the “Un-carrier’s” impacted users, who probably saw the change coming a long time ago as Netflix kept jacking up its prices, what followed after the initial revelation was indeed surprising for everyone.

Without any warning, it appears that the Netflix “Standard with ads” plan offered for free to high-paying T-Mobile customers has also started to restrict some content. That’s right, certain movies and TV shows that are technically available on Netflix can’t actually be streamed by T-Mo subscribers even with ad support, and as insane as it sounds, that’s intended behavior on the streaming platform’s part rather than the result of some temporary glitch or error.
Of course, this is not technicallyT-Mobile‘s fault, but rather entirely Netflix’s doing, which is not stopping people from shouting in frustration at their carrier all across social media. It’s also not a new situation… and that’s part of the problem. 
When T-Mobile communicated to its users that their Netflix benefit was about to be “updated” back in January, there was absolutely no mention of this “little” detail. That continued after the change took effect, and even right now no content restrictions of any sort are mentioned or detailed on Magenta’s “Netflix on Us” webpage.
For its part, Netflix is also keeping things awfully vague about the “lock icon” that sometimes appears on TV shows and movies that “aren’t available with your current plan”, so we’re afraid you’ll just have to discover for yourselves what content you can and cannot watch with ads. 

Before getting too angry at T-Mobile, it’s important to remember that you’re not really paying anything for your Netflix Standard with ads subscription, which would otherwise cost you $6.99 a month. And if you simply can’t accept these compromises, you can always upgrade to a no-ads Standard or Premium streaming plan at a discount. That doesn’t make the whole thing right, but it arguably makes it a little easier to stomach.

[ad_2]

Source link

Stanford University Hack Exposes Over 27K People’s Data

0

[ad_1]

The Stanford University data breach involved a ransomware attack by the Akira ransomware gang.

The breach occurred between May 12, 2023, and September 27, 2023, with the university discovering the attack on September 27, 2023.

The compromised information varied but could include dates of birth, Social Security numbers, government IDs, passport numbers, driver’s licenses, and potentially biometric data, health/medical information, email addresses with passwords, usernames with passwords, security questions and answers, digital signatures, and credit card information with security codes.

Impact on Affected People

The breach has put over 27,000 individuals at risk, including 3 Maine residents, underscoring the widespread impact of the incident.

The delay in detecting the hack has potentially given bad actors ample time to misuse the exposed information, increasing the risk of identity theft and financial fraud for those affected.

Notification Process

Stanford University began notifying affected individuals through breach notification letters in March 2024, approximately 10 months after the initial compromise.

This delay was attributed to the time required to analyze the incident.

The notification process was conducted in writing, with specific letters sent to affected Maine residents as per regulatory requirements.

The university has been transparent about the breach, stating that the compromised system was isolated to the Department of Public Safety and did not involve other Stanford systems or networks.

The Maine Attorney General’s office in the US has recently reported that a hack at Stanford University exposed sensitive data belonging to over 27,000 individuals.

Identity Theft Protection Services

To mitigate the breach’s impact, Stanford University offered victims 24 months of complimentary credit monitoring and identity protection services through IDX and TransUnion.

These services are designed to help affected individuals monitor their credit for signs of fraudulent activity and take steps to protect their identity.

The university’s response also includes ongoing investigations in collaboration with federal and local law enforcement to address and prevent future cybersecurity incidents.

This incident is part of a series of cybersecurity challenges Stanford University faces. Other challenges include a previous breach 2021 involving the Clop ransomware gang and the Accellion File Transfer Appliance software, which affected Stanford Medicine.

With Perimeter81 malware protection, you can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits. All are incredibly harmful and can wreak havoc on your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link

New Facebook photo rule hoax spreads

0

[ad_1]

Some hoaxes on Facebook are years old, but like a cat with nine lives they keep coming back again and again. This is certainly the case with this most recent hoax.

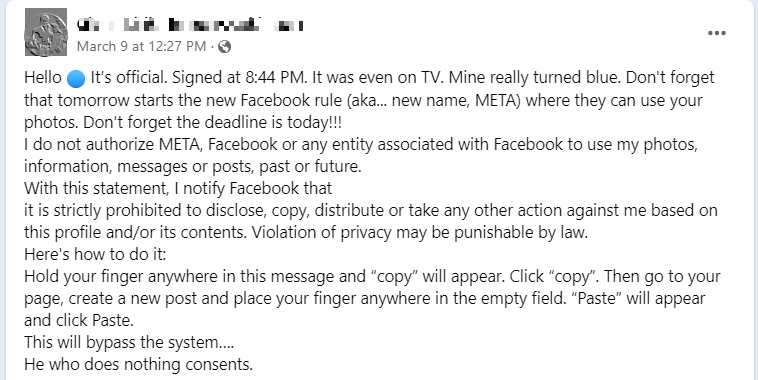
Fact-checking site Snopes is reporting on a hoax that concerns Meta’s use of our photos, messages and other posts on Facebook. Users are told in numerous ways to repost something that contains the phrase:

“I do not authorize META, Facebook or any entity associated with Facebook to use my photos, information, messages or posts, past or future.”

“Hello 🔵 It’s official. Signed at 8:44 PM. It was even on TV. Mine really turned blue. Don’t forget that tomorrow starts the new Facebook rule (aka… new name, META) where they can use your photos. Don’t forget the deadline is today!!!

I do not authorize META, Facebook or any entity associated with Facebook to use my photos, information, messages or posts, past or future.

With this statement, I notify Facebook that

it is strictly prohibited to disclose, copy, distribute or take any other action against me based on this profile and/or its contents. Violation of privacy may be punishable by law.

Here’s how to do it:

Hold your finger anywhere in this message and “copy” will appear. Click “copy”. Then go to your page, create a new post and place your finger anywhere in the empty field. “Paste” will appear and click Paste.

This will bypass the system….

He who does nothing consents.”

The first round of hoax posts similar to this one surfaced in 2012 (and have resurfaced many times since then). As you can see in this page on the Internet archives, Facebook even issued a statement about it:

“Fact Check

Copyright Meme Spreading on Facebook

There is a rumor circulating that Facebook is making a change related to ownership of users’ information or the content they post to the site. This is false. Anyone who uses Facebook owns and controls the content and information they post, as stated in our terms. They control how that content and information is shared. That is our policy, and it always has been.”

It’s not a Real Thing

With all the—legitimate—concern around keeping personal data private, one can see why people fall for hoaxes like this. However, this copy-paste post does nothing. Facebook doesn’t get to “own” your content and you don’t need to make any declarations about copyright issues since the law already protects you.

Equally, Facebook users cannot retroactively negate any of the privacy or copyright terms they agreed to when they signed up for their accounts, simply by posting a contrary legal notice on to Facebook.

In other words, you agreed to Facebook’s terms of use and when you did, you provided Facebook with a right to use, distribute, and share the things you post, subject to the terms and applicable privacy settings. If that doesn’t sit well with you, it’s worth considering deactivating or deleting your Facebook account.

Sharing posts like this “just in case” continues the hoax and unnecessarily worries people who might see your post. If you’re not sure about whether you should share something, it’s worth googling the post’s text to check if there are any alerts about it.

If you are worried about how much of your data has been exposed online, you can try our free Digital Footprint scan. Fill in the email address you’re curious about (it’s best to submit the one you most frequently use) and we’ll send you a free report.


We don’t just report on threats – we help safeguard your entire digital identity

Cybersecurity risks should never spread beyond a headline. Protect your—and your family’s—personal information by using Malwarebytes Identity Theft Protection.

[ad_2]

Source link