MediaTek partnered with every Android brand, but one

0
[ad_1]

To show its prowess in the Android chipset market, MediaTek has now successfully partnered with every Android brand in the industry except Google. The Taiwanese semiconductor manufacturer has garnered its reputation with mid-range and budget Helio chipsets. Now, the company is shifting priorities, focusing mainly on high-end 5G-enabled SoCs.

MediaTek has successfully partnered with every Android manufacturer, except for Google

With previous doubts about their ability to compete against Qualcomm in the flagship market, a new report from the Economic Times suggests MediaTek’s comeback. With 15 different chipset designs created specifically for Android manufacturers (an expanded portfolio), MediaTek looks set to give Qualcomm a run for its money, especially at its most expensive prices.

Anku Jain, the Managing Director of MediaTek India, says that they now have deals with Samsung and Nothing. The only exception is Google. According to reports, Google itself is currently developing its in-house chipset called Tensor G4, which looks to be a prime component for the Pixel 9 series. However, this hasn’t stopped MediaTek’s ambition or belief that they can replace Qualcomm as the top dog.

MediaTek had an impressive first quarter of this year outpacing Qualcomm in terms of chips shipped according to a report by Economic Times. On top of that, they’re also working on a Dimensity 9400 Chipset, which should pose a serious threat to Qualcomms Snapdragon 8 Gen 4 when it launches.

Qaulcomm’s hiking prices may cause MediaTek to leap ahead in the competition

Earlier, an X leak reported that Qualcomm may be raising prices for its new chipset set to launch early next year. Resultantly, this price hike opens the door further for MediaTek’s new Dimensity 9400 Chipset, which is due for launch later this year and could offer better value for money than Qualcomm’s Snapdragon 8 Gen 4.

Morgan Stanley analyst speculates that about 35% of global smartphone chipsets will be powered by MediaTek by 2024. So it appears that Qualcomm might face some tough competition in the near future. The new entrant in the market seems to be worth considering, and it might make Qualcomm rethink its strategies.


[ad_2]
Source link

Opera One is getting an AI Features Drop program

0
[ad_1]
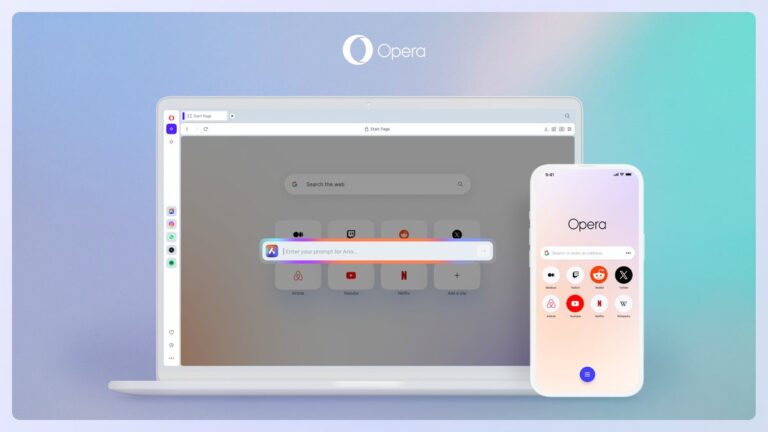
Artificial intelligence seems to have become the main focus of many tech companies. Everyone has a chatbot these days and while this is certainly not a bad thing, it’s probably going to take some time before the AI will be used for truly meaningful tasks like discovering treatments for diseases or solutions to prevent global warming.Opera is one of the companies that invested heavily in AI. Opera One, its rather new AI-focused browser, is an attempt to offer users an innovative experience to those looking for such a product.

Over the weekend, Opera announced it’s starting an AI Feature Drops program to provide users with even more AI-powered features. Opera One’s developer version will allow users to test new AI features on a bi-weekly basis thanks to this new AI Feature Drops initiative.

Video Thumbnail

Unlike other AI-centric browsers, Opera One features a native browser AI, which promises to improve the users’ browsing experience without the need for additional paid services or extensions.

Dubbed Aria, the Opera One integrated native AI offers free access to a GPT-based solution and real-time web data. Aria can also be trained to write in the user’s unique style.


[ad_2]
Source link

Dropbox Abused in New Phishing, Malspam Scam to Steal SaaS Logins

0
[ad_1]

Beware of phishing and malspam scams targeting your Software-as-a-Service (SaaS) logins! Cybercriminals are using fake Dropbox emails to steal login credentials. Learn how to protect yourself from this new attack and keep your data safe.

Dropbox Emails Abused in New Phishing, Malspam Scam to Steal SaaS Logins

Cybersecurity firm Darktrace is warning users about a notorious new phishing and Malspam campaign targeting customers of popular Software-as-a-Service (SaaS) platforms by exploiting Dropbox emails.

Cambridge, UK-based cybersecurity firm Darktrace’s latest research reveals a new Dropbox phishing attack successfully bypassing MFA (multi-factor authentication) protocols. This exploit aims to trick users into downloading malware and exposing their login credentials.

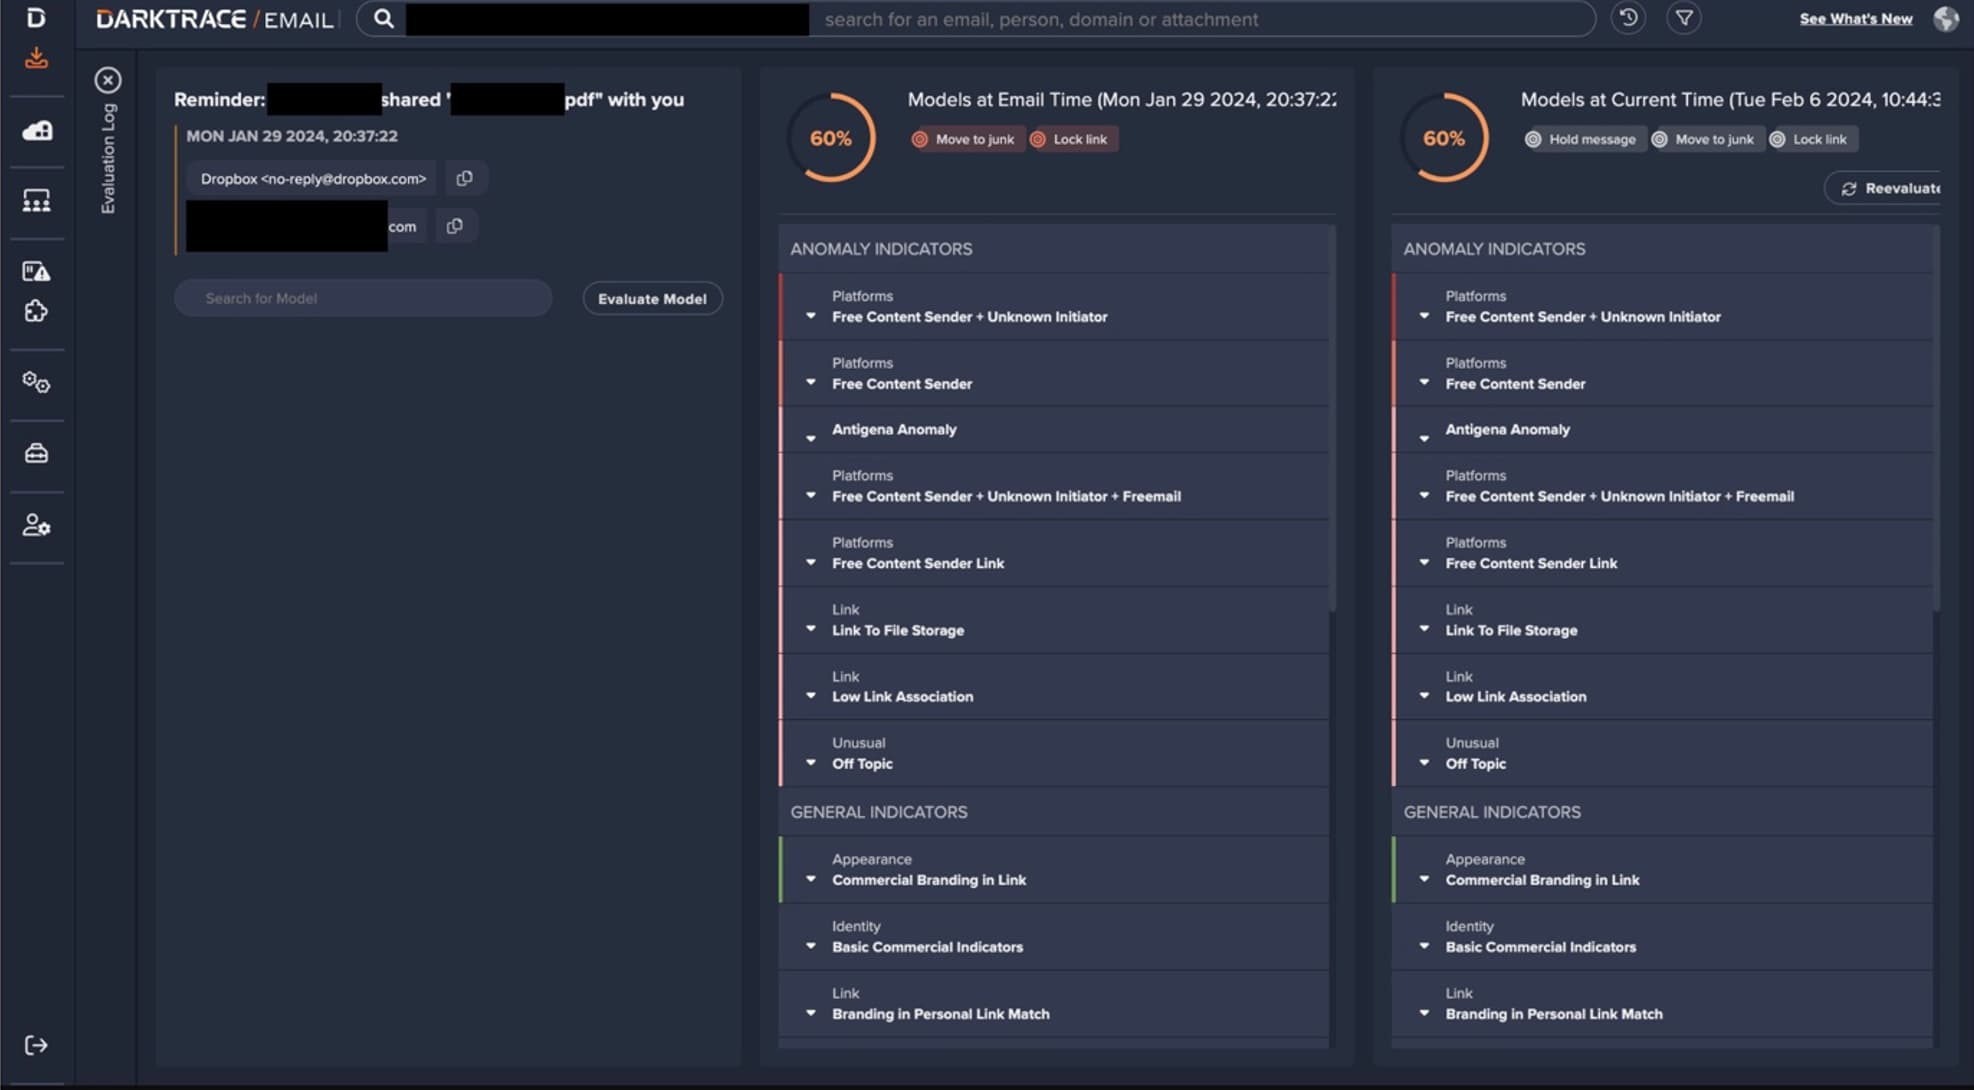
It’s been observed that attackers send seemingly harmless emails originating from a legitimate Dropbox address, containing a malicious link. On January 25, 2024, researchers detected a suspicious email sent to 16 internal users of the Darktrace SaaS environment, originating from a legitimate email address- ‘no-reply@dropboxcom’. 

Dropbox Abused in New Phishing, Malspam Scam to Steal SaaS Logins
Screenshot credit: Darktrace

The email contained a link to a PDF file hosted on Dropbox, possibly named after a Dropbox partner organization. The PDF file contained a suspicious link to a domain named ‘mmv-securitytop.’ Darktace’s email security tool detected and held the email, but a user received another email from a legitimate no-reply@dropboxcom on January 29, requesting to open the previously shared PDF file.

“Darktrace/Email moved the email to the user’s junk file and applied a lock link action to prevent the user from directly following a potentially malicious link,” but couldn’t prevent the damage because an employee clicked on the link.

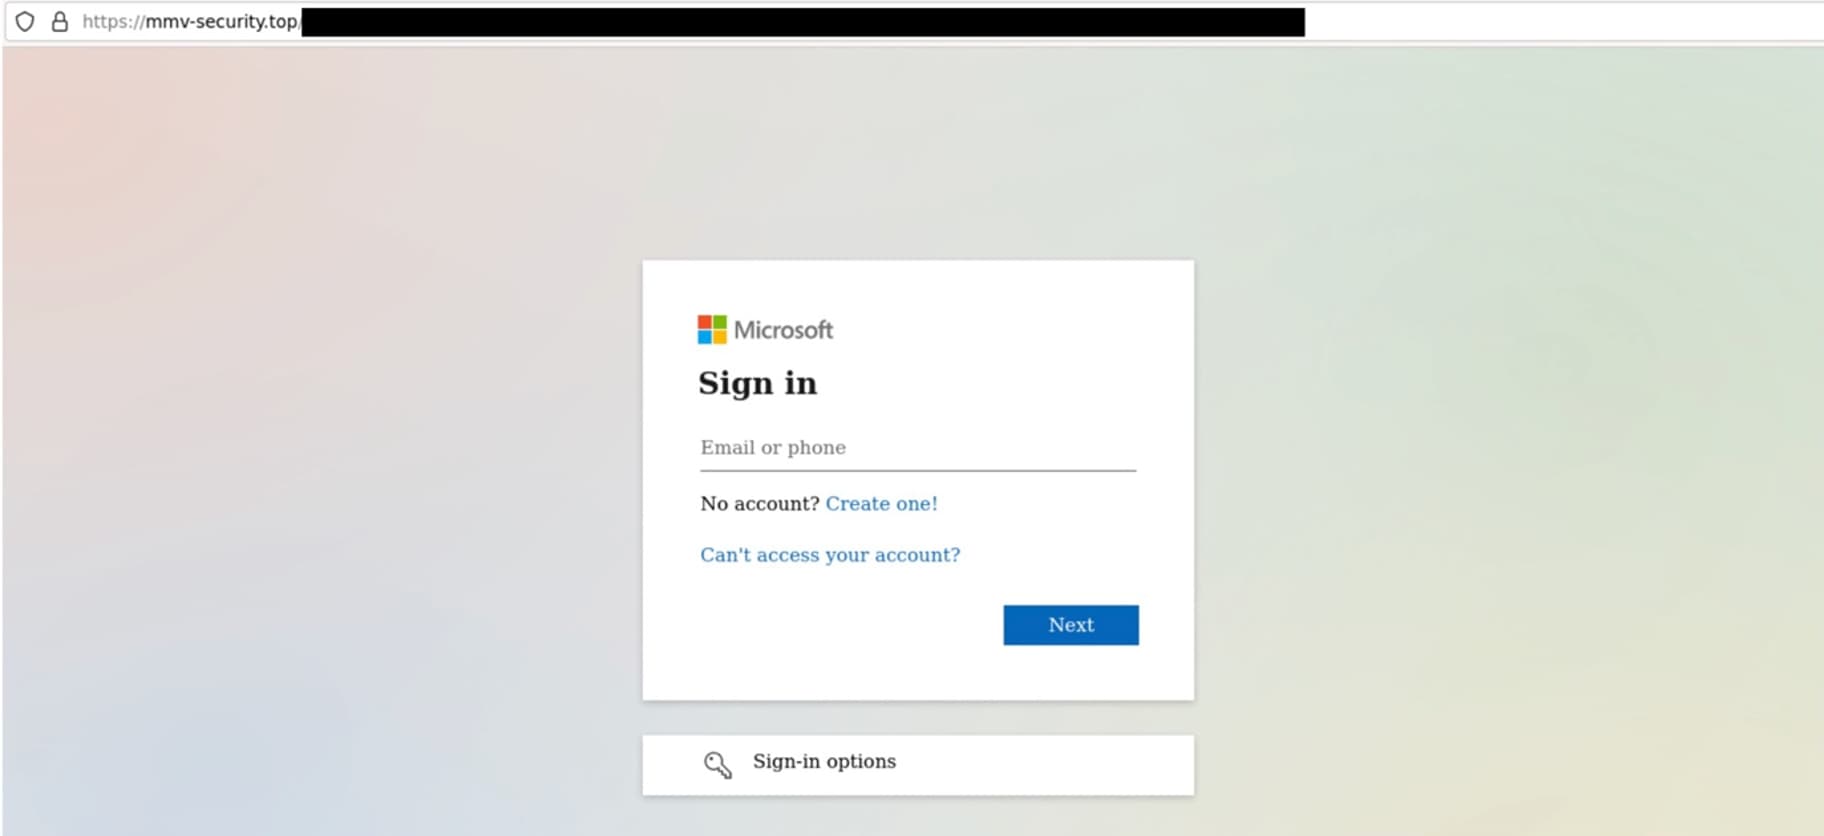
Next, the user’s device got connected to a malicious endpoint, ‘mmv-securitytop’, leading to a fake Microsoft 365 login page. These credential harvesters, disguised as trusted organizations like Microsoft, increase the likelihood of stealing privileged SaaS account credentials. 

Dropbox Abused in New Phishing, Malspam Scam to Steal SaaS Logins
The fake Microsoft login page – Screenshot credit: Darktrace

Since January 31, Darktrace observed suspicious SaaS activity, including logins from unusual locations and endpoints associated with ExpressVPN, suggesting threat actors are using a VPN to mask their true location.

An interesting finding was that threat actors bypassed a customer’s MFA policy using valid tokens and meeting authentication requirements. An additional login was observed from 87.117.225155, using the HideMyAss VPN service.

According to Darktrace’s blog post, the actor created a new email rule, ‘….’, to move emails to the ‘Conversation History’ mailbox folder, a tactic used by threat actors during phishing campaigns. This generic name helps maintain undetected activity on target networks.

Dropbox exploitation is gaining popularity among threat actors, as it is difficult to detect foul play because emails are sent from legitimate addresses. In September 2023, Hackread.com reported a BEC 3.0 attack campaign leveraging Dropbox to send emails redirecting users to credential-harvesting pages.

Clicking on malicious links in phishing emails can lead to malware infections, stealing of sensitive data, and compromising login credentials. In business settings, a single employee’s account can allow attackers to access the entire SaaS environment, thereby disrupting operations.

Protection Against Phishing Attacks

While relying on common sense is typically the best defence against such attacks, scammers’ increasing sophistication can sometimes override our natural caution. Therefore, it’s crucial to proactively protect yourself. Here are 5 key points to help you recognize and safeguard against email phishing:

Suspicious Sender Addresses and Email Content:

  • Check sender email addresses carefully for typos or misspellings of legitimate companies.
  • Be wary of generic greetings or an impersonal tone.
  • Look for grammatical errors or unusual phrasing in the email body.
  • Watch out for emails with a strong sense of urgency or pressure to act quickly.

Malicious Links and Attachments:

  • Never click on links or open attachments in emails from unknown senders.
  • Hover over a link to see the actual destination URL before clicking. It might not match the displayed text.
  • Don’t download attachments you weren’t expecting, even from seemingly familiar senders.

Phishing for Information:

  • Phishing emails often try to trick you into revealing personal information like passwords or credit card details.
  • Legitimate companies will never ask for such information via email.

Multi-Factor Authentication (MFA) and Strong Passwords:

  • Although, in this case, scammers bypass MFA, it is still the most preferred way to protect suspicious logins.
  • Enable MFA on all your online accounts whenever possible. This adds an extra layer of security beyond just your password.
  • Use strong, unique passwords for all your online accounts and avoid using the same password for multiple accounts.

Staying Informed and Reporting Phishing Attempts:

  • Keep yourself updated on the latest phishing tactics by reading security blogs or news articles.
  • Report suspicious emails to your email provider or the platform it impersonates. This helps them track and block future phishing attempts.
  1. How Human Elements Impact Email Security
  2. Microsoft Teams Flaw Sends Malware to Employees’ Inboxes
  3. Employee Duped by AI-Generated CFO in $25.6M Deepfake Scam
  4. ALPHV Ransomware Used Vishing to Scam MGM Resorts Employee
  5. MoleRats using Facebook, Dropbox, Google Docs to spread malware
  6. A Tricky PayPal Phishing Scam That Comes From Official PayPal Email

[ad_2]
Source link

Cybercriminals Hacking Systems with 10+ Legitimate Data-Extraction Tools

0
[ad_1]

In recent months, the cybersecurity landscape has witnessed a significant evolution in ransomware attacks, with perpetrators deploying an increasingly diverse array of data-exfiltration tools.

Symantec’s latest findings reveal that attackers have utilized at least a dozen different tools for data exfiltration in the past three months alone.

This trend underscores a strategic shift towards leveraging malware and dual-use tools—legitimate software repurposed for malicious intent—to siphon data from victim organizations.

Document @import url(‘https://fonts.googleapis.com/css2?family=Poppins&display=swap’); @import url(‘https://fonts.googleapis.com/css2?family=Poppins&family=Roboto&display=swap’); *{ margin: 0; padding: 0; text-decoration: none; } .container{ font-family: roboto, sans-serif; width: 90%; border: 1px solid lightgrey; padding: 20px; background: linear-gradient(2deg,#E0EAF1 100%,#BBD2E0 100%); margin: 20px auto ; border-radius: 40px 10px; box-shadow: 5px 5px 5px #e2ebff; } .container:hover{ box-shadow: 10px 10px 5px #e2ebff; } .container .title{ color: #015689; font-size: 22px; font-weight: bolder; } .container .title{ text-shadow: 1px 1px 1px lightgrey; } .container .title:after { width: 50px; height: 2px; content: ‘ ‘; position: absolute; background-color: #015689; margin: 20px 8px; } .container h2{ line-height: 40px; margin: 2px 0; font-weight: bolder; } .container a{ color: #170d51; } .container p{ font-size: 18px; line-height: 30px; } .container button{ padding: 15px; background-color: #4469f5; border-radius: 10px; border: none; background-color: #00456e ; font-size: 16px; font-weight: bold; margin-top: 5px; } .container button:hover{ box-shadow: 1px 1px 15px #015689; transition: all 0.2S linear; } .container button a{ color: white; } hr{ / display: none; / }
Integrate ANY.RUN in your company for Effective Malware Analysis

Are you from SOC and DFIR teams? – Join With 400,000 independent Researchers

Malware analysis can be fast and simple. Just let us show you the way to:

  • Interact with malware safely
  • Set up virtual machine in Linux and all Windows OS versions
  • Work in a team
  • Get detailed reports with maximum data
  • If you want to test all these features now with completely free access to the sandbox:


Double Extortion: A Growing Threat

According to the Symantec report, Ransomware operators have adopted a more aggressive tactic known as double extortion. By stealing sensitive data before encrypting the victim’s files, attackers can exert additional pressure on organizations to pay the ransom.

This approach not only complicates recovery efforts for the affected entities but also increases the potential for reputational damage and regulatory scrutiny.

The Expanding Toolkit

Among the tools favored by ransomware actors, Rclone remains the most commonly used for data exfiltration.

most frequently used exfiltration tools

However, there is a noticeable rise in the use of remote administration and management tools like AnyDesk, ScreenConnect, and Atera.

  • Rclone: An open-source cloud management tool, sometimes exploited by ransomware actors for data theft.
  • AnyDesk: A remote desktop application that attackers use for unauthorized access, occasionally disguising it to avoid detection.
  • RDP (Remote Desktop Protocol): Developed by Microsoft, this protocol enables remote control of computers. Attackers often enable it through registry modifications and firewall rule adjustments to gain malicious access.
  • Cobalt Strike: A tool meant for penetration testing but commonly used by attackers for stealthy data exfiltration and establishing covert communications.
  • ScreenConnect: Remote desktop software by ConnectWise for computer access.
  • Atera: Remote monitoring software often utilized by attackers for network access.
  • WinRAR and similar utilities: Used by attackers for file archiving in preparation for data exfiltration.
  • Restic: An efficient and secure backup tool, exploited by ransomware groups like those using Noberus for data theft.
  • TightVNC: Open-source remote desktop software.
  • WinSCP: A legitimate FTP and SFTP client for Windows.
  • Pandora RC: Commercial remote access tool, sometimes used maliciously for information theft and deploying additional tools.
  • Chisel: An open-source proxy tool, abused in ransomware attacks for data tunneling to attacker-controlled sites.
  • PowerShell: A Microsoft scripting tool, exploited for various malicious activities including data exfiltration through commands like Compress-Archive.

These tools offer a blend of functionality that appeals to attackers, including the ability to act as a backdoor into compromised systems.

Case Study: Rclone in Action

A notable instance of Rclone’s misuse occurred during a RagnarLocker ransomware attack in July 2023. Attackers deployed Rclone to transfer data from network shares to external storage solutions, demonstrating the tool’s versatility in facilitating large-scale data exfiltration.

The initial sign of malicious behavior was the execution of PowerShell commands to deactivate Local Security Authority (LSA) protection.

Following this, the attackers utilized SoftPerfect Network Scanner (netscan.exe), a widely accessible tool, for identifying host names and network services.

On the subsequent day, their operations continued with the deployment of Mimikatz and LaZagne for credential theft.

They then employed several native tools to collect system data, backup registry hives, run commands remotely across the network, and activate Remote Desktop Protocol (RDP) to enable external access.

Protection and Mitigation Strategies

In response to these evolving threats, Symantec emphasizes the importance of robust cybersecurity measures. Organizations are advised to monitor outbound traffic for anomalies, restrict the use of dual-use tools, and implement strong identity and access management practices.

Additionally, maintaining up-to-date software and employing endpoint detection and response (EDR) tools can significantly enhance an organization’s resilience against ransomware attacks.

The diversification of data-exfiltration tools in ransomware campaigns highlights the need for continuous vigilance and adaptive security strategies.

As attackers refine their techniques, organizations must prioritize the detection and mitigation of these threats to safeguard their data and maintain operational integrity.

Indicators of Compromise

SHA-256 hashDescription
d5e01c86dab89a0ecbf77c831e4ce7e0392bea12b0581929cace5e08bdd12196Rclone
df69dc5c7f62c06b0a64c9b065c3cbe7d034af6ba14131f54678135c33806f3eRclone
2cbe4368f75f785bf53cbc52b1b357d6281dc41adc1a1aa1870e905a7f07ed5eRclone
e94901809ff7cc5168c1e857d4ac9cbb339ca1f6e21dcce95dfb8e28df799961Rclone
9b5d1f6a94ce122671a5956b2016e879428c74964174739b68397b6384f6ee8bRclone
aaa647327ba5b855bedea8e889b3fafdc05a6ca75d1cfd98869432006d6fecc9Rclone
9bbc9784ce3c818a127debfe710ec6ce21e7c9dd0daf4e30b8506a6dba533db4Rclone
64e0322e3bec6fb9fa730b7a14106e1e59fa186096f9a8d433a5324eb6853e01Rclone
de96a6e69944335375dc1ac238336066889d9ffc7d73628ef4fe1b1b160ab32cRclone
5cc2c563d89257964c4b446f54afe1e57bbee49315a9fc001ff5a6bcb6650393Rclone
8a878d4c2dff7ae0ec4f20c9ddbbe40b1d6c801d07b9db04597e46b852ea2dc5Rclone
6ad342fbfe679c66ecf31b7da1744cbf78c3dc9f4dbc61f255af28004e36a327Rclone
8e21c680dab06488014abca81348067753be97fd0413def630701019dea00980Rclone
f63ff9c6f31701c1dca42d47ca4d819645e8d47586cf375db170503ce92b777eRclone
d6c1e30368d7ed406f0a6c6519287d589737989e8ff1297b296054b64b646b3fRclone
109b03ffc45231e5a4c8805a10926492890f7b568f8a93abe1fa495b4bd42975AnyDesk
7d531afcc1a918df73f63579ca8d1a5c8048d8ac77917674c6805f31c8c9890fAnyDesk
734f3577aa453fe8e89d6f351a382474a5dab97204aff1e194eee4e9fdff0a4aAnyDesk
fc19f3275d02764cf249dc6fe8962e06b83a4f5769cc369bc4f77b90c567df18AnyDesk
e69f82a00ab0e15d2d5d9f539c70406cbfaffd2d473e09aab47036d96b6a1bc1AnyDesk
5b70972c72bf8af098350f8a53ec830ddbd5c2c7809c71649c93f32a8a3f1371AnyDesk
7bcff667ab676c8f4f434d14cfc7949e596ca42613c757752330e07c5ea2a453AnyDesk
cd37a69b013336637a1ee722a6c7c8fd27439cf36ac8ed7e29374bbe4a29643eAnyDesk
8cd552392bb25546ba58e73d63c4b7c290188ca1060f96c8abf641ae9f5a8383AnyDesk
ec33d8ee9c3881b8fcea18f9f862d5926d994553aec1b65081d925afd3e8b028AnyDesk
bbbedd933ac156b476e1b3edb3e09501c604a79c4ff1a917df779a9f1bec5ccaAnyDesk
7c20393e638d2873153d2873f04464d4bad32a4d40eabb48d66608650f7d4494AnyDesk
355faa21f35d4a15c894445f09af97b2ad90604425b9a4b9076e293dbd4504abAnyDesk
580f6a285c6c3b7238bd16e1aeb62a077ae44b5061a2162e9fd6383af59028bbAnyDesk
af61905129f377f5934b3bbf787e8d2417901858bb028f40f02200e985ee62f6AnyDesk
4de898c139fb5251479ca6f9ec044cac4d83a2f5d1113b7a4b8f13468a130c97AnyDesk
d928708b944906e0a97f6a375eb9d85bc00de5cc217d59a2b60556a3a985df1eAnyDesk
cdb82be1b9dd6391ed068124cfdf2339d71dd70f6f76462a7e4a0fdadd5a208aCobalt Strike
0242c29a20e19a4c19ff1e5cc7f28a8af3c13b6ec083d0569b3ba15a02c898b6Cobalt Strike
9242846351a65655e93ed2aeaf36b535ff5b79ddf76c33d54089d9005a66265bCobalt Strike
935c1861df1f4018d698e8b65abfa02d7e9037d8f68ca3c2065b6ca165d44ad2Cobalt Strike
8d6a398f97d734412de03340bbb8237d00c519479649af8933afb8fb4fa2f695Cobalt Strike
837fa64038a1e46494b581020606c386fbd79898aab9f38f90df8cfa7d4599ecCobalt Strike
3cc56d5b79877a8ee6d15f0109d1c59937d6555ae656924686cafeee36ec0d57Cobalt Strike
3e2bda57454efa2e87ae4357f5c6c04edafa6b1efcda8093cbfd056a211d0f39Cobalt Strike
840e1f9dc5a29bebf01626822d7390251e9cf05bb3560ba7b68bdb8a41cf08e3Cobalt Strike
6cf60c768a7377f7c4842c14c3c4d416480a7044a7a5a72b61ff142a796273ecCobalt Strike
5adfef3f7721d6616650711d06792c087fd909f52435c8124c5f940f7acbdb48Cobalt Strike
270c888f8fbeb3bdc2dbcf8a911872791e05124d9bd253932f14dc4de1d2aed2Cobalt Strike
6c5338d84c208b37a4ec5e13baf6e1906bd9669e18006530bf541e1d466ba819Cobalt Strike
0f4fa41c4ab2ac238cbe92438cb71d139a7810c6c134b16b6c6005c4c5b984e4Cobalt Strike
b53f3c0cd32d7f20849850768da6431e5f876b7bfa61db0aa0700b02873393faCobalt Strike
c4753ca743f0bfa82590e9838ad48af862814052e5c90a6dab97c651942a9d61Cobalt Strike
040f59f7e89787ee8db7ba44a11d7ed2ce9065ac938115933ca8cb37bb99abc5Cobalt Strike
89a09433e0a57d8c01d5bab4ef4e6def979d2bc8e1ffad47ee6eadd3b85d09e9Cobalt Strike
64dd55e1c2373deed25c2776f553c632e58c45e56a0e4639dfd54ee97eab9c19Cobalt Strike
523dcd9d9b971a8b4c53b5cfd9a003d7fcc0e6a4e0a06039db7f87ba7fb0a167Cobalt Strike
664bb48bf3e8a7d7036e4b0029fa10e1a90c2562ad9a09a885650408d00dea1bCobalt Strike
461ba29d9386de39071d8f2f7956be21fb4fa06df8dd1db6dec3da0982e42f9fCobalt Strike
d551b4f46ad7af735dfa0e379f04bdb37eda4a5e0d9fe3ea4043c231d034176cCobalt Strike
8b23414492ebf97a36d53d6a9e88711a830cbfb007be756df4819b8989140c2dCobalt Strike
a8611c0befdb76e8453bc36e1c5cfea04325e57dffb21c88760c6e0316319b36Cobalt Strike
d4e9986e9ad85daae7fabd935f021b26d825d693209bed0c9084d652feef0d77Cobalt Strike
a7f477021101837696f27159031c27afec16df0a92355dfe0eb06e8b23bff7f6Cobalt Strike
00be065f405e93233cc2f0012defdcbb1d6817b58969d5ffd9fd72fc4783c6f4Cobalt Strike
3f0256ae16587bf1dbbd3b25a50f972883ae41bce1d77f464b2a5c77fd736466Cobalt Strike
e2a5fb1ca722474b76d6da5c5b1d438a1e58beca52864862555c9ab1b533e72dScreenConnect
ea38cff329692f6b4c8ade15970b742a9a8bb62a44f59227c510cb2882fa436fScreenConnect
d7267fe13e073dcfe5b0d319e41646a3eb855444d25c01d52d6dab9de695e1b1ScreenConnect
91605641a4c7e859b7071a9841d1cd154b9027e6a58c20ec4cadafeaf47c9055ScreenConnect
df28158ea229ab67f828328fc01ea7629f3b743ecea8c0b88fba80cd7efc3a75ScreenConnect
5778bf9e4563a80ec48e975eaa81fd6fe2f4b504ffcd61fcfbceb65a45eb8345ScreenConnect
bcaa3d8dcba6ba08bf20077eadd0b31f58a1334b7b9c629e475694c4eeafd924ScreenConnect
d40ae98a7d18c2c35c0355984340b0517be47257c000931093a4fc3ccc90c226ScreenConnect
935c1861df1f4018d698e8b65abfa02d7e9037d8f68ca3c2065b6ca165d44ad2Atera
d0ceb18272966ab62b8edff100e9b4a6a3cb5dc0f2a32b2b18721fea2d9c09a5Atera
840e1f9dc5a29bebf01626822d7390251e9cf05bb3560ba7b68bdb8a41cf08e3Atera
cef987a587faded1a497d37cf8d1564a287ef509338dbd956ea36c8e6aa9a68eAtera
bc866cfcdda37e24dc2634dc282c7a0e6f55209da17a8fa105b07414c0e7c527Atera
3a3fe8352e0a2bca469dba0dc5922976d6ba4dc8b744ac36056bfb25dbf7fc68Atera
8258756c2e0ca794af527258e8a3a4f7431fbd7df44403603b94cb2a70cb1bdfAtera
b99d61d874728edc0918ca0eb10eab93d381e7367e377406e65963366c874450Atera
486b2c2b0ca934ab63a9cf9f4b660768ad34c8df85e6f070aec0b6a63f09b0d8Atera
6f88fb88ffb0f1d5465c2826e5b4f523598b1b8378377c8378ffebc171bad18bAtera
ec436aeee41857eee5875efdb7166fe043349db5f58f3ee9fc4ff7f50005767fAtera
5d8f9cf481d72c53438cdfff72d94b986493e908786e6a989acad052d1939399Atera
5157d2c1759cb9527d780b88d7728dc4ba5c9ce5fddff23fb53c0671febb63bcAtera
de96a6e69944335375dc1ac238336066889d9ffc7d73628ef4fe1b1b160ab32cAtera
9a7c58bd98d70631aa1473f7b57b426db367d72429a5455b433a05ee251f3236Atera
ff79d3c4a0b7eb191783c323ab8363ebd1fd10be58d8bcc96b07067743ca81d5Atera
35e6742e840490ee8ccfbbccacd5e7e61a1a28a2e23fb7b5083a89271a5fd400Atera
265b69033cea7a9f8214a34cd9b17912909af46c7a47395dd7bb893a24507e59WinRAR
f6c9532e1f4b66be96f0f56bd7c3a3c1997ea8066b91bfcc984e41f072c347baWinRAR
b1e7851bd2edae124dc107bec66af79febcb7bc0911022ac31b3d24b36b3f355WinRAR
8258756c2e0ca794af527258e8a3a4f7431fbd7df44403603b94cb2a70cb1bdfWinRAR
9e3c618873202cd6d31ea599178dd05b0ab9406b44c13c49df7a2cbc81a5caa4WinRAR
b99d61d874728edc0918ca0eb10eab93d381e7367e377406e65963366c874450WinRAR
d1144b0fb4e1e8e5104c8bb90b54efcf964ce4fca482ee2f00698f871af9cb72WinRAR
0244b889e1928a51b8552ab394f28b6419c00542a1bbc2366e661526790ec0a7WinRAR
0d068a6aa2df88613e1c5c7ba412a5a5bc3cadc3f3ab4b76d10035ba8eec27bfWinRAR
33f6acd3dfeda1aadf0227271937c1e5479c2dba24b4dca5f3deccc83e6a2f04Restic
99abf0d33e2372521384da3c98fd4a3534155ad5b6b7852ebe94e098aa3dc9b8TightVNC
366f5d5281f53f06fffe72f82588f1591191684b6283fb04102e2685e5d8e95cWinSCP
eea7d9af6275c1cbf009de73a866eac4bc5d0703078ffe73b0d064cca4029675WinSCP
2e64bf8ca66e4363240e10dd8c85eabbf104d08aba60b307435ff5760d425a92Pandora RC
40c81a953552f87de483e09b95cbc836d8d6798c2651be0beba3b1a072500a15Chisel
d3b125f6441485825cdf3e22e2bfdeda85f337e908678c08137b4e8ef29303dbChisel
b9ef2e948a9b49a6930fc190b22cbdb3571579d37a4de56564e41a2ef736767bChisel
9b78a7d8fd95fe9275c683f8cca54bc6c457b2cb90c549de227313a50da4fc41Chisel
7ef2cc079afe7927b78be493f0b8a735a3258bc82801a11bc7b420a72708c250

The post Cybercriminals Hacking Systems with 10+ Legitimate Data-Extraction Tools appeared first on GBHackers on Security | #1 Globally Trusted Cyber Security News Platform.


[ad_2]
Source link

Vulnerability in 16.5K+ VMware ESXi Let Attackers Execute Code

0
[ad_1]

VMware’s ESXi, Workstation, and Fusion products could allow attackers to execute malicious code on affected systems.

Impacted VMware Products

These vulnerabilities impact the following VMware products:

  • VMware ESXi
  • VMware Workstation Pro / Player (Workstation)
  • VMware Fusion Pro / Fusion (Fusion)
  • VMware Cloud Foundation (Cloud Foundation)

VMware has acknowledged the presence of several vulnerabilities in its products after they were privately reported.

Document
Integrate ANY.RUN in your company for Effective Malware Analysis

Malware analysis can be fast and simple. Just let us show you the way to:

  • Interact with malware safely
  • Set up virtual machine in Linux and all Windows OS versions
  • Work in a team
  • Get detailed reports with maximum data
  • If you want to test all these features now with completely free access to the sandbox:

The company has released updates to address these issues in the affected software.

While each vulnerability is rated as ‘Important,’ their combined potential impact escalates to ‘Critical’ severity.

Shadowserver has tweeted a warning about vulnerabilities in VMware ESXi instances.

These vulnerabilities can enable a malicious actor with local admin privileges to bypass sandbox protections.

Shadowserver is conducting scans and sharing its findings to help mitigate the risks associated with these vulnerabilities.

Use-After-Free Vulnerability in XHCI USB Controller (CVE-2024-22252)

A use-after-free vulnerability, CVE-2024-22252, has been found in the XHCI USB controller component of VMware ESXi, Workstation, and Fusion.

This flaw has been assigned a CVSSv3 base score of 9.3 for Workstation and Fusion and 8.4 for ESXi, indicating a critical threat level for the former and an important one for the latter.

Attackers with local administrative access to a virtual machine can exploit this vulnerability to run code as the VMX process on the host.

The attack is confined to the VMX sandbox for ESXi, but for Workstation and Fusion, it could lead to code execution on the host machine.

VMware advises users to apply the patches listed in the ‘Fixed Version’ column of their ‘Response Matrix.’

Workarounds are also provided for those who cannot immediately patch their systems.

Use-After-Free Vulnerability in UHCI USB Controller (CVE-2024-22253)

Another use-after-free vulnerability, CVE-2024-22253, affects the UHCI USB controller in the same VMware products.

It shares similar severity scores and attack vectors as CVE-2024-22252.

ESXi Out-of-Bounds Write Vulnerability (CVE-2024-22254)

VMware ESXi is also susceptible to an out-of-bounds write vulnerability, tracked as CVE-2024-22254, with a CVSSv3 base score of 7.9, falling into the ‘Important’ severity category.

An attacker accessing the VMX process could exploit this vulnerability to break out of the sandbox, leading to further unauthorized actions on the host system.

VMware has released patches to address this vulnerability, but no workarounds are available.

Users are urged to apply the updates as soon as possible.

Information Disclosure Vulnerability in UHCI USB Controller (CVE-2024-22255)

An information disclosure vulnerability, CVE-2024-22255, also exists in the UHCI USB controller, with a CVSSv3 base score of 7.1.

This could allow a malicious actor with administrative access to a virtual machine to leak memory from the VMX process.

VMware extends its gratitude to the security researchers from Team Ant Lab and TianGong Team of Legends at Qi’anxin Group, as well as VictorV and Wei of Team CyberAgent for their responsible disclosure of these vulnerabilities through the 2023 Tianfu Cup Pwn Contest.

VMware product users are strongly encouraged to review the provided documentation and apply the necessary patches to ensure their systems are protected against these vulnerabilities.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

DoNex Ransomware Observed in the Wild Targeting Enterprises

0
[ad_1]

Enterprises across the United States and Europe are on high alert as a new ransomware strain, dubbed “DoNex,” has been actively compromising companies and claiming victims.

This emergent threat has cybersecurity experts working overtime to understand the attack’s full scope and develop countermeasures.

The DoNex ransomware group has made its presence known by listing several companies as its victims on their dark web portal, accessible via the Onion network.

The group’s tactics are particularly insidious, employing a double-extortion method.

This not only involves the encryption of files, which are then appended with a unique.

VictimID extension, but also the exfiltration of sensitive data, holding it hostage to leverage additional pressure on the victims to pay the ransom.

Ransom Notes and Communication

Affected companies have discovered ransom notes named Readme.VictimID.txt on their systems, which instruct them to establish contact with the DoNex group through Tox messenger, a peer-to-peer instant messaging service known for its security and anonymity features.

Document
Integrate ANY.RUN in your company for Effective Malware Analysis

Malware analysis can be fast and simple. Just let us show you the way to:

  • Interact with malware safely
  • Set up virtual machine in Linux and all Windows OS versions
  • Work in a team
  • Get detailed reports with maximum data
  • If you want to test all these features now with completely free access to the sandbox:

The use of Tox indicates an attacker’s preference for secure communication channels, making it more challenging for law enforcement to track and intercept.

Broadcom recently spotted the emergence of a new ransomware actor, self-dubbed “DoNex,” which was detected in the wild during March.

Currently, the exact methods DoNex uses to infiltrate enterprise systems remain a mystery.

Cybersecurity teams diligently monitor the situation and conduct thorough investigations to uncover the group’s modus operandi.

Understanding the attack vectors is crucial for preventing further incidents and developing effective defense strategies.

A recent tweet by HackManac reported the emergence of a new ransomware group called Donex.

This group has already leaked data from 5 companies on their website.

Protection Against DoNex

Symantec, a leader in cybersecurity solutions, has identified protections against the DoNex ransomware through its products.

Symantec’s systems detect the threat in two ways:

  • File-based Detection: Known as Ransom. Darkrace, this signature-based detection is designed to catch known ransomware file indicators.
  • Machine Learning-based Detection: Labeled as Heur.AdvML.B!200, this advanced detection uses machine learning algorithms to identify and block ransomware behaviors that traditional signature-based methods may not catch.

The rise of the DoNex ransomware is a stark reminder of the evolving threat landscape.

Enterprises are advised to stay vigilant, ensure their security systems are up to date, and educate their employees on the risks of ransomware.

Regular backups and a robust incident response plan are also critical in mitigating the impact of such attacks.

As the situation develops, cybersecurity firms and law enforcement agencies are expected to issue further updates and advisories.

It is imperative for companies to monitor these communications and to collaborate with the cybersecurity community to defend against these and future ransomware threats.

With Perimeter81 malware protection, you can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits. All are incredibly harmful and can wreak havoc on your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

Shark Tank investor says he would buy TikTok to prevent the platform from getting banned in the U.S.

0
[ad_1]

Last week, a bipartisan House bill was introduced that could mean the end of popular video app TikTok in the U.S. The proposed legislation would ban TikTok in the states if its parent company, ByteDance doesn’t sell its interest in the app. ByteDance is a Chinese company and U.S. lawmakers are concerned about TikTok’s connection with China and fear that the company collects personal data from TikTok subscribers.

The bill was introduced by introduced by Reps. Mike Gallagher (R-Wis.) and Raja Krishnamoorthi (D-Ill.); the pair are the top lawmakers on the House Select Committee on the Chinese Communist Party. If the bill becomes law, ByteDance would have more than five months to divest itself of TikTok. If ByteDance stands pat, TikTok would become illegal to distribute from a U.S. app storefront or a web housing platform.
But according to The Hill, there is a deep-pocketed investor out there who said on Friday that he would buy the platform if it is going to get banned. Shark Tank investor Kevin O’Leary, who sold The Learning Channel to Mattel for $3.2 billion in 1999, said on Fox News that he will buy TikTok if the platform is about to get banned. “Not going to get banned, ’cause I’m gonna buy it,” O’Leary said on Fox News’ show “The Story.” He continued by saying, “Somebody’s going to buy it, it won’t be Meta and it won’t be Google, ’cause…regulator [will] stop that.”

The investor known sarcastically as Mr. Wonderful on ABC’s long-running Shark Tank television show said about TikTok, “This is worth billions, it’s one of the most successful advertising platforms in social media today. All my companies use it, I’ll buy it.”

TikTok spokesperson Alex Haurek told The Hill, “This bill is an outright ban of TikTok, no matter how much the authors try to disguise it. This legislation will trample the First Amendment rights of 170 million Americans and deprive 5 million small businesses of a platform they rely on to grow and create jobs.” President Joe Biden already said on Friday that if the bill makes it out of Congress, he will sign it.

By monthly average users, TikTok is the fourth largest social media platform in the world. It currently has over 1 billion monthly average users. Since its launch in 2016, the app has been installed over 3 billion times.


[ad_2]
Source link

Google Lens update will save your searched images to access later

0
[ad_1]
Google Lens, the visual search tool that is available as a standalone app and embedded into Google’s Pixel phones, is getting a major update. Soon, you’ll be able to save the images you analyze with Lens and easily revisit them whenever you’d like. This is a much-needed feature that users have been asking for.Previously, when you used Google Lens to search for information about an image, the image itself wasn’t saved. This meant you had to either take a separate photo with your camera app and then search with Lens or lose the visual content after your search was complete.

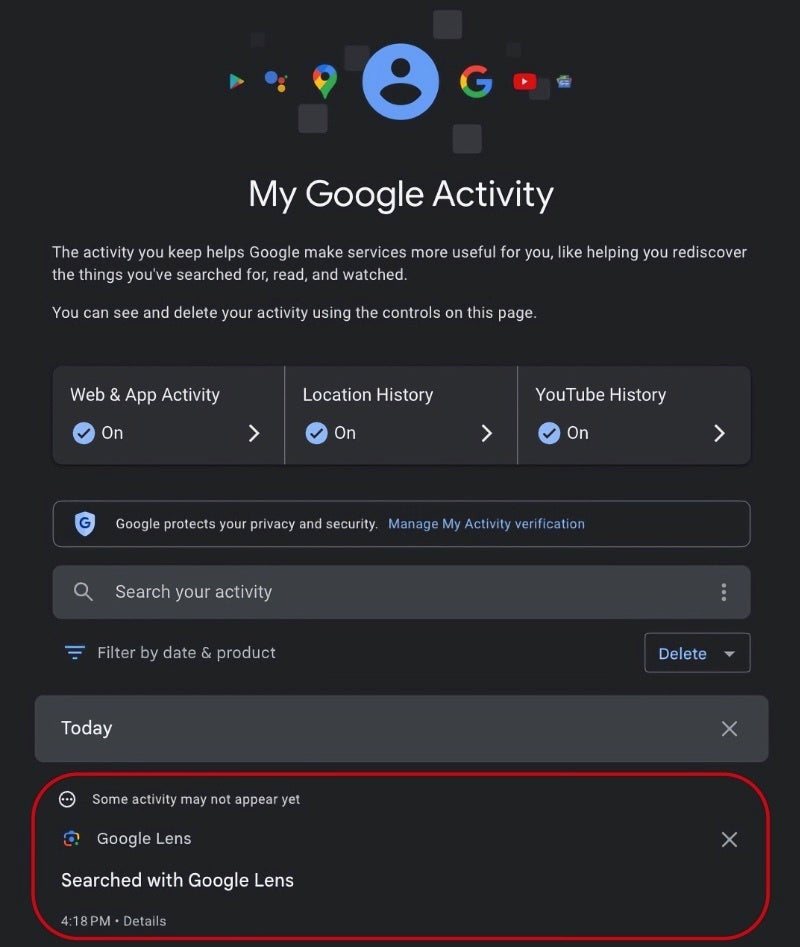
Now, as reported by 9to5Google, Google Lens can automatically save the images you search with it. You can always find them later by visiting myactivity.google.com. From there, you can even re-download the images if you want to run another Lens search or use them for something else. This eliminates the issue of having to go through several steps to capture and then identify an image with Lens and makes it easier to reference past searches in the future.


This change applies specifically to searches done with Google Lens within the Google app. Images analyzed through the Google Photos integration or other Lens features, such as Circle to Search, won’t be saved in this history.

The new feature is optional and will need to be turned on manually by navigating to your Google account settings, which can be found at myaccount.google.com. From there, enable the “Include Visual Search History” option under “Data & Privacy” > “Web & App Activity.”

The rollout of this new Visual Search History capability starts today and should reach all users within the coming weeks. Keep an eye out for a pop-up in Google Lens that will let you know when the feature is available for you.


[ad_2]
Source link

Hacker Claims Breaching US Federal Contractor Acuity, Selling ICE, USCIS Data

0
[ad_1]
Hacker Claims Breaching US Federal Contractor Acuity, Selling ICE, USCIS Data

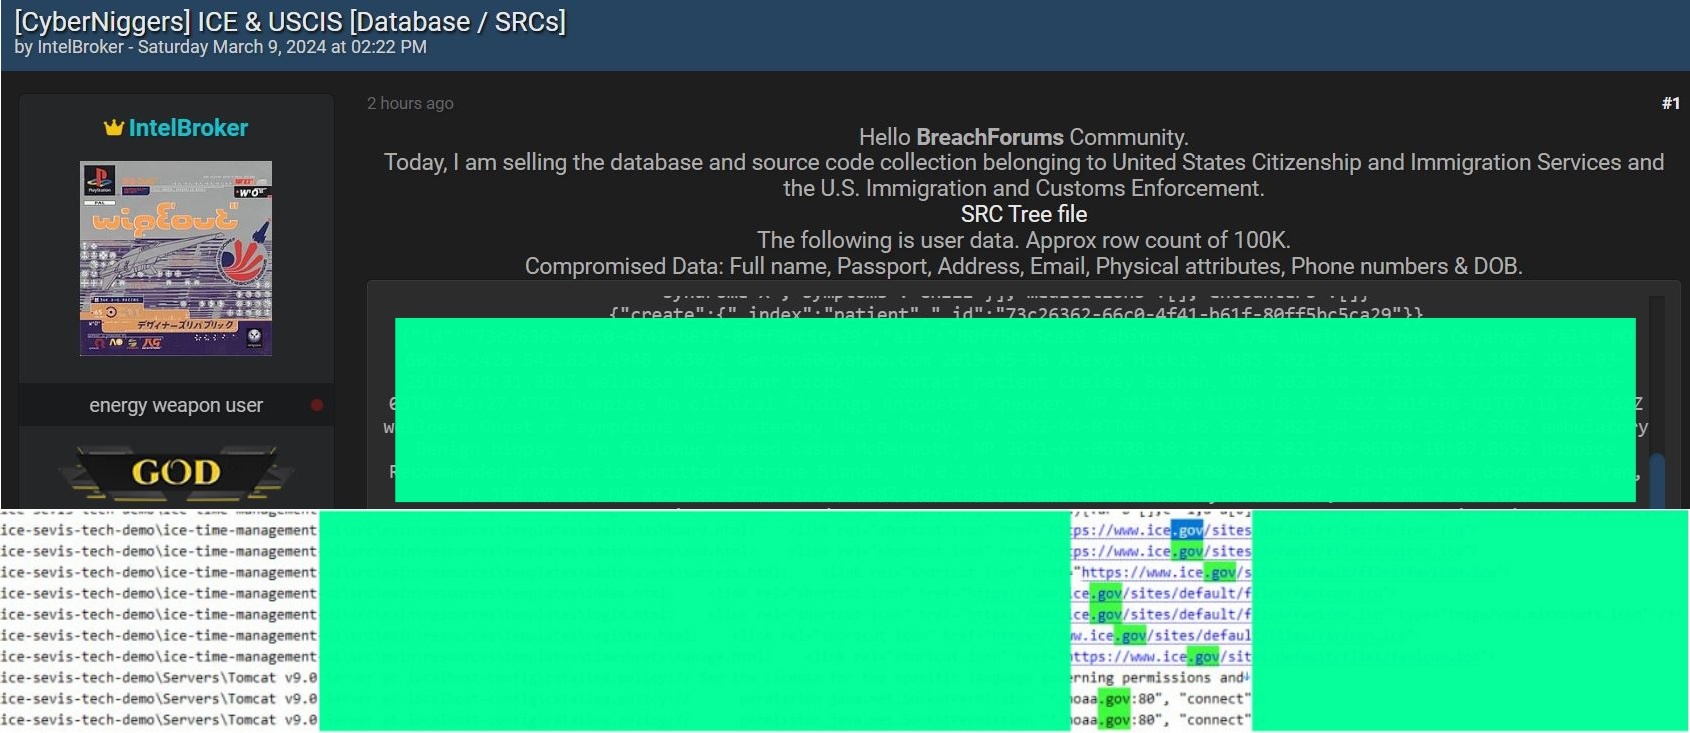
The IntelBroker hacker claims to have breached Acuity, a US federal contractor and is now selling data belonging to ICE and USCIS – This incident could potentially expose sensitive information of immigrants and could have national security implications.

The notorious hacker known as IntelBroker has claimed responsibility for a recent data breach allegedly targeting Acuity Inc., a Federal contractor based in Reston, Virginia. The breach has resulted in the theft of sensitive data and documents from two prominent U.S. government entities: U.S. Immigration and Customs Enforcement (ICE) and U.S. Citizenship and Immigration Services (USCIS).

For your information, Acuity Inc. is a federal technology consulting firm headquartered in Reston, Virginia. They offer their deep industry expertise to federal agencies, particularly those focused on National Security and Public Safety. According to the company, their core mission is to help these agencies plan for the future, improve their ability to serve citizens and deliver measurable results through innovative technology solutions and proven management techniques.

These alarming claims surfaced in a recent post on Breach Forums, a notorious cybercrime and hacker forum. Hackread.com has exclusively confirmed that the stolen data is currently being offered for sale on the forum for a mere $3,000 in Monero (XMR) cryptocurrency.

Screenshot: Hackread.com

Following the breach announcement on Breach Forums, IntelBroker proceeded to showcase a sample of the alleged stolen data, purportedly containing personal and Personally Identifiable Information (PII) of over 100,000 victims. The showcased records include:

  • Full names
  • Passport
  • Date of Birth
  • Phone numbers
  • Email addresses
  • Physical addresses
  • Physical attributes.

According to the hacker, “everything belongs to the US citizens,” implying that the compromised data contains information about civilians as well as government agents.

The Sensitive Nature of Data

In addition to the information available on the forum, Hackread.com gained insight into further sensitive data, including source code, user manual, confidential conversations and feedback exchanged between ICE agents and contractors. This extended to discussions on investigative techniques such as those utilized by the Five Eyes alliance, the Ukraine, and Russia conflict, information on terrorism-related seminars globally, etc.

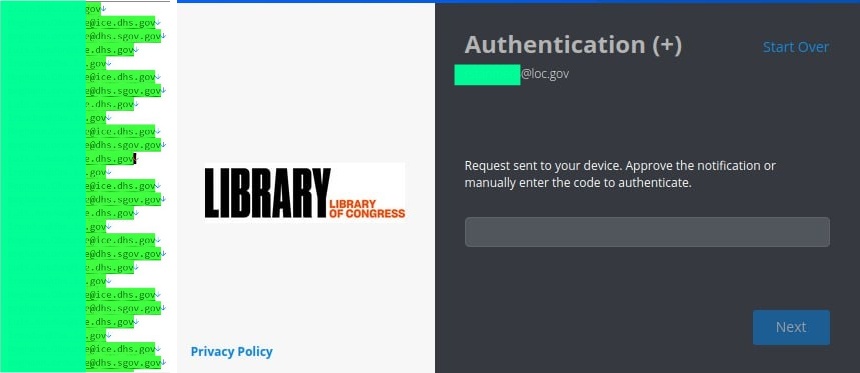
Moreover, the alleged compromised data includes .GOV-hosted emails containing plain-text passwords for some. It’s worth noting, however, that these accounts are protected by Two-factor Authentication (2FA), and any unauthorized attempts to access them are promptly blocked until a valid code is provided.

Leaked email addresses (left) and what happened when the hacker attempted to sign in (right) Screenshot: Hackread.com

Given the highly sensitive nature of this information, Hackread.com has refrained from sharing some screenshots and has redacted sample data accordingly. It’s essential to emphasise that, at no point, did Hackread.com attempt to access these accounts.

How did the alleged hack take place?

In an exclusive conversation with the hacker, Hackread.com learned that they had exploited a critical 0-day vulnerability in GitHub. Despite not disclosing technical details of the Proof of Concept (PoC) regarding the alleged vulnerability, the hacker claimed that this flaw enables attackers to steal GitHub tokens and advance their malicious activities.

In response to these developments, Hackread.com has initiated contact with GitHub, ICE, USCIS, and Acuity Inc. to request their comments on the matter.

Who is IntelBroker?

IntelBroker is known for targeting high-profile targets in the United States. Some of their previous data breaches include Las Angeles Intl. Airport, US DoD Documents, Staffing Giant Robert Half, Facebook Marketplace Database, DARPA-related accesses in General Electric breach, Weee! Grocery and several others.

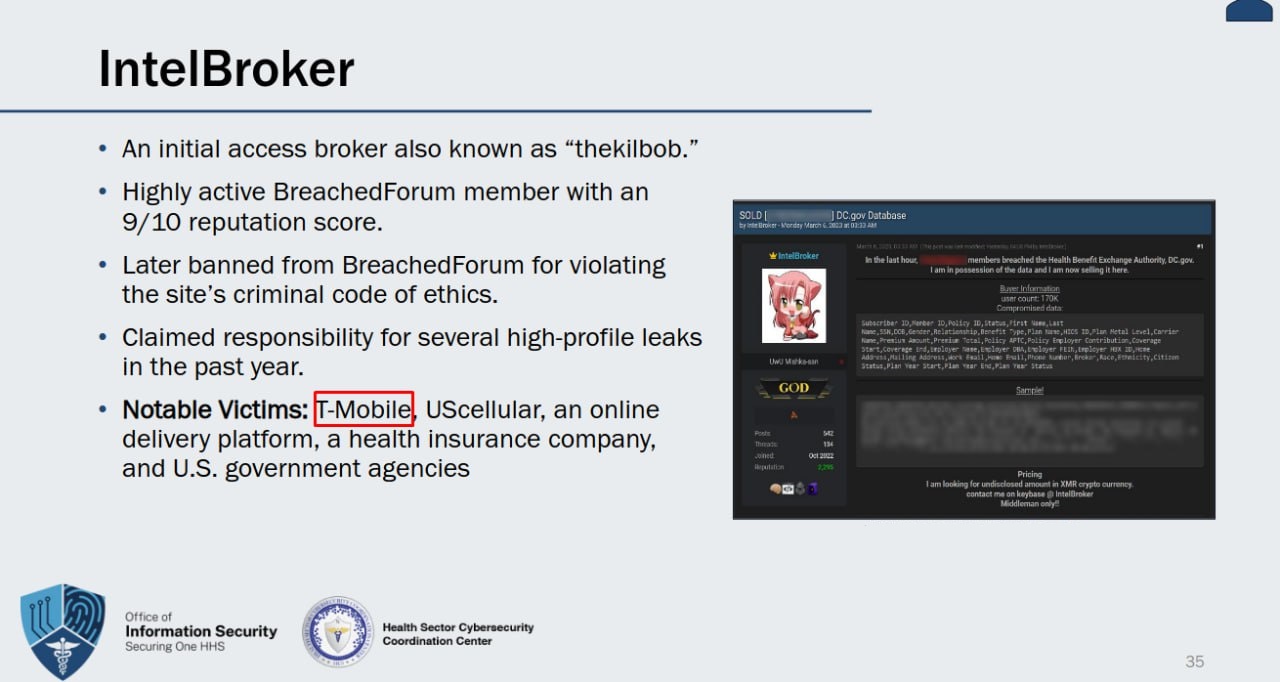
In fact, according to the United States government, IntelBroker is also the hacker behind one of the T-Mobile data breaches.

Aftermath of Acuity Inc.’s Alleged Breach

The aftermath of Acuity Inc.’s alleged breach carries potentially severe and long-lasting repercussions. The compromised data, if obtained by nations deemed adversarial by the United States, could pose significant risks to national security. The exploitation of such intelligence-related information may jeopardize the safety of agents and officials, as well as compromise ongoing operations.

Moreover, recent events highlight the vulnerability posed by third-party contractors. Just recently, on March 4th, 2024, American Express disclosed that its cardholders had been affected by a significant data breach originating from a third-party vendor.

In August 2023, an IT contractor employed by the Metropolitan Police Force experienced a cyberattack that impacted over 50,000 MET police personnel.

In September 2023, a third-party contractor experienced a data breach that affected over 8,000 Greater Manchester Police Officers. In October 2023, another contractor inadvertently exposed their database, resulting in the leakage of sensitive details about 500,000 Irish Police vehicle seizure records.

  1. US Govt’s secret terrorist watchlist with 2M records exposed online
  2. Chinese Group Storm-0558 Hacked European Govt Emails, Microsoft
  3. Adobe ColdFusion Flaw Used by Hackers to Access US Govt Servers
  4. Traffic sign near ICE headquarters hacked with “Abolish ICE” message
  5. Norweigian researcher exposes how a US firm collected his location data

[ad_2]
Source link

Chrome for Android will soon help you multitask with PiP web links within apps

0
[ad_1]
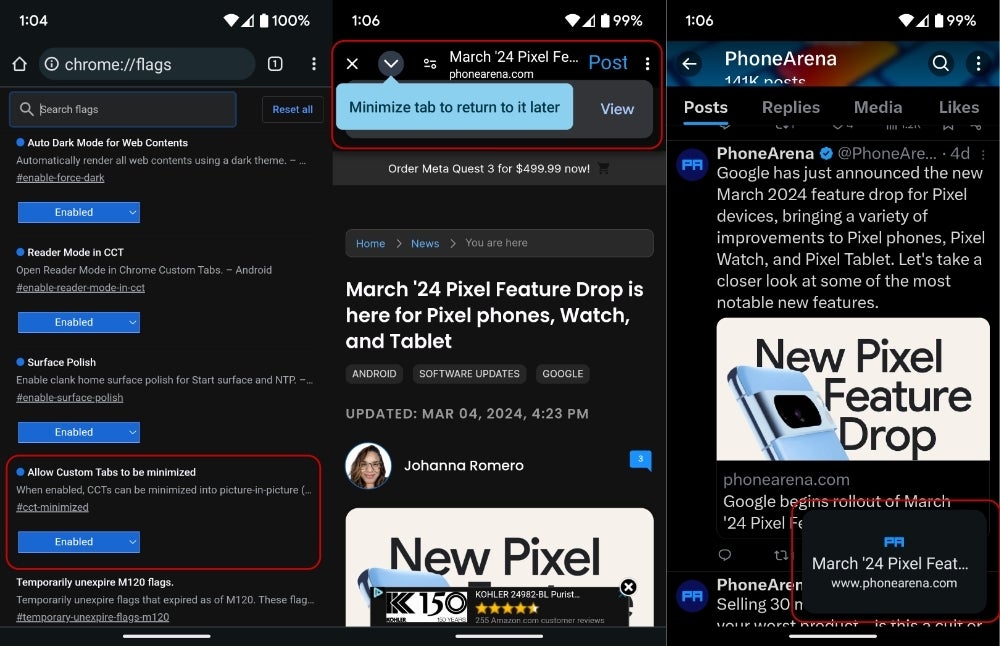
Chrome Custom Tabs were added to Android back in 2020 as a way to provide app developers and users with a way to have a customized browser experience within a specified app. The feature allows users to open web pages within the app without having to switch to a separate browser or using the old WebView method.However, even with the added convenience of having all the features of a full browser available within apps like X or Slack, for example, there were still some caveats when you wanted to still have access to the original post. Once you opened a web link within an app, you were stuck in that view, and the only way to see the original post again was by backing out of the web page. This will soon change.A new experimental flag has appeared in Chrome for Android, which Mishaal Rahman and Artem Russakovskii noticed. The flag named “Allow Custom Tabs to be minimized” allows you to minimize the webpage that loads within an app after clicking on a link, showing it as a small overlay at the bottom of the screen, picture-in-picture style. This view allows you to move back and forth to the web content without fully navigating away from the original post.
This feature can be currently enabled in the stable version of Chrome for Android by navigating to chrome://flags and searching for the #cct-minimized flag. However, we do not recommend doing this if you are not an experienced user (or a daredevil) simply because enabling experimental flags can sometimes break features, lead to crashes, or cause other issues with the browser.

Having said that, Chrome for Android Beta already has this feature turned on by default. It became available with version 122 and is at version 123 currently. The stable version of Chrome for Android is at version 122, so we shouldn’t have to wait much longer for this to become a standard feature for all users.


[ad_2]
Source link