The Andariel threat group was observed conducting persistent attacks against domestic businesses, specifically installing MeshAgent for remote screen control while conducting the attack.
MeshAgent collects basic system information for remote management and performs activities such as power and account management, chat or message pop-ups, file upload/download, and command execution.
It also has remote desktop support. In particular, the web supports remote desktop protocols like RDP and VNC.
“The attacker exploited domestic asset management solutions to install malicious code, most notably AndarLoader and ModeLoader”, AhnLab Security Intelligence Center (ASEC) shared with Cyber Security News.
Among the threat groups currently targeting Korea are the Andariel group, the Kimsuky group, and the Lazarus group.
As part of the initial access, it has also been known to launch supply chain, spear phishing, or watering hole attacks.
The malware is spread by taking advantage of installed software or flaws in the attack process.
Several Malware Backdoors Employed
AndarLoader is similar to Andardoor, discovered in an attack case that misused the Innorix Agent.
However, in contrast to Andardoor, the majority of the backdoor functions used by AndarLoader carry out the attacker’s commands via binary, executable data obtained from the C&C server, such as the .NET assembly.
“The AndarLoader confirmed this time is characterized by being obfuscated using KoiVM, unlike past types that were obfuscated with the Dotfuscator tool,” researchers said.
The attacker erased the compromised system’s security event log using AndarLoader and the command “wevtutil cl security.”
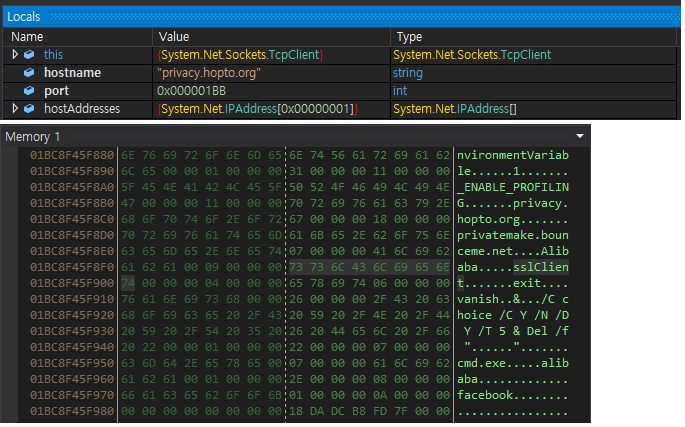
AndarLoader obfuscated with KoiVM
Additionally, MeshAgent gathers the fundamental system information needed for remote management.
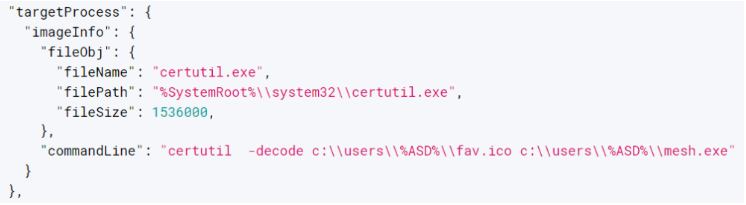
The use of MeshAgent by the Andariel group was first verified, and it was downloaded externally under the name “fav.ico.”
MeshAgent installation log
ModeLoader is a JavaScript malware that the Andariel group has been using nonstop in the past.
It is downloaded and run externally via Mshta rather than being created as a file.
“Attackers mainly exploit asset management solutions to execute the Mshta command that downloads ModeLoader”, researchers said.
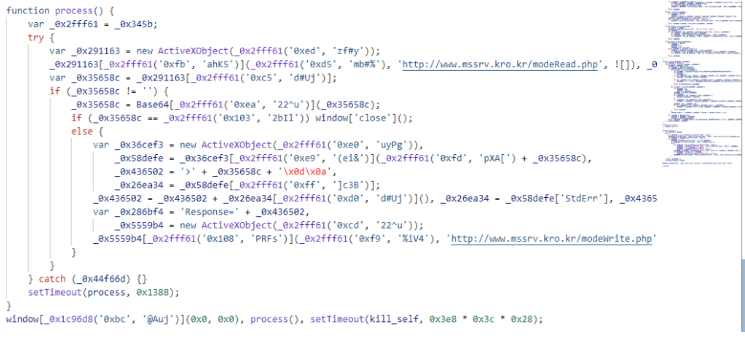
ModeLoader executing commands received from the C&C server
Researchers say the attack campaign verified a feature:
in the majority of attack cases, keylogger malware was also detected.
The malware records data copied to the clipboard and keylogger and offers keylogging functionality.
Users must exercise extra caution when opening executable files from websites or attachments to emails from unknown senders.
Corporate security employees ought to strengthen asset management solution monitoring and apply fixes when there are program security flaws.
Also, take precautions to avoid being infected by this kind of malware beforehand by updating the most recent patches and V3 for operating systems and web browsers.
With Perimeter81 malware protection, you can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits. All are incredibly harmful and can wreak havoc on your network.
Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.
Critical security flaws found in ChatGPT plugins expose users to data breaches. Attackers could steal login details and access sensitive data on third-party websites – Update your plugins now and only use extensions from trusted sources to stay safe from AI-driven cyber threats.
Salt Security, a leader in application programming interface (API) security, has discovered critical security vulnerabilities within popular plugins of OpenAI’s AI chatbot ChatGPT. These flaws may allow attackers to steal sensitive user data and gain unauthorized access to accounts on third-party websites or data retrieval from Google Drive.
This means ChatGPT plugin functionality, now known as GPTs, could be an attack vector, allowing vulnerabilities to access third-party user accounts, including GitHub repositories, and letting bad actors gain control of an organization’s account on third-party websites and access sensitive data.
For your information, ChatGPT plugins (exclusively accessible for users with a GPT-4 model, requiring a ChatGPT Plus subscription for utilization), are designed to enhance the chatbot’s capabilities by enabling it to interact with external services and be applicable across various domains. However, while using ChatGPT plugins, organizations may inadvertently permit them to send sensitive data to third-party websites and access private external accounts.
Three Vulnerabilities
According to Salt Labs research shared with Hackread.com ahead of publication on Wednesday, the company discovered three vulnerabilities within ChatGPT plugins.
First Vulnerability
The first was within ChatGPT itself, where users are directed to the plugin website to receive a code to be approved. Attackers can exploit this function to deliver users a code approval with a malicious plugin, allowing them to install their credentials on a victim’s account. Any message written in ChatGPT may be forwarded to a plugin and the attacker can then access proprietary information.
Second Vulnerability
The second vulnerability was identified in PluginLab, a framework used to develop ChatGPT plugins. Salt Labs found that PluginLab doesn’t implement proper security measures during the installation process, hence, allowing attackers to potentially install malicious plugins without users’ knowledge.
Since PluginLab did not authenticate user accounts, attackers can insert another user ID and gain a victim’s code, leading to account takeover. One affected plugin, “AskTheCode,” integrates between ChatGPT and GitHub, allowing attackers to access a victim’s account.
Third Vulnerability
Another vulnerability was OAuth redirection manipulation, allowing attackers to send malicious URLs to victims, and steal user credentials. Many ChatGPT plugins request broad permissions to access various websites. This means compromised plugins could potentially steal login credentials or other sensitive data from these third-party websites.
Following responsible disclosure practices, Salt Labs’ researchers collaborated with OpenAI and third-party vendors to promptly address issues before their exploitation in the wild.
This research highlights the growing prevalence of AI and its potential security risks. In January 2024, Kaspersky discovered over 3,000 dark web posts where threat actors discussed exploiting AI-powered chatbots like ChatGPT for developing similar tools to conduct cybercrimes.
Recently published Group-IB’s “Hi-Tech Crime Trends 23/24” report shows a surge in the use of AI by cybercriminals, particularly for stolen ChatGPT credentials, which can be used to access sensitive corporate data. Over 225,000 infostealer logs containing compromised ChatGPT credentials were detected between January-October 2023.
Therefore, users are advised to carefully review permissions, only install plugins from trusted sources, and regularly update ChatGPT and plugins. Developers should address code execution vulnerabilities to safeguard user data. PluginLab developers should implement robust security measures throughout the plugin development lifecycle.
Samsung is on a roll lately. The company is incessantly rolling out the March 2024 update for eligible Galaxy devices. Over the past few days, it has pushed the new security patch to over a dozen models. A few more are joining the party today. The new SMR (Security Maintenance Release) is available for the Galaxy S20 series and Galaxy A32 5G. It is also rolling out widely to the Galaxy Z Fold 5 and Galaxy Z Flip 5.
Galaxy S20 series grabs Samsung’s March 2024 update
As of this writing, Samsung’s March security update is available for the Galaxy S20, Galaxy S20+, and Galaxy S20 Ultra in Europe. Both 4G and 5G versions of the 2020 flagship phones are receiving the update. The new firmware build numbers are G98*FXXSJHXC1 and G98*BXXSJHXC1, respectively. A wider rollout covering the devices globally, including the US, should follow in the coming days.
The update brings 46 vulnerability fixes as part of Samsung’s March 2024 SMR. The company has combined 37 Android OS patches from Google with 9 Galaxy vulnerabilities it fixed on its own. At least two security issues patched this month are confirmed to be critical flaws. Threat actors can exploit these flaws to gain remote access to an affected Android or Galaxy device. You should update your phone as soon as possible.
Don’t expect the update to bring anything more to your Galaxy S20, though. The 2020 Samsung flagships are well past their prime. They have stopped receiving feature updates (didn’t get Android 14) and will soon fall out of the Korean firm’s security support list. It is about time you upgrade to a newer model. For the time being, make sure to update the phone to the new security patch. You can check for updates from the Settings app.
The aforementioned security fixes are also rolling out to the Galaxy A32 5G in Latin America. The device is picking up the latest update with the build number A326BXXSACXC5. Like the Galaxy S20 series, this mid-range phone is also no longer eligible for feature updates and will stop getting security patches in a year or so. Samsung may or may not release the March update for it in other regions.
Galaxy Z Fold 5 and Flip 5 are getting the new security patch globally
A few days back, Samsung released the March update for the Galaxy Z Fold 5 and Galaxy Z Flip 5 in the US. The new security patch is now rolling out to the two foldables globally. European versions of the phones are receiving the update with build numbers F946BXXS1BXBM and F731BXXS1BXBM, respectively. The duo will soon get the One UI 6.1 update with a host of new features.
eSIM has been around for quite some time, having been first released in 2016. But these days, it’s starting to get more and more popular. Now with the new iPhone 14 series going all-in on eSIM and not even offering a physical SIM card slot, it’s really going to take off. So we’re here to tell you everything you need to know about eSIM.
What is a SIM card?
You may already be familiar with a SIM card. Or a Subscriber Identity Module card, which is basically a little card that lives inside of your phone and essentially tells your phone what carrier you’re on and what plan you have. It’s a pretty simple thing, but necessary for every phone out there. It also makes switching phones and carriers pretty easy. Back in the 3G days with Sprint and Verizon using CDMA, you had to call and ask them to switch your phone – which they may or may not do very easily.
There are four sizes of SIM cards, there’s the full size, mini-SIM, micro-SIM and nano-SIM. These days, most phones use nano-SIM, while a few older phones might still use micro-SIM. The full size SIM was introduced in 1991, and five years later the mini-SIM was introduced. Then in 2003, we got the micro-SIM which we lived with for most of the 3G and early 4G generation of smartphones. With the nano-SIM being introduced in 2012.
What is eSIM?
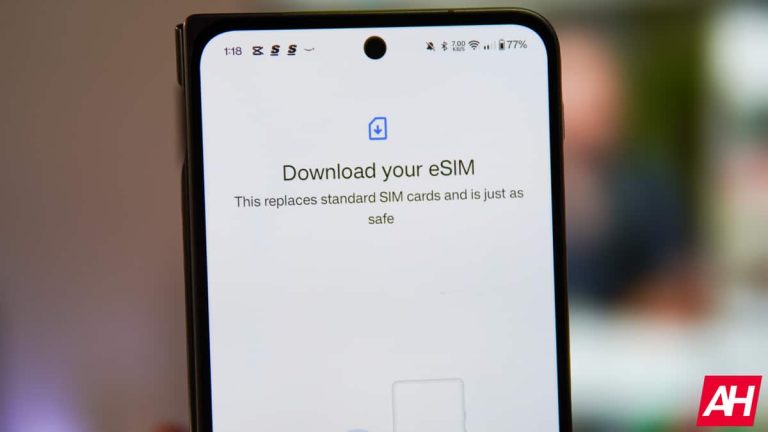
So now that we know what a SIM is, what is an eSIM? It’s an embedded-SIM, or a programmable SIM that is built into the phone and you’ll never see it. This has been available for things like cellular-connected smartwatches and some tablets. Some phones are compatible with eSIM as well.
eSIM was first introduced in 2016, so it’s still fairly new. The Samsung Gear S2 Classic 3G was the first device to use an eSIM. Apple first introduced eSIM back in September 2017 on its Apple Watch Series 3, and the following year on the iPhone XS.
Interestingly, some MVNO carriers like Google Fi use eSIM and prefer it over a regular SIM card. Likely because that’s one less thing they need to ship to the customer.
eSIMs give customers more flexibility for switching carriers. Which is something the carriers don’t like. Since you are able to just go into settings and add another carrier, of course you do need an account and plan with that carrier for it to really work.
What advantages does eSIM bring?
The biggest one is being able to switch carriers and phones at a moment’s notice. Of course, the switching phones thing is a small group of people – mostly reviewers like myself. But switching carriers will be more useful to others. Say you’re on AT&T and are fed up with their coverage and prices. You can sign up for Verizon and have your phone on Verizon’s network within a few minutes. Without heading to a store to get a SIM card or waiting for it to ship.
Another advantage is the environment. While SIM cards are fairly small these days, they do tend to break or just stop working. Typically after you’ve switched them between phones a few times. And thus end up in the trash, adding more waste to the environment. Carriers also have to keep tons of these in stock at every store across the country. So moving to eSIM means that’s one less thing they need to stock. Obviously a stack of a thousand SIM cards is still going to use less space than a Galaxy S22 Ultra box. But still.
Finally, with eSIM, it makes it easier to have multiple carrier plans on the same phone. This is really useful if you do any traveling outside of your country. So you can have your home carrier on your phone, and then a roaming carrier say in Europe, without having to pick up a SIM card when you land in that country. In some third-world countries like India, they typically use multiple carriers, because no one carrier has coverage everywhere. And this is very helpful there too.
What phones support eSIM?
Almost every phone these days supports eSIM, but many don’t market it as a feature. Every iPhone since 2018 with the iPhone XS, XS Max and XR have supported eSIM.
In 2017, Google unveiled the Pixel which was their first smartphone to have eSIM, and every Pixel since then has had it. This is partly because their own carrier, Google Fi, works with eSIM preferably over SIM.
Motorola started with eSIM in 2020 with the Motorola Razr. Motorola is a bit different from the others here, as they haven’t put eSIM in every phone. Since a big majority of their phones are cheaper ones.
Samsung started shipping the Galaxy S20 and Galaxy S21 with eSIMs in 2020. Though it’s not quite as straight-forward as some other manufacturers’ phones.
What tablets and smartwatches support eSIM?
As mentioned, the Samsung Gear S2 Classic 3G was the first watch to use a eSIM for cellular connectivity. Now, most watches that do have cellular connectivity use eSIM. That’s mainly due to the size of the smartwatch and the fact that there’s really not any room for a physical SIM card slot there.
So this mostly includes Samsung’s watches like the new Galaxy Watch 5 and 5 Pro, and Apple’s watches like the new Apple Watch Series 8, Ultra and SE (gen 2).
When it comes to tablets, every iPad since the iPad Pro 11-inch (1st Generation) released in 2018, has eSIM.
Which carriers support it?
Technically, all three US carriers support eSIM, some make it easier to use than others though. It’s not something they really market as a feature, and that’s because carriers don’t really like eSIM.
A lot of MVNO carriers also support eSIM. We’ve already mentioned Google Fi here, but there’s also Xfinity Mobile, Straight Talk and many more that also support eSIM.
How do you activate an eSIM?
It’s pretty easy to set up an eSIM on your device. Typically you’ll need to download and use your carrier’s app – which on most Android phones, that will be pre-installed. From there you’ll be asked to log into your account and then it’ll activate your eSIM. You can also opt to scan a QR code to get started in activating your eSIM.
Here’s the support pages for the three carriers on activating eSIM:
It’s pretty straight-forward, hopefully with the iPhones going eSIM exclusively in the US, that will mean that carriers will be more willing to support eSIM on their network.
Why do carriers dislike eSIM?
It’s pretty simple. Carriers hate making it easy for you to switch carriers. They want you to stick with their network and never leave. Though they are quite happy to get you to leave a competitor for their network. eSIM makes it super simple to switch networks, and that’s something that carriers do not like.
A big reason for that is because it eliminates needing to order a SIM card and head to your local store to pick it up, or wait for it to come in the mail, which can take a few days. Instead, you can be up and running with an eSIM in a matter of minutes.
The other big reason carriers hate eSIM is store traffic. Carriers rely pretty heavily on customers coming into their stores to drive sales of new phones, accessories and so much more. Carriers like Verizon sell just about everything you can think of now. They’ve become a small Best Buy in some sense. With eSIM, it eliminates the reason for most people to head to the Verizon, AT&T or T-Mobile store, though. This may change now, after the pandemic where the stores were closed for a few months.
Is eSIM the future?
Yes, eSIM is definitely the future. But moving to this new form of SIM is going to take some time. Moving from micro to nano SIM cards even took a few years, despite there really being no change, other than the size of the SIM card. But as we’ve said already in this post, with Apple going exclusively with eSIM on the iPhone 14 series, it’s going to push carriers to support eSIM, since iPhones are a big part of their sales and commissions. Not to mention a large part of the market in the US.
Typically, once Apple adopts some new technology, the rest of the industry adopts it too. But in this case, many have adopted it already, it’s just the carriers that aren’t embracing it. However, where there’s no other option for using a physical SIM card, carriers have no choice but to use it.
Following its declaration in a blog post last month, X (formerly Twitter) is once again affirming its status as a video first platform. As proof of this, X CEO Linda Yaccarino shared yesterday some interesting stats on how the platform is growing in the video sharing space.
Four out of every five user sessions on X include video consumption, according to the stats originally provided by the official @XData account. Furthermore, the account reported that the average annual growth rate for video views on X is 35%, and the average amount of time spent on video has increased by 17%. These are numbers that the company considers very promising, declaring that “the future of video on X is bright!”
X’s transition to a video-first platform has greatly transformed the social media environment. X was once known for its short-form text updates, but it now prioritizes video content in a variety of formats. The platform’s emphasis on immersive, short-form videos matches the efforts of competitors such as TikTok, which adapt to shifting audience preferences. This transition is also driving the growth of long-form videos on the platform, as X strives to compete with established platforms such as YouTube.
As a consequence of this shift, many content creators on X are now focusing their efforts on video. X’s algorithmic prioritization of video content is promoting this pattern, influencing how information is consumed on the site. Furthermore, the recent addition of video-focused features has opened up additional possibilities for income, attracting creators eager to capitalize on this opportunity.
While the shift towards video content has shown promise in increasing engagement and revenue, X still has a long way to go in order to maintain a healthy and trustworthy platform for both creators and users. Implementing robust moderation tools and fact-checking mechanisms might become crucial in ensuring the long-term success of this new direction.
In the wake of the LockBit ransomware group’s takedown, a shift has occurred within the cybercriminal underworld, leading to a sharp rise in activities by the Akira ransomware collective.
This group, known for its sophisticated attacks, particularly against healthcare entities in the US, has seen an influx of talent from the remnants of the notorious Conti group, specifically from its post-Ryuk faction.
The Rise of Akira Post-LockBit
Following the dismantling of LockBit, a notable vacuum was left in the ransomware landscape. Akira, a group previously operating in the shadows, has quickly stepped in to fill this gap.
According to cybersecurity firm RedSense, which has been closely monitoring these developments since the Summer of 2023, Akira has established deep ties with former members of the Conti group, especially those involved with the Ryuk ransomware.
Conti-Akira R&D Collaboration
The collaboration between Akira and the post-Conti group, particularly the developers behind Ryuk, has been pivotal.
The original creator of the Ryuk locker, known for his affinity for anime (hence the name “Akira”), has played a crucial role in supplying Akira with research and development insights.
This partnership was first identified during Royal’s research competition for a new locker, ultimately leading to the BlackSuit locker’s development.
Despite releasing a decryptor to counter Akira’s ransomware, the group saw a significant increase in compromised entities and successful encryptions during the summer of 2023.
This surge is attributed to the direct involvement of the Ryuk developer in Akira’s operations.
Yelisey Bohuslavskiy, co-founder of Redsense and advIntel, recently posted on LinkedIn about the sharp increase in threats from the Akira ransomware.
Following the takedown of LockBit, the Akira ransomware group is now attracting highly skilled post-Conti pen-testers targeting healthcare organizations in the United States.
The Emergence of “Ghost Groups”
Akira’s relationship with the post-Conti ecosystem has also led to the formation of “ghost groups,” such as Zeon, which previously aligned with Conti1 and played a significant role in deploying Ryuk.
In December, intelligence indicated that Zeon had been acting as a group of elite pen testers for Akira and LockBit, focusing primarily on the latter until its takedown.
The LockBit takedown has forced Zeon to redirect its efforts toward supporting Akira, leading to an expected increase in the sophistication and frequency of Akira’s ransomware attacks.
Recommendations & Mitigations
RedSense recommends several mitigation strategies to combat the rising threat from Akira and its associated groups.
These include prioritizing Remote Monitoring and Management (RMM) deployments, updating hypervisors and cloud backup frameworks, and implementing network segmentation and segregation to complicate these groups’ infiltration efforts.
Furthermore, awareness of specific Common Vulnerabilities and Exposures (CVEs) exploited by Zeon pentesters, such as CVE-2024-22252, CVE-2024-22253, and CVE-2024-22254 CVE-2024-22255, is crucial for defending against these sophisticated attacks.
As the cyber threat landscape continues to evolve, the rise of Akira in the post-LockBit era serves as a stark reminder of cyber criminals’ persistent and adaptive nature.
Vigilance and proactive cybersecurity measures are more important than ever to protect against these emerging threats.
With Perimeter81 malware protection, you can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits. All are incredibly harmful and can wreak havoc on your network.
Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.
There are hundreds of third-party apps that Mac endpoint use on a daily basis—and with that large number of apps comes a dizzying amount of software updates to apply on a rolling basis.
With VPM for Mac, Nebula and OneView users can now easily find missing updates and install them to take care of the large volume of software updates in third-party applications on Mac endpoints. Some key features include:
Single, lightweight agent: Updates install in minutes, using the same agent and cloud-based console that powers all ThreatDown endpoint security technologies.
Quick scans: Identifies software updates dates in modern and legacy applications in less than a minute.
Install software updates easily: Create a schedule to install third-party software updates regularly.
Let’s dive into how to set up software updates for Mac endpoints with ThreatDown VPM.
Configuring VPM for Mac
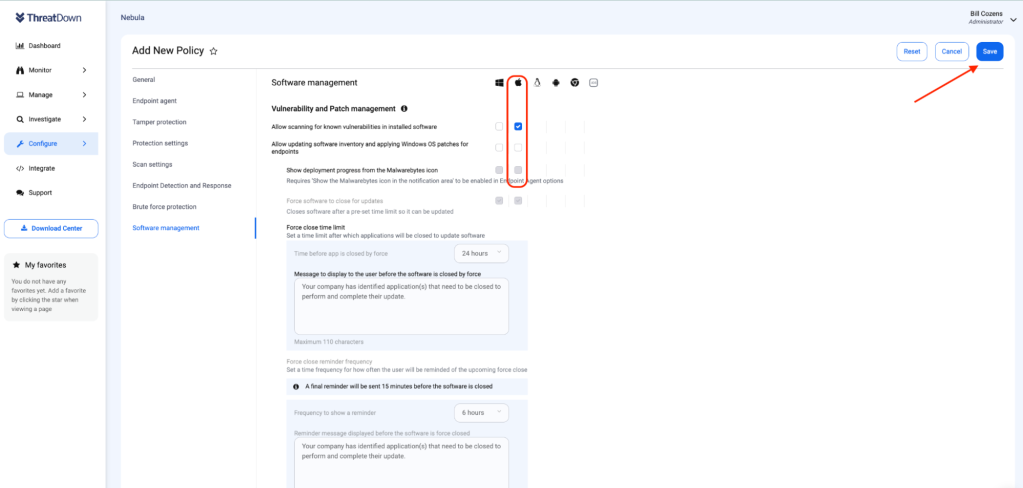
To configure VPM for Mac in Nebula/OneView:
Go to Configure > Policies
Create a new policy or select an existing policy.
Click the Software management tab.
Check mark Allow scanning for known vulnerabilities in installed software Mac endpoints.
Click Save.
In order to be able to apply software updates, users need to enable the policy setting Allow updating software inventory and applying Windows OS patches for endpoints for Mac.
Viewing outdated software
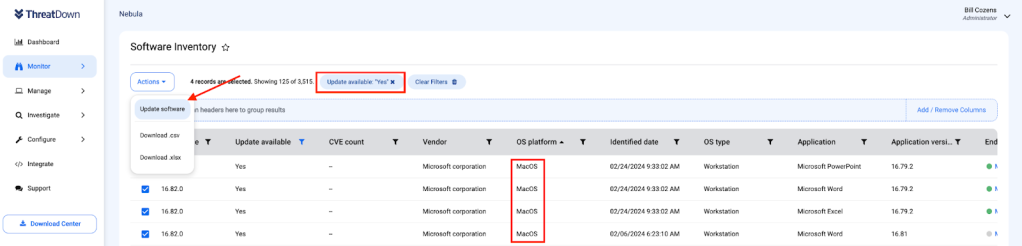
To view and update software:
Go to Monitor > Software Inventory page.
Filter Update available as Yes.
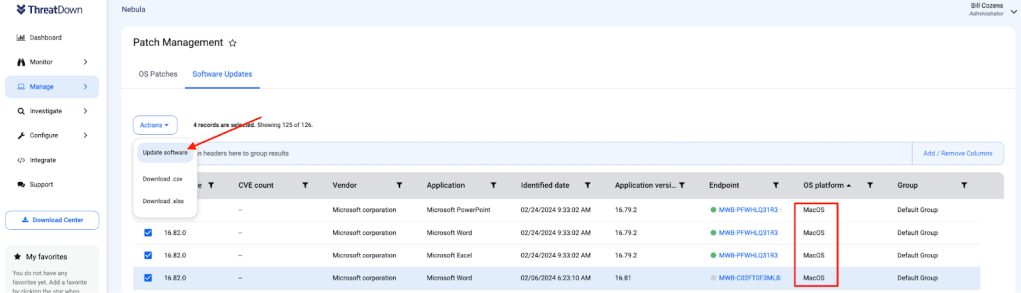
Click Actions.
Select Update Software.
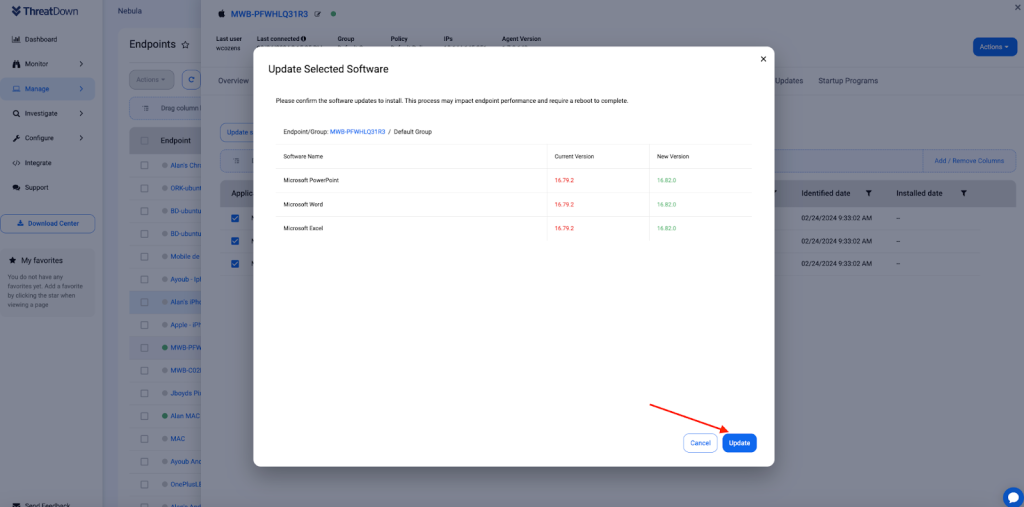
Click Update.
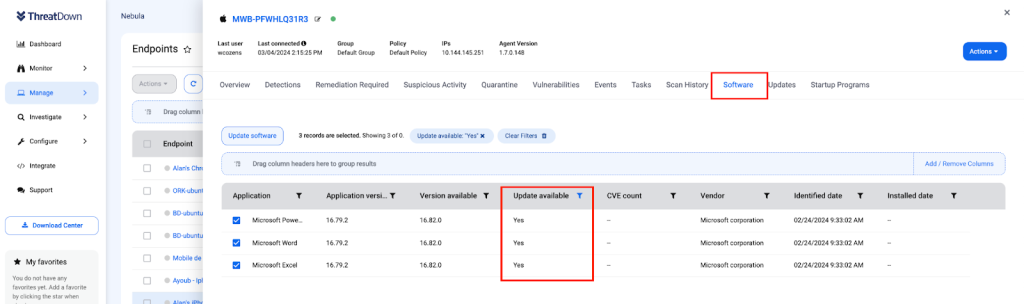
You can also view outdated software by endpoint by:
Click Manage > Endpoints
Select specific endpoint(s) under the Software tab.
Click Update Software.
Click Update.
Updating outdated software
To update outdated software, you can go directly to the Patch Management page as well:
Manage > Patch Management
Under Software Updates tab, select specific version(s) .
Click Actions.
Select Update Software.
Click Update.
Try VPM for Mac today
3rd party software updates for Mac endpoints is available on both Nebula and OneView for our Patch Management users or users on an Advanced bundles and above.
Starting March 13th, Spotify is integrating music videos into its library in 11 countries including Brazil, Colombia, Germany, Indonesia, Italy, Kenya, Netherlands, Poland, Philippines, Sweden, and UK. Spotify has reportedly been working on this addition since July last year. Notably, the music videos are currently further limited to premium subscribers who are in beta. Spotify says that they have chosen the markets based on the market size and availability of local content support.
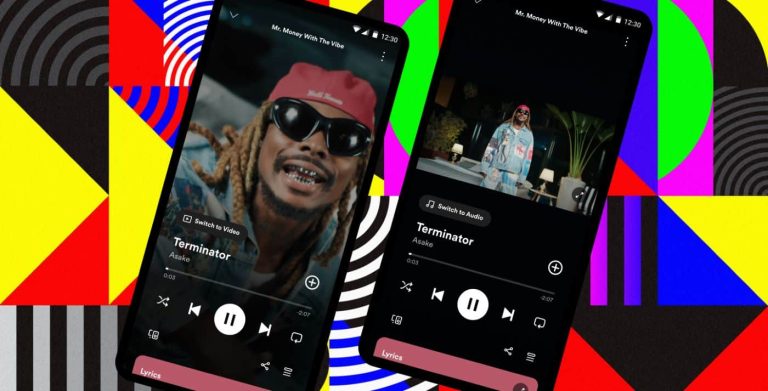
A “Switch to Video” button will appear on the “Now Playing” screen
If you happen to be from one of the countries and also meet the other criteria, you will see a “Switch to Video” button on the “Now Playing” screen for specific content. Clicking the button replaces the album image with the video, which starts playing from the beginning. You can rotate the phone to landscape and enjoy the video. The video is reportedly ad-free, unlike YouTube at least now in the testing phase. Just like how you switch to video, you also get an option to switch back to audio.
Notably, Spotify is hosting the music videos itself instead of working with any other service provider. Now you might have been thinking about royalties associated with the videos. Well, the music streaming giant was asked by TechCrunch about this matter, but as of the time of writing, it has not yet replied.
Music Videos are also available on TVs
Spotify says that music videos are also available on TVs where it might prove a lot more helpful. Likely, the initial collection of video content is limited on the platform. As The Verge notes, currently supported artists include Ed Sheeran, Doja Cat, Ice Spice, Aluna, and Asake. With the public rollout of this feature, you can expect Spotify to include content from a wider variety of artists.
“In our initial beta rollout, we’re starting with a limited subset of the full catalog, which includes thousands of music videos. Within this subset, we aimed to prioritize a wide range of genres and artists across our launch markets,“ said Sten Garmark, Spotify’s VP Global Head of Consumer Experience.
It’s good to see Spotify is catching up with other streaming services like YouTube Music and Apple Music, both of which have video content available at this point. For those unfamiliar with the platform, it has been offering video podcasts and Clips (short vertical videos). So, it previously had what it takes to host videos to a global audience as well.
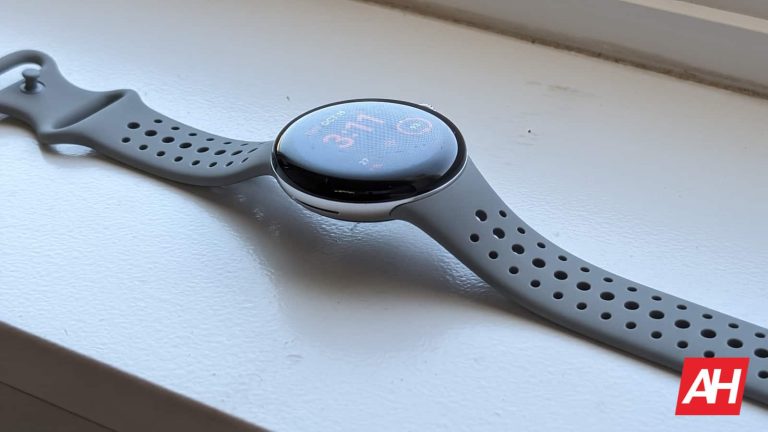
Some Pixel Watch and Pixel Watch 2 owners have noticed a new handy feature that enables them to monitor the progress of app installation directly from the app drawer. Checking individual app downloads at the Google Play Store will become redundant with this feature, thus simplifying the process of handling downloads and updates.
App installs are now easier to track on a Pixel Watch making it more functional
Google’s commitment to enhancing the Pixel watch experience shines through with this feature. Among other things, adding an on-screen indicator for app installations means that Google’s Wear OS is one step closer to improved functionality.
The latest feature was first discovered by one user known as Dimitrios Vlachos, whose revelation was then seconded by Mishaal Rahman. The progress bar appears within the app drawer allowing Pixel Watch owners to oversee their workflow without interruption.
From Mishaal Rahman on X
The progress bar feature on WearOS underscores the convenience of a Pixel Watch. Google further optimizes performance and functionality across the Pixel Watch lineup through regular updates and feature additions like those brought about by new Pixels’ Feature Drop releases.
The feature remains exclusive to Pixel Watch 1 and Pixel Watch 2
It indicates that Google has not stopped innovating or improving its smartwatch ecosystem. However, the added functionalities are only available for Pixel Watch and Pixel Watch 2 users. Nevertheless, it is important to note that other wearables using Wear OS like the OnePlus Watch 2 cannot execute this function yet.
Incorporating a feature showing the app download progress is a demonstration of Google’s desire to make Pixel watches much more integrated into the user’s ecosystem. Folks no longer have to check their app download status within the Play Store. The app drawer will let users know every time an installation progresses successfully or when there may be any issues that may need intervention while they are still working on something else on their watches.
NBC News reports that the U.S. House of Representatives has overwhelmingly voted in favor of a bill that would ban video app TikTok in the United States unless the app is divested by the owner of the app, China’s TikTok. The vote count of 352-65 (with one member voting “present”) shows how much lawmakers are concerned about the relationship between TikTok owner ByteDance and the Communist Chinese government.
The concern is that ByteDance collects a large amount of personal data from TikTok subscribers in the U.S. Per Statista, the app had 102 million users in the states last year and that total is expected to rise to nearly 108 million this year. House Speaker Mike Johnson (R-La) said, “Communist China is America’s largest geopolitical foe and is using technology to actively undermine America’s economy and security. Today’s bipartisan vote demonstrates Congress’ opposition to Communist China’s attempts to spy on and manipulate Americans, and signals our resolve to deter our enemies.”
50 Democrats and 15 Republicans voted against the bill including a surprising “no” vote from Rep. Marjorie Taylor Greene, R-Ga who pointed out that she had previously been banned from social media. Greene’s vote matched that of Rep. Jim Himes, D-Conn., the top Democrat on the Intelligence Committee. Rep. Himes voted against the bill noting that countries like China “shut down newspapers, broadcast stations, and social media platforms. We do not. We trust our citizens to be worthy of their democracy. We do not trust our government to decide what information they may or may not see.”
TikTok is trying to fight back by stating that the bill violates American’s First Amendment right to enjoy free speech.
The next stop for the bill is the Senate where it might have a harder time getting through. If the Senate does advance the bill, the House and Senate versions will need to be reconciled and the final version of the bill will be sent to the president for his signature. President Biden has already said that if the bill is advanced to his desk, he will sign it.