Sony’s new high-end smartphones are on the horizon. The Sony Xperia 1 VI and Xperia 5 VI are coming, and their RAM options have just surfaced. In addition to those two phones, the info also surfaced for the Xperia 10 VI.
The Sony Xperia 1 VI & Xperia 5 VI RAM options appear
According to Suamodigest, the Sony Xperia 1 Vi will be coming in 12GB and 16GB RAM flavors. The Xperia 5 VI will be on offer with a single option only, 8GB of RAM. The Xperia 10 VI will launch in both 6GB and 8GB RAM configurations.
We do expect Sony to utilize LPDDR5X RAM and UFS 4.0 flash storage in the two high-end phones. The Xperia 10 VI probably won’t offer those, chances are it will rely on LPDDR5 and UFS 3.1, but we’ll see.
We don’t have a lot of information about these phones just yet. The Sony Xperia 1 V and Xperia 10 V launched in May last year, while the Xperia 5 V arrived in September. It remains to be seen if Sony will launch either of the phones sooner this time around. The Xperia 1 VI was rumored to arrive during MWC 2024, but that didn’t happen.
The Snapdragon 8 Gen 3 will fuel both of those high-end phones
The Snapdragon 8 Gen 3 will fuel the Xperia 1 VI and Xperia 5 VI, that’s almost certain. The Xperia 1 VI is said to include three 48-megapixel cameras on the back. The main one will use a two-layer Transistor Pixel tech. It will be a 1/1.4-inch sensor, and offer a lens aperture of f/1.4. Full-pixel dual-PD autofocus is also rumored, along with 2x optical zoom capabilities of the main camera.
The ultrawide unit will measure 1/2.7 inches, and offer a pixel size of 0.6um. Sony’s 2×2 On-Chip Lens (OCL) tech will also be in use. That camera should offer enhanced sensitivity, capture resolution, dynamic range, and speed.
The third camera will be a telephoto unit, but we don’t have a lot of information about it at this point. Android 14 will come pre-installed on all three of these devices from the get-go.
Are you among the unfortunate people who have encountered a sticky scrolling problem with your Pixel Fold (Review)? Then you are not alone. This annoying issue has been reported by some users, which can make using applications and websites extremely difficult. This article will examine the problem in more detail, as well as possible causes and solutions.
The purpose of Pixel Fold’s Inner Screen is to offer consumers a smooth and user-friendly scrolling experience. Nevertheless, a few customers have complained about the screen’s sporadic loss of scroll inertia. If you’re experiencing this issue, here are the potential causes of the issue and how to work around it.
What is the sticky scrolling issue?
The sticky scrolling issue on Pixel Fold units refers to a problem where the screen doesn’t respond smoothly when you try to scroll through content. Instead of gliding effortlessly up or down a page, you may find that the screen jitters or jumps, making it difficult to read or interact with the content. This can be particularly annoying when trying to browse the web or read articles on your device.
Potential causes of the issue
There are a few possible causes for the sticky scrolling issue you’re having with your Pixel Fold. A software error or defect that is impairing the functionality of the device is one potential reason. Sometimes the problem can also involve the calibration of the touchscreen sensors, which could result in readings that are off when you try to scroll.
It’s also important to take into account if any physical harm or debris is obstructing the touchscreen’s operation. It’s conceivable that internal component damage caused by drops or water exposure is what’s causing the sticky scrolling issue on your smartphone.
How to fix the sticky scrolling issue
There are several actions you can take to try to fix the sticky scrolling issue on your Pixel Fold. The following troubleshooting advice can assist you in returning your gadget to normal:
Occasionally, a straightforward restart might assist in removing any transient glitches or flaws that might be the source of the problem. To check if it helps, try turning your Pixel Fold off and then back on. Moreover, ensure that the most recent software version is installed on your device. Updates frequently come with speed enhancements and bug fixes, which may help with the sticky scrolling issue.
Furthermore, to make sure your Pixel Fold’s touchscreen sensors are correctly recording your touch inputs, you may recalibrate them. Please refer to your device’s user manual or online guides for instructions since this procedure may differ based on its settings. Eventually, scrolling problems could arise if there is any dirt or debris on the touchscreen. Check to see whether the responsiveness is improved by gently cleaning the screen with a soft, lint-free cloth.
You might be able to troubleshoot and resolve the stuck scrolling issue on your Pixel Fold by following these methods. Users may need to contact Google support. You may also go to an approved service facility if the problem continues.
Is there anything else you can do to prevent this issue from happening in the future?
There are a few steps you can take to stop the Pixel Fold’s Inner Screen from sometimes losing scroll inertia in the future. Keep your smartphone away from moisture and very hot or cold temperatures since they might harm the screen and degrade its functionality. Cleaning the screen regularly and getting rid of any dust or debris that could be interfering with it is also a smart idea. Furthermore, keep your gadget away from any electrical gadgets that could be interfering with it.
Threat actors target a niche group of internet users, security researchers, penetration testers, and even cybercriminals.
The weapon of choice is malicious software known as CyberGate Remote Access Trojan (RAT), which has been lurking in the cyber realm for several years.
The latest twist in its deployment involves a cunning disguise, where the RAT is being distributed under the guise of a URL to a seemingly harmless Dork converter tool.
Understanding “Dorks” in Cybersecurity
For the uninitiated, “Dorks” are not the awkward characters from a high school drama but rather specialized search queries.
DocumentIntegrate ANY.RUN in your company for Effective Malware Analysis
Malware analysis can be fast and simple. Just let us show you the way to:
Interact with malware safely
Set up virtual machine in Linux and all Windows OS versions
Work in a team
Get detailed reports with maximum data
If you want to test all these features now with completely free access to the sandbox:
These queries are instrumental for cybersecurity professionals and ethical hackers in uncovering vulnerable websites, sensitive data leaks, and hidden malware.
While Dorks serve as a force for good in the hands of defenders, enabling them to patch up security holes and protect data, they can also be wielded by malicious actors to exploit the same vulnerabilities.
Symantec’s Multi-Layered Defense Against CyberGate
Cybersecurity giant Symantec has developed a robust defense mechanism to combat this insidious threat.
Broadcom has recently reported that CyberGate RAT has been identified as masquerading as a Dork tool.
This RAT is a remote access Trojan that allows an attacker to gain unauthorized access to a computer system.
Symantec’s protection suite is designed to identify and neutralize the CyberGate RAT using a multi-layered approach:
Adaptive-based detection is represented by the signature ACM.Ps-RgPst!g1, which adapts to the evolving tactics of the RAT.
Behavior-based protection comes in the form of SONAR.
Dropper, a heuristic that monitors for suspicious behavior indicative of a trojan dropper.
W32 provides a file-based defense—Spyrat, which targets the file signatures associated with the CyberGate RAT.
Machine Learning-based security is cutting-edge and Heur.AdvML.B!100 employs advanced algorithms to predict and prevent attacks before they happen.
Threat Intelligence recently reported on Twitter that the CyberGate Remote Access Trojan (RAT) is disguised as a Dork tool, potentially allowing attackers to gain unauthorized access to targeted systems.
Symantec’s comprehensive strategy showcases the importance of adaptive, behavior-based, file-based, and machine-learning defenses in the ever-evolving battle against cyber threats.
As the CyberGate RAT continues to mimic legitimate tools to infiltrate the cybersecurity community’s systems, awareness and advanced protection systems like those offered by Symantec are critical in safeguarding against such deceptive attacks.
You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.
Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.
Not too long ago, we saw a post where Mark Zuckerberg was testing out the in-app camera in Threads. He also teased being able to save drafts within the app. At that point, they were testing the features.
When you are typing a new post in Threads, but you can’t finish it and need to return to it later, you can simply press the back button on your phone or swipe down on the post. Before exiting, the app will give you the option to save a draft to finish later. This is also for people who like to pre-draft their posts and publish them at a later time.
To access the draft again, up on the Add Post button again. This will bring up the last draft that you had. One thing to note is that, if you have a draft, the Add Post button will be different.
Threads now has an in-app camera
People who typically like to share pictures on social media have shared this gripe with Threads. When sharing a picture with the platform, there was no way of doing so quickly. People would have to go to their default camera app, pick the picture, and upload it to threads. Granted, it’s not the most labor-intensive task. However, if you’re a person who shares a lot of pictures on social media, that can get pretty annoying.
Well, when you are making a new post, you will see a new camera icon under your profile picture. When you tap on it, you’ll be taken to an in-app camera.
One thing we noticed is that, rather than being taken to a unique camera interface, it looks like the Threads app will just open your device’s default camera and directly import the picture once you take it. We’ve tested this on the Galaxy S24+ (Review) and the Tecno Phantom V Flip (Review), and we can confirm this. Even the confirmation screen, asking you whether you want to use that picture or retry it, is different across devices.
In order to access these features, make sure your Threads app is fully updated. If your app is updated, and you don’t have these features, then you may just want to wait a day or two for it to reach your device.
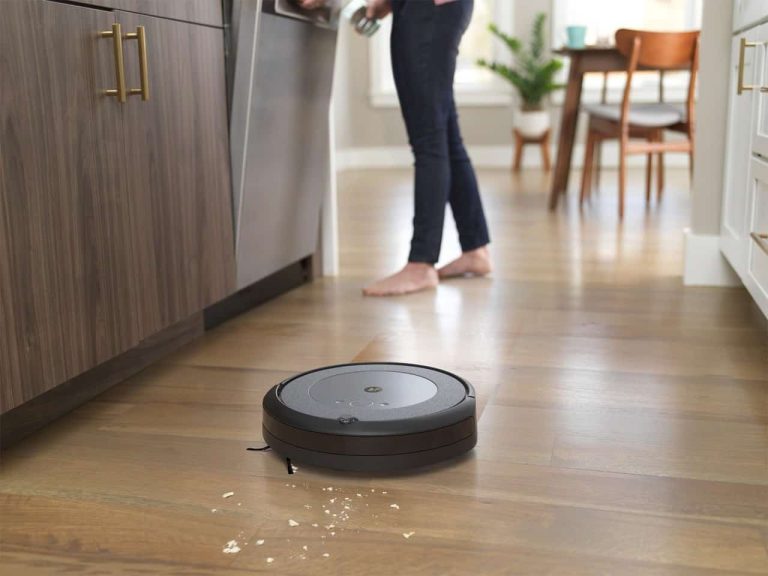
The newest Roomba is on sale right now, saving you $200 off of its regular price. That’s the iRobot Roomba Combo i5+, which is now $349. That’s a pretty good price for a robot vacuum and mop combo here. The Roomba Combo i5+ was announced back in August and has been pretty popular ever since. It also won our Reader’s Choice Award as the Best Robot Vacuum for 2023.
The iRobot Roomba Combo i5+ is the cheapest vacuum/mop combo from iRobot on the market. And it’s a pretty nifty one. Unlike the Roomba Combo j7+, this one has separate dustbins. So, to go from mopping to vacuuming, you’d need to swap out the bins. This means there is a little more work on your end, but for this price, that’s okay.
This is a great robot vacuum for pet hair due to the rubber rolling brushes here, as well as the increased suction. So you’ll never have to worry about it missing any pet hair or getting tangled. This is a really great vacuum to pick up for those who have pets since the pet hair won’t get tangled in the brushes, and it will also do an excellent job of picking up all of the pet hair. Both things are super important these days.
This is the “Plus” model, which means it comes with an auto-empty dock. With this feature, you won’t have to worry about emptying the dustbin for up to 60 days. Once the time is up, you can take out the dustbag and replace it with a new one. It’s a hassle-free and easy process.
You can pick up the iRobot Roomba Combo i5+ from Amazon today.
QNAP has disclosed a series of vulnerabilities within its operating systems and applications that could potentially allow attackers to compromise system security and execute malicious commands.
These vulnerabilities, identified as CVE-2024-21899, CVE-2024-21900, and CVE-2024-21901, pose significant risks to users of affected QNAP devices.
The company has promptly responded by releasing updates to mitigate these vulnerabilities.
Understanding the Vulnerabilities
CVE-2024-21899: Compromising System Security Through Improper Authentication
This vulnerability could allow unauthorized users to bypass authentication mechanisms, allowing them to compromise the system’s security via a network.
DocumentIntegrate ANY.RUN in your company for Effective Malware Analysis
Malware analysis can be fast and simple. Just let us show you the way to:
Interact with malware safely
Set up virtual machine in Linux and all Windows OS versions
Work in a team
Get detailed reports with maximum data
If you want to test all these features now with completely free access to the sandbox:
The improper authentication flaw poses a critical risk, as it could enable attackers to gain unauthorized access to sensitive information or disrupt system operations.
CVE-2024-21900: Command Execution Through Injection Vulnerability
CVE-2024-21900 is an injection vulnerability that could allow authenticated users to execute arbitrary commands via a network.
This vulnerability could enable attackers to manipulate the system to their advantage, potentially leading to data theft, system damage, or further unauthorized access.
The SQL injection vulnerability, identified as CVE-2024-21901, could allow authenticated administrators to inject malicious code via a network.
This vulnerability is particularly concerning as it could enable attackers to manipulate or corrupt database contents, leading to data loss or unauthorized access.
Hunter recently tweeted about a severe issue related to QNAP operating systems. The tweet warns users to be cautious and take necessary measures to avoid exploitation.
A critical vulnerability (CVE-2024-21899, CVSS 9.8) has been found in multiple versions of QNAP operating systems.
🚨Alert🚨CVE-2024-21899 (CVSS 9.8): Critical QNAP Flaw opens the door to Hackers ⚠An improper authentication vulnerability has been reported to affect several QNAP operating system versions. It could allow attackers to slither into your NAS without a username or password. 📊… pic.twitter.com/BMA05kOjZY
QNAP has taken swift action to address these vulnerabilities by releasing updates for the affected products.
Discovering these vulnerabilities in QNAP’s systems is a crucial reminder to maintain up-to-date security measures.
The following table outlines the affected products and their corresponding fixed versions:
Affected Product
Fixed Version
QTS 5.1.x
QTS 5.1.3.2578 build 20231110 and later
QTS 4.5.x
QTS 4.5.4.2627 build 20231225 and later
QuTS hero h5.1.x
QuTS hero h5.1.3.2578 build 20231110 and later
QuTS hero h4.5.x
QuTS hero h4.5.4.2626 build 20231225 and later
QuTScloud c5.x
QuTScloud c5.1.5.2651 and later
myQNAPcloud 1.0.x
myQNAPcloud 1.0.52 (2023/11/24) and later
Users of the affected versions are urged to update their systems and applications to the latest versions to protect against these vulnerabilities.
To safeguard against these vulnerabilities, QNAP strongly recommends that users regularly update their systems and applications to the latest versions.
These updates include critical fixes that can protect devices from potential attacks.
Users can update their QTS, QuTS hero, or QuTScloud systems via the Control Panel’s Firmware Update section or download the updates directly from the QNAP website.
For myQNAPcloud, updates can be performed through the App Center.
The discovery of these vulnerabilities was credited to DEVCORE, under the identifiers ZDI-CAN-22493/22494.
QNAP’s swift response underscores the importance of proactive security measures and the company’s commitment to protecting its users.
Users of QNAP devices are urged to update their systems immediately to protect against potential threats.
You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.
Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.
Microsoft confirms that Russian state-sponsored hackers, known as Midnight Blizzard, infiltrated their systems and stole source code. Experts warn of potential zero-day vulnerabilities.
Microsoft has been hit by a significant cybersecurity breach, with the company confirming that Russian hackers infiltrated its infrastructure, compromising valuable source code.
The breach, originally discovered on January 12, 2024, and reported on January 19, raised concerns about the potential misuse of proprietary information and the security of millions of users relying on Microsoft’s products and services.
Earlier this year, Microsoft disclosed that Russian state-sponsored hackers referred to as Midnight Blizzard (also known as Nobelium, Cozy Bear, and APT29), have been spying on the email accounts of Microsoft’s team members. The group, known for the devastating SolarWinds attack, successfully stole source code in what Microsoft now terms an “ongoing attack.”
Reportedly, the hackers infiltrated a “small percentage of corporate email accounts” and stole internal messages and files in an attack that began in late November 2023. The threat actor compromised a non-production test tenant account using a password spray attack, accessing some Microsoft corporate email accounts, including senior leadership and cybersecurity employees, and exfiltrating emails and documents.
The attackers exploited vulnerabilities in Microsoft’s defences, gaining unauthorized access to a substantial portion of source code, including Windows OS components, Office Suite, and other critical software elements.
Update from Microsoft
Previously, Microsoft stated that there was no evidence that the “threat actor had any access to customer environments, production systems, source code, or AI systems.” However, as per Microsoft’s update published on March 8, 2024, Midnight Blizzard is using information from corporate email systems to gain unauthorized access, including access to source code repositories and internal systems. Still, the company asserts that there’s no evidence that attackers compromised Microsoft-hosted customer-facing systems.
Midnight Blizzard is using various tactics to attack Microsoft, some of which were shared between Microsoft and its customers via emails. Moreover, the company claims hackers increased the attack volume, such as password sprays, by up to 10 times in February compared to January.
Microsoft has increased security investments and coordinated cross-enterprise efforts to counter Midnight Blizzard’s persistent threat. The company is enhancing its security controls, detections, and monitoring, as well as conducting ongoing investigations into the group’s activities.
Hackread will continue to share findings and information as they evolve. Users are advised to implement security updates, report suspicious activity, and adhere to security best practices.
Expert Comments
Ariel Parnes, former Head of the Israeli Intelligence Service Cyber Department, winner of the Israel Defense Prize for tech innovations in the cyber field, and COO and Co-Founder at SaaS incident response leader, Mitiga, shared the following insights with Hackread.com:
“For advanced nation-state cyber groups, access to a company’s source code is akin to finding the master key to its digital kingdom, opening up avenues for finding new zero-day vulnerabilities: undiscovered security flaws that can be exploited before they’re known to the software creators or the public.”
Ariel warned that “Zero-day vulnerabilities represent a critical threat because there’s no straightforward way to detect them until after they’ve been discovered and disclosed by the software creators. Given this challenging landscape, organizations need to double down on cybersecurity measures focused on proactive defence.”
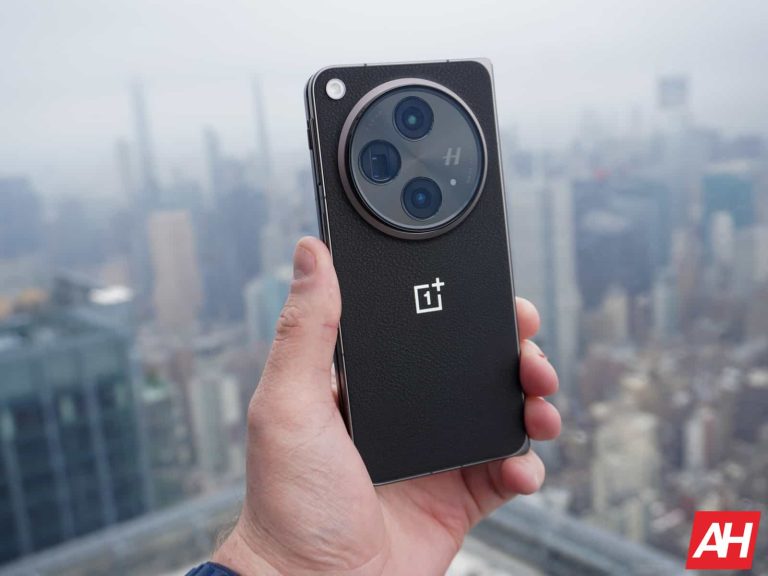
Android 14 is finally coming to the OnePlus Open in the US
We hoped that the update would spread to other markets quicker than this, but there you have it. We had to wait for about a month and a half at this point. The update is finally rolling out in the US, though.
The update is marked as CPH2551_14.0.0.501(EX01). This update does bring OxygenOS 14 to the table, along with Android 14. The update itself weighs 2.54GB, so chances are you’ll want to be connected to Wi-Fi before you download it.
All the base Android 14 changes are included, but this changelog is focused on OxygenOS, of course. This update is bringing Aqua Dynamics to the table. It’s a new way of interacting with morphing forms. It allows you to view up-to-date information at a glance.
OnePlus added several new, interesting features
‘File Dock’ has been added, so you can now use drag and drop action to transfer files between apps and devices. The ‘Content Extraction’ feature is also included here. It can recognize and extract text and images from the screen with a single tap.
Cutting out objects/subjects from a photo also becomes a lot easier now, thanks to the ‘Smart Cutout’ feature. It allows you to cut out several subjects from a photo thanks to some help from AI.
The ‘Shelf’ has been improved too, as more widget recommendations have been added. The security has been improved, and so has Aquamorphic Design. Color styles have been changed, while new Aquamorphic-themes ringtones have been included too. OnePlus also tweaked the animations and the always-on display (AOD) OnePlus Open feature here.
This OnePlus Open update is rolling out in stages, as per usual. Some of you probably already got it, while it’s on the way to the rest, you may have to wait a bit, though.
Qualcomm is prepping to host an event as early as March 18 at 2:30 PM local time in China where it could introduce the latest flagship Snapdragon chip. Notably, the conference’s slogan is “Intelligence is in the core, and there is a dragon in it.” Per reports, the chip maker could announce the Snapdragon 8s Gen 3 and the Snapdragon 7+ Gen 3 chips. But take note that Qualcomm hasn’t announced anything about these developments yet. Both the chipsets are said to be built on the same architecture as the Snapdragon 8 Gen 3, which has been receiving praises since its launch.
Qualcomm may launch a flagship chip on March 18th
The news about the event comes from a post on Weibo, where the chip maker could announce at least two chips, including a flagship one. The Snapdragon 8s Gen 3 will steal the limelight of the event, while we anticipate the other chip, 7+ Gen 3, to power up budget smartphones releasing ahead.
Delving into the technicals of the upcoming chips, the Snapdragon 8s Gen 3 could boast one 3.01GHz Cortex-X4 core, four 2.61GHz Cortex-A720 cores, and three 1.84GHz Cortex-A520 cores, alongside an Adreno 735 GPU. Conversely, the Snapdragon 7+ Gen 3 could exhibit a similar architecture but with different clock speeds, including a 2.9GHz Cortex-X4 core, four 2.61GHz Cortex-A720 cores, and three 1.9GHz Cortex-A520 cores, completed by an Adreno 732 GPU.
Which phones will feature the upcoming Qualcomm Snapdragon chips?
The rumored candidates, according to folks at Gizmochina, include the Realme GT Neo6 series, Redmi Note 13 Turbo, Xiaomi Civi 4, OnePlus Ace 3V, Vivo Pad 3, and new devices in the iQOO Neo 9 series. These devices might feature either of the upcoming chips. Notably, the publication adds that we might’ve to wait until March 18 when Qualcomm will confirm the releases during its event. So, until then, you may have to take this information with a grain of salt. But regardless of that, we could say that new Qualcomm processors are on their way.
A Proof of Concept (PoC) exploit has been released for a vulnerability in the OpenEdge Authentication Gateway and AdminServer.
This vulnerability, CVE-2024-1403, affects multiple versions of the OpenEdge platform and could potentially allow unauthorized access to sensitive systems.
The vulnerability arises when the OpenEdge Authentication Gateway (OEAG) or the AdminServer is configured with an OpenEdge Domain that utilizes the OS local authentication provider.
DocumentIntegrate ANY.RUN in your company for Effective Malware Analysis
Malware analysis can be fast and simple. Just let us show you the way to:
Interact with malware safely
Set up virtual machine in Linux and all Windows OS versions
Work in a team
Get detailed reports with maximum data
If you want to test all these features now with completely free access to the sandbox:
This configuration can lead to unauthorized access during login attempts due to a flaw in the authentication routines.
Specifically, the vulnerability allows authentication success to be incorrectly returned from an OE local domain under certain conditions, such as when unexpected content is present in the credentials passed during the login process.
Affected versions include OpenEdge Release 11.7.18 and earlier, OpenEdge 12.2.13 and earlier, and OpenEdge 12.8.0.
The vulnerability has been addressed in the latest updates: OpenEdge LTS Update 11.7.19, 12.2.14, and 12.8.1.
Community Progress has addressed the issue and has Updates in OpenEdge LTS Update 11.7.19, 12.2.14, and 12.8.1.
Impact and Affected Components
The vulnerability has a broad impact, potentially affecting various components of the OpenEdge platform, including:
OpenEdge Database access through OEAG
AdminServer logins via OpenEdge Explorer (OEE) and OpenEdge Management (OEM)
Database Servers accepting OEAG-generated tokens
Secure Token Service Utilities
Pro2 web application utility for Pro2 management
Ptrace SecurityGmbH recently tweeted about a security vulnerability, CVE-2024-1403, that affects Progress OpenEdge software.
The vulnerability allows for authentication bypass, potentially putting sensitive information at risk.
Mitigation and Upgrade Instructions
A Proof of Concept (PoC) exploit has been made available for a significant vulnerability identified in the OpenEdge Authentication Gateway and AdminServer.
This flaw can potentially be exploited by attackers to gain unauthorized
For users running vulnerable versions of OpenEdge, upgrading to the fixed versions is crucial.
The fixed versions are:
Vulnerable Version: OpenEdge Release 11.7.18 and earlier
Fixed Version: OpenEdge LTS Update 11.7.19
Vulnerable Version: OpenEdge Release 12.2.13 and earlier
Fixed Version: OpenEdge LTS Update 12.2.14
Vulnerable Version: OpenEdge Release 12.8.0
Fixed Version: OpenEdge LTS Update 12.8.1
For those unable to upgrade immediately, temporary mitigation steps include library replacement and domain replacement mitigation for OEAG and AdminServer mitigation strategies, such as using AdminServer Group controls and disabling the AdminService.
The release of the PoC exploit for CVE-2024-1403 underscores the importance of maintaining up-to-date security measures in software systems.
OpenEdge users are urged to review their systems, apply the necessary updates or mitigations, and remain vigilant against potential unauthorized access attempts.
You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.
Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.