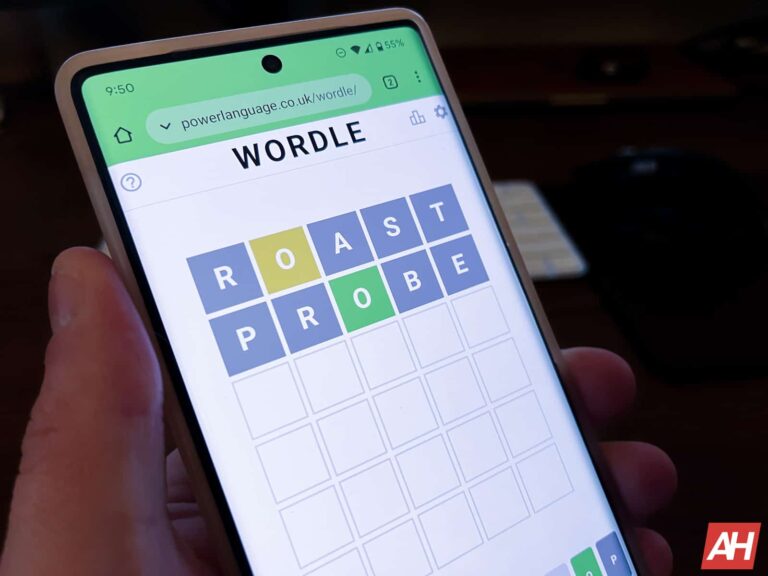
This is another example of large corporations using their massive weight and wealth to bully smaller entities. Soon after Wordle, the puzzle game where you have to get a secret word by using the process of elimination, took off back in 2021, the New York Times acquired it for a large sum of money. Obviously, since Wordle was a sensation, many small-time Developers made their own clones of it. However, many of the companies brought their own unique and fresh takes on the genre.
That doesn’t matter, as the New York Times is suing developers making Wordle clones
The large publication, according to the reports, has issued hundreds of copyright notices to developers making their own Wordle clones. Many of the companies making these clones are small-time developers relying on ad revenue to stay afloat. So, it’s a little scummy that a big-time corporation is suing them.
Undoubtedly, many, if not all of the developers, will have to fold in court, as the New York Times has plenty of money to outlast any lawsuit. This is a tactic used by all major companies. Only major lawsuits from multimillion or multi-billion-dollar companies ever make it to court. That’s one reason why the landmark Samsung vs. Apple lawsuit lasted so many years
This is scummy behavior
Realistically, The New York Times should not be distributing these lawsuits. For starters, the company owns the property of Wordle, not the genre of gameplay. That genre of gameplay existed many years before Wordle was created. Many of us remember playing similar games online or on portable consoles years ago. It is an entire genre of puzzle game. We can see if a developer used a similar logo or a similar font to what Wordle uses. However, most Wordle clones only nip the gameplay. Imagine if Nintendo sued every company that made a platformer.
Also, as pointed out by Matthew Schultz from Android Police, emulation is how the video game industry flourishes. One company invents a concept, but hundreds of other companies mold and innovate on that concept adding their own specific style and ideologies to it. This is what breeds growth in the gaming industry. Many early platformers emulated Super Mario. However, just look at where the platforming games are now.
The New York Times should not have the right to sue other companies making games in a specific genre. Other companies add their own flair and personality to the genre. Since Wordle was acquired by the New York Times, there has been little to no innovation in the game itself from the company. So, it’s very wrong for the New York Times to gate-keep this genre of game.
Consumer Reports exposes security vulnerabilities in popular video doorbells allowing unauthorized access, stolen footage, and privacy risks. Learn how to protect your home from insecure devices.
The video doorbell market has been flooded with a wide variety of brands, devices, versions, and sellers, making it difficult for buyers to find safe and reliable products. To make it more complicated, according to a report by Consumer Reports (CR), these devices lack basic access controls in network traffic enabling strangers to freely access private video thumbnails.
Investigation
As per CR’s investigation, significant security vulnerabilities were identified in video doorbells potentially allowing attackers to gain unauthorized access to video footage, control doorbell functions, or even steal personal information.
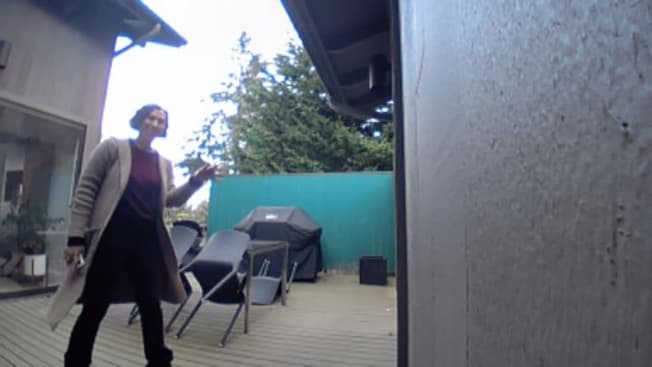
It all started when a CR journalist received an email with grainy images of herself waving at a doorbell camera, sent by CR privacy and security test engineer Steve Blair after hacking into the doorbell from 2,923 miles away.
Screenshot credit: Consumer Reports
Blair and fellow test engineer Della Rocca probed further and discovered security flaws in cheap, insecure electronics from Chinese manufacturers sold on online marketplaces like Amazon, Walmart, Sears, and Shein.
The doorbells lacked a visible ID issued by the Federal Communications Commission (FCC), making them illegal to be distributed in the U.S. The researchers discovered security issues in video doorbells sold under Eken and Tuck brands, with at least 10 similar devices and all analyzed doorbells being controlled through an Eken-owned mobile app, Aiwit. Two products, sold under Fishbot and Rakeblue brands, showed similar vulnerabilities.
Eken and Tuck are strong sellers, with multiple listings on Amazon generating over 4,200 sales in January 2024 alone. The doorbells are also available on Walmart.com, sears.com, and global marketplaces Shein and Temu under different names like Andoe, Gemee, and Luckwolf.
Potential Dangers
Anyone with physical access can hijack the doorbell without needing advanced tools or hacking skills. They only have to download the app and pair the device to their phone to view the camera’s video feed indefinitely.
Threat actors can control doorbells to monitor family members’ movements and expose their IP addresses and WiFi network names without encryption. Poor security on company servers storing videos may further increase threats. The Aiwit smartphone app can pair doorbells with WiFi hotspots, allowing people to access video feeds without passwords or accounts. Stalkers/adversaries can identify device serial numbers and access still images from the video feed even if the original owner regains device control.
Justin Brookman, director of technology policy for CR, suggests that e-commerce platforms, particularly big names like Amazon, should take responsibility for the harm caused by their products. Eken, Tuck, Amazon, Walmart, Sears, Shein, Temu, and the Federal Trade Commission have been notified about the issues by CR.
Temu has now removed all doorbells made by Eken and its app from its website and Walmart stated items not meeting safety, reliability, and compliance standards will be removed and blocked, but CR found “similar-looking” doorbells still available on these platforms. Amazon, Sears, and Shein are yet to respond.
How to secure your doorbell camera?
Although, 100% security is a myth, here are some steps you can take to make sure your doorbell is protected from hackers and spying by third parties:
Choose a Reputable Brand:
Avoid unbranded or cheap video doorbells, especially those from unfamiliar manufacturers.
Look for established security companies or well-known brands with a history of prioritizing security.
Check for Security Features:
Make sure your doorbell uses strong encryption for video transmission and storage.
Look for features like two-factor authentication (2FA) for logins and activity alerts.
Secure Your Wi-Fi Network:
Use a strong password for your Wi-Fi network and enable encryption (WPA2 or WPA3).
Consider creating a separate guest network for devices like your doorbell, keeping it isolated from your main network with sensitive data.
Manage App Permissions:
Only grant the doorbell app the minimum permissions necessary, like access to the camera and microphone.
Avoid apps from unknown developers and stick to official ones from the manufacturer.
Keep Firmware Updated:
Regularly update your doorbell’s firmware to ensure you have the latest security patches and bug fixes.
Enable automatic updates if available to stay protected.
Monitor Activity:
Be aware of who has access to your doorbell and monitor activity logs.
Look for any suspicious login attempts or unusual activity.
Consider Privacy Settings:
Adjust your doorbell’s privacy settings to control what areas are recorded and how long footage is stored.
Disable features you don’t need, like motion detection in public areas.
FCC ID: Look for a visible FCC ID on your doorbell. Devices without it might be illegal and lack proper security measures.
Physical Security: Make sure your doorbell is physically secure and can’t be easily tampered with.
Social media is great for sharing content, but it’s not the best when it comes to viewing it. Pictures and videos posted to social media tend to be much lower quality than what our phones can produce. However, that is changing for some. According to a new report, Threads now supports Ultra HDR and 10-bit HDR content on certain Pixel devices.
You can take wonderful and beautiful pictures using your amazing smartphone camera. However, they don’t quite show up like that on social media feeds. This is because companies typically compress pictures and videos when they’re uploaded. This is one thing that many people have an issue with.
But, Threads will now show Ultra HDR and 10-bit HDR content on certain Pixel devices
Ever since its launch, Meta has been introducing more features to Threads. Now, it’s a pretty feature-packed social media platform, but there are some things that Threads can’t do. Regardless, Ultra HDR and 10-bit HDR content are coming to the platform. If you record any content in these formats, they will show up picture-perfect in the Threads Android app. This is great for people who want to share high-quality content to Threads.
There is one drawback. This feature is limited in terms of which devices are supported. You can only use this feature if you’re using the Google Pixel 7, Pixel 7 Pro, Pixel Fold, Pixel 8, or Pixel 8 Pro (Review). The reason for this is that Google designed the displays in these phones specifically to display this kind of content. It’s a similar case for viewing 10-bit HDR video using Google Photos. You can view the content using devices with the proper display.
So, if you have one of these phones, you will be able to view Ultra HDR and 10-bit HDR content in Threads. This functionality should be available now. If you don’t see it just yet, then you are going to have to wait for it to make it to your device.
At this point, Pixel 8 users are happy that they are included in this list of supported devices. Recently, we got the news that the Pixel 8 will not be receiving Gemini Nano due to Hardware limitations.
The ability to group and share Wi-Fi passwords, hotspots, and moving video calls between Android devices has been rumored for some time now. However, new evidence suggests that the video call transfer feature in particular might be bound to just one specific app: Google Meet.
“Call transfer,” as the feature is believed to be called, will reportedly allow you to link devices that are logged in with the same Google account, enabling seamless sharing of those services. Recently, an Android Authority breakdown of the underlying code powering this feature found more info on how it will reportedly work.
At first glance, it appears as if the feature has had a recent name change. This is because in a previous version of Google Play services (v24.06.12), tipster @AssembleDebug found references to it by enabling some hidden flags. These referred to it as “Call cast,” instead of “Call transfer,” as found in the latest version (v24-08-12). However, because in this latest version there is also a reference to “Call cast,” it is now believed that these may indeed be separate features— one for video and one for audio.
Cross Device Services in Google Play Services
✓ Call Cast ✓ Wifi Sharing ✓ Hotspot Sharing
Might be enabled in upcoming beta version of Play Services. Screenrecord is from version 24.06.12, enabled with a lot of flags.#Google#Androidpic.twitter.com/bvUbnYbB9d
In this latest iteration, the code was found to have a very specific reference to Google Meet and apps like it. This suggests that Meet will most definitely be one of the apps supported, and the “apps like Google Meet” reference could mean that it extends to other video calling apps such as Zoom and Microsoft Teams.
<string name=”enrollment_feature_description_call_transfer”>Switch between devices on video calls in apps like Google Meet</string> <string name=”enrollment_feature_explanation_call_transfer”>See video calls across your devices and switch between them;/string>
While we still don’t have a confirmed release date, it’s clear that Google is gearing up to make the Android experience even more connected. The ability to transfer video calls – and maybe even voice calls – between our devices will be a real game-changer for those juggling multiple Android smartphones or tablets.
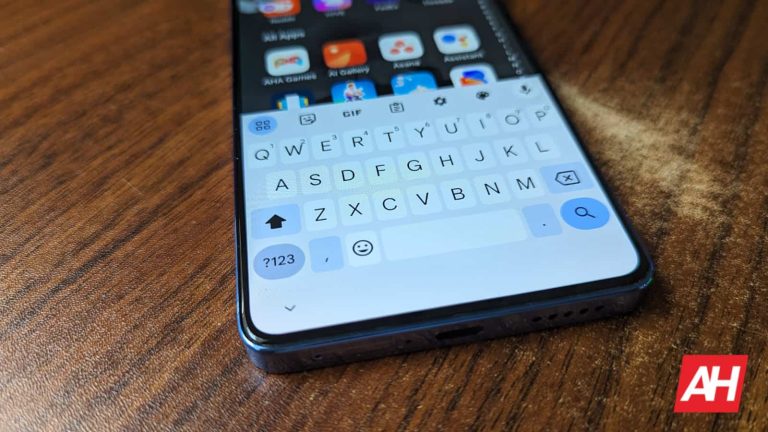
A big part of using a digital keyboard is actually being able to see the text and numbers that you’re typing. Well, this isn’t much of a possibility for some users thanks to a new Gboard bug. This Gboard bug is resulting in tiny text and a tiny floating window.
At this point, we’re not certain what the cause of this bug is. However, it seems to only affect people using Pixel devices. Also, reports state that this issue happens after using Android Auto. So far, it doesn’t seem that Google is aware of the issue. Once this issue gains more traction, we know that the company will swiftly issue an update to fix it.
A new Gboard bug is causing tiny text
Several users on Reddit reported this issue. After using Android Auto on their phone, they would open the Gboard to find that the keyboard itself is the proper size, but all of the letters and numbers inside of the keys are extremely tiny. This is obviously going to be an issue for people who can’t see well. Also, another issue will show all of the keys and the keyboard in their proper size, but when you pop out the keyboard as a floating window, the floating window will be minuscule.
It’s an irritating bug to have, but there are workarounds. According to users, to fix the keyboard, you can restart your phone. However, that can get annoying after a while. Another thing you can do is force-stop the keyboard from the App Info screen. Other than that, users are just going to have to wait until Google fixes the issue. Since Gboard and Android Auto are very popular services, we’re certain that a substantial amount of people are experiencing this bug. So, we expect enough reports to come out to get Google’s attention.
Speaking of Gboard, Google recently released a feature that allows the Gboard Proofreader to proofread selected text. This makes it a lot more convenient to use rather than proofreading entire bodies of text.
Right now, we are trying to figure out how to differentiate between what’s real and what’s artificially generated. It’s extremely tough for companies to do this because AI companies like OpenAI, Google, MidJourney, etc. are constantly improving their technology. It’s to the point where they are indistinguishable from real-life images.
This wasn’t much of a problem back in 2022 when AI image generation first hit the public. However, it’s now a major concern in 2024, as the US presidential election is set to begin within a few months. So, we can expect unscrupulous individuals to artificially generate false images of wrongdoing on either side of the political spectrum.
AI-generated images of Trump with black supporters hit the internet
Even though the elections are months out, we are already getting our first taste of AI-generated political misinformation. According to sources, there have been a handful of images depicting former president Donald Trump with black supporters. These are the types of images that distort reality and make people assume things that didn’t really happen. Unfortunately, we do not know the source of the images. However, according to the report, one image was actually generated as satire.
In any case, this still foreshadows a major issue that is only going to ramp up as we get closer to the official election. In fact, there have been several studies that show just how easy it is to create fake political images.
For example, one fairly recent report found that some of the top AI image generators are more susceptible to generating images of voter fraud than generating images of either Donald Trump or Joe Biden. Also, a report conducted by the nonprofit Center for Countering Digital Hate found that they were able to create images of armed militia members at polling spots and President Joe Biden stuffing ballot boxes.
So, it’s only the beginning of a storm we are going to have to weather over the next couple of months. Not only will the US be in a bind, but other countries as well. They will also have to deal with this type of drama with their government elections.
At this point, the companies making these image generators are not properly managing them. So, it’s extremely easy to create images like these. We’re going to have to see if major companies are going to be able to call or reduce these types of images before the elections take off.
GoPlus Security, a leading cybersecurity provider for the Web3 ecosystem, has successfully concluded its Series II+ private funding round, raising $4 million from a consortium of top-tier venture capital firms.
This latest financial injection provides additional funding to a private round conducted in 2022 by Binance Labs. These resources will bolster GoPlus Security’s mission to enhance the Web3 experience, aiming to provide robust protection and peace of mind for millions of users across the globe.
GoPlus Security provides a security data infrastructure layer for Web3. In total, $15M funding from several different rounds was led by major investment funds including Binance Labs, SevenX Ventures, Redpoint China Ventures, Avalanche, and Crypto.com. The latest investment provides follow-on funding to a private round conducted in 2022 that Binance Labs led.
GoPlus Security Co-Founder Eskil Tsu said: “This funding in our Private II+ round is not just a financial boost but a strong endorsement of our vision to redefine user security network in the Web3 space, in the Web3 way. I’m thrilled for the support and excited about the future we’re building together.”
GoPlus Security, with secured funding, is set to broaden its User Security Network. The goal is to develop a Web3 User Security Network that focuses on transparency and empowering users. This involves offering open-access security data that users can verify and trust, backed by a robust decentralized data and computing layer.
Additionally, GoPlus is launching an end-user service platform named “SecWareX”, by engaging third-party “User Security Services” like Harpio, Webacy, Kekkai, Trusta, Wallet Guard, etc. Through these initiatives, GoPlus aims to become the leading provider of User Security Modules as a Service across various blockchains, essentially creating a foundational layer for Web3 user security.
About GoPlus Security
GoPlus is building a Web3 User Security Network that prioritizes transparency and user empowerment by providing permissionless security data and an end-user service environment. Goplus offers User Security Modules as a Service to any Chain.
With a cutting-edge AI module, we adopted into the tech architecture, Goplus has already served 10K+ partnerships with 21M+ User Security Data calls daily, supporting 20+ public chains.
Leveraging top-notch advancements in Web3 defences, GoPlus Security enhances safety with end user-focused services in “SecWareX” while empowering protocol User Security teams with “SecWare” advanced resources for developers. More facts about Goplus in the following:
The utilization of GoPlus’s security data infrastructure has significantly increased, with a 5000-fold growth from 2022 to the present, and daily API calls reaching 21 million.
The platform incorporates an AI-driven module to monitor Web3 security, offering real-time detection of risks associated with tokens, NFTs, and malicious activities. It evaluates over thirty risk parameters to dynamically address thousands of potential attack vectors.
GoPlus provides a range of User Security Modules as a Service, supporting over 20 blockchain networks. This includes collaborations with Risk as a Service (RaaS) providers like Altlayer and partnerships with Layer 2 solutions such as zkSync, Manta, and Scroll.
The introduction of new products, such as the “Secscan” security engine and Secware Middleware, marks steps towards a more decentralized approach in data and computing security.
Plans are underway to launch SecWareX Planned in early March, aiming to offer users a customizable on-chain security experience. The GoPlus Token will serve as a utility token within this ecosystem, facilitating operations and expanding its utility.
GoPlus continues to focus on Web3 security innovation and user-centric solutions. This includes encouraging participation from the community by allowing them to contribute as SecWare Service Providers, Data Providers, and Computing Node Providers, in exchange for GoPlus Tokens, thereby enhancing the overall User Security Network.
Switching from one mobile platform to another is never easy. This is especially true when the two platforms are so different like iOS and Android are. Fortunately, it seems like Apple is working on a way to make switching from iPhone to Android easier, even if there’s still some time for the changes to take effect.
It’ll be easier to switch to the Android side soon
The European Union’s Digital Markets Act, or DMA, is rattling the entire tech industry. Since the act aims to increase competition in the EU’s digital markets, some of the largest online companies like Apple, ByteDance, Meta, and Microsoft brought changes to how they operate. One of those changes includes Apple making it easier for iPhone users to switch to Android phones.
Apple had the following to say as a part of Apple’s “Non-Confidential Summary” of how it’s complying with the European Union’s new Digital Markets Act.
“Apple plans to make further changes to its user data portability offering. Third parties offer migration solutions that help users transfer data between devices with different operating systems. To build on those options, Apple is developing a solution that helps mobile operating system providers develop more user-friendly solutions to transfer data from an iPhone to a non-Apple phone. Apple aims to make this solution available by fall 2025.”
While it’s unclear how it will work, this wouldn’t be the first “iPhone to Android” solution. Google made the “Switch to Android” app for iOS users a while back. However, it’s limited in what data you can transfer and, in our experience, doesn’t work the best. Most of the limitations stem from the restrictions of iOS in providing the “Switch to Android” application access to data.
The document states that the solution will “build on” currently existing migration tools. This suggests Apple’s plan might be to give Google better access to data from iOS devices. Doing this would make the “Switch to Android” application a complete solution for users switching from iPhone to Android.
There’s still time until Apple gives more information on this change since Apple likely plans to make it available by late 2024 or early 2025. Naturally, making it easier for iPhone users from the EU to switch to Android devices but restricting others wouldn’t fare well with anyone. Therefore, the solution might initially be only for EU users. Hopefully, everyone will get access to it shortly after its launch.
Update: In an announcement on April 21, 2022, CNN+ will cease operations on April 30,2022. Lasting just 33 days. Some of the content will shift over to HBO MAX in the future.
CNN Plus is yet another streaming service that is launching in 2022. It’s not a full-fledged streaming service like Disney Plus or Hulu, but instead a compliment to the existing CNN channel that you get with your cable or streaming live TV subscription. It’s a lot like what ESPN Plus is to ESPN.
The service is not yet available, but will be launching on March 29, 2022. So here is everything that we know about CNN Plus right now.
What is CNN Plus?
CNN says that this service will serve as a way for people to get the news who don’t already have a cable or satellite TV service, and also does not have a streaming Live TV service. Basically, WarnerMedia is looking to capture the cord-cutters with CNN Plus, who still want to keep up on the news.
WarnerMedia has said that CNN Plus will offer between eight and 12 hours of live programming every single day. There will also be on-demand news specials, including some that are going to be exclusive to CNN Plus.
There has been some talk about some interactive elements to the service, like allowing those that watch content on CNN Plus to interact directly with its news anchors and commentators. Though this has not been revealed just yet.
When does it launch?
CNN announced in early March, that the new service is going to start streaming on March 29, 2022. Prior to this, WarnerMedia kept referencing a “Spring 2022” date. This is in the early part of Spring which is likely surprising to a number of people.
If you sign up for CNN Plus now, you’ll be able to log in a much cheaper price, before it goes live on March 29, 2022.
How much will CNN Plus cost?
CNN Plus will be available for $5.99 per month, or you can get an annual plan for $59.99/year (basically giving you two months free). That makes it one of the cheaper streaming services out there. CNN is likely hoping that due to the low price, many will sign up and keep the subscription, since it is so cheap compared to Netflix, Hulu and others.
For a limited time, if you sign up for CNN Plus ahead of the March 29, 2022 launch date, you can get it for $2.99 per month for as long as you keep your subscription. At that price, it is a lot more attractive.
Will there be ads?
WarnerMedia has confirmed that there will be no ads or commercial within CNN Plus. What that means is that you won’t see ads for retirement homes and such on CNN Plus, like you do on regular CNN. But you will see “ads” for other content on CNN and CNN Plus. So there will be some breaks in the live video on demand, but to promote its own content. Peacock does this already on its ad-free plan.
There could be a time in the future where CNN Plus does ad some ads and commercials to the service though, for a cheaper price. Offering an ad-free and ad-supported tier like Peacock, HBO MAX and Hulu.
Can I bundle it with HBO MAX?
Currently, WarnerMedia has no plans to bundle CNN Plus with HBO MAX (or Discovery Plus once that merger goes through). But that could change in the future, and likely will. Given how popular the Disney Plus bundle has been for Disney since it launched. But at this time, that is not the plan.
Where will I be able to stream CNN Plus?
At launch, CNN Plus will only be available in the US. This could change in the future, as CNN is an international news channel. But for now, WarnerMedia has said it will be US only.
For those that already use the CNN app for things like CNNgo, that will sunset. All of the different streaming services that CNN has worldwide will live within the CNN app starting on March 29.
“At the launch of CNN+, the CNNgo brand will sunset for users on desktop, mobile and several streaming platforms and devices, and the functionality of accessing CNN TV content will be fully integrated within CNN’s app. CNN will have a single app where CNN+ subscribers can access CNN+ programming and pay TV subscribers can get the TV Everywhere experience they have enjoyed for many years. The app will include CNN’s linear TV feeds of CNN, CNN International, HLN and CNN en Español channels, which will be available exclusively for pay TV subscribers. Pay TV subscribers will also have the opportunity to subscribe to CNN+ to access the full CNN+ programming all in one place. CNNgo will remain on some select streaming platforms.”
What platforms will it be available on
As mentioned in the last section, CNN Plus is going to be available within the CNN app, so it will work everywhere that the CNN app already works. Which is virtually everywhere. But here’s the full list as of right now:
Apple TV
Amazon Fire TV
iPhone
iPad
Android Phone
Android Tablet
Web
At launch, surprisingly CNN Plus is not available on Android TV or Roku. But we wouldn’t be surprised to see those two platforms added in a few weeks or even sooner. Especially considering how large of a platform Roku is right now.
What can I watch on CNN Plus?
Since announcing CNN Plus last year, the company has gone on a hiring spree. It has already hired over 450 people for the service. And that hiring spree is likely to continue. WarnerMedia has announced some exclusive shows for CNN Plus already, these include:
The Newscast with Wolf Blitzer – A daily evening newscast hosted by The Situation Room’s Wolf Blitzer
Jake Tapper’s Book Club – A weekly show focusing on a number of diverse writers, hosted by CNN anchor Jake Tapper.
The Don Lemon Show – A weekly talk show hosted by CNN Anchor Dom Lemon.
Who’s Talking to Chris Wallace? – Chris Wallace, who formerly was a reporter and anchor for Fox News, has jumped over to CNN Plus. His weekly show will feature interviews with newsmakers, entertainers and other major figures.
In addition to that, over 1,000 hours of CNN library programming will be available. This includes all 12 seasons of Anthony Bourdain: Parts Unknown, all seven seasons of This is Life with Lisa Ling and many more titles. You will also have access to over 40 years of CNN’s news archive, allowing you to watch coverage of major world and national events, along with episodes of the classic talk show Larry King Live.
It will also feature some docuseries that are exclusive to the service, including:
The Land of the Giants: Titans of Tech – A five-part series on the rise of tech companies like Facebook, Google, and others.
The Murdochs: Empire of Influence – A six-part look at the Murdoch family, the media moguls that own Fox News, The Wall Street Journal, and more.
The Last Movie Stars – A six-part series about the lives of the movie star couple Joanne Woodward and Paul Newman.
And that’s really just the tip of the iceberg for what will be available on CNN Plus.
VMWare has issued secuity fixes for its VMware ESXi, Workstation, Fusion, and Cloud Foundation products. It has even taken the unusual step of issuing updates for versions of the affected software that have reached thier end-of-life, meaning they would normally no longer be supported.
This flaws affect customers who have deployed VMware Workstation, VMware Fusion, and/or VMware ESXi by itself or as part of VMware vSphere or VMware Cloud Foundation.
A virtual machine (VM) is a computer program that emulates a physical computer. A physical “host” computer can run multiple separate “guest” VMs that are isolated from each other, and from the host. The physical resources of the host are allocated to the VMs by a software layer called the hypervisor, which acts an intermediary between the host and the VM (the guest system).
VMWare’s decision to offer fixes for end-of-life software is because the vulnerabilities patched in these updates are escape flaws that allow a computer program to breack of the confines of a VM and affect the host operating system. Specifically, an attacker with privileged access, such as root or administrator, on a guest VM can access the hypervisor on the host.
Besides instructions about how to update the affected products, the advisory lists possible workarounds that would block an attacker from exploiting the vulnerabilities. Since three of the vulnerabilities affect the USB controller, applying the workarounds will effectively block the use of virtual or emulated USB devices. For guest operating systems that do not support using a PS/2 mouse and keyboard, such as macOS, this means they will effectively be unable to use a mouse and keyboard.
The Common Vulnerabilities and Exposures (CVE) database lists publicly disclosed computer security flaws. The CVEs patched in these updates are:
CVE-2024-22252 and CVE-2024-22253 are use-after-free vulnerabilities in the XHCI and UHCI USB controllers of VMware ESXi, Workstation, and Fusion. A malicious actor with local administrative privileges on a virtual machine can exploit the issues to execute code as the virtual machine’s VMX process running on the host. On ESXi, the exploitation of either is contained within the VMX sandbox, but on Workstation and Fusion this may lead to code execution on the machine where Workstation or Fusion is installed.
The VMX process is a process that runs in the kernel of the VM and is responsible for handling input/output (I/O) to devices that are not critical to performance. The VMX is also responsible for communicating with user interfaces, snapshot managers, and remote consoles.
Use-after-free vulnerabilities are the result of the incorrect use of dynamic memory during a program’s operation. If, after freeing a memory location, a program does not clear the pointer to that memory, an attacker can exploit the error to manipulate the program. Referencing memory after it has been freed can cause a program to crash, use unexpected values, or execute code.
CVE-2024-22254 is an out-of-bounds write vulnerability in VMWare ESXi. A malicious actor with privileges within the VMX process can trigger an out-of-bounds write leading to an escape of the sandbox.
A sandbox environment is another name for an isolated VM in which potentially unsafe software code can execute without affecting network resources or local applications.
An out-of-bounds write can occur when a program writes outside the bounds of an allocated area of memory, potentially leading to a crash or arbitrary code execution. This can happen when the size of the data being written to memory is larger than the size of the allocated memory area, when the data is written to an incorrect location within the memory area, or when the program incorrectly calculates the size or location of the data to be written
CVE-2024-22255 is an information disclosure vulnerability in the UHCI USB controller of VMware ESXi, Workstation, and Fusion. A malicious actor with administrative access to a VM may be able to exploit this issue to leak memory from the VMX process.
We don’t just report on vulnerabilities—we identify them, and prioritize action.